
 Third Party Risk Management Market | 2026-2036
Third Party Risk Management Market Size, Share, and Industry Trends Forecast 2026-2036
Third Party Risk Management Market Intelligence
Enterprise software procurement channels is reconfiguring as buyers consolidate vendor relationships around integrated governance platforms. BitSight leverages security ratings to anchor its position in cyber risk quantification. ProcessUnity specializes in cloud-native workflow automation for vendor assessments. OneTrust competes across privacy and third-party risk convergence.
Third party risk management encompasses the systematic identification, assessment, and mitigation of hazards introduced by external vendors, suppliers, and service providers, typically deployed through continuous monitoring dashboards and automated control frameworks that score vendor resilience against standardized criteria. The discipline protects organizational assets from supply chain disruption, data breaches, and regulatory penalties. Software Solutions commands the largest revenue share as enterprises replace point tools with unified platforms. Compliance Risk accelerates fastest as regulators mandate demonstrable vendor oversight across financial services and healthcare verticals. Managed Services captures expanding margin pools as mid-market buyers outsource specialist monitoring functions.
The EU Digital Operational Resilience Act and NIS2 Directive mandate granular third-party risk documentation for critical infrastructure operators, directly expanding addressable demand for audit-ready platforms. In the United States, SEC cybersecurity disclosure rules and FFIEC guidance compel public companies to disclose vendor risk governance practices. Stakeholders must evaluate whether native AI risk scoring capabilities or API ecosystem breadth will determine platform selection as automation expectations escalate.
Market Dynamics
Vendor consolidation around integrated governance platforms is compressing procurement cycles and elevating automation expectations across enterprise security operations. Financial institutions now mandate continuous monitoring rather than point-in-time assessments.
Growth Catalysts
- EU Digital Operational Resilience Act:Critical infrastructure operators must maintain granular third-party risk documentation, directly expanding demand for audit-ready platforms with native compliance mapping.
- Cloud-native workflow automation:Mid-market enterprises accelerate platform adoption to replace spreadsheet-based vendor assessments and eliminate manual control testing bottlenecks.
- United States:SEC cybersecurity disclosure rules and FFIEC guidance compel public companies to demonstrate vendor risk governance practices in quarterly filings.
Market Restraints
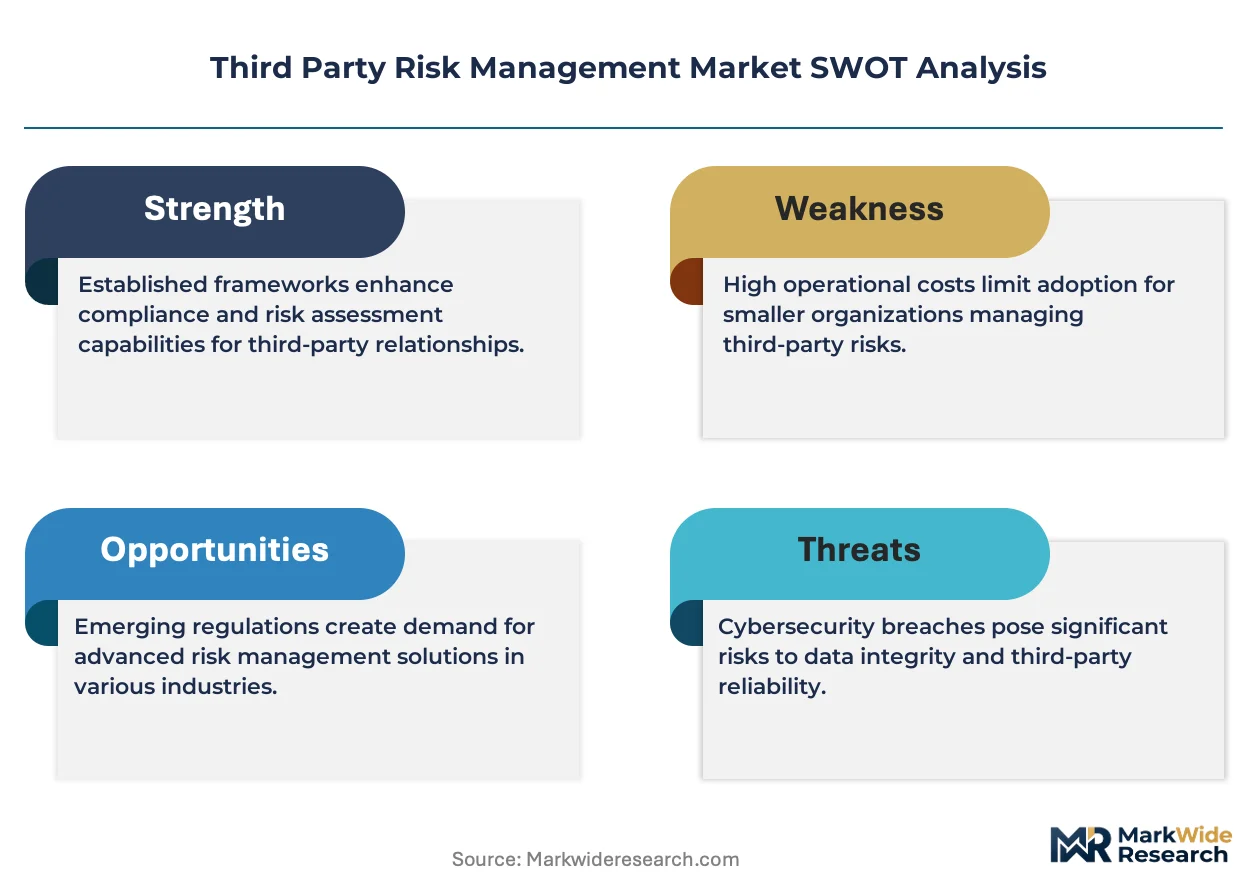
- Implementation cost structure:Enterprise-grade platform deployment requires substantial professional services investment, pricing out sub-$500M revenue organizations.
- Data source concentration:Reliance on limited security rating providers for external risk signals creates single-point-of-failure exposure in vendor scoring models.
- Technical interoperability limitation:Legacy ERP and GRC systems lack standardized APIs, forcing expensive custom integration workarounds.
Strategic Opportunities
- India:RBI guidelines on IT outsourcing and vendor risk management create immediate addressable demand among domestic banks and non-banking financial companies.
- AI-native risk scoring:Machine learning convergence with natural language processing enables automated contract clause extraction and dynamic risk tiering.
- Managed service channel:Mid-market buyers increasingly outsource continuous monitoring functions to specialist providers rather than building in-house capabilities.
Industry Challenges
- Quantitative risk modeling skill gap:Shortage of professionals combining cybersecurity expertise with statistical modeling capabilities delays platform value realization.
- Multi-jurisdictional compliance complexity:Divergent documentation requirements across EU DORA, US state privacy laws, and sector-specific mandates fragment vendor assessment workflows.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Third Party Risk Management Market |
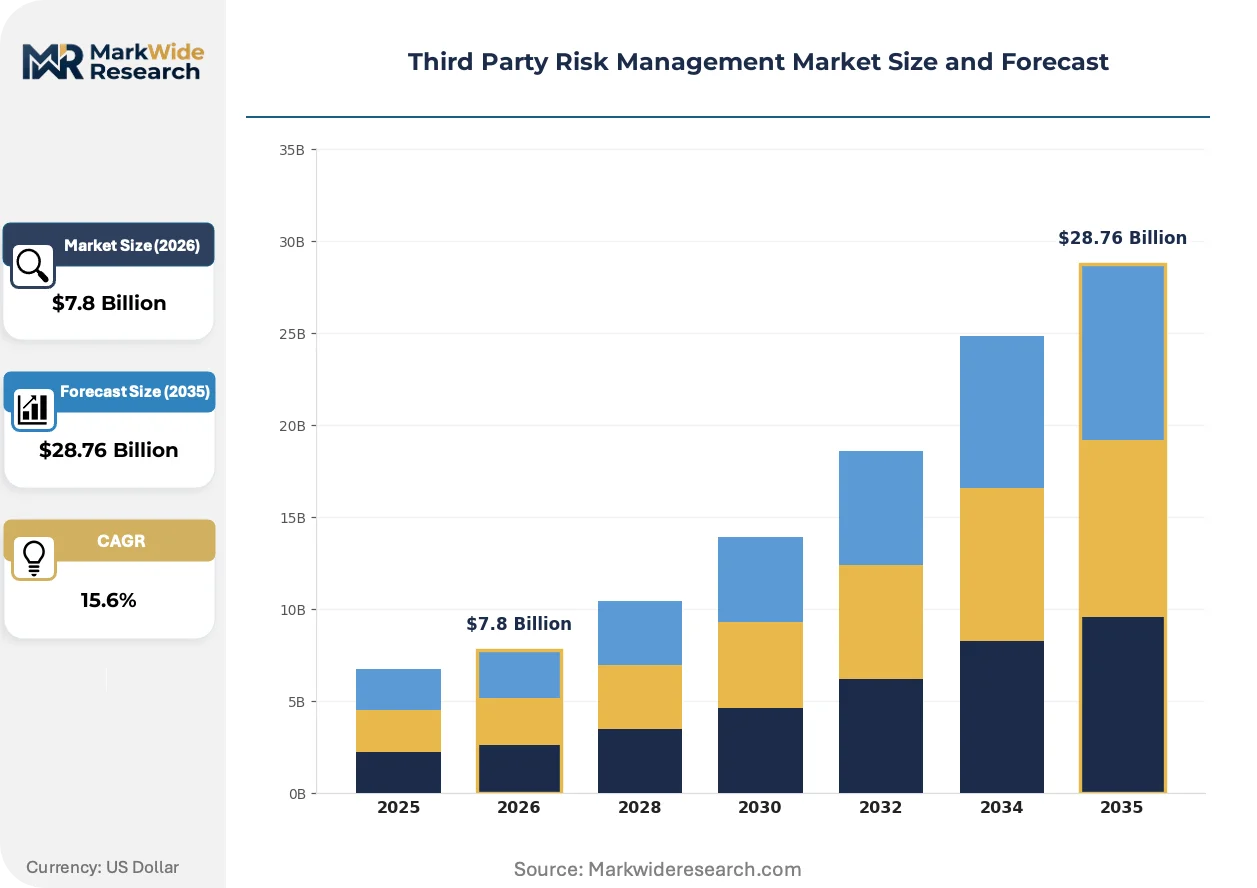
| Market Size in 2026 | $7.8 Billion |
| Market Size in 2035 | $28.76 Billion |
| CAGR (2026 – 2036) | 15.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Risk Type: Operational Risk, Credit Risk, Compliance Risk, Strategic Risk Service Type: Consulting Services, Software Solutions, Managed Services, Training Services Industry Vertical: Financial Services, Healthcare, Manufacturing, Technology Deployment Model: On-Premises, Cloud-Based, Hybrid, Mobile |
| Companies Covered | Archer, Mitratech, Riskonnect, UpGuard, ProcessUnity, OneTrust, Diligent, BitSight, AuditBoard, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Third Party Risk Management Market Strategic Shifts & Innovations
Automation architectures are fundamentally restructuring how enterprises orchestrate vendor oversight, compressing assessment cycles from quarters to days. Three convergent developments define this transformation.
Continuous control monitoring is migrating from periodic questionnaire-based assessments to real-time telemetry ingestion from vendor security postures. Large financial institutions now demand API-fed risk signals rather than annual attestations. This migration from static documentation to dynamic data streams is collapsing the traditional procurement-security handoff timeline.
The EU NIS2 Directive mandates incident reporting and supply chain risk management for essential and important entities across member states. Industrial operators must document sub-contractor dependencies and establish coordinated vulnerability disclosure procedures. Energy and transport verticals in Germany, France, and the Netherlands face the steepest compliance ramps.
Consolidated vendor relationship strategies now dominate enterprise procurement, with CISOs and Chief Procurement Officers jointly evaluating platforms. Point solutions for security ratings, privacy management, and ESG screening are losing budget share to unified governance suites. This pattern is most pronounced in US healthcare and financial services, where regulatory overlap between HIPAA, GLBA, and state privacy laws favors integrated tooling.
Third Party Risk Management Market Segmentation
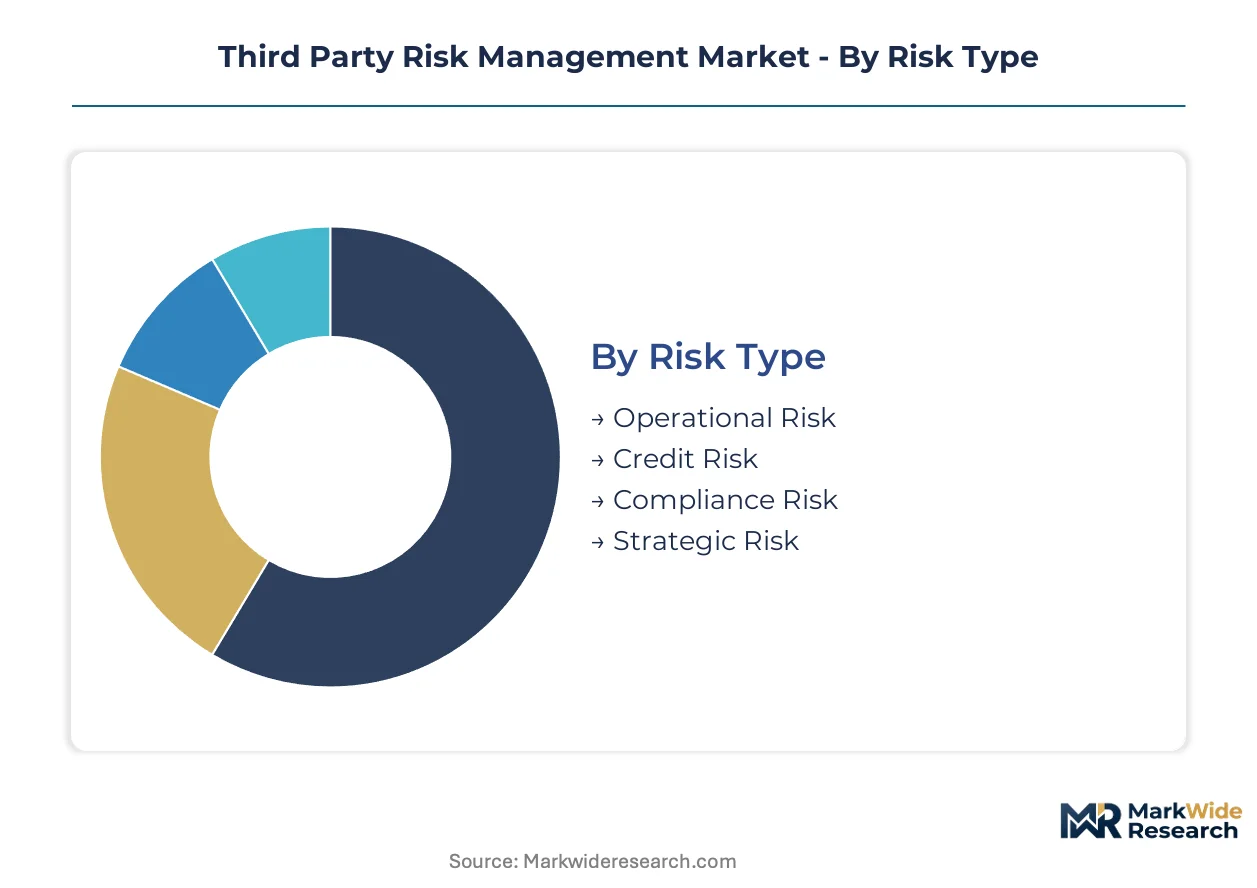
Third party risk management platforms segment across risk taxonomy, service delivery modes, industry verticals, and infrastructure deployment. Procurement patterns diverge sharply between financial institutions demanding continuous monitoring and mid-market buyers prioritizing cost-effective managed alternatives.
Risk Type:
Mature governance frameworks now distinguish four distinct risk categories with varying automation maturity and regulatory treatment intensity.
- Operational Risk:Encompasses business disruption, process failures, and system outages originating from vendor dependencies. Financial institutions in the United States concentrate procurement here as FFIEC guidance mandates operational resilience documentation for critical service providers.
- Compliance Risk:Covers regulatory violations, data protection breaches, and audit failures triggered by third-party actions. EU DORA and NIS2 Directive requirements are accelerating platform adoption among critical infrastructure operators seeking audit-ready compliance mapping.
- Credit Risk:Addresses counterparty default and financial instability of vendors. Supply chain finance programs and vendor concentration limits drive assessment protocols in corporate treasury functions.
- Strategic Risk:Captures reputational damage, competitive disadvantage, and innovation dependency from external partnerships. M&A due diligence and strategic sourcing teams deploy specialized scoring methodologies.
Operational Risk handles the majority of throughput; Compliance Risk is the fastest mover on share.
Service Type:
Cost tier stratification separates enterprise buyers investing in integrated platforms from resource-constrained organizations outsourcing specialist functions.
- Software Solutions:Unified governance platforms replace point tools with continuous monitoring dashboards, automated control frameworks, and native AI risk scoring. Enterprise procurement concentrates in the United States as SEC disclosure rules compel demonstrable vendor oversight.
- Managed Services:Specialist providers deliver continuous monitoring, threat intelligence integration, and incident response coordination on subscription basis. Mid-market buyers across healthcare and manufacturing verticals outsource capabilities rather than building in-house security operations centers.
- Consulting Services:Advisory engagements cover vendor assessment program design, regulatory readiness reviews, and remediation roadmap development. Professional services investments dominate initial platform deployment phases.
- Training Services:Certification programs and workforce development modules address quantitative risk modeling skill gaps limiting platform value realization.
Software Solutions commands the dominant revenue position; Managed Services is expanding most quickly as mid-market buyers prioritize operational leverage over capital deployment.
Industry Vertical:
Application intensity varies by regulatory exposure and supply chain complexity, with financial services and healthcare maintaining the most mature assessment protocols.
- Financial Services:Banks, insurers, and asset managers confront overlapping mandates from SEC, FFIEC, and EU DORA requiring continuous vendor oversight. Native compliance mapping and API-fed risk signals are now baseline procurement requirements.
- Healthcare:HIPAA privacy and security rules intersect with state breach notification laws, favoring integrated tooling that consolidates vendor risk with patient data governance. US hospital systems and pharmaceutical manufacturers lead adoption.
- Manufacturing:Industrial operators under EU NIS2 Directive must document sub-contractor dependencies and establish coordinated vulnerability disclosure procedures. Energy and transport sub-verticals face the steepest compliance ramps.
- Technology:Cloud service providers and software vendors face customer audit demands and downstream liability exposure from integrated third-party components.
Financial Services sustains the deepest platform penetration; Healthcare is gaining share fastest as state privacy law proliferation intensifies vendor oversight requirements.
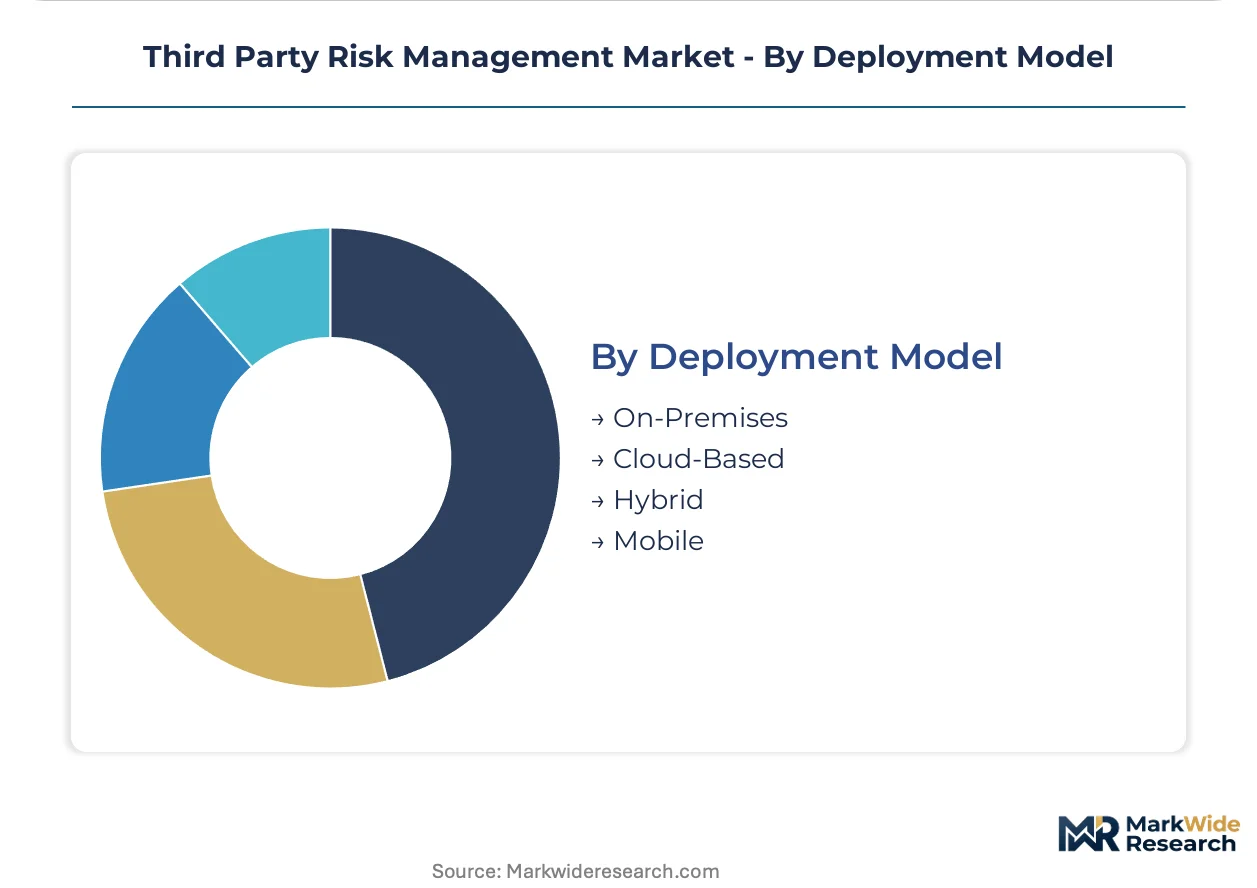
Deployment Model:
Infrastructure preferences reflect data sovereignty requirements, legacy system constraints, and workforce mobility patterns across buyer segments.
- Cloud-Based:SaaS delivery enables rapid deployment, elastic scaling, and continuous feature updates without on-premises maintenance burden. Mid-market enterprises across all verticals accelerate migration to replace spreadsheet-based assessment workflows.
- Hybrid:Combines cloud-native analytics with on-premises data repositories to address jurisdictional data residency mandates. German and French critical infrastructure operators favor this architecture under EU data localization expectations.
- On-Premises:Self-managed installations persist in defense contractors, classified environments, and organizations with strict air-gapped security requirements.
- Mobile:Native applications extend executive dashboards and alert notifications to distributed risk management teams and field audit personnel.
Cloud-Based deployment dominates new procurement volume; Hybrid configurations are climbing the fastest as multi-jurisdictional compliance complexity fragments data architecture decisions.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States-based enterprises extract pricing premiums from integrated governance suites that European buyers resist, creating a transatlantic value-capture gap. Vendor consolidation accelerates faster in North American procurement cycles. Regulatory fragmentation across jurisdictions sustains regional deployment preferences.
United States
Financial institutions and healthcare systems drive platform procurement as SEC cybersecurity disclosure rules and FFIEC guidance mandate demonstrable vendor oversight. HIPAA intersects with state breach notification laws across California, New York, and Texas. Silicon Valley clusters anchor cloud-native workflow automation adoption among technology vendors.
Germany
Industrial operators under EU NIS2 Directive face steep compliance ramps for sub-contractor dependency documentation. The Federal Office for Information Security enforces granular third-party risk standards for critical infrastructure. Energy and transport verticals in North Rhine-Westphalia and Bavaria prioritize hybrid deployment architectures for data residency.
United Kingdom
Post-Brexit regulatory divergence creates demand for platforms mapping both EU DORA and domestic Prudential Regulation Authority requirements. The Financial Conduct Authority mandates operational resilience documentation for outsourcing arrangements. London's financial services concentration sustains the deepest continuous monitoring penetration in Europe.
India
RBI guidelines on IT outsourcing and vendor risk management create immediate addressable demand among domestic banks and non-banking financial companies. SEBI mandates strengthen governance expectations for capital market participants. Mumbai and Bangalore clusters lead adoption of managed service alternatives to in-house security operations.
France
ANSSI oversight of critical infrastructure operators under NIS2 drives documentation requirements for supply chain risk management. The CNIL intersects with sectoral mandates for data protection impact assessments. Paris-based energy and transport operators coordinate vulnerability disclosure procedures across subcontractor networks.
Third Party Risk Management Market Key Industry Players
Platform integrators command the system tier; component specialists sit upstream in security ratings and workflow automation. The vendor base stratifies between unified governance suites and point solutions for cyber risk quantification. Two dominant archetypes emerge: cloud-native workflow automation providers and security rating aggregators. Competitive moves concentrate on API ecosystem expansion and native AI risk scoring capabilities.
Within the platform integration tier, Archer and Mitratech occupy positions anchoring enterprise governance, risk, and compliance consolidation. Riskonnect exemplifies the workflow automation archetype. BitSight and UpGuard represent the cyber risk quantification specialist segment. These five entities collectively illustrate the competitive tension between breadth-first platform strategies and depth-first security signal specialization.
| Leading Market Players |
|---|
| Archer |
| Mitratech |
| Riskonnect |
| UpGuard |
| ProcessUnity |
| OneTrust |
| Diligent |
| BitSight |
| AuditBoard |
| Others |
Cost & Logistics Intelligence
Silicon Valley's concentration of cloud-native platform engineering talent compresses deployment timelines and elevates automation premiums for integrated governance suites. Buyers in the United States extract faster value realization from these capabilities than European counterparts facing data residency constraints.
Pricing Analysis
The customization-premium spread between configured enterprise deployments and standardized SaaS tiers spans three-to-five multiples in annual contract value. Three-tier pricing structure across premium, standard, and economy levels reflects integration depth, AI-native risk scoring inclusion, and managed service bundling. Pricing pressure stems from mid-market buyers consolidating around unified platforms rather than point solutions. Healthcare systems exhibit highest price sensitivity due to constrained IT budgets, while financial institutions prioritize capability depth over cost minimization.
Supply Chain Analysis
Tariff exposure between the United States and China dominates component sourcing risk for on-premises hardware appliances still deployed in classified environments. Software supply chains draw from India for engineering talent, Ireland for EU data residency infrastructure, and Singapore for Asia-Pacific delivery hubs. Reliance on limited security rating providers for external risk signals creates single-point-of-failure exposure. Distribution runs through direct enterprise sales teams, hyperscaler marketplaces, and managed service provider channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation opportunity persists as regulatory divergence between EU DORA, US SEC disclosure rules, and India's RBI guidelines creates jurisdiction-specific platform requirements. Mid-market buyers seeking operational leverage without capital deployment represent underserved niches.
For Market Incumbents: Build API ecosystem moats by expanding native integrations with legacy ERP and GRC systems that lack standardized interfaces. Defensive consolidation should prioritize workflow automation specialists in cloud-native vendor assessment. Threat from AI-native entrants with automated contract clause extraction capabilities demands accelerated machine learning investment. Channel control through managed service provider certification programs protects margin pools.
For New Entrants and Emerging Players: Establish a beachhead in India's domestic banking sector where RBI guidelines on IT outsourcing create immediate compliance-driven demand. White-space targets include non-banking financial companies lacking in-house security operations centers and European industrial operators under NIS2 Directive sub-contractor documentation mandates. Go-to-market through managed service channel partnerships accelerates customer acquisition without enterprise sales infrastructure.
For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-complexity play because vendor oversight mandates intensify across jurisdictions regardless of macroeconomic cycles. Acquisition target archetype: workflow automation specialists with cloud-native architectures and established API ecosystems. Signal to watch is EU DORA implementation timeline adherence among critical infrastructure operators as inflection indicator for audit-ready platform demand.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidation of security ratings, privacy management, and ESG screening into unified governance suites addresses regulatory overlap. |
| AI-Native Risk Scoring Development | Machine learning convergence with natural language processing enables automated contract clause extraction and dynamic risk tiering. |
| Managed Service Channel Expansion | Mid-market buyers across healthcare and manufacturing verticals outsource continuous monitoring functions rather than building in-house capabilities. |
| Geographic Expansion | India's RBI guidelines and SEBI mandates create immediate addressable demand among domestic banks and capital market participants. |
| Strategic Partnership | Joint evaluation by CISOs and Chief Procurement Officers favors integrated tooling that collapses procurement-security handoff timelines. |
Research Approach
Desk research of regulatory filing databases, vendor assessment platform documentation, and compliance framework publications preceded structured interviews with chief information security officers, third-party risk program directors, procurement executives at financial institutions, and managed service provider operations leads. Primary intelligence combined with secondary validation from SEC disclosure filings, EU regulatory impact assessments, and RBI circular archives. Bottom-up vendor revenue analysis triangulated against top-down market sizing by deployment model and organization size tier.
Assumptions held fixed include regulatory implementation timelines for EU DORA and NIS2 Directive, cloud migration penetration curves across mid-market enterprises, and AI risk scoring technology maturation trajectories. Variables stress-tested encompass interest rate sensitivity affecting enterprise software procurement cycles, talent availability for quantitative risk modeling roles, and hyperscaler marketplace channel expansion rates. Segmentation modeling spanned risk taxonomy, service delivery mode, industry vertical, and infrastructure deployment across the analysis window. CAGR derivation incorporated platform replacement cycle acceleration and compliance-driven upgrade patterns.
Stress conditions across regulatory enforcement intensity, vendor consolidation velocity, and AI automation adoption curves were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect assumptions about continuous monitoring becoming baseline procurement requirement rather than point-in-time assessment persistence. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Financial Services Security Software Market
Risk Management and Compliance
Asset Liability Management (ALM) Solution Market
Risk Management and Compliance
Anti-Money Laundering (AML) Market
Risk Management and Compliance
Asia-Pacific BFSI Biometrics Market
Risk Management and Compliance
Sell-Side Due Diligence Services Market
Risk Management and Compliance
Crypto Compliance Software Market
Risk Management and Compliance
Fraud Detection and Prevention (FDP) Market
Risk Management and Compliance
Global Credit Risk Rating Software Market
Risk Management and Compliance
North America Strategic Consulting Market
Risk Management and Compliance
NPL Management Market
Risk Management and Compliance
Disclosure Management Market
Risk Management and Compliance
Stress Testing Services Market
Risk Management and Compliance
Global Compliance Management Software Market
Risk Management and Compliance
UK Anti Money Laundering Solutions Market
Risk Management and Compliance
Global Risk and Compliance Consulting Services Market
Risk Management and Compliance
Cyber Security in BFSI Market