
 Vendor Risk Management Market | 2026-2036
Vendor Risk Management Market Size, Share, and Industry Trends Forecast 2026-2036
Vendor Risk Management Market Intelligence
Healthcare and life sciences procurement is expanding its use of vendor risk platforms as pharmaceutical supply chains face heightened scrutiny over cybersecurity and quality failures. BitSight Technologies leverages continuous security scoring to differentiate its offering across financial services clients. MetricStream sustains broad governance, risk, and compliance integration that anchors its position in highly regulated industries. Genpact competes through specialized managed services that combine technology with human analyst oversight for complex vendor portfolios.
Vendor risk management encompasses the systematic identification, assessment, mitigation, and monitoring of third-party supplier risks across financial, operational, cybersecurity, and compliance dimensions. The discipline employs automated data ingestion, continuous control monitoring, and predictive analytics to reduce supply chain disruption and regulatory exposure. Cloud-based deployment models are capturing the fastest growth as enterprises prioritize scalability and remote accessibility over capital-intensive on-premises infrastructure. AI and machine learning technology segments command premium pricing due to their capacity for real-time anomaly detection and predictive risk scoring across thousands of vendor relationships.
The US Federal Reserve, OCC, and FFIEC collectively enforce third-party risk management guidance that mandates documented oversight of critical service providers. The EU Digital Operational Resilience Act (DORA) imposes binding incident reporting and resilience testing requirements on financial entities and their ICT vendors. ISO 27001 and SOC 2 Type II certifications function as baseline market-access credentials that filter vendor eligibility in enterprise procurement. Stakeholders must monitor the convergence of cybersecurity frameworks with ESG due diligence requirements as procurement teams consolidate supplier evaluation criteria into unified risk platforms.
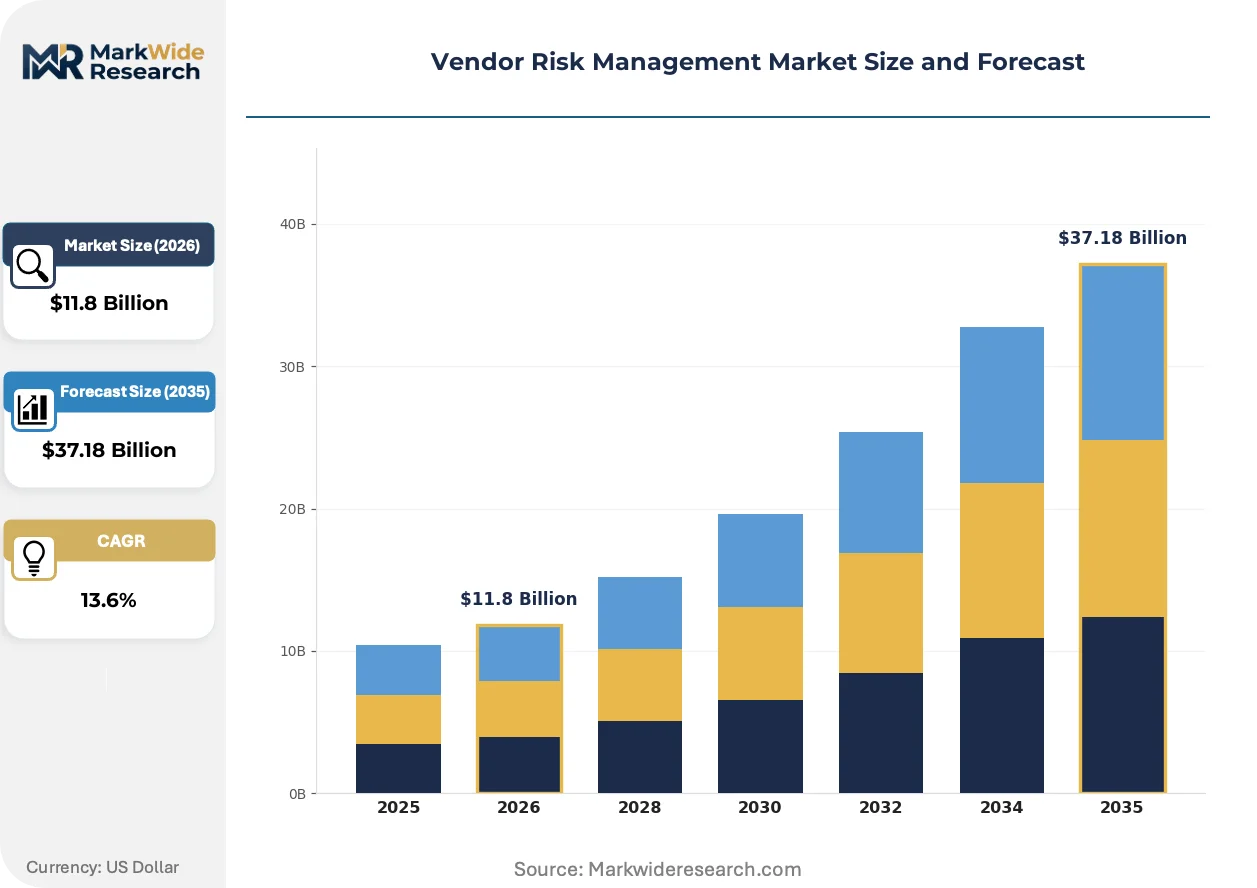
Market Dynamics
Cloud-native vendor risk platforms are compressing deployment cycles from months to weeks, forcing incumbent providers to accelerate platform modernization or cede mid-market share to agile challengers.
Growth Catalysts
- DORA compliance mandates:EU financial institutions must implement continuous monitoring of critical ICT vendors by early 2025, creating immediate procurement urgency for automated oversight tools.
- Pharmaceutical supply chain scrutiny:FDA quality system regulations now explicitly require documented third-party risk assessments for contract manufacturing organizations.
- AI-powered anomaly detection:Machine learning models trained on vendor performance telemetry enable predictive intervention before contract breaches materialize.
Market Restraints
- Data integration complexity:Heterogeneous ERP landscapes at Fortune 500 enterprises require expensive custom API development to achieve unified vendor visibility.
- Cyber insurance cost inflation:Premium spikes of 40-60% for vendor-related breach coverage are squeezing procurement budgets and delaying platform investments.
- Talent scarcity in quantitative risk modeling:The shortage of professionals combining domain expertise with data science capabilities limits implementation velocity.
Strategic Opportunities
- ESG-vendor risk convergence:Procurement teams seek unified platforms scoring suppliers on carbon exposure, labor practices, and financial stability simultaneously.
- Mid-market penetration in Germany:Mittelstand manufacturers remain underserved by enterprise-focused solutions, presenting white space for modular SaaS offerings.
- Embedded risk scoring APIs:Banking core system vendors can integrate continuous monitoring directly into loan origination and treasury workflows.
Industry Challenges
- Legacy system integration friction:Mainframe-based procurement systems at established banks resist API connectivity, forcing parallel manual processes.
- Cross-border data sovereignty:GDPR restrictions on vendor data transfer outside the EU complicate centralized risk analytics for multinational corporations.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Vendor Risk Management Market |
| Market Size in 2026 | $11.8 Billion |
| Market Size in 2035 | $37.18 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Assessment Services, Compliance Management, Continuous Monitoring, Reporting Solutions Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services Technology: AI & Machine Learning, Big Data Analytics, Automation Tools, Risk Assessment Software Customer Type: SMEs, Large Enterprises, Government Agencies, Non-Profits |
| Companies Covered | BitSight Technologies, MetricStream, Genpact, IBM Corporation, ServiceNow, NAVEX Global, Prevalent, LogicGate, OneTrust, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Vendor Risk Management Market Strategic Shifts & Innovations
Continuous control monitoring is displacing point-in-time assessments as the default operating model, with real-time data feeds replacing annual vendor questionnaires across regulated industries.
Natural language processing applied to vendor contracts is rewriting how procurement teams extract obligation clauses and renewal triggers. Fortune 500 legal departments deploy these tools to audit thousands of supplier agreements within days rather than quarters. The compression of contract review cycles is enabling more frequent vendor renegotiation and faster termination of underperforming relationships.
The EU Digital Operational Resilience Act imposes binding incident reporting timelines on financial entities and their critical ICT vendors. Institutions must notify regulators within four hours of significant operational disruptions, forcing investment in automated detection and escalation workflows. Asset managers and payment processors are prioritizing vendors with pre-certified DORA compliance to avoid procurement delays.
Enterprise buying committees now demand outcome-based pricing tied to measurable risk reduction rather than seat-based SaaS subscriptions. Healthcare systems and regional banks are piloting contracts where platform fees scale with prevented vendor incidents or accelerated remediation times. This shift is most pronounced in the United States, where procurement leaders face heightened board accountability for third-party failures.
Vendor Risk Management Market Segmentation
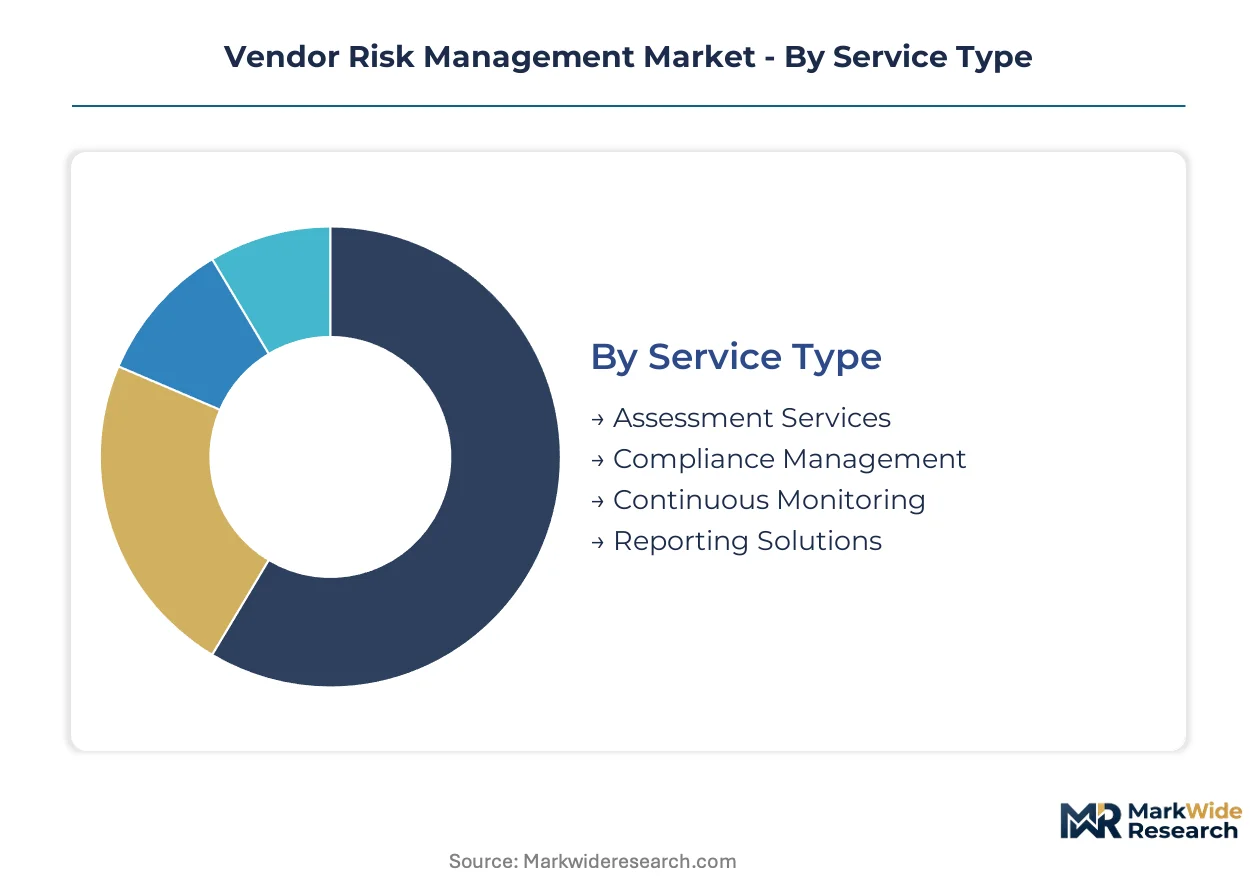
Vendor risk management procurement diverges sharply by organizational scale and regulatory exposure, with Fortune 500 financial institutions demanding predictive analytics while mid-market buyers prioritize rapid deployment. Segmentation reveals where platform vendors can defend premium pricing versus where modular SaaS offerings capture share.
Service Type:
Procurement teams weigh upfront assessment depth against ongoing operational burden when selecting service tiers.
- Assessment Services:Point-in-time vendor evaluations using standardized questionnaires and on-site audits. Large US banks with legacy supplier portfolios rely on these for baseline risk cataloging despite longer cycle times.
- Compliance Management:Continuous regulatory mapping against DORA, FFIEC guidance, and ISO 27001 requirements. EU financial institutions facing binding incident reporting mandates are concentrating demand here.
- Continuous Monitoring:Real-time telemetry from vendor security ratings and financial health indicators.
- Reporting Solutions:Automated board-ready dashboards and regulatory submission packages.
Assessment Services leads on scale; Continuous Monitoring leads on momentum.
Deployment Model:
IT infrastructure maturity and data sovereignty requirements shape deployment architecture decisions across buyer segments.
- Cloud-Based:Multi-tenant SaaS platforms with API-first integration architectures. US healthcare systems and regional banks are prioritizing these for remote accessibility and reduced capital expenditure.
- On-Premises:Dedicated hardware installations behind corporate firewalls. German automotive manufacturers and US defense contractors mandate these for classified supplier data.
- Hybrid:Sensitive risk data on-premises with analytics processing in cloud environments.
- Managed Services:Outsourced analyst teams handling vendor onboarding and ongoing monitoring.
Cloud-Based deployments are climbing the fastest; On-Premises retains pricing power in regulated verticals.
Technology:
Platform differentiation increasingly depends on algorithmic sophistication rather than workflow automation alone.
- AI & Machine Learning:Predictive models trained on vendor bankruptcy signals and security incident patterns. US asset managers and payment processors are paying premium pricing for real-time anomaly detection across thousands of supplier relationships.
- Big Data Analytics:Aggregation of external data feeds including credit ratings, news sentiment, and breach disclosures. Financial services procurement teams in London and New York use these for concentration risk visualization.
- Automation Tools:RPA-driven questionnaire distribution and response validation.
- Risk Assessment Software:Rules-based scoring engines with configurable weighting frameworks.
Big Data Analytics leads on scale; AI & Machine Learning commands the steepest expansion trajectory.
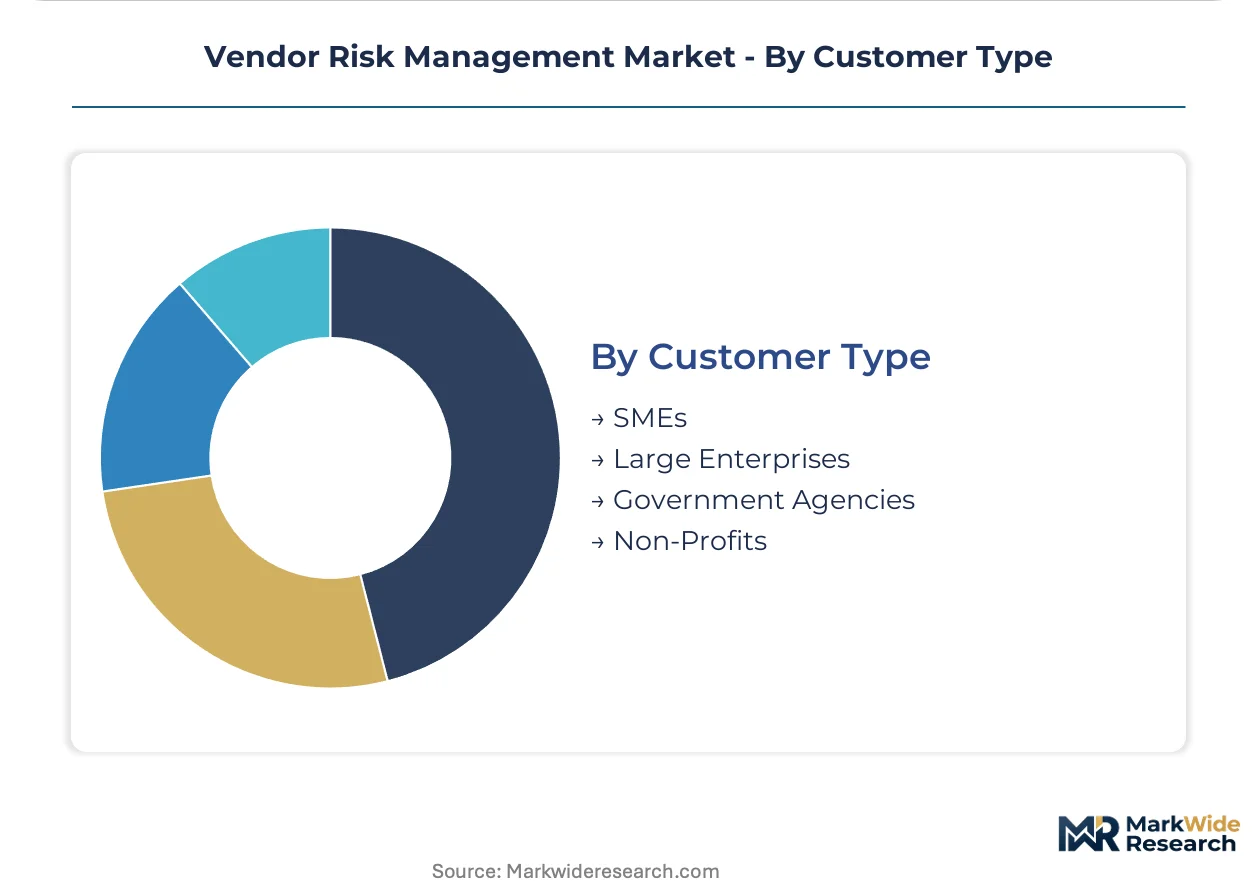
Customer Type:
Budget availability and procurement committee complexity create distinct selling motions across organizational categories.
- Large Enterprises:Multi-divisional implementations with custom integration requirements. Fortune 500 companies in the United States with complex supplier ecosystems drive the majority of platform revenue.
- SMEs:Standardized SaaS subscriptions with pre-configured risk frameworks. UK and German mid-market manufacturers represent underserved white space for modular offerings.
- Government Agencies:FedRAMP-authorized or equivalent certified deployments.
- Non-Profits:Grant-funded implementations with donor transparency requirements.
Large Enterprises dominate current revenue; SMEs are gaining share fastest as self-service platforms mature.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory divergence between jurisdictions with binding third-party mandates and those with voluntary frameworks is redirecting procurement investment toward compliance-heavy markets. Financial institutions in stricter regulatory environments now outspend peers on automated vendor oversight platforms by significant margins.
United States
Fortune 500 financial services firms with complex supplier ecosystems drive the majority of platform revenue. The Federal Reserve, OCC, and FFIEC collectively enforce third-party risk management guidance mandating documented oversight of critical service providers. New York and Chicago anchor concentrated demand among asset managers and payment processors prioritizing vendors with pre-certified compliance.
Germany
Mittelstand manufacturers remain underserved by enterprise-focused solutions, presenting white space for modular SaaS offerings. The EU Digital Operational Resilience Act imposes binding incident reporting and resilience testing requirements on financial entities and their ICT vendors. Frankfurt's banking cluster and Munich's industrial corridor are accelerating procurement of continuous monitoring tools ahead of early 2025 deadlines.
United Kingdom
Financial services procurement teams in London use big data analytics for concentration risk visualization across thousands of supplier relationships. The Prudential Regulation Authority and Financial Conduct Authority maintain stringent third-party oversight expectations aligned with evolving EU standards. The City of London and Canary Wharf districts concentrate demand among asset managers seeking predictive risk scoring capabilities.
France
EU DORA compliance mandates are creating immediate procurement urgency for automated oversight tools among banking and insurance sectors. ANSM and CNIL oversight extends to vendor data handling in life sciences and digital services. Paris and Lyon host expanding procurement teams consolidating cybersecurity frameworks with ESG due diligence into unified risk platforms.
Japan
Financial institutions are prioritizing cloud-native deployments for remote accessibility and reduced capital expenditure. METI guidance on supply chain resilience is tightening expectations for documented third-party assessments. Tokyo and Osaka concentrate demand among regional banks and pharmaceutical distributors modernizing legacy procurement systems.
Vendor Risk Management Market Key Industry Players
Platform modernization dominates the current landscape as incumbent providers accelerate cloud migration to defend mid-market share against agile challengers. The vendor base segments into three distinct tiers: established governance platforms with broad compliance integration, specialized security scoring services, and managed service providers combining technology with analyst oversight. Strategic archetypes include predictive analytics specialists commanding premium pricing, modular SaaS vendors penetrating underserved mid-markets, and vertically integrated consultancies bundling software with implementation. M&A activity and outcome-based pricing contracts represent the dominant competitive moves reshaping vendor selection criteria.
Within the predictive analytics tier, BitSight Technologies exemplifies continuous security scoring differentiation across financial services clients. MetricStream occupies a position anchoring broad governance, risk, and compliance integration for highly regulated industries. Genpact sits within the managed services archetype, combining technology platforms with human analyst oversight for complex vendor portfolios. These three represent distinct strategic positions rather than direct substitutes, with procurement committees often engaging multiple archetypes for complementary capabilities.
| Leading Market Players |
|---|
| BitSight Technologies |
| MetricStream |
| Genpact |
| IBM Corporation |
| ServiceNow |
| NAVEX Global |
| Prevalent |
| LogicGate |
| OneTrust |
| Others |
Cost & Logistics Intelligence
API integration labor costs cascade through vendor risk management platform tiers, with enterprise buyers absorbing premium pricing for custom ERP connectors while mid-market adopters select standardized SaaS bundles to limit implementation spend.
Pricing Analysis
Distributor margins compress at the value-added reseller layer as direct-to-enterprise sales channels expand. Subscription-based SaaS pricing dominates, with tiered pricing separating AI-enabled predictive tiers from rules-based automation tiers. Price differentiation hinges on ISO 27001 certification tier and integration complexity scale. Pricing pressure stems from outcome-based contract demands by US healthcare systems. SMEs exhibit highest price sensitivity; Fortune 500 financial institutions demonstrate lowest.
Supply Chain Analysis
EU data residency rules are reshaping sourcing decisions, forcing platform vendors to establish EU-based cloud infrastructure for financial services clients. Software development concentrates in the United States, India, and Ireland. Cloud compute capacity draws from hyperscaler networks in Virginia, Frankfurt, and Singapore. Supply chain risk centers on single-source vulnerability for specialized AI talent. Distribution runs through direct enterprise sales teams with limited channel partner penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vendor risk management procurement operates as a geographic-arbitrage play, with EU DORA compliance deadlines accelerating premium pricing in Frankfurt and Paris while US mid-market buyers delay purchases amid budget compression.
For Market Incumbents: Extend platform modernization roadmaps to compress cloud-native deployment cycles below six weeks, countering agile challengers capturing mid-market share. Invest in pre-certified DORA compliance modules to defend pricing power against specialized security scoring entrants. Prioritize embedded API partnerships with banking core system vendors as the priority channel lever.
For New Entrants and Emerging Players: Begin with modular SaaS offerings targeting German Mittelstand manufacturers, the most penetrable white space underserved by enterprise-focused solutions. Pursue outcome-based pricing pilots with US regional banks as the specific go-to-market angle, differentiating against seat-based incumbents.
For Investors and Strategic Acquirers: Roll-up economics work for managed service providers combining technology with analyst oversight because talent scarcity in quantitative risk modeling limits organic scaling. Target firms with pre-built DORA compliance workflows and established EU banking relationships. Watch EU regulatory enforcement intensity as the inflection signal for platform consolidation velocity.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedded risk scoring APIs within banking core systems accelerate procurement cycles for US asset managers. |
| Acquisition of Specialist Firm | Continuous monitoring technology targets fill capability gaps in legacy governance platforms serving EU insurers. |
| Geographic Expansion | EU cloud infrastructure investments satisfy DORA data sovereignty requirements for Frankfurt banking clusters. |
| Strategic Partnership | Hyperscaler alliances reduce compute costs for AI-powered anomaly detection across thousands of vendor relationships. |
| Product Launch | Unified ESG-cyber risk scoring modules address procurement committee demands for consolidated supplier evaluation. |
Research Approach
Coverage spans the United States, Germany, United Kingdom, France, and Japan, with primary inputs from each market triangulated against secondary validation. Chief risk officers, procurement directors at Fortune 500 financial institutions, vendor management leads at pharmaceutical manufacturers, compliance officers at EU asset managers, and cloud platform engineers provided structured interviews. Secondary sources include FFIEC guidance documents, EU DORA regulatory texts, ISO 27001 certification databases, SEC 10-K risk disclosures, and healthcare system procurement records. Bottom-up vendor platform revenue estimates reconcile with top-down market sizing across deployment models.
Granularity-level modeling segments the market by service type, deployment architecture, technology tier, and customer scale, with additional dimensioning by regulatory jurisdiction cluster. Value projections across the analysis window derive from pricing elasticity assumptions by buyer archetype and adoption curve penetration by organization size. CAGRs incorporate technology substitution rates for AI-enabled platforms versus rules-based alternatives and cloud-native displacement of on-premises installations.
Caveats apply where EU DORA enforcement intensity or US Federal Reserve guidance revisions could materially shift the outlook for compliance-driven procurement. Forecasts reflect assumptions about mid-market SaaS maturation and talent availability for quantitative risk modeling. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Treasury and Risk Management Application Market
Risk Management and Compliance
Cyber Security in BFSI Market
Risk Management and Compliance
Treasury and Risk Management Market
Risk Management and Compliance
Third Party Risk Management Market
Risk Management and Compliance
Europe Risk Management Market
Risk Management and Compliance
Loan Compliance Management Software Market
Risk Management and Compliance
Oil and Gas Risk Management Market
Risk Management and Compliance
Asia-Pacific BFSI Biometrics Market
Risk Management and Compliance
NPL Management Market
Risk Management and Compliance
Asset Liability Management (ALM) Solution Market
Risk Management and Compliance
Quality Warranty Management Market
Risk Management and Compliance
Anti-Money Laundering (AML) Market
Risk Management and Compliance
Fraud Detection and Prevention (FDP) Market
Risk Management and Compliance
AI in Fraud Management Market
Risk Management and Compliance
Risk Assessment Software Market
Risk Management and Compliance
Operations Advisory Service Market