
 Cyber Security in BFSI Market | 2026-2036
Cyber Security in BFSI Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Security in BFSI Market Outlook
Managed detection and response services is restructuring how cybersecurity value gets delivered to financial institutions, shifting capital expenditure into recurring operational contracts. IBM Corporation leverages its hybrid cloud security portfolio to anchor institutional clients with compliance-integrated offerings. Palo Alto Networks competes through platform consolidation, bundling network, cloud, and endpoint protection into unified architectures. Fortinet dominates price-sensitive mid-tier banking segments with integrated firewall and SD-WAN security stacks.
Cyber Security in BFSI encompasses the technologies, processes, and governance frameworks that protect financial data, transaction integrity, and customer identity across banking, insurance, and investment operations, typically incorporating encryption standards such as AES-256, multi-factor authentication protocols, and real-time behavioral analytics to detect anomalous access patterns. Its primary purpose is to prevent unauthorized data exfiltration, ensure regulatory compliance, and maintain operational continuity during targeted attacks. The solution type dimension shows firewall and intrusion detection systems commanding established spending pools, while risk assessment tools are gaining share as institutions face escalating third-party vendor exposure. Deployment model patterns reveal managed services expanding fastest among regional banks lacking in-house security operations centers, though hybrid architectures retain the largest installed base among multinational financial conglomerates.
The Federal Financial Institutions Examination Council (FFIEC) and the Securities and Exchange Commission (SEC) in the United States enforce cybersecurity examination protocols and incident disclosure requirements that directly shape vendor qualification criteria and procurement timelines. The European Banking Authority (EBA) and the EU Digital Operational Resilience Act (DORA) impose stringent third-party risk management and resilience testing mandates that redirect technology budgets toward compliant platform investments. Stakeholders must monitor how fragmented regulatory timelines across jurisdictions will force architectural decisions between unified global platforms and regionally segmented compliance stacks.
Market Dynamics
Retail banking institutions are consolidating vendor relationships around integrated security platforms as zero-trust architecture adoption accelerates across branch networks and mobile platforms. Regulatory mandates from the EU Digital Operational Resilience Act and comparable national frameworks are compelling financial institutions to harden third-party risk management protocols.
Growth Catalysts
- EU Digital Operational Resilience Act (DORA):This framework mandates stringent third-party risk management and resilience testing, redirecting technology budgets toward compliant platform investments across European banking operations.
- Zero-trust architecture:Retail banking institutions are expanding adoption across branch networks and mobile platforms, creating sustained demand for identity verification and micro-segmentation technologies.
- Managed detection and response services:Regional banks lacking in-house security operations centers are shifting capital expenditure into recurring operational contracts, restructuring how cybersecurity value gets delivered.
Market Restraints
- Specialized cybersecurity talent scarcity:The shortage of professionals certified in cloud security architecture and threat hunting limits institutional capacity to operate advanced security operations centers.
- Legacy system integration complexity:Core banking infrastructure built on decades-old architectures creates friction when deploying modern encryption standards and real-time behavioral analytics.
- Fragmented regulatory timelines:Divergent compliance deadlines across the United States, European Union, and Asia-Pacific force architectural decisions between unified global platforms and regionally segmented stacks.
Strategic Opportunities
- Open banking API security:The proliferation of third-party financial data aggregators creates demand for specialized API gateway protection and consent management frameworks.
- Quantum-resistant cryptography:Forward-thinking institutions are piloting post-quantum encryption standards ahead of anticipated regulatory mandates, securing early-mover positioning.
- India's digital banking expansion:The Reserve Bank of India's push for financial inclusion and digital payment infrastructure creates underpenetrated demand for cloud-native security solutions among regional banks.
Industry Challenges
- Multi-cloud security orchestration:Financial institutions operating across AWS, Azure, and Google Cloud environments struggle to maintain consistent policy enforcement and threat visibility.
- Third-party vendor due diligence:The Securities and Exchange Commission's incident disclosure requirements compress procurement timelines while elevating documentation burdens for vendor qualification.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Security in BFSI Market |
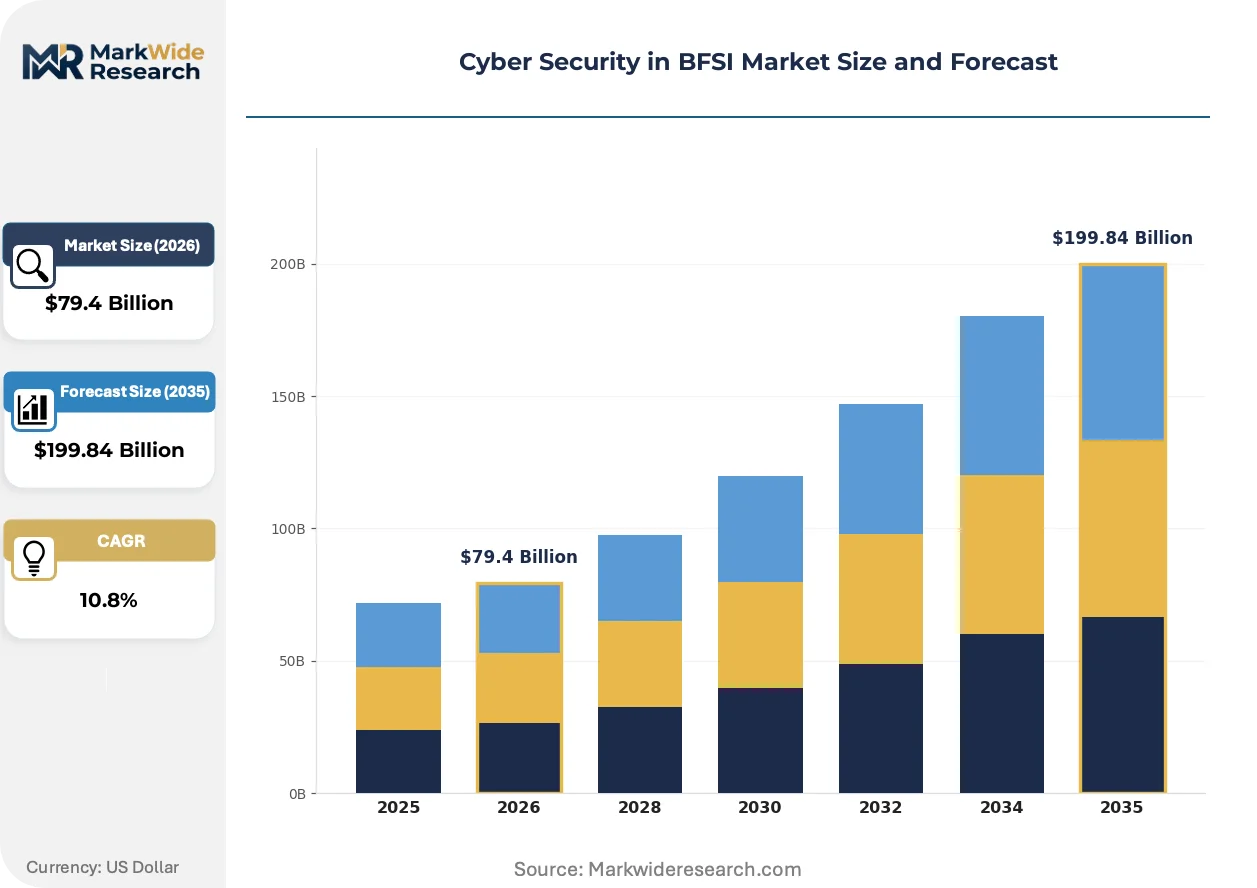
| Market Size in 2026 | $79.4 Billion |
| Market Size in 2035 | $199.84 Billion |
| CAGR (2026 – 2036) | 10.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Threat Type: Malware, Phishing, Ransomware, DDoS Solution Type: Firewall, Antivirus, Intrusion Detection, Risk Assessment Deployment Model: On-premises, Cloud, Hybrid, Managed Services End User: Banking, Insurance Firms, Investment Companies, Credit Unions |
| Companies Covered | IBM Corporation, Cisco Systems, Microsoft Corporation, Palo Alto Networks, Check Point Software Technologies, Trend Micro, Fortinet, Broadcom, McAfee, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Security in BFSI Market Strategic Shifts
Financial institutions are re-architecting security operations around cloud-native platforms and AI-driven threat detection, moving away from perimeter-based defenses toward continuous verification models.
Confidential computing is decentralizing how sensitive financial data gets processed, enabling banks to analyze encrypted datasets without exposing raw information. Major card networks and payment processors are piloting trusted execution environments for fraud detection workloads. This architecture is decentralizing risk concentration away from centralized data lakes toward distributed enclaves.
The EU Digital Operational Resilience Act imposes mandatory third-party risk management and resilience testing mandates that redirect technology budgets toward compliant platform investments. Financial institutions must now conduct thorough due diligence on cloud service providers and fintech partners. Investment banking and asset management segments face the steepest compliance burdens, accelerating consolidation around integrated vendor platforms.
Chief information security officers are unbundling traditional managed security service contracts, demanding modular pricing for detection, response, and recovery functions. This purchasing transformation disrupts legacy annual retainer arrangements and favors outcome-based engagement structures. The United States exhibits the most pronounced shift, where the largest banking conglomerates negotiate granular service-level agreements tied to mean-time-to-detection metrics.
Cyber Security in BFSI Market Segmentation
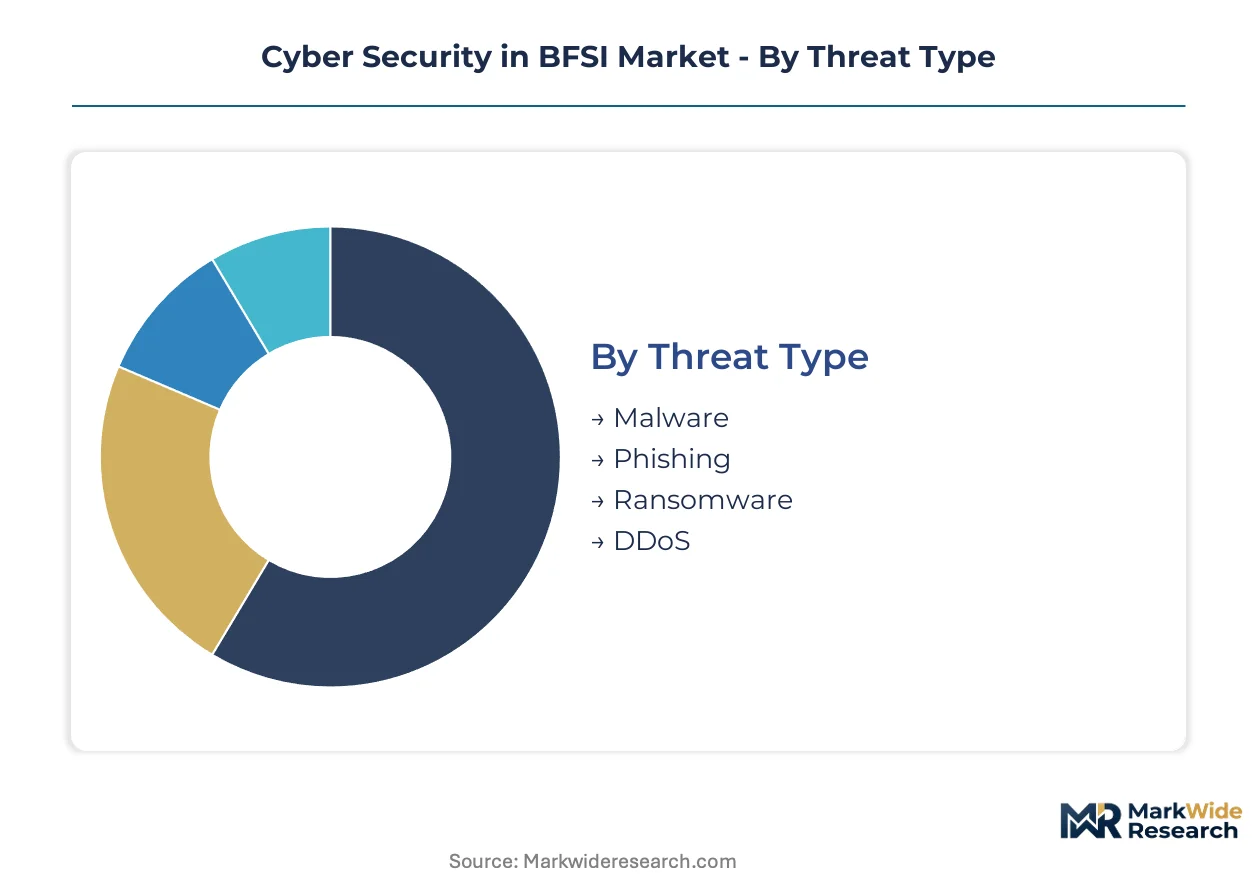
Cybersecurity procurement in financial services follows distinct technical and operational logics. Threat vectors dictate defensive technology choices, while deployment constraints shape vendor selection and contract structures across institutional tiers.
Threat Type:
Financial institutions prioritize threat coverage based on attack frequency and regulatory disclosure obligations.
- Malware:Persistent file-based threats targeting core banking terminals and SWIFT messaging infrastructure demand signature-based detection combined with behavioral heuristics. Demand concentrates among multinational banks operating across jurisdictions with divergent malware reporting requirements.
- Phishing:Credential-harvesting campaigns against retail banking customers and treasury staff require email gateway filtering and real-time link analysis. Regional banks in the United States allocate disproportionate budgets here due to FFIEC examination emphasis on customer-facing controls.
- Ransomware:Extortion attacks encrypting critical payment systems drive investment in immutable backup architectures and network segmentation.
- DDoS:Volumetric attacks against digital banking portals necessitate scrubbing center capacity and upstream provider coordination.
Malware leads on scale; phishing leads on momentum.
Solution Type:
Technology selection hinges on integration complexity with legacy core banking platforms and compliance audit trail requirements.
- Firewall:Next-generation firewalls with application-layer inspection form the perimeter defense backbone for branch networks and data centers. Mid-tier banks favor consolidated firewall-SD-WAN stacks to reduce vendor management overhead.
- Intrusion Detection:Network and host-based monitoring systems feed security operations centers with alert streams requiring analyst triage. Investment banking operations demand the lowest false-positive rates to maintain trading system availability.
- Antivirus:Endpoint protection platforms with extended detection and response capabilities replace traditional signature scanning.
- Risk Assessment:Automated vendor security scoring and control gap analysis tools address DORA-mandated third-party due diligence.
Firewall deployments dominate installed value; risk assessment tools climb the fastest.
Deployment Model:
Capital availability and in-house security expertise determine whether institutions build, buy, or outsource defensive capabilities.
- Cloud:Native security controls from hyperscale providers enable rapid scaling for digital banking workloads without data center capital expenditure. Neobanks and fintech subsidiaries adopt this model exclusively.
- Hybrid:Split architectures protecting on-premises core systems while extending cloud-native controls to customer-facing applications retain the largest footprint among established institutions. Multinational conglomerates require this approach to satisfy data residency mandates across operating jurisdictions.
- On-premises:Air-gapped or sovereign cloud deployments persist for critical payment infrastructure and classified regulatory examinations.
- Managed Services:Outsourced security operations center functions deliver 24/7 monitoring without specialized hiring. Regional banks lacking cybersecurity talent pipelines drive expansion here.
Hybrid architectures lead on scale; managed services gain share fastest.
End User:
Regulatory intensity and transaction velocity create divergent security investment patterns across financial subsectors.
- Banking:Retail and commercial banks face the broadest attack surface spanning branches, ATMs, mobile applications, and correspondent networks. The largest United States banking conglomerates consolidate vendor relationships around integrated platforms to streamline FFIEC examination preparation.
- Insurance Firms:Property-casualty and life insurers protect actuarial databases and claims processing systems with emphasis on data integrity and availability. European insurers allocate substantial budgets to DORA compliance for resilience testing and third-party risk management.
- Investment Companies:Asset managers and hedge funds prioritize trade execution security and algorithm protection. The SEC's incident disclosure requirements compress their procurement cycles.
- Credit Unions:Member-owned institutions with limited IT staff rely heavily on managed service providers and cooperative security purchasing arrangements.
Banking leads on scale; insurance firms lead on regulatory-driven momentum.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States concentrates cybersecurity procurement around consolidated vendor platforms, whereas Germany anchors European demand through DORA-mandated resilience investments. Japan and India represent contrasting growth trajectories shaped by regulatory maturity and digital banking expansion respectively.
United States
The FFIEC examination protocols and SEC incident disclosure requirements drive banking conglomerates toward integrated security platforms. Federal mandates compress procurement timelines while elevating documentation standards for vendor qualification. New York and San Francisco host the densest concentrations of financial institutions consolidating around hybrid cloud security architectures.
Germany
The EU Digital Operational Resilience Act redirects technology budgets toward compliant platform investments across Frankfurt's banking cluster. BaFin supervision enforces stringent third-party risk management protocols for critical financial infrastructure. Munich and Berlin anchor demand for quantum-resistant cryptography pilot programs among forward-thinking institutions.
United Kingdom
The Financial Conduct Authority's operational resilience rules compel insurers and asset managers to harden third-party vendor assessments. London's investment banking corridor prioritizes trade execution security and algorithm protection frameworks. Edinburgh and Manchester regional banks accelerate managed detection and response service adoption.
Japan
METI guidelines and the Financial Services Agency's cybersecurity framework shape procurement patterns among megabanks and regional institutions. Tokyo's financial district concentrates demand for confidential computing architectures in payment processing. Osaka and Nagoya commercial banks invest in API gateway protection for open banking integration.
India
The Reserve Bank of India's digital payment infrastructure push creates underpenetrated demand among regional banks lacking in-house security operations. Mumbai and Bangalore anchor fintech security innovation clusters serving both domestic and export markets. Hyderabad and Chennai emerging financial centers adopt cloud-native solutions for financial inclusion programs.
Cyber Security in BFSI Market Competitive Environment
Top-tier vendors anchor the integrated platform tier, while specialized threat detection providers occupy mid-market segments. The vendor structure concentrates around three strategic archetypes: hybrid cloud security platforms, network consolidation specialists, and price-optimized mid-tier stacks. Competitive dynamics center on M&A activity absorbing point-solution vendors and strategic partnerships embedding compliance modules into core banking systems.
Within the hybrid cloud security tier, IBM Corporation and Microsoft Corporation exemplify platform consolidation strategies that bind institutional clients through compliance-integrated offerings. Palo Alto Networks occupies a position representing network-centric vendors bundling perimeter and cloud-native controls. Fortinet anchors the price-sensitive segment with integrated firewall-SD-WAN stacks targeting mid-tier banking procurement.
| Leading Market Players |
|---|
| IBM Corporation |
| Cisco Systems |
| Microsoft Corporation |
| Palo Alto Networks |
| Check Point Software Technologies |
| Trend Micro |
| Fortinet |
| Broadcom |
| McAfee |
| Others |
Value Chain & Pricing Dynamics
Horizontal consolidation among managed security service providers anchors both supply positioning and pricing power in the Cyber Security in BFSI market, as regional banks lacking in-house security operations centers drive recurring contract structures that favor scale economies over point-solution premiums. The EU Digital Operational Resilience Act and comparable frameworks in the United States compress procurement timelines while elevating compliance-integrated offerings, concentrating vendor relationships around platforms that bundle detection, response, and recovery functions.
Pricing Analysis
Capacity additions in India and Southeast Asia are reshaping price floors for cloud-native security solutions, intensifying competition among managed detection and response providers. Three-tier pricing structure across premium, standard, and economy levels separates global banking conglomerates with custom SLAs from mid-tier institutions purchasing modular bundles and regional credit unions relying on cooperative purchasing arrangements. Price differentiation hinges on mean-time-to-detection guarantees and FFIEC examination preparation support. Cost compression in the standard tier is intensifying because Fortinet and similar vendors consolidate firewall-SD-WAN stacks. Credit unions exhibit the highest price sensitivity; investment banks with SEC disclosure obligations show the least.
Supply Chain Analysis
Dual-sourcing requirements embedded in DORA and FFIEC examination protocols mandate multi-supplier qualification for critical security functions, fragmenting vendor concentration across the United States, Germany, and India. Supply rests on specialized semiconductor components for encryption hardware, threat intelligence feeds from global security research networks, and certified cloud infrastructure from hyperscale providers. Single-source vulnerability concentrates in quantum-resistant cryptography pilot programs where qualified vendors remain scarce. Distribution runs through direct enterprise sales teams for multinational banking conglomerates, while regional banks source through managed service provider channels and cooperative security purchasing arrangements.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Cyber Security in BFSI market functions as a stable compounder, with regulatory mandates across multiple jurisdictions driving sustained technology refresh cycles regardless of macroeconomic conditions.
For Market Incumbents: Deepen platform integration by embedding DORA compliance modules directly into core banking system partnerships, defending against point-solution vendors that unbundle detection and response functions. Expand capacity additions in India to capture Reserve Bank of India digital payment infrastructure spending before regional banks consolidate vendor relationships. Certification investment in quantum-resistant cryptography secures early-mover positioning ahead of anticipated mandates.
For New Entrants and Emerging Players: Regional banks in India's emerging financial centers represent the most penetrable buyer archetype, lacking in-house security operations centers and receptive to cloud-native solutions for financial inclusion programs. API gateway protection for open banking integration offers white-space targeting, as Tokyo and Osaka commercial banks accelerate third-party data aggregator security spending. A channel partnership strategy with cooperative banking associations bypasses direct competition with IBM and Microsoft for multinational conglomerate accounts.
For Investors and Strategic Acquirers: Roll-up economics work for specialized threat detection providers because CISOs are unbundling traditional managed security service contracts and demanding modular pricing for discrete functions. The five-to-ten year viability window favors vendors with established FFIEC examination preparation capabilities and existing relationships with federal regulatory frameworks. Watch mean-time-to-detection metric standardization as the inflection indicator for outcome-based contract adoption.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Bundling network, cloud, and endpoint protection into unified architectures anchors institutional clients with compliance-integrated offerings. |
| Regulatory Compliance Module Development | Embedding DORA and FFIEC examination preparation capabilities directly into security platforms redirects technology budgets toward compliant investments. |
| Managed Detection and Response Expansion | Outsourced security operations center functions capture regional banks lacking cybersecurity talent pipelines and capital expenditure flexibility. |
| Quantum-Resistant Cryptography Piloting | Forward-thinking institutions in Germany and the United States secure early-mover positioning ahead of anticipated regulatory mandates. |
| Geographic Expansion in India | The Reserve Bank of India's digital payment infrastructure push creates underpenetrated demand among regional banks adopting cloud-native solutions. |
Study Parameters
Direct dialogue with chief information security officers, managed security service provider executives, regulatory affairs specialists at banking conglomerates, and procurement officers at regional credit unions grounded qualitative insights, validated against secondary sources including FFIEC examination guidelines, SEC cybersecurity disclosure filings, EU Digital Operational Resilience Act regulatory texts, and cloud security alliance certification databases. Bottom-up and top-down triangulation reconciled vendor revenue disclosures with institutional technology spending patterns across banking, insurance, and investment subsectors.
Segmentation-level projections across threat type, solution type, deployment model, and end user dimension incorporated zero-trust architecture adoption curves, managed services penetration rates among regional banks, and regulatory compliance timeline variations across the United States, European Union, and Asia-Pacific. CAGRs were derived from installed base growth trajectories and replacement cycle analysis rather than macroeconomic extrapolation. Industry-specific inputs included SWIFT messaging infrastructure security refresh patterns and open banking API proliferation rates.
Underlying measurement precision varies by segment; firewall and intrusion detection system spending pools carry tighter precision than emerging risk assessment tool categories where vendor definitions remain fluid. Forecasts reflect documented assumptions regarding regulatory enforcement intensity and cloud migration acceleration among mid-tier institutions. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Compliance As a Service Market
Risk Management and Compliance
Asia-Pacific BFSI Biometrics Market
Risk Management and Compliance
Healthcare Fraud Detection Market
Risk Management and Compliance
AI in Fraud Management Market
Risk Management and Compliance
Asset Liability Management (ALM) Solution Market
Risk Management and Compliance
Global Liquidity Asset Liability Management Solutions Market
Risk Management and Compliance
Risk Management Market
Risk Management and Compliance
Artificial Intelligence and Regtech Market
Risk Management and Compliance
Asia-Pacific Sustainable Finance Market
Risk Management and Compliance
United States Governance, Risk and Compliance Platform Market
Risk Management and Compliance
Legal Advisory Service Market
Risk Management and Compliance
Enterprise Governance, Risk, and Compliance (Egrc) Market
Risk Management and Compliance
Risk Assessment Software Market
Risk Management and Compliance
Operational Risk Management Consulting Services in Manufacturing Market
Risk Management and Compliance
BFSI Crisis Management Market
Risk Management and Compliance
Operations Advisory Service Market