
 Financial Services Security Software Market | 2026-2036
Financial Services Security Software Market Size, Share, and Industry Trends Forecast 2026-2036
Financial Services Security Software Market Analysis
Israeli cybersecurity R&D clusters is broadening the supply base for threat-intelligence modules purpose-built for banking infrastructure. ScienceSoft leverages its Eastern European engineering footprint to sustain cost-competitive delivery of encryption and compliance tooling. Check Point Software anchors its position through deep specialization in network security appliances tailored to payment processor environments.
Financial services security software encompasses endpoint protection, encryption, identity and access management, and network security platforms engineered to safeguard transactional data, customer records, and interbank communications against unauthorized access, malware infiltration, and insider threats. These systems integrate real-time behavioral analytics, tokenization protocols, and zero-trust architecture enforcement to maintain operational continuity across distributed banking networks. Identity and access management currently occupies the largest margin pool as institutions confront privileged-account sprawl across hybrid cloud estates, while cloud-based deployment configurations represent the fastest-expanding delivery mode as regulated entities retire on-premise hardware. Banks constitute the most mature end-user segment with established procurement cadences, whereas payment processors are emerging as the highest-velocity buyers as real-time settlement networks multiply.
The Federal Financial Institutions Examination Council in the United States, the European Banking Authority under EU-wide frameworks, and the Financial Conduct Authority in the United Kingdom collectively mandate minimum cyber-resilience standards that directly shape vendor product roadmaps and institutional procurement specifications. Compliance services and consulting engagements are expanding in tandem as institutions seek external validation against evolving supervisory expectations. Stakeholders must monitor divergence between regional encryption standards and cross-border data-localization requirements when architecting multi-jurisdiction deployments.
Market Dynamics
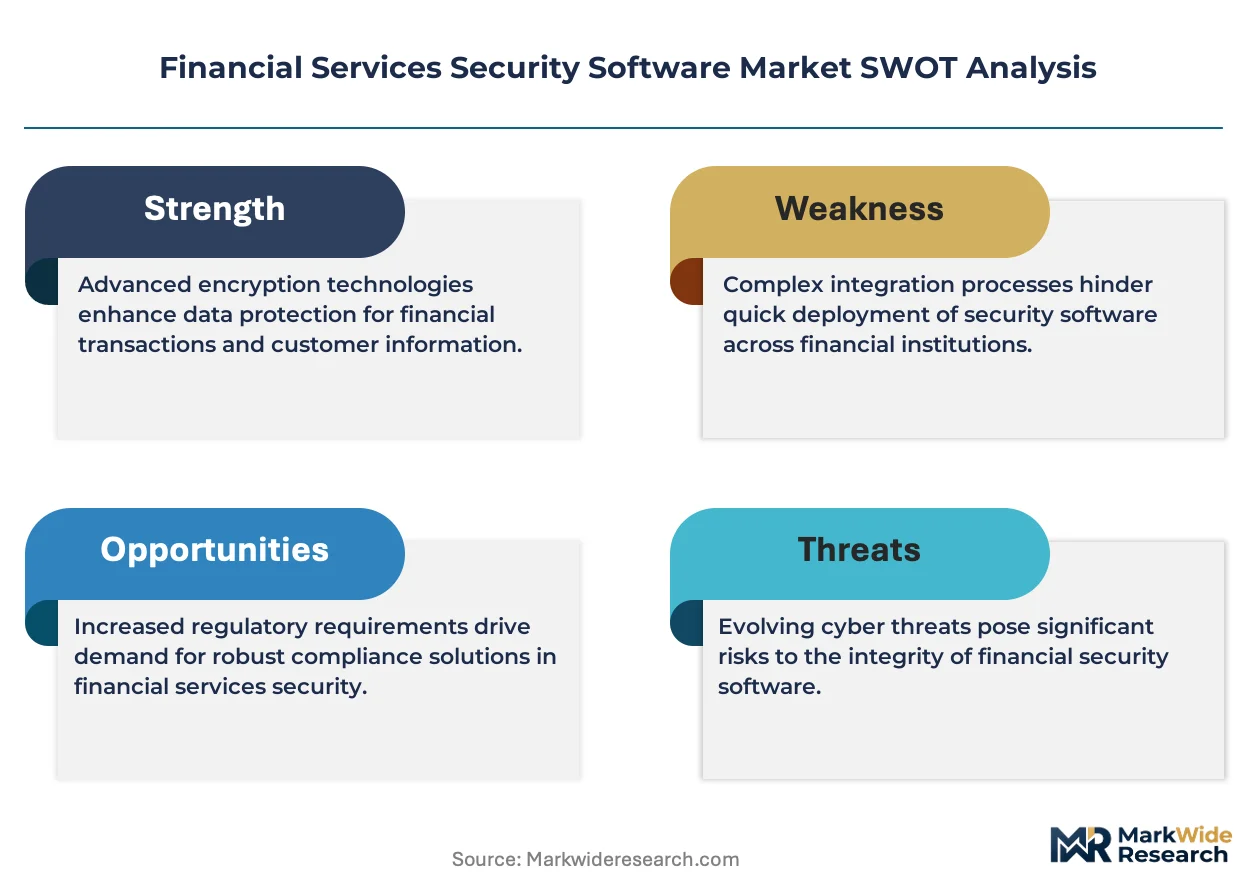
Zero-trust architecture mandates are forcing banks to dismantle perimeter-based security models and rebuild around continuous identity verification, creating cascading procurement waves across endpoint, network, and data protection layers.
Growth Catalysts
- GDPR and state-level US privacy frameworks:Financial institutions face escalating supervisory penalties for data breaches, accelerating replacement of legacy security stacks with cloud-native compliance tooling.
- Real-time payment networks:Payment processors demand sub-millisecond threat detection capabilities, pulling investment into behavioral analytics and automated response orchestration.
- Hybrid cloud estate expansion:Privileged-account sprawl across multi-cloud environments is concentrating vendor selection on unified identity and access management platforms.
Market Restraints
- Specialized cybersecurity talent scarcity:Shortages in zero-trust architecture and cloud security engineering constrain deployment velocity and inflate implementation costs.
- Cross-border data-localization conflicts:Divergent encryption standards between the United States, European Union, and United Kingdom fragment vendor product roadmaps and complicate multi-jurisdiction deployments.
- Legacy infrastructure interdependence:Core banking systems running on decades-old codebases resist API-based security integration, trapping institutions in hybrid complexity.
Strategic Opportunities
- EU AI Act compliance services:Automated governance tooling for algorithmic decision-making in credit and fraud detection represents an emerging white space as enforcement timelines crystallize.
- Quantum-resistant cryptography migration:Early-mover institutions are piloting post-quantum encryption standards, creating premium advisory and implementation revenue streams.
- Embedded finance security orchestration:Banking-as-a-Service platforms require white-label security modules, opening distribution through fintech infrastructure providers rather than direct bank sales.
Industry Challenges
- Multi-cloud security posture management:Institutions struggle to maintain consistent policy enforcement across AWS, Azure, and Google Cloud environments without creating visibility gaps.
- Insider threat program maturation:Behavioral monitoring systems generate false-positive rates that overwhelm security operations centers, demanding refined machine-learning training pipelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Financial Services Security Software Market |
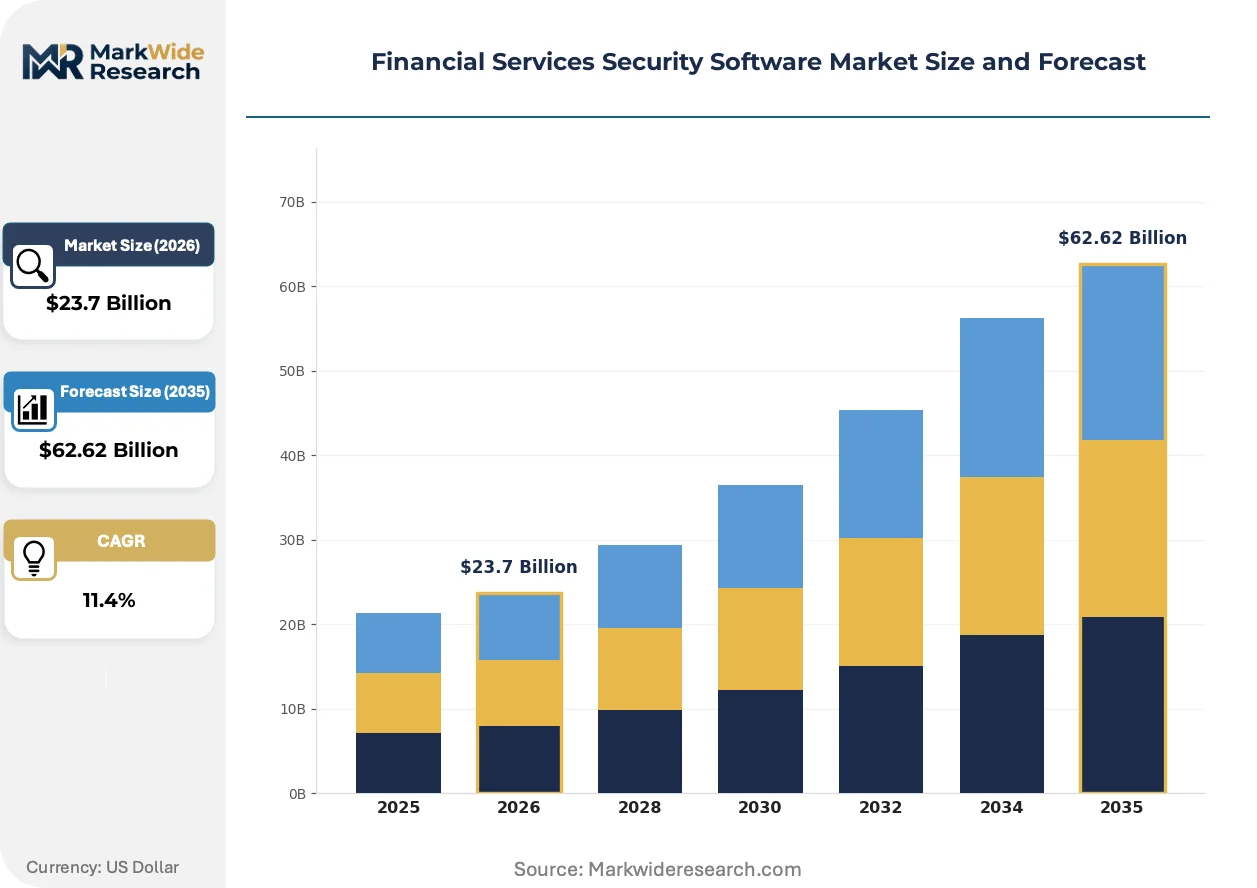
| Market Size in 2026 | $23.7 Billion |
| Market Size in 2035 | $62.62 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Protection, Encryption, Identity & Access Management, Network Security Deployment: On-Premise, Cloud-Based, Hybrid, Managed Services End User: Banks, Insurance Companies, Investment Firms, Payment Processors Service Type: Consulting Services, Training Services, Support Services, Compliance Services |
| Companies Covered | 10Clouds, Euvic, ScienceSoft, AvePoint, Intellectsoft, DBB Software, SDK.finance, Check Point Software, Relevant Software, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Financial Services Security Software Market Emerging Trajectories
Security software architectures are pivoting from reactive detection to predictive prevention, embedding artificial intelligence directly into transaction flows and access decisions rather than operating as external monitoring layers.
Extended detection and response platforms aggregate telemetry from endpoints, networks, and cloud workloads into unified threat-hunting consoles. Large banks and payment processors are deploying these systems within eighteen-month refresh cycles. XDR is converging with security information and event management consolidation, compressing vendor counts and forcing point-solution providers toward platform partnerships or acquisition.
The EU Digital Operational Resilience Act imposes strict third-party risk management requirements on critical financial infrastructure. Vendors must now maintain contractual liability caps and audit rights that reshape procurement negotiations. Cloud security providers serving EU-headquartered banks are restructuring service agreements to satisfy DORA's incident reporting timelines and concentration risk limits.
Outcome-based contracting is displacing perpetual license models as institutional buyers demand measurable risk reduction guarantees. Security vendors now face penalty clauses tied to mean-time-to-detect metrics and breach containment performance. This shift is most visible in the United Kingdom, where the Financial Conduct Authority's operational resilience deadlines have compressed vendor selection cycles and elevated chief information security officer authority in procurement decisions.
Financial Services Security Software Market Segmentation
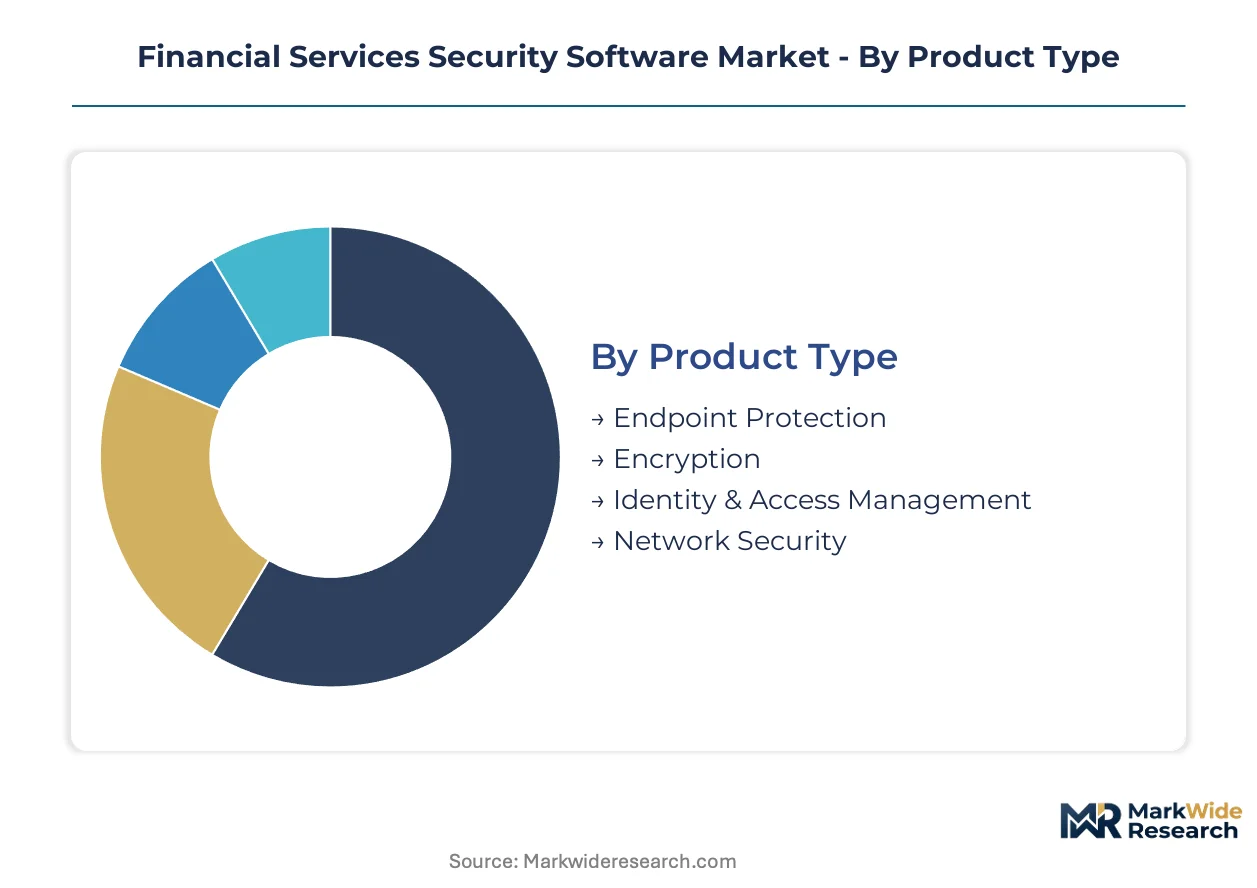
Financial institutions select security software through layered procurement criteria that balance regulatory mandates against operational architecture. Segmentation reveals how deployment constraints, end-user maturity, and compliance obligations fragment purchasing patterns across the value chain.
Product Type:
Buyers differentiate by the attack surface each solution protects and its integration burden with legacy core banking systems.
- Identity & Access Management:Unified platforms for privileged-account governance across hybrid cloud estates command the largest procurement budgets. Banks in the United States and Germany concentrate demand here as zero-trust mandates eliminate perimeter-based trust models.
- Endpoint Protection:Real-time behavioral analytics and automated threat containment defend workstations and mobile banking channels. Payment processors in the United Kingdom are accelerating refresh cycles to sub-eighteen-month intervals as real-time settlement networks expand.
- Encryption:Tokenization protocols and quantum-resistant algorithm suites protect data-at-rest and data-in-transit across interbank communications.
- Network Security:Deep packet inspection and microsegmentation appliances secure payment processor environments and SWIFT messaging infrastructure.
Identity & Access Management leads volumes today; Endpoint Protection is climbing the fastest as endpoint sprawl accelerates.
Deployment:
Institutional risk appetite and data-localization obligations determine whether buyers retain control or outsource operational responsibility.
- Cloud-Based:Native SaaS architectures deliver continuous compliance updates without hardware refresh cycles. Regulated entities in Germany and the United States are retiring on-premise hardware fastest where supervisory enforcement timelines are most aggressive.
- Hybrid:Split workloads across private data centers and public cloud instances preserve control over crown-jewel transactional data. Banks with decades-old core systems depend on hybrid configurations to bridge API-incompatible legacy codebases.
- On-Premise:Air-gapped installations persist where national data-localization statutes prohibit cross-border data flows.
- Managed Services:Outsourced security operations centers address talent scarcity in zero-trust architecture and cloud security engineering.
Hybrid deployments dominate current installed base; Cloud-Based configurations show steepest expansion trajectory as DORA and state-level US frameworks mature.
End User:
Maturity of procurement cadences and velocity of transactional infrastructure renewal separate buyer segments.
- Banks:Established three-to-five-year refresh cycles and dedicated CISO authority enable complex multi-year platform deployments. Retail and commercial banking divisions across the United States, United Kingdom, and Germany anchor baseline demand.
- Payment Processors:Real-time settlement networks and open banking APIs demand sub-millisecond threat detection. This segment exhibits the shortest procurement cycles and highest willingness to adopt outcome-based contracting with risk-reduction guarantees.
- Insurance Companies:Solvency II and state-level capital requirements shape cyber-resilience investment priorities around policyholder data protection.
- Investment Firms:SEC and FCA market abuse surveillance obligations drive surveillance-technology integration with security stacks.
Banks retain the largest aggregate spend; Payment Processors are expanding share fastest as real-time payment networks multiply.
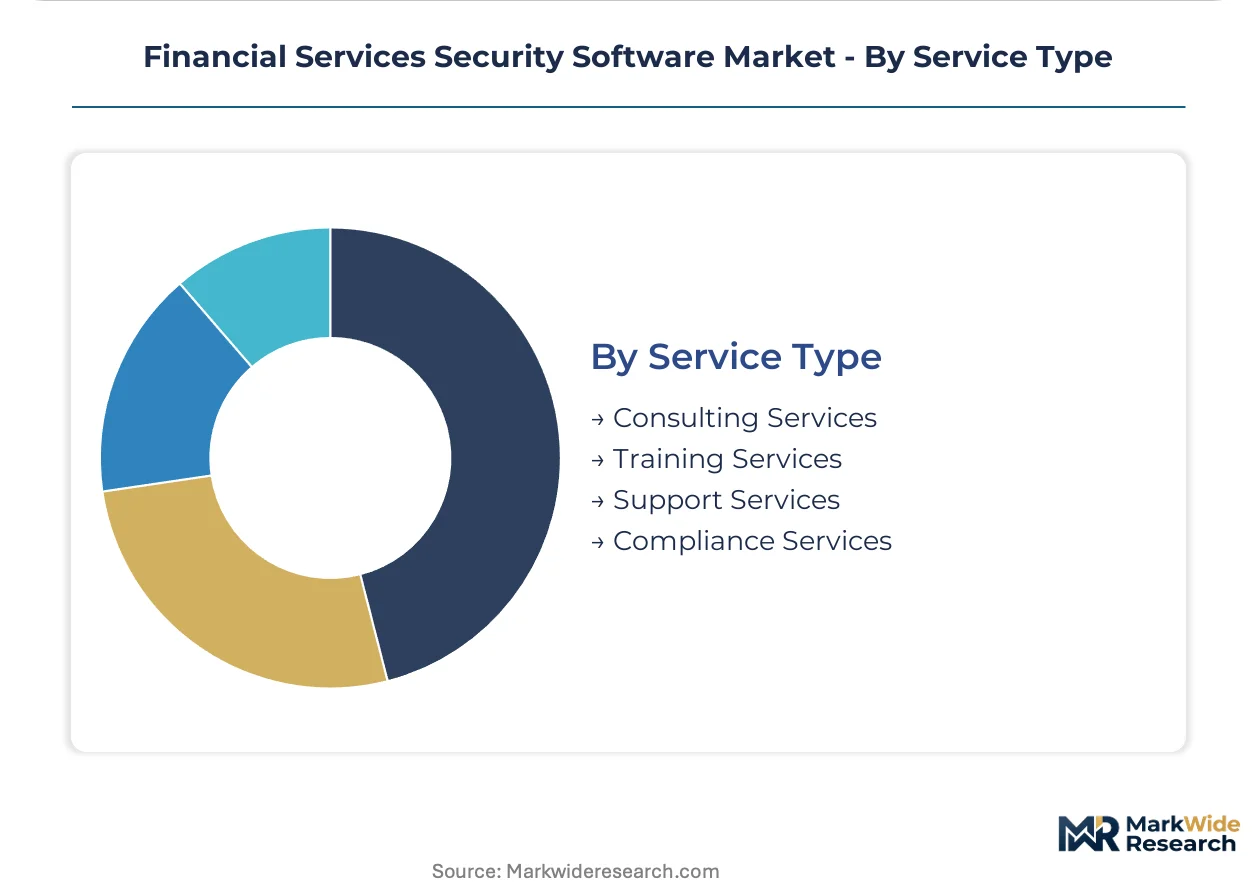
Service Type:
Supervisory complexity and internal capability gaps determine whether institutions self-deliver or externalize implementation risk.
- Compliance Services:External validation against evolving GDPR, DORA, and state-level US privacy frameworks accelerates as penalty regimes stiffen. EU-headquartered banks are restructuring vendor agreements to satisfy contractual liability caps and audit rights.
- Consulting Services:Advisory engagements for zero-trust architecture migration and post-quantum cryptography pilot programs command premium pricing.
- Support Services:Tiered response commitments with mean-time-to-detect guarantees replace break-fix arrangements.
- Training Services:CISO authority elevation in procurement decisions elevates demand for security-literate board and executive education.
Compliance Services generate the largest revenue pool today; Consulting Services are gaining share fastest as quantum-resistant and AI Act readiness deadlines approach.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory-arbitrage dynamics are redistributing security software procurement toward jurisdictions with the steepest compliance cost gradients. Financial institutions in high-enforcement markets absorb premium tooling costs, while mid-tier banks in emerging centers adopt standardized cloud-native stacks to bypass legacy migration burdens.
United States
The Federal Financial Institutions Examination Council mandates minimum cyber-resilience standards that reshape vendor roadmaps. State-level privacy frameworks in California and New York impose breach penalties that accelerate cloud-native compliance tooling replacement. New York City and San Francisco anchor the largest banking security procurement clusters, with real-time payment processors driving sub-eighteen-month refresh cycles.
Germany
BaFin enforcement timelines for zero-trust architecture compel banks to dismantle perimeter-based security models. The EU Digital Operational Resilience Act imposes strict third-party risk management requirements that restructure vendor contractual liability. Frankfurt and Munich concentrate the densest banking security R&D activity, with hybrid cloud deployments dominating as institutions bridge API-incompatible legacy systems.
United Kingdom
The Financial Conduct Authority's operational resilience deadlines compress vendor selection cycles and elevate chief information security officer authority. Outcome-based contracting with penalty clauses tied to mean-time-to-detect metrics displaces perpetual license models. London anchors the highest-velocity payment processor security procurement as real-time settlement networks multiply.
Israel
Cybersecurity R&D clusters in Tel Aviv and Herzliya broaden the supply base for threat-intelligence modules purpose-built for banking infrastructure. Military technology transfer pipelines feed specialized talent into financial security engineering. Israeli vendors occupy niche positions in behavioral analytics and automated response orchestration for payment environments.
Poland
Eastern European engineering footprints sustain cost-competitive delivery of encryption and compliance tooling for Western European banks. ScienceSoft leverages Polish development centers to maintain margin discipline on implementation timelines. Warsaw and Krakow emerge as secondary hubs for GDPR-aligned compliance services and consulting engagements.
Financial Services Security Software Market Vendor Landscape
Established producers occupy the standard tier; emerging entrants pursue embedded finance and Banking-as-a-Service security orchestration. The vendor base stratifies across three maturity levels: legacy network security appliance specialists, cloud-native platform consolidators, and regional compliance service boutiques. Two dominant competitive vectors define current positioning: platform partnerships that compress vendor counts through XDR-SIEM convergence, and outcome-based contracting that transfers implementation risk to vendors through measurable risk-reduction guarantees.
Within the cloud-native platform tier, Check Point Software anchors network security specialization for payment processor environments, while ScienceSoft exemplifies cost-competitive Eastern European delivery models for encryption and compliance tooling. Israeli R&D clusters represented by 10Clouds occupy positions in threat-intelligence modules engineered for real-time banking infrastructure. These three archetypes—appliance specialists, offshore engineering platforms, and intelligence-module developers—collectively map the competitive terrain without any single player commanding integrated stack dominance.
| Leading Market Players |
|---|
| 10Clouds |
| Euvic |
| ScienceSoft |
| AvePoint |
| Intellectsoft |
| DBB Software |
| SDK.finance |
| Check Point Software |
| Relevant Software |
| Others |
Supply Flow & Price Mechanics
Vertical integration into threat-intelligence development anchors Israeli vendors' supply position while compressing third-party module costs, a pattern that simultaneously elevates their pricing power in behavioral analytics and automated response orchestration for payment processor environments.
Pricing Analysis
Distributor margins in financial services security software are collapsing as direct SaaS subscriptions displace channel-mediated perpetual licenses. Pricing stratifies across premium zero-trust platforms, standard endpoint protection suites, and economy-tier compliance automation tools. Cost compression in the economy tier is intensifying because Eastern European engineering centers are flooding GDPR-aligned compliance services into Western European markets. Payment processors exhibit the lowest price sensitivity due to outcome-based contracting with breach-containment guarantees, while mid-tier regional banks remain the most price-constrained buyers.
Supply Chain Analysis
Workforce availability in Poland, Ukraine, and Romania sustains cost-competitive delivery of encryption and compliance tooling for Western European banking clients. Engineering talent pipelines draw from military technology transfer programs in Israel and computer science faculties in Warsaw and Krakow. Single-source vulnerability concentrates in quantum-resistant cryptography algorithm development, where NIST-standardized implementations remain tethered to a handful of academic research centers. Distribution runs through fintech infrastructure providers and direct enterprise sales teams rather than traditional value-added resellers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a regulatory compounder where enforcement timelines for the EU Digital Operational Resilience Act and state-level US privacy frameworks continuously refresh procurement cycles and expand addressable spend.
For Market Incumbents: Deploy platform consolidation levers to compress vendor counts through XDR-SIEM convergence before cloud-native challengers fragment the endpoint protection layer. Incumbents must anchor positions in outcome-based contracting with mean-time-to-detect guarantees to neutralize emerging entrants' pricing aggression in the payment processor segment. Investment in zero-trust architecture certification programs defends against talent scarcity constraining deployment velocity. For New Entrants and Emerging Players: Capture embedded finance security orchestration white space by developing white-label modules for Banking-as-a-Service platforms rather than competing directly for bank procurement cycles. The most penetrable entry point lies in EU AI Act compliance automation for algorithmic credit and fraud detection systems, where enforcement timelines are crystallizing but incumbent tooling remains immature. Go-to-market execution should route through fintech infrastructure partnerships rather than direct financial institution sales. For Investors and Strategic Acquirers: Roll-up economics work for regional compliance service boutiques because supervisory divergence between GDPR, DORA, and state-level US frameworks fragments standardization and sustains premium advisory pricing. Long-term viability across the analysis window rests on identifying targets with established audit rights and contractual liability structures that satisfy EU Digital Operational Resilience Act third-party risk requirements. The signal to watch is outcome-based contracting penetration in the United Kingdom, where Financial Conduct Authority operational resilience deadlines are compressing vendor selection cycles and elevating acquisition multiples for performance-guarantee capabilities.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | XDR-SIEM convergence compresses vendor counts and forces point-solution providers toward partnership or acquisition. |
| Outcome-Based Contracting | Penalty clauses tied to mean-time-to-detect metrics displace perpetual licenses in United Kingdom procurement. |
| Quantum-Resistant Migration | Post-quantum encryption pilot programs create premium advisory revenue streams for early-mover institutions. |
| Embedded Finance Orchestration | Banking-as-a-Service platforms require white-label security modules distributed through fintech infrastructure providers. |
| EU AI Act Compliance Automation | Automated governance tooling for algorithmic decision-making addresses enforcement timeline crystallization in credit and fraud detection. |
Methodological Framework
Coverage spans the United States, United Kingdom, Germany, Israel, and Poland, with primary inputs from each jurisdiction combining interviews with chief information security officers, IT procurement officers at tier-1 banks, payment processor platform engineers, regulatory compliance consultants, and fintech infrastructure providers. Secondary validation draws from SEC filings, FFIEC examination guidelines, EBA technical standards, Financial Conduct Authority operational resilience publications, and hyperscaler security capex disclosures. Bottom-up segmentation modeling triangulates against top-down macroeconomic and regulatory scenario analysis.
Rate-of-change decomposition separates baseline replacement demand from incremental compliance-driven procurement across the projection horizon. Segmentation dimensions modeled include deployment architecture, end-user maturity tier, product type integration burden, and regional enforcement intensity. CAGRs are derived from fitted growth curves applied to disclosed vendor revenue patterns and institutional procurement cycle data. Industry-specific forecast inputs incorporate DORA implementation timelines and real-time payment network expansion trajectories.
Regulatory enforcement acceleration, quantum computing advancement timelines, and cross-border data-localization treaty negotiations are the dominant revision risks that could compress or extend the projected expansion. Forecasts reflect assumptions about supervisory consistency and technology substitution rates. Material deviation in named triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Revenue Assurance Market
Risk Management and Compliance
UK Anti Money Laundering Solutions Market
Risk Management and Compliance
Trade Surveillance Market
Risk Management and Compliance
Global Risk and Compliance Consulting Services Market
Risk Management and Compliance
Enterprise Governance, Risk, and Compliance (Egrc) Market
Risk Management and Compliance
Asia-Pacific Sustainable Finance Market
Risk Management and Compliance
NPL Management Market
Risk Management and Compliance
BFSI Security Market
Risk Management and Compliance
Europe BFSI Biometrics Market
Risk Management and Compliance
Global Compliance Management Software Market
Risk Management and Compliance
Europe Risk Management Market
Risk Management and Compliance
Global Credit Risk Rating Software Market
Risk Management and Compliance
North America Strategic Consulting Market
Risk Management and Compliance
Crypto Compliance Software Market
Risk Management and Compliance
United States Governance, Risk and Compliance Platform Market
Risk Management and Compliance
Asset Liability Management (ALM) Solution Market