
 Software Defined Perimeter (SDP) Market | 2026-2036
Software Defined Perimeter (SDP) Market Size, Share, and Industry Trends Forecast 2026-2036
Software Defined Perimeter (SDP) Market Intelligence
The capital-intensity divergence between cloud-native platforms and legacy appliance vendors is rotating competitive advantage toward software-first architectures. Palo Alto Networks leverages its integrated platform strategy to sustain engineering density across network and identity layers. Check Point Software Technologies anchors its position through deep on-premises installed bases transitioning to hybrid deployments. Fortinet competes by bundling SDP functionality within broader security fabric licensing, controlling customer switching costs.
Software Defined Perimeter denotes an access-control architecture that authenticates both user and device before establishing any network connection, typically employing single-packet authorization and mutual TLS tunnels to cloak infrastructure from unauthorized discovery. Its primary commercial purpose is to replace perimeter-centric VPNs with identity-bound micro-segmentation that minimizes lateral movement risk. Cloud-based deployment leads solution delivery as enterprises abandon hardware refresh cycles, while identity and access management captures concentrated margin pools due to integration complexity with existing directories. Secure remote access applications are maturing fastest as post-pandemic hybrid work normalizes, though secure cloud access segments are expanding rapidly with multi-cloud sprawl.
NIST zero-trust architecture guidelines, ISO 27001 certification requirements, and sector-specific mandates from HIPAA for healthcare data access are shaping enterprise procurement criteria and product roadmaps across the SDP vendor landscape. The EU AI Act and GDPR cross-border data transfer rules are additionally forcing non-European vendors to localize policy enforcement nodes for European customers. Stakeholders must monitor how sovereign data requirements fragment standardization efforts and whether identity interoperability becomes the decisive procurement filter.
Market Dynamics
The Software Defined Perimeter market is being fundamentally restructured by the collapse of implicit trust architectures as NIST zero-trust mandates force enterprises to dismantle perimeter-centric security models and rebuild around identity-bound micro-segmentation.
Growth Catalysts
- NIST SP 800-207 Framework:Federal agencies and contractors must implement zero-trust architecture by specific deadlines, creating mandatory procurement pipelines for SDP solutions across defense and civilian sectors.
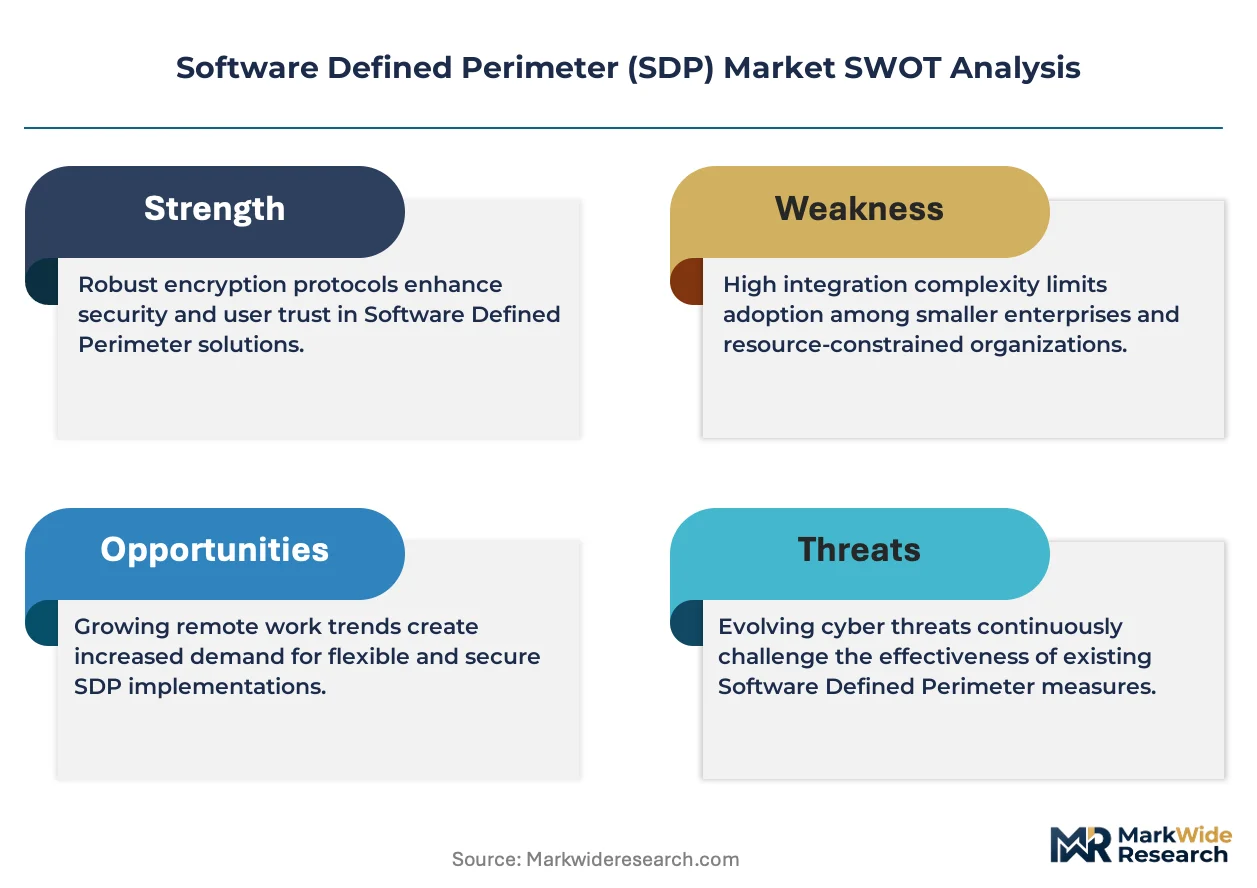
- Hybrid Workforce Normalization:Financial services and healthcare organizations require secure remote access that replaces VPN vulnerabilities with device-trusted tunnels for distributed employees.
- Multi-Cloud Sprawl:Enterprises operating across AWS, Azure, and Google Cloud environments demand unified policy enforcement that SDP architectures deliver through cloud-native control planes.
Market Restraints
- Identity Integration Complexity:Deep directory service integration with legacy Active Directory and modern cloud identity providers requires specialized engineering resources that elongate deployment timelines.
- Skills Concentration:Zero-trust architecture expertise clusters in technology hubs including San Francisco, Tel Aviv, and Bangalore, creating talent access disparities for enterprises in secondary markets.
- Certificate Management Overhead:Mutual TLS and device certificate lifecycle management impose operational burdens that smaller IT organizations struggle to operationalize without managed service support.
Strategic Opportunities
- Operational Technology Convergence:Manufacturing and energy sectors are extending SDP principles to industrial control systems, creating demand for protocols that bridge IT and OT network segmentation.
- Sovereign Cloud Requirements:Germany, France, and Japan are mandating data localization that favors SDP deployments with in-country policy enforcement nodes and regional certificate authorities.
- AI-Driven Policy Orchestration:Machine learning integration with SDP controllers enables dynamic risk scoring that adjusts access permissions based on behavioral anomalies and threat intelligence feeds.
Industry Challenges
- Legacy VPN Displacement Friction:Enterprises with sunk costs in hardware VPN concentrators face internal resistance to SDP migration despite security advantages, requiring phased coexistence strategies.
- Cross-Domain Interoperability:Fragmented standards between identity providers, endpoint detection vendors, and SDP controllers force custom integration work that delays production deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Software Defined Perimeter (SDP) Market |
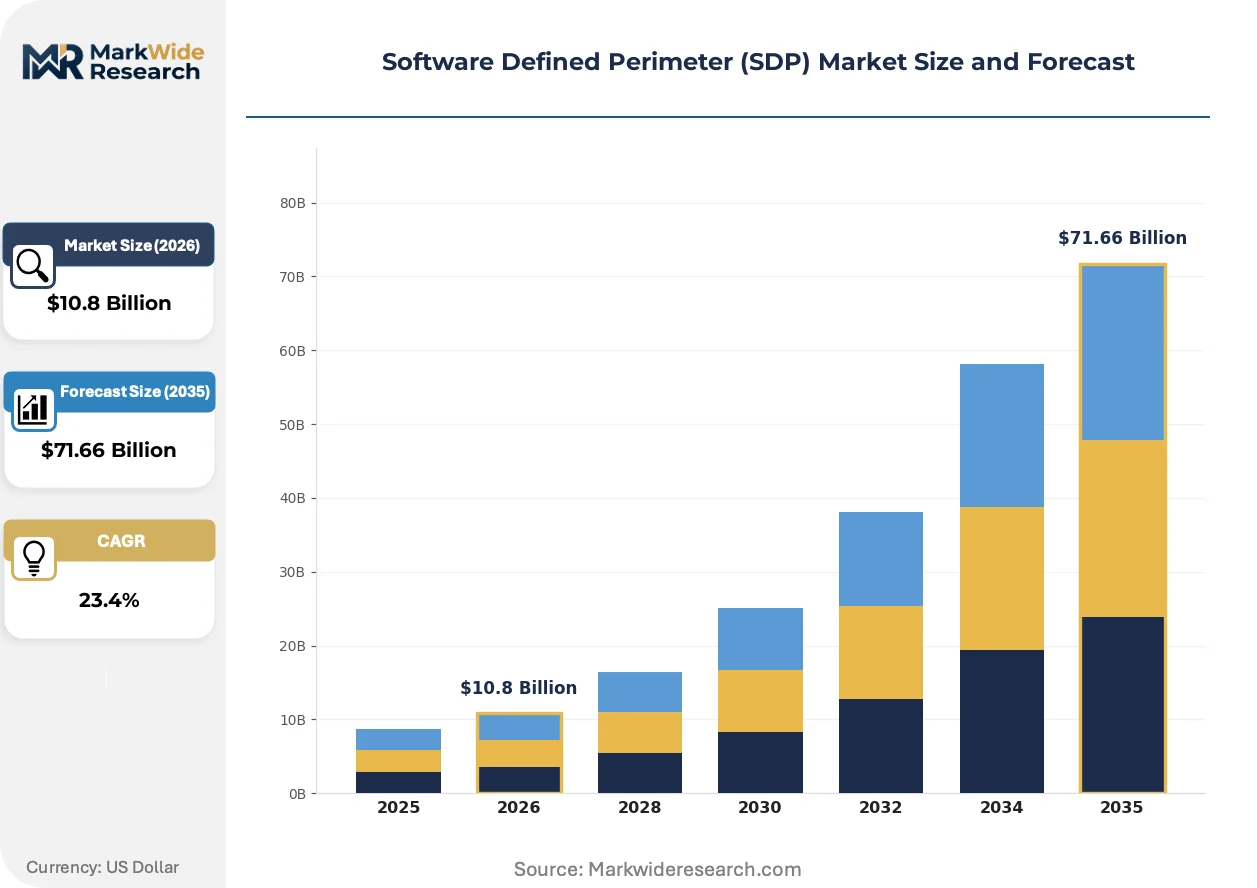
| Market Size in 2026 | $10.8 Billion |
| Market Size in 2035 | $71.66 Billion |
| CAGR (2026 – 2036) | 23.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Hosted Private Cloud Solution/Offering: Identity & Access Management, Network Security, Endpoint Security, Data Loss Prevention, Threat Intelligence Application: Secure Remote Access, Secure Cloud Access, Data Center Security, Application Layer Security, IoT Security End User Industry: BFSI, IT & Telecom, Government & Defense, Manufacturing, Education |
| Companies Covered | Zscaler, Check Point Software Technologies, Palo Alto Networks, Okta, Verizon, Fortinet, Perimeter 81, Appgate, Cisco Systems, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Software Defined Perimeter (SDP) Market Strategic Shifts & Innovations
Security architecture is pivoting from network-location trust to continuous identity verification, with three converging developments reshaping how enterprises design access control and segment critical assets.
Single-packet authorization is fragmenting traditional port-scanning reconnaissance by rendering infrastructure invisible until cryptographic authentication succeeds. Healthcare providers and financial institutions are deploying SPA gateways at scale to eliminate attack surface discovery. This cloaking capability is compressing the advantage window for threat actors who previously relied on network mapping to plan lateral movement.
The EU AI Act and GDPR Article 44 cross-border transfer restrictions are compelling non-European vendors to deploy regional policy enforcement nodes within European Economic Area boundaries. Vendors must now architect federated control planes that keep authentication logs and identity metadata within jurisdictional boundaries. Healthcare and financial services verticals in Germany and France are prioritizing SDP solutions with certified EU data residency.
Security procurement is consolidating around platform licensing that bundles SDP with adjacent controls including cloud access security brokers and zero-trust network access. Enterprise buyers are rejecting point solutions in favor of integrated fabrics that reduce vendor management overhead. This bundling preference is most pronounced among Fortune 500 organizations in the United States undergoing comprehensive zero-trust transformations.
Software Defined Perimeter (SDP) Market Segmentation
SDP architectures fragment across deployment models, solution stacks, use cases, and vertical requirements. Understanding where margin pools concentrate and how buyer priorities diverge across these dimensions determines vendor positioning and partnership strategy.
Deployment:
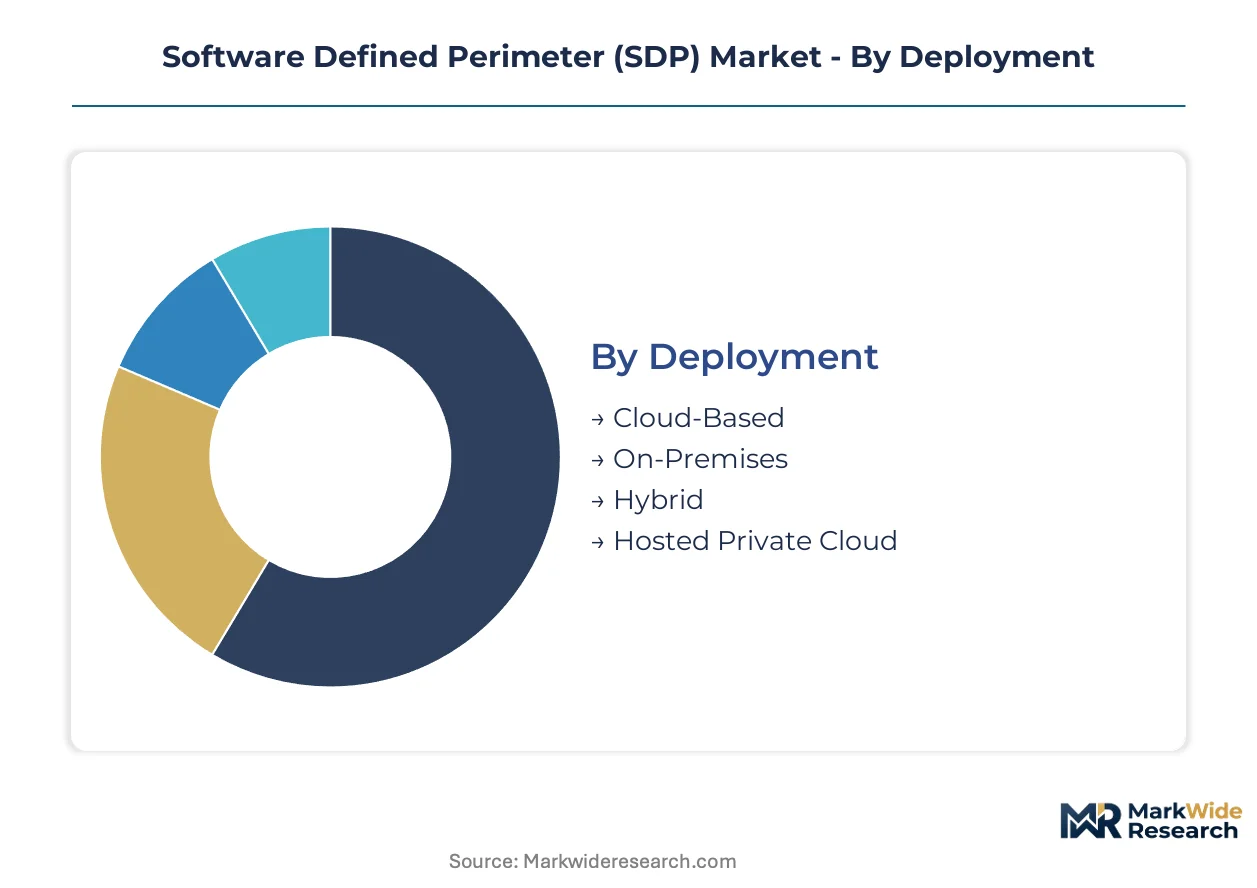
Margin pools concentrate in cloud-native delivery where operational efficiency scales with subscriber growth and infrastructure refresh cycles vanish.
- Cloud-Based:Multi-tenant control planes with elastic capacity scaling eliminate hardware procurement delays. Financial services firms in the United States and Germany are standardizing on cloud-native SDP to satisfy sovereign data requirements while avoiding capital expenditure.
- On-Premises:Dedicated appliance deployments retain traction where air-gapped networks or classified workloads prohibit external connectivity. Government and defense contractors maintain this preference despite higher total cost of ownership.
- Hybrid:Split policy enforcement across cloud and on-premises controllers accommodates phased migration from legacy VPN infrastructure. Manufacturing enterprises favor this model for OT/IT convergence scenarios.
- Hosted Private Cloud:Single-tenant cloud instances with dedicated infrastructure address data residency mandates without full operational burden. Japanese financial institutions are deploying this model to satisfy METI guidance on financial data localization.
The dominant share belongs to Cloud-Based, while Hybrid is closing the gap fastest as enterprises seek compromise between agility and control.
Solution/Offering:
Cost tier stratification separates integrated platform licensing from modular point solutions, with bundled offerings commanding premium pricing through reduced integration overhead.
- Identity & Access Management:Directory integration, certificate lifecycle management, and continuous authentication form the technical core of SDP architecture. Healthcare organizations implementing HIPAA-compliant access controls drive concentrated demand here.
- Network Security:Micro-segmentation engines and software-defined gateways enforce east-west traffic policies within virtualized infrastructure. This capability anchors hybrid cloud security strategies for multi-cloud enterprises.
- Endpoint Security:Device posture verification and mutual TLS certificate provisioning extend trust boundaries to distributed endpoints. Demand concentrates in financial services with BYOD workforce policies.
- Data Loss Prevention:Content inspection and exfiltration controls layered atop SDP tunnels address regulatory data handling requirements. German manufacturers deploy this combination to satisfy GDPR Article 32 technical measures.
- Threat Intelligence:Real-time feed integration with SDP controllers enables dynamic access revocation based on indicator-of-compromise matches. This segment expands as security operations centers consolidate tool stacks.
Identity & Access Management captures the largest revenue share, though Threat Intelligence is gaining share fastest through AI-driven policy automation.
Application:
Volume concentration tracks workforce distribution patterns, with remote access deployments scaling linearly against employee headcount while cloud access correlates with infrastructure sprawl.
- Secure Remote Access:Zero-trust network access replaces VPN concentrators with identity-bound per-session tunnels. Post-pandemic hybrid work normalization in IT & Telecom sectors sustains deployment velocity.
- Secure Cloud Access:Unified policy enforcement across AWS, Azure, and Google Cloud environments eliminates cloud-native security tool fragmentation. Multi-cloud enterprises in the United States prioritize this application for operational simplification.
- Data Center Security:East-west segmentation within on-premises virtualization stacks contains lateral movement after perimeter breach. Legacy data center operators maintain this focus during extended migration timelines.
- Application Layer Security:Granular access controls at the API and workload level protect microservices architectures. Containerized application deployments in technology hubs drive specialized demand.
- IoT Security:Device-identity verification and protocol-constrained tunneling extend SDP principles to operational technology networks. Energy sector deployments in Japan are pioneering this convergence.
Secure Remote Access maintains volume leadership, while Secure Cloud Access shows the steepest expansion trajectory as multi-cloud adoption accelerates.
End User Industry:
Customer type determines procurement complexity, with regulated verticals demanding certified compliance documentation and extended vendor due diligence cycles.
- BFSI:Bank, insurance, and capital markets firms require transaction-grade availability with regulatory audit trails. NIST zero-trust mandates for federal financial institutions create mandatory procurement pipelines.
- IT & Telecom:Technology-native organizations with distributed engineering workforces prioritize seamless user experience and broad device support. This segment tolerates higher architectural complexity for integration flexibility.
- Government & Defense:Classified and controlled unclassified information handling demands FIPS-validated cryptography and supply chain attestation. FedRAMP authorization requirements filter vendor eligibility.
- Manufacturing:Converged IT/OT environments with legacy industrial protocols require SDP adaptations for non-IP traffic. German automotive suppliers are deploying these specialized configurations.
- Education:Diverse device populations and limited security staffing drive preference for managed service delivery models. K-12 and university systems in the United States are consolidating around platform bundles.
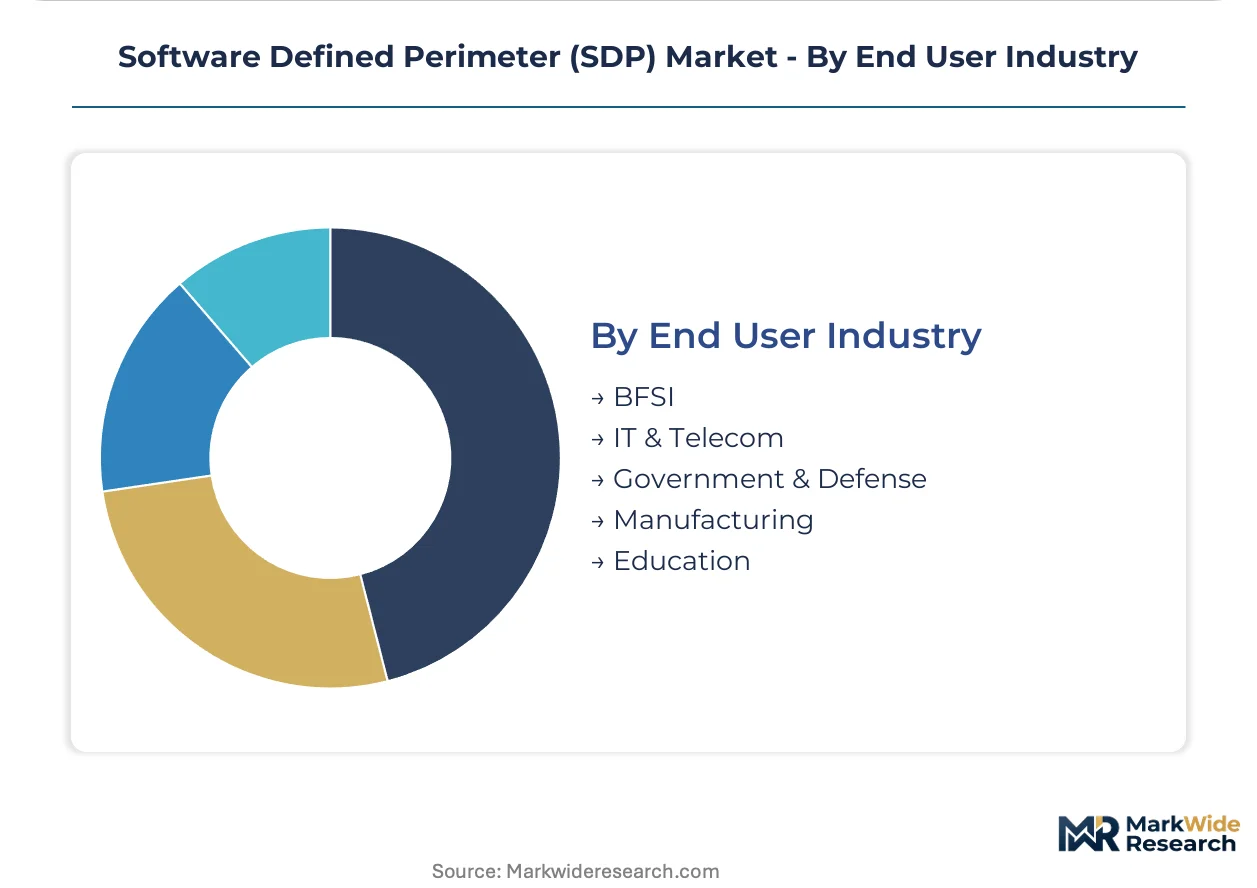
BFSI commands the dominant procurement value, while Manufacturing is climbing the fastest as industrial digitization mandates converge with security imperatives.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics in cybersecurity services favor net-importing economies with stringent data localization mandates. Sovereign cloud requirements and zero-trust procurement pipelines are redistributing SDP deployment gravity toward specific national markets with active regulatory enforcement.
United States
Federal agencies and defense contractors drive mandatory procurement volumes through NIST SP 800-207 implementation deadlines. The Cybersecurity and Infrastructure Security Agency coordinates zero-trust architecture rollouts across civilian departments. Technology clusters in Northern Virginia and San Francisco concentrate vendor engineering operations and enterprise pilot deployments.
Germany
Automotive suppliers and financial institutions demand EU data residency with certified policy enforcement nodes. The Federal Office for Information Security (BSI) issues technical guidelines that privilege domestic certificate authority integration. Industrial manufacturing corridors in Bavaria and Baden-Württemberg extend SDP principles to converged IT/OT environments.
Japan
METI guidance on financial data localization compels regional control plane deployment by foreign vendors. Energy sector operators pioneer IoT security extensions for operational technology networks. Tokyo and Osaka financial districts host concentrated demand for transaction-grade availability with regulatory audit trails.
United Kingdom
Post-Brexit data adequacy negotiations intensify scrutiny of cross-border authentication flows. The National Cyber Security Centre publishes zero-trust implementation profiles for critical national infrastructure. London's financial services ecosystem sustains premium-tier procurement for hybrid workforce security.
India
IT services exporters and domestic banks accelerate cloud-native SDP adoption for distributed engineering workforces. CERT-In directives on data localization shape vendor architecture decisions for policy enforcement placement. Bangalore and Hyderabad technology corridors concentrate deployment expertise and managed service delivery capacity.
Software Defined Perimeter (SDP) Market Key Industry Players
Concentration sits with integrated platform vendors that bundle SDP functionality within broader security fabrics. The vendor landscape stratifies across three tiers: cloud-native specialists with multi-tenant control planes, legacy network security vendors transitioning appliance bases to software delivery, and identity-centric providers leveraging directory integration depth. Competitive dynamics center on strategic partnerships with cloud hyperscalers and vertical integration into adjacent controls including cloud access security brokers and endpoint detection.
Within the integrated platform tier, Palo Alto Networks and Fortinet exemplify architecture strategies that embed SDP within comprehensive licensing bundles. Check Point Software Technologies anchors a distinct position through deep on-premises installed bases navigating hybrid migration timelines. Cloud-native specialists including Zscaler and Okta occupy positions defined by born-in-the-cloud delivery models and identity-provider integration density.
| Leading Market Players |
|---|
| Zscaler |
| Check Point Software Technologies |
| Palo Alto Networks |
| Okta |
| Verizon |
| Fortinet |
| Perimeter 81 |
| Appgate |
| Cisco Systems |
| Others |
Cost & Logistics Intelligence
Cloud-native control plane substitution for on-premises hardware appliances simultaneously redistributes supply geography toward hyperscaler regions and compresses pricing economics through elimination of capital refresh cycles. This shift concentrates vendor engineering operations in United States technology corridors while forcing legacy appliance manufacturers toward SaaS-tiered subscription models.
Pricing Analysis
Industrial OEM buyers anchor pricing structure around three-tier subscription licensing across premium, standard, and economy levels. Price differentiation hinges on FedRAMP authorization tier and multi-cloud integration complexity, with certified government-grade deployments commanding substantial premiums over commercial tiers. Pricing pressure stems from hyperscaler-native security bundles that commoditize baseline SDP functionality. Financial services procurement teams exhibit lowest price sensitivity due to regulatory compliance mandates, while education sector buyers prioritize economy-tier managed service delivery.
Supply Chain Analysis
Just-in-time capacity scaling through multi-tenant cloud architectures dominates inventory strategy, eliminating hardware stockpile requirements. Supply concentration centers on United States, Ireland, and Singapore hyperscaler regions for control plane hosting, with certificate authority services drawing from Germany and Japan for sovereign compliance. Raw material dependencies include cryptographic hardware security modules, mutual TLS certificate infrastructure, and identity provider federation protocols. Single-source vulnerability in cloud hyperscaler concentration presents structural risk. Distribution runs through direct enterprise sales with channel partner overlay for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
SDP vendors face substitution defense against zero-trust network access bundles from adjacent platform players that threaten to absorb standalone perimeter solutions into broader security fabrics.
For Market Incumbents: Shield installed base relationships through backward integration into identity provider ecosystems, deepening Active Directory and cloud-native directory service interlocks that elevate switching costs. Prioritize FedRAMP and BSI certification maintenance as defensive moats against unaccredited entrants. Counter hyperscaler-native bundle threats by emphasizing multi-cloud policy consistency that single-vendor stacks cannot replicate.
For New Entrants and Emerging Players: Anchor in operational technology convergence white space where manufacturing and energy sectors require IT/OT protocol bridging that incumbent software vendors underserve. Target German automotive supplier corridors with specialized industrial control system adaptations. Pursue managed service delivery models that address education sector staffing constraints through outcome-based pricing.
For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors identity-centric platform plays with deep directory integration over point-solution specialists. Long-term viability favors vendors with cloud-native architectures and sovereign data residency capabilities. Monitor NIST zero-trust implementation deadline progress as inflection indicator for federal procurement pipeline velocity.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidation of SDP with CASB and endpoint controls reduces vendor management overhead for Fortune 500 CISOs. |
| Strategic Partnership | Hyperscaler marketplace listings accelerate procurement velocity for cloud-first enterprise buyers. |
| Acquisition of Specialist Firm | OT security boutiques add industrial protocol expertise for manufacturing vertical penetration. |
| Geographic Expansion | Regional policy enforcement nodes in Germany and Japan satisfy METI and BSI data localization mandates. |
| Product Launch | AI-driven policy orchestration differentiates against rule-based competitors in threat response latency. |
Research Approach
A standing panel of CISOs, identity architects, cloud infrastructure directors, and federal procurement officers provided ongoing calibration against vendor roadmap disclosures and deployment case studies. Primary interview intelligence combined with secondary validation from SEC 10-K filings, FedRAMP authorization databases, hyperscaler security service announcements, and NIST publication archives. Bottom-up deployment sizing triangulated against top-down security software market estimates.
Consistency checks validated volume and value outputs against external benchmarks across the projection horizon. Segmentation modeling incorporated deployment model, organization size tier, vertical regulatory intensity, integration complexity, and regional adoption pattern dimensions. CAGRs derived from logistic diffusion curves fitted to technology substitution patterns. Forecast inputs included federal zero-trust mandate compliance timelines and cloud workload migration velocity indicators.
Material uncertainties — sovereign data requirement fragmentation, identity interoperability standardization failures, and hyperscaler bundle pricing aggression — sit outside the modeled envelope. Forecasts reflect assumptions regarding sustained hybrid workforce normalization and continued multi-cloud sprawl. Revision becomes warranted when federal procurement pipeline velocity deviates substantially from mandated implementation schedules.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Data Breach Notification Software Market
Security Software
Global Enterprise Data Loss Prevention Software Market
Security Software
Secure Email Gateway Market
Security Software
Europe Video Management System Market
Security Software
Global Electronic Offender Monitoring Solutions Market
Security Software
Europe User Provisioning Market
Security Software
Global Password Management Software Market
Security Software
Cybersecurity Software Market
Security Software
Security Information and Event Management (SIEM) Market
Security Software
Public Cloud Management and Security Services Market
Security Software
Global Advanced Authentication Market
Security Software
Smart Video Doorbell Market
Security Software
Disk Encryption Software Market
Security Software
Global IMSI Catcher Market
Security Software
Stalkerware Market
Security Software
Asia-Pacific Smart Doorbell Market