
 Global Data Breach Notification Software Market | 2026-2036
Global Data Breach Notification Software Market Size, Share, and Industry Trends Forecast 2026-2036
Global Data Breach Notification Software Market Foresight
Platform bundling is consolidating breach detection, notification dispatch, and regulatory filing into unified subscription tiers. TrustArc leverages its privacy management heritage to anchor enterprise accounts across North America and Europe. BigID competes through deep data discovery integration that feeds directly into notification workflows. Securiti differentiates via autonomous AI agents that map data lineage and trigger jurisdiction-specific disclosure protocols without manual intervention.
Data breach notification software automates the detection, assessment, communication, and documentation of unauthorized data access incidents, typically integrating with SIEM feeds, identity systems, and legal hold platforms to compress disclosure windows to under 72 hours. The primary commercial purpose is to eliminate regulatory penalties and reputational damage by ensuring precise, timely stakeholder communication when personal or confidential records are compromised. Cloud-based deployment leads solution distribution because elastic infrastructure supports burst notification volumes during major incidents, while compliance management modules capture the deepest margin pools due to recurring subscription structures and annual regulatory update dependencies. Automated alerts represent the fastest-growing solution type as machine learning classifiers reduce false-positive rates and accelerate incident triage.
The U.S. SEC cyber disclosure rules, EU GDPR Article 33/34 mandates, and state-level statutes such as California's CPRA collectively shape product roadmaps by forcing multi-jurisdictional rule engines and audit-trail documentation into core architectures. The FDA's evolving guidance on medical device cybersecurity and Health Canada's breach reporting requirements for health data further expand addressable demand in regulated verticals. Stakeholders must monitor whether emerging AI governance frameworks in the European Union and draft federal privacy legislation in the United States will mandate real-time automated notification as a baseline compliance requirement rather than a risk-mitigation option.
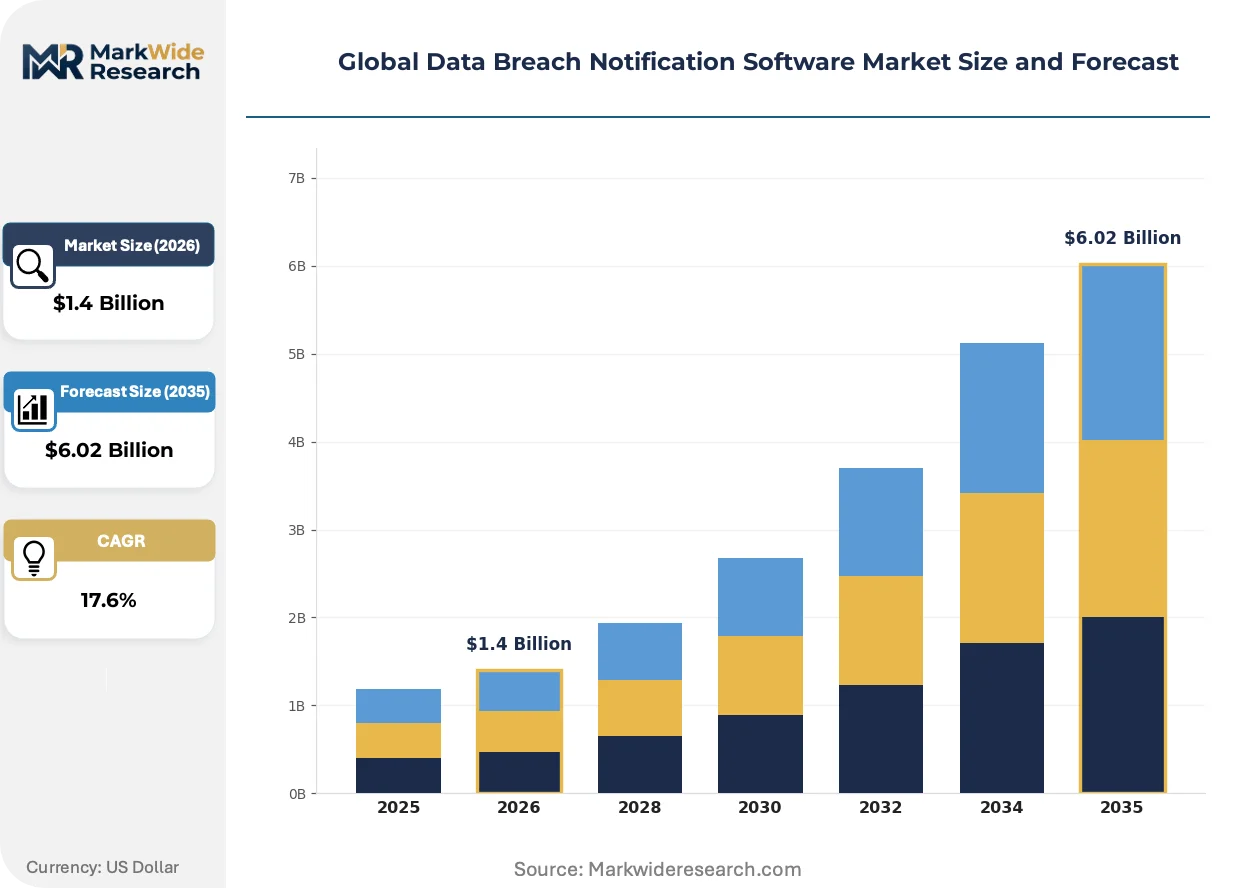
Market Dynamics
Platform consolidation is compressing vendor margins as breach detection, notification dispatch, and regulatory filing collapse into unified subscription tiers, forcing specialization at the module level to defend pricing power.
Growth Catalysts
- GDPR Article 33/34 mandates:The European Union's strict 72-hour disclosure window compels enterprises to automate incident response workflows, directly expanding procurement of real-time alert systems.
- Financial services:Banks and insurers face escalating supervisory scrutiny from the SEC and state-level statutes, driving replacement of manual compliance processes with integrated notification platforms.
- Machine learning classifiers:Advanced pattern recognition reduces false-positive rates in SIEM feeds, accelerating incident triage and compressing disclosure timelines to regulatory thresholds.
Market Restraints
- Cloud infrastructure concentration:Elastic notification burst capacity depends on hyperscaler availability zones, creating single-point vulnerability during regional outages.
- Multi-jurisdictional rule complexity:Divergent state-level privacy statutes in the United States fragment platform architectures, elevating implementation costs for cross-border deployments.
- Skilled analyst scarcity:Shortage of professionals versed in both cybersecurity operations and regulatory interpretation extends deployment timelines and inflates professional services margins.
Strategic Opportunities
- Medical device cybersecurity:FDA guidance evolution creates addressable demand for breach notification modules tailored to healthcare IoT ecosystems and patient data flows.
- AI governance frameworks:Draft EU AI Act provisions may mandate real-time automated notification as baseline compliance, expanding the addressable market beyond voluntary risk mitigation.
- Subscription bundling:Vendors can capture recurring revenue pools by embedding annual regulatory update dependencies into compliance management modules.
Industry Challenges
- Legacy SIEM integration:Heterogeneous security information architectures resist standardized API connections, forcing costly custom middleware development.
- Audit-trail documentation:Jurisdictional rule engines must generate defensible evidentiary records under GDPR, CPRA, and SEC rules simultaneously, multiplying engineering complexity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Data Breach Notification Software Market |
| Market Size in 2026 | $1.4 Billion |
| Market Size in 2035 | $6.02 Billion |
| CAGR (2026 – 2036) | 17.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Hosted Solution Type: Automated Alerts, Compliance Management, Incident Tracking, Risk Assessment Application: Financial Institutions, Government Agencies, Telecommunications, Education End User: Data Protection Officers, IT Security Teams, Legal Advisors, Privacy Consultants |
| Companies Covered | TrustArc, Keepabl, Securiti, PrivacyEngine, Seers, BigID, Enactia, BreachRx, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Data Breach Notification Software Market Shifts & Advancements
Autonomous AI agents are rewiring competitive dynamics by eliminating manual intervention in data lineage mapping and jurisdiction-specific protocol triggering, compressing the traditional services-heavy deployment model.
Autonomous AI agents perform continuous data lineage mapping across distributed cloud environments and trigger jurisdiction-specific disclosure protocols without human triage. Large enterprises in Germany and the United States are piloting these systems for 24/7 incident response coverage. This capability is expanding into mid-market accounts previously priced out of automated compliance.
The EU AI Act's risk-based classification system is mandating embedded governance documentation for high-risk AI systems handling personal data. Software vendors must now architect audit-trail modules that capture algorithmic decision pathways alongside breach incident logs. Financial institutions and healthcare providers face the steepest compliance engineering requirements.
Enterprise procurement of breach notification capabilities is consolidating through privacy management platform extensions rather than standalone purchases. Chief privacy officers increasingly source notification modules as add-ons to existing data governance contracts. This pattern concentrates most acutely in North American and German markets where privacy program maturity supports integrated vendor relationships.
Global Data Breach Notification Software Market Segmentation
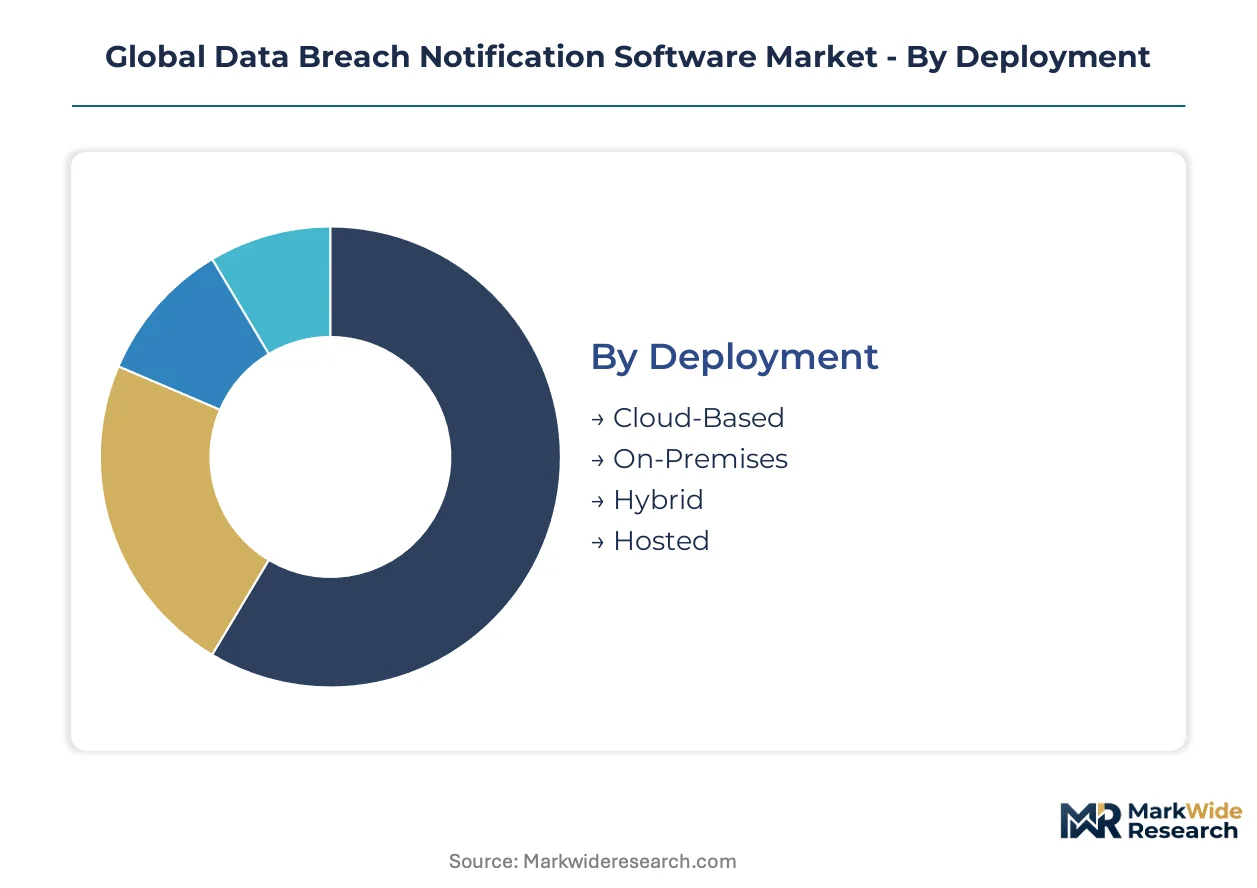
Deployment architecture determines burst capacity during mass-casualty breaches, while solution type governs whether procurement centers on reactive notification or preventive compliance automation. Application verticals impose divergent regulatory timelines that reshape feature prioritization across vendor roadmaps.
Deployment:
Elastic infrastructure requirements dominate buyer evaluation as notification volumes spike unpredictably during major incidents.
- Cloud-Based:Hyperscaler-backed elasticity supports burst notification volumes exceeding 10 million messages within regulatory windows. Financial institutions in Germany and the United States anchor procurement here due to GDPR Article 33 and SEC cyber disclosure mandates compressing response timelines.
- On-Premises:Air-gapped architectures serve defense contractors and classified government facilities where data sovereignty overrides operational convenience. Sovereign cloud requirements in France and classified handling protocols in the United States sustain this segment despite higher capital intensity.
- Hybrid:Sensitive data processing remains on-premises while notification dispatch leverages cloud scale.
- Hosted:Managed service providers operate dedicated tenant environments for mid-market accounts lacking internal security operations centers.
Volume sits with Cloud-Based deployment; growth tilts toward Hybrid configurations as data residency rules fragment across jurisdictions.
Solution Type:
Procurement patterns split between organizations seeking point solutions for disclosure automation and those embedding notification within broader privacy management platforms.
- Automated Alerts:Machine learning classifiers integrated with SIEM feeds reduce false-positive rates and accelerate incident triage. Banks and insurers across the United States and Germany are replacing manual escalation workflows with real-time stakeholder notification systems.
- Compliance Management:Subscription modules bundle annual regulatory updates with audit-trail documentation for GDPR, CPRA, and SEC rules simultaneously. Healthcare providers face the steepest engineering requirements as FDA guidance on medical device cybersecurity evolves.
- Incident Tracking:Forensic timeline reconstruction supports legal hold requirements and regulatory examination.
- Risk Assessment:Pre-breach vulnerability scoring prioritizes notification resource allocation.
Compliance Management captures the deepest recurring revenue pools; Automated Alerts are climbing the fastest as supervisory scrutiny intensifies.
Application:
Regulatory timeline variation across verticals forces vendors to embed industry-specific rule engines rather than generic disclosure templates.
- Financial Institutions:SEC cyber disclosure rules and state-level banking statutes mandate 72-hour disclosure windows with granular materiality assessments. Supervisory scrutiny from the Federal Reserve and European Central Bank drives replacement of spreadsheet-based compliance processes.
- Government Agencies:Classified information spillage protocols and Freedom of Information Act coordination requirements create specialized procurement criteria. Federal civilian agencies in the United States and national ministries in Germany represent anchor accounts.
- Telecommunications:Customer data volume and cross-border infrastructure complexity elevate automation priorities.
- Education:FERPA compliance and limited security operations budgets favor hosted service models.
Financial Institutions concentrate procurement volume; Government Agencies show the steepest expansion trajectory as critical infrastructure designations proliferate.
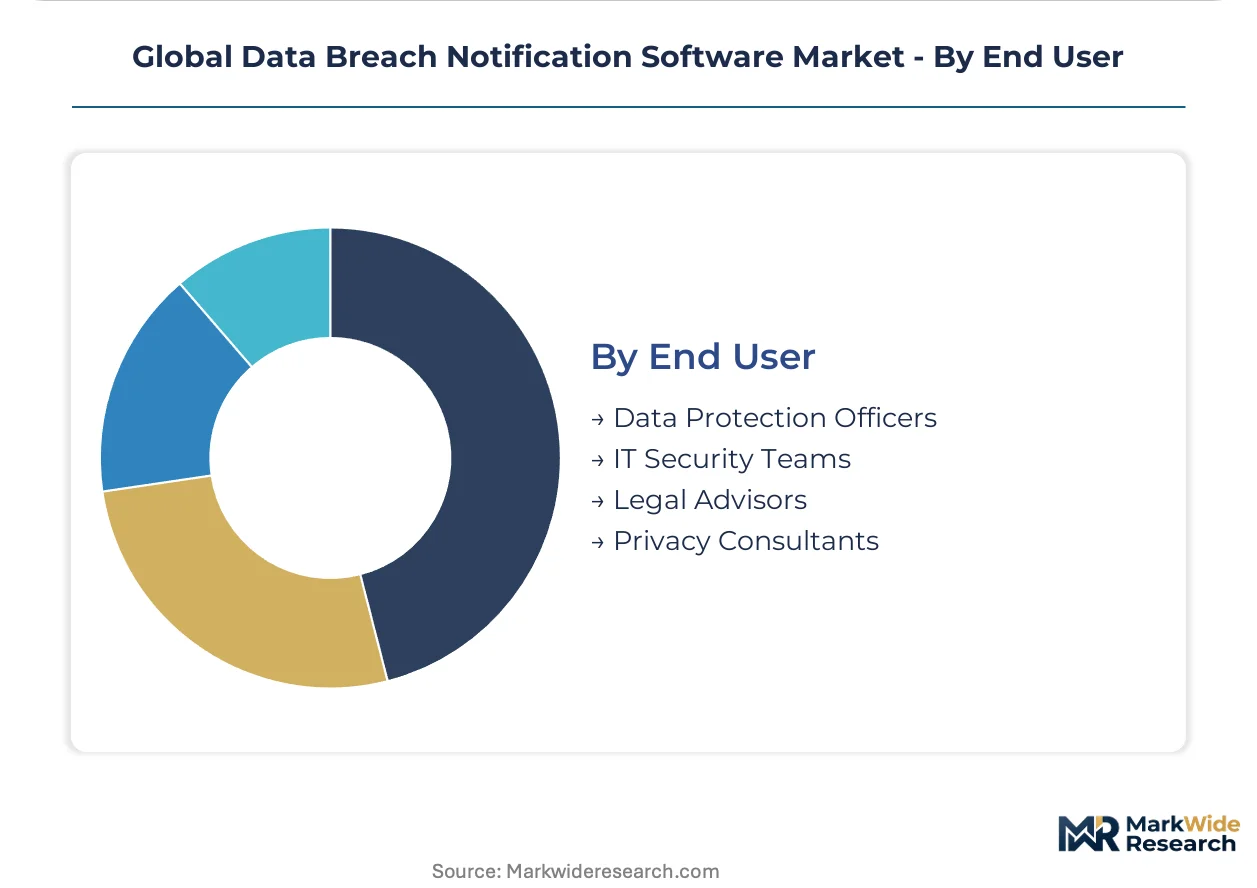
End User:
Role-based purchasing authority determines whether procurement flows through privacy program budgets or cybersecurity capital allocations.
- Data Protection Officers:GDPR-mandated roles in European Union member states drive integrated privacy platform procurement with notification modules as extensions. German DPOs particularly favor vendors embedding BSI technical guidelines into automated workflows.
- IT Security Teams:SIEM-native integration and API-first architectures dominate technical evaluation criteria. Incident response automation that compresses mean-time-to-notification anchors purchasing decisions.
- Legal Advisors:Evidentiary defensibility and regulatory examination support shape vendor selection.
- Privacy Consultants:Multi-tenant management capabilities serve advisory practices supporting distributed client portfolios.
IT Security Teams hold dominant procurement volume; Data Protection Officers are gaining share fastest as privacy program maturity deepens across European markets.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Specialized data protection zones in Frankfurt and Singapore concentrate software procurement through tax-advantaged data residency frameworks. These jurisdictions anchor compliance automation clusters serving cross-border financial services and healthcare operations.
United States
SEC cyber disclosure rules and state-level banking statutes compress incident response timelines to 72 hours. The California Privacy Rights Act mandates granular consumer notification thresholds. Financial institutions in New York and San Francisco anchor procurement volume for automated alert systems.
Germany
BSI technical guidelines and GDPR enforcement patterns create the reference market for compliance automation across the European Union. The Federal Office for Information Security mandates standardized breach documentation protocols. Frankfurt's financial services cluster drives demand for real-time disclosure workflows.
United Kingdom
Post-Brexit data protection regulations maintain GDPR-equivalent notification standards with additional UK-specific documentation requirements. The Information Commissioner's Office enforces strict materiality assessments. London's insurance and fintech sectors concentrate procurement of integrated notification platforms.
Japan
METI guidelines on cybersecurity incident reporting mandate sector-specific disclosure timelines for critical infrastructure operators. The Personal Information Protection Commission enforces cross-border data transfer notification rules. Tokyo's financial district and Osaka's manufacturing hubs pilot autonomous AI-driven response systems.
India
Draft Digital Personal Data Protection Bill provisions propose 72-hour breach notification windows with sector-specific variations. RBI cybersecurity frameworks for banks and NBFCs drive early procurement. Bengaluru's technology services cluster and Mumbai's financial district anchor domestic demand for cloud-based deployment.
Global Data Breach Notification Software Market Competitive Landscape
Diversified conglomerates compete with focused pure-play specialists across tiered market positions. Platform consolidation compresses vendor margins as breach detection, notification dispatch, and regulatory filing collapse into unified subscription tiers. Three strategic archetypes dominate: privacy heritage platforms extending into notification automation, data discovery specialists feeding lineage intelligence into disclosure workflows, and autonomous AI agents eliminating manual intervention. Dominant competitive moves include portfolio diversification through module bundling and geographic expansion via jurisdictional rule engine localization.
Within the privacy heritage archetype, TrustArc leverages its North American and European enterprise account base to anchor integrated platform procurement. Data discovery specialists BigID and Securiti exemplify the AI-native tier, occupying positions where autonomous agents map data lineage and trigger jurisdiction-specific protocols without human triage. These three entities represent the dominant architectural approaches reshaping competitive positioning as mid-market accounts gain access to previously enterprise-exclusive automation capabilities.
| Leading Market Players |
|---|
| TrustArc |
| Keepabl |
| Securiti |
| PrivacyEngine |
| Seers |
| BigID |
| Enactia |
| BreachRx |
| Palo Alto Networks |
| Others |
Supply & Pricing Matrix
GDPR Article 33's 72-hour disclosure mandate forces hyperscaler-backed elasticity into procurement specifications, compelling vendors to absorb burst-capacity infrastructure costs into subscription pricing rather than pass through usage spikes. This demand-side compression collapses margin buffers for providers lacking established cloud partnerships.
Pricing Analysis
Short lead-time deployment premiums dominate enterprise procurement as regulatory windows compress incident response timelines. Three-tier pricing structure across premium, standard, and economy levels segments by integration complexity and jurisdictional rule engine depth. Price differentiation hinges on SIEM-native API availability and automated audit-trail generation. Cost compression in mid-market tiers intensifies because platform consolidation forces module-level specialization. Healthcare providers and financial institutions show least price sensitivity due to penalty avoidance calculus; education and hosted service segments exhibit highest elasticity.
Supply Chain Analysis
France's sovereign cloud requirements and India's data localization mandates reshape sourcing toward domestic hyperscaler partnerships. Software development concentrates in the United States, Germany, and India. Cloud infrastructure draws from hyperscaler availability zones; AI/ML classifiers rest on proprietary training pipelines; regulatory content feeds from jurisdiction-specific legal databases. Single-source vulnerability concentrates in hyperscaler regional outages. Distribution runs through direct enterprise sales with channel partners penetrating mid-market accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Autonomous AI engineering talent scarcity props pricing power for vendors capable of self-mapped data lineage, constraining supply expansion despite demand acceleration.
For Market Incumbents: Acquire specialized jurisdictional rule engine libraries to compress multi-state compliance deployment timelines. Consolidate SIEM integration partnerships to defend against API-first challengers. Threat substitution from autonomous AI agents eliminating manual triage demands backward integration into data discovery capabilities. Capacity addition in Frankfurt and Singapore data residency zones anchors geographic pricing power. For New Entrants and Emerging Players: Enter via healthcare IoT breach notification modules where FDA guidance evolution creates specification gaps. White-space targets include mid-market education institutions with FERPA compliance needs and Japanese manufacturing hubs piloting METI-mandated automation. Go-to-market angle centers on hosted service models eliminating internal security operations center requirements. For Investors and Strategic Acquirers: Re-rating potential sits with privacy heritage platforms extending into notification automation given enterprise procurement consolidation through data governance contracts. Long-term viability favors vendors embedding annual regulatory update dependencies into recurring subscription structures. Acquisition target archetype: autonomous AI specialists with proven jurisdiction-specific protocol triggering. Signal to watch: EU AI Act final provisions mandating real-time automated notification as baseline compliance rather than voluntary risk mitigation.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unified breach detection and notification tiers compress vendor margins while capturing enterprise accounts. |
| Geographic Expansion | Jurisdictional rule engine localization in Germany and Singapore opens data residency-compliant revenue pools. |
| Acquisition of Specialist Firm | Autonomous AI agent capabilities eliminate manual triage, differentiating against services-heavy deployment models. |
| Strategic Partnership | Hyperscaler alliances secure burst notification capacity for GDPR Article 33 compliance windows. |
| Product Launch | Healthcare IoT modules address FDA medical device cybersecurity guidance and patient data flow requirements. |
Research Methodology
Document review covered SEC cyber disclosure filings, EU GDPR enforcement patterns, and BSI technical guideline updates, complemented by interviews with Chief Privacy Officers, IT Security Directors, and Data Protection Officers across financial services and healthcare verticals. Secondary validation drew from FDA guidance documents, state-level banking statute databases, and hyperscaler infrastructure capex disclosures. Bottom-up deployment modeling triangulated against top-down regulatory mandate sizing.
Market sizing outputs segmented across deployment architecture, solution type, application vertical, and end-user role dimensions throughout the forecast period. CAGRs derived from regulatory mandate velocity analysis and enterprise procurement cycle normalization. Industry-specific inputs included SIEM integration complexity scoring and jurisdictional rule engine maintenance cost curves.
Forecast precision tightens around the base case; tail outcomes carry wider variance under AI governance framework acceleration or federal US privacy legislation passage. Projections reflect assumptions of sustained GDPR enforcement intensity and SEC disclosure rule adherence. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Network Camera Market
Security Software
Asia-Pacific Encryption Software Market
Security Software
Endpoint Detection and Response Market
Security Software
Anomaly Detection Tools Market
Security Software
Network Video Recorder (NVR) Market
Security Software
Devsecops Market
Security Software
Website Monitoring Software Market
Security Software
Mass Notification System Market
Security Software
Global Security Operation Center As a Service Market
Security Software
Device-Embedded Biometric Authentication Market
Security Software
Cloud Data Loss Prevention Solution Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Ultra-Secure Smartphone Market
Security Software
BYOD Security Market
Security Software
Global Insider Threat Management ITM Software Market