
 Security Information and Event Management (SIEM) Market | 2026-2036
Security Information and Event Management (SIEM) Market Size, Share, and Industry Trends Forecast 2026-2036
Security Information and Event Management (SIEM) Market Intelligence
Managed security service provider distribution is fragmenting as hyperscale cloud vendors and boutique cybersecurity firms compete for enterprise telemetry contracts. Splunk leverages its data analytics heritage to anchor premium deployments in Fortune 500 environments. Securonix specializes in user and entity behavior analytics, differentiating its platform from commodity log management tools. IBM Security QRadar sustains broad protocol support across legacy infrastructure, occupying a defensive position in regulated industries with entrenched technology stacks.
Security Information and Event Management denotes a software architecture that aggregates log data from network hardware, endpoints, and applications into a centralized repository for real-time correlation, threat identification, and forensic investigation using rule-based and machine-driven detection engines. Cloud deployment models are capturing the fastest expansion as organizations migrate security operations centers away from capital-intensive on-premises infrastructure. Large enterprises dominate current spending, though compliance management services represent the emerging margin pool as GDPR, SEC disclosure rules, and sector-specific mandates multiply audit complexity.
The EU AI Act, NIS2 Directive, and GDPR enforcement by national data protection authorities are mandating automated incident detection and documented response workflows, directly accelerating SIEM procurement across European financial services and critical infrastructure operators. In the United States, SEC cybersecurity disclosure rules and HIPAA breach notification requirements from HHS are producing parallel compliance pressure in healthcare and publicly traded corporations. Stakeholders must monitor how regulatory fragmentation between jurisdictions shapes product roadmaps and whether unified platforms can satisfy divergent evidentiary standards without costly regional customization.
Market Dynamics
Cloud-native SIEM architectures are compressing deployment timelines from quarters to weeks, forcing incumbent vendors to re-platform or cede enterprise renewals to software-as-a-service specialists.
Growth Catalysts
- NIS2 Directive:European critical infrastructure operators must deploy automated threat detection by October 2024, mandating SIEM procurement across energy, transport, and digital services sectors.
- Financial audit intensity:Basel Committee operational resilience guidelines are compelling multinational banks to centralize log correlation across fragmented branch networks.
- Extended detection and response:Security operations centers are consolidating tool stacks, elevating SIEM from log repository to orchestration hub for endpoint and identity telemetry.
Market Restraints
- Data storage cost volatility:SIEM platforms ingest petabyte-scale telemetry; cloud egress and hot storage pricing unpredictability erodes budget certainty for security operations.
- Vendor concentration risk:Three hyperscale cloud providers dominate managed SIEM infrastructure, creating single-point-of-failure exposure for regulated enterprises.
- Alert fatigue saturation:Correlation engines generate false-positive rates exceeding 40% in complex environments, degrading analyst trust and platform utilization.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy facilities are extending SIEM coverage to industrial control systems, creating demand for protocol-aware parsers.
- Japan's cybersecurity framework:METI guidelines for critical infrastructure operators are accelerating localized SIEM deployment with domestic data residency requirements.
- Managed detection and response bundling:Mid-market enterprises lacking security operations center staffing are purchasing SIEM-as-a-service through channel partners rather than direct procurement.
Industry Challenges
- Threat intelligence integration complexity:Normalizing disparate indicator feeds from government agencies, commercial providers, and industry ISACs demands specialized engineering resources.
- Compliance documentation burden:GDPR Article 33 breach notification timelines require forensic-ready log chains, forcing architectural redesign of retention and immutability policies.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Information and Event Management (SIEM) Market |
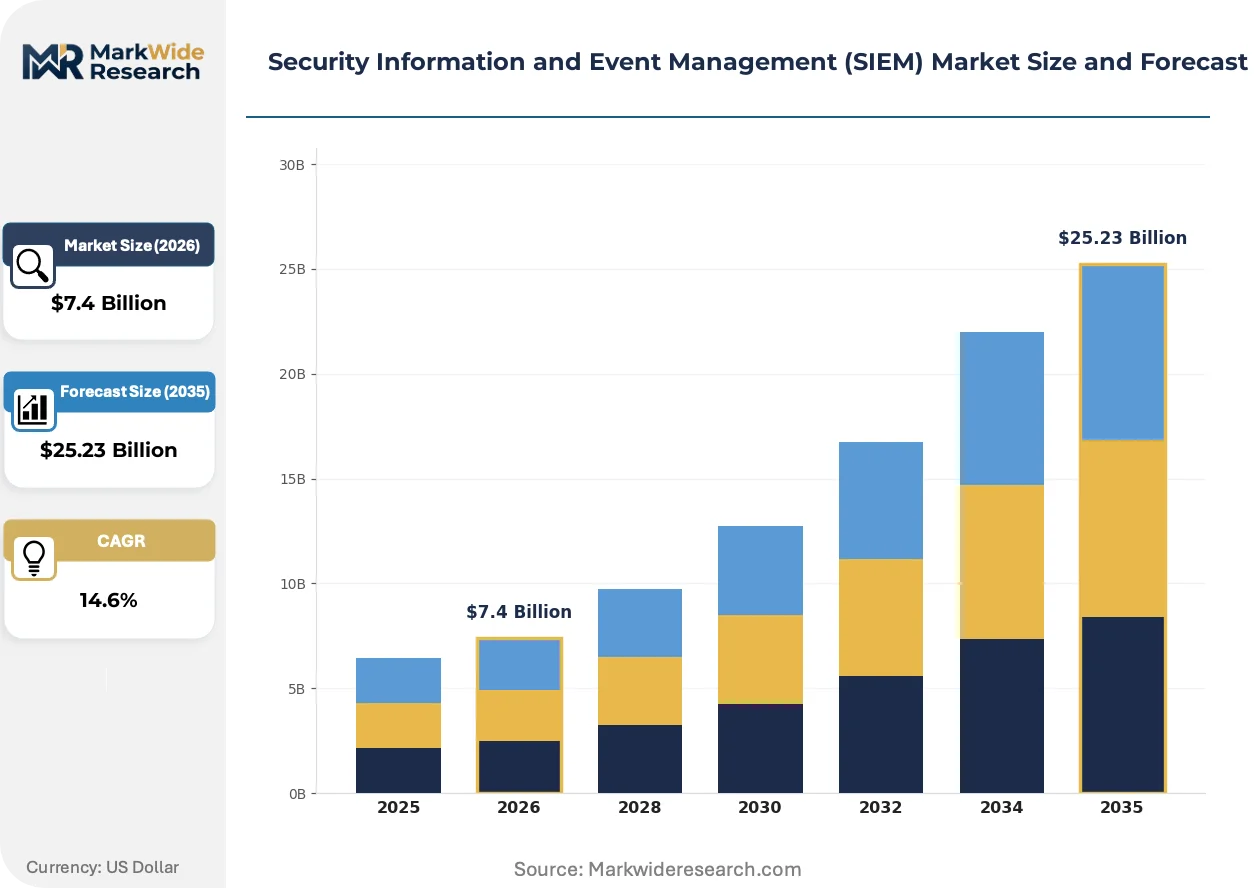
| Market Size in 2026 | $7.4 Billion |
| Market Size in 2035 | $25.23 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premises, Cloud, Hybrid, Managed Service End User: Financial Services, Government, Healthcare, Retail Organization Size: Small Enterprises, Medium Enterprises, Large Enterprises, Startups Service Type: Incident Response, Monitoring, Compliance Management, Threat Detection |
| Companies Covered | Exabeam, Securonix, Splunk, Rapid7, Sumo Logic, Microsoft Sentinel, SentinelOne, Stellar Cyber, IBM Security QRadar, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Information and Event Management (SIEM) Market Strategic Shifts & Innovations
Machine-driven detection is displacing rule-based correlation as the primary value proposition, compressing mean-time-to-detect metrics and reshaping vendor competitive positioning around analytics sophistication.
Extended Berkeley Packet Filter is virtualizing network telemetry collection at the kernel level, eliminating agent deployment overhead. Cloud-native security operations centers in technology and financial services are adopting this instrumentation for sub-millisecond flow analysis. The approach is virtualizing traffic visibility economics, collapsing the cost barrier that previously restricted full packet capture to the largest enterprises.
The EU AI Act's risk classification framework is mandating algorithmic transparency for automated security decision systems. SIEM vendors must document detection logic and human oversight mechanisms for high-risk deployments. European financial institutions are responding by demanding explainable machine learning modules and audit trails for model retraining events.
Security operations staffing constraints are compressing buyer tolerance for complex on-premises deployments. Mid-market enterprises are delegating platform management to managed security service providers, unbundling software procurement from operational execution. This pattern is most visible in Germany, where Mittelstand manufacturers lack dedicated security operations personnel but face NIS2 compliance deadlines.
Security Information and Event Management (SIEM) Market Segmentation
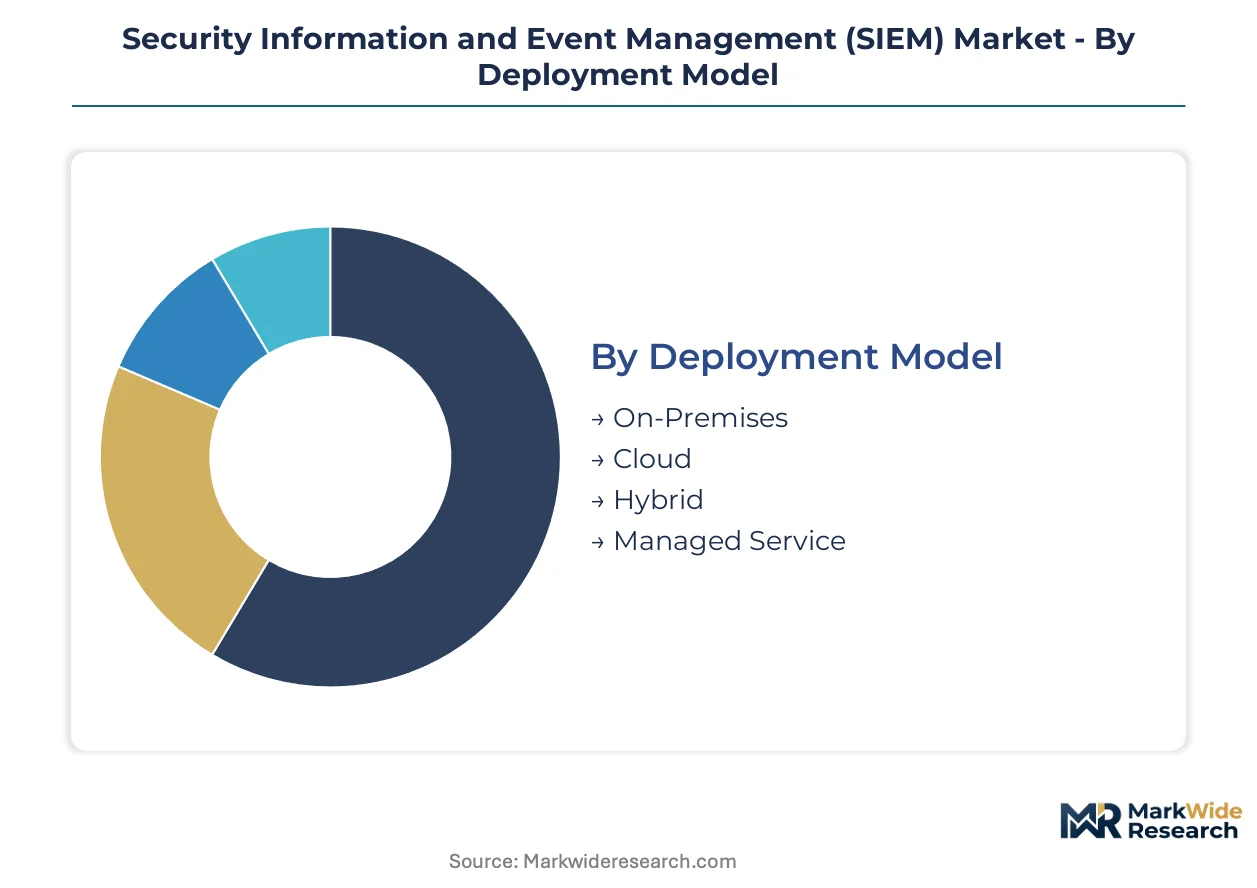
SIEM procurement patterns diverge sharply across deployment architectures and organizational maturity levels. Buyers select configurations based on existing security operations center capabilities, regulatory exposure, and capital allocation preferences for telemetry infrastructure.
Deployment Model:
Mature on-premises installations coexist with emerging cloud-native architectures as enterprises navigate data residency requirements and operational complexity trade-offs.
- On-Premises:Hardware and software deployed within customer-controlled data centers, offering complete log chain custody for forensic requirements. Financial services institutions in Germany and Japan favor this model to satisfy domestic data sovereignty mandates from BaFin and METI guidelines.
- Cloud:Fully managed SaaS platforms eliminating capital expenditure for storage and compute scaling. Technology firms in the United States are migrating security operations centers to cloud-native SIEM to compress deployment timelines from quarters to weeks.
- Hybrid:Split architectures retaining sensitive log processing on-premises while leveraging cloud analytics for non-critical telemetry. Healthcare organizations with HIPAA obligations use hybrid models to isolate patient data while accessing advanced correlation engines.
- Managed Service:Outsourced platform operation bundled with analyst staffing through security service providers. Mid-market enterprises lacking dedicated security operations personnel purchase SIEM-as-a-service to meet NIS2 compliance deadlines without internal hires.
On-Premises retains volume leadership among regulated industries; Cloud holds the steepest expansion curve.
End User:
Cost tier segmentation separates compliance-driven procurement from threat-intensity purchasing, with audit complexity determining platform sophistication requirements.
- Financial Services:Multinational banks centralize log correlation across fragmented branch networks to satisfy Basel Committee operational resilience guidelines. Institutions in the United States face parallel pressure from SEC cybersecurity disclosure rules mandating documented incident response workflows.
- Government:National and sub-national agencies deploy SIEM for classified network monitoring and inter-agency threat sharing. European critical infrastructure operators under NIS2 Directive must deploy automated threat detection across energy, transport, and digital services sectors.
- Healthcare:Hospital systems and insurers balance HIPAA breach notification timelines against constrained information security budgets. HHS enforcement actions are accelerating procurement of forensic-ready log chains for Article 33-equivalent documentation.
- Retail:Payment card industry compliance and e-commerce fraud detection drive adoption among omnichannel merchants. Point-of-sale telemetry integration creates demand for protocol-aware parsers handling high-velocity transaction streams.
Financial Services commands the premium tier; Healthcare is climbing fastest as breach notification rules tighten.
Organization Size:
Customer type segmentation reveals divergent tolerance for operational complexity, with staffing availability constraining platform selection more than budget availability.
- Large Enterprises:Fortune 500 corporations operate dedicated security operations centers with 24/7 analyst coverage. These buyers demand orchestration hub capabilities extending SIEM beyond log repository to endpoint and identity telemetry integration.
- Medium Enterprises:Organizations with 500-5,000 employees represent the emerging margin pool for compliance management services. Germany's Mittelstand manufacturers fall into this category, lacking dedicated security operations personnel but facing NIS2 compliance deadlines.
- Small Enterprises:Resource-constrained organizations prioritize managed detection and response bundling over direct platform procurement. Channel partners in Japan are capturing this demand through localized SIEM deployment with domestic data residency requirements.
- Startups:Venture-backed technology firms adopt cloud-native security operations centers from inception, avoiding technical debt from legacy infrastructure. Extended Berkeley Packet Filter instrumentation appeals to these buyers for sub-millisecond flow analysis without agent deployment overhead.
Large Enterprises anchor current spending; Startups are expanding most quickly as cloud-native architectures eliminate deployment barriers.
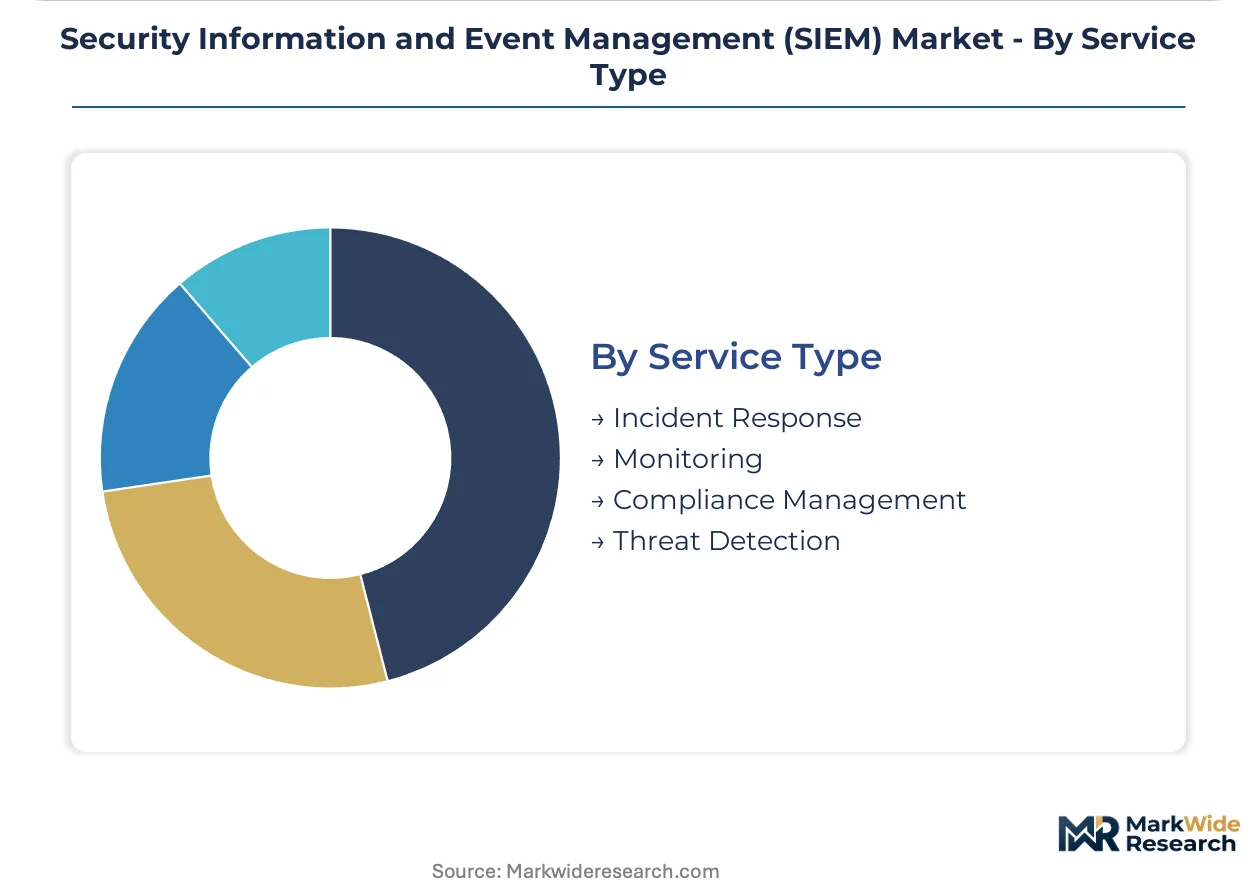
Service Type:
Application segmentation tracks the evolution from reactive incident handling toward predictive threat intelligence integration.
- Threat Detection:Machine-driven detection engines displacing rule-based correlation as the primary value proposition. European financial institutions under EU AI Act risk classification frameworks demand explainable machine learning modules with audit trails for model retraining events.
- Compliance Management:GDPR, SEC disclosure rules, and sector-specific mandates multiply audit complexity. This service type represents the emerging margin pool as documented response workflows become mandatory across jurisdictions.
- Incident Response:Forensic investigation capabilities requiring immutable log retention and chain-of-custody documentation. GDPR Article 33 breach notification timelines are forcing architectural redesign of retention policies.
- Monitoring:Continuous telemetry ingestion and alert generation forming the foundational SIEM layer. Alert fatigue saturation in complex environments degrades analyst trust, driving demand for correlation engines with reduced false-positive rates.
Threat Detection captures technology leadership; Compliance Management is gaining share fastest as regulatory fragmentation intensifies documentation burdens.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The submarine cable landing stations at Porthcurno and Highbridge anchor the United Kingdom's role in transatlantic data flows, creating concentrated demand for SIEM platforms that monitor cross-border traffic for financial services and critical infrastructure operators.
United States
Financial services institutions in Manhattan and Chicago drive premium SIEM procurement to satisfy SEC cybersecurity disclosure rules mandating documented incident response workflows. Healthcare systems across the Midwest and Southeast accelerate adoption following HHS breach notification enforcement actions. Silicon Valley technology firms deploy cloud-native security operations centers using Extended Berkeley Packet Filter instrumentation for sub-millisecond flow analysis.
Germany
BaFin's operational resilience guidelines compel Frankfurt-based banks to centralize log correlation across fragmented branch networks. The NIS2 Directive mandates automated threat detection for energy and transport operators by October 2024. Mittelstand manufacturers in Baden-Württemberg and Bavaria purchase managed SIEM services through channel partners to meet compliance deadlines without internal security operations hires.
Japan
METI cybersecurity framework guidelines for critical infrastructure operators accelerate localized SIEM deployment with domestic data residency requirements. Financial institutions in Tokyo's Marunouchi district invest in orchestration hub capabilities extending beyond log repository functions. Osaka-based manufacturers extend platform coverage to industrial control systems, creating demand for protocol-aware parsers.
United Kingdom
The Financial Conduct Authority's operational resilience rules drive adoption among London-based multinational banks with complex branch telemetry requirements. NHS Digital's data security standards compel hospital systems to implement forensic-ready log chains for breach documentation. Edinburgh and Manchester emerge as secondary hubs where mid-market enterprises procure compliance management services.
Security Information and Event Management (SIEM) Market Key Industry Players
On the supply side, the industry is consolidating around three strategic tiers as cloud-native architectures compress deployment timelines and force incumbent vendors toward re-platforming investments. Specialized user and entity behavior analytics providers occupy differentiated positions against commodity log management tools. Hyperscale cloud vendors and boutique cybersecurity firms fragment managed security service provider distribution. Dominant competitive moves include strategic partnerships for telemetry integration and portfolio diversification into extended detection and response orchestration.
Within the data analytics heritage tier, Splunk anchors premium deployments in Fortune 500 environments. Securonix occupies a specialized position in user and entity behavior analytics, differentiating from rule-based correlation engines. IBM Security QRadar exemplifies the defensive incumbent archetype, sustaining broad protocol support across legacy infrastructure in regulated industries with entrenched technology stacks. These three represent contrasting strategic postures as machine-driven detection displaces traditional correlation value propositions.
| Leading Market Players |
|---|
| Exabeam |
| Securonix |
| Splunk |
| Rapid7 |
| Sumo Logic |
| Microsoft Sentinel |
| SentinelOne |
| Stellar Cyber |
| IBM Security QRadar |
| Others |
Cost & Logistics Intelligence
Single-source hyperscale cloud dependency determines both pricing tier spreads and supply chain shape in SIEM markets, compressing margins for mid-tier vendors while concentrating procurement leverage among three dominant infrastructure providers.
Pricing Analysis
Volume-discount tiering structures stratify across enterprise, mid-market, and small-business levels, with per-terabyte ingestion rates declining logarithmically at scale. Price differentiation hinges on machine-learning sophistication and compliance certification depth, with EU AI Act audit-trail capabilities commanding substantial premiums. Cost compression in the mid-market tier intensifies as channel partners bundle managed detection services, eroding standalone software margins. Small enterprises exhibit acute price sensitivity, while Fortune 500 buyers prioritize orchestration depth over unit economics.
Supply Chain Analysis
Contract-manufacturing concentration rests with hyperscale cloud providers in the United States, Germany, and Japan, where domestic data residency mandates anchor regional infrastructure deployment. Raw material dependencies center on specialized silicon for kernel-level packet processing, enterprise-grade storage arrays, and proprietary machine-learning training datasets. Supply chain risk concentrates in single-source vulnerability for cloud egress bandwidth, where three providers control managed SIEM infrastructure. Distribution runs through managed security service providers and direct enterprise sales, with channel partners capturing mid-market bundling opportunities.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is shifting toward consolidated hyperscale procurement offices, fragmenting vendor pricing power as enterprises centralize security operations center tooling decisions under single-source cloud contracts.
For Market Incumbents: Harden platform differentiation through explainable machine-learning modules that satisfy EU AI Act documentation requirements. Anchor renewal rates by embedding orchestration hub capabilities that extend beyond log correlation into endpoint and identity telemetry. Defensive consolidation around user and entity behavior analytics preserves margin against commodity cloud-native entrants.
For New Entrants and Emerging Players: Build out protocol-aware parsers for industrial control systems in Japanese and German manufacturing corridors, where operational technology convergence creates unmet demand. Target Mittelstand manufacturers through managed SIEM-as-a-service offerings that bypass internal security operations hiring constraints. Channel-centric go-to-market positioning captures compliance-driven procurement without direct enterprise sales overhead.
For Investors and Strategic Acquirers: The NIS2 Directive reshapes the acquisition landscape by mandating automated threat detection across European critical infrastructure, elevating vendors with established energy and transport sector deployments. Long-term viability favors platforms with hybrid architecture flexibility spanning on-premises custody and cloud analytics. Watch for consolidation signals as alert-fatigue solutions demonstrating sub-40% false-positive rates emerge as differentiated acquisition targets.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, identity, and network telemetry into orchestration hubs for Fortune 500 security operations centers. |
| Geographic Expansion | Establishes domestic data residency infrastructure in Japan and Germany to satisfy METI and BaFin sovereignty mandates. |
| Strategic Partnership | Aligns with managed security service providers to capture mid-market bundling demand without direct sales investment. |
| Acquisition of Specialist Firm | Absorbs user and entity behavior analytics capabilities to differentiate from commodity log management tools. |
| Product Launch | Introduces explainable machine-learning modules with audit trails for EU AI Act high-risk deployment compliance. |
Research Approach
Operator-level perspectives from chief information security officers, security operations center directors, managed security service provider executives, and regulatory compliance officers anchored the qualitative base. Primary interview data combined with secondary validation from SEC cybersecurity disclosure filings, NIS2 Directive implementation guidance, BaFin operational resilience circulars, and METI framework documentation. Bottom-up deployment modeling and top-down market sizing triangulated volume estimates across the analysis window.
Scenario-bracketing framed the analytical approach, with segmentation dimensions spanning deployment architecture, organization size, end-user vertical, and regional regulatory cluster. CAGRs derived from telemetry ingestion growth curves, compliance mandate enforcement timelines, and cloud migration velocity indicators. Machine-learning adoption rates and managed service penetration thresholds served as industry-specific forecast inputs throughout the projection horizon.
Stress conditions across hyperscale vendor concentration, data storage cost volatility, and alert-fatigue degradation were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions regarding NIS2 implementation rigor and SEC disclosure enforcement intensity. Quarterly review of breach notification timeline compliance and cloud egress pricing trajectories is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Smartphone Security Market
Security Software
Encryption Software Market
Security Software
Certification Authority Market
Security Software
Mobile Threat Management Security Software Market
Security Software
Employee Computer Monitoring Software Market
Security Software
US Hardware Encryption Market
Security Software
Patch and Remediation Software Market
Security Software
AI in Security Market
Security Software
Global Security Orchestration Automation and Response (SOAR) Market
Security Software
Global Insider Threat Management ITM Software Market
Security Software
GDPR Software and Tools Market
Security Software
Disk Encryption Software Market
Security Software
Secure Flash Drive Market
Security Software
Global Cloud IAM Market
Security Software
Network Camera and Video Analytics Market
Security Software
Network Camera Market