
 Global Enterprise Data Loss Prevention Software Market | 2026-2036
Global Enterprise Data Loss Prevention Software Market Size, Share, and Industry Trends Forecast 2026-2036
Global Enterprise Data Loss Prevention Software Market Foresight
The gap between premium integrated suites and standalone point solutions is expanding in enterprise data loss prevention software. Microsoft Purview leverages its cloud ecosystem dominance to bundle DLP with broader security workloads, while Proofpoint Enterprise DLP anchors its position through specialized email and cloud application protection. Digital Guardian competes on endpoint-centric deployment flexibility for regulated industries.
Enterprise data loss prevention software monitors, detects, and blocks sensitive data exfiltration across network, endpoint, cloud, and storage vectors using content inspection, contextual analysis, and policy enforcement engines. Cloud DLP solutions are capturing the fastest growth as SaaS adoption accelerates, while endpoint DLP retains the deepest margin pools due to complex agent architecture and persistent device-level control requirements.
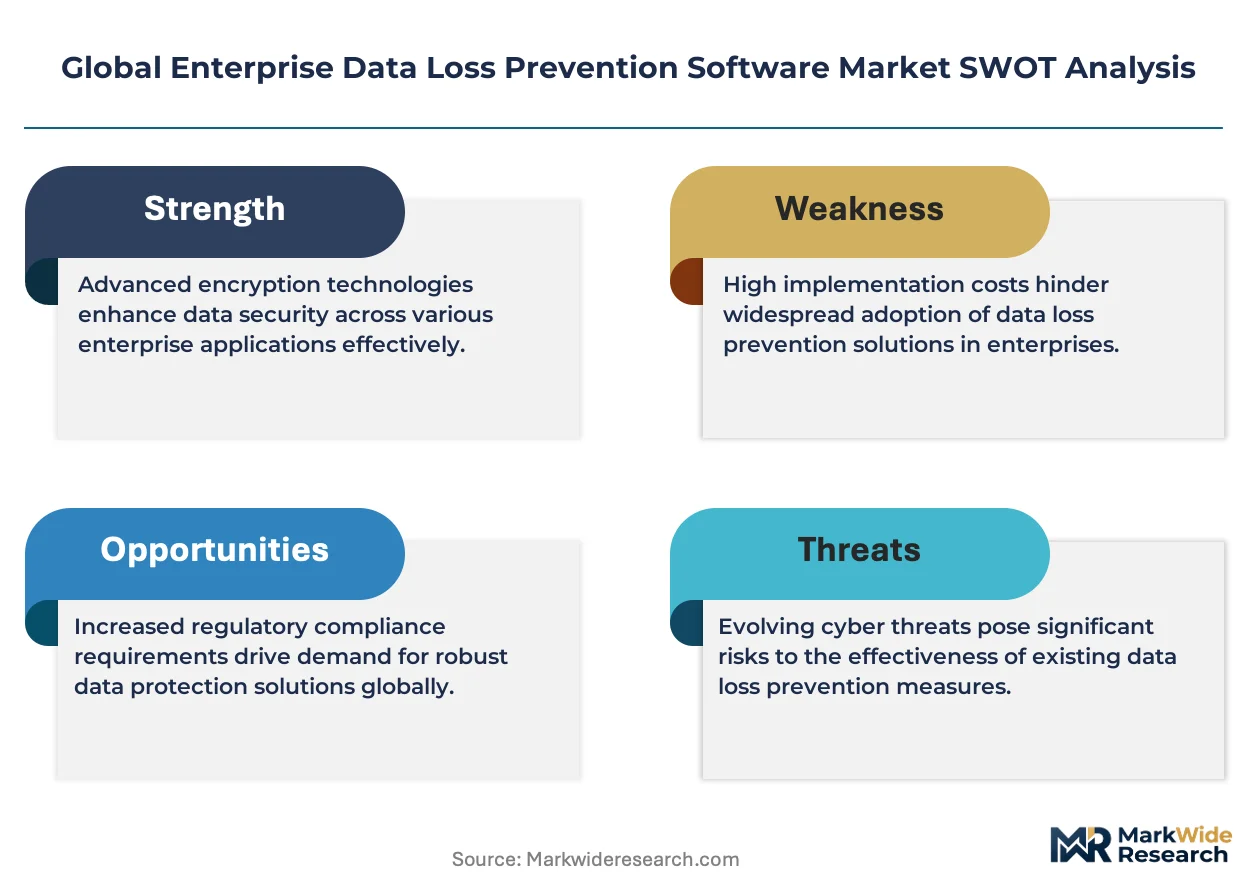
FDA, HIPAA, and SEC frameworks in the United States impose stringent data handling and breach disclosure mandates on healthcare and financial entities, directly shaping procurement specifications for audit-ready DLP platforms. The EU AI Act and GDPR add cross-border complexity for multinational deployments. Stakeholders must weigh integration depth against deployment agility when selecting between platform-native and best-of-breed architectures.
Market Dynamics
The migration from on-premises security stacks to cloud-native architectures is compressing deployment cycles and forcing vendors to re-architect agent-based inspection engines for serverless environments.
Growth Catalysts
- GDPR enforcement:European data protection authorities are imposing fines exceeding operational budgets, compelling multinational enterprises to deploy enterprise-grade DLP with automated breach notification workflows.
- Healthcare digitization:HIPAA-covered entities in the United States are replacing signature-based data classification with machine learning models that identify protected health information across unstructured clinical notes.
- Agentless inspection:API-based cloud DLP is eliminating endpoint agent friction, accelerating adoption among SaaS-heavy organizations with distributed developer teams.
Market Restraints
- Skilled analyst shortage:Organizations report 18-month average timelines to staff security operations centers capable of tuning DLP policies without excessive false-positive rates.
- Encryption blind spots:TLS 1.3 and perfect forward secrecy protocols are degrading network DLP visibility, forcing costly proxy re-architecture or endpoint agent expansion.
- Vendor consolidation risk:Cloud platform providers are bundling DLP functionality into broader security suites, compressing standalone vendor pricing power and channel access.
Strategic Opportunities
- India's data localization mandate:The Digital Personal Data Protection Act is creating demand for in-country DLP deployments among global enterprises serving Indian consumer markets.
- AI model governance:The EU AI Act's training data provenance requirements are opening adjacent markets for DLP vendors to extend into MLOps pipeline monitoring.
- Managed detection integration:MSSP channel partnerships are enabling mid-market penetration without direct field sales investment, particularly in Brazil and Mexico.
Industry Challenges
- Cross-border data routing complexity:Schrems II rulings are invalidating standard contractual clauses, forcing enterprises to maintain parallel DLP policy sets for EU-US data flows.
- Shadow SaaS proliferation:Unauthorized cloud application usage is outpacing discovery capabilities, creating persistent data exfiltration vectors outside sanctioned DLP coverage.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Enterprise Data Loss Prevention Software Market |
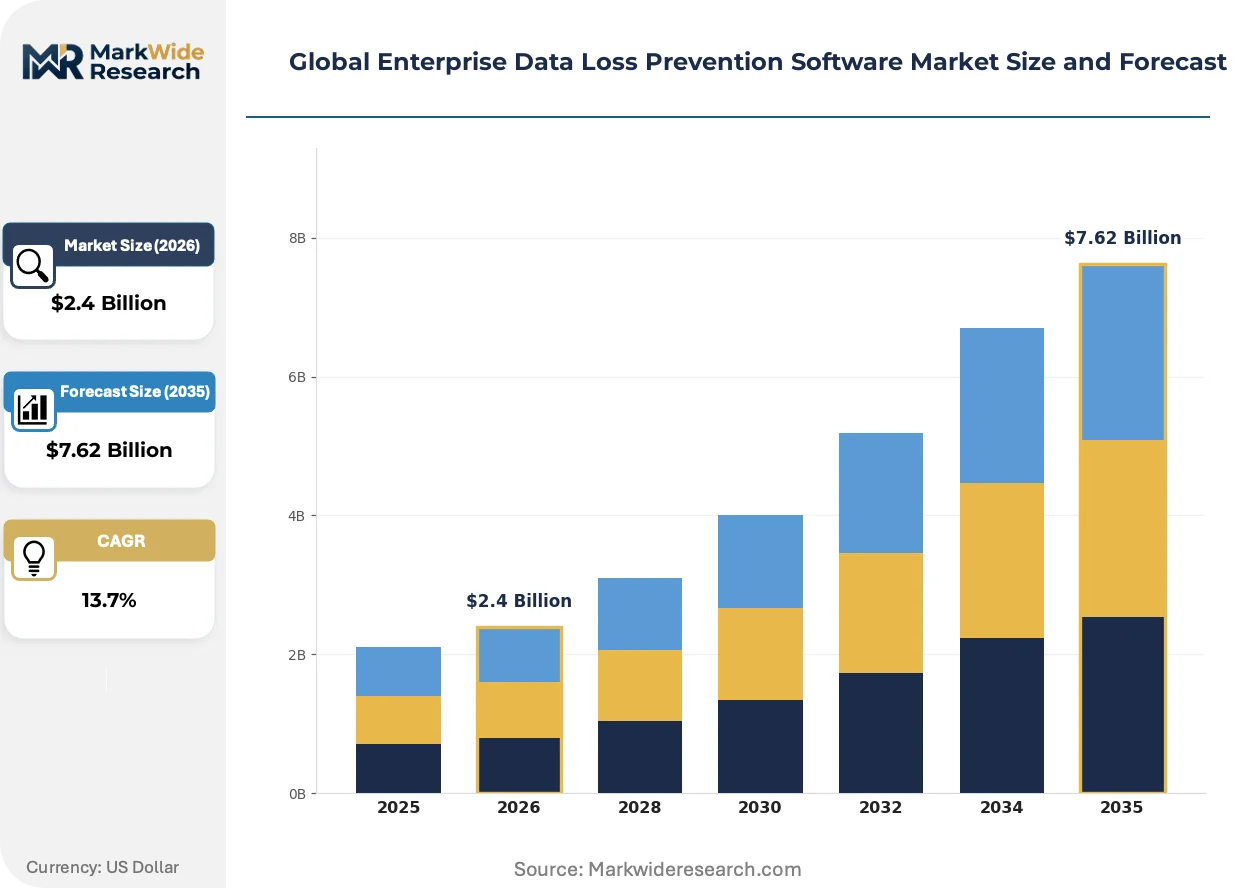
| Market Size in 2026 | $2.4 Billion |
| Market Size in 2035 | $7.62 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Virtual, Containerized Solution Type: Network DLP, Endpoint DLP, Cloud DLP, Storage DLP, Email DLP Application: Data Compliance, Insider Threat Prevention, Intellectual Property Protection, Regulatory Monitoring, Access Controls End User: Financial Institutions, Government Agencies, Telecommunications, Manufacturing Firms, Educational Institutions |
| Companies Covered | Proofpoint Enterprise DLP, Digital Guardian, Microsoft Purview, Fortra DLP, Netskope DLP, Symantec DLP, Trellix DLP, Varonis, Forcepoint DLP, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Enterprise Data Loss Prevention Software Market Shifts & Advancements
Artificial intelligence is redefining how sensitive data gets identified, shifting competitive advantage from static pattern libraries toward dynamic contextual inference engines trained on organizational communication patterns.
Natural language processing is consolidating classification accuracy for unstructured content types previously resistant to regex-based detection. Financial services procurement teams are mandating NLP-native DLP for contract and email surveillance. The technology is consolidating previously separate data discovery, classification, and protection workflows into unified pipeline architectures.
The EU AI Act's risk-based compliance tiers are mandating audit trails for high-risk automated decision systems. Enterprises deploying customer-facing algorithms must now document training data lineage and inference outputs. Healthcare and financial services verticals in Germany and France are prioritizing DLP platforms with embedded AI governance modules.
Security procurement committees are displacing siloed point solution evaluations with integrated platform assessments. CISOs are consolidating vendor relationships to reduce operational overhead and improve incident correlation. This pattern is most pronounced in United States-based Fortune 500 enterprises completing post-merger security stack rationalization programs.
Global Enterprise Data Loss Prevention Software Market Segmentation
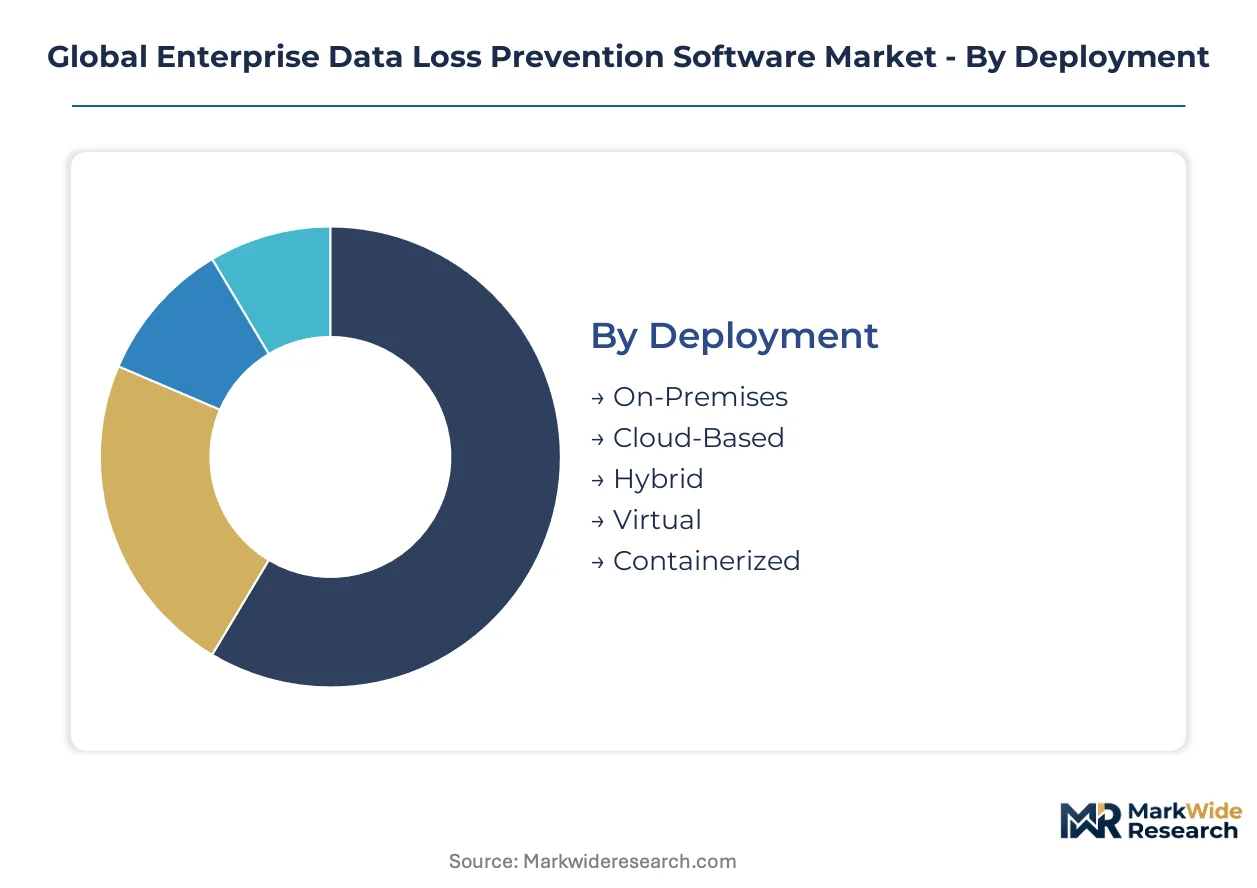
Enterprise data loss prevention software procurement hinges on architectural fit with existing security stacks. Buyers evaluate deployment models against cloud migration timelines, solution types against data exfiltration vectors, and end-user verticals against regulatory exposure.
Deployment:
Total cost of ownership and integration complexity drive deployment selection across enterprise security committees.
- On-Premises:Hardware-appliance or software-based inspection engines operating within customer data centers. Financial institutions in the United States and Germany retain this model for air-gapped environments subject to SEC and BaFin audit requirements.
- Cloud-Based:SaaS-delivered policy engines with API-native inspection of sanctioned cloud applications. Demand concentrates among distributed technology firms in California and Washington state replacing endpoint agent maintenance with agentless CASB integration.
- Hybrid:Unified policy management spanning on-premises appliances and cloud-native enforcement points. Healthcare systems in Massachusetts and Texas deploy this architecture to bridge legacy clinical networks with Epic-hosted cloud instances.
- Virtual:Software-defined DLP instances deployable across private cloud infrastructure. Telecommunications carriers in South Korea and Japan favor virtual form factors for elastic capacity scaling across subscriber data processing nodes.
- Containerized:Microservice-based inspection modules integrated into Kubernetes orchestration layers. DevOps-intensive enterprises in Singapore and the Netherlands adopt this model for CI/CD pipeline data governance.
Volume sits with Cloud-Based deployments; growth tilts toward Containerized architectures.
Solution Type:
Data exfiltration vector coverage determines solution procurement priorities for security architects.
- Network DLP:Deep packet inspection appliances monitoring egress traffic at perimeter and internal network boundaries. Manufacturing firms in Germany and automotive clusters in Stuttgart maintain network DLP for OT-IT convergence zones where endpoint agents prove infeasible.
- Endpoint DLP:Kernel-level agents enforcing data handling policies at workstations, servers, and removable media interfaces. HIPAA-covered entities across Florida and Illinois prioritize endpoint DLP for PHI protection on clinician devices with offline functionality requirements.
- Cloud DLP:API-connected inspection of SaaS application content and user activity telemetry. Technology companies in Ireland and the Netherlands expanding EU operations deploy cloud DLP to satisfy GDPR Article 32 security processing mandates.
- Storage DLP:At-rest scanning of file shares, databases, and object storage repositories. Government agencies in Australia and Canada mandate storage DLP for classified document repositories under TGA and Public Safety Canada data handling directives.
- Email DLP:Gateway and inline inspection of message content, attachments, and routing patterns. Professional services firms in London and New York deploy email DLP for client confidentiality enforcement under SRA and ABA ethical guidelines.
Revenue concentrates in Endpoint DLP; expansion accelerates fastest in Cloud DLP.
Application:
Functional use case specificity shapes RFP requirements and vendor shortlist composition.
- Data Compliance:Automated classification, retention, and disposition workflows aligned to regulatory frameworks. Pharmaceutical manufacturers in Switzerland and France implement compliance-focused DLP for EMA pharmacovigilance data lineage requirements.
- Insider Threat Prevention:Behavioral analytics correlating data access patterns with user risk profiles. Defense contractors in the United Kingdom and Australia deploy insider threat modules under Defence and Security Equipment International supply chain security protocols.
- Intellectual Property Protection:CAD file, source code, and research data exfiltration controls. Semiconductor design houses in Taiwan and Israel prioritize IP protection DLP for foundry collaboration environments.
- Regulatory Monitoring:Continuous audit trail generation and breach notification automation. Insurance carriers in Connecticut and Bermuda implement monitoring-centric DLP for NAIC and BMA cybersecurity examination readiness.
- Access Controls:Dynamic data access rights enforcement based on classification and context. Energy utilities in Texas and Alberta deploy access control DLP for NERC CIP critical cyber asset protection.
Deployment scale favors Data Compliance; steepest expansion trajectory belongs to Insider Threat Prevention.
End User:
Vertical-specific regulatory pressure and data asset sensitivity determine segment investment intensity.
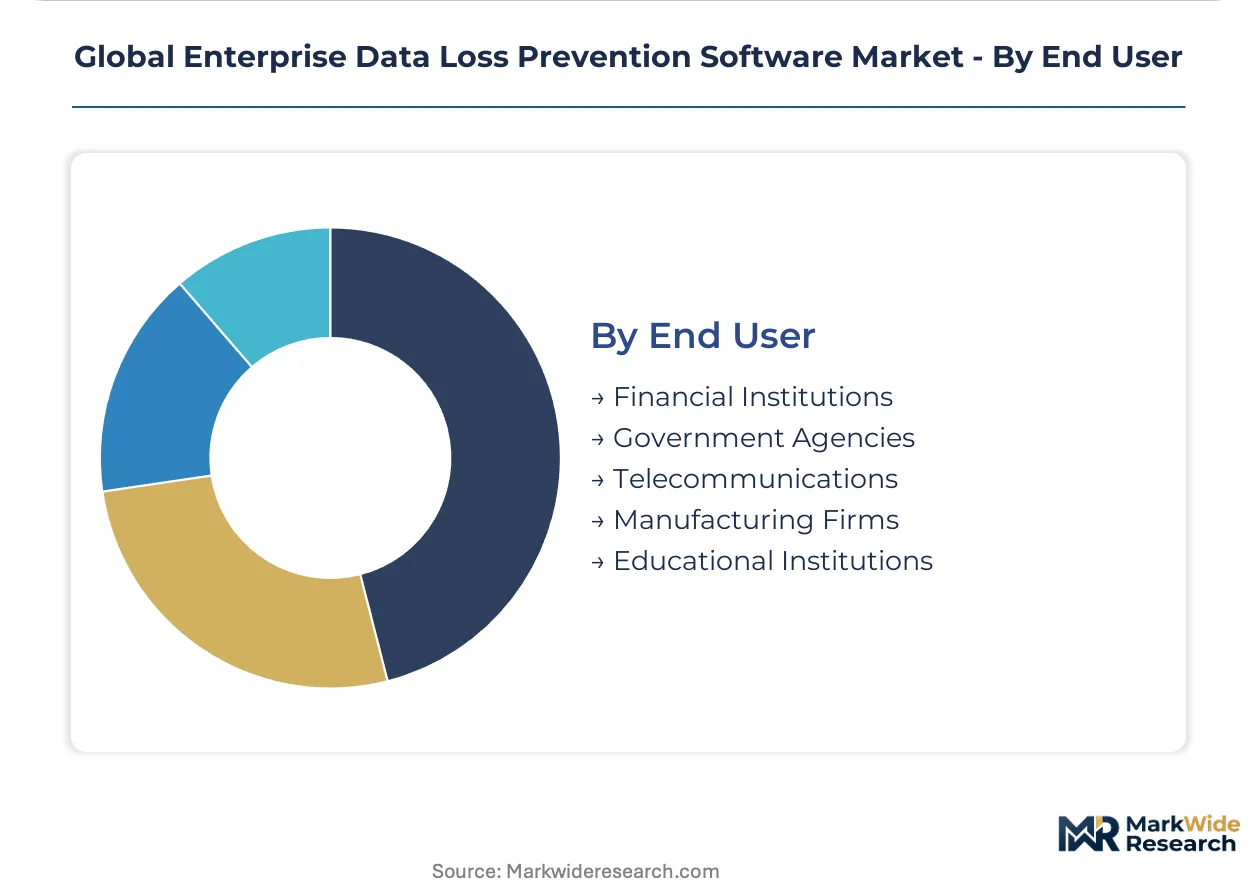
- Financial Institutions:Banks, insurers, and asset managers subject to PCI-DSS, SOX, and Basel operational risk frameworks. Major institutions in New York, London, and Singapore allocate largest DLP budgets for trading floor surveillance and client data protection.
- Government Agencies:Civilian and defense entities with classified and controlled unclassified information mandates. National security organizations in the United States, United Kingdom, and Australia drive requirements for hardware-rooted encryption and tamper-evident logging.
- Telecommunications:Carriers and ISPs managing subscriber metadata and lawful intercept data. Operators in Brazil, South Africa, and India face data localization mandates compelling in-country DLP infrastructure deployment.
- Manufacturing Firms:Discrete and process manufacturers protecting product designs and supply chain data. Automotive OEMs in Germany, Japan, and South Korea extend DLP into supplier quality management systems.
- Educational Institutions:Universities and research hospitals managing student records and grant-funded research data. R1 research universities in California, Massachusetts, and North Carolina deploy DLP for NIH and NSF data management plan compliance.
Spend intensity peaks with Financial Institutions; addressable market expansion runs strongest through Educational Institutions.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
San Francisco Bay Area technology corridors anchor global demand for cloud-native DLP architectures, with venture-backed SaaS firms driving agentless inspection adoption. Financial institutions in Manhattan and London simultaneously expand endpoint DLP footprints for trading floor surveillance. Regulatory enforcement divergence across jurisdictions shapes deployment priorities.
United States
HIPAA-covered healthcare systems in Massachusetts and Texas prioritize endpoint DLP for clinician device protection, while SEC-registered broker-dealers in New York deploy network DLP for trade surveillance. The FDA's 21 CFR Part 11 electronic records mandates shape pharmaceutical procurement specifications. Defense contractors in Northern Virginia anchor insider threat prevention deployments under CMMC supply chain security protocols.
Germany
Automotive OEMs in Stuttgart and Munich extend DLP into supplier quality management systems for CAD file protection. BaFin operational risk frameworks mandate audit-ready data lineage for Frankfurt-based financial institutions. The EU AI Act's risk-based compliance tiers drive AI governance module adoption among industrial manufacturers in Bavaria.
United Kingdom
Professional services firms in London deploy email DLP for Solicitors Regulation Authority confidentiality enforcement. Defence and Security Equipment International protocols require insider threat modules for aerospace contractors in Bristol and BAE Systems supply chains. The Information Commissioner's Office GDPR enforcement actions accelerate automated breach notification workflow procurement.
India
The Digital Personal Data Protection Act's data localization mandates compel in-country DLP infrastructure among global enterprises serving Mumbai and Bangalore consumer markets. RBI cybersecurity guidelines for scheduled commercial banks drive cloud DLP adoption in Hyderabad's fintech corridors. IT services exporters in Chennai and Pune integrate DLP into client delivery centers for HIPAA and PCI-DSS compliance.
Singapore
Monetary Authority of Singapore technology risk management guidelines mandate DLP for wealth management platforms in the central business district. Containerized DLP architectures gain traction among DevOps-intensive enterprises in one-north technology precinct. Cross-border data routing complexity from Schrems II rulings drives parallel policy set maintenance for EU-Asia data flows.
Global Enterprise Data Loss Prevention Software Market Competitive Landscape
Premium-margin players sit above commodity-margin players across integration depth and deployment flexibility. Cloud platform providers bundle DLP into broader security suites, compressing standalone vendor pricing power. Three archetypes dominate: ecosystem-anchored platforms, endpoint-centric specialists, and API-native cloud specialists. Strategic consolidation and channel partnership expansion represent the dominant competitive vectors.
Within the ecosystem-anchored tier, Microsoft Purview exemplifies platform-native bundling strategies, while Proofpoint Enterprise DLP and Digital Guardian occupy positions as specialized best-of-breed alternatives. These three entities represent divergent architectural bets—cloud ecosystem dominance versus targeted vector protection versus deployment flexibility for regulated industries.
| Leading Market Players |
|---|
| Proofpoint Enterprise DLP |
| Digital Guardian |
| Microsoft Purview |
| Fortra DLP |
| Netskope DLP |
| Symantec DLP |
| Trellix DLP |
| Varonis |
| Forcepoint DLP |
| Others |
Supply & Pricing Matrix
Agentless cloud inspection architectures are compressing both development costs and vendor concentration simultaneously, as API-native delivery eliminates hardware appliance manufacturing while concentrating engineering talent in California and Washington state corridors. This dual compression reshapes how procurement committees evaluate total cost of ownership against deployment flexibility.
Pricing Analysis
Outcome-based pricing tied to prevented data breach incidents anchors enterprise DLP contracts, with annual recurring revenue models dominating over perpetual licenses. Three-tier pricing structure across premium, standard, and economy levels separates ecosystem-integrated suites from best-of-breed point solutions and open-source alternatives. Cost compression in the mid-market tier is intensifying because cloud platform providers bundle baseline DLP functionality at marginal cost. Financial institutions in New York and London exhibit lowest price sensitivity due to regulatory penalty exposure, while educational institutions in California and North Carolina face acute budget constraints.
Supply Chain Analysis
Engineering workforce availability in India, Ireland, and Poland shapes R&D center placement for DLP vendors pursuing 24-hour development cycles. Core intellectual property draws from machine learning model training pipelines, cloud infrastructure APIs, and cryptographic libraries sourced from open-source foundations. Single-source vulnerability concentrates in hyperscaler cloud compute dependencies, where AWS, Azure, and GCP outages cascade to SaaS-delivered policy engines. Distribution runs through direct enterprise field sales in regulated verticals and MSSP channel partnerships for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The enterprise DLP market functions as a vertical-integration race, with vendors capturing upstream control over ML training data pipelines and downstream embedding into security orchestration platforms.
For Market Incumbents: Hedge against cloud platform bundling by deepening endpoint agent specialization for air-gapped environments in defense and pharmaceutical sectors. Fortify channel relationships with MSSPs in Brazil and Mexico where direct sales economics fail. Prioritize certification investment for CMMC, HIPAA, and EU AI Act audit readiness to maintain pricing power against commodity alternatives. For New Entrants and Emerging Players: Containerized microservice architectures targeting DevOps-intensive enterprises in Singapore and the Netherlands offer the most penetrable wedge, as incumbent platforms lack Kubernetes-native deployment flexibility. Pursue white-space in MLOps pipeline monitoring for EU AI Act training data provenance compliance. Lead with API-first integration stories rather than feature parity against established endpoint agents. For Investors and Strategic Acquirers: Exit pathways concentrate in strategic acquisition by cloud platform providers seeking to fill DLP gaps, with financial sponsor roll-ups of regional specialists as secondary liquidity. Target mid-cap vendors with embedded AI governance modules and existing healthcare or financial services customer concentration. Watch Schrems II enforcement actions as the signal indicating accelerated demand for parallel EU-US policy set architectures.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Microsoft Purview's bundling strategy forces standalone vendors toward API-native interoperability claims. |
| Acquisition of Specialist Firm | NLP-native classification startups in Israel and Taiwan address semiconductor IP protection gaps. |
| Geographic Expansion | In-country infrastructure deployment satisfies India's Digital Personal Data Protection Act localization mandates. |
| Strategic Partnership | MSSP alliances in Latin America bypass direct field sales investment for mid-market penetration. |
| Product Launch | AI governance modules embedded in DLP platforms capture EU AI Act risk-tier compliance requirements. |
Research Methodology
Multi-period observation of breach disclosure filings, regulatory enforcement actions, and vendor pricing disclosures anchored the trend analysis, supplemented by interviews with CISOs, IT procurement officers, platform engineers, and MSSP channel partners. Secondary validation drew from SEC 10-K security spend disclosures, GDPR enforcement tracker databases, hyperscaler capex reports, and healthcare system RFP documentation. Bottom-up deployment model estimates triangulated against top-down security software market sizing.
Segment-weighting across deployment architecture, solution type, and end-user vertical determined value distribution throughout the forecast period. Modeled dimensions included cloud migration timeline, regulatory exposure tier, and integration complexity level. CAGRs derived from regression analysis of historical security software spend patterns against exogenous regulatory shock timing. Forecast inputs incorporated HIPAA audit frequency trends and EU AI Act implementation phase transitions.
Several conditions sit outside the modeled scope, including sovereign cloud mandates beyond India, quantum cryptography disruption timelines, and vendor consolidation outcomes. Forecasts reflect documented assumptions about sustained GDPR enforcement intensity and cloud migration continuation. A small set of named triggers warrants ongoing watch: Schrems II ruling expansion, TLS protocol evolution degrading network visibility, and shadow SaaS discovery capability breakthroughs.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Patch and Remediation Software Market
Security Software
Network Video Recorder (NVR) Market
Security Software
VPN Software Market
Security Software
Mobile Identity Management Market
Security Software
Data Privacy Software Market
Security Software
Hardware OTP Token Authentication Market
Security Software
Passport Reader Market
Security Software
Wi-Fi Based Home Camera Market
Security Software
Europe Lawful Interception Market
Security Software
Information Rights Management Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Application Control Software Market
Security Software
Antivirus Software Package Market
Security Software
Global Mobile Identification Market
Security Software
US Hardware OTP Token Authentication Market