
 Secure Email Gateway Market | 2026-2036
Secure Email Gateway Market Size, Share, and Industry Trends Forecast 2026-2036
Secure Email Gateway Market Outlook
Cybersecurity talent scarcity is redrawing competitive boundaries in the Secure Email Gateway space. Proofpoint leverages its specialized threat research workforce to sustain premium positioning in advanced persistent threat defense. Cisco Secure Email anchors its market presence through deep channel control across enterprise networking accounts.
A Secure Email Gateway is a network security solution that inspects inbound and outbound email traffic through protocol analysis, sandbox detonation, and machine-learning classification to block phishing, malware, and data exfiltration. Cloud-based deployment now leads segment growth as organizations retire on-premises infrastructure, while integrated security solutions command the widest margin pools by bundling threat detection with compliance archiving. Large enterprises remain the dominant end-user category, though government buyers are expanding fastest under tightened procurement standards.
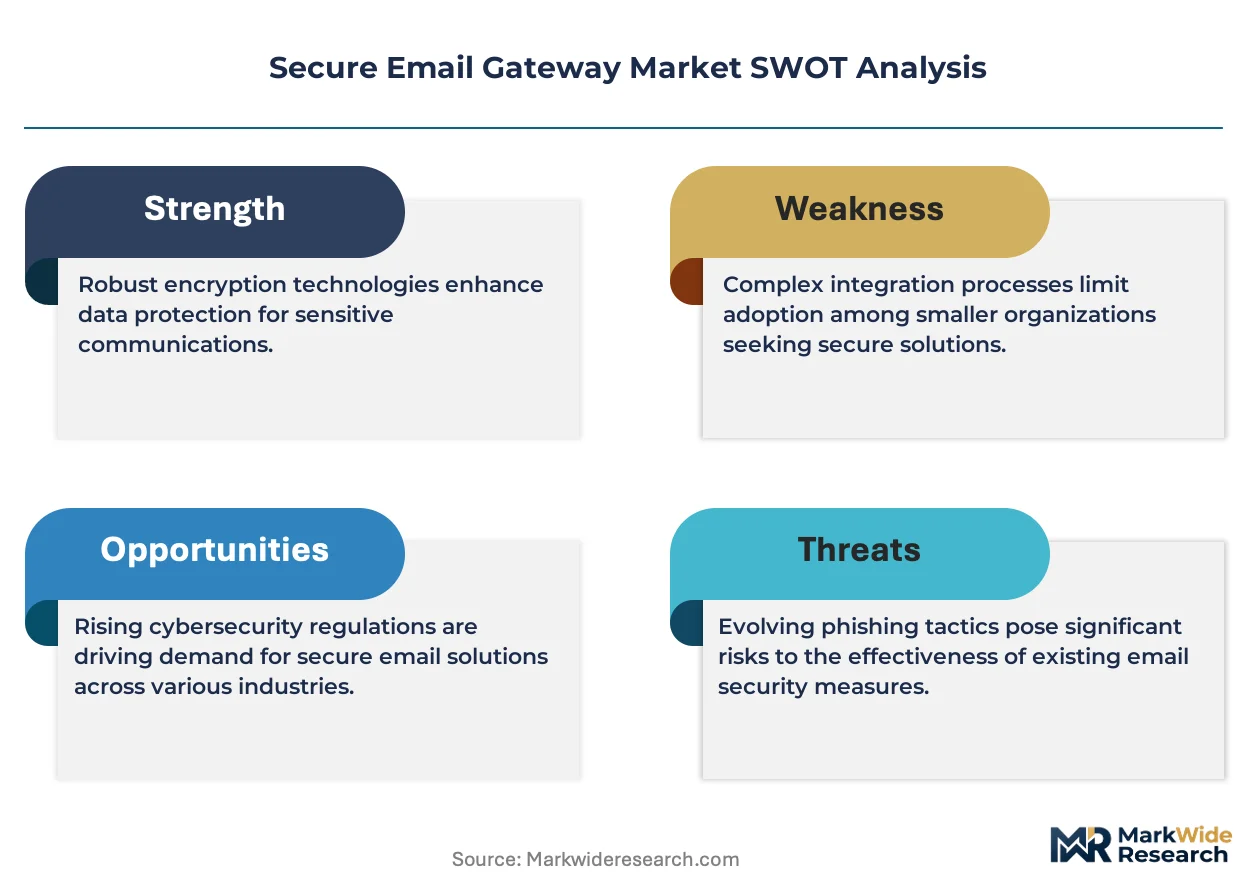
The EU AI Act, NIS2 Directive, and GDPR collectively shape product roadmaps by mandating explainable threat scoring and cross-border incident reporting. In the United States, SEC cybersecurity disclosure rules and HIPAA requirements drive healthcare and financial services procurement cycles. Stakeholders must weigh sovereign data requirements against cloud-native scalability when selecting architecture and vendor partnerships.
Market Dynamics
Cloud migration is compressing deployment timelines and forcing vendors to rearchitect delivery models around API-first integrations rather than perimeter appliances.
Growth Catalysts
- EU AI Act:Mandates for explainable automated threat scoring are accelerating procurement of ML-enabled inspection platforms among European financial institutions.
- Healthcare digitization:HIPAA-covered entities in the United States are expanding email security budgets to address business associate agreement enforcement.
- Sandbox detonation:Attachment analysis through isolated execution environments is displacing signature-based detection in enterprise security stacks.
Market Restraints
- Skewed talent distribution:Cybersecurity engineering expertise concentrates in the United States and Germany, inflating implementation costs elsewhere.
- Legacy protocol dependencies:SMTP and IMAP persistence limits deep inspection capabilities without traffic decryption infrastructure.
- False positive fatigue:Overly aggressive filtering erodes user trust and drives shadow IT email usage outside monitored channels.
Strategic Opportunities
- Japan:METI guidelines on supply chain cybersecurity are creating first-mover advantages for vendors with localized data residency architectures.
- API convergence:Native integration between email security and zero-trust network access platforms is opening unified procurement budgets.
- Government vertical:FedRAMP and equivalent national certification programs in Germany and Japan are erecting procurement barriers favoring compliant incumbents.
Industry Challenges
- Threat researcher scarcity:Specialized malware reverse engineering talent commands premium compensation, constraining vendor R&D scaling.
- Cross-border data routing:Conflicting sovereignty requirements between GDPR, China's PIPL, and sectoral US rules complicate multi-tenant cloud architectures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Secure Email Gateway Market |
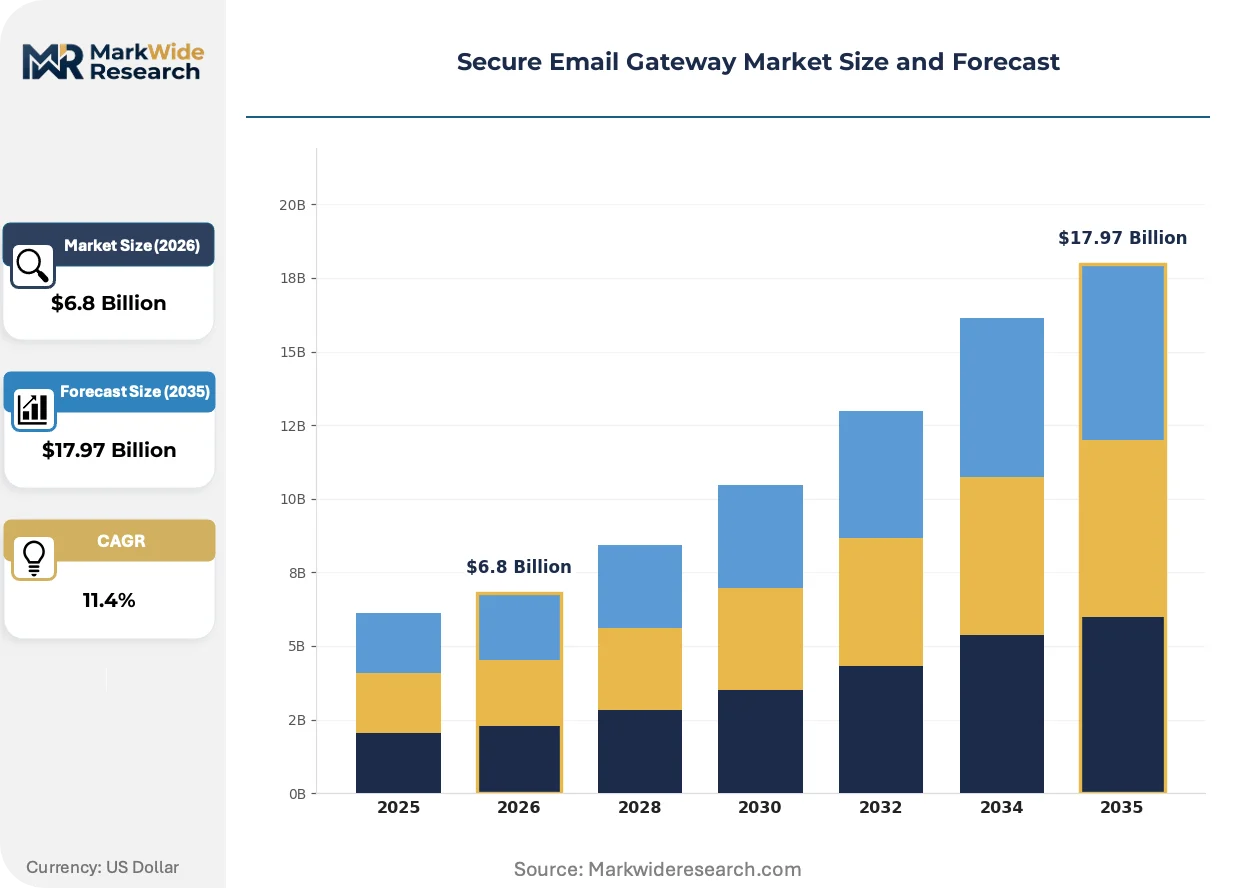
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $17.97 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Hosted End User: SMEs, Large Enterprises, Government, Educational Institutions Service Type: Email Filtering, Threat Detection, Data Loss Prevention, Archiving Solution: Integrated Security, Standalone Solutions, Compliance Solutions, Others |
| Companies Covered | Barracuda, Microsoft Defender for Office 365, Proofpoint, CrowdStrike, Trend Micro, Cisco Secure Email, Check Point Avanan, Sophos, Mimecast, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Secure Email Gateway Market Strategic Shifts
Generative AI is weaponizing phishing at scale while simultaneously enabling defensive automation, creating an arms race between attacker sophistication and detection velocity.
Behavioral biometrics is fragmenting authentication paradigms in email security. Typing cadence and device telemetry now supplement credential validation for high-risk transaction verification. Large banks in the United States and Germany are piloting continuous authentication models that reduce password reset volumes. This convergence of identity and email security is fragmenting vendor categories previously separated by function.
The EU NIS2 Directive is mandating incident reporting timelines that compress from 72 hours to 24 hours for critical infrastructure operators. Email security platforms must now embed automated forensic extraction and standardized threat intelligence formatting. Healthcare and energy utilities in France, Germany, and the Netherlands are prioritizing vendors with pre-built regulatory reporting modules over pure detection performance.
Security service edge consolidation is displacing standalone email gateway procurement. Chief information security officers are bundling email inspection with web filtering and cloud access broker functions under single-vendor contracts. This preference for integrated stacks is most pronounced among mid-market enterprises in the United States seeking to reduce vendor management overhead. Reseller margins are compressing as direct cloud marketplaces capture an expanding share of transactional volume.
Secure Email Gateway Market Segmentation
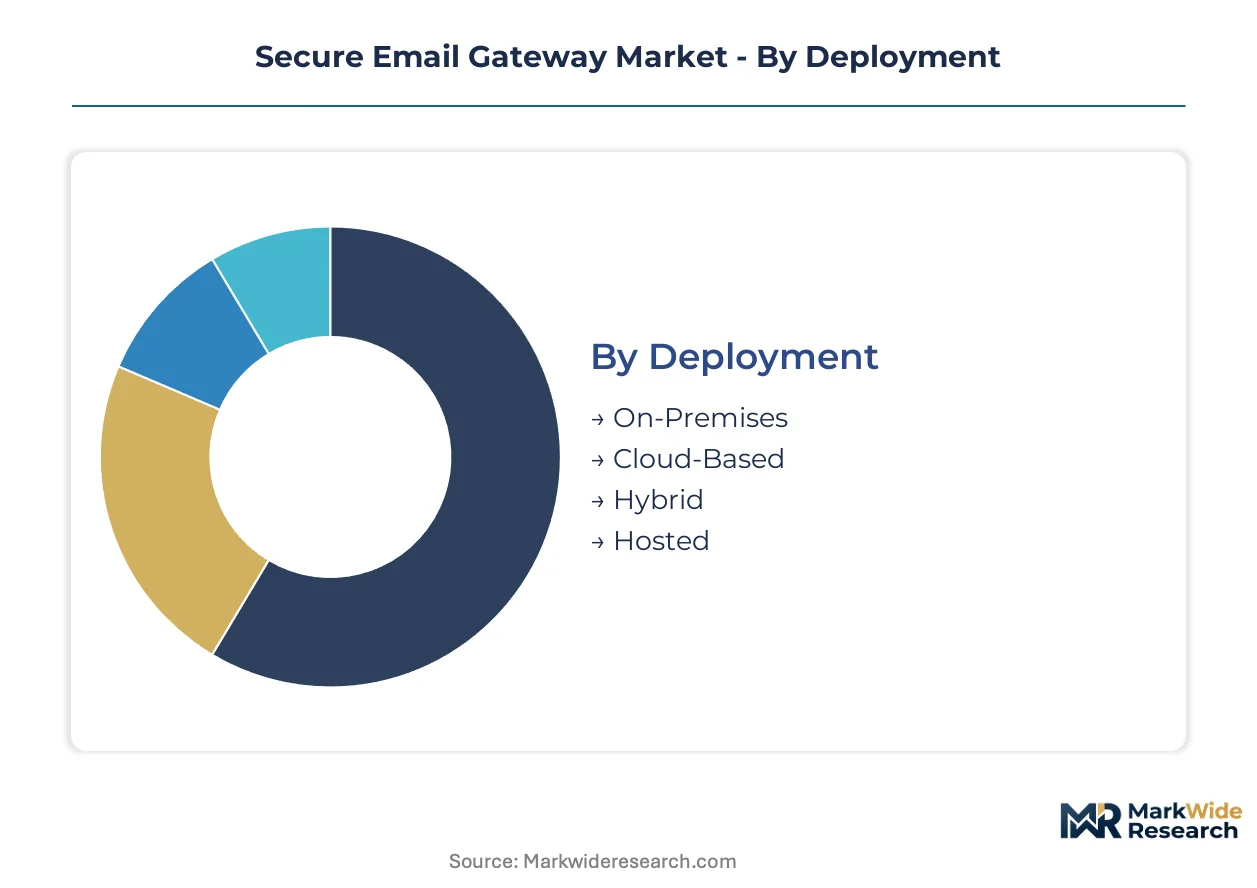
Deployment architecture determines data residency compliance and operational control for security-conscious buyers. End-user scale shapes procurement complexity and integration requirements across the Secure Email Gateway landscape.
Deployment:
Cloud-based platforms dominate procurement in export-led technology hubs, while on-premises retention persists in domestic defense and finance sectors with strict data localization mandates.
- Cloud-Based:Multi-tenant SaaS delivery enables rapid scaling through API-first integrations with Microsoft 365 and Google Workspace environments. Financial services firms in the United States and Germany are retiring perimeter appliances in favor of cloud-native inspection to satisfy SEC and BaFin audit trails.
- On-Premises:Physical or virtual appliance deployment within customer data centers maintains complete traffic sovereignty and decryption key control. Defense contractors and classified government networks in the United States, Japan, and Germany retain this architecture to meet FedRAMP High, METI guidelines, and BSI baseline protection requirements.
- Hybrid:Split traffic processing routes sensitive domains through on-premises inspection while cloud handles high-volume general correspondence.
- Hosted:Single-tenant managed service in third-party facilities bridges compliance and outsourcing needs for mid-market regulated entities.
Cloud-based platforms command the established base. The steepest expansion runs through hybrid configurations balancing sovereignty with scalability.
End User:
Procurement sophistication separates enterprise buyers with dedicated security operations centers from resource-constrained segments prioritizing managed service simplicity.
- Large Enterprises:Complex multi-domain environments demand granular policy orchestration, sandbox detonation at scale, and native SIEM integration. Manufacturing conglomerates and healthcare systems in the United States, Germany, and Japan drive premium feature roadmaps.
- Government:National certification requirements create procurement moats favoring vendors with FedRAMP, BSI C5, or ISMAP Japan accreditation. Critical infrastructure operators under EU NIS2 Directive mandates are expanding fastest.
- SMEs:Bundled security service edge offerings reduce vendor management overhead for mid-market buyers lacking specialized cybersecurity staff.
- Educational Institutions:Open research collaboration requirements clash with student data privacy rules, creating unique filtering policy challenges.
Large enterprises command the established base. The steepest expansion runs through government verticals under tightened procurement standards.
Service Type:
Service bundling intensity correlates with buyer maturity, with advanced segments demanding integrated forensic and compliance capabilities beyond basic filtering.
- Threat Detection:Machine-learning classification and behavioral analysis identify zero-day phishing and business email compromise campaigns. Banks in the United States and Germany pilot continuous authentication models reducing password reset volumes.
- Data Loss Prevention:Content inspection and policy enforcement block accidental or malicious exfiltration of regulated data classes. HIPAA-covered entities expand DLP budgets to address business associate agreement enforcement.
- Email Filtering:Protocol-level spam and malware blocking remains foundational for all buyer tiers.
- Archiving:Immutable retention with e-discovery search satisfies SEC, GDPR, and sectoral record-keeping mandates.
Threat detection commands the established base. The steepest expansion runs through data loss prevention under regulatory pressure.
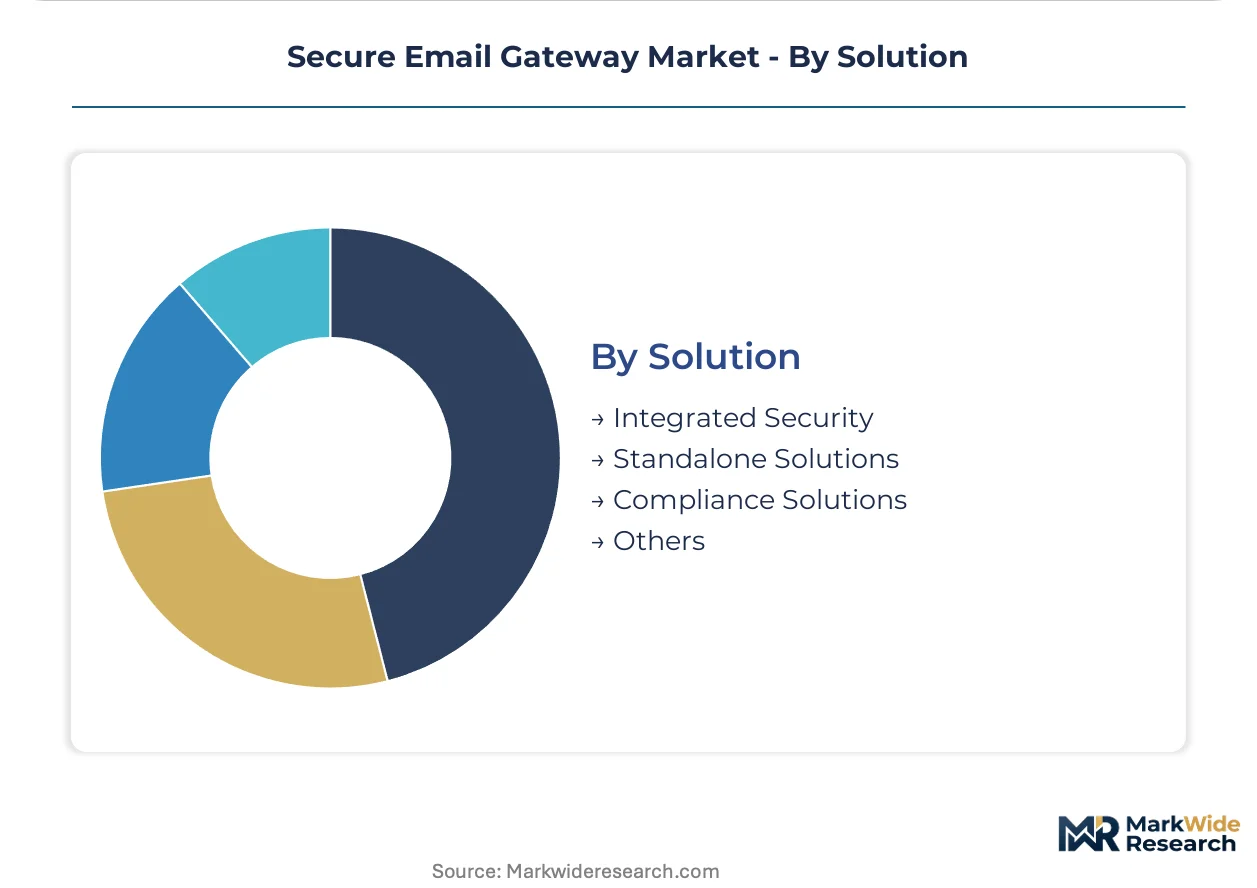
Solution:
Vendor consolidation preferences are fragmenting standalone gateway specialists as buyers prioritize unified security stack procurement.
- Integrated Security:Bundled email inspection with web filtering, CASB, and zero-trust network access functions under single-vendor contracts. Mid-market enterprises in the United States favor this approach to reduce vendor management overhead.
- Compliance Solutions:Pre-built regulatory reporting modules for EU NIS2 Directive, SEC cybersecurity disclosure rules, and HIPAA audit requirements. Healthcare and energy utilities in France, Germany, and the Netherlands prioritize vendors with automated forensic extraction.
- Standalone Solutions:Dedicated email security appliances or cloud services for buyers with best-of-breed procurement policies.
- Others:Specialized offerings including encrypted messaging gateways and industry-specific communication compliance tools.
Integrated security commands the established base. The steepest expansion runs through compliance solutions accelerating under disclosure rule tightening.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
SEC cybersecurity disclosure rules and HIPAA enforcement are accelerating procurement cycles across the United States. Financial services and healthcare verticals drive premium feature adoption as regulatory pressure intensifies.
United States
Healthcare systems and financial institutions dominate demand as HIPAA-covered entities expand budgets for business associate agreement enforcement. SEC disclosure rules mandate rapid incident reporting, compressing vendor selection timelines. Silicon Valley and New York Metro clusters anchor cloud-native adoption among technology and banking sectors.
Germany
BaFin audit requirements and BSI baseline protection standards shape procurement for financial and defense sectors. The EU AI Act mandates explainable threat scoring, favoring vendors with transparent machine-learning architectures. Munich and Frankfurt banking clusters prioritize automated forensic extraction for NIS2 Directive compliance.
Japan
METI guidelines on supply chain cybersecurity create procurement advantages for vendors with localized data residency. ISMAP Japan certification erects barriers favoring compliant incumbents in government and critical infrastructure. Tokyo and Osaka manufacturing conglomerates drive hybrid deployment adoption balancing sovereignty with scalability.
United Kingdom
NCSC guidance and sector-specific regulators shape financial services and government procurement patterns. Post-Brexit data sovereignty requirements complicate cross-border cloud architectures for multinational enterprises. London financial services clusters prioritize integrated security service edge bundles reducing vendor management overhead.
France
ANSSI certification and CNIL data protection enforcement shape critical infrastructure procurement under NIS2 Directive mandates. Healthcare and energy utilities prioritize vendors with pre-built regulatory reporting modules. Paris and Lyon industrial clusters accelerate 24-hour incident reporting compliance through automated forensic platforms.
Secure Email Gateway Market Competitive Environment
A small set of integrated leaders sits above a broader specialist tier in the Secure Email Gateway space. Consolidation pressure favors vendors bundling email inspection with zero-trust network access and cloud access broker functions. Three archetypes dominate: cloud-native specialists, networking incumbents with channel depth, and cybersecurity pure-plays with threat research differentiation. Competitive moves center on API-first integration investments and FedRAMP/BSI C5 certification acceleration.
Within the cloud-native tier, Microsoft Defender for Office 365 and Mimecast exemplify platform-centric positioning leveraging native productivity suite integration. Proofpoint occupies a position among threat research-intensive specialists commanding premium positioning through specialized malware reverse engineering capabilities. Cisco Secure Email anchors the networking incumbent archetype with deep enterprise account control through channel partnerships.
| Leading Market Players |
|---|
| Barracuda |
| Microsoft Defender for Office 365 |
| Proofpoint |
| CrowdStrike |
| Trend Micro |
| Cisco Secure Email |
| Check Point Avanan |
| Sophos |
| Mimecast |
| Others |
Value Chain & Pricing Dynamics
Cloud-native API architectures displacing perimeter appliance hardware are redrawing procurement economics across the Secure Email Gateway landscape, compressing capital expenditure cycles while expanding recurring revenue streams for vendors with multi-tenant SaaS delivery. This substitution simultaneously concentrates engineering talent demand in United States and Germany technology hubs while fragmenting physical infrastructure requirements, creating divergent cost structures between cloud-first and sovereignty-bound deployment models.
Pricing Analysis
Geographic price spreads widen between North American and Asia-Pacific procurement, with United States financial services buyers absorbing premium SaaS tiers for FedRAMP-compliant platforms while Japanese manufacturing conglomerates negotiate hybrid deployment discounts. Subscription tiering anchored to data residency controls and sandbox detonation scale separates enterprise buyers from mid-market segments. Cost compression in standard cloud tiers intensifies as Microsoft and Google bundle email security with productivity suites. Government verticals exhibit lowest price sensitivity due to certification barriers, while educational institutions face acute budget constraints.
Supply Chain Analysis
Inbound logistics costs for hardware appliances spike during transpacific container congestion, though cloud-native delivery increasingly bypasses physical distribution entirely. Engineering talent concentrates in the United States, Germany, and Israel, with specialized malware reverse expertise commanding premium compensation. Threat intelligence feeds from Israel, United Kingdom, and United States security researchers anchor detection efficacy. Single-source vulnerability persists for GPU-accelerated sandbox hardware sourced from Taiwan and South Korea. Distribution runs through hyperscaler marketplaces, direct enterprise sales, and networking channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is concentrating through security service edge consolidation, with chief information security officers reducing vendor counts and bundling email inspection with zero-trust network access under unified procurement.
For Market Incumbents: Compound channel control advantages by deepening API-first integrations with Microsoft 365 and Google Workspace environments while accelerating FedRAMP High and BSI C5 certification timelines. Threat researcher scarcity constrains R&D scaling for pure-play competitors; incumbents should lock specialized malware reverse engineering talent through captive research centers in Israel and Germany. Defensive moats erode fastest among standalone gateway vendors lacking zero-trust convergence. For New Entrants and Emerging Players: Compliance automation layers where incumbents under-serve present the most penetrable white space, particularly NIS2 Directive reporting modules for French and German critical infrastructure operators. Japan's ISMAP certification gap creates first-mover opportunity for vendors with localized data residency architectures. Target mid-market healthcare systems in the United States through managed service packaging that reduces security operations center staffing requirements. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors integrated security platforms with zero-trust convergence over standalone email specialists. Long-term viability hinges on API ecosystem positioning and national certification portfolios rather than detection performance alone. Watch hyperscaler bundling intensity as the inflection indicator; accelerating Microsoft Defender attach rates signal compression risk for independent vendors.| Strategic Initiative | Industry Significance |
|---|---|
| API-First Platform Integration | Native Microsoft 365 and Google Workspace connectors capture procurement preference from cloud-migrating enterprises. |
| National Certification Acceleration | FedRAMP High, BSI C5, and ISMAP Japan credentials erect procurement barriers favoring compliant vendors. |
| Threat Research Center Expansion | Israel and Germany engineering hubs lock scarce malware reverse engineering talent away from competitors. |
| Compliance Automation Module Development | Pre-built NIS2 Directive reporting satisfies 24-hour incident disclosure mandates for European utilities. |
| Zero-Trust Network Access Convergence | Unified SASE bundling captures mid-market buyers seeking vendor management reduction. |
Study Parameters
Desk research of regulatory filing databases, hyperscaler partnership disclosures, and national certification registries preceded structured interviews with chief information security officers, email security product managers, channel partner principals, and government procurement officers across the United States, Germany, and Japan. Primary intelligence combined with secondary validation from SEC cybersecurity disclosure filings, EU NIS2 Directive implementation guidance, and METI supply chain security guidelines. Bottom-up deployment modeling and top-down regulatory impact assessment were triangulated against vendor revenue segmentation disclosures.
Variance decomposition across deployment architecture, end-user scale, and service type dimensions shaped the analytical framework throughout the projection horizon. CAGRs derived from segment-level growth rate reconciliation against macroeconomic sensitivity factors. Forecast inputs included cloud migration velocity indices, national certification pipeline timelines, and threat intelligence feed subscription trends.
Forecasts assume regulatory continuity in SEC disclosure regimes, EU AI Act implementation schedules, and METI guideline enforcement; material policy shifts would require re-modeling. Threat actor sophistication acceleration, hyperscaler bundling intensity, and cross-border data routing restrictions represent specific revision risks. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Spain Endpoint Detection and Response Market
Security Software
Security Testing Market
Security Software
Global User Activity Monitoring Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Sound Masking Systems Market
Security Software
Network Camera and Video Analytics Market
Security Software
Confidential Computing Market
Security Software
Global Digital Identity Solutions Market
Security Software
Global Network Security Software Market
Security Software
Global Password Management Software Market
Security Software
Mobile Data Protection Solutions and Services Market
Security Software
Passport Reader Market
Security Software
Anomaly Detection Market
Security Software
Europe IP Video Intercom Device and Equipment Market
Security Software
ATM Security Market
Security Software
Global Data Breach Notification Software Market