
 Europe Software Defined Perimeter Market | 2026-2036
Europe Software Defined Perimeter Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Software Defined Perimeter Market Analytics
ISO/IEC 27001 certification is reorganizing the competitive landscape for European cybersecurity procurement. Cisco Systems leverages its established channel relationships across EU enterprise accounts. Fortinet sustains engineering density in next-generation firewall integration with SDP architectures. Zscaler competes through cloud-native delivery models aligned with EU data sovereignty requirements.
Software Defined Perimeter denotes a security architecture that authenticates users and devices before granting network access through encrypted micro-tunnels, typically operating at Layer 7 with session-specific trust scoring. The framework replaces perimeter-based VPNs with identity-centric access for distributed workforces and multi-cloud environments. Cloud-based deployment leads European adoption as organizations migrate from legacy on-premise gateways. Managed services within the service-type dimension capture expanding margin pools as mid-market buyers outsource policy orchestration. API security technology is gaining velocity alongside open-banking and embedded finance expansion.
GDPR, NIS2 Directive, and the EU Cybersecurity Act shape product requirements by mandating encryption standards, incident reporting timelines, and certified trust-service validation for critical infrastructure operators. ETSI technical specifications further constrain interoperability claims, forcing vendors to demonstrate conformance before public-sector eligibility. Stakeholders must monitor how ENISA threat intelligence feeds will recalibrate baseline compliance expectations across member states.
Market Dynamics
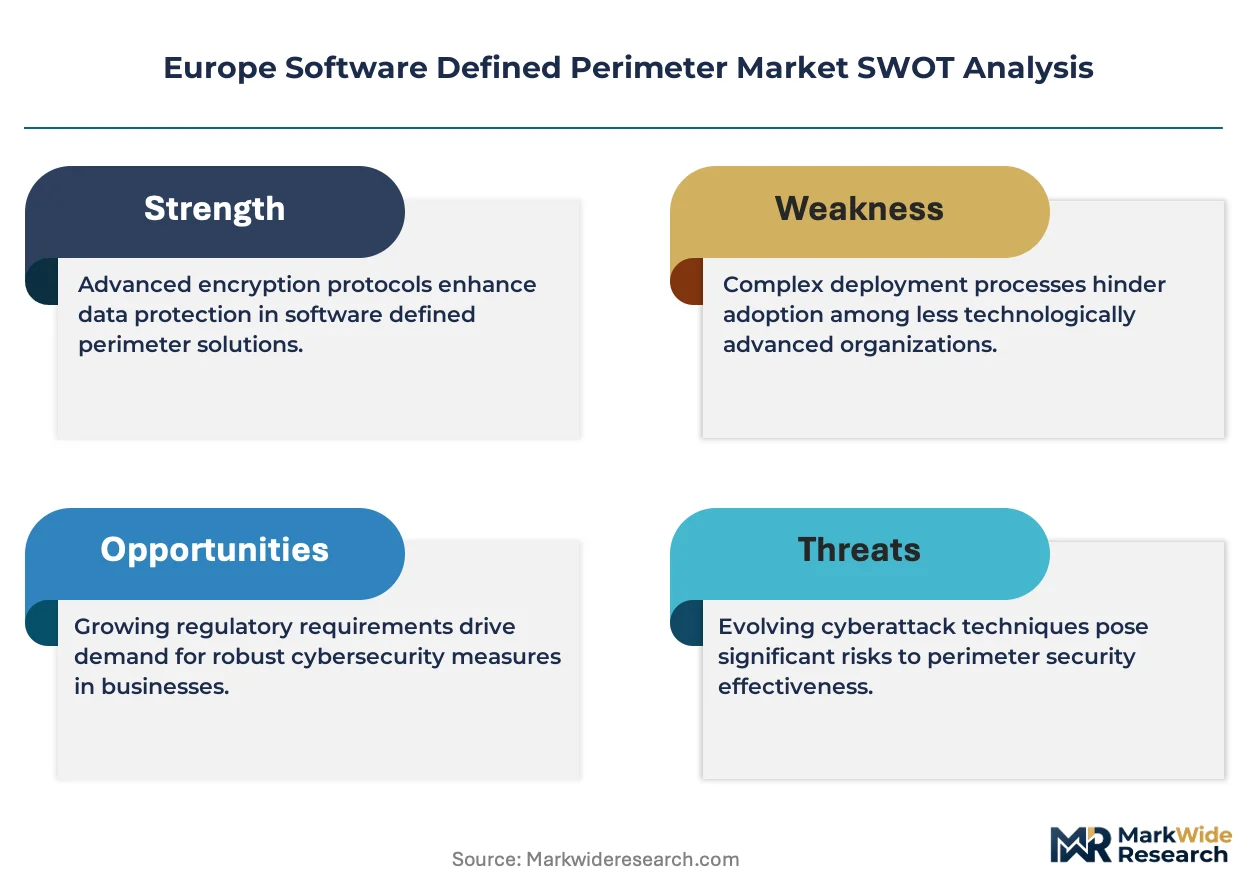
The EU NIS2 Directive and GDPR enforcement are compressing procurement cycles for zero-trust architectures across European financial services and critical infrastructure operators. Vendors must now demonstrate certified interoperability before qualifying for public-sector tenders, reshaping competitive positioning.
Growth Catalysts
- NIS2 Directive:The directive mandates incident reporting and supply-chain security assessments for critical infrastructure operators in Germany and France, accelerating SDP procurement timelines.
- Embedded finance expansion:Open-banking APIs across the Netherlands and Sweden require micro-segmented access controls that legacy VPNs cannot provision.
- Cloud migration velocity:Mid-market enterprises in the United Kingdom are retiring on-premise gateways for cloud-native SDP delivery, creating replacement demand.
Market Restraints
- Certification bottlenecks:ETSI technical specifications and EU Cybersecurity Act certification timelines extend vendor qualification periods by 12-18 months.
- Skill scarcity:Zero-trust architecture expertise concentrates in London, Frankfurt, and Amsterdam, inflating implementation costs for buyers outside these clusters.
- Legacy integration friction:Mainframe-dependent banks in Italy and Spain face technical debt barriers when overlaying SDP on existing identity infrastructure.
Strategic Opportunities
- Poland and Czech Republic:Underpenetrated mid-market manufacturing and logistics sectors lack mature security operations centers, creating first-mover openings for managed SDP services.
- AI-driven policy orchestration:Convergence of machine learning with SDP policy engines enables real-time risk scoring for dynamic access decisions.
- EU AI Act:The Act's high-risk system classification creates compliance-driven demand for auditable access logs and identity verification workflows.
Industry Challenges
- Cross-border data residency:GDPR Article 44 transfer mechanisms complicate multi-tenant SDP architectures serving users across Ireland, Germany, and non-EU subsidiaries.
- Interoperability verification:ENISA threat intelligence integration requirements lack standardized implementation guides, forcing vendors to rebuild connectors per member state.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Software Defined Perimeter Market |
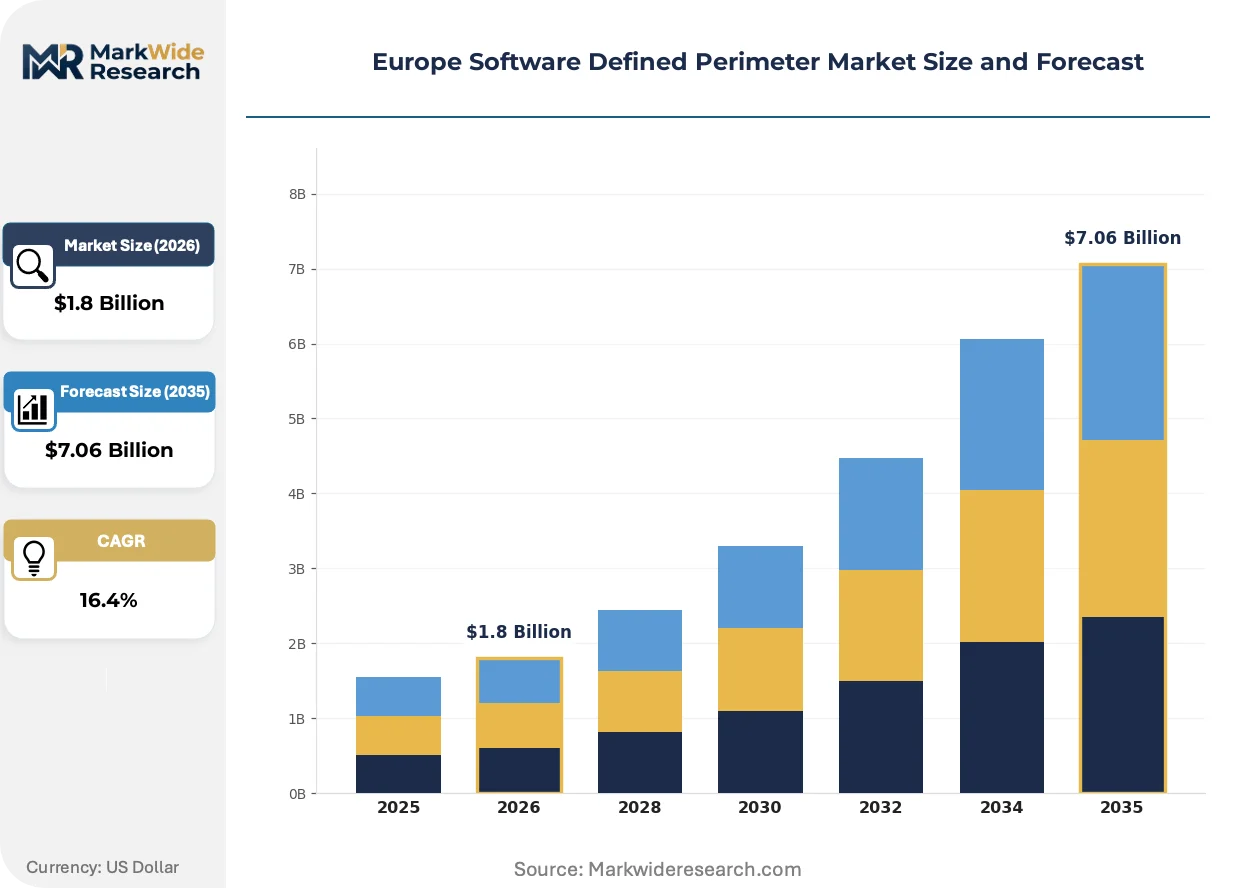
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $7.06 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Virtual Appliances End User: Healthcare, Finance, Telecommunications, Government Service Type: Consulting, Managed Services, Integration, Support Technology: Identity Management, Encryption, Access Control, API Security |
| Companies Covered | Verizon Communications, Cisco Systems, Fortinet, Akamai Technologies, Perimeter 81, Zscaler, Check Point Software Tech, Cato Networks, Palo Alto Networks, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Software Defined Perimeter Market Evolving Landscape
European cybersecurity procurement is pivoting from perimeter defense to identity-centric architectures. Three convergent forces are compressing traditional vendor advantage windows and creating openings for specialized providers.
Zero-trust network access is decomposing monolithic VPN appliances into distributed policy enforcement points. Financial institutions in the City of London and Frankfurt's Bankenviertel are deploying session-specific micro-tunnels at scale. This decomposition collapses the distinction between network and application-layer security, forcing firewall vendors to rearchitect around identity fabrics.
The EU AI Act's risk-based classification system is recalibrating product roadmaps for vendors serving healthcare and transport operators. High-risk AI system providers must implement human oversight and audit trails, which SDP logging architectures now support. Medical device manufacturers in Germany and the Netherlands are prioritizing access solutions with pre-built compliance mappings.
Mid-market buyers are unbundling implementation from software licensing. Systems integrators in Manchester and Munich are capturing margin pools through policy-as-code deployment services. This shift is most pronounced among pharmaceutical and professional services firms with limited in-house security engineering capacity.
Europe Software Defined Perimeter Market Segmentation
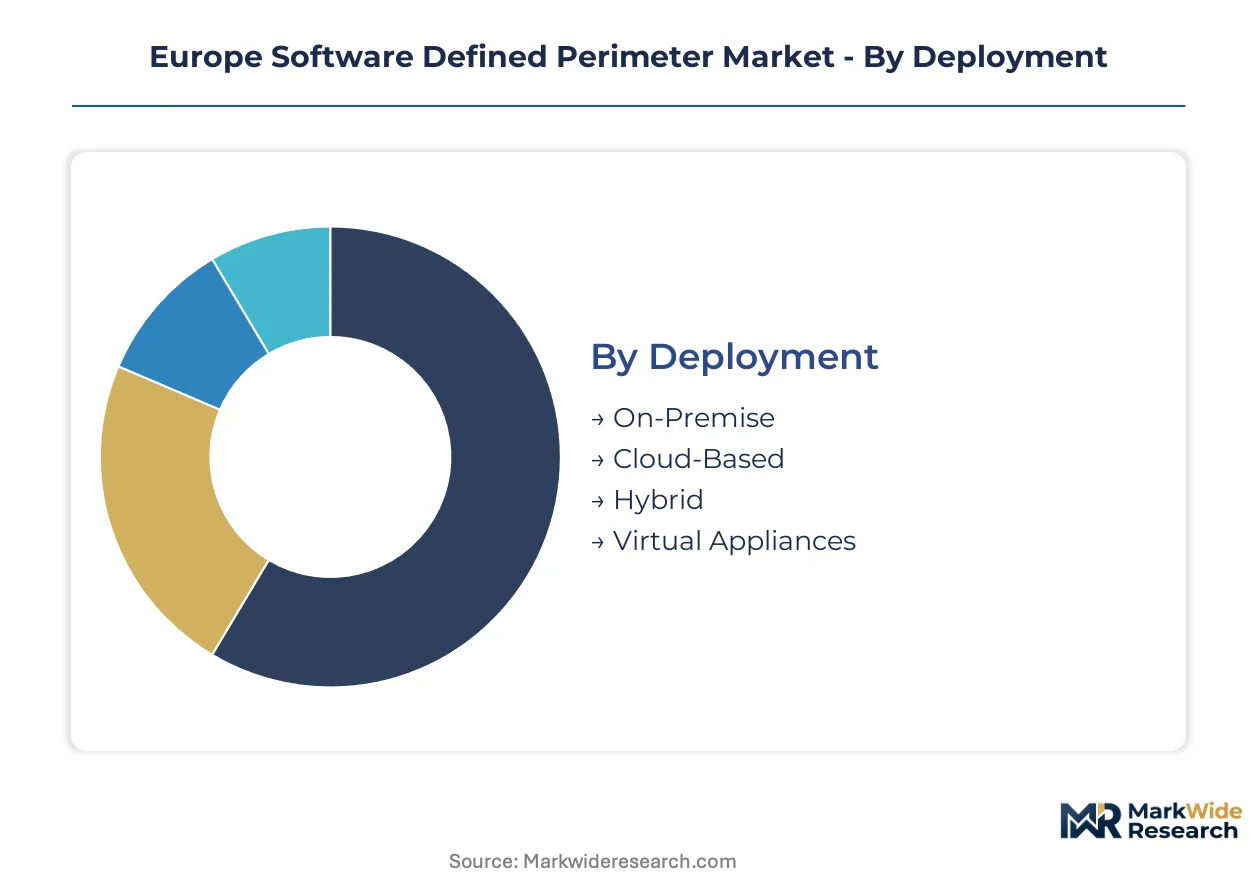
SDP architectures fragment across deployment models, regulatory exposure, and service delivery economics. Buyers optimize for GDPR data residency, NIS2 compliance velocity, and cloud migration timelines. Vendors configure pricing and partnership strategies around these fault lines.
Deployment:
Margin pools concentrate in cloud-native delivery where recurring revenue models and reduced implementation overhead improve unit economics. On-premise deployments retain value in sovereign cloud mandates and classified infrastructure environments.
- Cloud-Based:Multi-tenant architectures with EU data center localization satisfy GDPR Article 44 transfer requirements. German automotive suppliers and Dutch fintechs favor this model for rapid provisioning without capital expenditure. NIS2 incident reporting automation integrates more cleanly with cloud policy orchestration layers.
- On-Premise:Hardware appliances deployed within customer data centers enforce air-gapped segmentation for defense and intelligence agencies. French critical infrastructure operators under ANSSI supervision maintain this posture despite higher total cost of ownership. Certification timelines extend 12-18 months for hardware security module integration.
- Hybrid:Split policy enforcement across cloud and on-premise gateways accommodates phased migration from legacy VPNs. UK financial services firms with mainframe dependencies use this bridge architecture during zero-trust transitions.
- Virtual Appliances:Software-only deployment on hypervisor infrastructure preserves hardware flexibility for mid-market manufacturing in Poland and Czech Republic. License portability between private cloud and edge locations appeals to distributed logistics operators.
Cloud-Based holds installed capacity. Hybrid is rotating up the share rankings.
End User:
Regulatory intensity varies sharply across verticals, with finance and government commanding premium pricing for certified compliance modules. Healthcare procurement cycles lag due to medical device validation requirements.
- Finance:Open-banking APIs and embedded finance expansion in Netherlands and Sweden demand micro-segmented access controls. PSD2 strong customer authentication mandates overlap with SDP identity verification workflows. Frankfurt and London banking clusters drive volume concentration.
- Government:EU Cybersecurity Act certification and ETSI interoperability standards gate public-sector eligibility. National procurement frameworks in Germany, France, and Italy require demonstrated ENISA threat intelligence integration.
- Healthcare:Medical device manufacturers in Germany and Netherlands prioritize access solutions with EU AI Act audit trail capabilities. HIPAA-equivalent national implementations slow procurement relative to finance.
- Telecommunications:5G network slicing and edge computing architectures require subscriber-specific micro-tunnels. Operators in Spain and Italy face NIS2 supply-chain security assessment deadlines.
Finance dominates current revenue contribution. Government is climbing the fastest on compliance-driven replacement cycles.
Service Type:
Value capture is shifting from perpetual licenses toward recurring policy management and integration services as mid-market buyers outsource security engineering.
- Managed Services:Continuous policy tuning and threat response delivered under subscription contracts. Manchester and Munich systems integrators capture margin pools from pharmaceutical and professional services firms with limited in-house capacity.
- Integration:Policy-as-code deployment and legacy identity system migration command project-based fees. Italian and Spanish banks with mainframe technical debt require specialized overlay expertise.
- Consulting:Zero-trust architecture design and NIS2 readiness assessments precede procurement decisions. Skill scarcity in London, Frankfurt, and Amsterdam inflates day rates for qualified practitioners.
- Support:Tiered response commitments with certified engineer access. Standard maintenance contracts face pressure as buyers prioritize outcome-based service level agreements.
Managed Services commands expanding margin contribution. Integration is gaining share fastest on legacy modernization demand.
Technology:
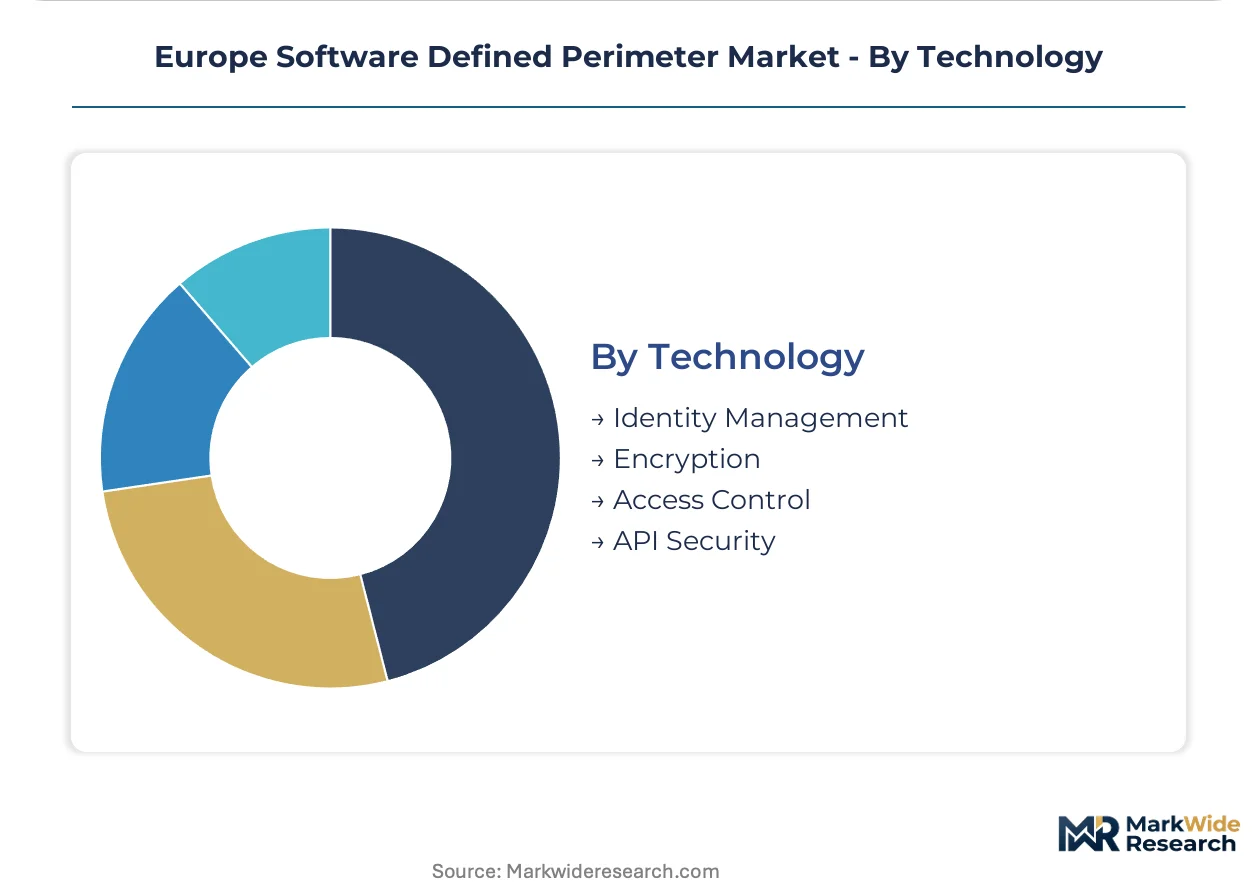
Identity-centric architectures are displacing network-layer enforcement, with API security gaining velocity alongside embedded finance and open-banking expansion.
- Identity Management:Continuous authentication and device trust scoring replace one-time VPN credentials. Session-specific micro-tunnels at Layer 7 collapse distinctions between network and application security. UK and German financial institutions deploy at scale.
- API Security:Granular access controls for machine-to-machine communication in open-banking and embedded finance environments. Netherlands and Sweden lead European adoption on regulatory mandate alignment.
- Encryption:End-to-end micro-tunnel encryption satisfies GDPR technical safeguard requirements. ETSI specifications constrain algorithm selection for public-sector eligibility.
- Access Control:Dynamic policy enforcement based on real-time risk signals. Convergence with machine learning enables adaptive trust scoring for high-risk AI systems under EU AI Act classification.
Identity Management anchors current architecture decisions. API Security is rotating up the share rankings on fintech infrastructure expansion.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The NIS2 Directive and GDPR enforcement are compressing procurement cycles for zero-trust architectures across European financial services and critical infrastructure operators. Vendors must now demonstrate certified interoperability before qualifying for public-sector tenders, reshaping competitive positioning.
Germany
Automotive suppliers and fintech clusters in Munich and Frankfurt are retiring legacy VPNs for cloud-native SDP delivery. The BSI (Federal Office for Information Security) mandates technical baseline protection under BSI IT-Grundschutz standards. Frankfurt's Bankenviertel banking district drives concentrated demand for micro-segmented access controls aligned with PSD2 strong customer authentication.
United Kingdom
Mid-market enterprises in London and Manchester are outsourcing policy orchestration to managed service providers under subscription contracts. The UK National Cyber Security Centre publishes zero-trust architecture guidance that influences procurement specifications. The City of London financial cluster deploys session-specific micro-tunnels at scale, collapsing distinctions between network and application-layer security.
France
Critical infrastructure operators under ANSSI supervision maintain air-gapped segmentation postures despite higher total cost of ownership. The EU Cybersecurity Act certification timelines extend vendor qualification periods for hardware security module integration. Paris and Lyon host concentrated defense and intelligence agency demand for on-premise gateway deployments.
Netherlands
Open-banking APIs and embedded finance expansion in Amsterdam and Rotterdam require granular machine-to-machine access controls. The Dutch Central Bank (DNB) supervises PSD2 compliance for payment service providers. Amsterdam's fintech corridor leads European adoption of API security technology alongside regulatory mandate alignment.
Poland
Underpenetrated mid-market manufacturing and logistics sectors in Warsaw and Krakow lack mature security operations centers. The Polish Financial Supervision Authority (KNF) implements NIS2 transposition deadlines for financial sector operators. Manufacturing clusters in Silesia create first-mover openings for virtual appliance deployments with license portability between private cloud and edge locations.
Europe Software Defined Perimeter Market Competitive Landscape
Player mix skews toward integrated network security vendors with established channel relationships across EU enterprise accounts. Tiered competitive structure separates cloud-native specialists from hardware-anchored incumbents and policy-as-code systems integrators. Dominant competitive moves include M&A for zero-trust capability augmentation and strategic partnerships for ENISA threat intelligence connector development.
Within the integrated network security tier, Cisco Systems and Fortinet occupy positions anchored by engineering density in next-generation firewall integration with SDP architectures. Zscaler exemplifies the cloud-native delivery archetype aligned with EU data sovereignty requirements. Systems integrators in Manchester and Munich capture margin pools from mid-market buyers unbundling implementation from software licensing.
| Leading Market Players |
|---|
| Verizon Communications |
| Cisco Systems |
| Fortinet |
| Akamai Technologies |
| Perimeter 81 |
| Zscaler |
| Check Point Software Tech |
| Cato Networks |
| Palo Alto Networks |
| Others |
Value Network & Pricing Analysis
Subscription contracts with tiered SaaS licensing lock in multi-year revenue visibility for European SDP vendors while binding mid-market buyers to predictable operational expenditure. These structures concentrate pricing power with cloud-native providers serving German automotive and Dutch fintech clusters.
Pricing Analysis
Certification level under EU Cybersecurity Act and ETSI specifications creates the primary spread between premium and standard tiers. Three-tier pricing structure across premium, standard, and economy levels anchors on hardware security module integration, managed policy orchestration, and self-service cloud delivery. Cost compression in standard tiers intensifies because mid-market manufacturing buyers in Poland and Czech Republic negotiate volume discounts. Government and defense buyers exhibit lowest price sensitivity due to sovereign cloud mandates.
Supply Chain Analysis
Germany and the United Kingdom anchor hardware security module production and cloud-native policy engine development. Israel and the United States feed specialized encryption IP and machine learning components. Single-source vulnerability in EU-based data center capacity creates exposure for multi-tenant architectures serving GDPR-sensitive workloads. Distribution runs through systems integrators in Manchester and Munich who unbundle implementation from software licensing.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Europe Software Defined Perimeter Market is cycling through a compliance-driven replacement wave as NIS2 deadlines compress procurement timelines across member states.
For Market Incumbents: Consolidate channel control through exclusive partnerships with Manchester and Munich systems integrators who capture mid-market policy orchestration contracts. Invest in ENISA threat intelligence connector development before public-sector tender eligibility gates tighten. Cloud-native specialists threaten hardware-anchored positions in Frankfurt banking clusters. For New Entrants and Emerging Players: Anchor in Polish and Czech manufacturing corridors where security operations center maturity lags and virtual appliance deployments face limited incumbent saturation. Target pharmaceutical and logistics firms with policy-as-code deployment services. Partner with regional value-added resellers to bypass direct enterprise sales friction. For Investors and Strategic Acquirers: Capital is best deployed toward cloud-native SDP specialists with pre-built EU AI Act compliance mappings and established GDPR Article 44 data localization architectures. Long-term viability hinges on sustained regulatory complexity rather than commoditized encryption. Watch for ENISA baseline recalibration as the inflection signal for compliance module refresh cycles.| Strategic Initiative | Industry Significance |
|---|---|
| ENISA Threat Intelligence Integration | Unlocks public-sector eligibility under German BSI and French ANSSI procurement frameworks. |
| EU AI Act Compliance Mapping | Captures healthcare and transport operator demand for auditable access logging architectures. |
| Managed Policy Orchestration Launch | Captures margin pools from Manchester and Munich pharmaceutical firms with limited security engineering. |
| Hardware Security Module Certification | Extends vendor qualification timelines but secures French defense and intelligence agency contracts. |
| API Security Platform Expansion | Aligns with Dutch Central Bank PSD2 mandates for Amsterdam fintech corridor micro-segmentation. |
Research Methodology
A spread of perspectives from CISOs at Frankfurt banking clusters, IT procurement officers at German automotive suppliers, policy engineers at Dutch fintechs, and integration specialists at Manchester systems integrators converged on the working assumptions. Secondary validation drew from ENISA threat intelligence reports, EU Cybersecurity Act certification databases, BSI IT-Grundschutz documentation, and hyperscaler European data center capex disclosures. Bottom-up deployment model sizing triangulated against top-down regulatory mandate coverage estimates.
Deployment model, organization size, vertical regulatory exposure, and cloud migration timeline shaped the segmentation dimensions modeled across the projection horizon. CAGRs derived from policy engine adoption curves calibrated to NIS2 transposition deadlines in Germany, France, and Italy. Forecast inputs included open-banking API proliferation rates and sovereign cloud procurement velocity under GDPR Article 44 constraints.
Decision-makers should treat outputs as directional under stable NIS2 enforcement intensity and continued EU AI Act risk classification expansion; material deviation would warrant model refresh. Specific risks include ENISA baseline recalibration, cross-border data residency litigation, and legacy mainframe integration failure at Italian and Spanish banks. Recalibration cycles align with material shifts in regulatory deadline schedules and threat intelligence feed standardization.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Endpoint Security Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Cyber Security Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Banking Cyber Security Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Global Ransomware Protection Market