
 Cybersecurity Software Market | 2026-2036
Cybersecurity Software Market Size, Share, and Industry Trends Forecast 2026-2036
Cybersecurity Software Market Analysis
Platform bundling is realigning procurement patterns across enterprise security stacks. Palo Alto Networks leverages integrated SASE and SOAR modules to anchor multi-year contracts. CrowdStrike differentiates through native XDR and identity threat detection, while Zscaler competes by dominating cloud-native SSE deployments without legacy appliance overhead.
Cybersecurity software encompasses programs, platforms, and services designed to detect, prevent, and respond to unauthorized access, malware, and data exfiltration across endpoints, networks, and cloud environments. These systems employ signature-based detection, behavioral analytics, and encryption protocols to protect digital assets and ensure operational continuity. Cloud Security within the Solution Type dimension is capturing the fastest expansion as workload migration accelerates, while Endpoint Security sustains the largest revenue pool due to persistent remote work infrastructure. The Deployment Model split reveals SaaS and Managed Security segments absorbing share from on-premises installations, with Hybrid configurations capturing margin from regulated industries requiring data residency controls.
The EU AI Act and NIS2 Directive impose mandatory incident reporting and supply-chain security assessments on critical service providers, directly expanding compliance-driven software procurement. In the United States, SEC cybersecurity disclosure rules and HIPAA enforcement by HHS OCR are compelling healthcare and publicly traded firms to upgrade continuous monitoring capabilities. Stakeholders must weigh sovereign data requirements against vendor consolidation trends when architecting multi-region security postures.
Market Dynamics
Zero-trust architecture mandates are compressing legacy perimeter security spend while redistributing procurement toward integrated cloud-native platforms that consolidate identity, network, and endpoint controls under unified policy engines.
Growth Catalysts
- NIS2 Directive:The EU's expanded incident reporting obligations for critical infrastructure operators are forcing energy and transport providers to deploy continuous monitoring suites.
- Cloud workload migration:Financial services institutions migrating core banking systems to sovereign cloud environments are procuring cloud security posture management tools at accelerated deployment schedules.
- Remote work infrastructure:Persistent hybrid workforce models sustain endpoint detection and response refresh cycles across healthcare and professional services verticals.
Market Restraints
- Skilled analyst scarcity:Security operations centers face acute shortages of professionals capable of tuning behavioral analytics and managing SOAR playbooks.
- Vendor concentration risk:Dominant cloud infrastructure providers in the United States control underlying compute and storage layers, creating dependency exposure for security software vendors.
- Encryption backdoor debates:Proposed lawful access mandates in multiple jurisdictions threaten to undermine zero-knowledge architecture credibility and slow enterprise adoption.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy facilities are merging IT and OT security stacks, creating demand for unified asset visibility platforms that span both domains.
- India's digital public infrastructure:The country's expanding critical infrastructure protection programs and data localization requirements are opening procurement channels for indigenous and foreign security vendors.
- AI-driven threat detection:Machine learning models trained on federated datasets are enabling predictive breach prevention without centralizing sensitive telemetry.
Industry Challenges
- Legacy system integration:Mainframe and custom-built applications in banking and government resist API-based security instrumentation, forcing expensive middleware development.
- Certification timeline compression:FedRAMP and ISO 27001 audit backlogs delay product launches for vendors targeting regulated industries, extending sales cycles by quarters.
- Alert fatigue management:Security teams drowning in false-positive noise require substantial professional services investment to tune detection thresholds effectively.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cybersecurity Software Market |
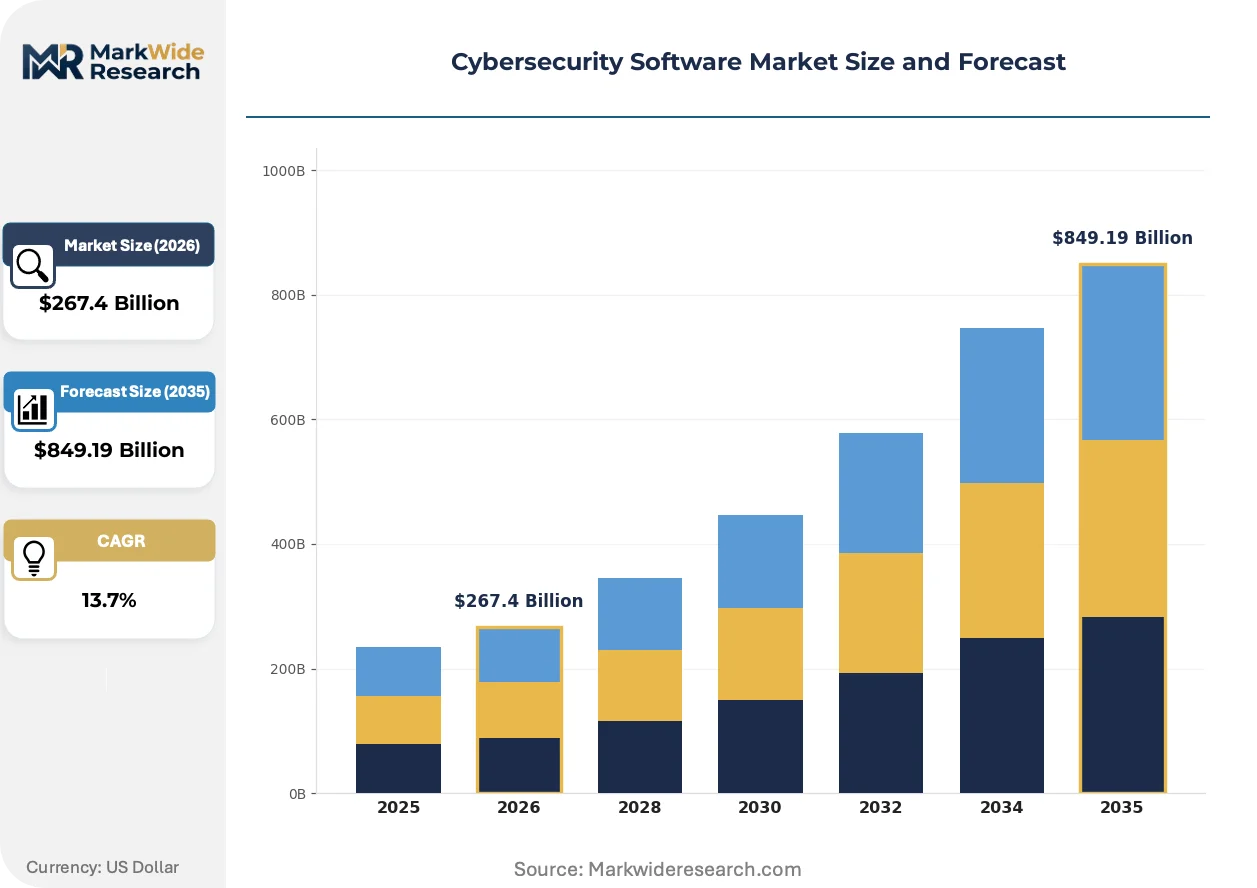
| Market Size in 2026 | $267.4 Billion |
| Market Size in 2035 | $849.19 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Security, Network Security, Application Security, Cloud Security Deployment Model: On-Premises, SaaS, Hybrid, Managed Security End User: SMBs, Enterprises, Government, Healthcare Compliance Standard: GDPR, HIPAA, PCI DSS, ISO 27001 |
| Companies Covered | Zscaler, Cisco Systems, Palo Alto Networks, Microsoft, Check Point Software Technologies, CrowdStrike, Cloudflare, Trend Micro, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cybersecurity Software Market Emerging Trajectories
Security platform consolidation is eliminating point-solution vendors while regulatory fragmentation across jurisdictions forces architectural flexibility. Buyers now prioritize vendors demonstrating cross-border compliance automation.
Extended detection and response platforms are consolidating endpoint, network, and identity telemetry into unified investigation workflows. Mid-market enterprises without dedicated SOAR teams adopt these suites to compress mean-time-to-response. Native XDR is consolidating security operations center tooling spend previously distributed across six to eight discrete vendors.
The EU AI Act's risk-based classification system imposes documentation and human oversight requirements on security products employing machine learning for threat scoring. Vendors must now maintain algorithmic audit trails and explainability interfaces. High-risk system providers serving European critical infrastructure are redesigning product roadmaps to embed compliance-by-design.
Enterprise buyers now demand consumption-based licensing aligned with actual protected asset counts rather than upfront enterprise agreements. Managed security service providers are capturing this preference shift through bundled detection and response subscriptions. Germany's Mittelstand manufacturing sector exhibits the most pronounced migration toward outsourced security operations.
Cybersecurity Software Market Segmentation
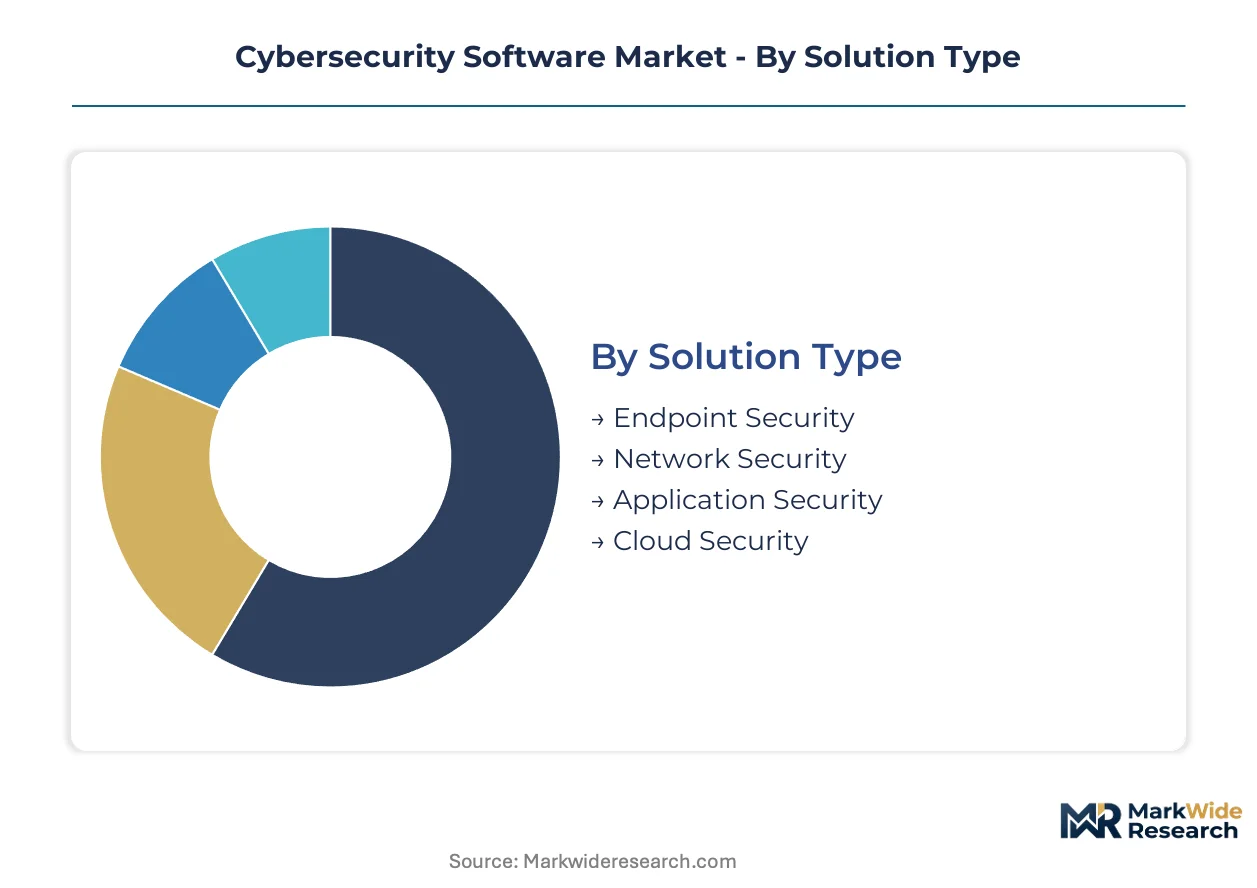
Procurement patterns in cybersecurity software diverge sharply across organizational scale, regulatory exposure, and infrastructure maturity. Vendors architect product tiers specifically to capture spend from regulated enterprises versus cost-constrained mid-market buyers.
Solution Type:
Supply concentration among integrated platform vendors is compressing point-solution margins and forcing specialization around cloud-native or OT-specific capabilities.
- Endpoint Security:Agent-based detection systems deploy across laptops, servers, and mobile devices to intercept malware and unauthorized access attempts. Healthcare systems in the United States sustain refresh cycles here due to HIPAA enforcement by HHS OCR and persistent remote clinical workflows. This segment absorbs the bulk of installed capacity; Cloud Security is expanding most quickly.
- Cloud Security:Cloud security posture management and workload protection platforms monitor misconfigurations and runtime threats across multi-tenant environments. German financial institutions migrating to sovereign cloud infrastructure are procuring these tools under accelerated timelines driven by BaFin operational resilience requirements.
- Network Security:Firewalls, intrusion detection systems, and zero-trust network access enforce perimeter and microsegmentation policies.
- Application Security:Static and dynamic testing tools plus runtime application self-protection secure DevOps pipelines and production codebases.
Endpoint Security commands the largest revenue pool due to persistent distributed workforces; Cloud Security climbs the fastest as workload migration accelerates.
Deployment Model:
Cost tier differentiation separates capital-intensive on-premises installations from consumption-based SaaS alternatives, with hybrid configurations capturing margin from regulated industries requiring data residency controls.
- SaaS:Cloud-delivered security services eliminate hardware procurement and reduce time-to-deployment from quarters to weeks. Indian SMBs scaling digital operations favor this model due to minimal upfront investment and TRAI-mandated data localization compliance frameworks.
- Managed Security:Outsourced security operations centers deliver 24/7 monitoring, threat hunting, and incident response through subscription contracts. Germany's Mittelstand manufacturing sector exhibits pronounced migration here as family-owned firms lack internal analyst capacity.
- On-Premises:Self-hosted security infrastructure maintains full data control within organizational perimeters.
- Hybrid:Split deployments combine on-premises control planes with cloud-delivered threat intelligence and analytics.
SaaS captures the greatest share of new procurement; Managed Security demonstrates the steepest expansion trajectory among deployment alternatives.
End User:
Application context dictates feature requirements, with government and healthcare buyers prioritizing audit trails and certification documentation over speed-to-deployment.
- Enterprises:Large organizations deploy integrated security platforms spanning identity, endpoint, network, and cloud controls under unified policy engines. United States publicly traded firms drive demand here as SEC cybersecurity disclosure rules mandate continuous monitoring and rapid incident reporting.
- Government:National and local agencies require FedRAMP or equivalent certification, air-gapped deployments, and supply-chain security attestations. India's critical infrastructure protection programs are opening procurement channels for indigenous and foreign vendors serving this segment.
- SMBs:Resource-constrained organizations prioritize simplified deployment and managed service overlays.
- Healthcare:Hospitals and payers face stringent patient data protection requirements under jurisdiction-specific privacy regimes.
Enterprises absorb the bulk of installed capacity; Government is gaining share fastest as sovereign cyber defense investments accelerate.
Compliance Standard:
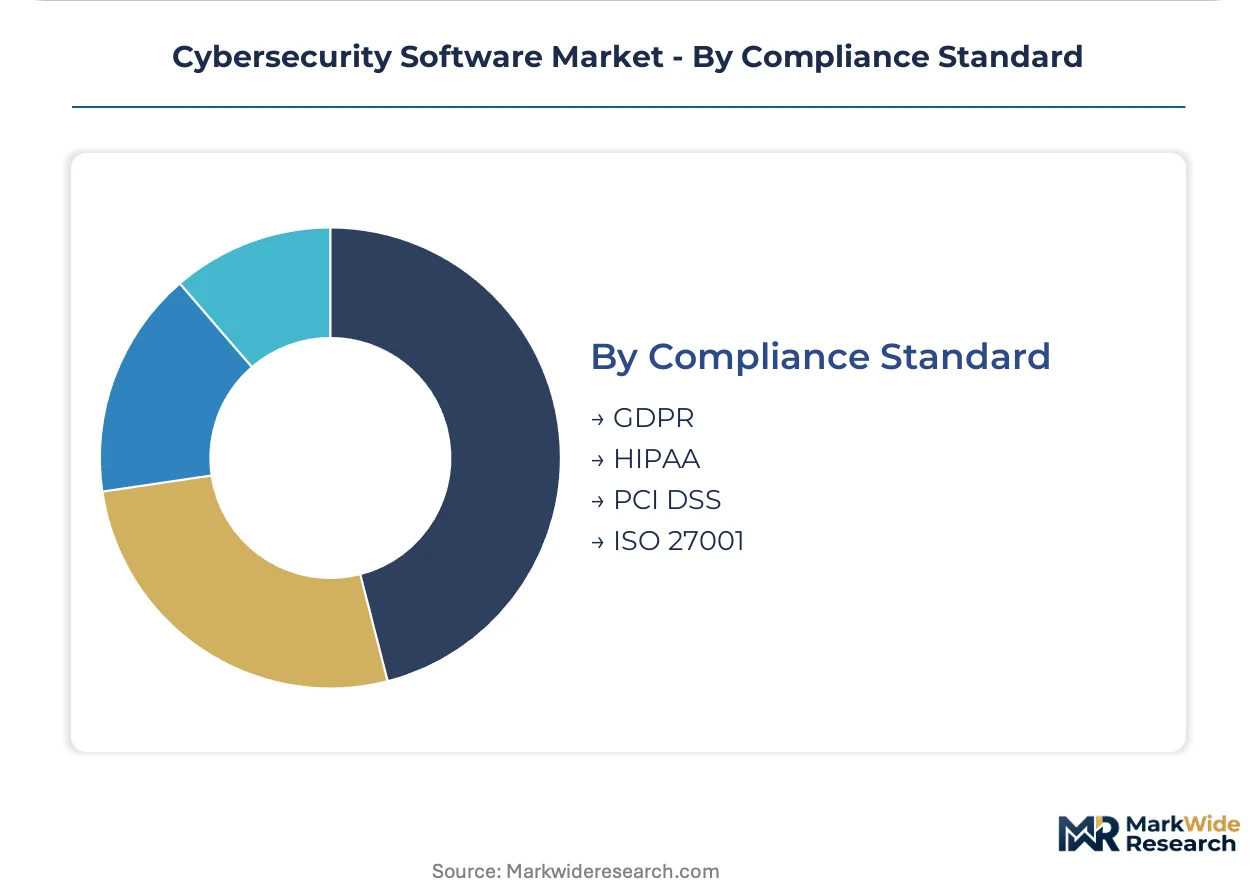
Maturity levels across certification frameworks create pricing stratification, with ISO 27001 and PCI DSS commanding premiums over self-attested alternatives due to audit rigor and cross-border recognition.
- GDPR:EU data protection mandates impose breach notification timelines, data minimization requirements, and privacy-by-design obligations on security software processing personal information. Vendors serving European critical infrastructure are redesigning product roadmaps to embed algorithmic audit trails under EU AI Act convergence pressures.
- HIPAA:United States healthcare privacy and security rules enforce access controls, encryption standards, and audit logging for protected health information. HHS OCR enforcement actions are compelling healthcare systems to upgrade continuous monitoring capabilities and document security risk assessments.
- PCI DSS:Payment card industry standards mandate network segmentation, vulnerability management, and access controls for cardholder data environments.
- ISO 27001:International information security management standards provide certifiable frameworks for risk assessment and control implementation.
GDPR-aligned solutions command the largest addressable market; HIPAA-specific tooling is climbing fastest as healthcare cyberattacks intensify regulatory scrutiny.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Special economic zones in India and sovereign cloud mandates across Germany are concentrating procurement for zero-trust infrastructure. These jurisdictional programs redistribute security software demand toward compliant vendors.
United States
SEC cybersecurity disclosure rules and HIPAA enforcement by HHS OCR compel healthcare systems and publicly traded firms to upgrade continuous monitoring. FedRAMP certification backlogs delay product launches for vendors targeting federal agencies. The Washington DC metro corridor anchors demand from defense contractors and intelligence-adjacent enterprises procuring air-gapped security stacks.
Germany
BaFin operational resilience requirements accelerate cloud security posture management procurement among financial institutions migrating to sovereign infrastructure. The EU AI Act and NIS2 Directive impose mandatory incident reporting obligations on critical service providers. Bavaria's Mittelstand manufacturing belt exhibits pronounced migration toward outsourced security operations as family-owned firms lack internal analyst capacity.
India
TRAI-mandated data localization frameworks and expanding critical infrastructure protection programs open procurement channels for indigenous and foreign vendors. The country's digital public infrastructure investments concentrate demand in Maharashtra and Karnataka. Mumbai and Bangalore anchor cloud-native security adoption among SMBs scaling digital operations with minimal upfront investment.
United Kingdom
NCSC cyber assessment frameworks and post-Brexit data adequacy negotiations reshape vendor selection criteria for financial services and healthcare. The UK GDPR retains EU-aligned breach notification timelines while diverging on automated decision-making rules. London's fintech cluster drives demand for cloud-native SSE deployments without legacy appliance overhead.
Japan
METI cybersecurity supply chain guidelines and critical infrastructure protection standards compel manufacturing and energy operators to merge IT and OT security stacks. Domestic vendors face pressure to demonstrate cross-border compliance automation for European export markets. Tokyo and Osaka anchor enterprise procurement of unified asset visibility platforms spanning operational technology convergence.
Cybersecurity Software Market Vendor Landscape
Diversified conglomerates compete with focused pure-play specialists across the cybersecurity software landscape. Platform consolidation eliminates point-solution vendors while regulatory fragmentation forces architectural flexibility. Three archetypes dominate: integrated platform vendors anchoring multi-year contracts, cloud-native specialists dominating SSE deployments, and identity-centric vendors consolidating XDR and threat detection. Competitive moves concentrate on M&A for capability gaps and strategic partnerships for sovereign cloud localization.
Within the integrated platform tier, Palo Alto Networks and CrowdStrike occupy positions exemplifying divergent bundling strategies. Zscaler represents the cloud-native specialist archetype, anchoring deployments without legacy infrastructure overhead. These three entities illustrate how vendor consolidation and architectural specialization reshape procurement patterns across enterprise security stacks.
| Leading Market Players |
|---|
| Zscaler |
| Cisco Systems |
| Palo Alto Networks |
| Microsoft |
| Check Point Software Technologies |
| CrowdStrike |
| Cloudflare |
| Trend Micro |
| Fortinet |
| Others |
Supply Flow & Price Mechanics
Cloud-native security delivery architectures are compressing infrastructure costs while redistributing value capture toward software vendors with direct hyperscaler partnerships, simultaneously flattening traditional channel markups and concentrating procurement leverage among platform consolidators.
Pricing Analysis
Short lead-time deployments command premium positioning in enterprise security procurement, with FedRAMP-authorized vendors extracting 15-30% uplifts over uncertified alternatives for identical feature sets. Subscription-based SaaS tiers dominate, with price differentiation resting on compliance certification grade and integration complexity rather than core detection capability. Cost compression in mid-market endpoint security is intensifying because CrowdStrike and Microsoft are bundling EDR into broader platform contracts. Healthcare systems exhibit the least price sensitivity due to HIPAA enforcement exposure, while Indian SMBs scaling digital operations demonstrate acute cost consciousness favoring consumption-based models.
Supply Chain Analysis
India's data localization mandates and Germany's sovereign cloud requirements are reshaping vendor sourcing strategies, forcing foreign security providers to establish domestic development centers and local hosting partnerships. Supply concentration centers on the United States for core threat intelligence infrastructure, Israel for specialized cryptography and endpoint innovation, and Ireland for EU data residency compliance. Component dependencies include hyperscaler compute capacity from AWS, Azure, and GCP, proprietary machine learning training datasets, and third-party vulnerability intelligence feeds. Single-source vulnerability runs through concentrated threat intelligence aggregation, where three commercial providers supply the majority of IOC feeds. Distribution runs through direct enterprise sales teams, managed security service providers, and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Zero-trust architecture mandates are displacing legacy perimeter security spend, creating a technology-transition phase where identity-centric platforms replace firewall-centric infrastructure across regulated industries.
For Market Incumbents: Deploy platform bundling as the primary defensive lever. Consolidate endpoint, identity, and cloud security modules under unified policy engines to anchor multi-year enterprise contracts and raise switching costs. Counter cloud-native specialists by embedding SOAR automation and managed detection response services that mid-market buyers cannot replicate internally. Invest in FedRAMP and EU sovereign cloud certifications to defend against emerging regional challengers in India and Germany. For New Entrants and Emerging Players: Mid-market manufacturing firms in Germany's Mittelstand belt represent the most penetrable buyer archetype, lacking internal SOC capacity and resisting incumbent platform complexity. Target OT-IT convergence use cases in energy and industrial facilities where legacy vendors lack unified asset visibility. Pursue channel partnerships with regional managed security service providers rather than direct enterprise sales to compress customer acquisition costs. For Investors and Strategic Acquirers: Exit pathways concentrate in platform consolidation by hyperscalers and private equity rollups of regional compliance specialists. Long-term viability favors vendors with demonstrated cross-border automation for GDPR, HIPAA, and emerging AI Act requirements. Acquisition targets should demonstrate embedded algorithmic audit trails and explainability interfaces. Watch NIS2 enforcement timelines as the critical inflection signal for compliance-driven procurement acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidating XDR, identity, and cloud security modules compresses customer switching costs and extends contract duration. |
| Sovereign Cloud Partnership | Localization agreements with German and Indian hosting providers satisfy BaFin and TRAI data residency mandates. |
| AI Compliance Certification | EU AI Act documentation and human oversight interfaces unlock critical infrastructure procurement channels. |
| OT-IT Convergence Development | Unified asset visibility spanning manufacturing and energy operational technology creates defensible specialization. |
| Managed Security Service Expansion | 24/7 SOC outsourcing captures Mittelstand manufacturing demand from analyst-constrained family enterprises. |
Methodological Framework
Independent corroboration across CISO interviews, channel partner assessments, and regulatory filing analysis underwrites the qualitative findings in this study. Primary fieldwork encompassed conversations with chief information security officers at financial services and healthcare systems, IT procurement officers at German manufacturing firms, platform engineers at hyperscaler security marketplaces, and integration specialists deploying zero-trust architectures. Secondary validation drew from SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, FedRAMP authorization databases, and TRAI data localization compliance records. Bottom-up deployment estimates triangulated against top-down security software spend reported in enterprise technology budgets.
Rate-of-change decomposition across the analysis window separates baseline security expenditure from incremental zero-trust migration and compliance-driven replacement cycles. Segmentation dimensions modeled include deployment model, organization size, vertical regulatory exposure, integration complexity, and regional adoption pattern. CAGRs were derived from fitted growth curves calibrated to disclosed vendor bookings and procurement pipeline data. Forecast inputs incorporated FedRAMP authorization backlog timelines, NIS2 enforcement phase-in schedules, and sovereign cloud infrastructure buildout trajectories.
Revisions become necessary when encryption backdoor legislation advances, hyperscaler security service bundling accelerates, or major breach events trigger regulatory enforcement surges beyond modeled baselines. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Antivirus Software Market
Security Software
Data Leakage Prevention Product Market
Security Software
Antivirus Software Package Market
Security Software
Public Key Infrastructure (PKI) Market
Security Software
Stalkerware Market
Security Software
Global Wireless Intrusion Prevention System Market
Security Software
Global Data Loss Prevention Software Market
Security Software
Global Background Screening Market
Security Software
Fraud Detection Software Market
Security Software
Security Information and Event Management Software Market
Security Software
Global Security Software in Telecom Market
Security Software
Consumer Endpoint Security Market
Security Software
Global Error Monitoring Software Market
Security Software
Extended Detection and Response Market
Security Software
Europe IP Video Intercom Device and Equipment Market
Security Software
Data Privacy Software Market