
 Public Cloud Management and Security Services Market | 2026-2036
Public Cloud Management and Security Services Market Size, Share, and Industry Trends Forecast 2026-2036
Public Cloud Management and Security Services Market Analytics
Subscription-based security monitoring is rebalancing what enterprises procure as a bundled operational expense rather than capital deployment. Amazon Web Services anchors the infrastructure layer with native threat detection tooling. Microsoft extends its identity management stack through Entra and Purview integration. Palo Alto Networks competes via cloud-native firewall platforms that span multi-tenant environments.
Public cloud management and security services encompass the orchestration, governance, and protection of compute, storage, and network resources delivered through third-party hyperscale platforms, typically governed by shared responsibility models that delineate provider versus customer obligations. These services employ automated policy enforcement, encryption key lifecycle management, and continuous compliance scanning to maintain operational integrity across distributed workloads. Managed services within the Service Type dimension command the deepest margin pools due to long-term contractual attach rates and specialized labor scarcity. Multi-Cloud deployment configurations generate the fastest expansion trajectory as organizations resist single-vendor concentration risk. AI-Based Security technology segments attract disproportionate R&D allocation from vendors seeking predictive threat remediation capabilities.
Enterprise demand for public cloud security services now faces binding constraints from GDPR data localization rules in Europe, SEC cybersecurity disclosure mandates in the United States, and China's GB standards for cross-border data transfer governance. Regulatory fragmentation compels service providers to maintain jurisdiction-specific compliance certifications that inflate operational overhead but create defensive moats against unqualified competitors. Stakeholders must evaluate whether their current vendor portfolios can satisfy emerging sector-specific requirements in healthcare, defense, and critical infrastructure without architectural overhaul.
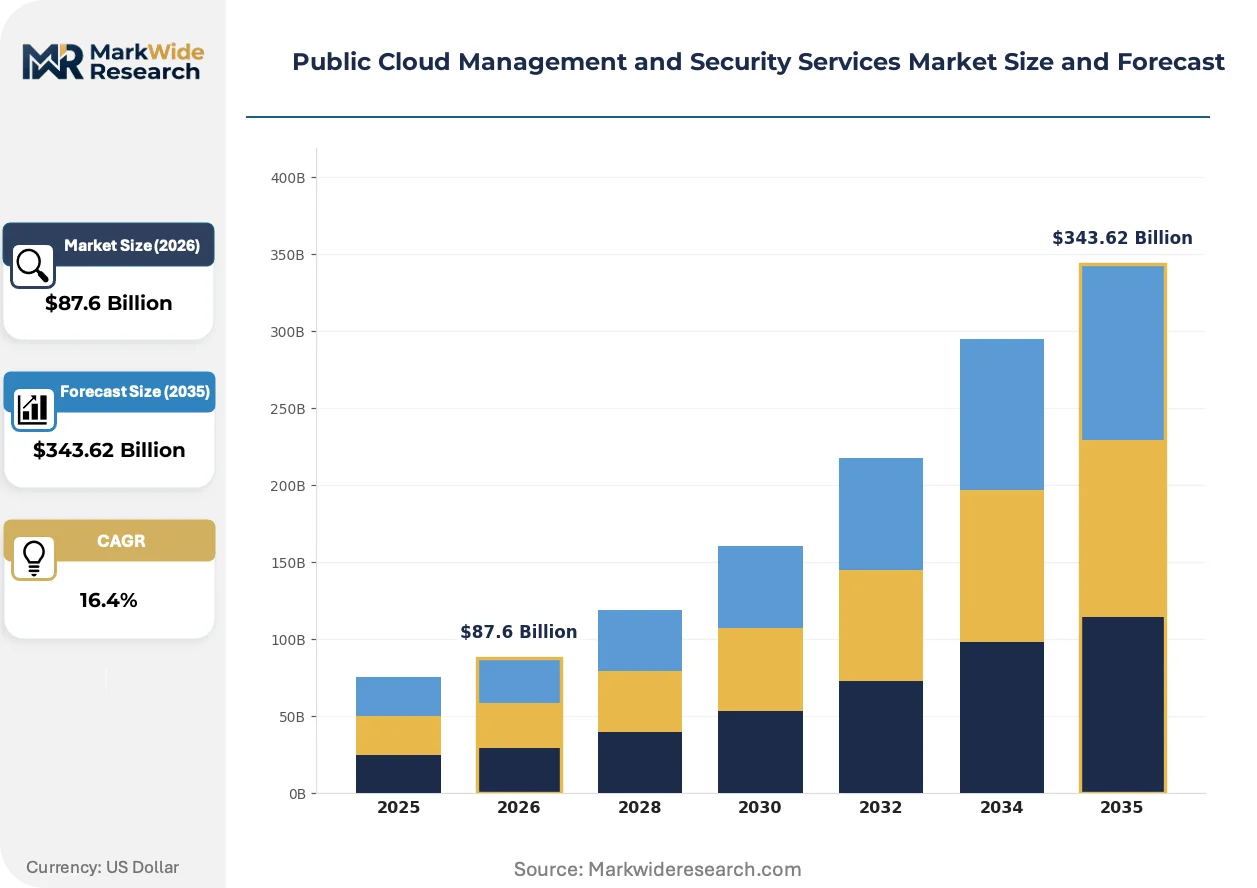
Market Dynamics
Regulatory fragmentation across data sovereignty regimes is forcing hyperscale providers to architect jurisdiction-specific compliance stacks, inflating operational overhead while creating defensive certification barriers against unqualified entrants.
Growth Catalysts
- EU AI Act enforcement:Risk-based classification of AI systems compels financial services firms to deploy automated compliance scanning and audit trails for cloud-hosted machine learning workloads.
- Industrial IoT expansion:German manufacturing conglomerates require sovereign cloud architectures with localized encryption key management to satisfy GDPR data residency guarantees for operational technology data streams.
- Zero-trust architecture mandates:US federal procurement guidelines now require continuous identity verification and micro-segmentation, accelerating replacement of perimeter-based security models in government contractor supply chains.
Market Restraints
- Specialized labor scarcity:Cloud security architects with multi-tenant environment expertise command compensation premiums that compress managed services margins and extend implementation timelines.
- Input cost volatility:GPU cluster pricing for AI-based threat detection fluctuates with semiconductor foundry capacity allocation, destabilizing consumption-based pricing models.
- Regulatory friction:China's GB standards for cross-border data transfer governance impose architectural constraints that prevent unified global deployments, fragmenting operational scale economies.
Strategic Opportunities
- Underpenetrated healthcare vertical:HIPAA-covered entities in the United States lag in cloud-native security adoption, presenting first-mover advantage for vendors with healthcare-specific compliance automation.
- Edge-to-cloud orchestration convergence:Integration of Kubernetes security posture management with 5G network slicing creates new service categories for telecommunications infrastructure operators.
- CSRD disclosure mandates:European sustainability reporting requirements drive demand for carbon-aware workload scheduling and renewable energy attribution tools within cloud management platforms.
Industry Challenges
- Multi-cloud skill fragmentation:Security teams struggle to maintain operational proficiency across divergent native tooling from AWS, Azure, and Google Cloud, elevating incident response latency.
- Certification timeline compression:FedRAMP and ISO 27001 audit cycles now exceed eighteen months, delaying market entry for emerging vendors and freezing procurement decisions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Public Cloud Management and Security Services Market |
| Market Size in 2026 | $87.6 Billion |
| Market Size in 2035 | $343.62 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Services, Security Assessment, Risk Management, Compliance Services Deployment Model: Single Cloud, Multi-Cloud, Hybrid Cloud, Community Cloud End User: Large Enterprises, SMEs, Government, Education Technology: AI-Based Security, Data Encryption, Identity Management, Threat Detection |
| Companies Covered | Amazon Web Services, Microsoft, Google Cloud, IBM Corporation, Oracle Corporation, Cisco Systems, Palo Alto Networks, VMware Inc., Fortinet Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Public Cloud Management and Security Services Market Evolving Landscape
Security service delivery is pivoting from reactive threat response toward predictive remediation through embedded artificial intelligence, while regulatory complexity forces architectural specialization that resists standardization.
Confidential computing hardware is converging with cloud-native application development to enable encrypted-in-use processing for sensitive workloads. Financial services institutions in Frankfurt and Singapore are deploying Intel SGX and AMD SEV-enabled instances for quantitative trading algorithms. This capability is converging with existing Kubernetes orchestration patterns, compressing the traditional boundary between infrastructure security and application-layer protection.
The EU AI Act's risk-based classification system imposes documentation and human oversight obligations on high-risk AI deployments. Cloud providers must now maintain audit trails for training data provenance and model versioning across their managed machine learning platforms. Healthcare and recruitment technology segments face the steepest compliance burden, driving procurement preference toward vendors with pre-certified sovereign cloud instances.
Consumption-based security licensing is displacing perpetual seat models as enterprises seek variable cost alignment with cloud workload scaling. Managed detection and response services now price per terabyte of log ingestion rather than per endpoint protected. This pattern is most visible among mid-market enterprises in the United States, where CFO pressure for OpEx optimization overrides traditional procurement evaluation cycles.
Public Cloud Management and Security Services Market Segmentation
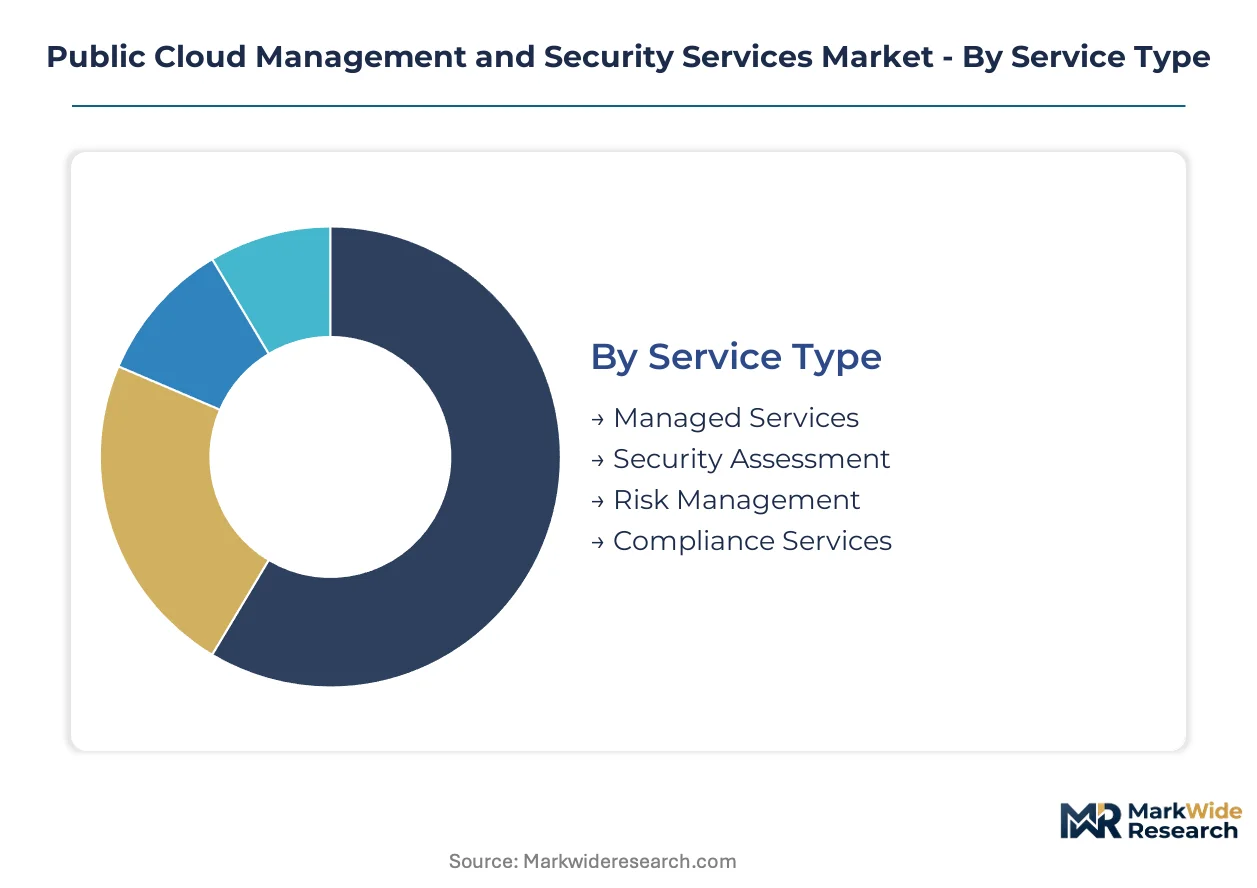
Segmentation in public cloud security services reveals how procurement priorities diverge across operational complexity, regulatory exposure, and technical maturity. Service providers configure delivery models differently depending on whether buyers seek bundled operational support or point solutions for specific compliance gaps.
Service Type:
Customization intensity varies sharply across this category, from fully tailored managed services to standardized assessment toolkits.
- Managed Services:Continuous monitoring, incident response, and policy enforcement delivered under long-term contracts with specialized labor attachments. Financial services firms in Frankfurt and Singapore drive premium demand for 24/7 security operations center coverage tied to EU AI Act documentation requirements.
- Security Assessment:Point-in-time vulnerability scanning, penetration testing, and configuration audits delivered as project-based engagements. Mid-market enterprises in the United States favor consumption-based pricing for these services to align with OpEx optimization mandates from CFO offices.
- Risk Management:Quantitative cyber risk modeling and third-party vendor security scoring.
- Compliance Services:Automated control mapping, audit preparation, and jurisdiction-specific certification maintenance.
Leading the category by volume: Managed Services. Growing fastest: Compliance Services.
Deployment Model:
Cost tier separation distinguishes this category, with single-cloud deployments commanding lowest unit economics and multi-cloud configurations carrying integration premiums.
- Multi-Cloud:Orchestration across AWS, Azure, and Google Cloud environments with unified policy enforcement and cost optimization. German industrial conglomerates require this architecture to satisfy GDPR data residency guarantees while avoiding single-vendor concentration risk.
- Hybrid Cloud:Integrated on-premises and public cloud infrastructure with consistent security posture management. Healthcare providers in the United States deploy this model to keep protected health information on-site while bursting analytics workloads to cloud infrastructure.
- Single Cloud:Native security tooling within one hyperscale provider ecosystem.
- Community Cloud:Shared infrastructure for specific industry verticals with common compliance requirements.
Multi-Cloud deployments carry the highest revenue per customer. Single Cloud retains the largest installed base.
End User:
Customer type determines procurement sophistication, with large enterprises negotiating enterprise license agreements and government buyers requiring FedRAMP certification.
- Large Enterprises:Global organizations with dedicated cloud security architects and multi-year transformation roadmaps. These buyers command dedicated customer success teams and custom service level agreements from managed security providers.
- Government:Federal, state, and local agencies with classified or controlled unclassified information handling requirements. US federal contractors now face zero-trust architecture mandates that accelerate replacement of perimeter-based security models.
- SMEs:Mid-market organizations purchasing standardized security packages through channel partners.
- Education:Universities and K-12 districts with limited security staffing and grant-funded procurement cycles.
Large Enterprises generate the deepest margin pools. Government vertical shows the steepest expansion trajectory.
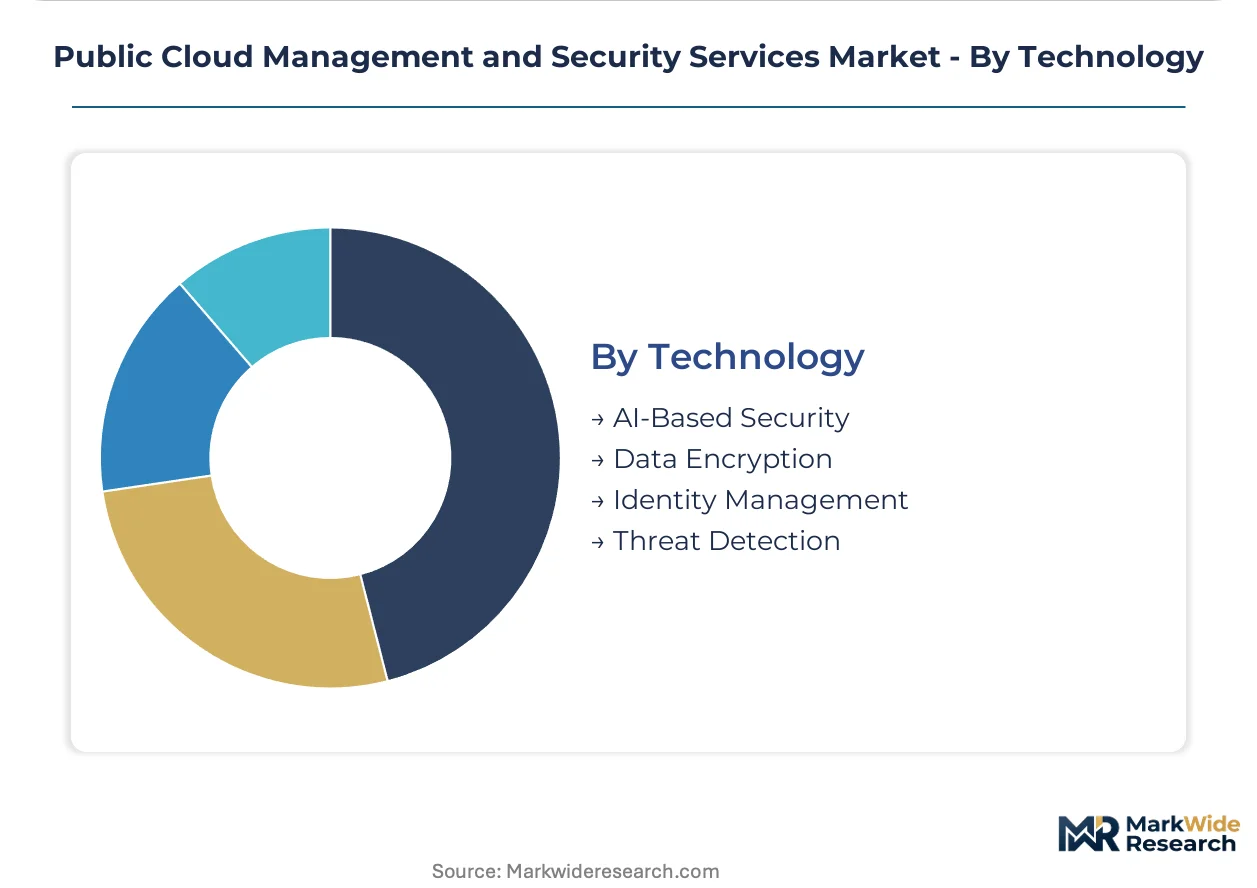
Technology:
Application maturity separates this category, with identity management representing established infrastructure and AI-based security attracting disproportionate R&D allocation.
- AI-Based Security:Machine learning models for behavioral anomaly detection, automated threat hunting, and predictive remediation. GPU cluster pricing volatility for these workloads destabilizes consumption-based pricing models for service providers.
- Identity Management:Single sign-on, privileged access management, and continuous authentication across distributed workforces. Microsoft extends market position through Entra integration with existing productivity suite deployments.
- Data Encryption:Key lifecycle management and confidential computing for encrypted-in-use processing.
- Threat Detection:Real-time log analysis and security information and event management correlation.
Identity Management anchors the largest revenue base. AI-Based Security climbs the fastest amid vendor competition for predictive capabilities.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cloud security consumption concentrates in financial centers and industrial hubs, while infrastructure deployment gravitates toward data sovereignty zones. Germany and Singapore anchor production capacity for confidential computing hardware, whereas the United States and United Kingdom drive service consumption through enterprise procurement.
United States
Financial services firms in New York and Chicago propel demand for AI-based threat detection and zero-trust architecture implementations. SEC cybersecurity disclosure mandates now require continuous audit trails for cloud-hosted trading infrastructure. Silicon Valley technology clusters and Northern Virginia data center corridors concentrate managed security operations center capacity.
Germany
Industrial conglomerates in Munich and Stuttgart require sovereign cloud architectures with localized encryption key management for operational technology data streams. GDPR data residency guarantees and EU AI Act risk classification rules compel domestic infrastructure deployment. Frankfurt's financial district anchors continental Europe's deepest pool of cloud security architects.
United Kingdom
London-based hedge funds and insurance underwriters drive procurement of confidential computing instances for quantitative risk modeling. The Financial Conduct Authority's operational resilience requirements mandate multi-region failover capabilities. Edinburgh and Manchester emerging technology clusters specialize in healthcare cloud compliance automation.
Singapore
Asset management firms and commodity trading houses demand encrypted-in-use processing for cross-border transaction data. The Monetary Authority of Singapore's Technology Risk Management Guidelines impose strict vendor risk management protocols. One-North and Changi Business Park concentrate Asia-Pacific security operations center delivery capacity.
Japan
Automotive manufacturers in Toyota City and electronics conglomerates in Osaka require hybrid cloud security posture management for connected vehicle data. METI's data free flow with trust initiatives shape cross-border governance frameworks. Tokyo's Marunouchi financial district anchors domestic demand for identity management integration.
Public Cloud Management and Security Services Market Competitive Landscape
Capital-heavy infrastructure operators compete with asset-light platform specialists for enterprise security budgets. Hyperscale cloud providers anchor the market with native tooling integration, while independent software vendors carve defensive positions through multi-cloud orchestration capabilities. Three archetypes dominate: vertically integrated hyperscalers, cloud-native security specialists, and legacy infrastructure vendors pivoting toward SaaS delivery. Competitive dynamics center on certification acquisition velocity and managed services attach rates.
Within the hyperscaler tier, Amazon Web Services and Microsoft exemplify platform-integrated security delivery, bundling threat detection with compute consumption. Palo Alto Networks occupies a position among cloud-native specialists competing through firewall abstraction across tenant environments. These three anchors represent divergent strategic postures: infrastructure lock-in versus best-of-breed flexibility versus network-centric legacy extension.
| Leading Market Players |
|---|
| Amazon Web Services |
| Microsoft |
| Google Cloud |
| IBM Corporation |
| Oracle Corporation |
| Cisco Systems |
| Palo Alto Networks |
| VMware Inc. |
| Fortinet Inc. |
| Others |
Value Network & Pricing Analysis
EU AI Act documentation mandates from financial services buyers in Frankfurt and Singapore are forcing managed security providers to absorb specialized labor premiums, compressing margins and accelerating consumption-based pricing adoption across compliance-heavy segments.
Pricing Analysis
Margin tightening in managed detection and response services reflects GPU cluster pricing volatility for AI-based threat detection workloads. Three-tier pricing structure across enterprise, mid-market, and SME levels stratifies by compliance certification depth and 24/7 security operations center coverage. Cost-down pressure on standardized assessment toolkits accelerates because CFO offices in US mid-market enterprises demand OpEx alignment with cloud workload scaling. Government buyers show least price sensitivity due to FedRAMP certification scarcity, while education verticals face acute budget constraints.
Supply Chain Analysis
Refurbished confidential computing hardware from decommissioned Frankfurt financial services deployments feeds secondary markets for encrypted-in-use processing capability. Supply concentrates in Taiwan for GPU semiconductor fabrication, Ireland for EU data sovereignty infrastructure, and Northern Virginia for security operations center labor pools. Raw material dependencies span advanced packaging substrates, specialized cooling systems, and jurisdiction-specific encryption modules. Single-source vulnerability in Intel SGX and AMD SEV chip supply creates procurement risk. Distribution runs through hyperscale direct sales teams, channel partners for mid-market penetration, and systems integrators for government contracts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Certification timeline compression exceeding eighteen months for FedRAMP and ISO 27001 is forcing subscale vendors toward distressed exits, creating acquisition opportunities for well-capitalized platforms.
For Market Incumbents: Hedge against multi-cloud skill fragmentation by acquiring Kubernetes security posture management specialists with pre-built Azure-AWS-Google Cloud orchestration layers. Prioritize backward integration into sovereign cloud infrastructure in Germany to capture EU AI Act compliance premiums before regional competitors consolidate localized encryption key management capabilities.
For New Entrants and Emerging Players: HIPAA-covered entities in the United States represent the most penetrable buyer archetype, with cloud-native security adoption lagging behind financial services by several procurement cycles. Target healthcare-specific compliance automation with pre-mapped control frameworks, selling through channel partners that already service hospital group purchasing organizations.
For Investors and Strategic Acquirers: The window for entry favors managed security providers with existing FedRAMP authorization and healthcare vertical expertise. Long-term viability hinges on attach rates for AI-based threat detection consumption, with GPU cluster pricing volatility serving as the critical inflection signal for margin sustainability across the projection horizon.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies AWS, Azure, and Google Cloud policy enforcement for German industrial conglomerates. |
| Acquisition of Specialist Firm | Captures Kubernetes security posture management talent amid multi-cloud skill scarcity. |
| Geographic Expansion | Establishes sovereign cloud instances in Frankfurt to satisfy EU AI Act documentation requirements. |
| Strategic Partnership | Links confidential computing hardware vendors with 5G network slicing operators for edge orchestration. |
| Product Launch | Introduces carbon-aware workload scheduling tools aligned with European CSRD disclosure mandates. |
Research Methodology
Document review covered hyperscaler capex disclosures, SEC 10-K filings from publicly traded security vendors, and EU regulatory filings, complemented by interviews with CISOs at financial services firms, cloud security architects at German industrial conglomerates, procurement officers at US healthcare systems, and channel partners serving mid-market enterprises. Secondary validation drew from FedRAMP authorization databases, ISO 27001 certification registries, and compliance automation vendor pricing disclosures. Bottom-up service revenue estimates triangulated against top-down IT security spending benchmarks.
Segment-level outputs across the analysis window reflect deployment model, organization size, vertical regulatory exposure, technology maturity, and geographic data sovereignty requirements. CAGRs derive from regression analysis of historical procurement velocity against regulatory mandate implementation timelines. Industry-specific forecast inputs include EU AI Act enforcement schedules and FedRAMP authorization pipeline data.
Revisions become necessary when semiconductor foundry capacity allocation shifts, sovereign cloud infrastructure investments accelerate, or regulatory fragmentation deepens beyond modeled jurisdictional complexity. Practitioners should monitor GPU cluster pricing volatility, certification backlog durations, and healthcare vertical procurement cycle lengths for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Mobile Data Protection Solutions and Services Market
Security Software
Global Secure Access Service Edge Market
Security Software
Hardware OTP Token Authentication Market
Security Software
Unified Threat Management (UTM) Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Global Hardware Security Modules (HSM) Market
Security Software
Software Defined Perimeter (SDP) Market
Security Software
Global Data Breach Notification Software Market
Security Software
Remote Access Management Market
Security Software
Global Consumer Identity and Access Management Market
Security Software
Business Email Compromise (BEC) Market
Security Software
Battery-Powered Doorbell Camera Market
Security Software
Keystroke Dynamics Market
Security Software
Secaas Market
Security Software
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market