
 Global Dynamic Application Security Testing Market | 2026-2036
Global Dynamic Application Security Testing Market Size, Share, and Industry Trends Forecast 2026-2036
Global Dynamic Application Security Testing Market Intelligence
The customer base for dynamic application security testing is expanding beyond large enterprises to encompass a fragmented set of small and medium-sized businesses. This shift creates new opportunities for vendors. Checkmarx leverages its comprehensive platform to serve large, complex organizations. In contrast, Invicti specializes in automated scanning solutions suitable for teams of all sizes. Veracode positions its offerings to support secure software development lifecycles across diverse industries.
Dynamic application security testing is a black-box security analysis method that examines applications during runtime. It simulates external attacks to identify vulnerabilities such as SQL injection and cross-site scripting without needing source code access. Cloud-based deployment models dominate the market due to their flexibility and scalability for modern development workflows. While web applications remain a primary focus, API security represents the fastest-growing segment as microservices architecture becomes more prevalent.
Regulatory frameworks like the EU's GDPR and the US's HIPAA compel organizations to implement rigorous application security measures. Compliance with standards such as PCI DSS for the payment card industry also necessitates continuous DAST adoption to protect sensitive data. The key decision for technology leaders is how to deeply embed automated DAST tools within their CI/CD pipelines to ensure security at speed.
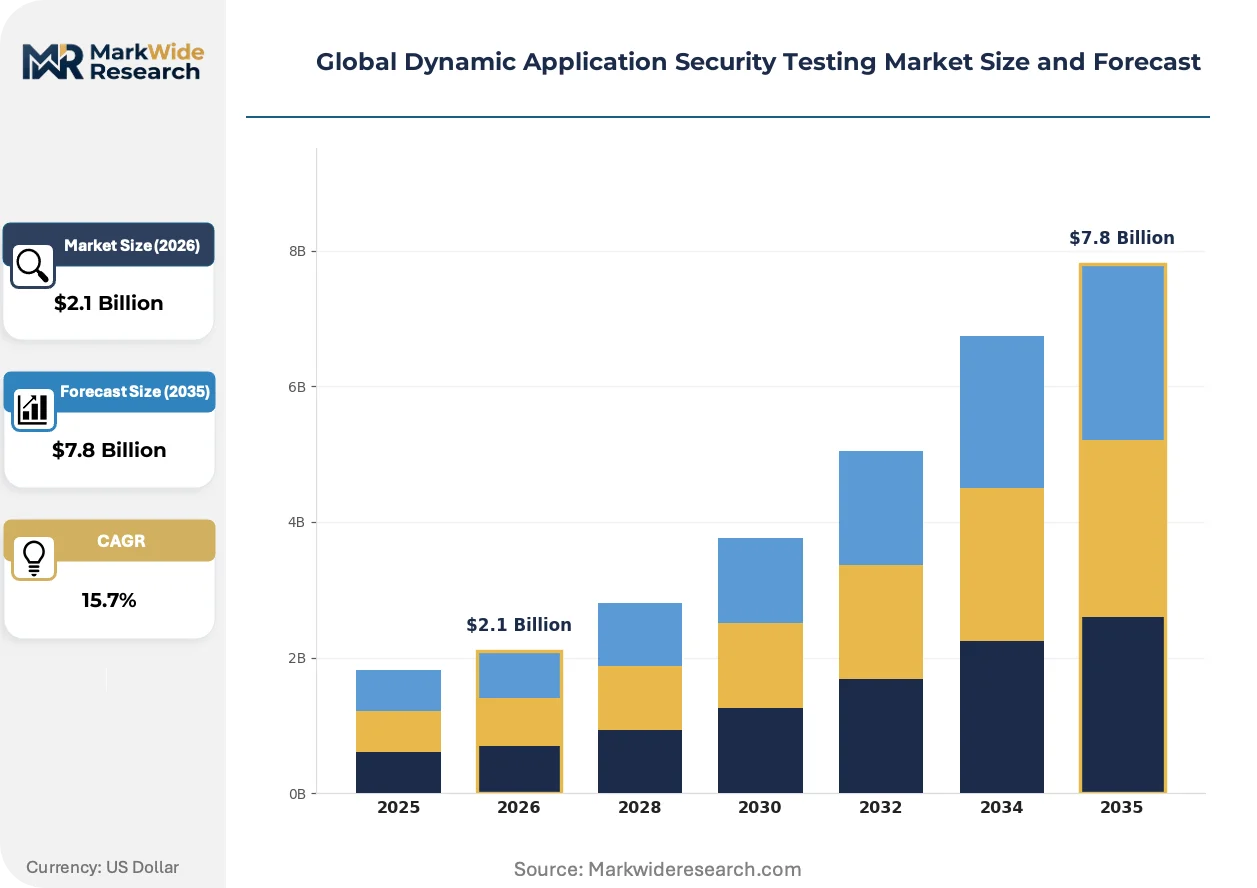
Market Dynamics
The central force shaping the market is the deep integration of automated security testing directly into continuous integration and continuous delivery (CI/CD) pipelines. This shift towards DevSecOps practices makes DAST an essential, non-negotiable step in modern software development.
Growth Catalysts
- Regulatory Mandates:The enforcement of data protection laws, including the EU's GDPR and the US's HIPAA, compels organizations to implement continuous application security testing to prevent data breaches and ensure compliance, particularly within healthcare and public sector applications.
- Financial Services Adoption:The banking and finance industry's push for secure digital services drives DAST adoption. Compliance with standards like the Payment Card Industry Data Security Standard (PCI DSS) requires rigorous testing of web applications that handle sensitive financial data.
- Microservices Architecture:The proliferation of microservices and APIs significantly expands the application attack surface. This architectural shift necessitates dedicated DAST solutions for API security, which represents the fastest-growing segment as companies decompose monolithic applications.
Market Restraints
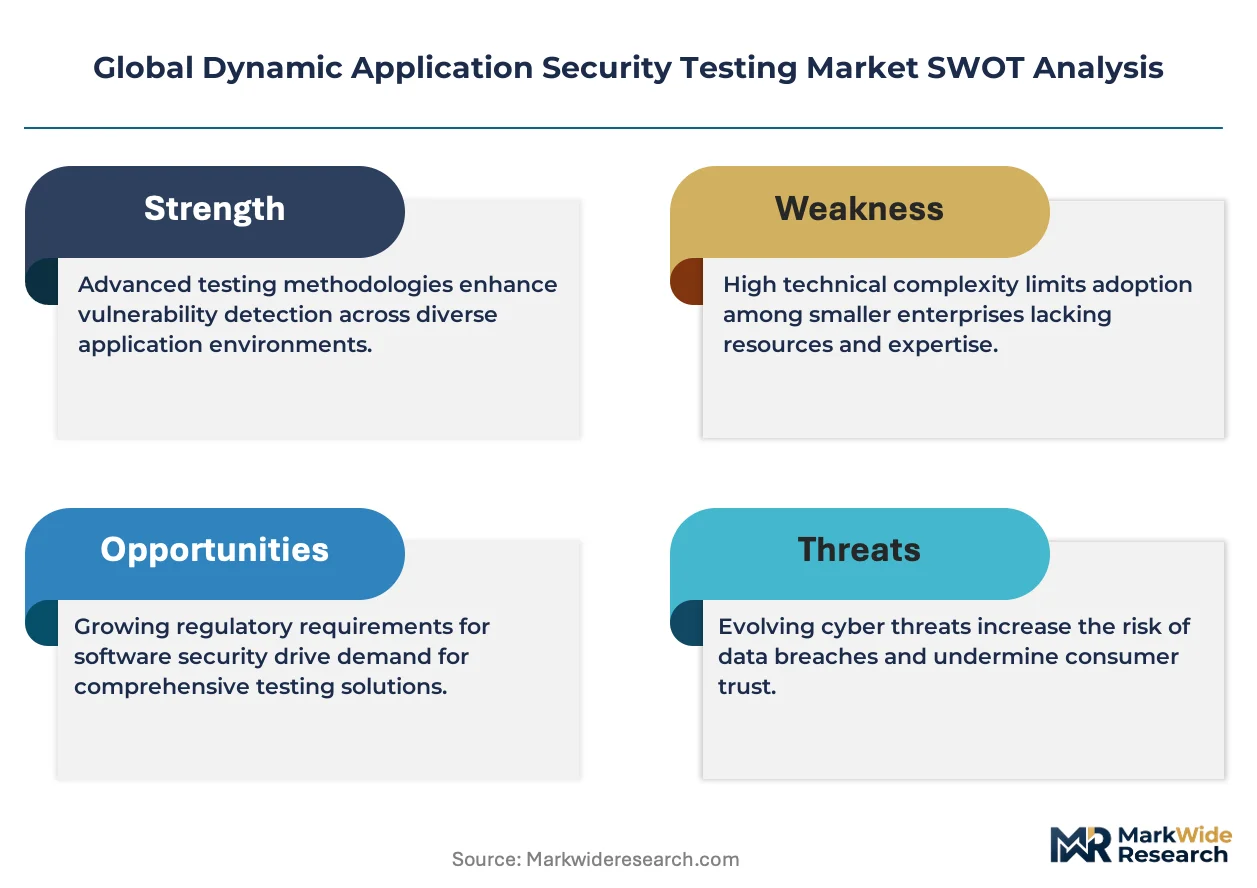
- High False Positive Rates:DAST tools can generate a high volume of false positives, requiring significant time and expertise from security teams to triage and validate findings. This operational overhead can slow down development velocity in fast-paced agile environments.
- Cost of Advanced Solutions:The total cost of ownership for enterprise-grade DAST platforms, including licensing, integration, and skilled personnel, presents a significant barrier for small and medium-sized businesses with limited cybersecurity budgets, hindering broader market penetration.
- Complex Environment Coverage:Dynamic testing struggles to achieve comprehensive coverage in applications with complex authentication, intricate user workflows, or non-standard communication protocols. This limitation can leave critical parts of an application untested against certain attack vectors.
Strategic Opportunities
- Emerging Geographic Markets:Software development hubs in Southeast Asia and Latin America represent underpenetrated regions. Vendors can target these growing markets with scalable, cloud-based DAST solutions tailored to the needs of emerging technology companies.
- IoT and Embedded Systems Security:The explosion of Internet of Things (IoT) devices creates a new frontier for application security. There is a distinct opportunity to develop specialized DAST tools designed to test the firmware and web interfaces of connected devices.
- IAST Convergence:Integrating DAST with Interactive Application Security Testing (IAST) offers a significant opportunity. This combined approach provides the external view of DAST with the internal context of IAST, delivering more accurate vulnerability detection with fewer false positives.
Industry Challenges
- Cybersecurity Talent Shortage:A persistent lack of security professionals skilled in operating DAST tools and interpreting complex vulnerability reports is a major operational challenge. This skills gap limits the ability of organizations to maximize the value of their security investments.
- Pace of DevOps:Integrating security checks without creating bottlenecks in rapid-release DevOps cycles remains a primary challenge. Security teams must find ways to run scans and remediate flaws at a pace that matches the speed of development.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Dynamic Application Security Testing Market |
| Market Size in 2026 | $2.1 Billion |
| Market Size in 2035 | $7.8 Billion |
| CAGR (2026 – 2036) | 15.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premise, Hybrid, Managed Services Solution Type: Vulnerability Scanning, Penetration Testing, Runtime Analysis, Threat Simulation Application: Web Applications, Mobile Applications, API Security, Microservices Security, E-Commerce Platforms End User Industry: Financial Services, Telecommunication Providers, Government Agencies, Software Vendors, Educational Institutions |
| Companies Covered | Invicti, Acunetix, Checkmarx, OWASP ZAP, Bright Security, HCL AppScan, StackHawk, Burp Suite, Veracode, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Dynamic Application Security Testing Market Strategic Shifts & Innovations
Automation within the software development lifecycle is reshaping the market's competitive positioning. The focus is shifting from standalone scanning tools to integrated platforms that embed security seamlessly into developer workflows, making security a shared responsibility rather than a separate function.
Artificial intelligence and machine learning are being embedded into DAST solutions to enhance detection accuracy. DevOps teams in the technology and e-commerce sectors are rapidly adopting these intelligent scanners to prioritize critical vulnerabilities. This AI-driven analysis is expanding into predictive threat modeling, enabling teams to identify and mitigate potential security weaknesses in application logic before code is even written.
Regulatory frameworks like the EU AI Act are introducing new compliance pressures on software development. The act imposes risk-based security and governance requirements on AI systems, which rely on complex application programming interfaces and data processing pipelines. This primarily affects developers of high-risk AI in sectors like finance and healthcare, compelling them to adopt continuous DAST for compliance validation.
Consumption models are shifting away from perpetual licenses toward subscription-based platform access. This change disrupts the traditional transactional sale, favoring vendors who bundle DAST with other testing tools like SAST and SCA into a unified DevSecOps platform. This trend is most visible in North American and European enterprises seeking to consolidate security tools and streamline procurement.
Global Dynamic Application Security Testing Market Segmentation
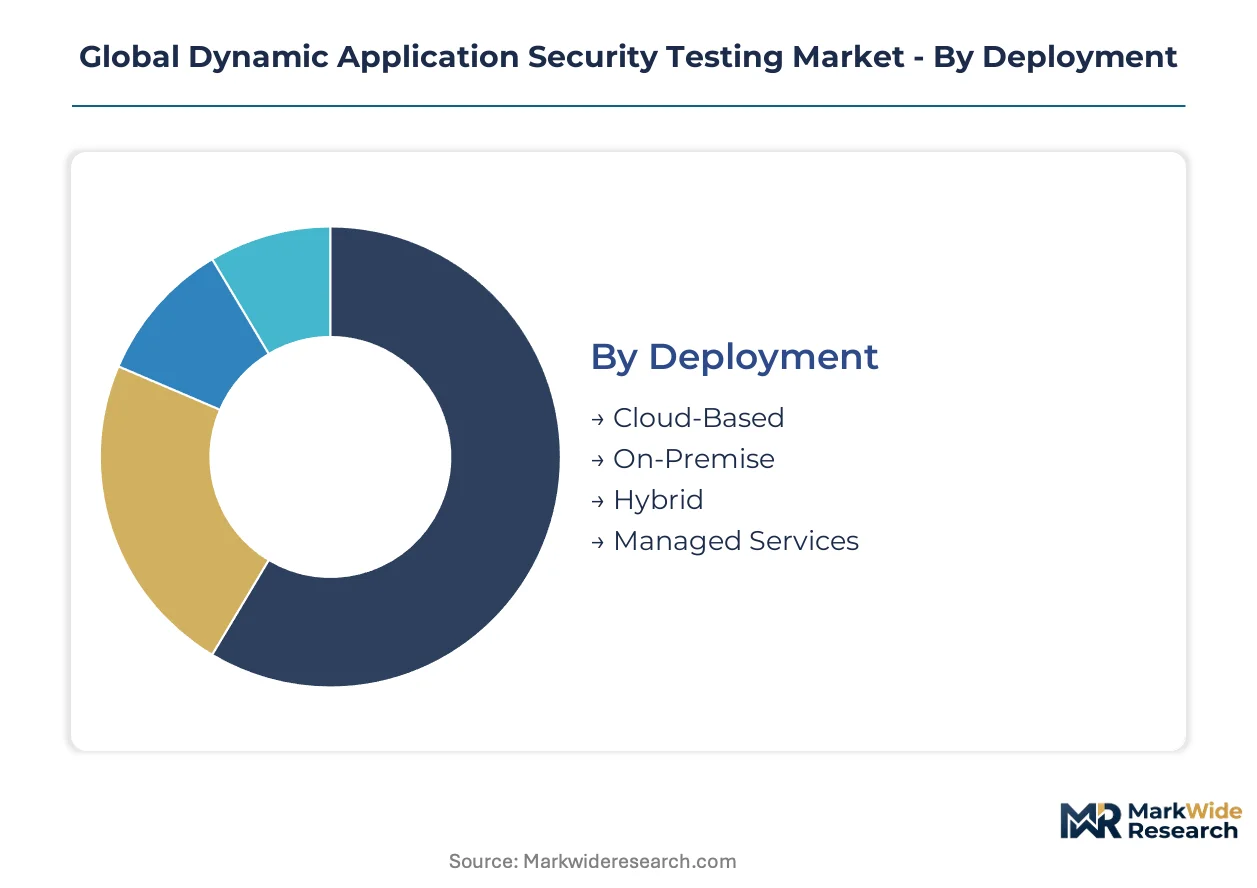
The segmentation of the dynamic application security testing market provides a granular understanding of where security investments are allocated across diverse technological and industry landscapes. This detailed categorization helps identify specific customer needs and the evolving demands for application protection. Understanding these segments is crucial for vendors to tailor offerings and for organizations to strategically deploy DAST solutions.
Deployment:
Supply concentration within deployment models for dynamic application security testing reflects vendor investment in scalable infrastructure and service delivery mechanisms.
- Cloud-Based:This model delivers DAST tools as a service over the internet, requiring no on-premise installation. Demand concentrates in technology and e-commerce sectors, driven by the need for flexible, scalable security solutions integrated into modern DevOps workflows.
- Managed Services:Third-party providers operate and manage DAST tools and processes on behalf of their clients, offering specialized security expertise. Demand stems from small and medium-sized businesses and organizations facing cybersecurity talent shortages, ensuring continuous security posture without in-house overhead.
- On-Premise:Organizations deploy and manage DAST software directly on their own servers and infrastructure. This model is often preferred by highly regulated industries for greater control over data and security operations.
- Hybrid:This deployment combines elements of both on-premise and cloud-based DAST solutions, leveraging the benefits of each model. Enterprises with complex IT environments often utilize hybrid deployments to secure diverse application portfolios.
Cloud-Based DAST absorbs the bulk of installed capacity; Managed Services is expanding most quickly.
Solution Type:
Customer type differentiation influences the selection of dynamic application security testing solution types, from foundational scanning to advanced analytical capabilities.
- Vulnerability Scanning:Automated tools systematically identify known security weaknesses and misconfigurations in running applications. All organizations utilize this foundational solution type for compliance with regulations like the EU's GDPR and the US's HIPAA.
- Penetration Testing:Security experts simulate real-world attacks, often manually, to uncover vulnerabilities and assess the overall security posture of an application. Financial services and government agencies frequently commission penetration testing for high-assurance systems handling sensitive data.
- Runtime Analysis:This solution monitors application behavior during execution to detect anomalies and potential security threats in real-time. It provides insights into how an application responds to various inputs and conditions.
- Threat Simulation:Specialized tools replicate specific attack scenarios, such as SQL injection or cross-site scripting, to validate the effectiveness of existing security controls. These simulations help organizations understand their resilience against targeted cyber threats.
The market prioritizes Vulnerability Scanning for initial security posture, while Penetration Testing secures complex, high-value assets.
Application:
Demand concentration across various application types drives specialized dynamic application security testing solutions.
- Web Applications:DAST primarily focuses on identifying vulnerabilities in browser-accessible applications and their underlying components. Nearly all industries rely on robust web application security for online presence and customer interaction.
- API Security:This segment secures the application programming interfaces that enable communication between different software components and services. The technology and financial sectors increasingly demand API security solutions, fueled by microservices architecture adoption.
- Mobile Applications:DAST tools are adapted to test native, hybrid, and progressive web applications running on mobile devices. This ensures the security of mobile banking, retail, and communication apps.
- Microservices Security:Solutions specifically designed to protect individual, independently deployable services within a larger application architecture. This is critical for maintaining the integrity of distributed systems.
- E-Commerce Platforms:DAST specifically targets the unique security requirements of online retail systems, including payment processing and customer data protection. Retailers use these solutions to prevent fraud and data breaches.
The largest portion of DAST activity targets Web Applications, with API Security demonstrating the steepest expansion trajectory.
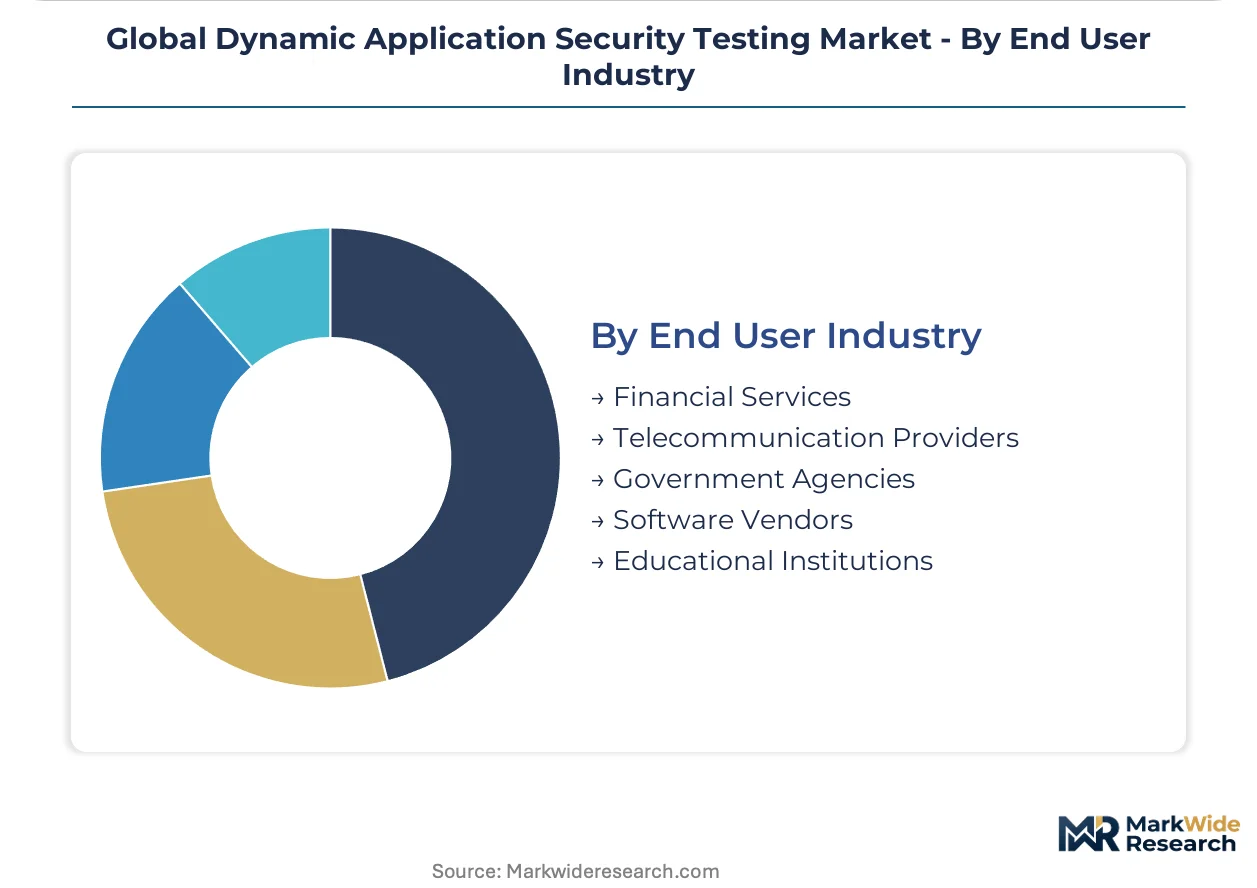
End User Industry:
Regulatory pressure significantly shapes the adoption and maturity of dynamic application security testing across diverse end-user industries.
- Financial Services:Banks, investment firms, and fintech companies require DAST to secure online banking platforms, payment gateways, and customer data. Compliance with standards like PCI DSS and the EU's GDPR mandates continuous application security testing.
- Software Vendors:Companies that develop and sell software products integrate DAST into their software development lifecycles to ensure the security of their offerings. This proactive approach supports secure software delivery to their customer base.
- Telecommunication Providers:These organizations use DAST to secure their network infrastructure, customer portals, and communication applications. Protecting sensitive subscriber data and maintaining service integrity are paramount.
- Government Agencies:Public sector entities employ DAST for citizen-facing online services, internal data systems, and critical infrastructure applications. Adherence to national data protection acts necessitates rigorous security testing.
- Educational Institutions:Universities, colleges, and online learning platforms utilize DAST to protect student information systems, research data, and digital learning environments. Safeguarding academic and personal data is a key concern.
Compliance requirements drive DAST implementation in Financial Services, while Software Vendors increasingly integrate security into their core product development.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States, with its mature technology ecosystem, anchors significant demand for dynamic application security testing solutions. This market is further shaped by stringent regulatory landscapes across diverse geographies. Global software development hubs necessitate continuous security validation for their digital products and services.
United States
Demand for DAST in the United States stems from its expansive financial services and technology sectors. Compliance with the US's HIPAA and PCI DSS mandates rigorous application security. Major tech clusters in Silicon Valley and Seattle drive innovation in DAST tool development and adoption.
Germany
Germany's strong industrial base and focus on secure digital transformation fuel DAST adoption. The EU's GDPR significantly influences data protection measures for German enterprises. Cities like Munich and Berlin are key centers for cybersecurity research and advanced software development.
India
India's rapid growth in software development and IT services drives substantial DAST demand. Government initiatives like Digital India encourage secure online platforms for public services. Bengaluru and Hyderabad are major software development hubs, integrating DAST into their development cycles.
Japan
Japan emphasizes secure digital infrastructure and emerging IoT security, propelling DAST market expansion. Regulations from METI guide cybersecurity practices for Japanese businesses. Tokyo's vibrant tech cluster focuses on integrating advanced DAST solutions for enterprise applications.
Singapore
Singapore functions as a significant regional hub for financial technology and cybersecurity innovation. The country's strict data protection laws compel organizations to adopt continuous application security testing. The One-North district fosters a robust ecosystem for cybersecurity startups and research.
Global Dynamic Application Security Testing Market Key Industry Players
Established producers occupy the standard tier; emerging entrants pursue adjacent spaces like API security and integrated DevSecOps platforms. The market structure exhibits a tiered approach, with comprehensive platform providers and specialized automated scanning solutions. Strategic partnerships for ecosystem expansion and technology consolidation through mergers and acquisitions are dominant competitive moves.
Specialists in automated scanning solutions include Invicti, recognized for its suitability across various team sizes. Checkmarx exemplifies providers offering comprehensive platforms tailored for large, complex organizations. Veracode positions its offerings to support secure software development lifecycles across diverse industries, anchoring a significant portion of the market's enterprise segment.
| Leading Market Players |
|---|
| Invicti |
| Acunetix |
| Checkmarx |
| OWASP ZAP |
| Bright Security |
| HCL AppScan |
| StackHawk |
| Burp Suite |
| Veracode |
| Others |
Cost & Logistics Intelligence
Stringent regulatory compliance requirements, such as the EU's GDPR and the US's HIPAA, compel organizations to procure DAST solutions that offer continuous validation. This demand for integrated, audit-ready platforms influences vendor supply and pricing models.
Pricing Analysis
Warranty and service bundling significantly differentiate DAST offerings, with comprehensive platforms often including extensive support and integration services. Subscription-based platform access represents the dominant pricing model, moving away from perpetual licenses. Price differentiation stems from customization levels for complex enterprise environments and the depth of after-sales support provided. Pricing softness exists in basic scanning tools, while premium solutions command higher prices, with small and medium-sized businesses exhibiting greater price sensitivity.
Supply Chain Analysis
Reverse logistics for DAST solutions primarily involves software updates, patch management, and end-of-life data migration rather than physical returns. Geographic supply concentration for DAST software development centers on the United States, India, and Germany. The industry relies heavily on skilled cybersecurity talent and robust cloud infrastructure services as key inputs. A persistent cybersecurity talent shortage represents a significant supply chain risk. Distribution runs through direct vendor sales and specialized channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The dynamic application security testing market is fundamentally a cost-of-compliance story, driven by stringent regulatory frameworks. The EU AI Act, for instance, creates a barrier-to-entry moat for vendors capable of validating high-risk AI systems.
For Market Incumbents: Lock in large enterprise customers by integrating DAST with SAST and SCA into comprehensive DevSecOps platforms. This strategy counters the threat from specialized API security entrants targeting microservices architectures. Invest heavily in R&D to embed artificial intelligence and machine learning, reducing false positive rates and improving detection accuracy. Consolidate market share by offering robust managed services to organizations facing cybersecurity talent shortages.
For New Entrants and Emerging Players: Cloud marketplaces and developer-centric API integrations offer effective digital channels for new entrants to gain traction. Target underpenetrated segments like IoT and embedded systems security, or emerging geographic markets in Southeast Asia. Offer scalable, automated DAST solutions tailored for small and medium-sized businesses, which are the most penetrable segment due to budget constraints. A go-to-market strategy emphasizing ease of deployment and low total cost of ownership will resonate.
For Investors and Strategic Acquirers: Re-rating potential sits with specialized DAST providers, particularly those in API security, given the proliferation of microservices architectures. The long-term viability of this market remains strong, driven by continuous software development and an evolving threat landscape. Acquire firms excelling in AI-driven vulnerability prioritization or offering seamless IAST convergence. Investors should monitor the adoption rate of integrated DevSecOps platforms as a key inflection indicator.
| Strategic Initiative | Industry Significance |
|---|---|
| Product Launch: AI-powered DAST scanner | Enhances detection accuracy and reduces false positives for security teams. |
| Platform Integration: DAST with SAST and SCA | Consolidates security tools for streamlined DevSecOps workflows. |
| Strategic Partnership: Cloud provider integration | Expands market reach and optimizes cloud-native application security. |
| Acquisition of Specialist Firm: API security vendor | Strengthens offerings in the fastest-growing application segment. |
| Geographic Expansion: Southeast Asian markets | Captures demand from growing software development hubs. |
Research Approach
Independent corroboration across SEC filings, industry reports from cybersecurity associations, and academic research underwrites the qualitative findings. This approach combined primary interviews with CTOs, security architects, DevOps engineers, and compliance officers, with secondary validation. Bottom-up and top-down triangulation ensured data integrity and consistency.
Comparable historical periods anchored the forecast window, allowing for robust trend analysis and projection. A quantitative model integrated statistical analysis across the analysis window, considering deployment model, solution type, application, and end-user industry. Compound annual growth rates were derived through regression analysis and expert consensus. Software development spending and regulatory enforcement trends served as key forecast inputs.
The model holds under conditions of a stable regulatory environment and consistent cybersecurity investment; deviation in major geopolitical events or rapid technological shifts would shift the forecast. Forecasts reflect assumptions regarding the persistent cybersecurity talent shortage and potential economic downturns. Practitioners should monitor new data privacy laws and AI regulation for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Identity Governance and Administration Market
Security Software
Information Rights Management Market
Security Software
US Hardware Encryption Market
Security Software
Global Software-Defined Security Market
Security Software
Device Vulnerability Management Market
Security Software
Mobile Security Market
Security Software
Video Intercom Devices Market
Security Software
Identity Verification Software Market
Security Software
Device-Embedded Biometric Authentication Market
Security Software
Communication Encryption Software Market
Security Software
Confidential Computing Market
Security Software
Digital Risk Protection Software Market
Security Software
Europe Lawful Interception Market
Security Software
Mass Notification System Market
Security Software
AI Security Platforms Market
Security Software
Door Phone Market