
 Global Software-Defined Security Market | 2026-2036
Global Software-Defined Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Software-Defined Security Market Foresight
Subscription-based delivery of software-defined security features is rebalancing vendor revenue models toward recurring streams and away from perpetual licensing. Palo Alto Networks leverages its cloud-native platform architecture to sustain recurring attach rates across enterprise accounts. Fortinet anchors its competitive position through integrated hardware-software bundles that extend SD-Security into branch edge deployments. Check Point Software Technologies differentiates via centralized policy orchestration that controls multi-cloud firewall rules from a single management plane.
Software-defined security decouples network security functions from dedicated hardware appliances, instead embedding threat detection, access control, and encryption into virtualized or containerized software layers that execute on standard compute infrastructure. The architecture uses programmable APIs to enforce security policies dynamically across distributed workloads, with latency targets typically under 50 milliseconds for real-time traffic inspection. Cloud-Native deployment leads structural growth as enterprises abandon capital-intensive appliance refresh cycles, while Zero Trust Network Access commands premium pricing within solution types due to its identity-centric architecture replacing legacy VPN tunnels. Firewall-as-a-Service remains the largest revenue pool among solution types but faces margin compression from hyperscaler-native alternatives.
The U.S. Securities and Exchange Commission mandates incident disclosure timelines that compress response windows, pushing financial institutions toward automated SD-Security orchestration. The EU AI Act classifies certain autonomous threat-response systems as high-risk, imposing conformity assessments that reshape product development roadmaps for vendors serving European enterprises. India's CERT-In directives on synchronized log retention and breach reporting create compliance-driven procurement cycles among domestic IT services exporters. Stakeholders must evaluate whether their policy engines can adapt to divergent jurisdictional requirements without fragmenting into region-specific product variants.
Market Dynamics
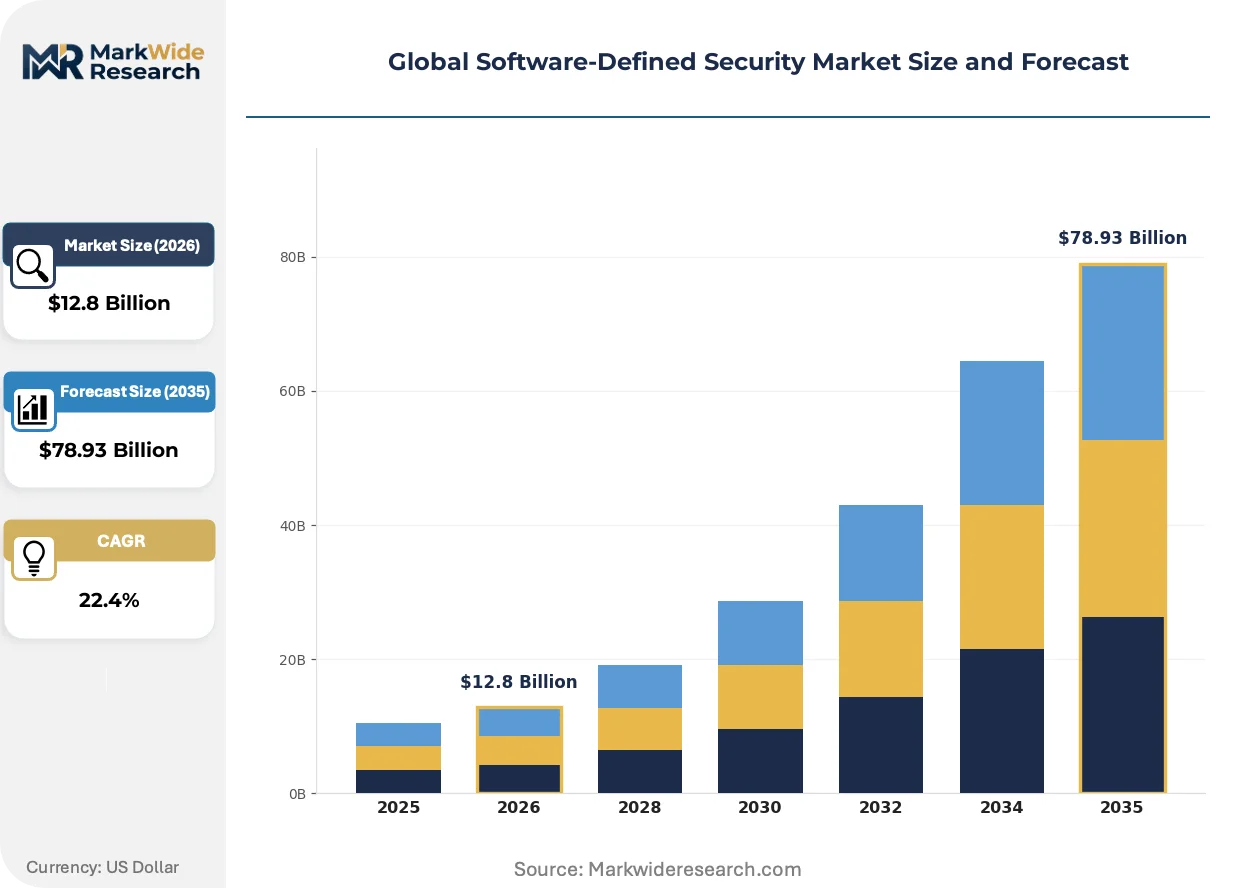
Financial institutions are abandoning hardware-bound security appliances in favor of policy-driven architectures that embed threat detection directly into virtualized compute layers. This decoupling of security functions from dedicated hardware compresses refresh cycles and redirects capital toward operational expenditure models.
Growth Catalysts
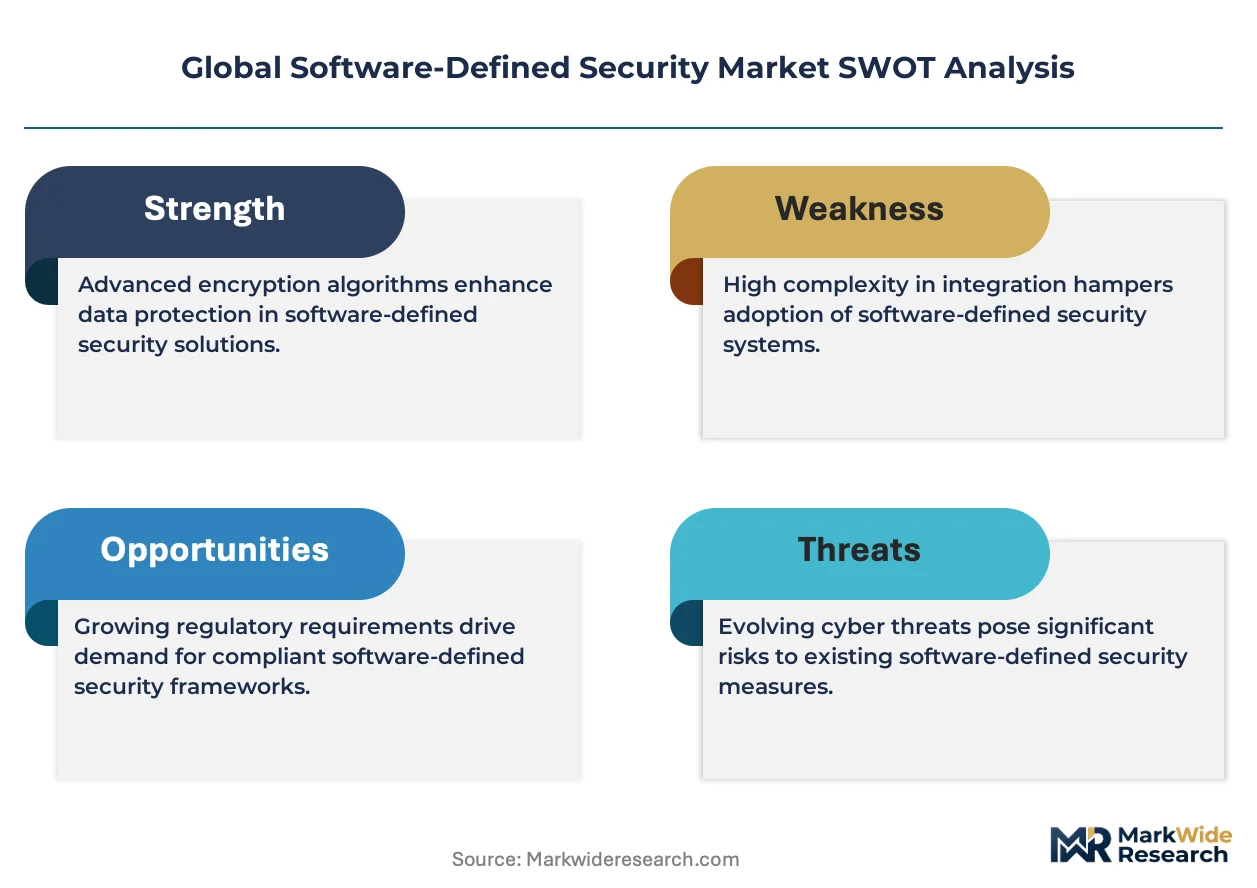
- EU AI Act compliance mandates:High-risk classification of autonomous threat-response systems forces European enterprises toward certified SD-Security platforms, creating procurement urgency.
- Cloud-native financial services:Banks and payment processors are migrating core transaction infrastructure to containerized environments that require API-driven security orchestration.
- Zero Trust architecture adoption:Identity-centric access controls are replacing legacy VPN tunnels across distributed workforces, accelerating demand for software-defined perimeter solutions.
Market Restraints
- Hyperscaler-native alternatives:AWS, Azure, and GCP are bundling competitive firewall-as-a-service offerings that compress margins for independent vendors.
- Conformity assessment costs:EU AI Act high-risk system certifications impose documentation and testing burdens that extend product development timelines.
- Skill scarcity in policy orchestration:Enterprise security teams lack expertise in API-driven policy engines, slowing deployment velocity and increasing professional services dependency.
Strategic Opportunities
- India's CERT-In directives:Mandatory synchronized log retention and breach reporting among IT services exporters creates compliance-driven procurement cycles for automated monitoring platforms.
- Convergence of SD-Security with AI/ML:Real-time behavioral analytics integrated with policy engines enables predictive threat containment with sub-50 millisecond response latency.
- Branch edge deployment expansion:Retail and logistics networks require distributed security enforcement at thousands of remote locations without hardware appliances.
Industry Challenges
- Multi-jurisdictional policy fragmentation:Vendors must adapt policy engines to divergent requirements from SEC disclosure timelines, EU AI Act conformity assessments, and India's CERT-In mandates without creating region-specific product variants.
- Legacy network architecture integration:Enterprises maintain hybrid environments where hardware firewalls coexist with software-defined controls, complicating unified threat visibility and creating configuration drift risks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Software-Defined Security Market |
| Market Size in 2026 | $12.8 Billion |
| Market Size in 2035 | $78.93 Billion |
| CAGR (2026 – 2036) | 22.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Native, Hybrid Cloud, On-Premises, Multi-Cloud, Edge Computing Solution Type: Firewall-as-a-Service, Intrusion Detection, Data Loss Prevention, Secure Web Gateway, Zero Trust Network Access Application: Threat Intelligence, Network Segmentation, Compliance Management, Identity & Access Management, Encryption End User Industry: IT & Telecom, Manufacturing, Government, Energy & Utilities, Education |
| Companies Covered | Cisco Systems, Inc., Palo Alto Networks, Inc., Fortinet, Inc., Check Point Software Technologies Ltd., VMware, Inc., Juniper Networks, Inc., IBM Corporation, Zscaler, Inc., Trend Micro Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Software-Defined Security Market Shifts & Advancements
Security policy enforcement is migrating from perimeter appliances to embedded software layers that execute on standard compute infrastructure. This architectural shift is compressing hardware refresh cycles and enabling real-time threat response through programmable APIs.
Extended detection and response (XDR) platforms are automating correlation of telemetry across endpoints, networks, and cloud workloads. Financial services firms in the United States are deploying these systems to meet SEC-mandated incident disclosure windows. The technology is automating investigation workflows that previously required manual analyst intervention, reducing mean-time-to-containment from hours to minutes.
The EU AI Act imposes conformity assessments on autonomous threat-response systems classified as high-risk. Vendors serving European enterprises must document algorithmic decision pathways and maintain human oversight mechanisms. This regulatory friction is reshaping product roadmaps, with development resources redirecting toward explainability features and audit trail capabilities.
Subscription-based consumption models are displacing perpetual licensing across enterprise procurement. Chief information security officers in Germany and India now prioritize operational expenditure flexibility over capital-intensive appliance purchases. This preference shift favors vendors with cloud-native delivery architectures and usage-based metering capabilities.
Global Software-Defined Security Market Segmentation
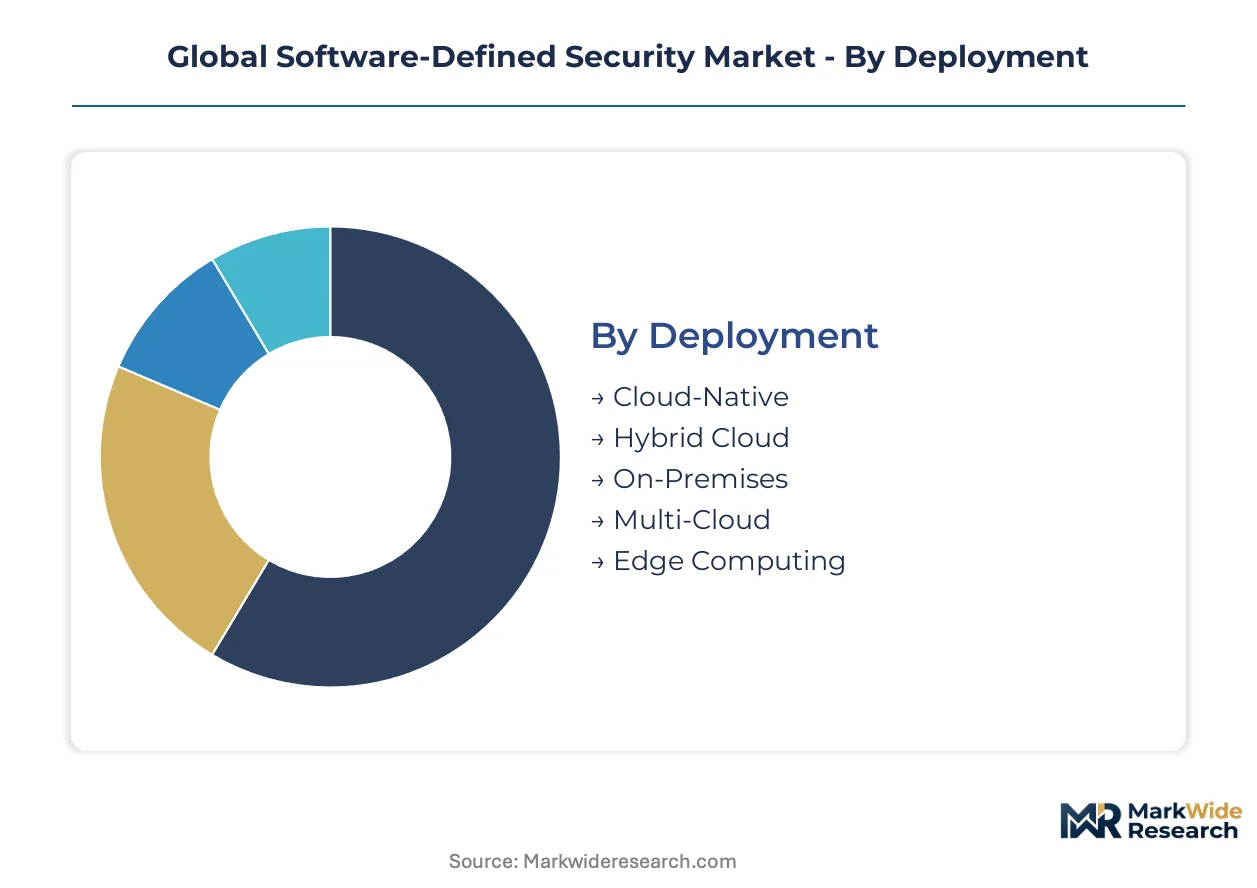
Software-defined security architectures fragment across deployment topologies, solution modalities, and compliance use cases. Each segment carries distinct certification burdens and procurement patterns that reshape vendor go-to-market strategies.
Deployment:
Cloud-Native deployments face EU AI Act high-risk system assessments when embedding autonomous threat response, while On-Premises configurations trigger India's CERT-In synchronized log retention mandates.
- Cloud-Native:Containerized security functions execute on Kubernetes-orchestrated infrastructure with sub-50 millisecond policy enforcement latency. Financial services firms in Germany are migrating core transaction processing to these environments to satisfy EBA cloud outsourcing guidelines.
- Zero Trust Network Access:Identity-centric perimeter replacement commands premium pricing through continuous authentication and microsegmentation. United States healthcare systems deploy these solutions to align with HIPAA access control modernization requirements.
- Hybrid Cloud:Policy orchestration spans private data centers and public cloud instances through unified control planes.
- On-Premises:Virtualized security functions run on customer-managed infrastructure to satisfy data sovereignty constraints.
- Multi-Cloud:Centralized policy management enforces consistent controls across AWS, Azure, and GCP environments.
- Edge Computing:Distributed enforcement points process traffic locally at retail branches and manufacturing floors.
Cloud-Native sits at the top of the volume ranking, with Zero Trust Network Access climbing the fastest.
Solution Type:
Firewall-as-a-Service absorbs the steepest margin compression from hyperscaler-native alternatives, while Zero Trust Network Access captures pricing power through identity-centric architecture differentiation.
- Firewall-as-a-Service:Cloud-delivered network filtering replaces physical appliances through API-driven rule propagation. United States enterprises dominate procurement volumes as SEC disclosure timelines compress refresh cycles toward operational expenditure models.
- Intrusion Detection:Behavioral analytics engines identify anomalous traffic patterns through machine learning classifiers. India's IT services exporters deploy these systems to satisfy CERT-In breach reporting mandates for automated anomaly flagging.
- Data Loss Prevention:Content inspection policies classify and block sensitive data exfiltration across egress channels.
- Secure Web Gateway:Cloud-proxy architectures filter malicious URLs and enforce acceptable use policies for distributed workforces.
- Zero Trust Network Access:Software-defined perimeters replace VPN tunnels with identity-verified session brokering.
Firewall-as-a-Service maintains the largest revenue pool, though Zero Trust Network Access demonstrates the steepest expansion trajectory.
Application:
Compliance Management applications concentrate procurement among EU-regulated entities facing CSRD sustainability disclosure and EU AI Act algorithmic accountability requirements.
- Threat Intelligence:Automated indicator ingestion and correlation platforms reduce analyst investigation cycles. German automotive manufacturers integrate these feeds with SIEM infrastructure to satisfy BSI baseline protection mandates.
- Network Segmentation:Microsegmentation policies isolate workloads through software-defined east-west traffic controls. United States energy utilities deploy these architectures to align with FERC critical infrastructure protection standards.
- Compliance Management:Policy automation engines map security controls to regulatory frameworks including GDPR and NIS2.
- Identity & Access Management:Privileged access orchestration enforces just-in-time credential provisioning across cloud workloads.
- Encryption:Key management services protect data-at-rest and data-in-transit through centralized cryptographic policy enforcement.
Threat Intelligence leads deployment volumes, with Network Segmentation gaining share fastest among critical infrastructure operators.
End User Industry:
IT & Telecom verticals drive subscription-based procurement through cloud-native platform consumption, while Government segments impose sovereign cloud and data localization requirements.
- IT & Telecom:Managed security service providers embed SD-Security into multi-tenant offerings for enterprise clients. India's software exporters dominate procurement volumes as CERT-In directives mandate automated log synchronization and incident reporting infrastructure.
- Government:Sovereign cloud deployments enforce data residency through nationally certified security controls. German federal agencies require Common Criteria EAL4+ certification for threat response automation under BSI technical guidelines.
- Manufacturing:Operational technology integration protects industrial control systems from ransomware targeting production lines.
- Energy & Utilities:Critical infrastructure operators deploy distributed security enforcement at generation and distribution facilities.
- Education:Campus network modernization replaces hardware appliances with software-defined access controls for hybrid learning environments.
IT & Telecom sits at the top of the volume ranking, with Government climbing the fastest as sovereign cloud mandates expand procurement cycles.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States financial institutions outpace German enterprises in cloud-native security procurement velocity, though both markets face tightening algorithmic accountability mandates. India's IT services exporters are accelerating software-defined security adoption to satisfy synchronized log retention directives. Enterprise migration from hardware appliances concentrates demand across these three jurisdictions.
United States
SEC disclosure timelines compress incident response windows to 96 hours, driving automated orchestration procurement among asset managers and payment processors. Financial institutions deploy API-driven policy engines to satisfy FERC critical infrastructure standards for energy sector operators. New York and San Francisco financial technology clusters anchor cloud-native firewall-as-a-service consumption.
Germany
Automotive manufacturers and federal agencies demand Common Criteria EAL4+ certification for threat response automation under BSI technical guidelines. The EU AI Act high-risk system classification imposes conformity documentation burdens on autonomous security platforms serving European enterprises. Stuttgart and Munich industrial corridors concentrate zero trust network access deployments for manufacturing supply chains.
India
IT services exporters face CERT-In mandates for synchronized log retention and six-hour breach reporting windows, creating compliance-driven procurement cycles. Domestic software vendors and managed security service providers scale cloud-native security operations to serve North American and European client bases. Bengaluru and Hyderabad technology clusters dominate subscription-based security platform consumption.
United Kingdom
Financial services firms align software-defined perimeter deployments with Prudential Regulation Authority operational resilience requirements. Post-Brexit data localization preferences sustain on-premises virtualized security function demand among insurance underwriters and investment banks. London's financial district anchors hybrid cloud security orchestration procurement.
Japan
Manufacturing conglomerates integrate software-defined security into operational technology environments to protect industrial control systems from ransomware targeting production lines. METI cybersecurity framework updates emphasize API-driven policy enforcement for supply chain digitization initiatives. Tokyo and Osaka metropolitan areas concentrate secure web gateway deployments for distributed enterprise workforces.
Global Software-Defined Security Market Competitive Landscape
Top-tier vendors anchor platform consolidation, while specialized pure-plays occupy vertical niches. The vendor base stratifies across three tiers: hyperscaler-aligned platform providers, independent cybersecurity specialists with hardware-software bundles, and cloud-native pure-plays with identity-centric architectures. Strategic archetypes include integrated platform consolidators, branch edge deployment specialists, and API-first policy orchestrators. Competitive moves concentrate on M&A for zero trust capabilities and strategic partnerships with managed security service providers.
Within the integrated platform tier, Cisco Systems, Inc. and Palo Alto Networks, Inc. exemplify archetypes spanning hardware-software convergence and cloud-native delivery. Fortinet, Inc. occupies a position among branch edge specialists extending software-defined controls into distributed retail and logistics networks. Check Point Software Technologies Ltd. anchors the policy orchestration segment through centralized multi-cloud firewall management capabilities.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Palo Alto Networks, Inc. |
| Fortinet, Inc. |
| Check Point Software Technologies Ltd. |
| VMware, Inc. |
| Juniper Networks, Inc. |
| IBM Corporation |
| Zscaler, Inc. |
| Trend Micro Inc. |
| Others |
Supply & Pricing Matrix
Containerized security function deployment is compressing hardware refresh cycles while redistributing value capture toward software engineering talent pools in India and Germany. This architectural transition simultaneously erodes appliance-based margin structures and concentrates procurement leverage among hyperscaler-aligned platform providers.
Pricing Analysis
Capacity additions in India are reshaping price floors for cloud-native security orchestration as domestic IT services exporters scale automated compliance platforms. Subscription-based SaaS tiers dominate enterprise procurement, with price differentiation anchored in EU AI Act certification grade and deployment latency guarantees under 50 milliseconds. Pricing pressure stems from AWS, Azure, and GCP bundling competitive firewall-as-a-service offerings that compress independent vendor margins. Mid-market financial services firms in the United States exhibit highest price sensitivity, while German automotive manufacturers absorbing BSI-mandated Common Criteria certifications show lowest.
Supply Chain Analysis
Policy engine development talent scarcity in Bengaluru and Hyderabad is constraining vendor delivery timelines for API-driven orchestration platforms. Supply concentrates in the United States for cloud-native platform engineering, India for compliance automation development, and Germany for sovereign-certified security controls. Raw material dependencies span Kubernetes container orchestration frameworks, behavioral analytics training datasets, and hardware security module integrations. Single-source vulnerability runs through hyperscaler infrastructure API dependencies. Distribution runs through managed security service providers embedding SD-Security into multi-tenant enterprise offerings.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market represents a late-cycle quality story as procurement shifts toward EU AI Act-certified platforms that command pricing power through algorithmic accountability documentation. Premium specification demand from German federal agencies and financial institutions is filtering procurement toward vendors with explainable AI audit trails.
For Market Incumbents: Hedge against hyperscaler-native margin compression by deepening API-first platform integration with managed security service providers. Prioritize backward integration into behavioral analytics training data pipelines to reduce dependency on third-party telemetry feeds. Accelerate Common Criteria EAL4+ certification investment for German government segments before conformity assessment queues lengthen.
For New Entrants and Emerging Players: Enter via India's CERT-In compliance automation white space among IT services exporters facing synchronized log retention mandates. Target mid-market United States healthcare systems modernizing HIPAA access controls through zero trust architectures. Lead with identity-centric microsegmentation capabilities that bypass incumbent firewall-as-a-service entrenchment.
For Investors and Strategic Acquirers: Valuations sit cheapest among branch edge deployment specialists with hardware-software bundle exposure to retail and logistics networks. Long-term viability favors vendors with multi-cloud policy orchestration capabilities spanning AWS, Azure, and GCP control planes. Watch hyperscaler partnership announcement velocity as inflection indicator for platform consolidation momentum.
| Strategic Initiative | Industry Significance |
|---|---|
| EU AI Act Certification Investment | BSI and EMA conformity assessments create procurement moats for German federal agencies. |
| API-First Platform Integration | Real-time policy orchestration with sub-50 millisecond latency satisfies SEC disclosure timelines. |
| Managed Security Service Partnership | Multi-tenant embedding accelerates recurring revenue attach across India's IT exporter base. |
| Behavioral Analytics Acquisition | Machine learning classifiers automate CERT-In anomaly flagging for breach reporting compliance. |
| Zero Trust Architecture Expansion | Identity-centric perimeter replacement captures premium pricing from United States healthcare systems. |
Research Methodology
Coverage spans the United States, Germany, India, the United Kingdom, and Japan, with primary inputs from each jurisdiction's regulatory environment. The approach combines structured interviews with CISOs, cloud platform engineers, managed security service provider executives, and compliance officers with secondary validation through SEC filings, EBA cloud outsourcing guidelines, CERT-In directive documentation, and BSI technical guideline repositories. Bottom-up deployment volume estimates triangulate against top-down vendor revenue segmentation.
Granularity-level modeling disaggregates revenue across cloud-native, hybrid cloud, and on-premises deployment configurations; firewall-as-a-service, intrusion detection, and zero trust network access solution types; and financial services, government, and IT & telecom end-user verticals. CAGRs derive from segment-specific adoption curve analysis and regulatory mandate implementation timelines. Forecast inputs include EU AI Act conformity assessment capacity constraints and India's CERT-In enforcement escalation patterns.
The model holds under sustained regulatory enforcement of algorithmic accountability and breach disclosure timelines; deviation in hyperscaler bundling aggression or sovereign cloud mandate relaxation would shift vendor competitive positioning. Practitioners should monitor EU AI Act delegated act publication schedules and CERT-In penalty enforcement frequency for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Asia-Pacific Encryption Software Market
Security Software
Network Video Recorder (NVR) Market
Security Software
Robocall Mitigation Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Global Data Protection As a Service (Dpaas) Market
Security Software
Smart Video Doorbell Market
Security Software
Public Key Infrastructure (PKI) Market
Security Software
Embedded Security Market
Security Software
Application Control Market
Security Software
Global Digital Identity Solutions Market
Security Software
Global Automatic Number Plate Recognition (ANPR) System Market
Security Software
Secure Web Gateway Market
Security Software
Global Privileged Access Management (PAM) Solutions Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Spam Blocking Software Market
Security Software
Battery-Powered Doorbell Camera Market