
 US Hardware Encryption Market | 2026-2036
US Hardware Encryption Market Size, Share, and Industry Trends Forecast 2026-2036
US Hardware Encryption Market Insights
Aftermarket key-management service revenue is rewriting profit dynamics across the US hardware encryption supply base. Thales e-Security, Inc. leverages its certified key-management infrastructure to sustain premium pricing in government verticals. Kingston Technology Corporation anchors consumer and enterprise segments through vertically controlled NAND supply chains. Micron Technology, Inc. competes on R&D intensity in self-encrypting drive controllers for hyperscale data centers.
US hardware encryption encompasses dedicated silicon-based cryptographic modules—typically AES-256 engines embedded within storage controllers, network processors, or secure element chips—that perform encryption and decryption operations independent of host CPU resources, primarily safeguarding data-at-rest and data-in-motion against unauthorized extraction. Hard disk drives and solid-state storage with embedded encryption engines dominate unit volume, while secure network equipment captures expanding margin pools as edge computing architectures proliferate. USB tokens and smart cards retain niche strength in regulated authentication workflows, though cloud security applications are displacing physical token dependence among enterprise adopters.
Federal procurement rules under NIST FIPS 140-3, SEC cybersecurity disclosure requirements, and HIPAA encryption mandates collectively shape product certification roadmaps and vendor qualification timelines across US hardware encryption suppliers. The Department of Defense's CMMC framework further segments addressable markets by restricting contract eligibility to vendors with validated module certifications. Stakeholders must monitor evolving quantum-resistant algorithm standards from NIST and assess early migration paths for lattice-based cryptography in next-generation silicon designs.
Market Dynamics
Federal procurement mandates under NIST FIPS 140-3 are compressing vendor qualification timelines and forcing accelerated silicon redesign cycles across the US hardware encryption supply base. Defense contractors now require validated module certifications before contract eligibility, creating a structural bottleneck that favors incumbent suppliers with established certification infrastructure.
Growth Catalysts
- NIST FIPS 140-3 compliance mandates:Federal agencies and defense contractors must procure only validated self-encrypting drives, creating guaranteed demand volume for certified suppliers.
- Hyperscale data center expansion:Northern Virginia's cloud infrastructure hub and California's Silicon Valley corridor are driving concentrated procurement of AES-256 embedded storage controllers.
- SEC cybersecurity disclosure rules:Public companies face liability exposure for data breaches, accelerating enterprise adoption of hardware-based encryption over software alternatives.
Market Restraints
- Certification timeline friction:NIST validation cycles for FIPS 140-3 Level 3 modules extend 18-24 months, freezing product roadmaps for mid-tier suppliers without dedicated compliance teams.
- NAND flash supply concentration:Controller fabrication depends on concentrated foundry capacity in East Asia, exposing US encryption module vendors to geopolitical supply disruption.
- Quantum computing threat horizon:Lattice-based migration paths remain undefined, forcing R&D allocation toward algorithm agility without near-term revenue return.
Strategic Opportunities
- CMMC framework segmentation:The Department of Defense's tiered certification requirements create contract eligibility tiers that mid-market vendors can target with specialized module configurations.
- Edge computing security architectures:Distributed processing nodes require hardware encryption for data-in-motion, expanding addressable market beyond traditional data-at-rest applications.
- Post-quantum algorithm standardization:NIST's pending lattice-based cryptography standards will necessitate silicon redesigns, creating first-mover advantage for vendors with advanced R&D pipelines.
Industry Challenges
- Cryptographic engineering talent scarcity:Qualified silicon designers with AES implementation expertise and side-channel attack mitigation experience command premium compensation, constraining team expansion.
- Legacy infrastructure integration complexity:Federal agencies operate mixed fleets of pre-FIPS 140-3 storage devices, requiring costly parallel certification maintenance during transition windows.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | US Hardware Encryption Market |
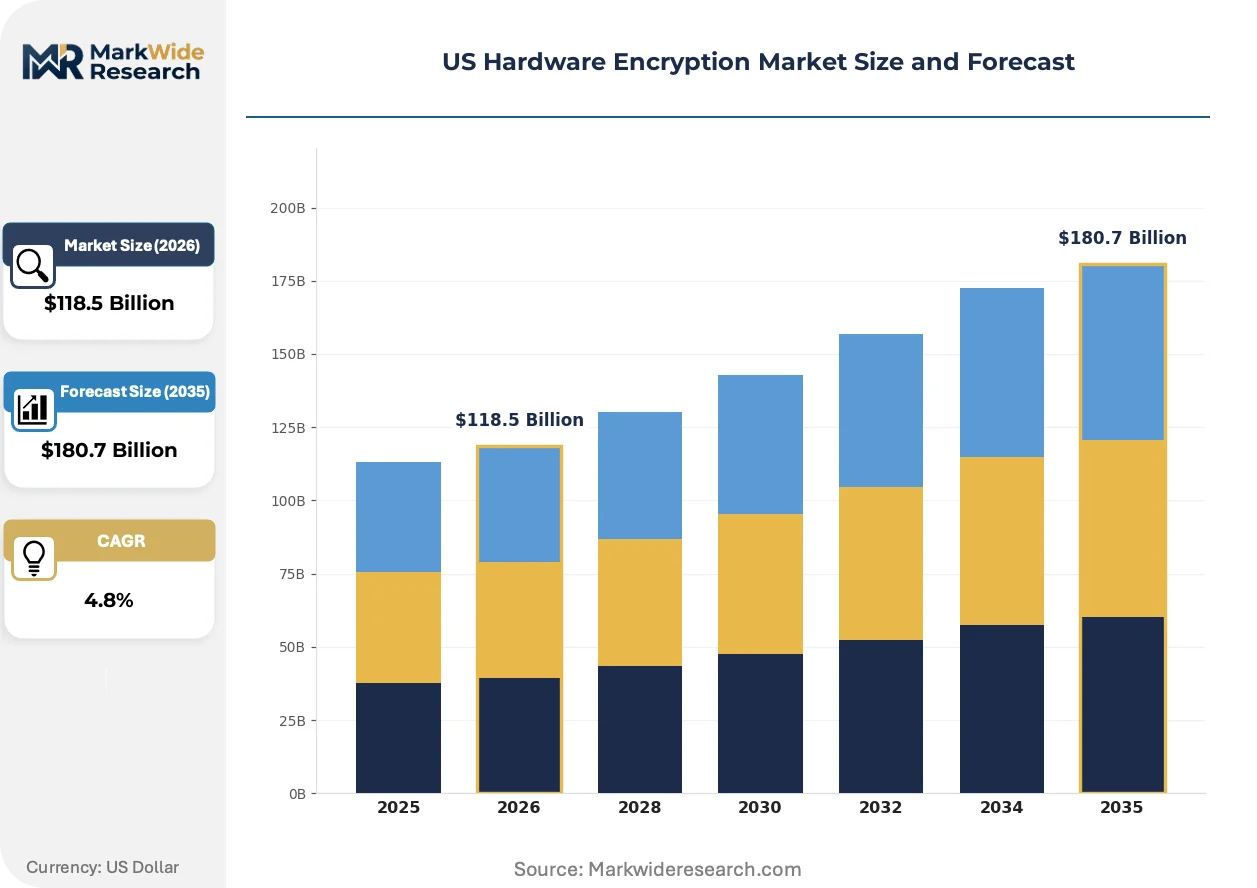
| Market Size in 2026 | $118.5 Billion |
| Market Size in 2035 | $180.7 Billion |
| CAGR (2026 – 2036) | 4.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: USB Tokens, Hard Disk Drives, Secure Network Equipment, Smart Cards Application: Data Storage, Network Security, Endpoint Protection, Cloud Security End User: Government, BFSI, Healthcare, Retail Deployment: On-premises, Hybrid, Cloud-based, Remote |
| Companies Covered | Western Digital Technologies, Micron Technology, Inc., Seagate Technology, Kingston Technology Corporation, Intel Corporation, NetApp, Inc., Thales e-Security, Inc., Kanguru Solutions, WinMagic Inc., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
US Hardware Encryption Market Trends and Innovations
Hardware encryption architectures are converging with quantum-resistant design principles, forcing simultaneous optimization for current AES performance and future algorithm agility. This dual-track development is compressing traditional product lifecycles and reallocating R&D budgets toward speculative silicon capabilities.
Self-encrypting drive controllers with embedded post-quantum cryptographic primitives are collapsing the traditional separation between current-generation and next-generation security silicon. Hyperscale operators in Northern Virginia and California are piloting these hybrid designs to avoid forklift upgrades when NIST finalizes lattice-based standards. The structural consequence is vendor consolidation around suppliers capable of field-upgradable firmware architectures.
HIPAA encryption mandates for healthcare data-at-rest are tightening audit requirements for hardware module provenance. Covered entities must now document supply chain integrity for encryption components, forcing vendors to implement component-level traceability systems. Medical device manufacturers and hospital networks are responding by restricting procurement to suppliers with validated manufacturing facility certifications.
Enterprise buyers are unbundling key-management services from hardware procurement, creating discrete purchasing decisions for encryption engines and credential lifecycle management. Cloud service providers and financial institutions are driving this separation to maintain operational control over cryptographic material. The shift is most visible in Northern Virginia's federal contracting corridor, where agencies demand sovereign key custody independent of drive vendors.
US Hardware Encryption Market Segmentation
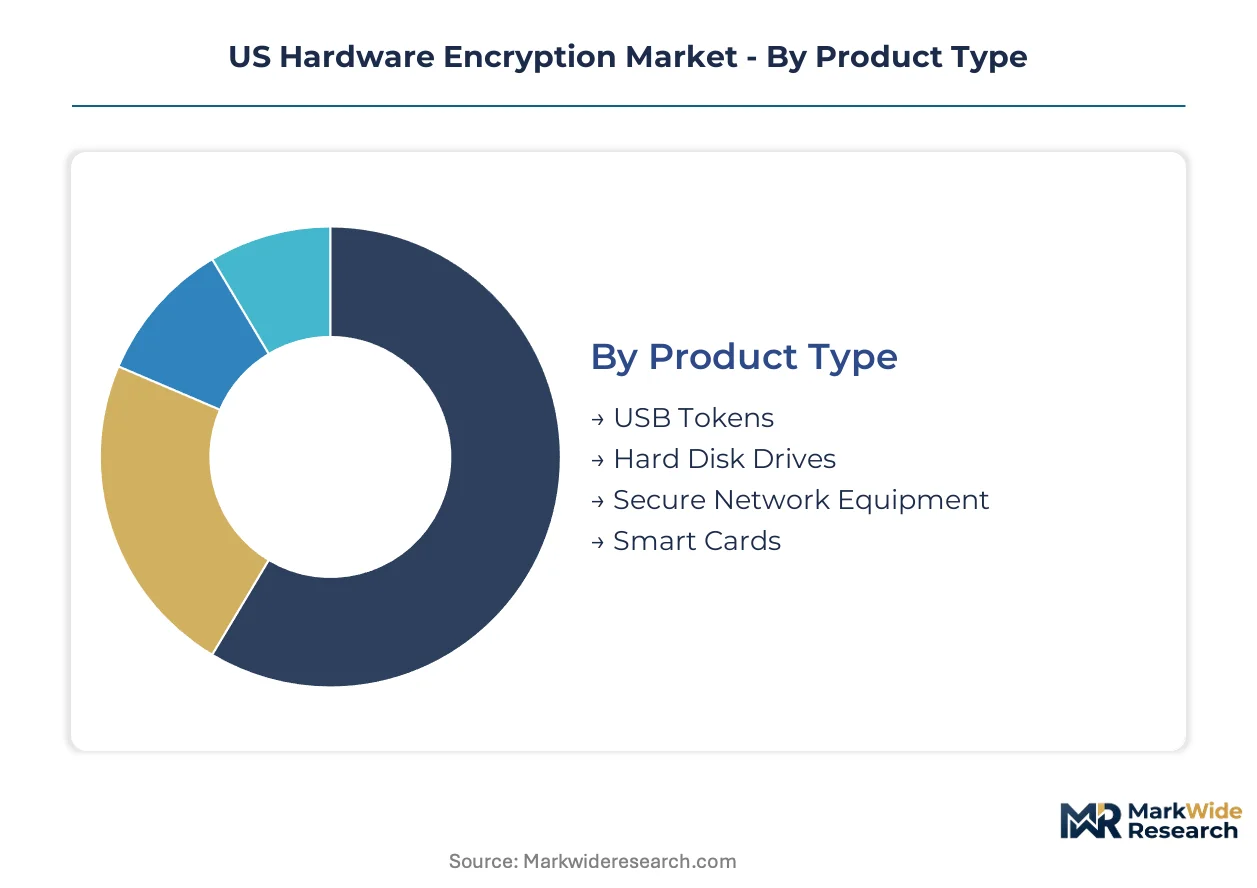
Hardware encryption architectures fragment across distinct technical layers, each commanding separate procurement cycles and certification requirements. Understanding these boundaries reveals where NIST FIPS 140-3 compliance costs concentrate and where margin pools shift between silicon suppliers and systems integrators.
Product Type:
Mature storage-centric modules dominate procurement volume, while emerging network-integrated designs capture expanding security budgets across federal and enterprise verticals.
- Hard Disk Drives:Self-encrypting drive controllers with embedded AES-256 engines process cryptographic operations independent of host CPU resources. Northern Virginia hyperscale operators and California data centers drive concentrated demand for FIPS 140-3 validated units under SEC cybersecurity disclosure pressure.
- Secure Network Equipment:Hardware security modules and encrypted network processors safeguard data-in-motion across distributed edge architectures. Defense contractors and cloud infrastructure providers in Northern Virginia's federal contracting corridor are accelerating procurement as CMMC framework requirements tighten.
- USB Tokens:Portable authentication devices with secure element chips retain niche strength in regulated federal workflows despite enterprise migration toward cloud-based alternatives.
- Smart Cards:Contact and contactless credential carriers support legacy government identification systems and healthcare access control deployments.
Hard Disk Drives handles the majority of throughput; Secure Network Equipment is the fastest mover on share.
Application:
Cost-tier segmentation separates foundational data-at-rest protection from premium data-in-motion and cloud-native security architectures.
- Data Storage:Encryption engines embedded within storage controllers protect information at rest across enterprise and federal data centers. HIPAA-covered entities and financial institutions in California's Silicon Valley corridor are tightening audit requirements for hardware module provenance and supply chain integrity documentation.
- Cloud Security:Hardware-rooted trust anchors and encrypted key hierarchies secure multi-tenant infrastructure. Hyperscale operators are unbundling key-management services from drive procurement to maintain sovereign cryptographic custody independent of component vendors.
- Network Security:Encrypted packet processing and secure tunnel termination defend perimeter and east-west traffic flows.
- Endpoint Protection:Device-level encryption modules secure laptops, mobile devices, and IoT endpoints against physical extraction attacks.
Data Storage commands the largest installed base; Cloud Security is climbing the fastest as workload migration accelerates.
End User:
Customer-type differentiation reflects divergent compliance burdens, with federal mandates forcing premium-certified procurement against commercial cost optimization.
- Government:Federal agencies and defense contractors operate under strict NIST FIPS 140-3 and CMMC framework requirements that restrict contract eligibility to validated module suppliers. Procurement concentrates through Northern Virginia's federal contracting corridor with mandatory sovereign key custody provisions.
- Healthcare:HIPAA encryption mandates for data-at-rest are tightening hardware module provenance requirements, forcing covered entities to document supply chain integrity and restrict procurement to certified manufacturing facilities.
- BFSI:Financial institutions balance SEC cybersecurity disclosure rules against operational cost pressures, driving selective hardware deployment for highest-risk data assets.
- Retail:Payment card industry compliance and customer data protection requirements support moderate encryption hardware adoption, with preference for integrated solutions over standalone modules.
Government absorbs the highest certification overhead; Healthcare is gaining share fastest as audit requirements harden.
Deployment:
Volume concentration follows infrastructure ownership patterns, with customer-controlled environments commanding hardware encryption investment against shared-responsibility cloud models.
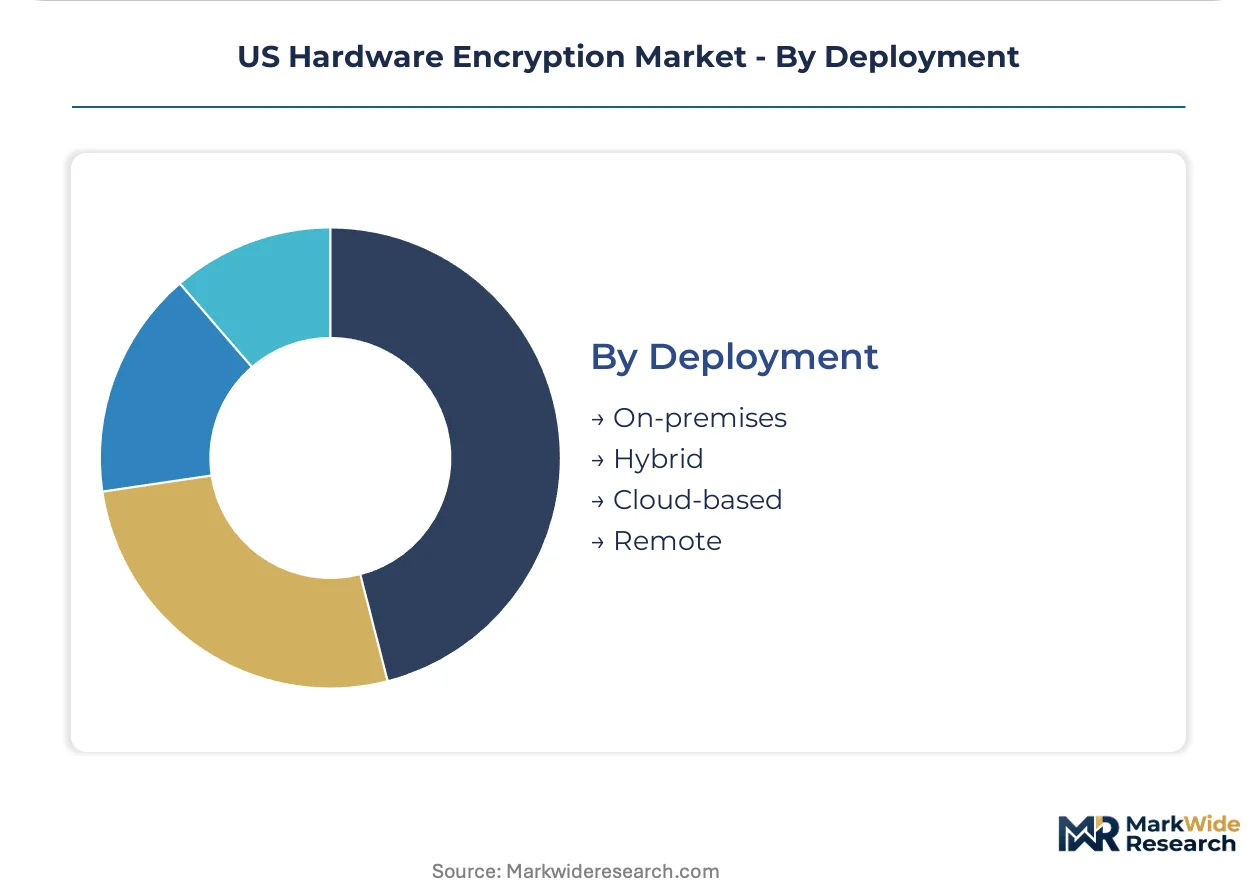
- On-premises:Customer-operated data centers and enterprise facilities deploy dedicated encryption hardware with full administrative control over cryptographic material. Federal agencies and defense contractors mandate on-premises deployment for classified and controlled unclassified information processing.
- Hybrid:Split workload architectures combine on-premises encryption hardware with cloud-integrated key management. Northern Virginia cloud infrastructure providers are piloting field-upgradable firmware designs to avoid forklift upgrades during post-quantum algorithm transitions.
- Cloud-based:Encryption services delivered as infrastructure components shift hardware procurement decisions to cloud service providers, reducing direct enterprise encryption hardware demand.
- Remote:Distributed workforce and edge computing nodes require portable or embedded encryption modules for endpoint data protection.
On-premises retains the deepest certification requirements; Hybrid is expanding most quickly as workload portability demands grow.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Federal procurement patterns concentrate demand in Northern Virginia and California, while commercial adoption spreads across Texas, New York, and Pacific Northwest data center corridors with distinct compliance burdens and infrastructure ownership models.
Northern Virginia
The Department of Defense's CMMC framework and NIST FIPS 140-3 mandates drive concentrated procurement of validated self-encrypting drives through federal contracting corridors. Defense contractors require sovereign key custody provisions independent of component vendors. Ashburn and Reston data center clusters host hyperscale cloud infrastructure with embedded AES-256 storage controllers.
California
SEC cybersecurity disclosure rules accelerate enterprise hardware encryption adoption across Silicon Valley enterprise campuses and Bay Area hyperscale facilities. HIPAA-covered entities in San Francisco and Los Angeles medical corridors tighten audit requirements for hardware module provenance documentation. NAND supply chain integration from captive foundry partnerships supports controller fabrication.
Texas
Energy sector data protection requirements and financial services compliance drive demand for hardware security modules in Dallas-Fort Worth enterprise data centers. State-level critical infrastructure regulations supplement federal encryption mandates for oil and gas operators. Austin's emerging cloud corridor attracts field-upgradable firmware pilot programs from edge computing architects.
New York Metro
Financial services SEC disclosure exposure and BFSI operational risk frameworks sustain premium-tier hardware encryption procurement across Manhattan and Jersey City trading infrastructure. State cybersecurity regulations for insurance and banking verticals mandate hardware-rooted trust anchors. Westchester County enterprise facilities deploy hybrid cloud encryption architectures with sovereign key management.
Pacific Northwest
Cloud service provider headquarters concentration in Seattle and Portland drives unbundled procurement of encryption engines separate from key-management services. Enterprise buyers demand firmware-upgradable designs to hedge post-quantum algorithm transitions. Regional data centers pilot lattice-based cryptographic primitives ahead of NIST standardization.
US Hardware Encryption Market Competitive Landscape
Capability concentration sits with established certification infrastructure holders; scale advantage sits with vertically integrated NAND suppliers. The vendor base separates into three functional tiers: federal-validated module specialists, captive-supply storage integrators, and key-management service unbundlers. Consolidation pressure favors incumbents with dedicated NIST compliance teams against mid-tier suppliers frozen by 18-24 month validation cycles. Dominant competitive moves include backward integration into controller fabrication and geographic clustering around Northern Virginia federal procurement corridors.
Within the federal-validated tier, Thales e-Security, Inc. and Western Digital Technologies occupy positions anchored by established FIPS 140-3 certification infrastructure. Kingston Technology Corporation represents the captive-supply archetype with vertically controlled NAND sourcing. These three exemplify the structural bifurcation between compliance-driven premium positioning and scale-driven cost optimization across government and commercial verticals.
| Leading Market Players |
|---|
| Western Digital Technologies |
| Micron Technology, Inc. |
| Seagate Technology |
| Kingston Technology Corporation |
| Intel Corporation |
| NetApp, Inc. |
| Thales e-Security, Inc. |
| Kanguru Solutions |
| WinMagic Inc. |
| Others |
Pricing and Supply Chain Analysis
East Asian foundry capacity in Taiwan and South Korea anchors controller fabrication for US encryption module vendors, translating concentrated upstream supply into asymmetric pricing power for certified suppliers against mid-tier competitors frozen by validation timelines. NAND flash supply chain integration determines margin capture across the value chain, with captive-sourcing vendors commanding premium positioning in federal procurement corridors.
Pricing Analysis
Long-term offtake agreements dominate federal procurement channels, while spot-market dynamics govern commercial volume transactions. Three-tier pricing structure across FIPS 140-3 Level 3 certified, Level 2 validated, and uncertified commercial tiers separates government-grade premiums from cost-optimized alternatives. Cost compression in mid-tier commercial modules is intensifying because hyperscale buyers unbundle key-management services from hardware procurement. Federal agencies exhibit lowest price sensitivity due to sovereign key custody mandates, while retail and SMB segments drive hardest bargain on per-unit costs.
Supply Chain Analysis
Contract-manufacturing concentration rests with TSMC and Samsung Foundry for advanced encryption controller silicon, while ASE Group and Amkor Technology handle post-fab packaging and test. Taiwan, South Korea, and Japan anchor wafer supply for secure element chips and NAND flash memory. Raw material dependencies span high-purity silicon wafers, rare earth elements for magnetic components, and specialized epoxy resins for packaging. Single-source vulnerability around leading-edge foundry nodes in Taiwan exposes US module vendors to geopolitical disruption. Distribution runs through authorized federal contractors in Northern Virginia and direct OEM relationships with hyperscale operators in California.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Software-based encryption and cloud-native key-management services threaten hardware module incumbents with functional substitution, forcing defensive capability investments to preserve contract eligibility under tightening federal mandates.
For Market Incumbents: Entrench certification infrastructure advantages by accelerating NIST FIPS 140-3 Level 3 validation pipelines ahead of CMMC framework tier expansions. Deepen backward integration into controller design to reduce foundry dependency exposure and capture margin pools currently flowing to fabless competitors. Sovereign key custody requirements create durable switching costs that incumbents must exploit through integrated hardware-software offerings. For New Entrants and Emerging Players: Build out specialized module configurations targeting CMMC Level 2 contract eligibility tiers where validation timelines compress competitive response windows. Healthcare verticals in California and Texas medical corridors present most penetrable white-space as HIPAA audit requirements harden hardware provenance documentation. Go-to-market through GPO contracts and hospital system partnerships bypasses incumbent federal channel lock-in. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors vendors with field-upgradable firmware architectures capable of absorbing post-quantum algorithm transitions without silicon respins. Long-term viability hinges on R&D pipelines with lattice-based cryptographic primitives and established NIST compliance relationships. Watch NIST standardization announcements as inflection signal for valuation repricing across the vendor base.| Strategic Initiative | Industry Significance |
|---|---|
| FIPS 140-3 Level 3 Certification Acceleration | Validates module eligibility for Department of Defense CMMC tiered contracts ahead of competitor timelines. |
| Post-Quantum Cryptographic R&D Investment | Positions silicon designs for NIST lattice-based standards without forklift infrastructure upgrades. |
| Key-Management Service Unbundling | Captures recurring revenue streams from federal agencies demanding sovereign cryptographic custody. |
| Healthcare Supply Chain Traceability Systems | Meets HIPAA audit requirements for hardware module provenance documentation in medical corridors. |
| Edge Computing Security Architecture Partnerships | Expands addressable market beyond data-at-rest into distributed data-in-motion protection nodes. |
Research Methodology
Cross-validation between primary interviews with defense procurement officers, NIST certification consultants, hyperscale data center engineers, and healthcare IT security directors anchors the qualitative findings against secondary validation from SEC cybersecurity disclosure filings, NIST validation database records, and hyperscaler capex expenditure reports. Bottom-up demand modeling triangulates against top-down market sizing across federal budget allocations and commercial encryption hardware procurement disclosures.
Calibration against historical NIST validation cycle durations and federal contract award patterns informs the projection framework across the analysis window. Segmentation dimensions span product type, application vertical, end-user compliance tier, and deployment architecture. CAGRs derive from regression analysis of procurement volume trends against regulatory mandate implementation schedules. Hyperscale operator infrastructure expansion timelines and CMMC framework rollout phases constitute key forecast inputs.
Stress conditions across foundry capacity constraints, tariff exposure scenarios, and post-quantum algorithm standardization delays were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions regarding federal mandate adherence rates and commercial migration timelines from software to hardware encryption. Quarterly review of NIST validation queue lengths, hyperscaler capex guidance revisions, and CMMC tier adoption metrics is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Messaging Security Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
DC and PKI Market
Security Software
Quantum Key Distribution System Market
Security Software
Global Data Masking Market
Security Software
Global Reputation Protection Software Market
Security Software
Global Security Assertion Markup Language (SAML) Authentication Market
Security Software
Secure Flash Drive Market
Security Software
Global Digital Vehicle Forensics Market
Security Software
Fraud Detection Software Market
Security Software
AI Security Platforms Market
Security Software
Secure Web Gateway Market
Security Software
Global Enterprise Data Loss Prevention Software Market
Security Software
Global Digital Signature Software Market
Security Software
Privacy Management Software Market
Security Software
Cloud Security Software Market