
 Device Vulnerability Management Market | 2026-2036
Device Vulnerability Management Market Size, Share, and Industry Trends Forecast 2026-2036
Device Vulnerability Management Market Analysis
Agentic AI and autonomous patching engines are tilting how security platforms architect remediation workflows. Tenable, Inc. leverages deep asset telemetry to sustain leadership in exposure management breadth. Microsoft Corporation anchors enterprise trust through native integration with Azure device directories and Entra identity layers. Rapid7, Inc. differentiates by embedding managed detection and response with vulnerability prioritization for mid-market buyers.
Device vulnerability management encompasses the systematic identification, classification, prioritization, and remediation of security weaknesses across endpoint hardware, IoT sensors, operational technology controllers, and mobile assets, typically operating through continuous passive or active scanning with CVSS scoring and exploitability indexing. Its primary commercial purpose is to compress the mean time to remediate while preventing lateral movement by threat actors through unpatched device surfaces. Cloud-based solutions are capturing the fastest expansion as organizations retire on-premise scan appliances in favor of elastic, API-first architectures that federate across multi-cloud estates. Healthcare institutions represent the most concentrated margin pool among end users, given FDA guidance on postmarket cybersecurity management for connected medical devices and the catastrophic cost of clinical downtime from ransomware.
NIST, FDA, and HIPAA collectively shape demand architecture in the United States by embedding vulnerability management into procurement baselines, medical device premarket submissions, and protected health information safeguards. The EU AI Act and MDR are extending similar obligations across European health systems and high-risk AI-enabled devices. Stakeholders must monitor how regulatory convergence between medical device safety and cybersecurity standards redistributes compliance burdens onto device manufacturers versus healthcare delivery organizations.
Market Dynamics
Agentic AI architectures are compressing remediation timelines by automating vulnerability prioritization and patch deployment decisions without human intervention, fundamentally restructuring how security operations centers allocate analyst bandwidth.
Growth Catalysts
- FDA Postmarket Guidance:Healthcare delivery organizations must maintain continuous monitoring of connected medical devices, creating sustained demand for passive scanning solutions that avoid clinical disruption.
- Operational Technology Convergence:Manufacturing and energy sectors are extending vulnerability management to industrial control systems as IT-OT network boundaries dissolve.
- United States Federal Procurement Rules:Contractual vulnerability disclosure mandates embedded in device acquisitions are forcing vendors to integrate exposure management capabilities.
Market Restraints
- Specialized Talent Scarcity:Shortage of professionals holding both CVSS scoring expertise and medical device engineering knowledge limits deployment velocity in healthcare.
- Legacy Asset Protocol Fragmentation:Proprietary communication standards in aging industrial equipment prevent uniform scanning coverage across heterogeneous device estates.
- Patch Certification Delays:FDA validation requirements for medical device firmware updates extend mean time to remediate beyond acceptable risk windows.
Strategic Opportunities
- EU AI Act Compliance Services:High-risk AI-enabled medical devices require continuous security monitoring, opening service revenue streams for European healthcare systems.
- API-First Architecture Adoption:Elastic cloud-native platforms are displacing on-premise appliances as multi-cloud estates federate vulnerability data across distributed environments.
- Mid-Market Managed Detection Bundles:Integrated vulnerability prioritization with MDR services addresses resource-constrained buyers previously priced out of enterprise solutions.
Industry Challenges
- Entrenched Scanning Appliance Infrastructure:Capital depreciation cycles and change management inertia slow migration to cloud-based continuous monitoring architectures.
- Cross-Functional Coordination Friction:Biomedical engineering, IT security, and clinical operations teams maintain conflicting priorities around device availability versus patch urgency.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Device Vulnerability Management Market |
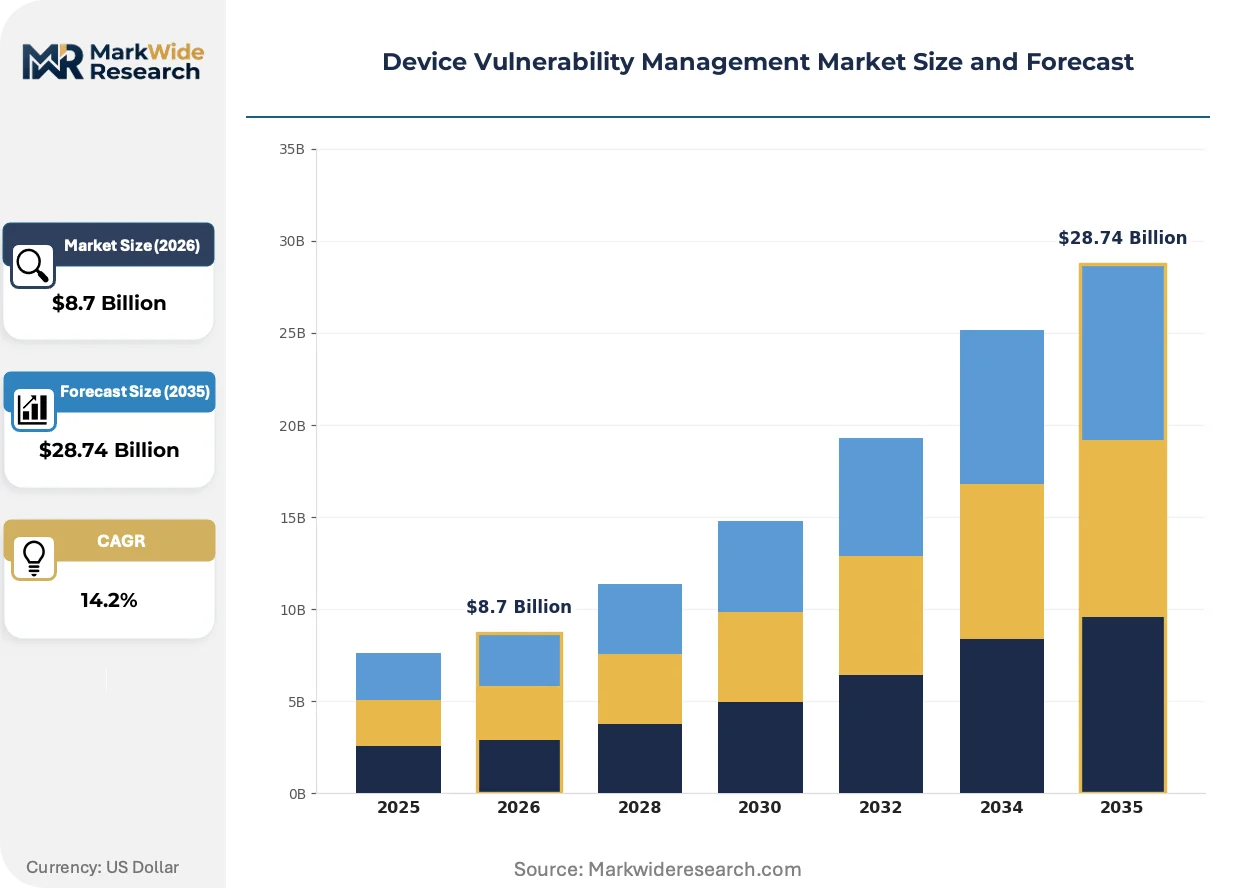
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $28.74 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: On-Premise Solutions, Cloud-Based Solutions, Hybrid Solutions, Consulting Services Deployment Model: Private Deployment, Public Deployment, Hybrid Deployment, Managed Services End User: Healthcare Institutions, Financial Services, Government Agencies, Educational Organizations Service Type: Incident Management, Risk Assessment, Compliance Management, Security Training |
| Companies Covered | Tenable, Inc., Microsoft Corporation, IBM Corporation, Qualys, Inc., Cisco Systems, Rapid7, Inc., Hewlett-Packard Enterprise Company, Veracode, Inc., CrowdStrike Holdings, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Device Vulnerability Management Market Emerging Trajectories
Remediation workflows are virtualizing through autonomous patching engines that eliminate human approval bottlenecks. Three developments are accelerating this transformation across vendor roadmaps and buyer procurement criteria.
Agentic AI is virtualizing vulnerability response orchestration by embedding large language models into exposure management platforms. Healthcare systems with limited security staffing are deploying these systems to interpret scan outputs and generate remediation playbooks automatically. The technology is compressing analyst decision cycles from hours to minutes while reducing false-positive fatigue.
NIST Cybersecurity Framework revisions are mandating asset discovery and patch management protocols for federal contractors and critical infrastructure operators. United States healthcare institutions must now demonstrate continuous visibility into connected device inventories to maintain Medicare reimbursement eligibility. Device manufacturers are responding by pre-integrating telemetry APIs that feed directly into buyer vulnerability management dashboards.
Consumption-based pricing models are displacing perpetual license structures as buyers demand elasticity aligned with seasonal device procurement cycles. Healthcare systems with fluctuating capital budgets prefer subscription tiers that scale with active endpoint counts rather than fixed appliance deployments. This shift is most pronounced in United States academic medical centers undergoing multi-year digital transformation programs.
Device Vulnerability Management Market Segmentation
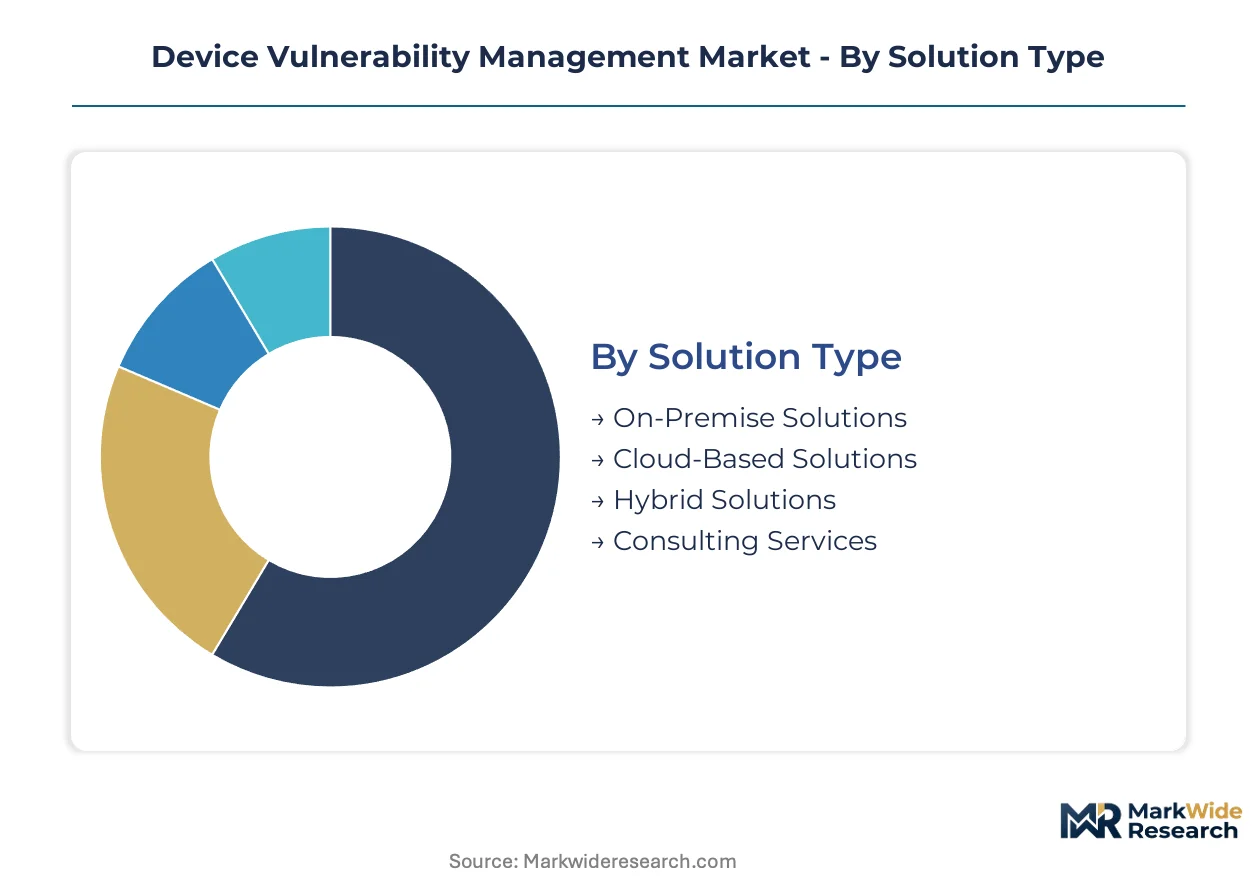
Device vulnerability management architectures fragment across solution delivery modes, operational models, and buyer capabilities. Healthcare institutions with constrained security staffing gravitate toward managed consumption models, while federal contractors prioritize on-premise control for classified environments.
Solution Type:
Deployment flexibility spans legacy infrastructure preservation through elastic cloud-native consumption, with hybrid architectures bridging compliance-bound data centers and distributed endpoints.
- On-Premise Solutions:Hardware appliances and software deployed within buyer-controlled data centers maintain air-gapped scanning for classified government facilities and HIPAA-constrained hospital networks. United States defense contractors and intelligence community agencies mandate these configurations for systems processing controlled unclassified information, though capital depreciation cycles and patch latency constrain refresh velocity.
- Cloud-Based Solutions:API-first architectures federate vulnerability telemetry across multi-cloud estates without appliance maintenance overhead. Healthcare delivery organizations with fluctuating device procurement cycles prefer subscription elasticity that scales with active endpoint counts rather than fixed infrastructure commitments.
- Hybrid Solutions:Split architectures anchor sensitive scanning functions on-premise while offloading analytics and reporting to cloud substrates. Financial services institutions with branch-distributed ATM fleets deploy this model to balance regulatory data residency with centralized visibility.
- Consulting Services:Advisory engagements address capability gaps in CVSS scoring expertise and medical device engineering knowledge. Boutique security firms staff remediation playbooks for mid-market buyers lacking dedicated vulnerability management teams.
Established volume favors On-Premise Solutions; emerging adoption favors Cloud-Based Solutions.
Deployment Model:
Operational control preferences stratify by data sensitivity classification, with public deployment accelerating among buyers prioritizing speed over sovereignty.
- Private Deployment:Dedicated infrastructure instances isolate scanning traffic for single-tenant environments. Pharmaceutical manufacturers with proprietary device firmware intellectual property mandate private deployment to prevent co-tenant exposure risks.
- Public Deployment:Shared-tenant cloud resources deliver cost efficiency for resource-constrained educational organizations and municipal healthcare systems. The model sacrifices customization depth for rapid provisioning and consumption-based economics.
- Hybrid Deployment:Policy-driven workload placement routes critical asset scanning to private infrastructure while relegating commodity endpoint coverage to public substrates. Energy sector operators with geographically dispersed generation assets leverage this model for OT-IT convergence scenarios.
- Managed Services:Third-party security operations centers assume continuous monitoring and remediation orchestration. Government agencies facing federal hiring freezes outsource vulnerability response to cleared contractors with existing security clearances and healthcare domain expertise.
Private Deployment retains the largest installed base; Managed Services are climbing the fastest as staffing constraints intensify.
End User:
Regulatory pressure intensity and device downtime cost profiles concentrate demand among institutions where clinical or financial continuity carries catastrophic failure modes.
- Healthcare Institutions:Academic medical centers and community hospital systems face FDA postmarket guidance mandating continuous monitoring of connected medical devices. The catastrophic cost of clinical downtime from ransomware compresses procurement cycles for passive scanning solutions that avoid operational disruption.
- Financial Services:Retail banks and payment processors extend vulnerability management to ATM fleets, point-of-sale terminals, and mobile banking infrastructure. PCI-DSS compliance deadlines and card brand audit findings accelerate replacement of legacy scan appliances.
- Government Agencies:Civilian departments and defense components embed vulnerability disclosure requirements into device acquisition contracts per United States federal procurement rules. NIST Cybersecurity Framework revisions mandate asset discovery and patch management protocols for Medicare reimbursement eligibility.
- Educational Organizations:Universities and K-12 districts manage heterogeneous device estates spanning research instrumentation, administrative systems, and student-owned BYOD endpoints. Budget volatility and distributed campus architectures favor elastic subscription tiers over capital-intensive infrastructure.
Healthcare Institutions command premium pricing; Educational Organizations represent the steepest expansion trajectory as ransomware targeting intensifies.
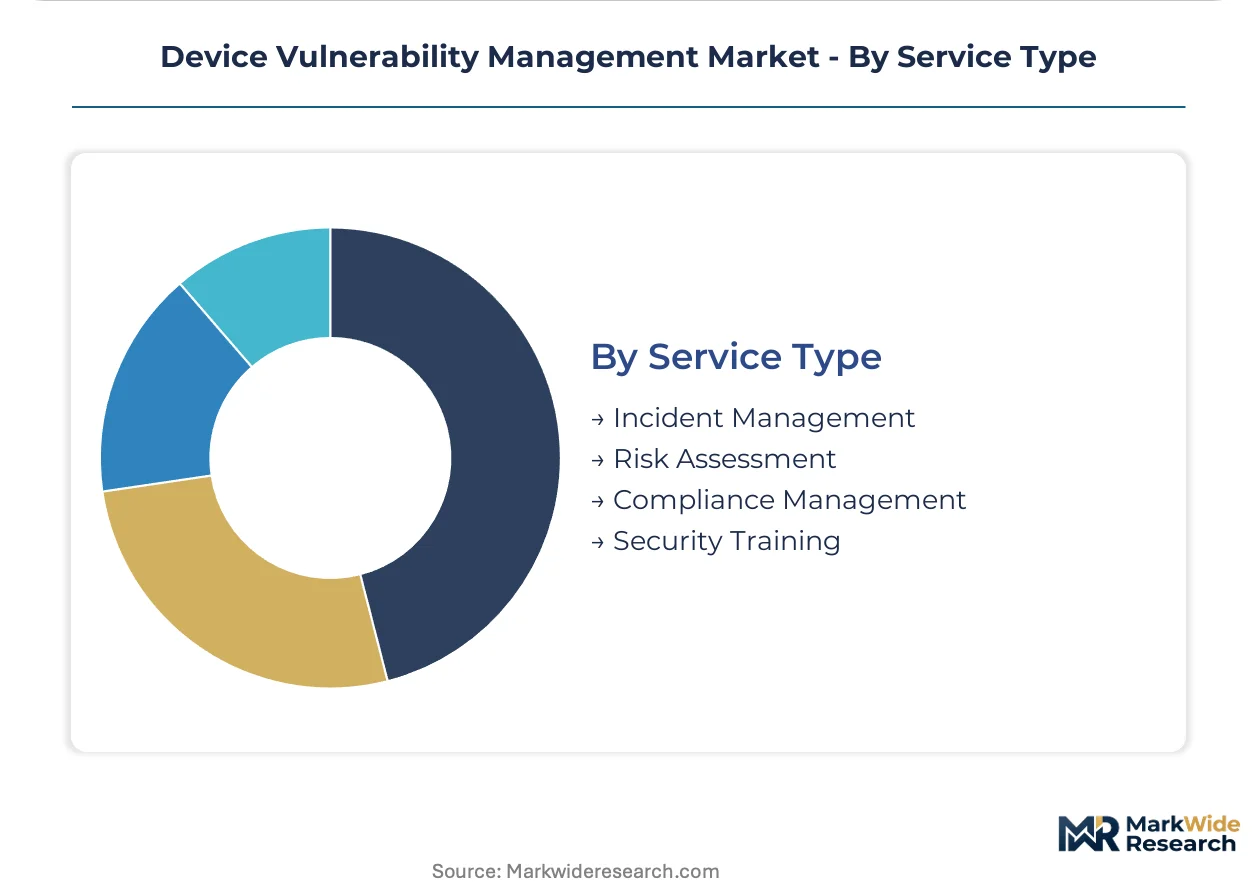
Service Type:
Value-added capabilities extend beyond scanning automation to risk quantification, regulatory documentation, and workforce enablement.
- Incident Management:Structured response workflows coordinate containment, eradication, and recovery across compromised device populations. Healthcare systems deploy these services to satisfy cyber insurance policy requirements for documented incident response capabilities.
- Risk Assessment:Quantitative analysis of exploitability and business impact prioritizes remediation queues beyond raw CVSS scoring. Financial services institutions integrate these assessments into enterprise risk management dashboards for board-level reporting.
- Compliance Management:Automated evidence collection and control mapping streamline HIPAA, FDA, and NIST audit preparation. Device manufacturers pre-integrate telemetry APIs that feed directly into buyer compliance documentation systems.
- Security Training:Workforce education addresses the specialized talent scarcity limiting deployment velocity in healthcare and OT environments. Curriculum modules combine CVSS methodology with domain-specific device engineering knowledge.
Risk Assessment dominates current procurement; Incident Management is gaining share fastest as mean-time-to-remediate targets tighten.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States-based cybersecurity vendors export device vulnerability management platforms to healthcare systems across Germany, Japan, and the United Kingdom, establishing transatlantic and transpacific trade corridors for continuous monitoring technologies.
United States
Federal procurement rules mandate vulnerability disclosure requirements in device contracts, while FDA postmarket guidance compels continuous monitoring of connected medical devices. NIST Cybersecurity Framework revisions enforce asset discovery protocols for Medicare reimbursement eligibility. Academic medical centers in Boston and the Research Triangle deploy passive scanning solutions to minimize clinical disruption during remediation.
Germany
Industrial manufacturing clusters drive demand for OT-IT convergence security as IT-OT network boundaries dissolve across automotive and chemical plants. The EU AI Act and MDR extend continuous security monitoring obligations to high-risk AI-enabled medical devices. Bavarian medical technology manufacturers in the Munich-Stuttgart corridor integrate telemetry APIs to satisfy cross-border healthcare procurement standards.
United Kingdom
NHS digital transformation programs accelerate replacement of legacy scan appliances with cloud-native architectures. GDPR and emerging post-Brexit cybersecurity frameworks mandate documented vulnerability response capabilities for healthcare delivery organizations. London-based financial services institutions extend exposure management to ATM fleets and mobile banking infrastructure under PCI-DSS compliance deadlines.
Japan
Manufacturing and energy sectors prioritize vulnerability management for industrial control systems amid critical infrastructure protection mandates. METI guidelines and PMDA medical device regulations align postmarket cybersecurity expectations with international standards. Osaka-Tokyo industrial corridors deploy hybrid scanning architectures to balance proprietary OT protocol coverage with centralized cloud analytics.
India
Healthcare digitization under the National Digital Health Mission creates procurement demand for managed detection and response bundles among resource-constrained hospital networks. CDSCO medical device regulations and BIS cybersecurity standards gradually converge with FDA and EU MDR frameworks. Hyderabad and Bengaluru health-tech clusters incubate domestic vulnerability management service providers targeting mid-market buyers.
Device Vulnerability Management Market Vendor Landscape
Channel-controlling players compete with product-specialist players across a moderately consolidated structure where scale advantages in telemetry data and cloud infrastructure concentration create tiered competitive positions. Enterprise platforms with native identity and directory integration anchor the premium segment, while managed service specialists capture mid-market expansion. Two strategic archetypes dominate: comprehensive exposure management suites and embedded security-native platforms. M&A activity concentrates on telemetry API acquisitions and cloud-native architecture transitions, while strategic partnerships bridge OT protocol expertise gaps.
Within the comprehensive exposure management tier, Tenable, Inc. and Qualys, Inc. exemplify archetypes built on deep asset telemetry and elastic cloud-native delivery. Microsoft Corporation anchors the embedded security-native position through directory-layer integration. Rapid7, Inc. occupies a specialist position bundling managed detection with vulnerability prioritization for staffing-constrained buyers.
| Leading Market Players |
|---|
| Tenable, Inc. |
| Microsoft Corporation |
| IBM Corporation |
| Qualys, Inc. |
| Cisco Systems |
| Rapid7, Inc. |
| Hewlett-Packard Enterprise Company |
| Veracode, Inc. |
| CrowdStrike Holdings |
| Others |
Supply Flow & Price Mechanics
Regulatory certification chokepoints for FDA-validated medical device firmware determine both tiered pricing spreads and supply chain configuration, as healthcare delivery organizations prioritize vendors with pre-integrated telemetry APIs that compress procurement cycles and reduce compliance documentation burdens.
Pricing Analysis
Next-generation agentic AI architectures command substantial premiums over legacy on-premise appliances and current-generation cloud-native platforms. Three-tier pricing structure across premium, standard, and economy levels stratifies by deployment complexity, with premium tiers bundling managed detection response and automated remediation playbooks. Pricing pressure stems from mid-market buyers demanding consumption-based elasticity aligned with seasonal device procurement cycles. Educational organizations and community hospital systems exhibit the highest price sensitivity, while academic medical centers with dedicated security budgets absorb premium positioning for passive scanning solutions that minimize clinical disruption.
Supply Chain Analysis
Extended payment terms and supply-chain finance facilities from cloud infrastructure hyperscalers have reconfigured vendor working capital requirements across the ecosystem. Software development concentrates in the United States, India, and Israel, with cloud substrate provisioning anchored in hyperscaler data center footprints across Northern Virginia, Frankfurt, and Singapore. Platform development draws from specialized cybersecurity talent pools, open-source vulnerability databases, and medical device engineering expertise. Single-source vulnerability in proprietary OT protocol coverage creates exposure for industrial control system deployments. Distribution runs through direct enterprise sales teams, value-added resellers with healthcare domain specialization, and hyperscaler marketplace listings.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation across deployment models, end-user sophistication, and regulatory jurisdictions creates multiple viable entry points, as the shift from capital-intensive appliance procurement to elastic subscription consumption fragments incumbent channel control and opens white-space for specialized service bundling.
For Market Incumbents: Entrench telemetry data advantages by deepening integration with medical device manufacturer APIs and Azure Active Directory estates, while accelerating cloud-native architecture transitions to defend against emerging specialists bundling managed detection with vulnerability prioritization for staffing-constrained buyers. For New Entrants and Emerging Players: Mid-market healthcare delivery organizations in India and Southeast Asia represent the most penetrable entry point, given resource constraints and accelerating digitization mandates under national health missions. Target managed detection and response bundles with localized compliance documentation for CDSCO and BIS alignment, leveraging channel partnerships with domestic health-tech integrators to bypass direct sales infrastructure requirements. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors telemetry API acquisitions and cloud-native architecture transitions over scale-capacity buildout. Long-term viability hinges on exposure management platform breadth and identity-layer integration depth. Monitor FDA guidance evolution on autonomous patching engines as the critical inflection signal for remediation workflow automation valuations.| Strategic Initiative | Industry Significance |
|---|---|
| Telemetry API Acquisition | Deepens asset visibility for healthcare delivery organizations under FDA postmarket guidance mandates. |
| Cloud-Native Architecture Transition | Displaces on-premise appliances as multi-cloud estates federate vulnerability data across distributed environments. |
| Managed Detection Bundle Launch | Captures mid-market buyers previously priced out of enterprise exposure management solutions. |
| OT Protocol Specialist Partnership | Bridges industrial control system coverage gaps as IT-OT network boundaries dissolve in manufacturing. |
| EU AI Act Compliance Service Development | Opens service revenue streams for high-risk AI-enabled medical device monitoring across European health systems. |
Methodological Framework
Demand-side practitioners and supply-side operators were both consulted across primary interviews with CISOs at academic medical centers, biomedical engineering directors, healthcare GPO contracts managers, and cloud security architects at hyperscaler platforms. Secondary validation drew from FDA 510(k) submissions, CMS Medicare reimbursement documentation, NIST Cybersecurity Framework revision drafts, and hospital procurement database extracts. Bottom-up endpoint count modeling and top-down security software spend analysis were triangulated to calibrate market sizing.
Calibration against historical appliance retirement cycles and cloud migration patterns anchored the analytical framework across the analysis window. Segmentation dimensions modeled include solution delivery mode, deployment model, end-user institution type, and service capability tier. CAGRs were derived from elasticity-adjusted subscription pricing trajectories and healthcare capital expenditure cycle analysis, with inputs from medical device procurement velocity and federal contracting rule evolution.
Macroeconomic conditions sit as an overlay; deviation in healthcare capital budget cycles, hyperscaler infrastructure pricing, or medical device regulatory validation timelines would shift the trajectory. Forecasts reflect documented assumptions around FDA guidance implementation pace and cloud-native platform adoption curves. Macroeconomic, regulatory, or technological deviation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Hardware OTP Token Authentication Market
Security Software
Certificate Authority Market
Security Software
Public Cloud Management and Security Services Market
Security Software
Mobile Security Market
Security Software
Global Background Check Software Market
Security Software
Global Email Verification Tools Market
Security Software
Key Management Service Market
Security Software
GDPR Software and Tools Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
United States Lawful Interception Market
Security Software
Data Privacy Software Market
Security Software
Network Security Appliance Market
Security Software
BYOD Security Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Identity and Access Management (IAM) Market
Security Software
Device-Embedded Biometric Authentication Market