
 Penetration Testing Market | 2026-2036
Penetration Testing Market Size, Share, and Industry Trends Forecast 2026-2036
Penetration Testing Market Intelligence
The shift toward continuous, automated penetration testing as a service (PTaaS) is unwinding the traditional, project-based engagement model. This evolution allows for more frequent and integrated security validation within development lifecycles. NetSPI specializes in delivering scalable PTaaS platforms for large enterprises. Bishop Fox differentiates through its focus on high-stakes red teaming and offensive security research, while Coalfire provides extensive compliance auditing and advisory services.
Penetration testing is a methodical, authorized process of simulating a cyberattack against a computer system to evaluate its security. Testers actively attempt to exploit vulnerabilities in network protocols, application code, or human behavior to measure defensive capabilities. Web Application testing remains a dominant service type, driven by the expansion of digital commerce and services. Within deployment models, the adoption of cloud-based and managed service solutions is accelerating as organizations seek flexible and expert-led security assessments.
Regulatory frameworks such as the General Data Protection Regulation (GDPR) in Europe and the Health Insurance Portability and Accountability Act (HIPAA) in the United States compel organizations to conduct regular security testing. The Payment Card Industry Data Security Standard (PCI DSS) also mandates vulnerability assessments for entities handling cardholder data. The primary decision for enterprises is how to balance automated testing for compliance with expert-led assessments for discovering complex, business-critical threats.
Market Dynamics
The market's central dynamic revolves around balancing mandatory, compliance-driven assessments against the demand for sophisticated, threat-led testing. This duality is amplified by regulations like GDPR and the high-stakes security needs of the global financial services sector.
Growth Catalysts
- Regulatory Mandates:The EU's GDPR and US's HIPAA compel regular security assessments, creating a stable demand base for compliance-focused testing.
- Expanding Attack Surfaces:Proliferation of IoT devices creates new vulnerabilities, driving demand for specialized testing beyond traditional web applications.
- Financial Sector Demand:The global financial services industry's security needs make it a primary consumer of advanced penetration testing to protect high-value assets.
Market Restraints
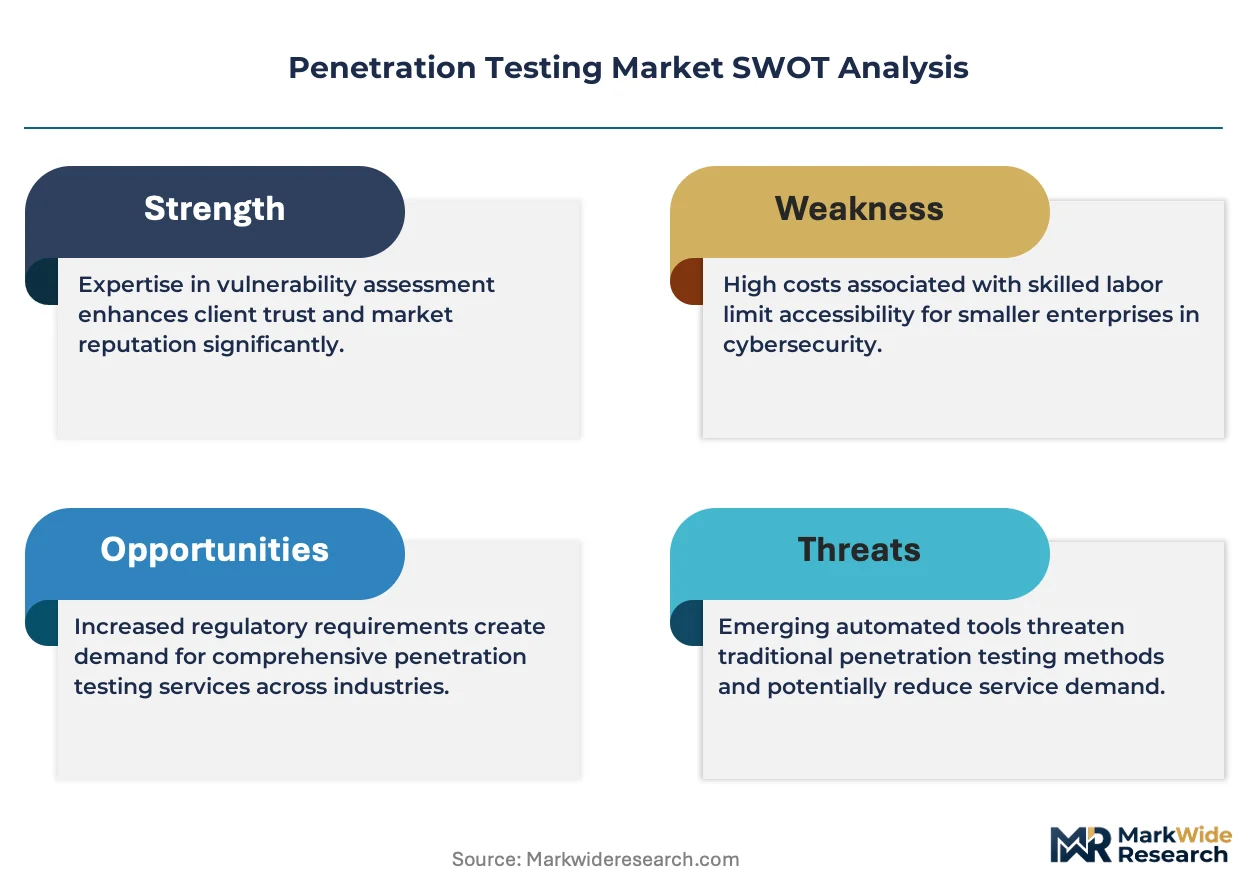
- High Service Costs:The expense of senior security talent makes comprehensive manual tests prohibitive for many smaller businesses, limiting market reach.
- Automated Tool Limitations:Automated scanners produce high false positive rates, consuming valuable analyst time for triage and diminishing perceived ROI.
- Bug Bounty Program Competition:Crowd-sourced bug bounty programs present a substitute model for vulnerability discovery, competing with traditional project-based engagements.
Strategic Opportunities
- Emerging Geographic Markets:Rapid digitalization in Southeast Asia creates white space for testing services as local data privacy regulations mature.
- AI and ML System Security:Testing AI models for unique vulnerabilities like data poisoning and adversarial attacks presents a new high-value service category.
- DevSecOps Integration:Embedding automated testing into CI/CD pipelines via PTaaS platforms captures value throughout the entire software development lifecycle.
Industry Challenges
- Talent Scarcity:A persistent global shortage of skilled offensive security engineers limits the ability of service providers to scale operations and meet client demand.
- Methodology Standardization:The absence of a uniform standard for reporting and testing creates inconsistency, making it difficult for clients to benchmark service quality.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Penetration Testing Market |
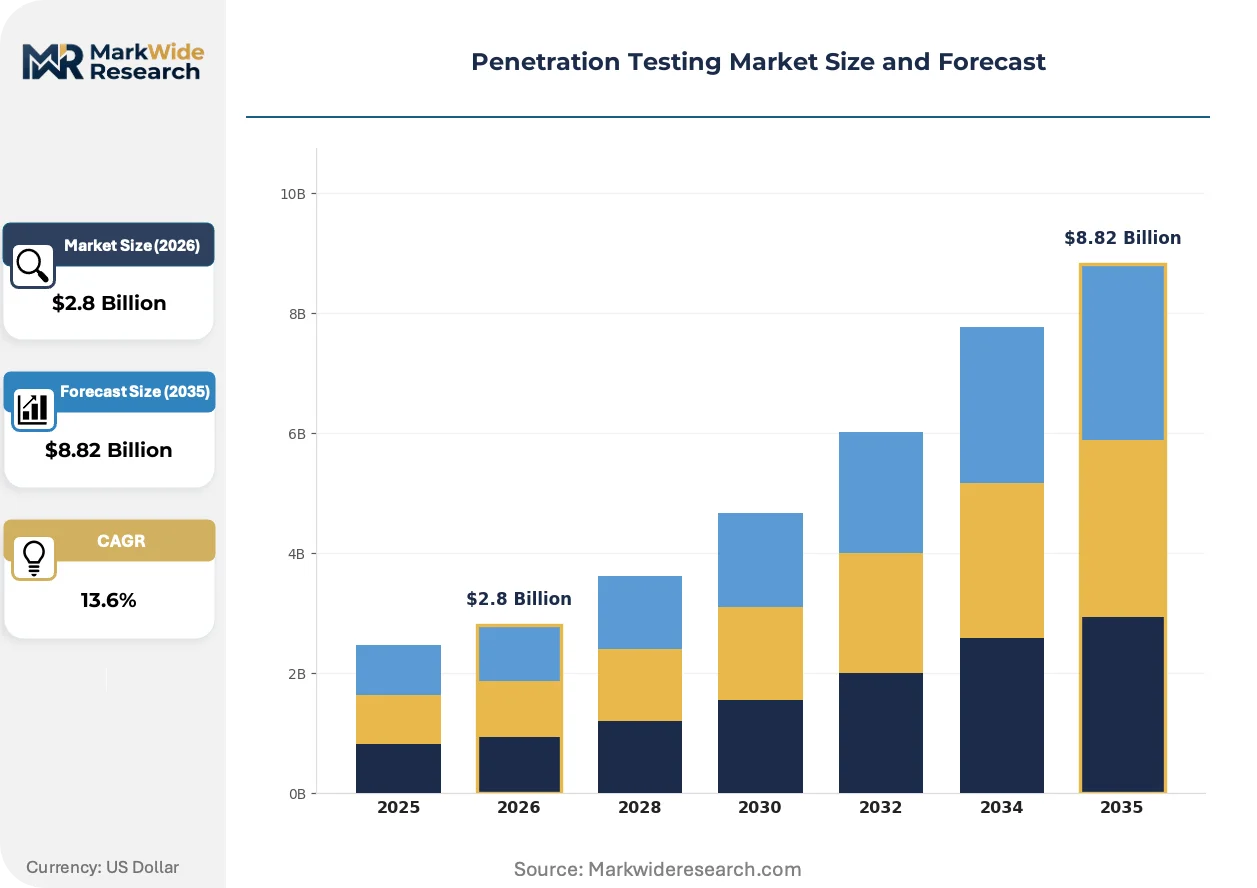
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $8.82 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Test Type: Network Penetration, Web Application, Wireless, Social Engineering, Physical, API Testing Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Service, SaaS End User: Financial Services, Telecommunications, Government Agencies, Education Sector, Hospitality, Energy Sector Service Offering: Vulnerability Assessment, Risk Management, Compliance Auditing, Security Consulting, Remediation Support, Training Services |
| Companies Covered | NetSPI, IOActive, DeepStrike, Trustwave, ScienceSoft, Bishop Fox, SpecterOps, GuidePoint Security, Coalfire, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Penetration Testing Market Strategic Shifts & Innovations
The industrialization of offensive security services is fundamentally altering market structure. A move away from artisanal, project-based work toward scalable, technology-enabled delivery models defines the current competitive environment for penetration testing providers.
Penetration Testing as a Service (PTaaS) platforms provide a hybrid model combining automated scanning with on-demand access to expert human testers. Large enterprises adopt these platforms to integrate security testing directly into their development workflows. This platform-based delivery model is supplanting the traditional, episodic, and purely manual project engagement structure.
New requirements within the Payment Card Industry Data Security Standard (PCI DSS) v4.0 push for more customized, risk-based testing. The standard allows entities to define their own testing frequency, moving from a rigid annual schedule. This change forces retail and financial sector organizations to adopt mature, continuous vulnerability management programs instead of simple compliance checks.
A shift in enterprise buying behavior is moving from procuring discrete penetration tests toward bundled service subscriptions. Buyers increasingly favor packages that combine testing with managed vulnerability management and threat intelligence. This trend is most pronounced in mid-market US and European companies that lack large, dedicated internal security teams and prefer a single security partner.
Penetration Testing Market Segmentation
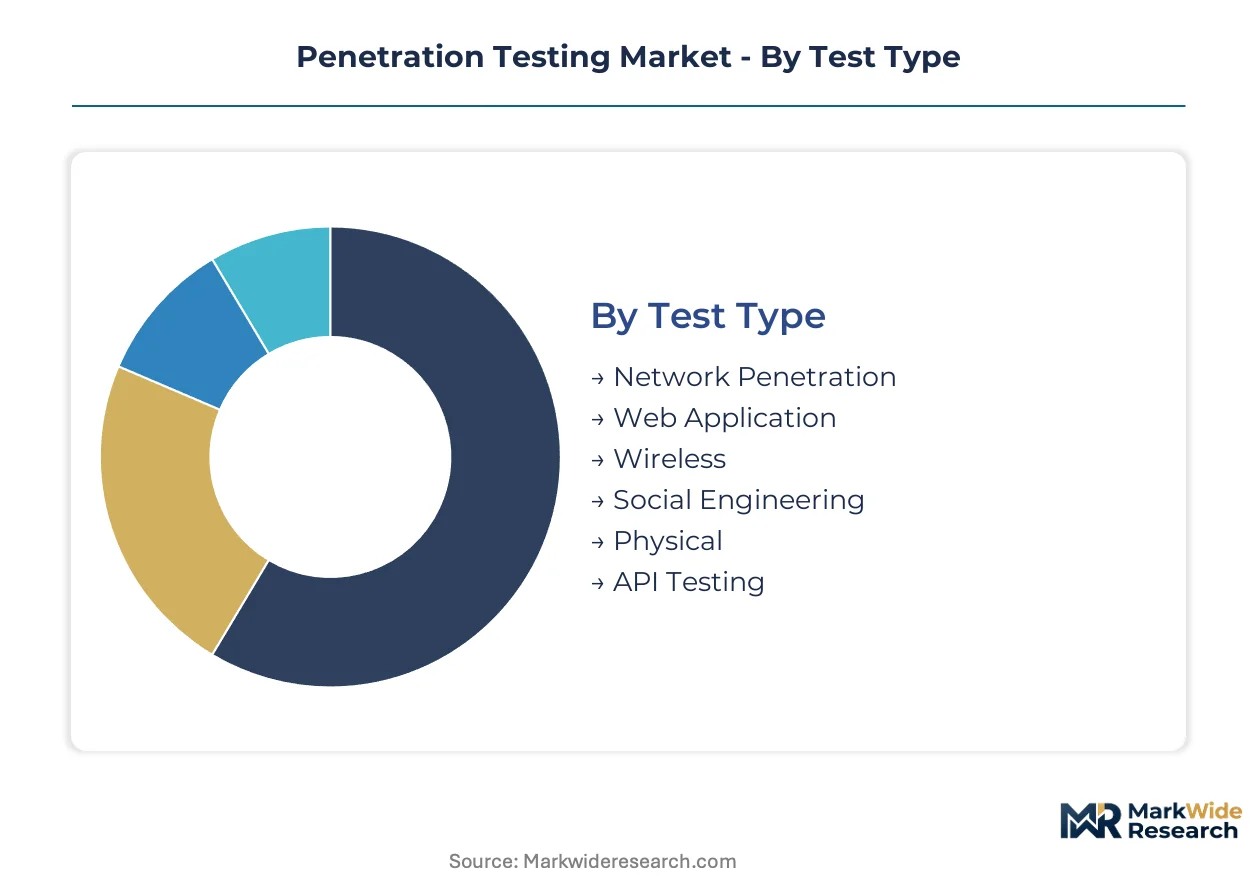
The Penetration Testing Market segments reveal distinct operational models and client priorities across the security landscape. Understanding these divisions helps service providers tailor offerings to specific technical requirements and regulatory environments. This detailed classification highlights where specialized expertise and advanced methodologies are most valued by enterprises.
Test Type:
Margin pools within test types concentrate in areas demanding deep technical specialization and continuous adaptation to evolving attack vectors. Web application and API testing services command higher value due to their direct impact on digital revenue streams and complex integration environments.
- Web Application:This testing identifies vulnerabilities in web-based applications, including code flaws and misconfigurations. Demand concentrates in financial services and e-commerce for data protection.
- API Testing:API testing assesses the security of application programming interfaces, checking data exposure and authentication bypasses. Microservices expansion in telecommunications drives demand.
- Network Penetration:Evaluates network infrastructure security, identifying exploitable weaknesses.
- Wireless:Assesses Wi-Fi and other wireless protocols, preventing unauthorized access.
- Social Engineering:Evaluates human vulnerabilities through simulated phishing attacks.
- Physical:Assesses physical premises security, identifying access control gaps.
Network Penetration testing holds installed capacity. API Testing is rotating up the share rankings.
Deployment Model:
The cost tier for deployment models varies significantly, with managed services and cloud-based solutions typically offering more predictable operational expenses compared to traditional on-premise deployments. Organizations often weigh initial capital outlay against long-term flexibility and expert resource access.
- Managed Service:Outsourcing penetration testing to a third-party offers continuous security validation and expert oversight. Mid-market US and European companies adopt this.
- Cloud-Based:Leverages remote infrastructure for testing, providing scalability and accessibility. Financial services and tech firms use this for agility.
- On-Premise:Conducts tests using internal infrastructure, providing maximum data control.
- Hybrid:Combines on-premise and cloud testing for specific asset types.
- SaaS:Delivers testing tools via subscription, enabling continuous automated assessments.
Customer preferences lean towards Managed Service solutions for comprehensive security oversight. Cloud-Based models are also gaining significant traction among enterprises.
End User:
The application of penetration testing varies widely across end-user sectors, with each industry presenting unique attack surfaces and compliance requirements. Financial services necessitate rigorous testing for data integrity, while telecommunications focus on network resilience and subscriber privacy.
- Financial Services:Requires extensive testing to protect customer data, prevent fraud, and comply with GDPR and PCI DSS. Banks in the United States are primary consumers.
- Telecommunications:Utilizes testing to secure network infrastructures, protect subscriber information, and ensure service resilience. Global carriers face threats.
- Government Agencies:Safeguards national security data and critical infrastructure from sophisticated attacks.
- Education Sector:Protects student records, research data, and campus networks.
- Hospitality:Secures customer booking systems and payment gateways against data theft.
- Energy Sector:Protects critical operational technology (OT) and industrial control systems (ICS).
The demand profile for Financial Services remains consistently high due to regulatory pressures. The Telecommunications sector also exhibits strong and sustained security investment.
Service Offering:
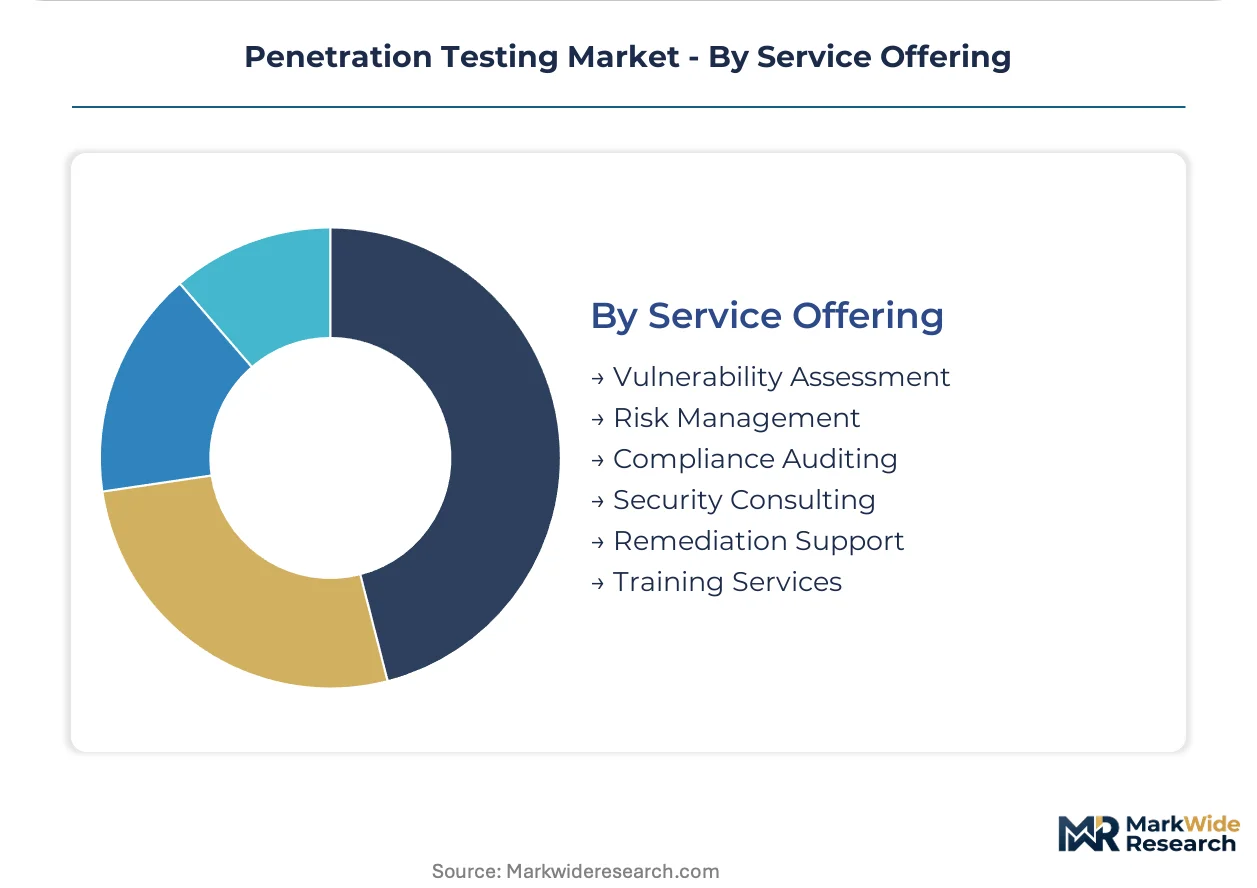
The volume of service offerings varies, with foundational vulnerability assessments and compliance auditing representing the highest frequency engagements. More specialized services like remediation support and security consulting are often bundled or provided on an as-needed basis.
- Vulnerability Assessment:Identifies security weaknesses in systems and networks, providing a security posture baseline. Enterprises utilize this as a fundamental component in the US.
- Compliance Auditing:Verifies adherence to standards like GDPR, HIPAA, or PCI DSS. Financial services and healthcare providers engage these to maintain standing.
- Risk Management:Identifies, assesses, and mitigates potential cyber risks.
- Security Consulting:Provides expert advice on security strategy and incident response.
- Remediation Support:Assists organizations in fixing identified vulnerabilities and implementing controls.
- Training Services:Educates internal staff on cybersecurity best practices.
Vulnerability Assessment remains a high-volume foundational service. Remediation Support is expanding most quickly as organizations seek integrated solutions.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand elasticity for penetration testing services varies significantly across geographies. Buyers in established markets prioritize advanced, continuous security validation, while those in developing regions often focus on foundational compliance and cost-efficient solutions.
United States
The United States drives substantial demand for penetration testing due to its large financial services sector and extensive tech industry. HIPAA and PCI DSS regulations compel regular security assessments across healthcare and retail. Major tech hubs like Silicon Valley and New York City exhibit high adoption of PTaaS platforms for integrated security.
Germany
German enterprises seek penetration testing to comply with GDPR and local data protection laws, particularly within its robust automotive and manufacturing sectors. The country's strong industrial base requires meticulous testing of operational technology and critical infrastructure. Munich and Berlin are centers for cybersecurity innovation and service provision.
United Kingdom
The United Kingdom's financial services hub in London generates consistent demand for advanced offensive security services and compliance auditing. GDPR and the UK's own data protection act mandate rigorous testing across all sectors. Fintech companies in London and Manchester actively integrate continuous testing into their development pipelines.
Japan
Japanese firms prioritize penetration testing for protecting sensitive consumer data and intellectual property, driven by evolving national cybersecurity strategies. The financial sector and automotive industry are key consumers of web application and API testing services. Tokyo's dense corporate environment focuses on securing complex digital ecosystems.
India
India's rapid digitalization and burgeoning IT services sector fuel demand for cost-effective penetration testing solutions. The country's data protection laws, similar to GDPR, are beginning to compel more structured security assessments. Technology parks in Bengaluru and Hyderabad are experiencing a rise in managed security service adoption.
Penetration Testing Market Key Industry Players
Technology leadership and cost leadership are held by different player archetypes within the penetration testing market. The landscape features a mix of specialized offensive security firms, broad-spectrum cybersecurity consultancies, and platform-centric providers. Strategic archetypes include high-end red teaming specialists, compliance-focused auditors, and scalable PTaaS providers. Key competitive moves involve portfolio diversification into adjacent security services and geographic expansion into emerging markets.
Specialists in scalable PTaaS platforms include NetSPI, which focuses on delivering continuous security validation for large enterprises. Bishop Fox exemplifies high-stakes red teaming and offensive security research, differentiating through its deep technical expertise. Coalfire occupies a position as a provider of extensive compliance auditing and advisory services, particularly for regulated industries.
| Leading Market Players |
|---|
| NetSPI |
| IOActive |
| DeepStrike |
| Trustwave |
| ScienceSoft |
| Bishop Fox |
| SpecterOps |
| GuidePoint Security |
| Coalfire |
| Others |
Cost & Logistics Intelligence
GDPR enforcement gates both service provider qualification and pricing tiers within the penetration testing market. Strict data handling and assessment requirements dictate which firms can operate and how their specialized services are valued.
Pricing Analysis
Managed services and continuous PTaaS subscriptions drive significant lifetime value for penetration testing providers. Hybrid subscription models, blending automated tools with expert human oversight, dominate service pricing. Price differentiation stems from the depth of technical specialization and continuous integration with client development pipelines. Pricing softness in basic vulnerability assessments reflects competition from automated tools. Smaller businesses exhibit high price sensitivity, while financial services firms prioritize comprehensive security over cost.
Supply Chain Analysis
The United States anchors the development of advanced penetration testing platforms and offensive security research. Service delivery draws from a global pool of highly skilled cybersecurity professionals and proprietary testing frameworks. Raw material dependencies include specialized software tools and curated threat intelligence feeds. Talent scarcity represents a significant structural risk for service providers. Distribution runs through direct enterprise sales and managed service provider channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The penetration testing market is experiencing a buyer-power shift as mid-market US and European companies consolidate their security needs with single partners. This trend favors providers offering bundled services and continuous engagement models.
For Market Incumbents: Fortify continuous PTaaS platform capabilities to counter competition from bug bounty programs and automated tool limitations. Incumbents should deepen integration with client DevSecOps pipelines and expand into AI/ML system security testing. Geographic expansion into emerging markets, particularly Southeast Asia, offers a growth lever. Investing in specialized talent acquisition and retention programs is crucial against talent scarcity.
For New Entrants and Emerging Players: PCI DSS v4.0 compliance expertise creates a fast-track for new entrants specializing in customized, risk-based testing. Target the burgeoning IoT device security market and AI/ML system security as white-space opportunities. Southeast Asia, with its maturing data privacy regulations, represents a penetrable geography for cost-effective managed services. A go-to-market angle focusing on niche regulatory compliance for mid-market firms can yield strong client acquisition.
For Investors and Strategic Acquirers: PCI DSS v4.0's shift to risk-based testing reshapes the acquisition landscape, favoring firms with robust continuous testing platforms. Long-term viability for the market remains strong over the next five to ten years due to persistent threat evolution. Acquisition targets should be PTaaS platform providers or specialized offensive security research firms with deep technical expertise. The signal to watch is the increasing integration of security testing into DevSecOps pipelines across more industries.
| Strategic Initiative | Industry Significance |
|---|---|
| PTaaS Platform Integration | Embeds security validation into client development workflows, capturing continuous value. |
| AI/ML System Security Research | Addresses unique vulnerabilities in AI models, creating a new high-value service category. |
| Geographic Expansion (Southeast Asia) | Captures demand from rapid digitalization and maturing data privacy regulations in new markets. |
| Managed Service Bundling | Attracts mid-market companies seeking comprehensive security oversight from a single partner. |
| Offensive Security Talent Development | Mitigates the persistent global scarcity of skilled penetration testing engineers. |
Research Approach
A standing panel of CISOs, offensive security engineers, and IT procurement managers provided ongoing calibration and primary insights. This involved combining direct interviews with extensive secondary validation from cybersecurity journals, regulatory body publications, and industry IT spending reports. Bottom-up analysis and top-down market sizing were triangulated to ensure robust data integrity.
Forecast outputs were validated for consistency against external benchmarks and prior market performance across the analysis window. Segmentation dimensions modeled included test type, deployment model, end-user industry, and regional adoption patterns. Compound annual growth rates were derived from historical growth trends and projected market dynamics. Key forecast inputs included global cybersecurity spending trends and regulatory enforcement intensity.
Underlying assumptions cover a stable regulatory environment and consistent technological advancement, with deviation risk concentrated in major geopolitical shifts or rapid AI evolution impacting attack surfaces. Forecasts reflect these conditions. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
DNS Security Market
Cybersecurity
Enterprise Firewall Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Global Database Security Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Deception Technology Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Banking Cyber Security Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Europe Mobile Security Market