
 Digital Risk Protection Software Market | 2026-2036
Digital Risk Protection Software Market Size, Share, and Industry Trends Forecast 2026-2036
Digital Risk Protection Software Market Outlook
Platform licensing revenue is reshaping competitive economics in digital risk protection, pulling margin pools from perpetual on-premises deployments toward recurring cloud-native subscriptions. CrowdStrike leverages its endpoint-native architecture to extend threat intelligence into adjacent risk surface domains. Recorded Future sustains differentiation through proprietary data collection across dark web and open-source channels. ZeroFox specializes in social media and brand protection, occupying a defensible niche against broader platform competitors.
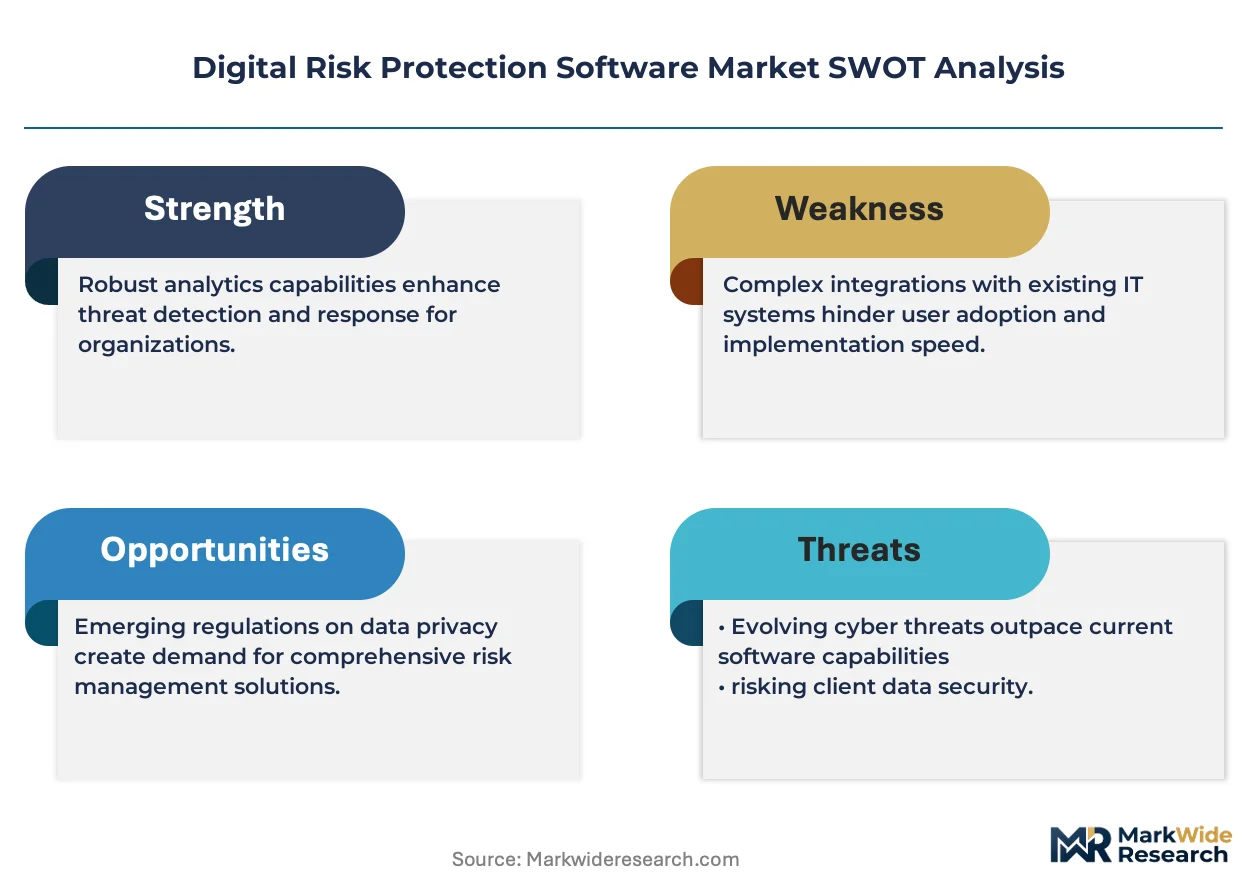
Digital risk protection software comprises integrated platforms that continuously monitor external digital assets, brand presence, and data exposure across surface web, social media, dark web, and third-party vendor ecosystems, typically employing automated collection engines with natural language processing and machine learning classification to detect impersonation, data leakage, and infrastructure vulnerabilities before exploitation. Its primary commercial purpose is to reduce mean time to detection for external threats that bypass perimeter defenses and to satisfy governance requirements for third-party risk visibility. Cloud-based deployment models attract the fastest-growing share of new bookings as security teams prioritize elastic scalability and reduced infrastructure overhead. Threat intelligence and incident response modules capture the deepest margin pools due to their integration complexity and reliance on proprietary data sources. Behavioral analytics technology is displacing rule-based detection in vulnerability management workflows across financial services and retail end users.
The EU AI Act, GDPR, and the SEC's cybersecurity disclosure rules collectively elevate accountability for external risk visibility, compelling enterprises to document continuous monitoring of digital assets and third-party exposures. ISO 27001 and NIST CSF implementations increasingly incorporate digital risk protection metrics into audit scopes, tightening procurement specifications for vendor selection. Stakeholders must weigh the trade-off between consolidated platform breadth and specialized depth as buyer procurement committees expand beyond CISOs to include legal, communications, and board-level risk committees.
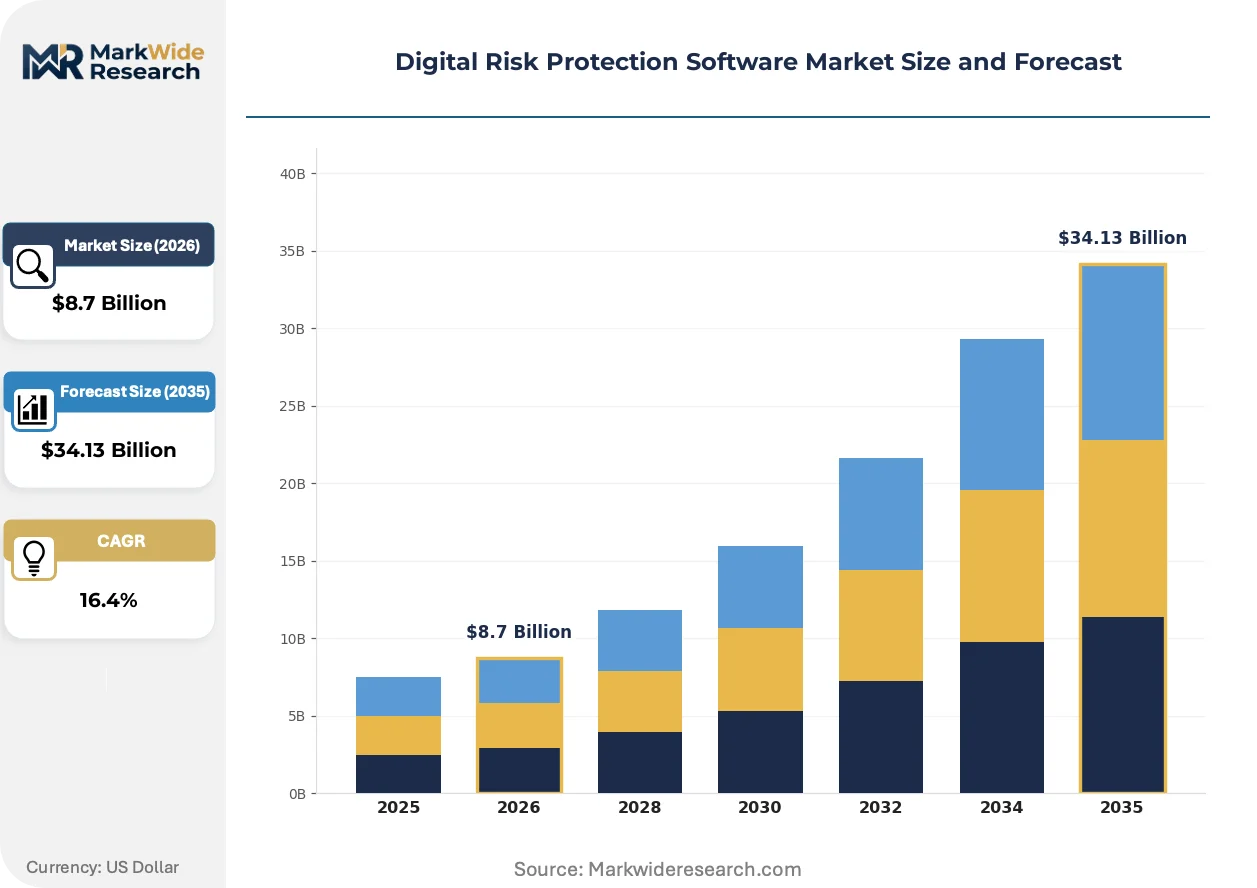
Market Dynamics
Cloud-native platform licensing is collapsing the economics of perpetual on-premises deployments, pulling margin pools toward recurring subscriptions as financial services institutions demand elastic scalability for external attack surface monitoring.
Growth Catalysts
- EU AI Act compliance mandates:Enterprises across Germany and France must document continuous monitoring of digital assets, accelerating procurement cycles for automated collection engines with machine learning classification.
- Financial services:Banks and insurance carriers in the United States face SEC cybersecurity disclosure rules that require third-party risk visibility, driving concentrated demand for threat intelligence modules.
- Behavioral analytics:Natural language processing engines are displacing rule-based detection in vulnerability management workflows across retail and healthcare end users.
Market Restraints
- Proprietary data source concentration:Dark web and open-source intelligence collection depends on a limited set of specialized collection infrastructure providers, creating supply bottleneck risk.
- GDPR friction:Cross-border data transfer restrictions complicate the aggregation of threat intelligence across European Union member states, limiting platform scalability.
- Integration cost volatility:Legacy security information and event management systems require substantial professional services expenditure to connect with cloud-native digital risk protection platforms.
Strategic Opportunities
- Japan manufacturing:Industrial control system operators in automotive and electronics sectors remain underpenetrated for external asset monitoring, representing expansion white space.
- ISO 27001 audit convergence:Certification bodies are incorporating digital risk protection metrics into standard audit scopes, creating regulatory tailwind for vendor selection committees.
- API-first architecture:The convergence of threat intelligence feeds with security orchestration platforms enables embedded distribution through existing cybersecurity marketplaces.
Industry Challenges
- Machine learning operations talent:Shortage of engineers capable of tuning natural language processing models for dark web dialects and emerging threat actor lexicons constrains product development velocity.
- Multi-cloud integration complexity:Enterprise buyers operating hybrid Amazon Web Services, Microsoft Azure, and Google Cloud environments face fragmented asset discovery, requiring customized deployment architectures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Digital Risk Protection Software Market |
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $34.13 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Threat Intelligence, Incident Response, Vulnerability Management, Compliance Monitoring Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Financial Services, Healthcare, Government, Retail Technology: Artificial Intelligence, Machine Learning, Blockchain, Behavioral Analytics |
| Companies Covered | ZeroFox, UpGuard, Proofpoint, CrowdStrike, Digital Shadows, ReliaQuest, Recorded Future, Rapid7, BlueVoyant, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Digital Risk Protection Software Market Strategic Shifts
Artificial intelligence is compressing detection latency while regulatory pressure is expanding the buyer committee beyond CISOs to legal and board-level risk functions.
Automated natural language processing engines are collapsing the distinction between surface web, social media, and dark web monitoring by unifying collection architectures under single data pipelines. Financial services institutions in the United States and Germany are adopting these engines at the fastest pace. This convergence is collapsing vendor count in procurement evaluations as buyers eliminate point solutions in favor of integrated platforms.
The EU AI Act's risk classification framework is mandating algorithmic transparency for automated threat detection systems deployed in European critical infrastructure. Industrial consequence includes mandatory documentation of machine learning model training data and decision boundaries. Healthcare and energy operators in France and Germany are responding by demanding vendor-provided compliance attestations before contract execution.
Enterprise buying committees now require legal and communications stakeholders to sign vendor selection decisions, extending sales cycles but increasing contract values. Security teams in financial services and retail verticals are replacing single-point procurement with cross-functional evaluation frameworks. This pattern is most visible in the United States, where SEC disclosure rules have elevated external risk visibility to board-level accountability.
Digital Risk Protection Software Market Segmentation
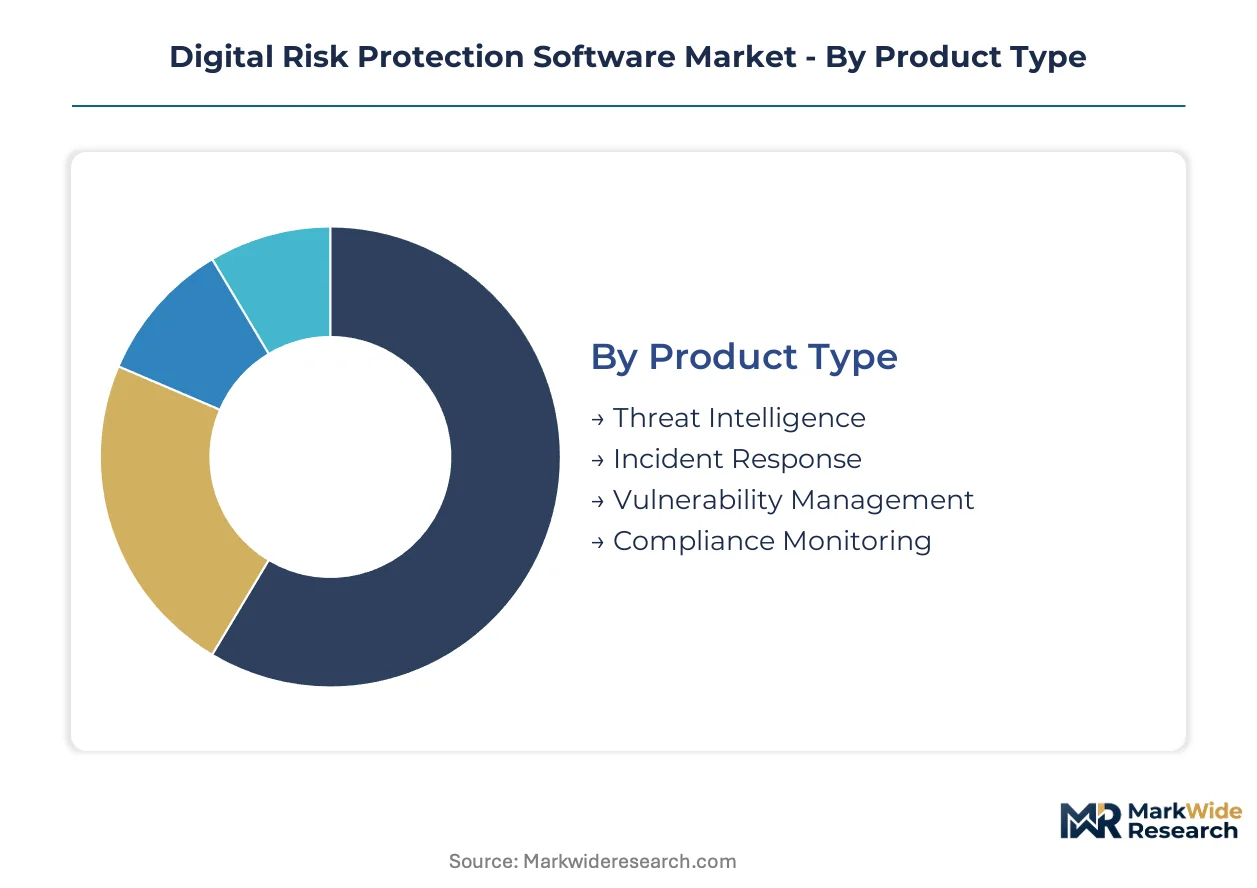
Digital risk protection software segments reveal divergent maturity curves across deployment architectures and intelligence modalities. Procurement committees weight integration complexity against compliance velocity when selecting product configurations.
Product Type:
Mature threat intelligence modules coexist with emerging compliance automation suites as financial services buyers prioritize audit-ready documentation.
- Threat Intelligence:Proprietary data pipelines aggregate dark web, open-source, and technical indicators into structured feeds. United States banks under SEC cybersecurity disclosure rules drive concentrated procurement for external risk visibility.
- Incident Response:Automated orchestration engines reduce mean time to containment for external asset compromises. Healthcare operators in Germany demand these modules to satisfy EU AI Act documentation requirements for algorithmic decision-making.
- Vulnerability Management:Continuous attack surface discovery with risk-based prioritization scoring.
- Compliance Monitoring:Automated evidence collection for ISO 27001 and GDPR audit trails.
Threat Intelligence retains volume leadership; Compliance Monitoring holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates enterprise-grade elasticity from constrained on-premises capital commitments.
- Cloud-Based:Elastic scalability with consumption-based pricing eliminates infrastructure overhead. Financial services institutions across Japan and Germany favor this model for rapid external asset onboarding.
- Hybrid:Split architectures preserve sensitive data on-premises while leveraging cloud analytics for non-critical workloads. German manufacturers select hybrid deployments to navigate GDPR cross-border transfer restrictions.
- On-Premises:Perpetual licensing with dedicated hardware for air-gapped environments.
- Managed Service:Outsourced monitoring with vendor-operated collection infrastructure and analyst augmentation.
Cloud-Based deployments dominate new bookings; Managed Services are climbing fastest among mid-market buyers.
End User:
Application intensity varies by sector-specific regulatory exposure and digital asset surface area.
- Financial Services:Banks, insurers, and payment processors face the most stringent third-party risk mandates. United States institutions respond to SEC disclosure rules with comprehensive external monitoring budgets.
- Government:National security and civilian agencies require supply chain visibility for critical infrastructure protection.
- Healthcare:HIPAA-covered entities and EU health operators balance patient data protection with emerging AI system accountability.
- Retail:Brand protection and customer data leak prevention across e-commerce and social channels.
Financial Services commands the deepest spending per account; Healthcare is expanding most quickly under regulatory pressure.
Technology:
Margin concentration aligns with proprietary algorithm development and specialized data science talent scarcity.
- Artificial Intelligence:Natural language processing engines unify surface web, social media, and dark web collection architectures. French and German critical infrastructure operators demand algorithmic transparency documentation under EU AI Act risk classifications.
- Behavioral Analytics:Pattern recognition for anomalous external asset activity and impersonation detection. United States retail chains deploy these engines to identify brand impersonation campaigns before customer impact.
- Machine Learning:Supervised and unsupervised model training for threat actor lexicon evolution.
- Blockchain:Distributed ledger applications for credential verification and supply chain attestation.
Artificial Intelligence captures the widest deployment footprint; Behavioral Analytics shows the steepest adoption acceleration among rule-base displacement scenarios.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Vendor engineering talent clusters in the United States, Germany, and Japan, creating regional specialization in threat intelligence collection architectures. Cloud infrastructure density in these markets accelerates deployment velocity for external attack surface monitoring platforms. Regulatory divergence between EU algorithmic transparency mandates and US disclosure rules fragments product roadmaps.
United States
SEC cybersecurity disclosure rules compel banks and insurers in New York and California to document continuous third-party risk visibility. Financial institutions allocate substantial procurement budgets toward automated threat detection modules. The Boston-Washington corridor hosts the densest concentration of cloud-native platform engineering teams.
Germany
EU AI Act risk classifications force critical infrastructure operators in Munich and Frankfurt to demand algorithmic transparency documentation before contract execution. Industrial manufacturers select hybrid deployment models to navigate GDPR cross-border transfer restrictions. The Ruhr Valley automotive sector drives specialized demand for external asset monitoring in operational technology environments.
Japan
Industrial control system operators in automotive and electronics sectors across the Chubu and Kansai regions remain underpenetrated for external attack surface monitoring. METI guidance on supply chain cybersecurity elevates procurement urgency among Tier-1 manufacturers. Tokyo-based financial institutions integrate digital risk protection into ISO 27001 audit preparation workflows.
France
CNIL enforcement of GDPR data localization requirements shapes vendor selection criteria for Paris-headquartered healthcare and energy operators. The EU AI Act mandates documentation of machine learning training data for automated threat detection systems deployed in critical infrastructure. Lyon and Grenoble technology clusters attract specialized natural language processing engineering talent.
United Kingdom
Financial services regulators in London require documented external risk visibility for systemic institutions under operational resilience frameworks. The convergence of threat intelligence procurement with ESG disclosure preparation expands buyer committees beyond CISOs to legal and board risk functions. Manchester and Edinburgh emerging technology clusters develop specialized capabilities in dark web dialect analysis.
Digital Risk Protection Software Market Competitive Environment
Endpoint-native platforms and specialized threat intelligence providers split the market into distinct competitive domains. Consolidation pressure intensifies as procurement committees favor integrated suites over point solutions. Two strategic archetypes dominate: cloud-native platforms extending from adjacent security domains, and pure-play specialists with proprietary data collection infrastructure. Dominant competitive moves include API-first architecture investments and strategic partnerships with security orchestration platforms.
Within the specialist tier, ZeroFox occupies a defensible position in social media and brand protection, while Recorded Future exemplifies threat intelligence depth through proprietary dark web and open-source data pipelines. CrowdStrike anchors the platform-extension archetype, leveraging endpoint-native architecture to expand into adjacent risk surface domains. These three companies represent the strategic positioning spectrum that procurement committees evaluate against integration complexity and compliance velocity requirements.
| Leading Market Players |
|---|
| ZeroFox |
| UpGuard |
| Proofpoint |
| CrowdStrike |
| Digital Shadows |
| ReliaQuest |
| Recorded Future |
| Rapid7 |
| BlueVoyant |
| Others |
Value Chain & Pricing Dynamics
Overcapacity in cloud infrastructure provisioning across the United States and Germany compresses hosting costs for digital risk protection platforms, driving subscription pricing downward while enabling vendors to absorb integration complexity without margin erosion.
Pricing Analysis
Extended threat intelligence contracts and managed detection response services drive lifetime value beyond initial platform licensing. Three-tier pricing structure across premium, standard, and economy levels segments buyers by data source depth and analyst support levels. Cost compression in mid-market tiers intensifies as CrowdStrike and Recorded Future bundle adjacent modules into consolidated suites. Financial services institutions show lowest price sensitivity due to SEC disclosure compliance mandates, while mid-market retail chains prioritize economy tiers with reduced dark web coverage.
Supply Chain Analysis
Supply-chain finance facilities from cloud hyperscalers enable extended payment terms for collection infrastructure vendors. Proprietary data pipeline development concentrates engineering talent in the United States, Germany, and Japan. Raw material inputs rest on specialized dark web crawling infrastructure, open-source intelligence aggregation nodes, and natural language processing compute clusters. Single-source vulnerability in dark web access partnerships creates concentration risk for specialist vendors. Distribution runs through direct enterprise sales teams and security orchestration platform marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is concentrating as financial services procurement committees consolidate vendor relationships from point solutions to integrated platforms, compressing supplier count per account.
For Market Incumbents: Entrench platform-native architecture advantages by deepening API integration with security orchestration workflows and acquiring specialist dark web collection infrastructure to eliminate supply bottlenecks. CrowdStrike's endpoint extension model demonstrates how adjacent domain control defends against pure-play threat intelligence erosion. Prioritize ISO 27001 certification investment to capture audit-convergence procurement specifications. For New Entrants and Emerging Players: Pursue Japan's underpenetrated manufacturing sector where METI supply chain guidance elevates procurement urgency without entrenched incumbent relationships. Industrial control system operators in automotive and electronics verticals lack specialized external asset monitoring. API-first distribution through existing cybersecurity marketplaces reduces customer acquisition friction against direct sales-dominated competitors. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting downward across cloud-native deployment architectures as hyperscaler infrastructure commoditizes compute costs. Long-term viability favors vendors with proprietary data collection infrastructure rather than algorithm-only differentiation. Acquisition targets should demonstrate sustained dark web source relationships and natural language processing engineering clusters. The signal to monitor is EU AI Act enforcement velocity against critical infrastructure operators, which would accelerate compliance-automation procurement cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | API-first architecture embeds threat intelligence into CrowdStrike and Palo Alto Networks security orchestration workflows. |
| Acquisition of Specialist Firm | Dark web collection infrastructure purchases eliminate supply bottlenecks and deepen proprietary data moats. |
| Geographic Expansion | Japan manufacturing sector penetration addresses METI supply chain cybersecurity guidance with localized collection nodes. |
| Product Launch | EU AI Act compliance automation modules capture audit-documentation procurement from French and German critical infrastructure. |
| Strategic Partnership | Hyperscaler cloud infrastructure agreements reduce hosting cost volatility and enable consumption-based pricing flexibility. |
Study Parameters
Desk research of SEC cybersecurity disclosure filings, EU regulatory guidance documents, and cloud infrastructure capex disclosures preceded structured interviews with CISOs, third-party risk officers, threat intelligence directors, and security procurement leads. Primary fieldwork combined with secondary validation across hyperscaler partnership announcements and ISO certification databases. Bottom-up deployment model sizing triangulated against top-down financial services IT security spending estimates.
Assumptions held fixed include EU AI Act enforcement timelines and SEC disclosure rule applicability scope, while cloud adoption velocity and behavioral analytics displacement rates varied across sensitivity scenarios. Segmentation modeling incorporated deployment architecture, end-user vertical, technology modality, and regional regulatory cluster dimensions. CAGRs derived from elasticity-adjusted adoption curves and compliance-mandate procurement acceleration patterns. Natural language processing talent scarcity and dark web infrastructure concentration served as industry-specific forecast inputs.
Macroeconomic conditions sit as an overlay; deviation in enterprise IT security budget growth or cloud infrastructure pricing would shift the trajectory. Forecasts reflect documented assumptions about regulatory enforcement velocity and technology substitution patterns. Macroeconomic, regulatory, or technological deviation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
US and Latin America Identity and Access Management (IAM) Market
Security Software
Employee Fraud Detection Market
Security Software
Doorbell Camera Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
US Hardware Encryption Market
Security Software
Mobile Data Protection Solutions and Services Market
Security Software
Extended Detection and Response Market
Security Software
Italy Endpoint Detection and Response Market
Security Software
Global Data Loss Prevention Software Market
Security Software
Cloud Identity and Access Management Software Market
Security Software
Cloud Data Loss Prevention Solution Market
Security Software
Global Hardware Security Modules (HSM) Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Bot Mitigation Market
Security Software
Remote Access Management Market
Security Software
Confidential Computing Market