
 AI Security Platforms Market | 2026-2036
AI Security Platforms Market Size, Share, and Industry Trends Forecast 2026-2036
AI Security Platforms Market Insights
The EU AI Act is shifting procurement criteria across enterprise security stacks. Palo Alto Networks leverages integrated AI-native security operations to sustain platform consolidation among multinational buyers. CrowdStrike anchors endpoint detection with behavioral models that compete on speed-to-triage. Microsoft dominates cloud security attach rates through embedded AI capabilities across Azure and Microsoft 365 environments.
AI security platforms combine machine learning inference, real-time telemetry pipelines, and automated response orchestration to detect, classify, and neutralize adversarial threats across digital infrastructure. These systems process petabyte-scale event streams with sub-millisecond latency requirements to protect distributed cloud and edge attack surfaces. Cloud-based deployment leads solution architecture as organizations abandon fixed-capacity data center investments. Threat detection and behavioral analytics command concentrated R&D allocation, while identity verification solutions capture expanding margin pools from privileged-access governance mandates. Banking and financial services anchor end-user demand, though government agencies represent the fastest-growing procurement segment driven by classified system protection requirements.
The U.S. NIST AI Risk Management Framework shapes product design standards for domestic vendors seeking federal authorization, while the EU AI Act imposes conformity assessment obligations on platforms deployed in European critical infrastructure. HIPAA security rule extensions pressure healthcare AI deployments toward enhanced audit and access controls. Stakeholders must monitor divergence between U.S. sectoral agency guidance and EU horizontal regulation as compliance costs fragment product roadmaps.
Market Dynamics
Zero-trust architecture mandates from federal agencies are compressing procurement cycles and forcing platform consolidation across enterprise security stacks. Vendors must now bundle AI-native detection, automated response, and cross-cloud telemetry into unified offerings or face disqualification from government and regulated-industry RFPs.
Growth Catalysts
- EU AI Act risk-classification protocols:Critical infrastructure operators across European energy and transport sectors must deploy audited AI security systems, creating mandatory replacement cycles for legacy tooling.
- Generative AI-enabled fraud:Banking institutions face synthetic identity attacks and deepfake authentication breaches that rule-based systems cannot detect, driving demand for behavioral biometrics and real-time inference engines.
- Edge computing expansion:Manufacturing and logistics networks processing sensitive operational data outside centralized clouds require distributed AI security nodes with local inference capabilities.
Market Restraints
- GPU compute cost volatility:Training and running large language model-based threat detection depends on NVIDIA H100 and equivalent accelerator availability, with spot pricing fluctuations exceeding 40% quarter-to-quarter.
- Talent concentration in Silicon Valley and Tel Aviv:Adversarial machine learning research and red-team AI expertise clusters in two metropolitan regions, constraining vendor R&D scaling.
- NIST framework fragmentation with EU AI Act:Divergent conformity assessment timelines and technical standards force dual product development tracks, elevating engineering overhead for multinational platforms.
Strategic Opportunities
- Operational technology security in Germany:Industrie 4.0 manufacturing sites lack AI-native monitoring for PLC and SCADA anomalies, presenting whitespace for specialized edge-deployed solutions.
- Convergence of confidential computing with AI inference:Hardware-based enclaves from Intel TDX and AMD SEV enable encrypted model execution, unlocking regulated healthcare and government deployments previously blocked by data sovereignty concerns.
- Managed detection and response channel expansion:Mid-market enterprises without security operations centers increasingly outsource AI-augmented monitoring to specialized service providers rather than building in-house teams.
Industry Challenges
- Adversarial robustness certification delays:No standardized testing regime exists for evasion attack resistance, forcing vendors to self-attest model resilience and slowing enterprise adoption.
- Legacy SIEM integration complexity:Decades of accumulated log formats and custom correlation rules in existing security information platforms resist seamless AI-native overlay deployment.
- Cross-border data flow restrictions:Training datasets spanning multiple jurisdictions face localization requirements that fragment model development and degrade detection accuracy for global threat patterns.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | AI Security Platforms Market |
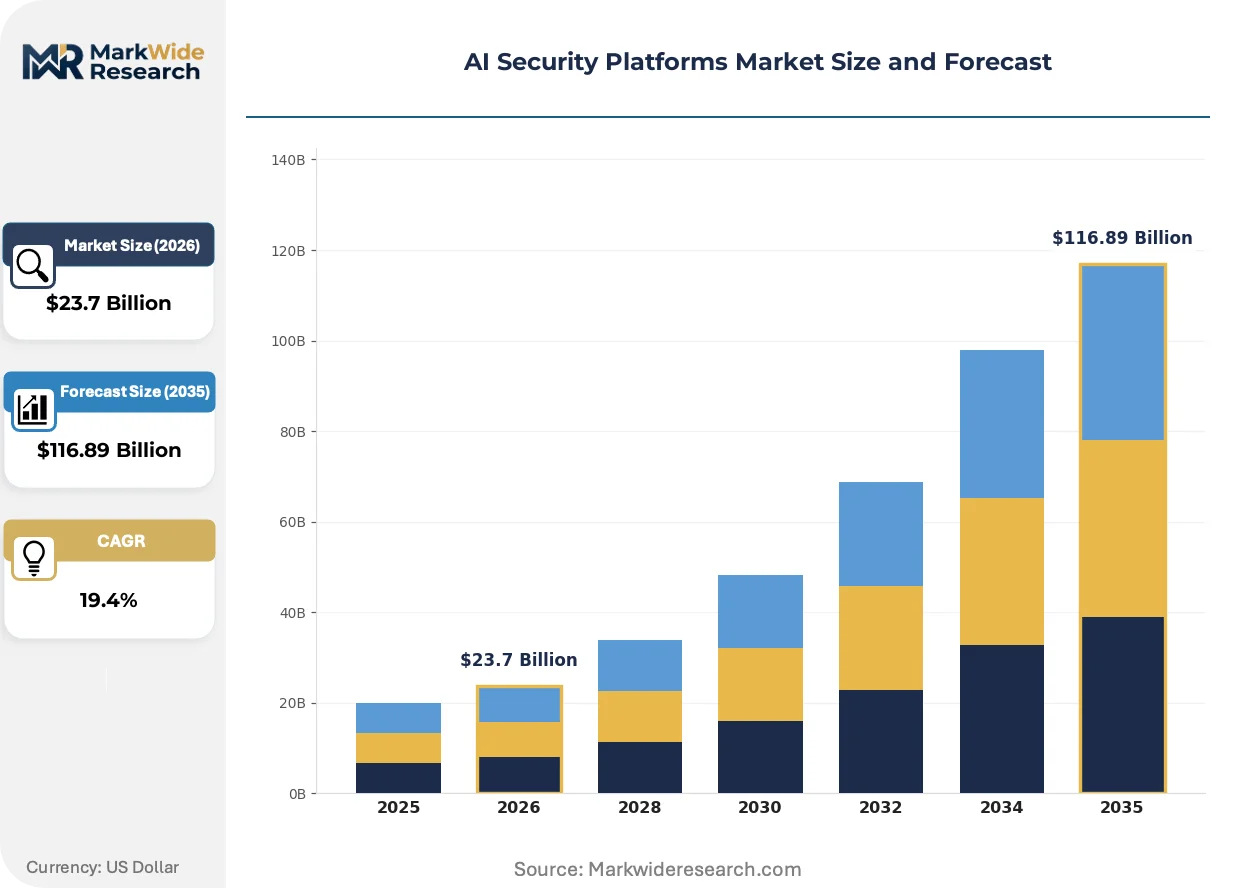
| Market Size in 2026 | $23.7 Billion |
| Market Size in 2035 | $116.89 Billion |
| CAGR (2026 – 2036) | 19.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Edge Computing Solution Type: Threat Detection, Behavioral Analytics, Identity Verification, Data Loss Prevention, Fraud Management Application: Network Security, Cloud Security, Endpoint Protection, Fraud Detection, Insider Threat Management End User: Banking & Financial Services, Government Agencies, Telecommunications, E-Commerce, Manufacturing |
| Companies Covered | Palo Alto Networks, CrowdStrike, Microsoft, Fortinet, Check Point Software Technologies, IBM, Cisco Systems, SentinelOne, Darktrace, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
AI Security Platforms Market Trends and Innovations
Security operations platforms are absorbing adjacent capabilities—threat intelligence, identity governance, cloud workload protection—into unified control planes. This consolidation compresses vendor counts per enterprise while elevating performance benchmarks for real-time detection and automated response.
Extended detection and response architectures are consolidating endpoint, network, and cloud telemetry into single-pane inference pipelines. Financial services institutions with mature security operations centers deploy these integrated stacks within 90-day implementation windows. The technology is consolidating previously separate budget lines for endpoint protection, network detection, and cloud security into single platform subscriptions.
The EU AI Act's conformity assessment obligations for high-risk automated decision systems are mandating third-party audit trails and explainability modules in security platforms. Industrial consequence includes documented model lineage and drift monitoring becoming standard procurement requirements. Critical infrastructure operators in France, Germany, and the Netherlands now demand CE-marked AI security components with notified body certification.
Buyer preference is rotating toward outcome-based engagement models where vendors guarantee mean-time-to-detect thresholds or assume breach response liability. The managed security services channel is displacing perpetual license purchases among mid-market healthcare and retail organizations. This shift is most visible in the United States, where cyber insurance carriers increasingly mandate AI-augmented monitoring as a condition of policy renewal.
AI Security Platforms Market Segmentation
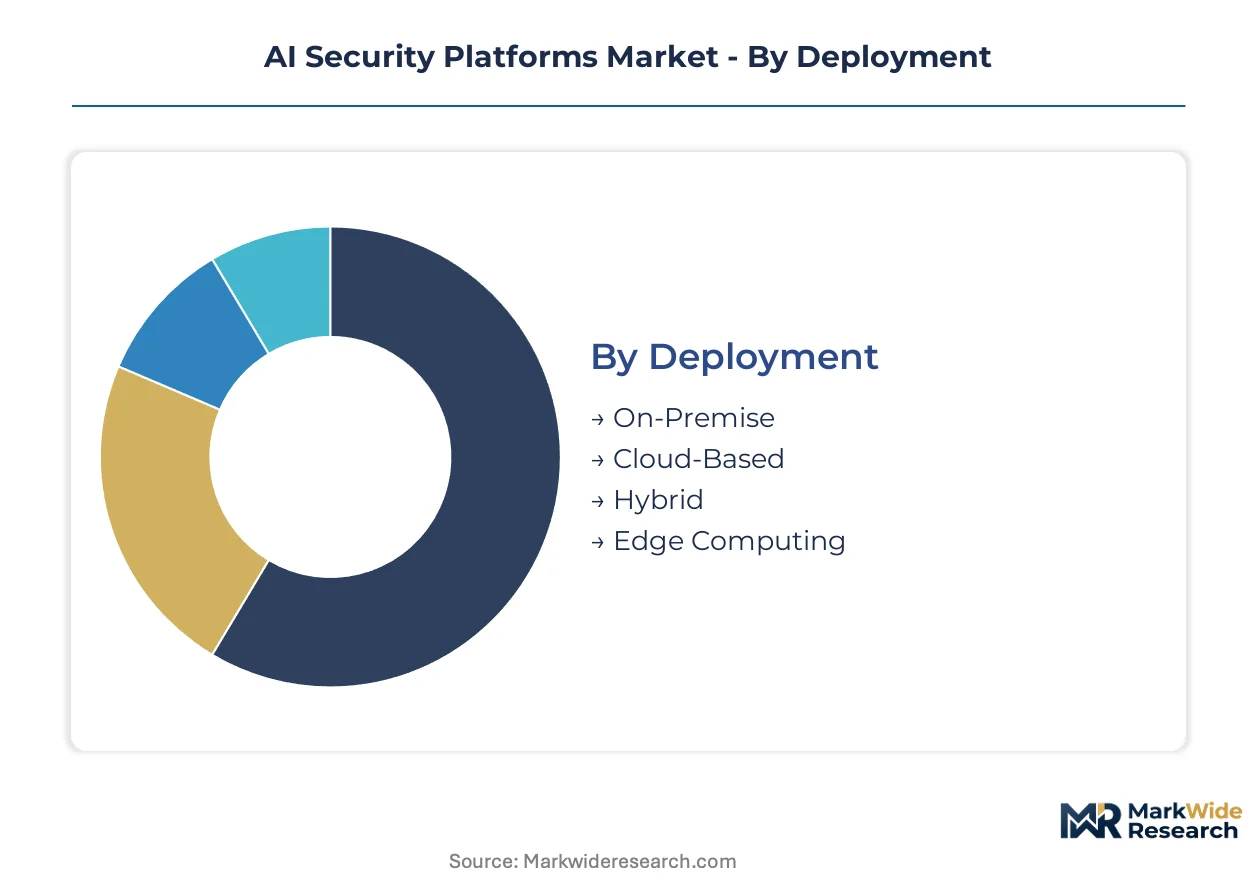
AI security platforms serve heterogeneous infrastructure environments and threat vectors. Deployment architecture, solution specialization, application domain, and end-user risk profiles create distinct commercial segments with diverging procurement criteria and margin structures.
Deployment:
Buyer infrastructure maturity and data sovereignty requirements determine deployment architecture selection.
- Cloud-Based:Organizations eliminate fixed-capacity data center investments while accessing elastic compute for petabyte-scale telemetry processing. Financial services institutions in the United States drive concentrated demand as federal zero-trust mandates compress procurement cycles.
- Edge Computing:Distributed inference nodes process sensitive operational data locally without cloud round-trips. Manufacturing and logistics networks across Germany's Industrie 4.0 corridor require these deployments for PLC and SCADA anomaly detection.
- On-Premise:Classified government systems and healthcare HIPAA environments mandate air-gapped infrastructure with hardware-based encryption.
- Hybrid:Enterprises with legacy SIEM investments bridge on-premise correlation engines with cloud-native AI detection layers.
Cloud-based deployments lead on scale; edge computing leads on momentum.
Solution Type:
Procurement budgets concentrate where adversarial pressure is most acute and regulatory penalties are steepest.
- Threat Detection:Real-time inference pipelines classify adversarial patterns across network, endpoint, and cloud telemetry streams. Sub-millisecond latency requirements define technical specifications for financial clearing systems.
- Behavioral Analytics:Machine learning models establish user and entity baselines to flag anomalous access patterns. EU AI Act conformity assessment obligations mandate explainability modules and documented model lineage for high-risk automated decision systems.
- Identity Verification:Biometric and behavioral authentication counters synthetic identity attacks and deepfake breaches. Privileged-access governance mandates expand margin pools in regulated industries.
- Fraud Management:Real-time transaction scoring detects generative AI-enabled payment fraud and account takeover attempts.
- Data Loss Prevention:Content-aware classification and encryption enforcement protect intellectual property across cloud collaboration platforms.
Threat detection commands the largest installed base; identity verification is climbing the fastest.
Application:
Attack surface expansion across distributed infrastructure drives application-specific platform requirements.
- Cloud Security:Native controls for containerized workloads, serverless functions, and multi-tenant data lakes. Azure and AWS environments dominate attach rates.
- Endpoint Protection:Behavioral models compete on speed-to-triage for laptop, mobile, and IoT device fleets. CrowdStrike and Palo Alto Networks anchor this segment with integrated detection and response.
- Network Security:East-west traffic inspection and zero-trust segmentation for hybrid cloud architectures.
- Fraud Detection:Real-time scoring for digital banking, payment processing, and e-commerce checkout flows.
- Insider Threat Management:User activity monitoring and data exfiltration prevention for high-value research and trading environments.
Cloud security leads on current spend; endpoint protection shows the steepest expansion trajectory.
End User:
Sector-specific regulatory frameworks and threat actor targeting intensity shape procurement patterns.
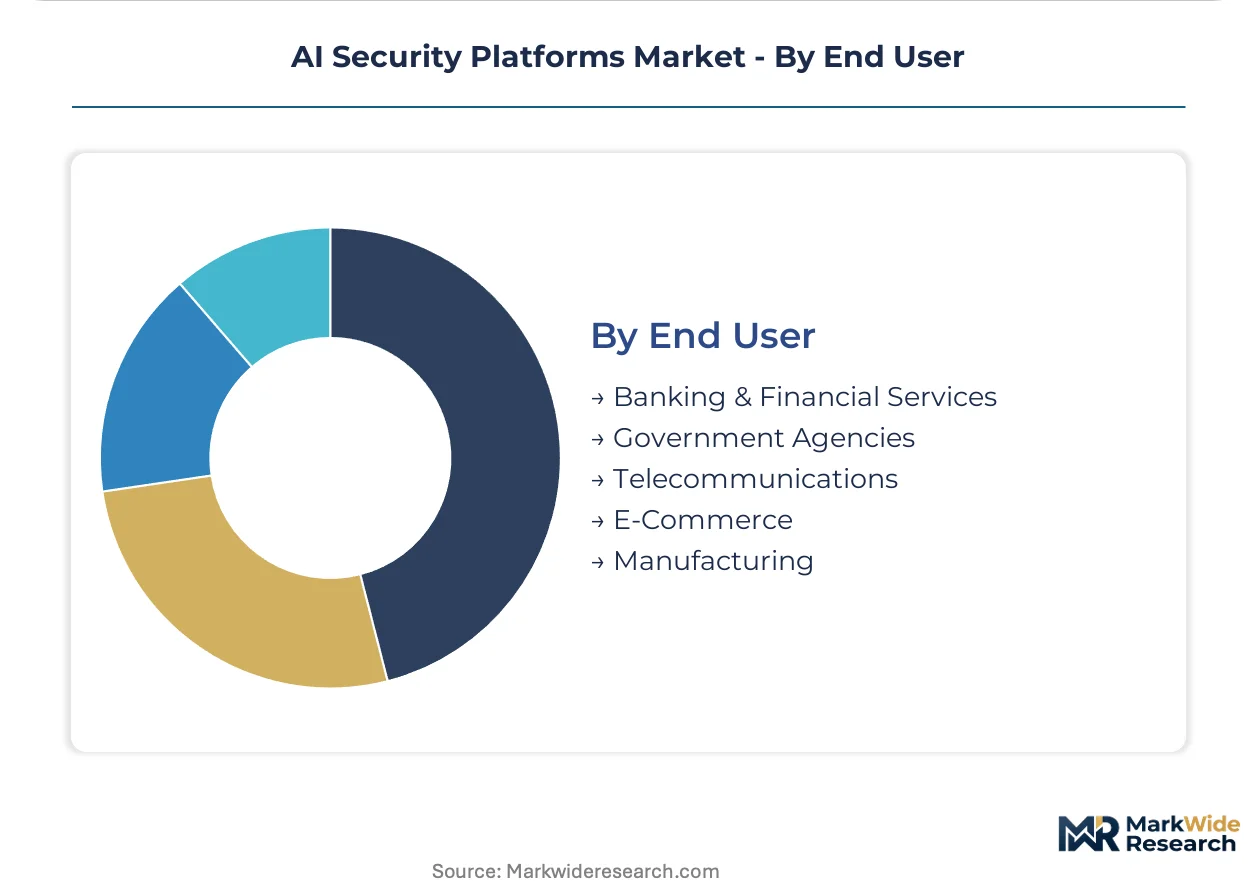
- Banking & Financial Services:Synthetic identity fraud and deepfake authentication attacks drive replacement of rule-based systems. Behavioral biometrics and real-time inference engines command premium pricing.
- Government Agencies:Classified system protection requirements and zero-trust architecture mandates accelerate procurement. The United States federal segment expands most quickly with NIST AI Risk Management Framework compliance obligations.
- Telecommunications:5G network slicing and edge infrastructure require distributed security monitoring.
- E-Commerce:Account takeover and payment fraud detection for high-velocity transaction environments.
- Manufacturing:Operational technology security for PLC and SCADA systems in Industrie 4.0 deployments.
Banking and financial services anchor current demand; government agencies are gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
AI security platforms emerged from cybersecurity research clusters in the United States and Israel during the 2010s, with commercial deployment scaling through Silicon Valley venture capital and Tel Aviv military technology transfer programs before expanding to European and Asian financial centers.
United States
Federal zero-trust architecture mandates from the Department of Defense and civilian agencies compress procurement cycles for integrated security stacks. NIST AI Risk Management Framework compliance obligations shape product design standards for vendors seeking federal authorization. The Washington DC-Baltimore corridor anchors government demand, while New York and San Francisco financial centers drive behavioral analytics adoption for fraud detection.
Germany
Industrie 4.0 manufacturing sites across Bavaria and Baden-Württemberg require AI-native monitoring for PLC and SCADA anomalies in operational technology environments. EU AI Act conformity assessment obligations mandate CE-marked components with notified body certification for critical infrastructure deployments. The Ruhr industrial region and Stuttgart manufacturing belt present whitespace for edge-deployed security solutions.
United Kingdom
Financial services institutions in the City of London deploy extended detection and response architectures within compressed implementation windows. The UK National Cyber Security Centre guidance on AI system assurance creates procurement criteria distinct from EU regulatory timelines. London's fintech cluster and Manchester's emerging technology hub drive demand for real-time inference engines.
Israel
Military technology transfer programs and Unit 8200 alumni networks concentrate adversarial machine learning expertise in Tel Aviv and Herzliya. The country's national cyber directorate shapes export-oriented platform development for global critical infrastructure markets. Tel Aviv's cybersecurity corridor hosts specialized vendors targeting behavioral biometrics and deepfake detection.
Japan
Manufacturing supply chain security requirements and Tokyo 2025 digital infrastructure investments accelerate AI-native monitoring adoption. METI guidelines on secure AI system deployment create compliance frameworks for industrial automation environments. The Tokyo-Osaka manufacturing corridor and emerging Fukuqua semiconductor cluster demand distributed edge security nodes.
AI Security Platforms Market Competitive Landscape
Premium-margin players sit above commodity-margin players across integration depth and response automation capabilities. The market exhibits tiered consolidation with three to five integrated platforms capturing government and large-enterprise procurement, while point-solution specialists occupy mid-market niches. Three strategic archetypes dominate: cloud-native platform consolidators, endpoint-centric behavioral specialists, and network-security incumbents with AI overlay strategies. Competitive moves center on cross-cloud telemetry bundling and managed detection and response channel expansion.
Within the integrated platform tier, Palo Alto Networks and CrowdStrike occupy positions exemplifying cloud-native consolidation archetypes, while Microsoft anchors the embedded-capability vector across Azure and Microsoft 365 environments. These three represent distinct strategic postures: Palo Alto Networks exemplifies best-of-breed platform bundling, CrowdStrike represents endpoint-centric behavioral modeling, and Microsoft demonstrates cloud-ecosystem attach-rate dominance.
| Leading Market Players |
|---|
| Palo Alto Networks |
| CrowdStrike |
| Microsoft |
| Fortinet |
| Check Point Software Technologies |
| IBM |
| Cisco Systems |
| SentinelOne |
| Darktrace |
| Others |
Pricing and Supply Chain Analysis
Federal zero-trust architecture mandates compressing procurement cycles force vendors to bundle AI-native detection, automated response, and cross-cloud telemetry into unified offerings or face disqualification from government RFPs, elevating platform pricing power while squeezing point-solution margins.
Pricing Analysis
Outcome-based subscription tiers with guaranteed mean-time-to-detect thresholds dominate enterprise procurement, separating premium platforms with breach response liability from standard SaaS tiers with telemetry-only access. Price differentiation hinges on NIST AI Risk Management Framework compliance certification and integration depth across legacy SIEM environments. Cost compression in mid-market segments intensifies as managed security services displace perpetual licenses. Healthcare organizations exhibit highest price sensitivity due to constrained IT budgets, while classified government systems show lowest sensitivity given mission-critical requirements.
Supply Chain Analysis
Refurbished GPU clusters and model weight optimization services create secondary supply flows as vendors seek to extend accelerator lifecycles amid H100 availability constraints. Hardware supply concentrates in Taiwan, South Korea, and the United States for advanced semiconductors, while adversarial machine learning research talent clusters in Silicon Valley and Tel Aviv. Raw material dependencies span NVIDIA H100 accelerators, high-bandwidth memory modules, and specialized optical networking gear. Single-source vulnerability around TSMC fabrication exposes vendors to geopolitical disruption. Distribution runs through hyperscaler marketplaces, direct enterprise sales teams, and managed detection and response service providers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
AI security platforms function as stable compounders where regulatory mandates for automated decision system auditing create durable replacement cycles and recurring revenue visibility.
For Market Incumbents: To counter generative AI-enabled fraud eroding rule-based detection margins, Palo Alto Networks and CrowdStrike must deepen backward integration into behavioral model training pipelines while accelerating CE-marking certification for EU AI Act conformity assessment. Channel control through managed detection and response partnerships defends against mid-market displacement. For New Entrants and Emerging Players: Launch via specialized edge-deployed solutions targeting Germany's Industrie 4.0 manufacturing corridor where PLC and SCADA anomaly detection lacks AI-native monitoring. White-space concentrates in operational technology security for critical infrastructure, with go-to-market traction through industrial automation system integrators rather than direct enterprise sales. For Investors and Strategic Acquirers: Asymmetric upside sits with adversarial machine learning specialists possessing red-team AI expertise and notified body certification relationships for EU critical infrastructure deployments. Long-term viability favors platforms with demonstrated federal authorization pathways and hardware-based confidential computing partnerships. Monitor NIST framework divergence from EU AI Act technical standards as inflection indicator for engineering overhead fragmentation.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and cloud telemetry into single-pane inference pipelines for financial services. |
| Acquisition of Specialist Firm | Captures adversarial machine learning talent concentrated in Tel Aviv and Silicon Valley research clusters. |
| Geographic Expansion | Establishes notified body certification relationships for EU AI Act CE-marking in German industrial corridors. |
| Product Launch | Deploys edge inference nodes for PLC and SCADA anomaly detection in Industrie 4.0 manufacturing sites. |
| Strategic Partnership | Integrates Intel TDX and AMD SEV confidential computing for encrypted model execution in healthcare. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs, federal procurement officers, managed security service provider executives, and adversarial machine learning researchers with secondary validation against NIST AI Risk Management Framework documentation, EU AI Act conformity assessment guidelines, hyperscaler security capex disclosures, and cyber insurance carrier policy requirements. Bottom-up telemetry processing benchmarks and top-down federal spending authorization data were triangulated.
Historical reference periods spanning pre-mandate and post-mandate procurement environments anchored the forecast window, with CAGRs derived from segment-level adoption curves across cloud-based, edge computing, on-premise, and hybrid deployment architectures. Modeled dimensions included solution type specialization, application domain attack surface, end-user regulatory intensity, and regional compliance framework divergence. Forecast inputs incorporated GPU compute cost volatility patterns and zero-trust mandate implementation timelines.
Forecast precision tightens around the base case; tail outcomes carry wider variance under accelerated EU AI Act enforcement or prolonged NVIDIA accelerator supply constraints. Practitioners should monitor divergence between NIST sectoral guidance and EU horizontal regulation, adversarial robustness certification standardization progress, and cross-border data flow restriction intensification for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global User Provisioning Market
Security Software
Hardware OTP Token Authentication Market
Security Software
Passwordless Authentication Market
Security Software
Video Intercom Devices Market
Security Software
Global Optical Encryption Market
Security Software
Software Defined Perimeter (SDP) Market
Security Software
Device Vulnerability Management Market
Security Software
Global Mobile Security Software Market
Security Software
DC and PKI Market
Security Software
AD-Blocking Software Market
Security Software
Digital Credential Management Software Market
Security Software
Communication Encryption Software Market
Security Software
Next-Generation Intrusion Prevention System (NGIPS) Market
Security Software
Source Code Escrow Market
Security Software
Encryption As A Service Market
Security Software
Battery-Powered Doorbell Camera Market