
 Mobile Security Market | 2026-2036
Mobile Security Market Size, Share, and Industry Trends Forecast 2026-2036
Mobile Security Market Intelligence
Financial institutions is realigning the end-use vertical mix as banks and payment processors prioritize mobile threat defense over traditional endpoint tools. Microsoft Corporation leverages its cloud ecosystem to anchor enterprise-grade mobile identity services. CrowdStrike Holdings, Inc. specializes in endpoint detection and response integration across iOS and Android fleets. Kaspersky Lab competes in biometric authentication modules for European telecommunications providers.
Mobile security encompasses software, hardware, and policy frameworks designed to protect smartphones, tablets, and wearable devices from malware, unauthorized access, and network intrusion through cryptographic protocols and runtime application self-protection. Its primary commercial purpose is to preserve data confidentiality and transactional integrity across distributed workforces and consumer mobile banking channels. Application security and identity access management occupy the highest-margin solution categories as enterprises consolidate vendor relationships. Cloud-based deployment is displacing on-premises alternatives among small and medium businesses seeking managed detection without dedicated security operations centers. Biometric authentication leads security feature adoption as hardware manufacturers integrate fingerprint and facial recognition at the chipset level.
The Federal Trade Commission enforces data breach notification standards that compel US mobile app developers to embed encryption by default, while the SEC mandates cybersecurity disclosure for publicly traded firms with consumer-facing mobile platforms. The EU AI Act and GDPR impose algorithmic transparency and cross-border data localization requirements that reshape how mobile security vendors architect cloud storage and threat analytics pipelines. Stakeholders must monitor how fragmented national encryption policies affect product certification timelines and determine whether regional data residency investments outweigh standardization economies.
Market Dynamics
Zero-trust architecture mandates from US federal agencies and large enterprises are compressing procurement cycles for mobile threat defense platforms, forcing vendors to bundle identity, endpoint, and network security into unified stacks rather than point solutions.
Growth Catalysts
- GDPR and EU AI Act compliance:European enterprises must demonstrate algorithmic transparency and data localization for mobile analytics, creating procurement urgency for compliant security stacks.
- Biometric hardware integration:Fingerprint and facial recognition modules at the chipset level are enabling passwordless authentication across banking and healthcare mobile applications.
- Financial services vertical:Payment processors and digital banks are prioritizing runtime application self-protection to secure mobile transaction channels against overlay attacks.
Market Restraints
- Semiconductor supply concentration:Trusted execution environment chipsets depend on a limited pool of foundry capacity in Taiwan and South Korea, creating hardware authentication bottlenecks.
- Cross-border data friction:China's data localization requirements and Russia's sovereign internet policies fragment cloud security architectures, forcing redundant infrastructure investments.
- Open-source substitution:Mobile device management vendors face pricing pressure from Android Enterprise and Apple Business Manager native tooling.
Strategic Opportunities
- India's digital payment expansion:The Unified Payments Interface and RBI cybersecurity guidelines are creating demand for localized mobile threat intelligence among fintechs and rural banks.
- Post-quantum cryptography:NIST-standardized algorithms are converging with hardware security modules to future-proof mobile key storage against cryptanalytic advances.
- Managed detection services:Small and medium businesses without security operations centers are adopting cloud-native mobile security platforms through MSP channels.
Industry Challenges
- Zero-trust skill scarcity:Enterprise IT teams lack expertise in microsegmentation and continuous authentication deployment for heterogeneous mobile fleets.
- Certification timeline compression:Common Criteria and FIPS 140-3 evaluations for mobile security modules are extending product launch windows by 12-18 months.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Mobile Security Market |
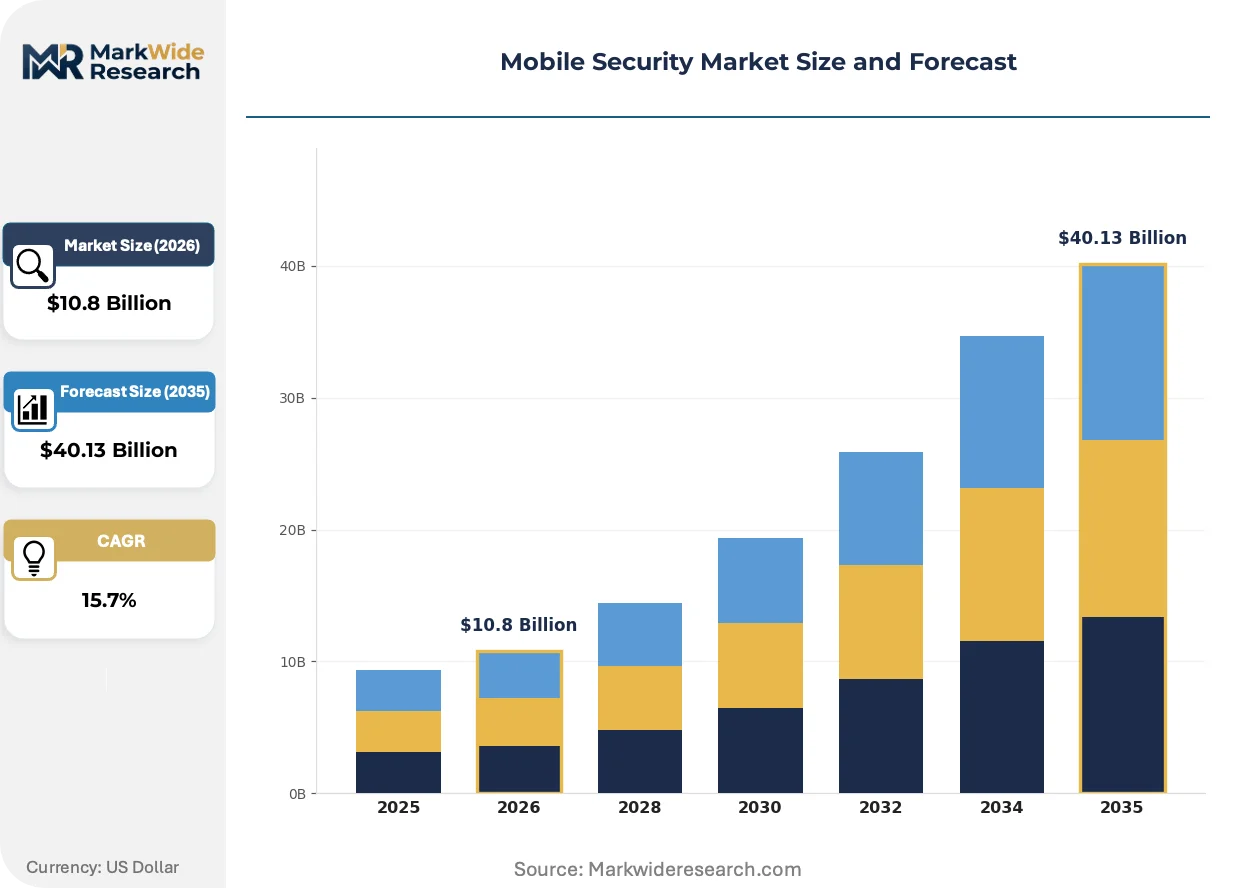
| Market Size in 2026 | $10.8 Billion |
| Market Size in 2035 | $40.13 Billion |
| CAGR (2026 – 2036) | 15.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Antivirus, Application Security, Data Encryption, Mobile Device Management, Network Security, Identity Access Management Deployment Mode: Cloud-Based, On-Premises, Hybrid, Managed Security Services, Virtual Private Network, Endpoint Security Security Features: Biometric Authentication, Two-Factor Authentication, Threat Detection, Firewall, Secure Boot, Anti-Phishing End User: Enterprises, Government Agencies, Financial Institutions, Telecommunications Providers, Educational Institutions, Small & Medium Businesses |
| Companies Covered | McAfee LLC, Trend Micro Inc., Symantec Corporation, Cisco Systems, Inc., Check Point Software Technologies Ltd., Microsoft Corporation, CrowdStrike Holdings, Inc., Bitdefender, Kaspersky Lab, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Mobile Security Market Strategic Shifts & Innovations
Runtime application self-protection is absorbing development resources as vendors embed security logic directly into mobile app binaries rather than relying on external agents, compressing the traditional endpoint security stack.
Artificial intelligence-driven behavioral biometrics is absorbing authentication workflows across financial services mobile applications. JPMorgan Chase and HSBC are deploying keystroke dynamics and gait analysis for continuous identity verification. The technology is absorbing market share from static fingerprint and facial recognition systems by reducing false acceptance rates without additional hardware.
The EU AI Act's risk classification framework is forcing mobile security vendors to document training data provenance and algorithmic decision logic for automated threat detection. European telecommunications providers must now maintain audit trails for AI-powered fraud prevention models. German and French regulators are conducting parallel compliance reviews, creating divergent certification requirements for cross-border service delivery.
Enterprise procurement of mobile security is consolidating around platform bundles rather than best-of-breed point solutions. Chief information security officers are negotiating master service agreements with cloud hyperscalers for integrated identity and endpoint protection. This pattern is most visible in United States healthcare systems responding to HIPAA breach notification pressures and FTC consent orders.
Mobile Security Market Segmentation
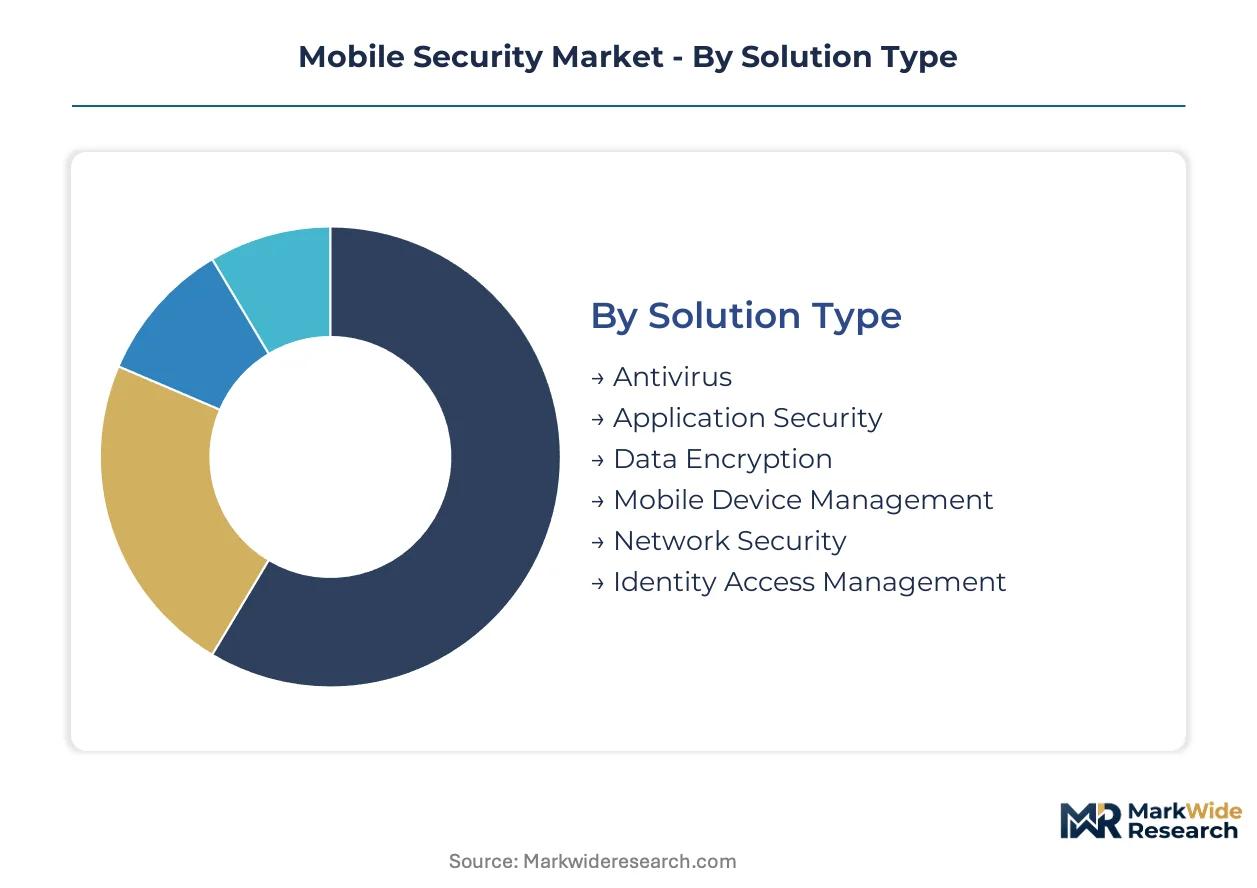
Mobile security procurement patterns diverge sharply across organizational maturity and threat exposure profiles. Solution architecture, deployment economics, and authentication requirements reshape vendor selection criteria for each segment cluster.
Solution Type:
Common Criteria EAL4+ certification burdens fall heaviest on identity and encryption modules for federal contractors, while antivirus and MDM solutions face lighter FIPS 140-2 validation requirements.
- Identity Access Management:Unified credential lifecycle platforms integrate zero-trust policy enforcement with hardware-backed key storage. Financial institutions in the United States dominate procurement volume as SEC disclosure mandates accelerate privileged access consolidation.
- Application Security:Runtime application self-protection embeds threat detection logic directly into mobile binaries, eliminating agent dependency. Digital payment processors prioritize this segment to defend against overlay attacks on Android transaction screens.
- Antivirus:Signature-based malware scanning for consumer and small business endpoints.
- Data Encryption:Full-disk and file-level cryptographic protection for data-at-rest compliance.
- Mobile Device Management:Fleet enrollment, policy enforcement, and remote wipe capabilities for enterprise-owned devices.
- Network Security:VPN tunneling, DNS filtering, and secure web gateway integration for mobile traffic.
Leading the category by volume: Identity Access Management. Growing fastest: Application Security.
Deployment Mode:
Cost tier stratification separates hyperscaler-native platforms from self-managed infrastructure, with hybrid architectures capturing mid-market price sensitivity.
- Cloud-Based:SaaS-delivered security operations eliminate capital expenditure for threat intelligence ingestion and automated response orchestration. Small and medium businesses in the United States adopt through managed service provider channels to bypass security operations center buildouts.
- Managed Security Services:Outsourced detection and response with guaranteed SLA coverage for incident containment. Healthcare systems facing HIPAA breach notification pressures contract for 24/7 mobile threat monitoring.
- On-Premises:Air-gapped or data-center-hosted control planes for classified or regulated workloads.
- Hybrid:Split architecture with cloud analytics and on-premises policy enforcement nodes.
- Virtual Private Network:Dedicated tunnel infrastructure for remote workforce connectivity.
- Endpoint Security:Agent-based protection deployed directly on mobile devices with local decision-making.
Highest margin concentration: Managed Security Services. Steepest expansion trajectory: Cloud-Based.
Security Features:
Application context determines feature prioritization—banking apps demand continuous behavioral verification while enterprise productivity tools emphasize containerization boundaries.
- Biometric Authentication:Fingerprint, facial, and iris recognition leveraging trusted execution environment hardware. JPMorgan Chase and HSBC deploy keystroke dynamics and gait analysis for step-up authentication in mobile banking workflows.
- Anti-Phishing:URL reputation scanning, SMS link analysis, and credential compromise detection integrated at the OS layer. Telecommunications providers bundle this capability to reduce subscriber fraud losses.
- Two-Factor Authentication:Time-based one-time passwords and push notification approval workflows.
- Threat Detection:Behavioral analytics and machine learning models for anomaly identification.
- Firewall:Application-aware traffic filtering and network segmentation controls.
- Secure Boot:Cryptographic verification of firmware integrity during device initialization.
Widest deployment: Biometric Authentication. Gaining share fastest: Anti-Phishing.
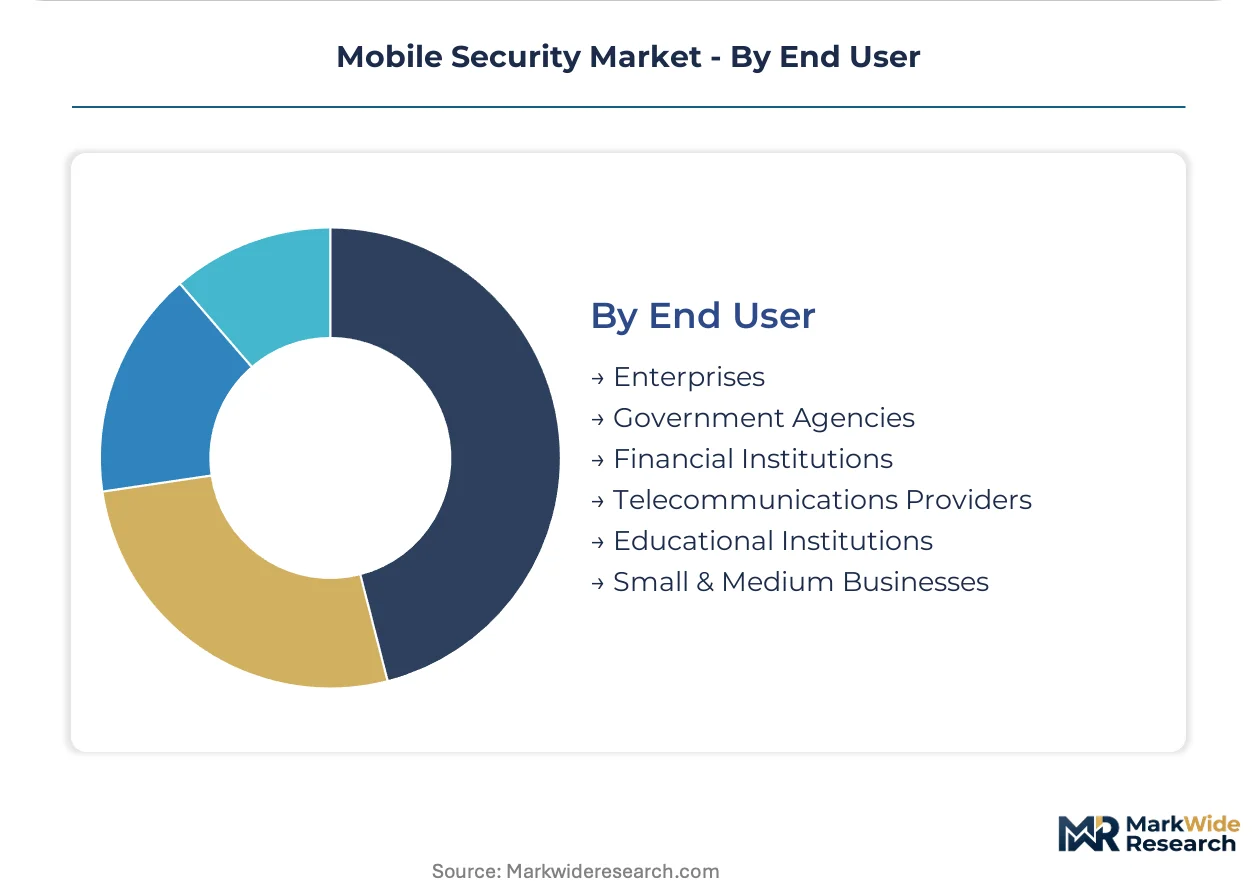
End User:
Procurement sophistication separates enterprise security operations centers from government certification requirements and SMB budget constraints.
- Financial Institutions:Regulatory capital requirements and FFIEC examination pressure drive integrated platform investments covering identity, endpoint, and fraud prevention. The Federal Reserve's operational resilience expectations mandate mobile channel redundancy.
- Government Agencies:FedRAMP authorization and DISA STIG compliance filter vendor eligibility for federal mobile deployments. Zero-trust architecture mandates from CISA compress evaluation timelines.
- Enterprises:Fortune 500 security operations centers with dedicated mobile threat hunting teams.
- Telecommunications Providers:Subscriber-facing security bundles and network-level fraud prevention.
- Educational Institutions:Student and faculty device management with limited security staffing.
- Small & Medium Businesses:Price-sensitive adoption through bundled productivity suites and MSP relationships.
Largest absolute spend: Financial Institutions. Expanding most quickly: Government Agencies.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Mobile security solution development concentrates in the United States and Western Europe, while consumption spreads across financial centers and government hubs worldwide. Production of trusted execution environment chipsets depends heavily on Taiwan and South Korea foundries. Regulatory divergence between Washington, Brussels, and Beijing fragments cloud architecture strategies.
United States
Zero-trust architecture mandates from CISA and SEC cybersecurity disclosure rules compress procurement cycles for federal contractors and publicly traded firms. The FTC enforces data breach notification standards that compel mobile app developers to embed encryption by default. Silicon Valley and Seattle clusters anchor cloud-native security operations, while New York financial institutions drive demand for runtime application self-protection.
Germany
Industrial conglomerates and automotive manufacturers prioritize hardware-backed mobile identity for connected workforce devices. The EU AI Act and GDPR impose algorithmic transparency requirements that reshape how vendors architect threat analytics pipelines. Munich and Stuttgart cybersecurity clusters specialize in Common Criteria certification for federal and defense mobile deployments.
United Kingdom
Financial services regulators at the Bank of England and FCA mandate operational resilience standards for mobile banking channels. Post-Brexit data adequacy negotiations with Brussels create uncertainty for cross-border cloud security architectures. London fintech density drives demand for behavioral biometrics in payment applications, while Cambridge security research clusters feed specialized talent pipelines.
India
The Unified Payments Interface and RBI cybersecurity guidelines create localized demand for mobile threat intelligence among fintechs and rural banks. Domestic data localization requirements force redundant infrastructure investments for foreign security vendors. Mumbai and Bangalore clusters concentrate payment processor security procurement, with Hyderabad emerging as a managed detection services hub for SMB banking.
Japan
METI guidelines on mobile workforce security and aging IT infrastructure accelerate cloud migration among manufacturers. Biometric authentication adoption concentrates in Tokyo banking consortia deploying facial recognition for corporate mobile access. Osaka industrial clusters drive demand for secure device management in supply chain logistics applications.
Mobile Security Market Key Industry Players
Top-tier vendors anchor enterprise platform bundles, while mid-tier specialists compete on vertical-specific compliance certifications. The vendor base separates into cloud hyperscalers with identity ecosystems, endpoint detection specialists with mobile agent expertise, and regional players with sovereign data residency capabilities. Strategic moves concentrate on zero-trust stack consolidation and managed security service expansion through MSP channels.
Within the cloud-integrated tier, Microsoft Corporation and CrowdStrike Holdings, Inc. exemplify divergent approaches to mobile threat defense. Kaspersky Lab occupies a position among European-focused specialists navigating GDPR and EU AI Act compliance complexity.
| Leading Market Players |
|---|
| McAfee LLC |
| Trend Micro Inc. |
| Symantec Corporation |
| Cisco Systems, Inc. |
| Check Point Software Technologies Ltd. |
| Microsoft Corporation |
| CrowdStrike Holdings, Inc. |
| Bitdefender |
| Kaspersky Lab |
| Others |
Cost & Logistics Intelligence
Captive foundry relationships with Taiwan Semiconductor Manufacturing Company and Samsung Electronics anchor supply security for trusted execution environment chipsets, embedding authentication hardware costs directly into mobile security platform pricing. This vertical integration pattern concentrates procurement leverage among vendors with guaranteed wafer allocation, compressing margins for second-tier competitors dependent on spot-market semiconductor availability.
Pricing Analysis
Short lead-time premiums of thirty to fifty percent over standard delivery schedules dominate procurement negotiations for FIPS 140-3 certified hardware security modules. Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized platforms from commercial-grade alternatives and open-source tooling. Cost compression in the SMB tier intensifies because Android Enterprise and Apple Business Manager native capabilities eliminate agent licensing fees. Government agencies exhibit lowest price sensitivity due to zero-trust mandate compliance deadlines, while educational institutions face acute budget constraints.
Supply Chain Analysis
Freight cost volatility from Asia-Pacific semiconductor hubs adds four to eight percent landed cost variance for European and North American security vendors sourcing trusted execution environment chipsets. Manufacturing concentration in Taiwan, South Korea, and China draws from specialized foundry capacity for hardware-backed key storage components. Single-source vulnerability around TSMC's advanced node production creates certification timeline risk for vendors awaiting Common Criteria evaluations. Distribution runs through hyperscaler marketplaces and managed service provider channels rather than direct hardware shipment.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Trusted execution environment foundry capacity constraints prop pricing power for vendors with secured wafer commitments, transforming procurement timelines into competitive moats. This supply-constrained dynamic favors incumbents with multi-year foundry agreements and disadvantages entrants lacking volume guarantees.
For Market Incumbents: Anchor zero-trust platform consolidation through bundling identity, endpoint, and network security into unified stacks rather than defending point solution margins. CrowdStrike and Microsoft ecosystem expansion threatens standalone mobile threat defense vendors. Certification investment in Common Criteria EAL4+ and FedRAMP authorization creates switching cost barriers against cloud-native challengers. For New Entrants and Emerging Players: Capture India's Unified Payments Interface security gap among rural banks and fintechs lacking dedicated security operations centers. Post-quantum cryptography hardware modules represent the most penetrable segment as NIST algorithm standardization creates first-mover certification opportunities. Go-to-market through managed service provider channels bypasses direct enterprise sales friction. For Investors and Strategic Acquirers: Exit pathways concentrate in hyperscaler acquisition of vertical-specific compliance specialists with sovereign data residency capabilities. Long-term viability hinges on EU AI Act audit trail infrastructure and hardware authentication differentiation against software-only substitutes. Watch NIST post-quantum cryptography deployment timelines as inflection signal for hardware security module refresh cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Platform Consolidation | Bundling identity and endpoint security responds to CISA mandate compression in federal procurement. |
| Post-Quantum Cryptography Certification | NIST algorithm standardization creates hardware refresh demand among financial institutions. |
| Managed Detection Service Expansion | MSP channel partnerships bypass SMB security operations center buildout barriers. |
| EU AI Act Compliance Infrastructure | Algorithmic transparency tooling captures European telecommunications provider procurement urgency. |
| India Data Localization Investment | RBI guidelines force redundant infrastructure for foreign vendors serving UPI security demand. |
Research Approach
Trade association data, regulatory filings, and customs records anchored secondary inputs, cross-referenced with primary interviews of CISOs at financial institutions, federal procurement officers, MSP channel managers, and semiconductor supply planners. SEC cybersecurity disclosure filings, FedRAMP authorization repositories, DISA STIG documentation, and EU AI Act implementation guidance provided validation benchmarks. Bottom-up vendor revenue triangulation against top-down enterprise IT security spending estimates refined market sizing.
Data-stream reconciliation across deployment mode, solution architecture, organization size, vertical compliance intensity, and regional regulatory cluster produced segment-level projections. CAGRs derived from weighted average of historical procurement velocity and policy-mandated replacement cycles. Runtime application self-protection adoption curves and biometric hardware integration rates served as mobile-specific demand inputs across the modeling period.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to semiconductor foundry capacity allocation and fragmented national encryption policy divergence. Outputs reflect documented assumptions regarding zero-trust mandate enforcement timelines and post-quantum cryptography standardization velocity. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Europe User Provisioning Market
Security Software
Security Software Market
Security Software
Unified Threat Management (UTM) Market
Security Software
Global Background Check Software Market
Security Software
AI Security Platforms Market
Security Software
AI in Security Market
Security Software
Encryption As A Service Market
Security Software
North America Video Management System Market
Security Software
Doorbell Camera Market
Security Software
DNS Protection Software Market
Security Software
Global Consumer Identity and Access Management Market
Security Software
Network Security Appliance Market
Security Software
Mass Notification System Market
Security Software
Global Mobile Identification Market
Security Software
Extended Detection and Response Market
Security Software
United States Consumer Identity and Access Management Market