
 Application Security Market | 2026-2036
Application Security Market Size, Share, and Industry Trends Forecast 2026-2036
Application Security Market Intelligence
The specialist vendor segment, once focused on standalone testing tools, is pivoting towards integrated DevSecOps platforms to meet enterprise demands. Synopsys, Inc. leverages its comprehensive portfolio to embed security across the software development lifecycle. Veracode specializes in cloud-native application security, offering a unified platform for developers. Checkmarx competes by providing a flexible suite of static and interactive testing solutions for its global enterprise clients.
Application security encompasses the processes and tools designed to find, fix, and prevent vulnerabilities throughout the software lifecycle. These systems identify flaws like SQL injection and insecure deserialization by analyzing code, dependencies, and runtime behavior to ensure data confidentiality and system integrity. Static Application Security Testing (SAST) forms a foundational segment, while Software Composition Analysis (SCA) is gaining traction for open-source component security. Cloud-based deployment is the dominant model for new implementations, particularly within the financial services and e-commerce end-user categories.
Regulatory frameworks like the EU's General Data Protection Regulation (GDPR) and the Payment Card Industry Data Security Standard (PCI DSS) mandate stringent application security measures. Directives from the US National Institute of Standards and Technology (NIST) and HIPAA requirements for healthcare data also compel organizations to adopt comprehensive testing. Vendor selection now hinges on providing a unified platform that addresses compliance and integrates into developer workflows.
Market Dynamics
The central force shaping the application security market is the "shift-left" paradigm, where security testing is integrated directly into the software development lifecycle. This structural change is driven by regulatory mandates and the need to secure increasingly complex, cloud-native applications.
Growth Catalysts
- Regulatory Mandates:Stringent frameworks like the EU's GDPR and the PCI DSS standard for payment processing compel organizations, particularly in financial services and e-commerce, to implement comprehensive application security testing to avoid severe penalties.
- Cloud-Native Development:The proliferation of microservices and container-based architectures expands the potential attack surface of applications, creating persistent demand for specialized cloud security posture management and container scanning tools.
- Open-Source Component Risk:Widespread use of open-source libraries necessitates robust Software Composition Analysis (SCA) tools to identify and mitigate vulnerabilities within third-party code, a critical concern for enterprise software developers.
Market Restraints
- Integration Complexity:Weaving disparate security tools such as SAST, DAST, and IAST into a unified CI/CD pipeline without causing developer friction or slowing release cycles presents a significant technical barrier for many organizations.
- High Platform Costs:The total cost of ownership for enterprise-grade DevSecOps platforms, including licensing, implementation, and specialized personnel, can be prohibitive for small and medium-sized businesses, limiting market penetration.
- Developer Resistance:Security tools that produce a high volume of false positives or are perceived as hindering development velocity often face resistance from engineering teams, impeding effective adoption and remediation efforts.
Strategic Opportunities
- Securing AI and ML Pipelines:The emerging field of AI/ML application development presents a new frontier for security vendors to offer specialized tools for model integrity validation, data poisoning prevention, and adversarial attack resistance.
- Expansion in Southeast Asia:Rapid digitalization and a growing technology sector in countries like Singapore and Indonesia create significant white-space opportunities for application security vendors to establish a foothold in an underpenetrated market.
- API Security Specialization:As APIs become the connective tissue for modern applications, there is a distinct opportunity for solutions focused exclusively on API discovery, testing, and real-time threat protection to address this specific vulnerability vector.
Industry Challenges
- DevSecOps Talent Scarcity:A persistent shortage of professionals with hybrid expertise in both software development and cybersecurity principles creates an operational bottleneck, hindering the effective implementation and management of advanced security programs.
- Managing Alert Fatigue:Automated scanning tools often generate a high volume of security alerts, overwhelming security teams and making it difficult to prioritize and remediate the most critical vulnerabilities in a timely manner.
- Legacy System Integration:Incorporating modern application security testing tools into workflows that rely on monolithic legacy applications and outdated development environments poses a significant integration and compatibility challenge for established enterprises.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Application Security Market |
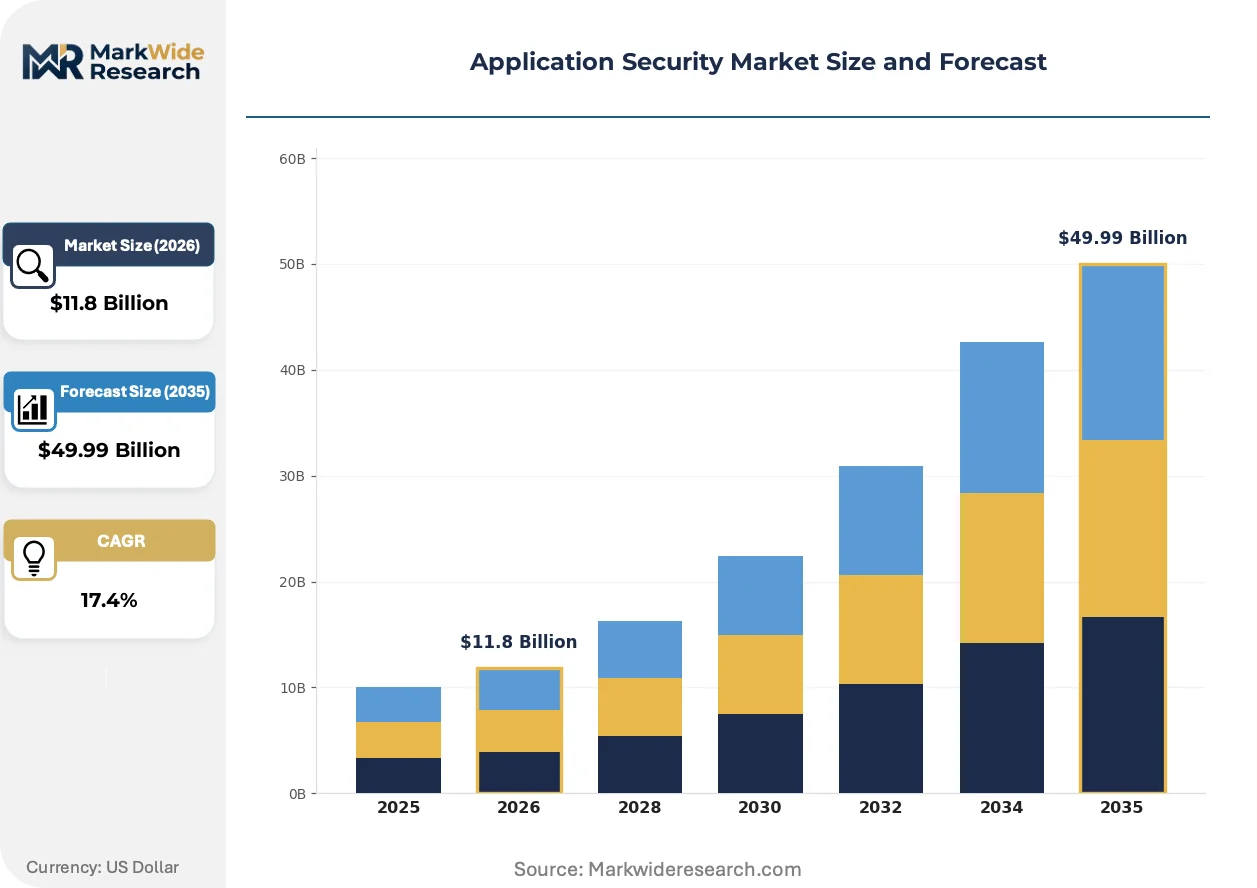
| Market Size in 2026 | $11.8 Billion |
| Market Size in 2035 | $49.99 Billion |
| CAGR (2026 – 2036) | 17.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Security Type: Static Application Security Testing, Dynamic Application Security Testing, Interactive Application Security Testing, Runtime Application Self-Protection, Software Composition Analysis Deployment Mode: Cloud-Based, On-Premises, Hybrid, Managed Service, Software as a Service End User: Financial Services, Telecommunications, Government Agencies, E-Commerce, Education Organization Size: Small Enterprises, Medium Enterprises, Large Enterprises, Startups, Nonprofit Organizations |
| Companies Covered | IBM Corporation, Synopsys, Inc., Veracode, Qualys, Inc., Checkmarx, HCL Technologies, Oracle Corporation, Imperva, Rapid7, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Application Security Market Strategic Shifts & Innovations
The market is defined by a decisive pivot from isolated, post-build scanning to embedded security intelligence within developer workflows. This evolution is driven by the need for speed and accuracy, with platform consolidation reshaping competitive positioning for vendors and buyers alike.
Application Security Posture Management (ASPM) provides a holistic, correlated view of security risks across the entire software development lifecycle. Large enterprises in the technology and financial sectors are the primary adopters, seeking to manage vulnerability data from numerous development teams. ASPM is unifying disparate findings from SAST, DAST, and SCA tools into a single, risk-prioritized dashboard, enabling more efficient remediation.
New regulations are compelling proactive security integration. The EU AI Act, for instance, imposes strict requirements on the security and robustness of high-risk artificial intelligence systems. This directive forces developers to embed security controls throughout the AI model lifecycle, from data ingestion to deployment. The technology and healthcare sectors in Europe are most affected, integrating security testing directly into MLOps pipelines to ensure compliance.
Enterprise buying behavior is consolidating around unified platforms rather than individual point solutions for different testing types. This trend disrupts the market for niche vendors specializing only in static or dynamic analysis, favoring providers with an integrated suite. This preference is most visible in the United States and Germany, where large organizations seek to simplify vendor management and streamline compliance reporting across their software portfolios.
Application Security Market Segmentation
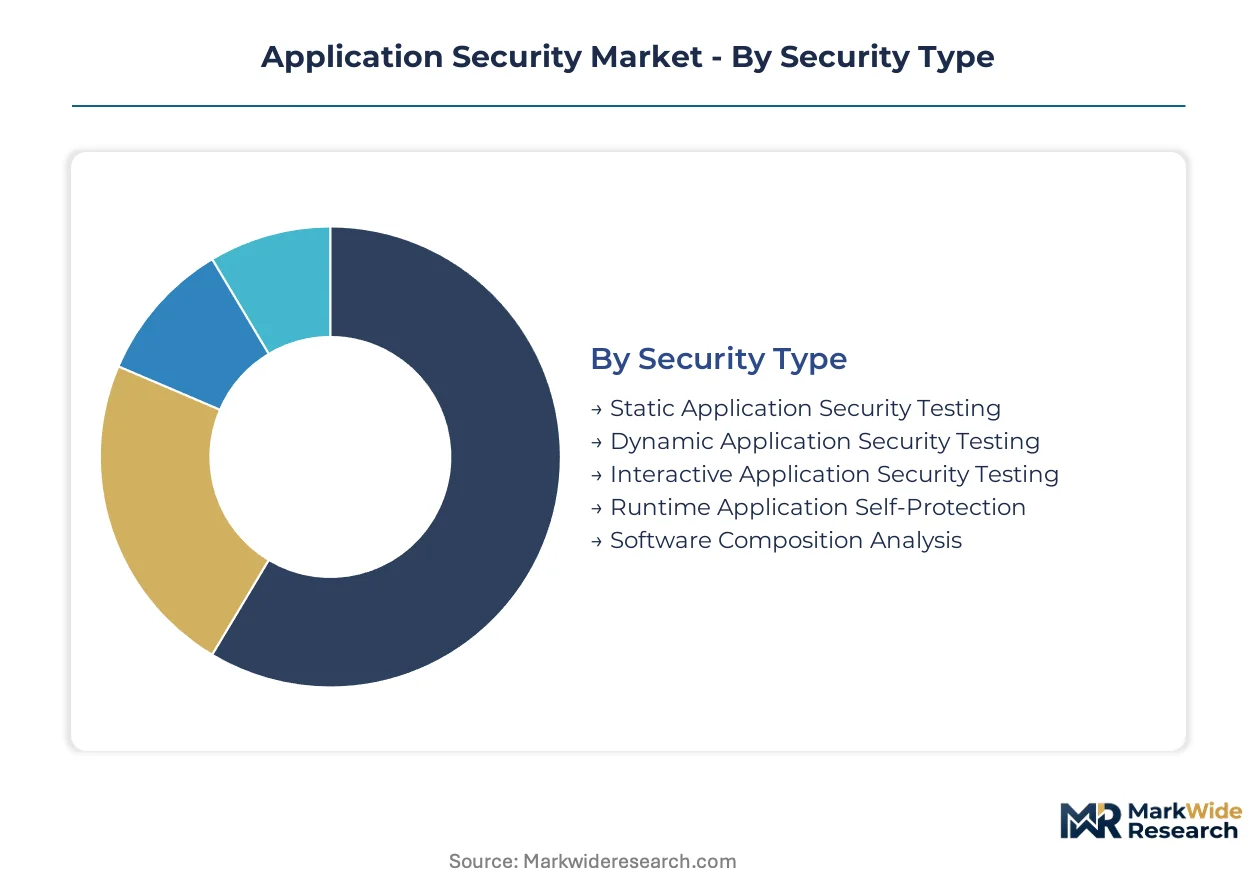
The application security market segments based on the specialized tools, deployment methods, and diverse end-user requirements. Understanding these segments reveals where security investments are concentrating and how different organizational needs drive solution adoption. This granular view highlights the evolving landscape of threat protection across various industries.
Security Type:
The capital intensity of application security solutions often dictates adoption patterns for specific security types. Organizations invest significantly in comprehensive tools that integrate across the software development lifecycle.
- Static Application Security Testing:SAST tools analyze source code, bytecode, or binary code without executing the application to find vulnerabilities like SQL injection. Large enterprises in technology and finance prioritize SAST for early detection in complex codebases.
- Software Composition Analysis:SCA tools identify security vulnerabilities and licensing issues in open-source components and third-party libraries. This is critical for enterprise software developers managing extensive dependencies, driven by compliance needs like the EU AI Act.
- Dynamic Application Security Testing:DAST tools test running applications from the outside, simulating attacks to identify runtime vulnerabilities. These solutions complement SAST by finding issues only visible during execution.
- Interactive Application Security Testing:IAST combines elements of SAST and DAST, analyzing code from within the running application. IAST provides more accurate results with fewer false positives, enhancing developer efficiency.
- Runtime Application Self-Protection:RASP tools integrate directly into the application runtime environment, detecting and blocking attacks in real-time. RASP offers immediate protection for deployed applications against active threats.
Most installed capacity flows through Static Application Security Testing. Expansion is steepest in Software Composition Analysis.
Deployment Mode:
Customer preferences for infrastructure management and service delivery shape the deployment mode segment. Organizations choose models based on their IT capabilities and operational strategies.
- Cloud-Based:Cloud-based deployment hosts application security solutions on public cloud infrastructure, offering scalability and accessibility. This model dominates new implementations, particularly for financial services and e-commerce platforms.
- Managed Service:Managed services outsource application security operations to third-party providers, leveraging external expertise. Organizations facing DevSecOps talent scarcity widely adopt managed services to ensure continuous security.
- On-Premises:On-premises deployment involves installing and running security software within an organization's own data centers. Highly regulated industries with strict data residency requirements, such as government agencies, often prefer this mode.
- Hybrid:Hybrid deployment combines both on-premises and cloud-based security solutions, offering flexibility and control. This approach suits enterprises transitioning to cloud environments while maintaining legacy systems.
- Software as a Service:SaaS delivers application security tools over the internet on a subscription basis, reducing upfront costs and maintenance burden. SaaS models appeal to small and medium-sized enterprises seeking rapid deployment.
Cloud-Based deployment holds the largest volume share. Managed Service deployment is gaining share fastest.
End User:
Regulatory frameworks and the sensitivity of data drive distinct application security needs across various end-user industries. Each sector faces unique compliance mandates and threat landscapes.
- Financial Services:This sector requires stringent application security measures to protect sensitive customer data and transaction platforms. Regulations like PCI DSS and GDPR compel financial institutions to implement comprehensive testing.
- E-Commerce:E-commerce platforms handle large volumes of personal and payment data, making them prime targets for cyberattacks. Adherence to PCI DSS and data privacy regulations is paramount for online retailers.
- Telecommunications:Telecommunication companies manage vast networks and critical infrastructure, demanding robust security for their applications. Protecting customer communication and network integrity drives security investments.
- Government Agencies:Government entities safeguard national security information and citizen data, necessitating high-assurance application security. NIST directives and other national security standards guide their adoption.
- Education:Educational institutions manage student records and research data, requiring protection against data breaches. Budget constraints often influence their choice of cost-effective, cloud-based security solutions.
Financial Services commands the largest market share by value. E-Commerce exhibits the most significant growth in new implementations.
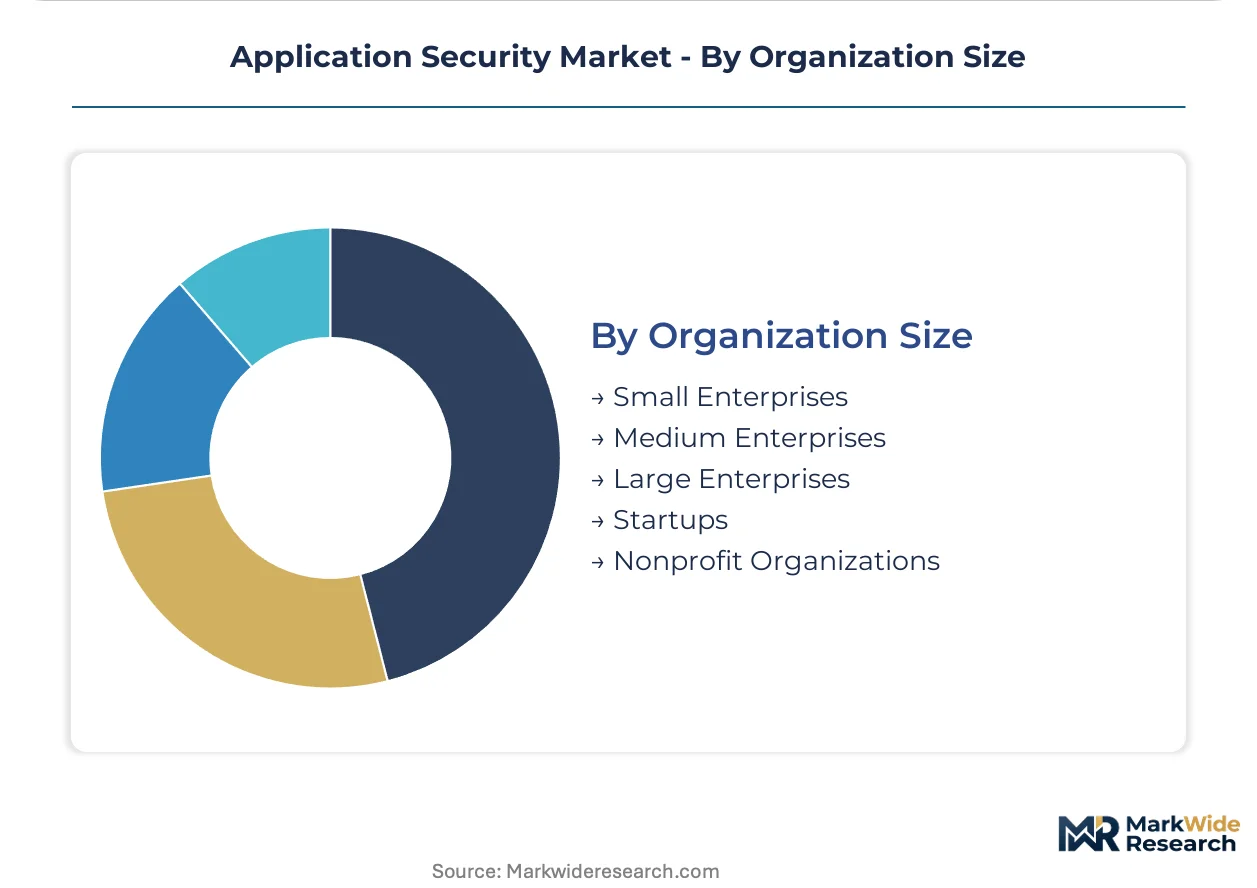
Organization Size:
The complexity of IT infrastructure and available budget influence application security adoption patterns across different organizational sizes. Solutions scale to meet varied operational demands.
- Large Enterprises:These organizations manage complex, distributed application portfolios and face extensive regulatory compliance. They demand integrated DevSecOps platforms and advanced security posture management solutions.
- Medium Enterprises:Medium-sized businesses balance growing security needs with moderate budgets, often seeking scalable and cost-effective cloud-based solutions. They prioritize tools that integrate easily into existing development workflows.
- Small Enterprises:Small businesses typically have limited IT resources and budget, favoring easy-to-use, often SaaS-based, security tools. Their focus is on foundational protection against common vulnerabilities.
- Startups:Startups prioritize rapid development and deployment, often integrating security tools early in their agile development cycles. Cloud-native security solutions are particularly attractive for their flexible infrastructure.
- Nonprofit Organizations:Nonprofits operate with budget constraints but still require protection for sensitive donor or beneficiary data. They often seek affordable, open-source, or managed security services.
Large Enterprises contribute the highest revenue. Medium Enterprises show the fastest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The global application security market exhibits varied adoption patterns, often influenced by the cost of regulatory compliance. Organizations may strategically locate development centers in regions offering a favorable balance between security mandates and operational expenditure. This dynamic shapes regional investment and technology deployment.
United States
United States enterprises drive significant demand for integrated DevSecOps platforms, particularly within financial services and technology sectors. NIST directives and HIPAA requirements compel robust security testing for data protection. Technology clusters like Silicon Valley and New York City concentrate innovation in cloud-native security solutions.
Germany
German industries prioritize advanced application security due to stringent data privacy laws and complex industrial systems. The EU AI Act and GDPR mandate comprehensive security throughout software lifecycles for high-risk applications. Major industrial hubs such as Munich and Berlin foster adoption of specialized testing tools.
Singapore
Singapore's rapid digitalization across financial services and e-commerce fuels demand for robust application security solutions. The Personal Data Protection Act (PDPA) and government cybersecurity initiatives guide secure software development practices. The One-North technology park and financial district are key centers for innovative security implementations.
India
India's burgeoning IT services and digital transformation initiatives generate substantial requirements for application security tools. The Information Technology Act and proposed Digital Personal Data Protection Act necessitate strong protection for consumer data. Major IT hubs in Bengaluru and Hyderabad are rapidly integrating DevSecOps practices.
Japan
Japanese technology firms and financial institutions require sophisticated application security to protect sensitive intellectual property and customer data. The Act on Protection of Personal Information (APPI) and national cybersecurity strategies drive enterprise security investments. Tokyo and Osaka remain critical centers for adopting advanced security testing technologies.
Application Security Market Key Industry Players
Established producers occupy the standard tier, focusing on foundational SAST and DAST offerings; emerging entrants pursue integrated DevSecOps platforms and specialized solutions for AI/ML security. The market structure features a blend of large, diversified technology conglomerates and agile, niche security vendors. Strategic archetypes include comprehensive platform providers, cloud-native specialists, and API security innovators. Portfolio diversification through strategic acquisitions and technology partnerships are common competitive moves.
Specialists in integrated DevSecOps platforms, Synopsys, Inc. represents a comprehensive portfolio approach to embedding security across the software development lifecycle. Veracode, meanwhile, exemplifies a strong focus on cloud-native application security, offering unified platforms tailored for modern development environments. Checkmarx occupies a position as a provider of flexible static and interactive testing solutions, catering to a global enterprise client base seeking adaptable security suites.
| Leading Market Players |
|---|
| IBM Corporation |
| Synopsys, Inc. |
| Veracode |
| Qualys, Inc. |
| Checkmarx |
| HCL Technologies |
| Oracle Corporation |
| Imperva |
| Rapid7 |
| Others |
Cost & Logistics Intelligence
Large enterprises in the technology and financial sectors drive demand for subscription-based DevSecOps platforms, where pricing models reflect comprehensive feature sets and ongoing support.
Pricing Analysis
Vendor margin on DevSecOps platforms reflects the value of integrated security intelligence. Subscription-based pricing dominates, offering tiered access based on features and user scale. Price differentiation stems from customization level for complex enterprise environments and bundled managed services. Pricing pressure stems from the increasing number of unified platform providers. Small and medium-sized enterprises are most price-sensitive, while large enterprises prioritize advanced integration capabilities.
Supply Chain Analysis
Application security development relies heavily on highly skilled software engineering talent, often concentrated in technology hubs across the United States and India. Cloud infrastructure services from major providers like AWS and Azure form a critical dependency for SaaS deployments. A key supply chain risk is the persistent DevSecOps talent scarcity, hindering effective implementation. Distribution runs through direct sales channels for large enterprise clients and cloud marketplaces for smaller businesses.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
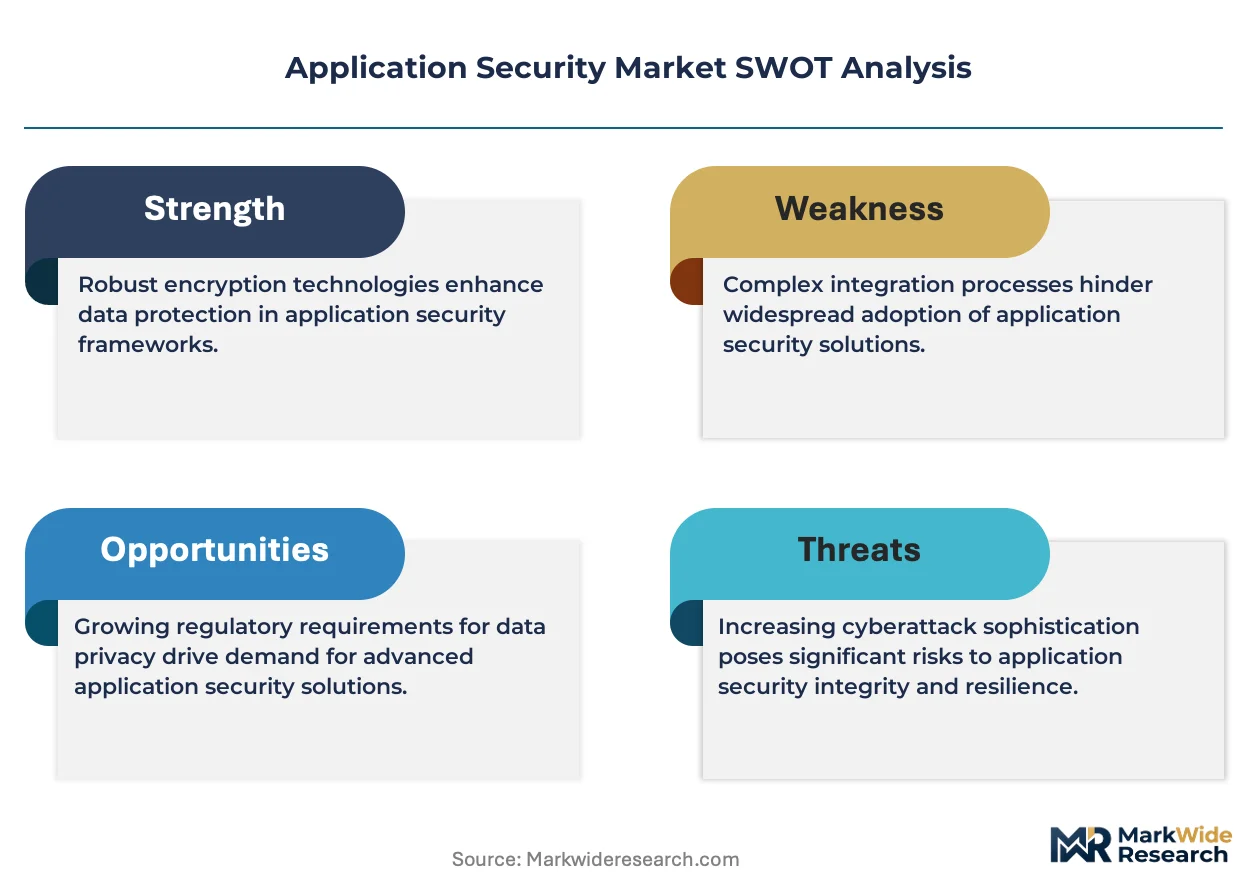
The application security market is evolving into a late-cycle quality story, driven by demand for unified platforms providing comprehensive security posture management. Enterprises increasingly seek premium specifications for integrated DevSecOps tools.
For Market Incumbents: Lock in existing enterprise clients by expanding platform capabilities to include emerging AI/ML security and API protection. Deepen integration with major CI/CD pipelines to counter developer resistance and competitive offerings from specialized point solutions. Invest in R&D for AI-driven false positive reduction, improving developer experience. Certification investment for EU AI Act compliance will also reinforce market position.
For New Entrants and Emerging Players: A price-point gap exists for specialized, cost-effective cloud-native security solutions targeting medium enterprises. Target underpenetrated markets like Southeast Asia with developer-first API security tools. Focus on providing SaaS-based solutions with low integration complexity to address developer resistance. Offer solutions for securing AI/ML pipelines, a nascent but critical vulnerability vector.
For Investors and Strategic Acquirers: Large technology conglomerates are the most active acquirers in this space, seeking to expand their DevSecOps platform offerings. The market demonstrates strong long-term viability over the next 5-10 years, driven by continuous software development and regulatory mandates. Target acquisition archetypes include cloud-native application security specialists and AI/ML pipeline protection innovators. The primary signal to watch is the pace of strategic acquisitions of niche technology providers.
| Strategic Initiative | Industry Significance |
|---|---|
| Launch AI-powered vulnerability detection module | Enhances SAST accuracy and reduces alert fatigue for security teams. |
| Integrate with leading CI/CD platforms | Streamlines developer workflows and embeds security earlier in the SDLC. |
| Form partnership for managed DevSecOps services | Addresses DevSecOps talent scarcity and expands reach to smaller enterprises. |
| Acquire API security startup | Strengthens portfolio against a critical and growing vulnerability vector. |
| Expand sales operations in Southeast Asia | Capitalizes on rapid digitalization and underpenetrated market opportunities. |
Research Approach
Bottom-up end-user adoption modeling reconciled against top-down vendor revenue tracking forms the analytical core of this study. Primary interviews with application security architects, DevSecOps engineers, and CISOs informed market dynamics. Secondary validation drew from NIST publications, PCI DSS reports, and corporate annual filings. This approach ensured robust triangulation of market size and growth drivers.
An input-output matrix structured the quantitative model, projecting market evolution across the analysis window. Segmentation dimensions included security type, deployment mode, end-user industry, and organization size. Compound annual growth rates were derived from historical data and projected adoption rates, considering technological shifts. Key forecast inputs included cloud-native application proliferation and enterprise regulatory compliance expenditure.
Caveats apply where rapid technological disruption or unforeseen regulatory shifts could materially shift the outlook. Forecasts reflect current market assumptions and observed adoption patterns. A small set of named triggers warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Cognitive Security Market
Cybersecurity
Global API Security Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Thailand IT and Security Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Data Protection Market
Cybersecurity
Enterprise Firewall Market
Cybersecurity
Global Database Security Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Europe Digital Forensics Market