
 Global Cloud Security Posture Management Market | 2026-2036
Global Cloud Security Posture Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Cloud Security Posture Management Market Foresight
Enterprise buyer demand is bifurcating between regulated financial institutions and agile SaaS-native firms, with the former gaining share as compliance complexity deepens. Palo Alto Networks dominates the high-assurance segment through Prisma Cloud's configuration management depth. Microsoft Corporation leverages its Entra and Defender ecosystem to anchor CSPM within broader security bundles. Check Point Software Technologies Ltd. competes on hybrid cloud visibility across on-premise and AWS environments.
Cloud Security Posture Management comprises automated tools that continuously scan cloud infrastructure for misconfigurations, policy violations, and compliance drift against frameworks such as CIS benchmarks and NIST SP 800-53, with detection latency typically measured in minutes rather than days. Its primary commercial purpose is to prevent data exposure and regulatory penalties before attackers exploit visible weaknesses. Multi-cloud deployments now generate the fastest growth in solution type demand, as organizations struggle with inconsistent security APIs across AWS, Azure, and Google Cloud. Risk assessment modules command premium pricing due to their integration with threat intelligence feeds and automated remediation workflows. Configuration management remains the largest volume category, though margin pools are shifting toward vulnerability management as exploit windows narrow.
The EU AI Act and NIS2 Directive are mandating continuous security monitoring for critical infrastructure operators, directly expanding CSPM procurement scope across European energy and telecommunications sectors. In the United States, NIST's zero-trust architecture guidance and SEC cybersecurity disclosure rules are pressuring publicly traded firms to demonstrate measurable cloud control effectiveness. Stakeholders must monitor how fragmented national cloud sovereignty laws fragment product roadmaps and force localization investments that alter competitive economics.
Market Dynamics
Multi-cloud fragmentation is forcing security teams to consolidate disparate visibility tools into unified control planes, compressing vendor consolidation timelines as configuration drift across AWS, Azure, and Google Cloud environments exposes organizations to compliance penalties.
Growth Catalysts
- NIST SP 800-53 integration:Federal contractors in the United States must demonstrate continuous monitoring capabilities, mandating automated posture assessment across cloud workloads handling controlled unclassified information.
- Payment Card Industry Data Security Standard:Financial services firms processing cardholder data across distributed cloud regions require real-time misconfiguration detection to avoid audit failures and transaction processing suspensions.
- Agentless scanning architectures:Containerized workloads and serverless functions in technology firms are accelerating adoption of passive assessment methods that avoid performance degradation in ephemeral compute environments.
Market Restraints
- API rate limiting:Cloud service providers impose throttling thresholds on security scanning frequency, constraining continuous assessment granularity in large-scale deployments exceeding ten thousand resource instances.
- Specialized talent scarcity:The intersection of cloud architecture expertise and security policy engineering commands compensation premiums exceeding forty percent above baseline cybersecurity roles, elevating total cost of ownership.
- Alert fatigue saturation:Security operations centers face threshold overflow from low-fidelity misconfiguration alerts, degrading mean-time-to-remediation for critical exposures.
Strategic Opportunities
- EU AI Act Article 15:High-risk AI system operators must implement continuous monitoring controls, extending CSPM procurement scope to machine learning training pipelines and inference endpoints.
- Edge computing convergence:Manufacturing facilities deploying industrial IoT gateways at plant perimeters require consistent policy enforcement across centralized cloud and distributed edge infrastructure.
- Managed security service providers:Mid-market enterprises lacking internal cloud security expertise are outsourcing posture management to channel partners delivering bundled assessment and remediation services.
Industry Challenges
- Remediation workflow orchestration:Automated response actions risk service disruption in production environments, requiring human-in-the-loop approval gates that slow vulnerability closure cycles.
- Policy language standardization:Rego, Cedar, and proprietary cloud-native policy formats fragment rule portability across multi-cloud estates, forcing redundant control implementation.
- Identity-perimeter dissolution:Zero-trust architectures eliminate network-based trust boundaries, compelling posture tools to evaluate identity-bound resource access patterns in real-time.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Cloud Security Posture Management Market |
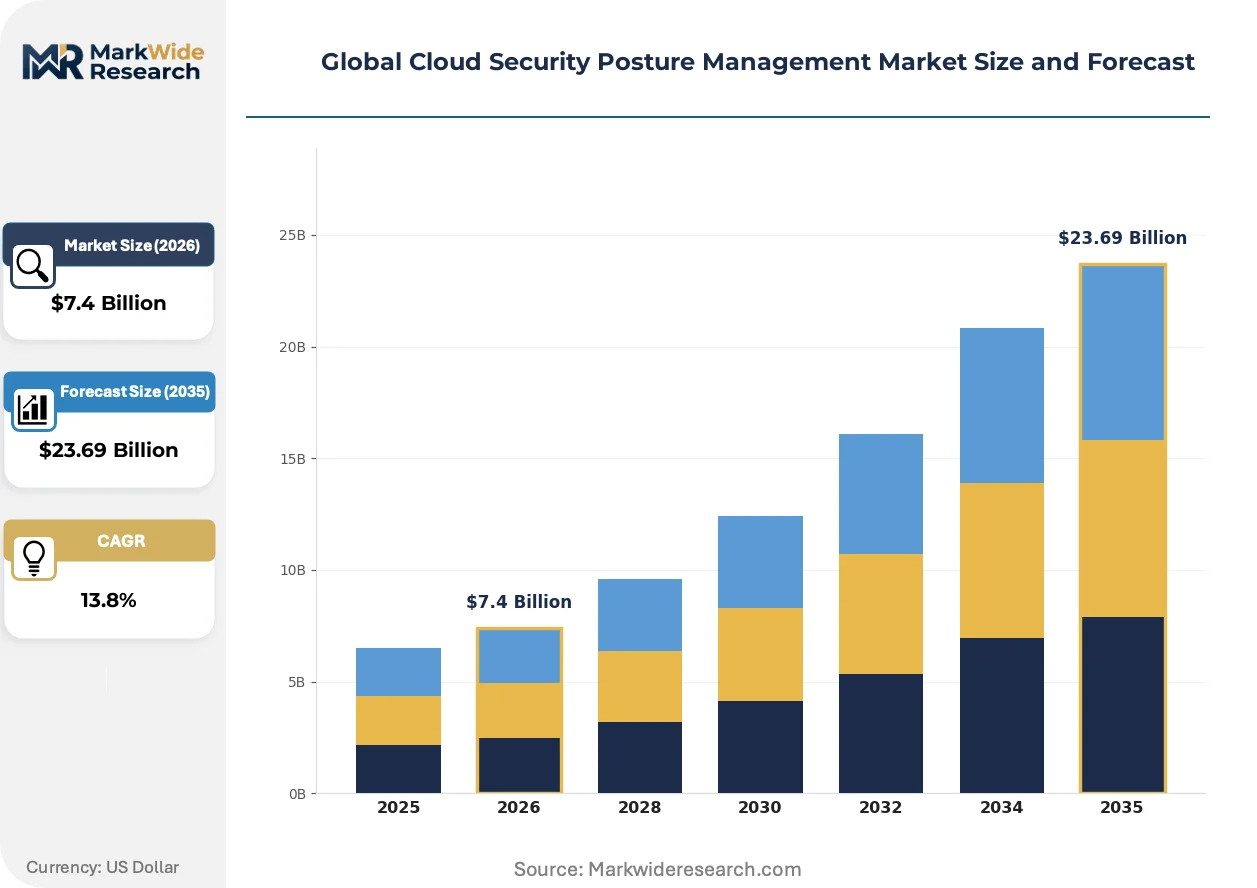
| Market Size in 2026 | $7.4 Billion |
| Market Size in 2035 | $23.69 Billion |
| CAGR (2026 – 2036) | 13.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud, Community Cloud Solution Type: Risk Assessment, Compliance Management, Threat Intelligence, Configuration Management, Vulnerability Management Use Case: Data Protection, Identity & Access Management, Infrastructure Security, Application Security, Incident Response End User Industry: Telecommunications, Manufacturing, Transportation, Energy & Utilities, Government |
| Companies Covered | International Business Machines Corporation, Google LLC, Palo Alto Networks Inc., Fortinet Inc., Amazon Web Services Inc., Check Point Software Technologies Ltd., Oracle Corporation, Trend Micro Incorporated, Microsoft Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Cloud Security Posture Management Market Shifts & Advancements
Cloud security tooling is consolidating around graph-based asset inventory systems that map dynamic relationships between ephemeral compute, identities, and data stores. This architectural shift is compressing point solution viability.
Agentless vulnerability assessment is bifurcating security operations workflows. The technology performs passive configuration analysis through cloud provider APIs without deploying code to target instances. Financial services institutions with strict change control requirements are adopting these methods to satisfy audit mandates. The approach is bifurcating procurement patterns between high-assurance regulated buyers prioritizing non-intrusive assessment and agile development teams accepting agent-based depth.
The EU AI Act is mandating continuous security monitoring for high-risk artificial intelligence systems deployed by critical infrastructure operators. Cloud providers hosting machine learning training pipelines must demonstrate configuration integrity across data ingestion, model versioning, and inference endpoints. European energy and telecommunications sectors are expanding CSPM procurement scope to cover MLOps infrastructure.
Security buying committees are consolidating vendor relationships around platform consolidation strategies. Chief information security officers are terminating point-tool contracts in favor of integrated cloud-native application protection platforms spanning posture management, workload protection, and entitlement management. United States federal agencies under zero-trust mandates are driving this pattern most aggressively.
Global Cloud Security Posture Management Market Segmentation
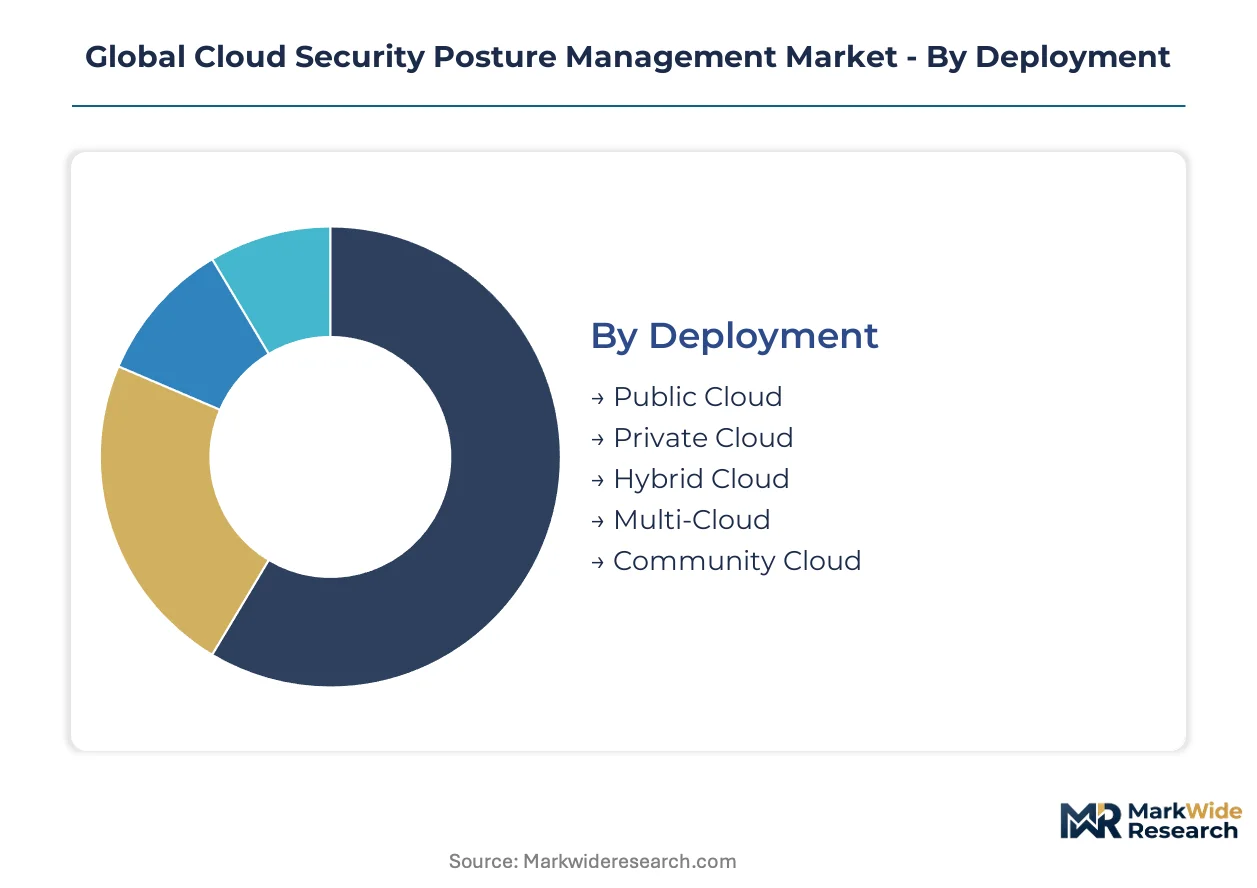
CSPM procurement patterns diverge sharply across deployment architectures and regulatory contexts. Solution buyers prioritize segments aligning with their cloud maturity and compliance exposure rather than pursuing uniform coverage.
Deployment:
Public cloud deployments concentrate in North American technology clusters, while hybrid and multi-cloud patterns dominate European and Asia-Pacific regulated industries.
- Public Cloud:Single-tenant assessments on AWS, Azure, and Google Cloud infrastructure dominate early-stage enterprise adoption. United States financial services firms drive procurement here, pressured by SEC cybersecurity disclosure rules demanding demonstrable control effectiveness.
- Multi-Cloud:Unified visibility across heterogeneous environments commands premium pricing due to API normalization complexity. German automotive manufacturers and Japanese telecommunications operators lead adoption, grappling with fragmented security controls across three-plus provider ecosystems.
- Private Cloud:On-premise OpenStack and VMware environments retain share in defense and intelligence sectors.
- Hybrid Cloud:Consistent policy enforcement bridging legacy data centers and public workloads attracts healthcare providers.
- Community Cloud:Shared infrastructure for government and education consortia operates under specialized procurement frameworks.
Public cloud commands the established base. The steepest expansion runs through multi-cloud.
Solution Type:
Margin pools concentrate in modules integrating threat intelligence with automated response, while configuration management remains the volume anchor.
- Configuration Management:Continuous scanning against CIS benchmarks and NIST SP 800-53 delivers the foundational compliance layer. United States federal contractors mandate this capability for controlled unclassified information workloads, creating procurement floor demand.
- Risk Assessment:Quantified exposure scoring with business-context weighting attracts European banking regulators under ECB supervisory pressure. French and Dutch institutions prioritize these tools for capital adequacy stress testing integration.
- Compliance Management:Automated evidence collection for PCI-DSS and ISO 27001 audits reduces audit preparation cycles.
- Threat Intelligence:Correlation of misconfigurations with active exploit feeds narrows remediation prioritization.
- Vulnerability Management:Agentless scanning of container registries and serverless functions addresses ephemeral compute gaps.
Configuration management delivers the revenue foundation. Risk assessment is climbing the fastest as regulatory quantification demands intensify.
Use Case:
Identity-centric deployments outpace infrastructure-hardening in zero-trust maturity corridors, reversing historical priority sequences.
- Identity & Access Management:Real-time evaluation of entitlement drift and privilege escalation paths dominates federal zero-trust implementations. United States Department of Defense agencies mandate continuous verification of cloud resource access patterns, compressing legacy perimeter-tool replacement timelines.
- Infrastructure Security:Network segmentation validation and storage bucket exposure detection retain importance in Asia-Pacific manufacturing hubs. South Korean semiconductor fabs deploy these controls to protect intellectual property in multi-tenant cloud environments.
- Data Protection:Classification-aware misconfiguration prevention addresses GDPR and CCPA exposure risks.
- Application Security:CI/CD pipeline integration for infrastructure-as-code scanning shifts security left.
- Incident Response:Automated containment workflows for compromised cloud credentials reduce dwell time.
Infrastructure security holds the installed base. Identity and access management is gaining share fastest as zero-trust architectures dissolve network perimeters.
End User Industry:
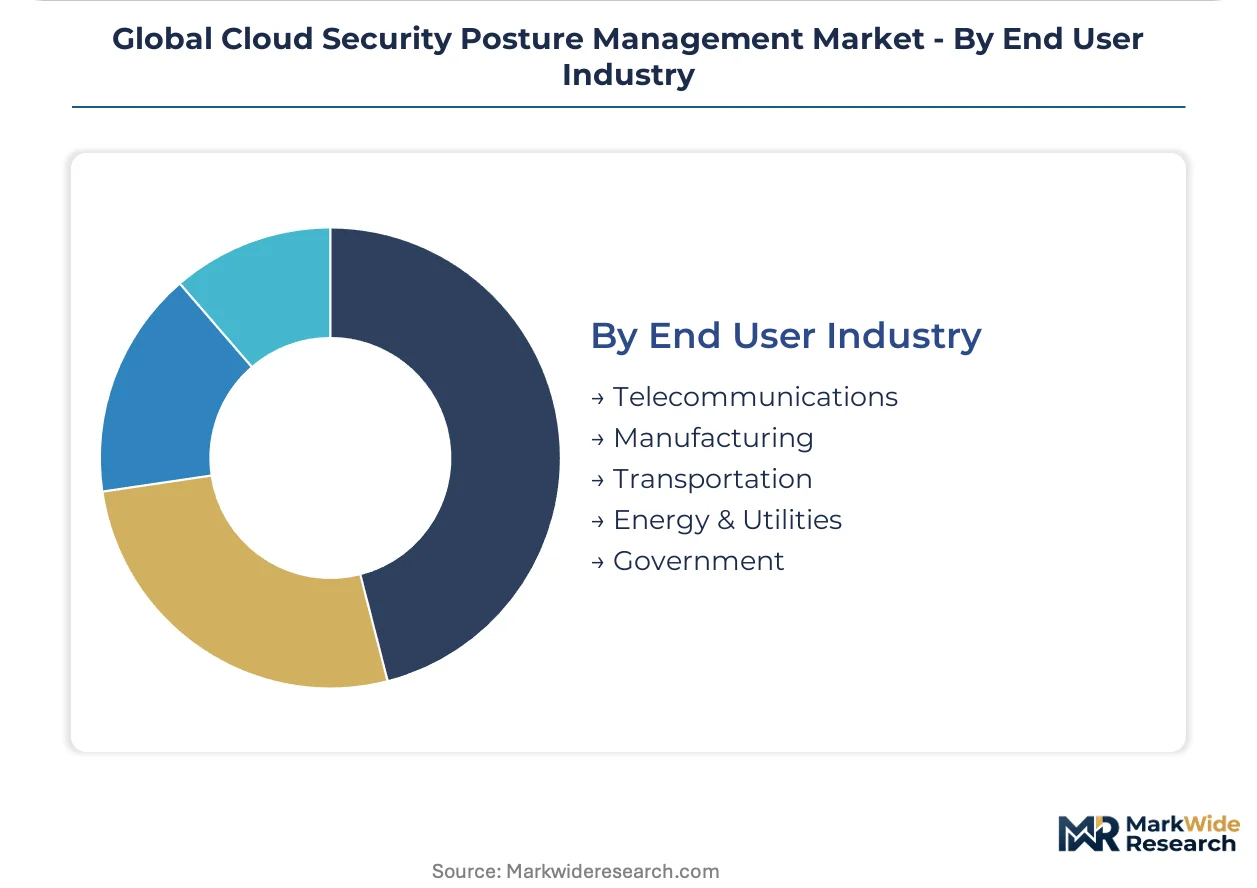
Regulated critical infrastructure operators outspend commercial sectors on assurance-depth premiums, reversing historical enterprise-IT leadership.
- Government:Federal, state, and municipal agencies across NATO member states mandate FedRAMP and equivalent certified posture management. United Kingdom Cabinet Office procurement frameworks and Canadian Shared Services Canada standardization drive concentrated vendor consolidation.
- Energy & Utilities:NIS2 Directive compliance and NERC CIP alignment force continuous monitoring of operational technology cloud gateways. Italian and Spanish grid operators expand CSPM scope to cover distributed renewable generation data pipelines.
- Telecommunications:5G network function virtualization and edge orchestration create attack surface complexity.
- Manufacturing:Industrial IoT convergence with cloud analytics platforms exposes legacy operational environments.
- Transportation:Autonomous vehicle data lakes and logistics platform security attract emerging procurement.
Government represents the deepest revenue pool. Energy and utilities is expanding most quickly as NIS2 enforcement deadlines approach.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States-based hyperscalers export cloud security infrastructure to European financial centers and Asian manufacturing hubs, establishing transatlantic and transpacific procurement corridors. Federal zero-trust mandates and SEC disclosure rules drive domestic demand concentration. German automotive and Japanese telecommunications sectors import multi-cloud governance frameworks.
United States
Federal contractors and hyperscaler concentration anchor CSPM procurement. NIST SP 800-53 mandates continuous monitoring for controlled unclassified information workloads. Greater Washington DC and Seattle-Tacoma technology corridors host defense integrators and cloud-native security engineering clusters.
Germany
Automotive manufacturers and industrial conglomerates demand unified visibility across AWS, Azure, and Google Cloud environments. EU NIS2 Directive enforcement deadlines accelerate procurement for energy grid operators. Stuttgart and Munich engineering centers deploy posture management across distributed supplier cloud gateways.
Japan
Telecommunications operators and semiconductor fabricators secure multi-tenant cloud infrastructure for intellectual property protection. METI cybersecurity guidelines emphasize continuous configuration assessment. Tokyo-Osaka technology corridor concentrates procurement for 5G network function virtualization.
United Kingdom
Financial services regulators under Bank of England supervision mandate demonstrable cloud control effectiveness. Cabinet Office procurement frameworks standardize FedRAMP-equivalent certification requirements. London fintech and Edinburgh banking clusters drive premium-tier risk assessment module adoption.
South Korea
Semiconductor manufacturers and electronics conglomerates secure cloud-based design collaboration platforms. MFDS-aligned critical infrastructure protections extend to cloud-hosted operational technology. Seoul Capital Area and Busan-Ulsan industrial zones concentrate manufacturing cloud security investment.
Global Cloud Security Posture Management Market Competitive Landscape
Listed leaders compete with private specialists across platform breadth versus configuration depth. The vendor base stratifies into three tiers: hyperscaler-native bundles, independent cybersecurity platforms, and vertical-focused specialists. Hyperscalers leverage infrastructure control for integrated posture management. Independent vendors compete on multi-cloud normalization and compliance depth. Consolidation pressure intensifies as security operations centers demand unified control planes over point-tool fragmentation.
Within the platform consolidation tier, Microsoft Corporation and Palo Alto Networks exemplify divergent strategies. Microsoft anchors posture management within broader Entra and Defender ecosystems, leveraging existing enterprise licensing relationships. Palo Alto Networks occupies a position emphasizing configuration management depth for high-assurance regulated buyers. Check Point Software Technologies Ltd. sits within the hybrid visibility archetype, bridging on-premise and AWS environments for organizations with legacy infrastructure investments.
| Leading Market Players |
|---|
| International Business Machines Corporation |
| Google LLC |
| Palo Alto Networks Inc. |
| Fortinet Inc. |
| Amazon Web Services Inc. |
| Check Point Software Technologies Ltd. |
| Oracle Corporation |
| Trend Micro Incorporated |
| Microsoft Corporation |
| Others |
Supply & Pricing Matrix
Hyperscaler infrastructure scale economies compress marginal delivery costs for posture management platforms, concentrating pricing power among AWS, Azure, and Google Cloud while forcing independent vendors toward premium configuration-depth positioning to defend margin floors.
Pricing Analysis
Next-generation agentless scanning architectures command pricing premiums over legacy agent-based deployments, while prior-generation configuration-only tools face cost compression from bundled hyperscaler offerings. The dominant pricing model runs through tiered SaaS subscriptions scaling by cloud resource count and compliance module depth. Price differentiation centers on FedRAMP certification tier and multi-cloud API normalization complexity. Pricing pressure stems from hyperscaler bundling of basic posture tools into enterprise agreements. Mid-market buyers exhibit highest price sensitivity, while regulated financial institutions accept assurance-depth premiums.
Supply Chain Analysis
Transpacific cable congestion and containerized software delivery latency elevate inbound distribution costs for European and Asia-Pacific deployments of US-originated platforms. Engineering talent concentrates in the United States, Israel, and Ireland, with Bangalore and Singapore emerging as delivery hubs. Raw material dependencies include cloud compute capacity from AWS, Azure, and Google Cloud, plus threat intelligence feeds from specialized cybersecurity vendors. Single-source vulnerability runs through hyperscaler API dependency. Distribution runs through direct enterprise sales with channel partner augmentation for mid-market segments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market sits in early-cycle expansion as NIS2 Directive enforcement deadlines and federal zero-trust mandates accelerate first-time buyer penetration beyond technology-forward adopters.
For Market Incumbents: Fortify configuration management depth against hyperscaler bundling by deepening Rego and Cedar policy engine investments. Anchor multi-cloud normalization capabilities as the priority lever to defend against emerging cloud-native specialists exploiting API fragmentation. Pursue FedRAMP High certification acceleration to maintain access to United States federal procurement corridors. For New Entrants and Emerging Players: Lead with EU AI Act Article 15 compliance automation as the wedge into high-risk AI system operators underserved by legacy configuration tools. Target Italian and Spanish energy grid operators facing NIS2 enforcement deadlines with managed security service provider partnerships. Build channel relationships with European system integrators possessing existing critical infrastructure operator access. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors multi-cloud normalization specialists over single-cloud point tools as platform consolidation accelerates. Five-to-ten year viability rests on graph-based asset inventory architecture and identity-centric posture evaluation capabilities. The signal to watch is hyperscaler acquisition of independent policy-engine startups as competitive blocking moves.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidates posture, workload, and entitlement management under unified control planes for federal zero-trust compliance. |
| Strategic Partnership | Aligns CSPM vendors with managed security service providers to capture mid-market outsourcing demand. |
| Acquisition of Specialist Firm | Absorbs graph-based asset inventory or identity-centric posture startups to fill architectural gaps. |
| Product Launch | Introduces EU AI Act-compliant monitoring modules for high-risk AI system operators in energy and telecommunications. |
| Geographic Expansion | Establishes delivery presence in Stuttgart and Munich engineering corridors for German automotive multi-cloud governance. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of SEC cybersecurity disclosures, hyperscaler capex filings, and NIST guidance documents. Primary interviews engaged chief information security officers, cloud platform engineers, federal procurement officers, and managed security service provider executives across the United States, Germany, Japan, and the United Kingdom. Secondary validation drew from FedRAMP authorization databases, EU NIS2 implementation trackers, and cloud provider API documentation. Bottom-up deployment estimates triangulated against top-down security software spending analysis.
Segmentation dimensions modeled encompass deployment architecture, solution type, use case, end-user industry, and regional regulatory framework across the projection horizon. CAGRs derived from elasticity-adjusted adoption curves calibrated to compliance deadline impacts and zero-trust mandate implementation timelines. Industry-specific forecast inputs include cloud resource growth trajectories and regulatory enforcement intensity indices.
The analysis sits within stated boundaries; outcomes outside sustained hyperscaler infrastructure investment and regulatory enforcement continuity would require recalibration. Forecasts reflect assumptions regarding NIS2 penalty implementation, SEC disclosure rule durability, and API rate limit evolution. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Switzerland Cybersecurity Market
Cybersecurity
Global Email Encryption Market
Cybersecurity
Enterprise Mobility Security Market
Cybersecurity
Data Protection Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Asia Pacific Data Exfiltration Market
Cybersecurity
SOC As a Service Market
Cybersecurity
Africa Cybersecurity Market
Cybersecurity
Saudi Arabia Cybersecurity Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Data Center Security Market