
 Data Protection Market | 2026-2036
Data Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Data Protection Market Intelligence
A capital-intensity divergence between cloud-native specialists and legacy infrastructure vendors is reorganizing competitive dynamics in data protection. Cisco anchors its position through integrated networking-security stacks that span enterprise campuses and cloud edge nodes. Varonis differentiates via deep metadata analytics for unstructured data governance across Microsoft and SaaS environments. IBM sustains relevance through mainframe-anchored encryption and long-tail backup services for regulated industries.
Data protection encompasses technical systems and processes that ensure confidentiality, integrity, and availability of digital information through encryption algorithms, access control frameworks, redundancy architectures, and recovery protocols. Its primary commercial purpose is to mitigate financial and operational losses from data breaches, system failures, and malicious attacks while maintaining regulatory compliance. Backup and Recovery solutions occupy the largest revenue pool as enterprises retain multi-year retention mandates, while Identity and Access Management segments are expanding fastest due to zero-trust architecture mandates. Cloud Security solutions command premium pricing as organizations migrate sensitive workloads to public and hybrid cloud deployments.
The EU AI Act, GDPR, and NIS2 Directive collectively reshape product requirements by mandating automated data classification, breach notification timelines, and supply-chain security attestations for vendors serving European enterprises. The US SEC cybersecurity disclosure rules and HIPAA enforcement actions similarly tighten accountability for publicly traded healthcare and financial entities. Stakeholders must monitor whether emerging quantum-resistant encryption standards will trigger premature replacement cycles for existing data-at-rest protection infrastructure.
Market Dynamics
Ransomware monetization through cryptocurrency settlement channels is forcing enterprises to rearchitect data protection around immutable backup architectures and air-gapped recovery protocols. Financial services and healthcare providers now treat ransomware resilience as a board-level operational risk metric rather than an IT hygiene exercise.
Growth Catalysts
- EU AI Act automated classification mandates:European enterprises must deploy machine-readable data labeling systems for high-risk AI training datasets, creating procurement pull for integrated governance platforms.
- Zero-trust architecture federal procurement:US government supply chain requirements under NIST SP 800-207 are cascading into defense contractor ecosystems and their commercial software vendors.
- Quantum-resistant encryption migration timelines:NIST's post-quantum cryptography standards are triggering premature replacement cycles for certificate authorities and hardware security module deployments.
Market Restraints
- Specialized cybersecurity talent scarcity:Shortages of incident response architects and forensics analysts in Germany, France, and the United Kingdom constrain implementation velocity for mid-market enterprises.
- Legacy mainframe integration complexity:Financial services institutions with IBM zSeries environments face extended validation timelines for modern backup agents, delaying cloud-hybrid deployments.
- Cross-border data localization friction:China's PIPL and Russia's data sovereignty requirements fragment unified protection architectures, forcing redundant infrastructure investments.
Strategic Opportunities
- India's Digital Personal Data Protection Act compliance:The 2023 framework mandates breach notification within 72 hours, creating first-mover advantage for vendors establishing localized data residency architectures.
- Convergence of confidential computing and homomorphic encryption:Hardware-based trusted execution environments combined with privacy-preserving analytics enable secure multi-party computation for healthcare consortiums.
- Managed detection and response channel expansion:Mid-market enterprises are outsourcing security operations to specialized service providers rather than building internal security operations centers.
Industry Challenges
- Fragmented endpoint agent proliferation:Enterprises average 15-20 distinct security agents per workstation, creating compatibility conflicts and coverage gaps during vendor consolidation.
- Recovery time objective compression:Board-level pressure to reduce ransomware recovery windows from days to hours demands expensive synchronous replication investments that strain capital allocation.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Data Protection Market |
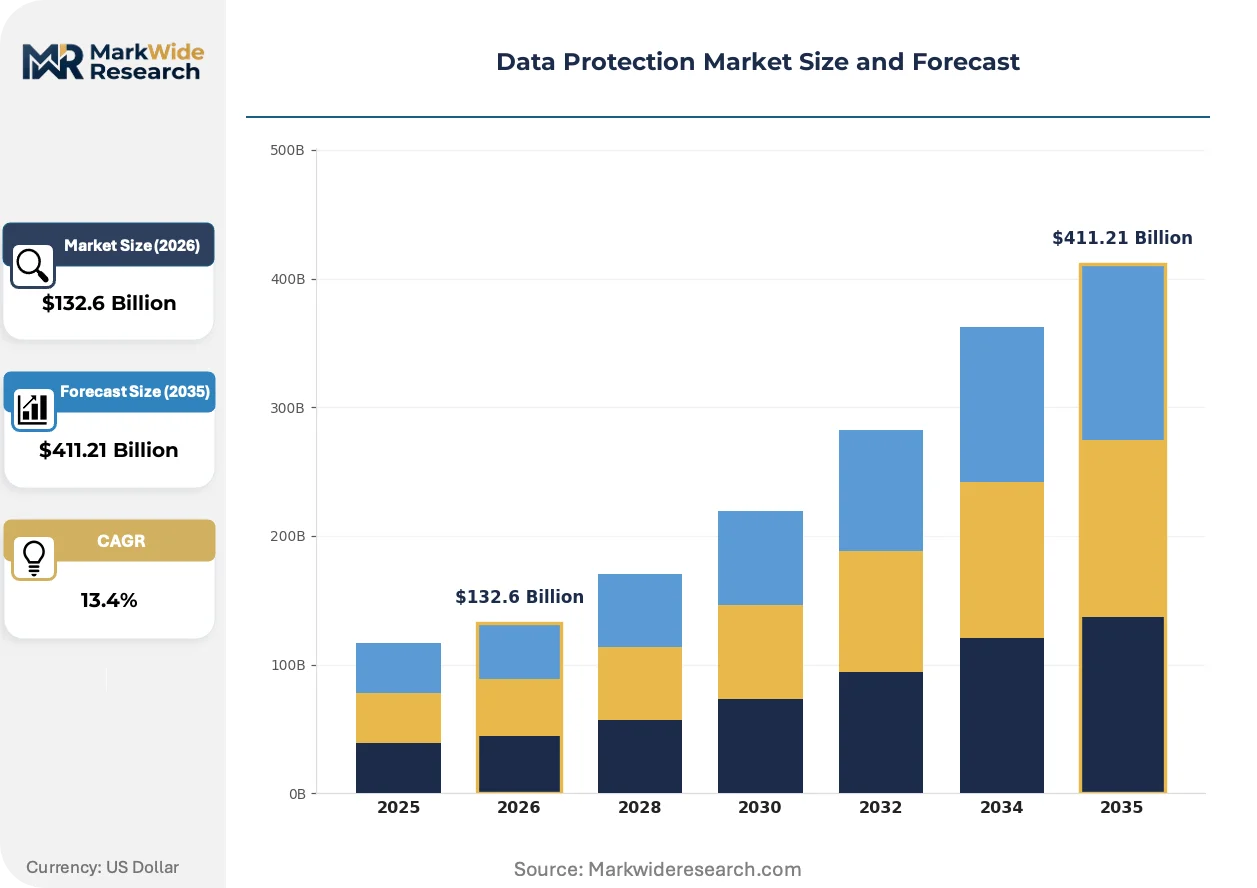
| Market Size in 2026 | $132.6 Billion |
| Market Size in 2035 | $411.21 Billion |
| CAGR (2026 – 2036) | 13.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Backup and Recovery, Data Encryption, Identity and Access Management, Data Loss Prevention, Cloud Security, Tokenization Deployment: On-Premises, Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud, Edge Computing Application: Financial Services, Retail Chains, Telecommunication Providers, Government Agencies, Education Institutions, Energy Companies End User: Small and Medium Enterprises, Large Corporations, Managed Service Providers, System Integrators, Data Centers, Software Vendors |
| Companies Covered | Cisco, Varonis, IBM, BigID, Cyera, Microsoft, Commvault, Immuta, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Data Protection Market Strategic Shifts & Innovations
Immutable storage architectures are rewriting recovery assumptions by eliminating administrative override capabilities that ransomware operators have systematically exploited. This technical shift is compressing vendor differentiation around hardware-rooted trust mechanisms rather than software-only protections.
Object-locking storage protocols with WORM (Write Once Read Many) enforcement are displacing traditional backup retention policies that relied on access control lists and administrative discretion. Healthcare providers and financial institutions are adopting these architectures fastest, driven by HIPAA and SEC cybersecurity disclosure requirements. The structural consequence is displacing incumbent backup vendors whose software stacks lack hardware-integrated immutability guarantees, forcing partnerships with specialized storage hardware manufacturers.
The EU AI Act's risk classification framework for training data governance is mandating automated provenance tracking and audit trail preservation across machine learning pipelines. Industrial consequence includes mandatory technical documentation for high-risk AI systems that must demonstrate data quality management and bias mitigation controls. Medical device manufacturers and automated credit scoring providers face the steepest compliance burden, responding by embedding data lineage tools directly into MLOps workflows rather than treating governance as a post-hoc audit function.
Consolidated security procurement through managed service providers is replacing direct enterprise licensing for point solutions in the mid-market segment. European manufacturing firms and US municipal governments are channeling security spending through regional MSPs who aggregate multiple vendor capabilities into unified service tiers. This pattern is most visible in Germany's Mittelstand sector, where family-owned enterprises lack internal security expertise and prefer outcome-based contracts with defined recovery guarantees over technology ownership.
Data Protection Market Segmentation
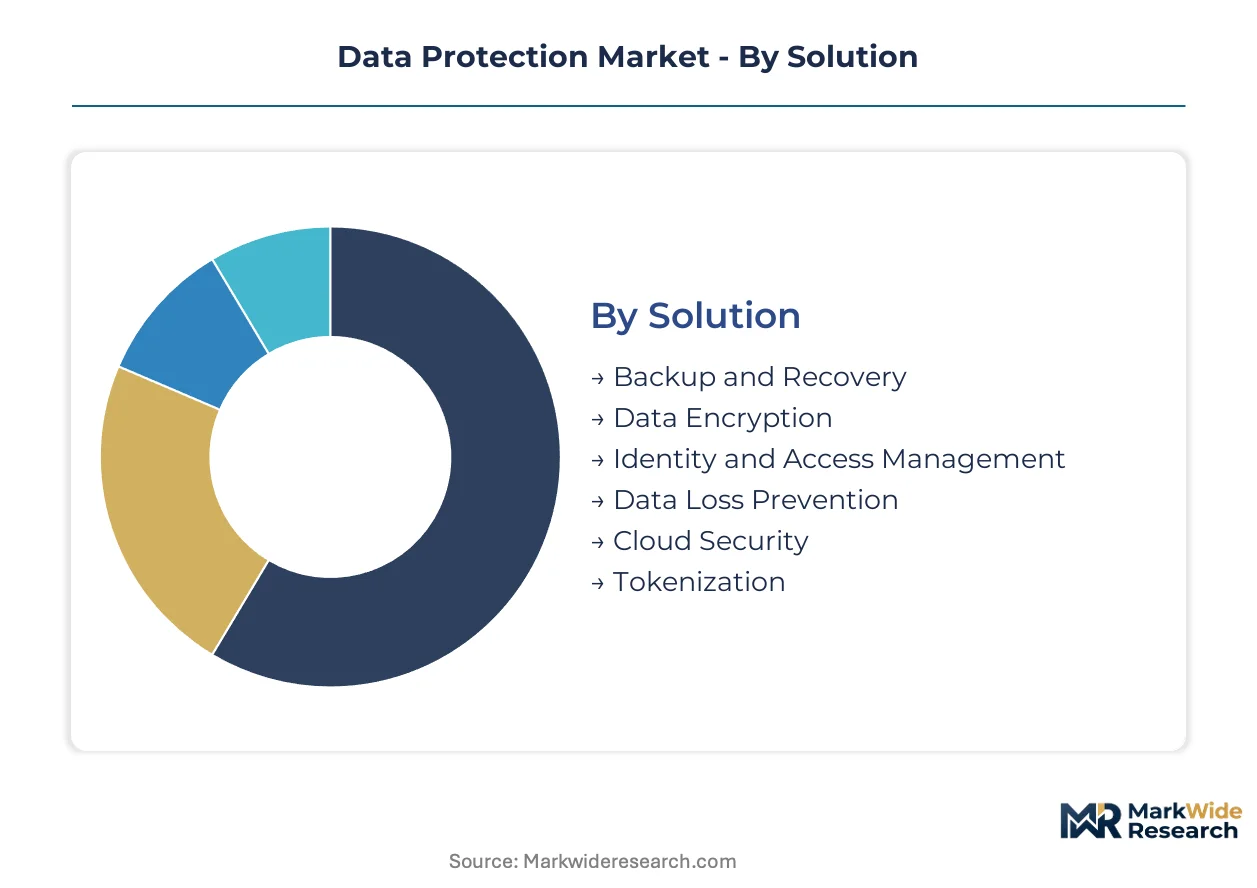
Data protection procurement patterns diverge sharply across solution types and deployment architectures, with regulatory mandates and ransomware exposure reshaping how enterprises allocate security budgets across technical layers.
Solution:
Backup and Recovery faces intensifying substitution pressure from immutable storage architectures that displace traditional software-only retention policies.
- Backup and Recovery:Multi-year retention mandates and air-gapped recovery protocols define this segment's technical specifications. Financial services firms in Germany and France concentrate procurement here, driven by SEC cybersecurity disclosure rules and GDPR enforcement timelines that demand demonstrable restoration capabilities.
- Data Encryption:Algorithmic protection for data-at-rest and data-in-transit using AES-256 and emerging post-quantum standards. Healthcare providers across the United Kingdom are upgrading certificate authorities and hardware security modules ahead of NIST migration timelines.
- Identity and Access Management:Zero-trust architecture mandates from US federal procurement are cascading into defense contractor ecosystems.
- Data Loss Prevention:Content inspection and egress monitoring tools that enforce policy across endpoint and cloud channels.
- Cloud Security:Premium-priced solutions for public and hybrid workload protection command vendor attention.
- Tokenization:Format-preserving substitution methods that reduce PCI-DSS scope for payment data environments.
Backup and Recovery anchors the volume base while Cloud Security gains share at the steepest rate.
Deployment:
Cost tier differentiation separates capital-intensive on-premises estates from consumption-priced cloud alternatives.
- On-Premises:Dedicated infrastructure requiring physical hardware ownership and facility security controls. IBM zSeries environments in regulated industries face extended validation timelines that delay modernization.
- Public Cloud:Shared-tenant infrastructure with metered consumption and native encryption services. European enterprises concentrate spending here, navigating GDPR data residency requirements through region-locked storage tiers.
- Private Cloud:Single-tenant virtualized environments delivering cloud agility with dedicated resource isolation.
- Hybrid Cloud:Orchestrated workloads spanning on-premises and cloud infrastructure with unified policy enforcement.
- Multi-Cloud:Distributed architectures across AWS, Azure, and Google Cloud requiring cross-platform consistency tools.
- Edge Computing:Distributed processing nodes that protect IoT-generated data before central aggregation.
On-Premises retains the largest installed base though Hybrid Cloud is climbing the fastest as enterprises reconcile legacy mainframe estates with cloud-native workloads.
Application:
Volume concentration tracks ransomware exposure severity, with financial and healthcare targets commanding premium protection spending.
- Financial Services:Trading systems, customer records, and transaction logs protected under PCI-DSS and SEC disclosure regimes. Board-level operational risk metrics in Germany and the United Kingdom are expanding budgets for immutable backup architectures.
- Retail Chains:Point-of-sale systems, e-commerce platforms, and loyalty databases requiring PCI-compliant tokenization. European merchants face GDPR Article 33 breach notification timelines that compress recovery objective windows.
- Telecommunication Providers:Subscriber data and network infrastructure subject to national security attestation requirements.
- Government Agencies:Classified and citizen data protected under country-specific sovereignty mandates.
- Education Institutions:Student records and research data with constrained IT security staffing.
- Energy Companies:Operational technology networks and smart grid data requiring IEC 62351 compliance.
Financial Services anchors the revenue base while Retail Chains are expanding most quickly as omnichannel payment fraud escalates protection requirements.
End User:
Customer type determines procurement channel, with internal capability gaps driving outsourcing to specialized service providers.
- Small and Medium Enterprises:Resource-constrained organizations averaging 15-20 security agents per workstation. Germany's Mittelstand sector channels spending through regional MSPs, preferring outcome-based contracts with defined recovery guarantees.
- Large Corporations:Complex multi-site environments with dedicated security operations centers and vendor consolidation programs. France-based multinationals are centralizing procurement around integrated networking-security stacks.
- Managed Service Providers:Regional aggregators delivering unified service tiers to mid-market clients lacking internal expertise.
- System Integrators:Professional services firms embedding protection into digital transformation projects.
- Data Centers:Colocation and hyperscale facilities offering protection-as-a-service to tenant workloads.
- Software Vendors:Application publishers embedding encryption and access controls into product offerings.
Large Corporations dominate direct licensing volume while Managed Service Providers are capturing share fastest as mid-market outsourcing accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Price sensitivity varies sharply across national markets. German and French enterprises absorb premium pricing for immutable backup architectures, while India's mid-market segment prioritizes cost-efficient managed service bundles over capital-intensive on-premises deployments.
Germany
Financial services firms in Frankfurt and Munich drive demand for air-gapped recovery protocols following BaFin enforcement actions on ransomware resilience. The EU AI Act's automated classification mandates compel machine-readable data labeling investments. Bavaria's Mittelstand sector channels procurement through regional MSPs, preferring outcome-based contracts with defined recovery guarantees over direct technology ownership.
France
Healthcare providers in Paris and Lyon upgrade hardware security modules ahead of NIST post-quantum cryptography timelines. CNIL guidance on GDPR breach notification compresses recovery objective windows to under 72 hours. The Île-de-France region concentrates procurement for integrated networking-security stacks as multinationals centralize European security operations.
United Kingdom
NHS trusts and London-based trading platforms invest in synchronous replication to meet SEC cybersecurity disclosure requirements for UK-listed entities. The Information Commissioner's Office intensifies enforcement on cross-border data flows post-Brexit. Scotland's financial services cluster in Edinburgh adopts confidential computing architectures for healthcare consortium data sharing.
United States
Federal zero-trust mandates under NIST SP 800-207 cascade through defense contractor supply chains into commercial software procurement. The SEC's cybersecurity disclosure rules tighten accountability for publicly traded healthcare and financial entities. Northern Virginia's data center corridor sees concentrated investment in region-locked storage tiers serving European enterprise workloads.
India
The 2023 Digital Personal Data Protection Act mandates 72-hour breach notification, accelerating localized data residency architecture deployments. Mumbai's financial services sector and Bangalore's SaaS exporters represent the steepest compliance-driven procurement curves. Gujarat's manufacturing hubs outsource security operations to specialized service providers rather than building internal capabilities.
Data Protection Market Key Industry Players
A small set of integrated leaders sits above a broader specialist tier in data protection. Cisco anchors its position through unified networking-security stacks spanning enterprise campuses and cloud edge nodes. Varonis and BigID occupy the metadata analytics specialist tier, differentiating via deep governance capabilities across Microsoft and SaaS environments. IBM sustains relevance through mainframe-anchored encryption services for regulated industries. Competitive moves concentrate on strategic partnerships with storage hardware manufacturers and managed detection and response channel expansion.
Among integrated platform vendors, Cisco exemplifies the converged infrastructure archetype, while Varonis represents pure-play metadata governance specialization. IBM occupies a distinctive position serving legacy mainframe estates with long-tail backup services. These three anchors illustrate how capital-intensity divergence between cloud-native specialists and legacy infrastructure vendors reorganizes competitive dynamics across European and North American procurement markets.
| Leading Market Players |
|---|
| Cisco |
| Varonis |
| IBM |
| BigID |
| Cyera |
| Microsoft |
| Commvault |
| Immuta |
| Palo Alto Networks |
| Others |
Cost & Logistics Intelligence
Immutable storage hardware displacing software-only backup agents is redrawing supplier geography toward Taiwan and South Korea while compressing margins for legacy vendors dependent on recurring license streams.
Pricing Analysis
Managed detection and response service contracts now generate lifetime value multiples exceeding perpetual licenses. Three-tier pricing structure across premium, standard, and economy levels stratifies by recovery guarantee SLAs and data residency certification. Pricing pressure stems from mid-market enterprises consolidating 15-20 endpoint agents into unified MSP bundles. Large financial institutions in Frankfurt and London absorb premium immutable storage pricing, while India's manufacturing hubs prioritize cost-efficient outcome-based contracts.
Supply Chain Analysis
Hardware security module inventory cycles stretch 12-16 weeks as NIST post-quantum cryptography migration accelerates demand. Taiwan, South Korea, and the United States concentrate semiconductor fabrication for trusted execution environments. Supply chains draw from specialized NAND flash foundries, cryptographic processor IP, and certified firmware stacks. Single-source vulnerability in hardware-rooted trust anchor manufacturing elevates procurement risk. Distribution runs through hyperscaler marketplaces and regional MSP aggregators serving Germany's Mittelstand sector.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Data protection is shifting toward platform economics where Cisco's networking-security stack interoperability and Microsoft SaaS-native governance tools create winner-take-most dynamics.
For Market Incumbents: Secure immutable storage hardware partnerships before Taiwanese and South Korean suppliers allocate capacity to cloud-native entrants. Deepen backward integration into cryptographic processor design to offset post-quantum certification cost inflation. Consolidate channel position through exclusive MSP tiering in France and Germany where family-owned enterprises lack internal security expertise. For New Entrants and Emerging Players: Anchor in India's Digital Personal Data Protection Act compliance window before incumbent vendors establish localized data residency architectures. Target healthcare consortiums in Scotland and the Île-de-France region seeking confidential computing for multi-party analytics. Lead with open-source data lineage tools embeddable into MLOps workflows rather than standalone governance platforms. For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed metadata analytics specialists holding Microsoft 365 and Salesforce integration depth but lacking hardware-rooted trust capabilities. Five-to-ten year viability hinges on quantum-resistant encryption migration timing. Watch NIST standard finalization as the inflection signal triggering premature replacement cycles and vendor consolidation.| Strategic Initiative | Industry Significance |
|---|---|
| Immutable Storage Hardware Partnership | Taiwanese and South Korean suppliers allocate capacity to vendors with air-gapped recovery architectures first. |
| Post-Quantum Cryptography Certification | NIST-compliant hardware security modules displace legacy encryption for financial services in Frankfurt and London. |
| Managed Detection and Response Channel Expansion | Germany's Mittelstand sector channels procurement through regional MSPs preferring outcome-based contracts. |
| Confidential Computing Platform Integration | Healthcare consortiums in Scotland adopt hardware-based trusted execution environments for multi-party analytics. |
| Data Lineage Tool Embedding | Medical device manufacturers integrate governance directly into MLOps workflows under EU AI Act mandates. |
Research Approach
Operator-level perspectives from CISOs, cloud infrastructure architects, MSP service directors, and hardware security module procurement leads anchored the qualitative base. Primary fieldwork combined with secondary validation against SEC cybersecurity disclosure filings, EU AI Act technical documentation requirements, GDPR enforcement action records, and hyperscaler capex disclosures for encryption services. Bottom-up segment sizing triangulated against top-down macroeconomic indicators across the analysis window.
Sensitivity analysis tested forecast robustness against quantum-resistant encryption migration acceleration, MSP channel consolidation velocity, and regulatory enforcement intensity variations. Segmentation modeled deployment architecture, solution type, end-use vertical, organization scale, and regional regulatory cluster complexity. CAGRs derived from installed base replacement cycles, net new workload protection demand, and pricing trajectory assumptions for cloud-native versus legacy delivery models.
Material uncertainties — NIST standard finalization timelines, EU AI Act delegated act specifications, and cross-border data localization enforcement shifts — sit outside the modeled envelope. Forecasts reflect assumptions about ransomware monetization persistence and federal zero-trust procurement cascade velocity. Revision becomes warranted when post-quantum cryptography hardware deployment crosses 30% of addressable base thresholds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Threat Intelligence Market
Cybersecurity
Global Zero-Trust Security Market
Cybersecurity
Cyber Security Market
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Global Healthcare IoT Security Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Data Center Security Market