
 Global Network Security Policy Management Market | 2026-2036
Global Network Security Policy Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Network Security Policy Management Market Intelligence
The expansion of managed services is rebalancing the value proposition from one-time product sales to recurring revenue models. Palo Alto Networks, Inc. leverages its integrated platform to capture this shift in enterprise spending. Check Point Software Technologies Ltd. competes through its focus on unified security management for hybrid data centers and cloud workloads. Meanwhile, Cisco Systems extends its vast networking hardware footprint with embedded security policy solutions to secure its installed base.
Network security policy management involves software platforms that automate the creation, auditing, and enforcement of security rules across firewalls, routers, and switches. These systems provide a centralized view for managing thousands of complex policies, ensuring consistent application and preventing critical misconfigurations. Within solution offerings, firewall management remains the foundational component, while compliance monitoring tools generate significant demand due to regulatory pressures. Cloud-based deployment models are showing the most rapid uptake, displacing traditional on-premises solutions in new enterprise accounts.
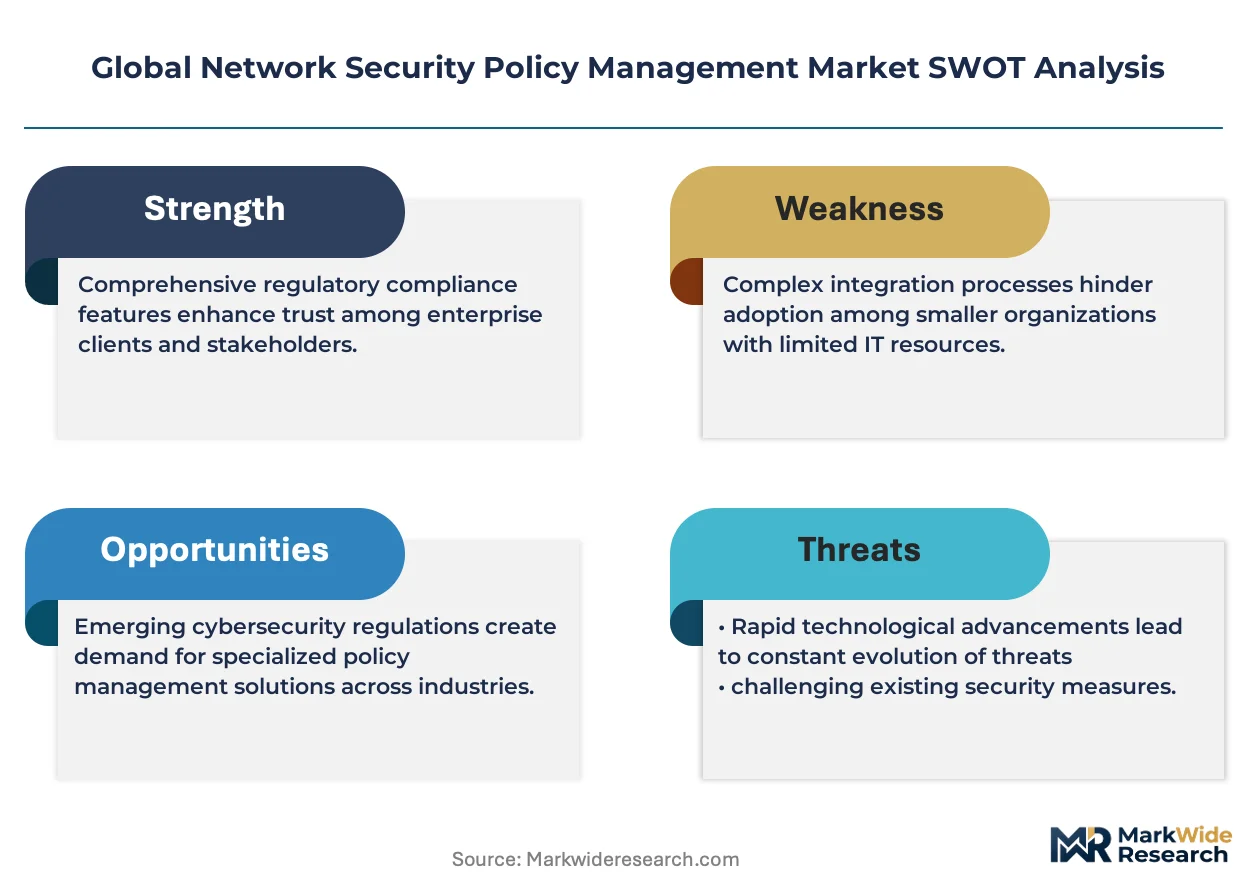
Regulatory frameworks such as the EU's GDPR and the US's HIPAA mandate stringent access controls and audit trails, directly driving solution adoption. In China, compliance with national data security laws requires organizations to implement verifiable policy enforcement mechanisms for cross-border data flows. Stakeholder success depends on their ability to integrate policy management with emerging security orchestration, automation, and response (SOAR) platforms to accelerate incident response times.
Market Dynamics
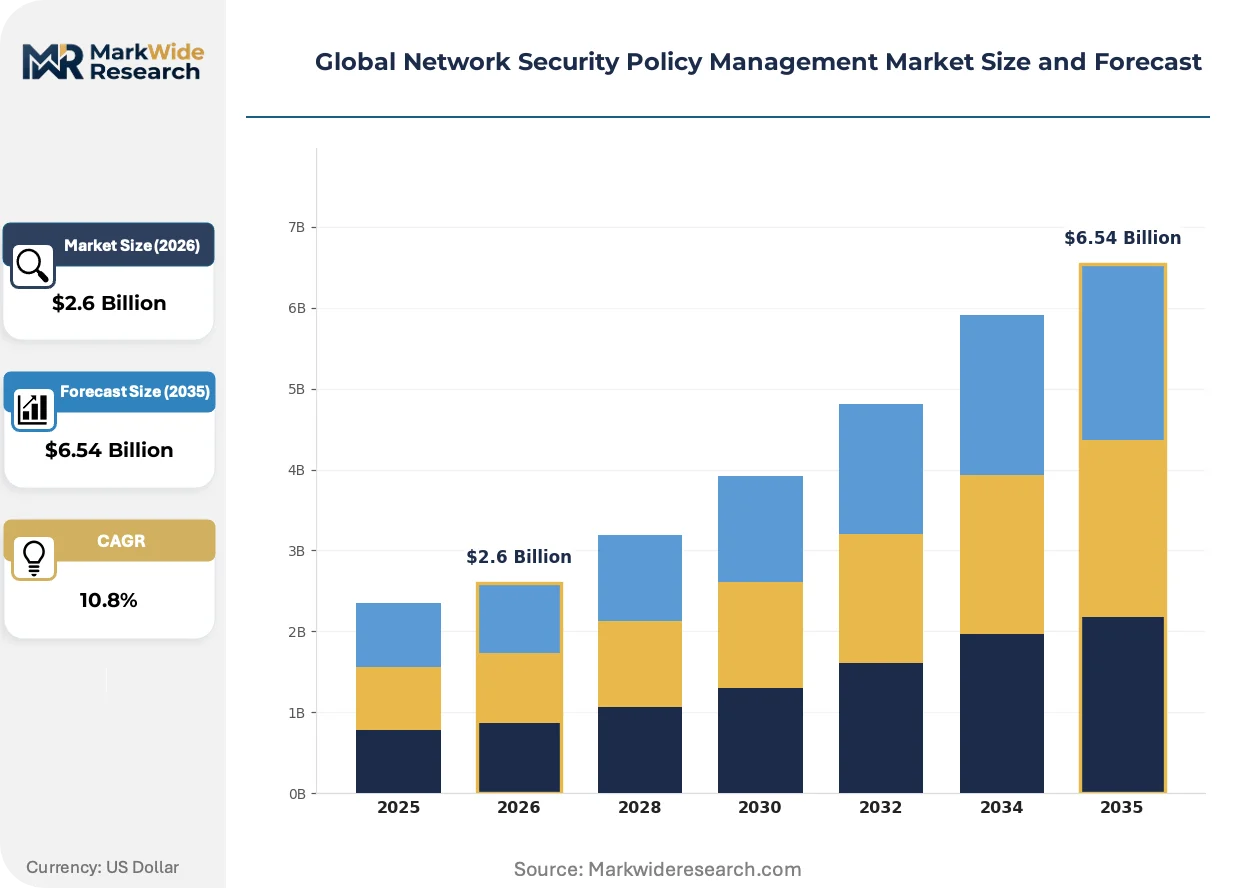
The central dynamic shaping the network security policy management market is the convergence of automation with stringent regulatory compliance. This is driven by the need to secure increasingly complex, multi-cloud environments while providing auditable proof of policy enforcement to authorities like those overseeing GDPR and HIPAA.
Growth Catalysts
- Regulatory Mandates:Stringent data privacy laws, including the EU's GDPR and the US's HIPAA, compel organizations to implement robust policy management for access control and auditability, directly fueling solution adoption in healthcare and finance.
- Hybrid Cloud Complexity:The proliferation of complex hybrid and multi-cloud architectures within large enterprises creates thousands of policy rules, making automated management platforms essential for preventing security gaps and misconfigurations.
- Zero Trust Architecture:The strategic shift by enterprises towards Zero Trust security models, which operate on the principle of "never trust, always verify," necessitates granular, dynamic, and centrally managed policy enforcement across all network segments.
Market Restraints
- High Implementation Costs:The substantial initial capital outlay for advanced policy management platforms, combined with the costs of integration and personnel training, can be a significant barrier for small and medium-sized enterprises.
- Legacy System Integration:The inherent difficulty and technical complexity of integrating modern policy management solutions with aging, heterogeneous network infrastructure from multiple vendors can delay or stall adoption projects.
- Open-Source Alternatives:The availability of functional open-source tools and native security controls within public cloud platforms like AWS and Azure presents a viable, lower-cost alternative for organizations with strong internal technical expertise.
Strategic Opportunities
- SOAR Platform Integration:Deepening integration with Security Orchestration, Automation, and Response (SOAR) platforms offers a significant opportunity to link policy auditing directly to automated incident response workflows, reducing mean time to resolution.
- Securing OT/IoT Environments:Extending policy management capabilities to secure converging Information Technology (IT) and Operational Technology (OT) networks in manufacturing and utilities represents a major growth vector.
- Emerging Economies:Market penetration in regions like Southeast Asia and Latin America, where rapid digitalization and new data protection laws are creating greenfield demand for centralized security controls, presents a key opportunity.
Industry Challenges
- Cybersecurity Skills Gap:A persistent shortage of security professionals with the specialized expertise to design, manage, and optimize complex network security policies across multi-vendor environments constrains effective solution deployment.
- Multi-Vendor Interoperability:Ensuring consistent policy application and seamless interoperability in environments with a diverse mix of firewalls, routers, and cloud platforms from different vendors remains a significant operational challenge.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Network Security Policy Management Market |
| Market Size in 2026 | $2.6 Billion |
| Market Size in 2035 | $6.54 Billion |
| CAGR (2026 – 2036) | 10.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Solution Offering: Firewall Management, Intrusion Prevention, Access Control, Compliance Monitoring, Risk Assessment Use Case: Threat Detection, Policy Enforcement, Network Mapping, Incident Response, Data Leakage Prevention End User Type: Telecommunication Providers, Government Agencies, Financial Institutions, Educational Organizations |
| Companies Covered | Palo Alto Networks, Inc., Check Point Software Technologies Ltd., AlgoSec Inc., Tufin Software Technologies Ltd., FireMon, LLC., Cisco Systems, Fortinet, IBM Corporation, Forcepoint LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Network Security Policy Management Market Strategic Shifts & Innovations
Automation and artificial intelligence are transforming network security policy management from a reactive, rule-auditing function into a proactive, predictive discipline. This evolution is driven by the need to manage security posture at machine speed across distributed, ephemeral cloud infrastructure.
AI-Powered Policy Optimization
Machine learning algorithms analyze network traffic and existing rules to identify redundant, shadowed, or overly permissive policies. Financial services and healthcare organizations are key adopters, using these tools to reduce their attack surface and simplify compliance audits. This AI-driven capability is expanding into predictive policy analysis, enabling security teams to model the impact of rule changes on security and connectivity before deployment.
Data Residency and Sovereignty Compliance
China's national data security framework, including the Personal Information Protection Law (PIPL), imposes strict requirements on the cross-border transfer and processing of data. These regulations compel multinational corporations to implement verifiable policy enforcement mechanisms to govern data flows and demonstrate compliance. The financial and technology sectors are most affected, redesigning network architectures to align with data localization mandates.
Shift to Managed and Subscription Services
A distinct pivot from perpetual software licensing toward subscription-based consumption and fully managed security policy services is underway. This model displaces large, upfront capital expenditures with predictable operational spending, appealing to organizations that lack deep in-house security expertise. The trend is most visible among mid-sized enterprises in developed economies like the United States and Germany.
Global Network Security Policy Management Market Segmentation
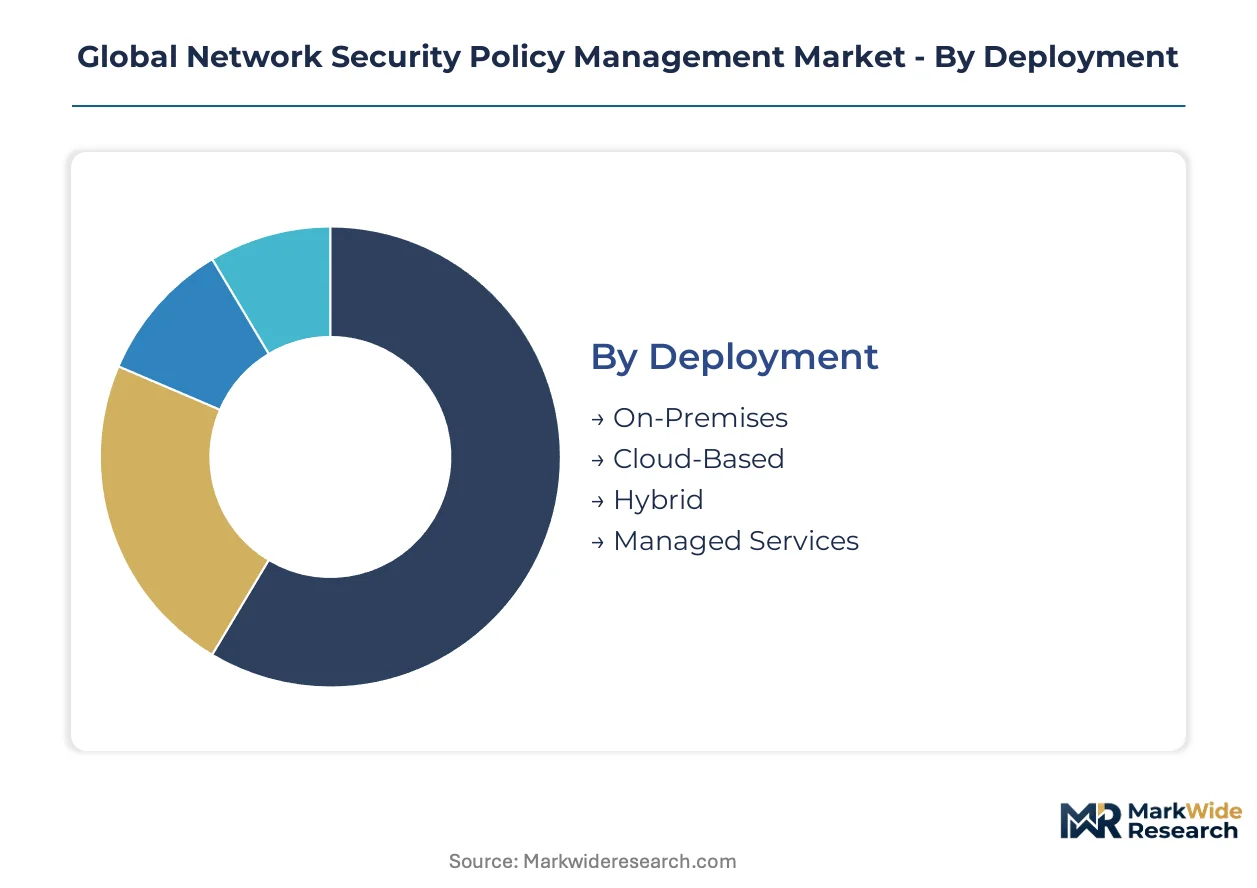
The network security policy management market segmentation reflects diverse operational needs and technological preferences across organizations. This granular breakdown enables a comprehensive understanding of how different solutions and deployment models address specific security challenges. The market's structure is influenced by factors like infrastructure complexity and stringent regulatory compliance demands.
Deployment:
The upgrade and replacement cycles for network security infrastructure significantly influence the uptake of new deployment models.
- Cloud-Based:These solutions leverage public or private cloud infrastructure for policy management, offering scalability and reduced operational overhead. Rapid uptake is observed in new enterprise accounts, displacing traditional on-premises solutions due to agility requirements.
- Managed Services:External providers assume responsibility for policy design, implementation, and ongoing management, appealing to organizations lacking deep in-house security expertise. This model is gaining traction among mid-sized enterprises in developed economies like the United States and Germany, shifting spending from CAPEX to OPEX.
- On-Premises:Policy management software is installed and run on local servers within an organization's own data center, offering full control over data.
- Hybrid:This model combines elements of both on-premises and cloud-based deployments, providing flexibility for organizations with mixed infrastructure.
On-Premises sits at the top of the volume ranking, with Managed Services climbing the fastest.
Solution Offering:
The application of policy management solutions varies widely depending on an organization's specific security priorities and infrastructure.
- Firewall Management:This foundational component automates the creation, auditing, and enforcement of security rules across various firewall types. It ensures consistent application of policies and prevents critical misconfigurations, especially in large, distributed networks.
- Compliance Monitoring:Tools within this offering continuously assess network configurations and access controls against regulatory standards like GDPR and HIPAA. Demand is significant in financial services and healthcare, where stringent audit trails and verifiable enforcement are mandated.
- Intrusion Prevention:Solutions that detect and block malicious network traffic based on predefined security policies and threat intelligence.
- Access Control:Systems that manage and enforce user and device permissions to network resources, ensuring least privilege principles are applied.
- Risk Assessment:Tools that identify vulnerabilities and evaluate potential security risks within the network infrastructure, informing policy adjustments.
Demand for Firewall Management solutions is particularly strong, while Compliance Monitoring is expanding most quickly.
Use Case:
Customer type and their operational environment dictate the primary use cases for network security policy management platforms.
- Policy Enforcement:This core function ensures that security rules are consistently applied across all network devices and cloud environments. It is crucial for maintaining a strong security posture and preventing unauthorized access or data flows, especially in multi-cloud architectures.
- Incident Response:Policy management tools contribute to faster incident resolution by providing clear visibility into policy violations and accelerating automated remediation actions. Integration with SOAR platforms is a significant opportunity to link policy auditing directly to response workflows.
- Threat Detection:Utilizing policy data to identify anomalous network behavior and potential security threats in real-time.
- Network Mapping:Visualizing network topology and data flows to understand the impact of policy changes and identify security gaps.
- Data Leakage Prevention:Implementing policies to prevent sensitive information from leaving the organization's controlled network boundaries.
Organizations prioritize Policy Enforcement for immediate threats, with Incident Response gaining significant traction for proactive security.
End User Type:
The maturity of cybersecurity practices and regulatory landscapes among different end-user types drives distinct requirements for policy management.
- Financial Institutions:These organizations require robust policy management to secure complex hybrid cloud environments and comply with stringent data privacy regulations. Their high cybersecurity investment reflects the critical nature of financial data and transactional integrity.
- Telecommunication Providers:Managing vast, distributed networks with numerous interconnected devices necessitates sophisticated policy enforcement mechanisms. They focus on maintaining service availability and securing critical infrastructure against advanced threats.
- Government Agencies:These entities implement policy management for national security, citizen data protection, and compliance with government-specific cybersecurity mandates.
- Educational Organizations:Solutions are deployed to secure academic networks, protect student and faculty data, and manage access across diverse user groups.
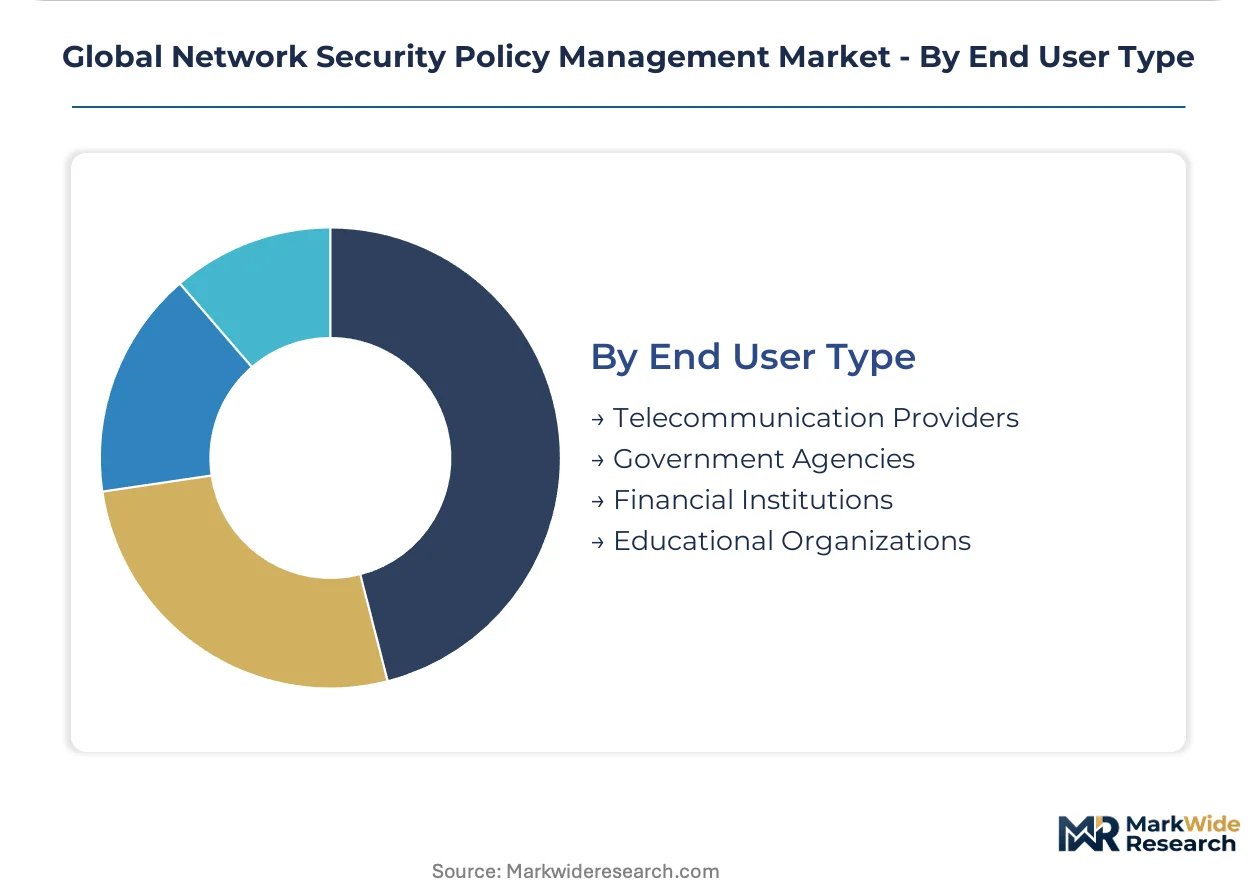
Financial Institutions consistently drive substantial investment, and Telecommunication Providers are demonstrating robust expansion.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States consistently demonstrates higher investment in cybersecurity solutions compared to Germany, yet both nations exhibit strong demand for network security policy management. Developed economies, driven by digital transformation and stringent regulatory frameworks, lead the adoption curve for sophisticated policy enforcement tools. Emerging markets are also beginning to implement similar solutions as their digital infrastructures mature and data protection laws evolve.
United States
Enterprises in the United States require robust policy management to secure complex hybrid cloud environments and comply with federal mandates. The Health Insurance Portability and Accountability Act (HIPAA) compels healthcare organizations to maintain stringent access controls and audit trails. Technology hubs across Silicon Valley and major financial centers like New York City drive innovation and early adoption of advanced security orchestration platforms.
Germany
German organizations prioritize network security policy management for compliance with the General Data Protection Regulation (GDPR) and to protect critical industrial data. The shift towards managed services is particularly pronounced among mid-sized enterprises in Germany, seeking to offload operational complexities. Major financial institutions in Frankfurt and manufacturing firms in Bavaria are key adopters, ensuring verifiable policy enforcement.
China
China's national data security framework, including the Personal Information Protection Law (PIPL), mandates verifiable policy enforcement mechanisms for cross-border data flows. Organizations operating in China must redesign network architectures to align with data localization requirements. Technology and financial sectors in cities like Shanghai and Beijing are rapidly implementing solutions to meet these stringent national data security laws.
United Kingdom
The United Kingdom's financial services sector drives significant demand for network security policy management, ensuring compliance with UK GDPR and other financial regulations. Organizations seek solutions that provide granular access controls and comprehensive audit capabilities across distributed networks. London, as a global financial and technology hub, sees substantial investment in integrated security platforms to manage complex policy rules.
Japan
Digitalization initiatives across various sectors in Japan are fueling the need for advanced network security policy management to protect sensitive data. The Act on the Protection of Personal Information (APPI) necessitates robust policy enforcement for data privacy and security. Tokyo's dense concentration of technology companies and manufacturing giants actively implements policy management to secure their expanding digital footprints.
Global Network Security Policy Management Market Key Industry Players
Top-tier vendors anchor comprehensive platform solutions, while specialized providers focus on niche policy management needs. The market exhibits a tiered structure with integrated security suites and networking hardware extensions forming distinct archetypes. Companies pursue strategic partnerships for SOAR integration and portfolio diversification into OT/IoT environments.
On the premium-tier vector, Palo Alto Networks, Inc. exemplifies integrated platform approaches, offering broad security management capabilities. Check Point Software Technologies Ltd. occupies a position among unified security management specialists, particularly for hybrid data centers and cloud workloads. Cisco Systems, Inc. represents established networking hardware providers extending their vast footprint with embedded security policy solutions.
| Leading Market Players |
|---|
| Palo Alto Networks, Inc. |
| Check Point Software Technologies Ltd. |
| AlgoSec Inc. |
| Tufin Software Technologies Ltd. |
| FireMon, LLC. |
| Cisco Systems |
| Fortinet |
| IBM Corporation |
| Forcepoint LLC |
| Others |
Cost & Logistics Intelligence
The global index for cloud infrastructure services, while not a direct commodity, influences the total cost of ownership for network security policy management. This cost cascades through vendor pricing models, affecting subscription tiers and managed service offerings.
Pricing Analysis
Capacity additions in major cloud regions are reshaping price floors for cloud-based network security policy management solutions. The dominant pricing model is subscription-based, often tiered by network size, policy count, or feature set. Customization level and after-sales service quality drive significant price differentiation for specialized deployments. Pricing softness stems from the availability of functional open-source alternatives and native cloud security controls. Small and medium-sized enterprises exhibit the highest price sensitivity, while large financial institutions prioritize comprehensive features over cost.
Supply Chain Analysis
Rigorous certification and qualification processes for cybersecurity software vendors are crucial gates in the network security policy management supply chain. Geographic supply concentration for core development talent centers on the United States, Germany, and Israel. The market relies heavily on skilled cybersecurity talent and robust cloud infrastructure services as key inputs. A persistent cybersecurity skills gap represents a significant structural risk across the entire supply chain. Distribution primarily runs through managed services providers and direct sales channels to large enterprises.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The network security policy management market offers a margin-expansion story, driven by the shift towards subscription-based cloud services. This model displaces large upfront capital expenditures with predictable operational spending, enabling vendors to capture recurring revenue streams.
For Market Incumbents: Deploy integrated platform strategies to counter fragmentation from niche providers and native cloud security tools. Consolidate product portfolios to offer unified management across hybrid cloud environments, addressing the multi-vendor interoperability challenge. Prioritize R&D in AI-powered policy optimization to reduce the attack surface and simplify compliance audits. This approach defends against emerging threats from open-source alternatives and enhances customer stickiness.
For New Entrants and Emerging Players: Launch via channel partnerships with managed security service providers (MSSPs) to gain rapid market access. Target mid-sized enterprises in emerging economies like Southeast Asia, where digitalization is accelerating and in-house expertise is limited. Focus on niche solutions for securing OT/IoT environments, a rapidly expanding but underserved segment. A value-based pricing model, emphasizing ease of deployment and compliance automation, offers a compelling go-to-market angle.
For Investors and Strategic Acquirers: Asymmetric upside sits with specialized firms offering AI-driven policy optimization and SOAR integration capabilities. The long-term viability of this market over the next decade is strong, anchored by persistent regulatory demands and escalating cyber threats. Target acquisition candidates with proven cloud-native solutions and strong intellectual property in automation. A key signal to watch is the increasing enterprise adoption rate of Zero Trust Architecture models.
| Strategic Initiative | Industry Significance |
|---|---|
| Launch AI-Powered Policy Optimization | Enhances predictive policy analysis, enabling security teams to model rule changes before deployment, especially for financial services. |
| Deepen SOAR Platform Integration | Links policy auditing directly to automated incident response workflows, significantly reducing mean time to resolution for enterprises. |
| Form Strategic Partnerships with MSSPs | Expands market reach to mid-sized enterprises lacking in-house security expertise, shifting spending from CAPEX to OPEX. |
| Acquire Cloud-Native Security Specialists | Strengthens capabilities in securing complex hybrid cloud environments, a critical area for large enterprises and telecommunication providers. |
| Expand into Emerging Economies | Captures greenfield demand for centralized security controls in regions undergoing rapid digitalization and new data protection laws. |
Research Approach
Direct dialogue with Chief Technology Officers, Chief Information Security Officers, IT procurement officers, and compliance leads informed the qualitative aspects of this analysis. This primary research was rigorously cross-referenced with secondary validation from corporate annual reports, regulatory body publications, and industry association studies. A robust bottom-up and top-down triangulation approach ensured data consistency and market sizing accuracy.
A bottom-up analytical lens, validated against top-down market estimates, formed the core of the forecast framework. The market was segmented across deployment models, solution offerings, specific use cases, end-user types, and organizational size for granular analysis. Compound Annual Growth Rates (CAGRs) were derived through a comprehensive regression analysis of historical trends and projected future adoption drivers across the modeling period. Key inputs included anticipated regulatory changes and enterprise cloud adoption rates.
Forecast precision tightens around the base case; tail outcomes carry wider variance under unforeseen cybersecurity threat landscape evolution or major geopolitical shifts. These projections reflect assumptions regarding technological advancements and market dynamics. A model refresh is warranted upon material change in global data privacy regulations.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Artificial Intelligence-Based Cybersecurity Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Domain Name System (DNS) Firewall Market
Cybersecurity
Wireless Network Security Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Micro Segmentation Technology Market
Cybersecurity
Global Managed Detection and Response (MDR) Market