
 Global Patch Management Market | 2026-2036
Global Patch Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Patch Management Market Foresight
Agent-based scanning architectures is rebalancing toward agentless and cloud-native delivery models, compressing deployment timelines from weeks to hours. Microsoft Corporation leverages its Azure ecosystem to embed patch orchestration within broader endpoint management suites. IBM Corporation anchors enterprise trust through mainframe-integrated vulnerability workflows that span hybrid estates. Qualys competes by extending its vulnerability management platform into native patch remediation without third-party connectors.
Patch management encompasses the systematic identification, acquisition, testing, and installation of software updates across operating systems, applications, and firmware to remediate security vulnerabilities and ensure operational continuity. Cloud-based deployment now leads expansion as organizations retire on-premises infrastructure, while vulnerability assessment solutions command premium pricing due to integrated threat intelligence feeds. Desktop management applications retain the largest installed base, though mobile device management is gaining share as bring-your-own-device policies proliferate across regulated industries.
The U.S. Securities and Exchange Commission mandates timely disclosure of material cybersecurity incidents, directly elevating patch management to board-level governance. Europe's NIS2 directive imposes stricter supply-chain security obligations, while Japan's METI promotes automated vulnerability response through its cybersecurity framework guidelines. Stakeholders must evaluate whether their current patch velocity satisfies emerging contractual liability clauses in cyber insurance policies and vendor risk assessments.
Market Dynamics
Automated patch orchestration is compressing vulnerability remediation windows from weeks to hours, forcing infrastructure teams to abandon manual approval workflows in favor of policy-driven deployment pipelines.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:US public companies must report material security incidents within four business days, elevating patch velocity to board-level accountability and accelerating enterprise automation procurement.
- Financial Services:Banks and insurers face continuous audit scrutiny over unpatched critical vulnerabilities, driving concentrated spending on integrated vulnerability-to-remediation platforms.
- Agentless Architectures:Cloud-native delivery models eliminate endpoint agent deployment overhead, shrinking proof-of-concept timelines and expanding addressable markets among mid-size enterprises.
Market Restraints
- Legacy System Inertia:Mainframe and industrial control system environments resist automated patching due to uptime guarantees, trapping substantial installed bases in manual workflows.
- Testing Environment Scarcity:Production-parity staging infrastructure demands capital-intensive hardware replication, particularly constraining regulated healthcare and energy verticals.
- Skills Concentration:Certified vulnerability management specialists cluster in Germany, Japan, and the United States, leaving secondary markets dependent on outsourced managed services.
Strategic Opportunities
- Operational Technology Convergence:Manufacturing and energy sectors are merging IT patch workflows with industrial control system maintenance, creating unified attack surface management demand.
- India:Digital infrastructure expansion under BIS cybersecurity guidelines is generating first-time enterprise patch management procurement among domestic conglomerates.
- Cyber Insurance Underwriting:Carriers are inserting patch velocity clauses into policy renewals, converting compliance verification into a recurring revenue services opportunity for vendors.
Industry Challenges
- Change Control Integration:IT service management ticketing systems require manual correlation with automated patch deployments, creating reconciliation overhead that erodes efficiency gains.
- False Positive Fatigue:Vulnerability scanners generate remediation queues that exceed operational capacity, forcing risk-based prioritization that leaves medium-severity exposures unaddressed.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Patch Management Market |
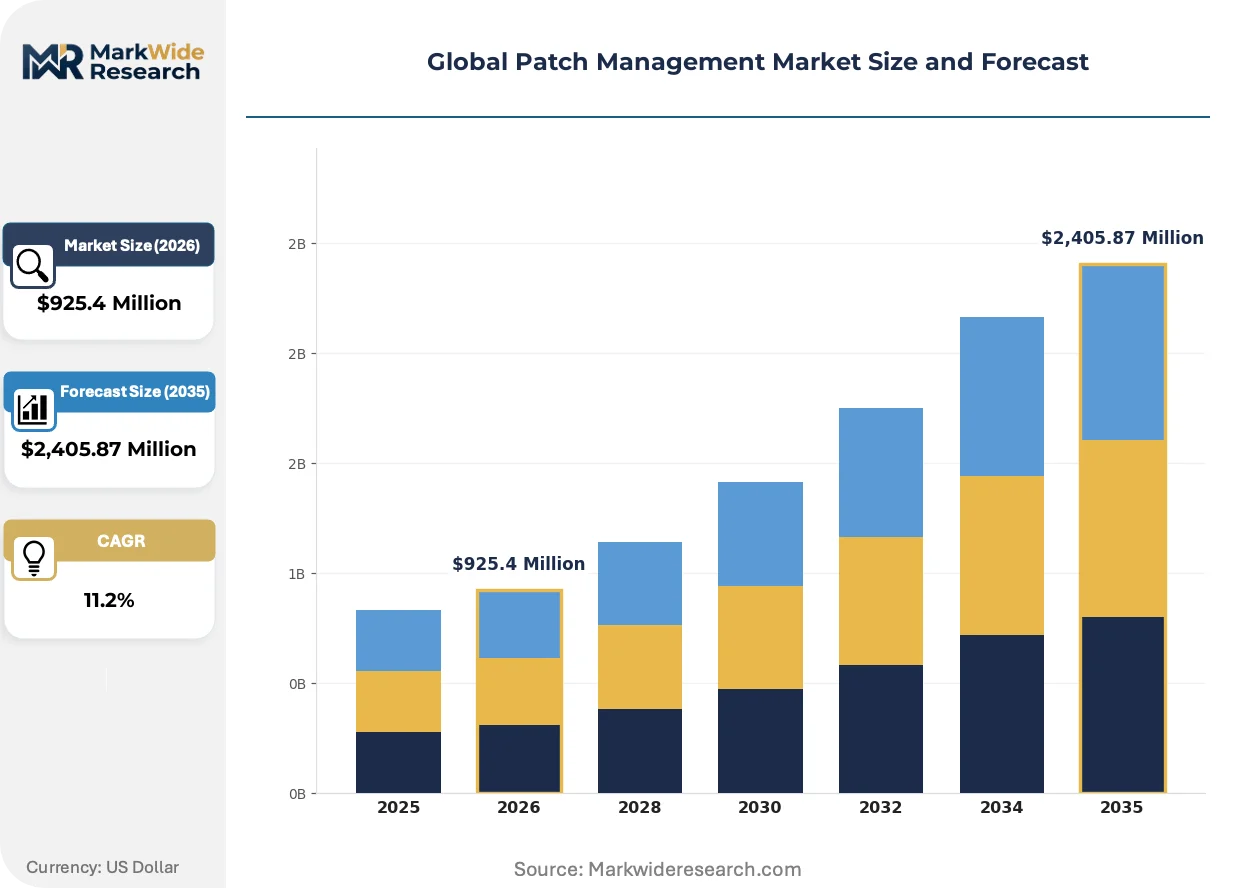
| Market Size in 2026 | $925.4 Million |
| Market Size in 2035 | $2,405.87 Million |
| CAGR (2026 – 2036) | 11.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Solution Offering: Automated Patch Deployment, Vulnerability Assessment, Compliance Management, Reporting & Analytics End User Industry: Information Technology, Telecommunications, Manufacturing, Education, Government Institutions Application: Desktop Management, Server Management, Mobile Device Management, Network Device Management |
| Companies Covered | Ivanti, ManageEngine, Microsoft Corporation, SolarWinds Corporation, ConnectWise, IBM Corporation, Automox, Qualys, Symantec, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Patch Management Market Shifts & Advancements
Continuous compliance validation is displacing point-in-time audit preparation, embedding patch verification directly into DevSecOps pipelines rather than treating remediation as a quarterly exercise.
Agentless vulnerability assessment is consolidating endpoint discovery and patch status monitoring into cloud-native platforms that require no local software installation. Healthcare providers with strict device certification requirements are adopting these architectures fastest. The technology is consolidating procurement decisions around single-vendor vulnerability-to-remediation stacks rather than multi-tool integrations.
Europe's NIS2 directive imposes supply-chain security obligations extending patch accountability to downstream software vendors. Critical infrastructure operators must now verify vendor patch commitments contractually. Germany's BSI and France's ANSSI are issuing implementation guidance that prioritizes automated response capabilities in procurement specifications.
Enterprise buyers are compressing vendor evaluation cycles by demanding proof-of-concept deployments against production workloads rather than sandbox demonstrations. This behavior shift favors vendors with frictionless cloud onboarding over those requiring extensive professional services engagement. The United States and Japan exhibit the most aggressive pilot-to-production acceleration.
Global Patch Management Market Segmentation
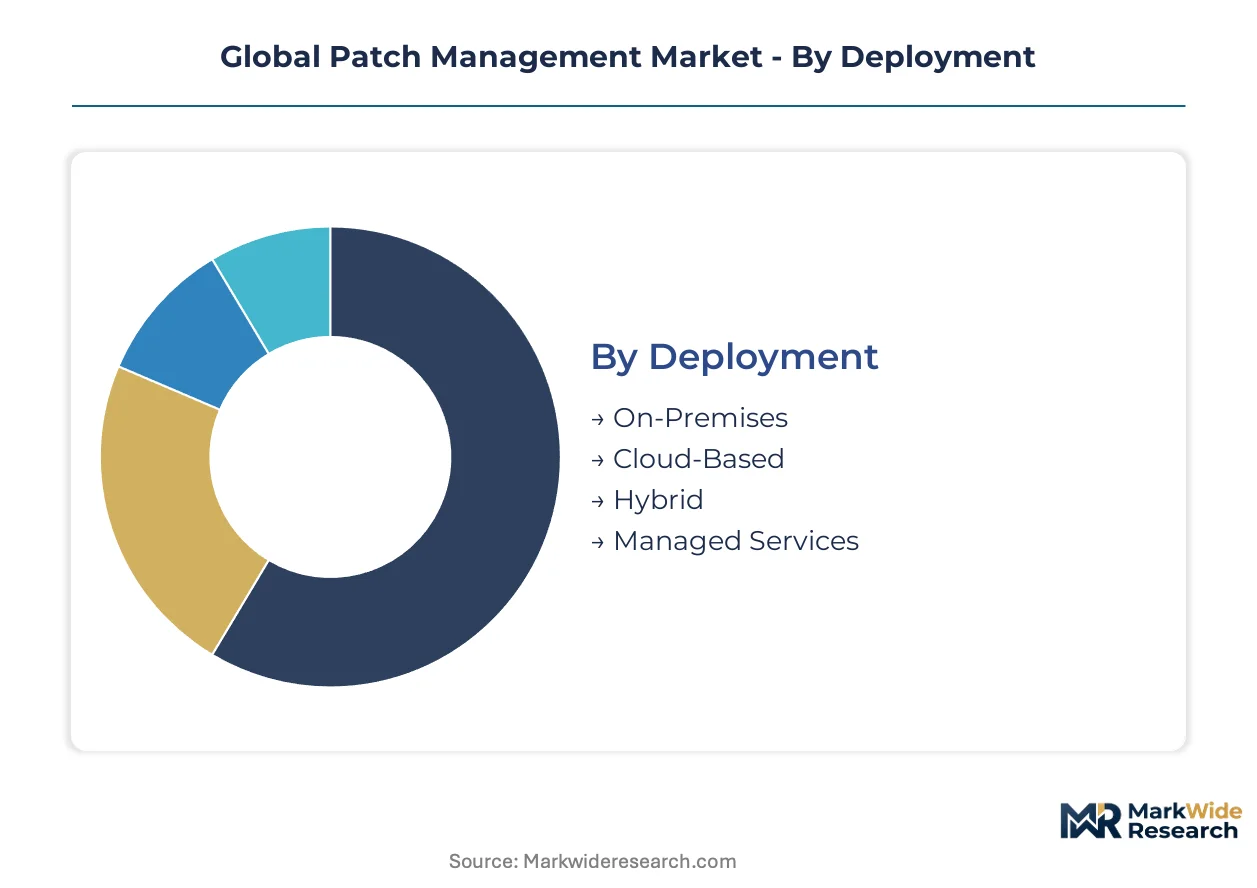
Patch management segmentation reveals how deployment architectures, solution capabilities, industry verticals, and application scopes create distinct procurement patterns. Buyers prioritize integrated vulnerability-to-remediation workflows over point solutions, compressing vendor consolidation timelines.
Deployment:
Cloud-native delivery models eliminate endpoint agent overhead and shrink proof-of-concept cycles from weeks to days.
- Cloud-Based:Multi-tenant architectures enable centralized policy orchestration across distributed endpoints without local infrastructure. Financial services institutions in the United States and Germany are migrating production workloads fastest, driven by SEC disclosure deadlines and BSI procurement guidelines.
- Managed Services:Third-party providers assume patch testing, scheduling, and compliance documentation obligations under SLA-backed contracts. Mid-size enterprises in Japan leverage METI-aligned providers to overcome certified specialist scarcity.
- On-Premises:Air-gapped environments in defense and critical infrastructure retain localized patch repositories for sovereignty requirements.
- Hybrid:Split architectures accommodate regulated data residency while offloading non-sensitive endpoint management to cloud tiers.
Cloud-Based leads on scale; Managed Services leads on momentum.
Solution Offering:
Pricing stratifies across integrated platforms commanding premium subscriptions versus standalone modules.
- Vulnerability Assessment:Continuous scanning engines with threat intelligence feeds identify exposure severity and exploitation probability. Healthcare providers in France prioritize ANSSI-certified scanners to satisfy NIS2 supply-chain verification mandates.
- Automated Patch Deployment:Policy-driven pipelines execute remediation without manual approval gates, compressing vulnerability windows. Banks in the United States deploy these capabilities to satisfy four-day SEC incident reporting requirements.
- Compliance Management:Audit-ready documentation templates map patch status to regulatory frameworks including GDPR, HIPAA, and ISO 27001.
- Reporting & Analytics:Executive dashboards translate technical metrics into board-accessible risk postures for governance disclosure.
Vulnerability Assessment anchors revenue concentration; Automated Patch Deployment climbs the fastest.
End User Industry:
Regulatory intensity and attack surface complexity determine solution sophistication requirements.
- Information Technology:Software vendors and technology service providers operate the most heterogeneous endpoint estates, demanding universal OS and application coverage. Enterprises in Germany consolidate procurement around BSI-compliant integrated stacks.
- Telecommunications:Network infrastructure operators patch routers, switches, and customer premises equipment at carrier scale. Japanese operators align deployments with METI cybersecurity framework automation guidelines.
- Manufacturing:Operational technology convergence merges IT patch workflows with industrial control system maintenance windows.
- Government Institutions:Classified and unclassified network separation mandates hybrid deployment architectures with sovereign data controls.
- Education:Bring-your-own-device proliferation across campuses drives mobile-first patch management procurement.
Information Technology dominates installed base; Telecommunications shows steepest expansion trajectory.
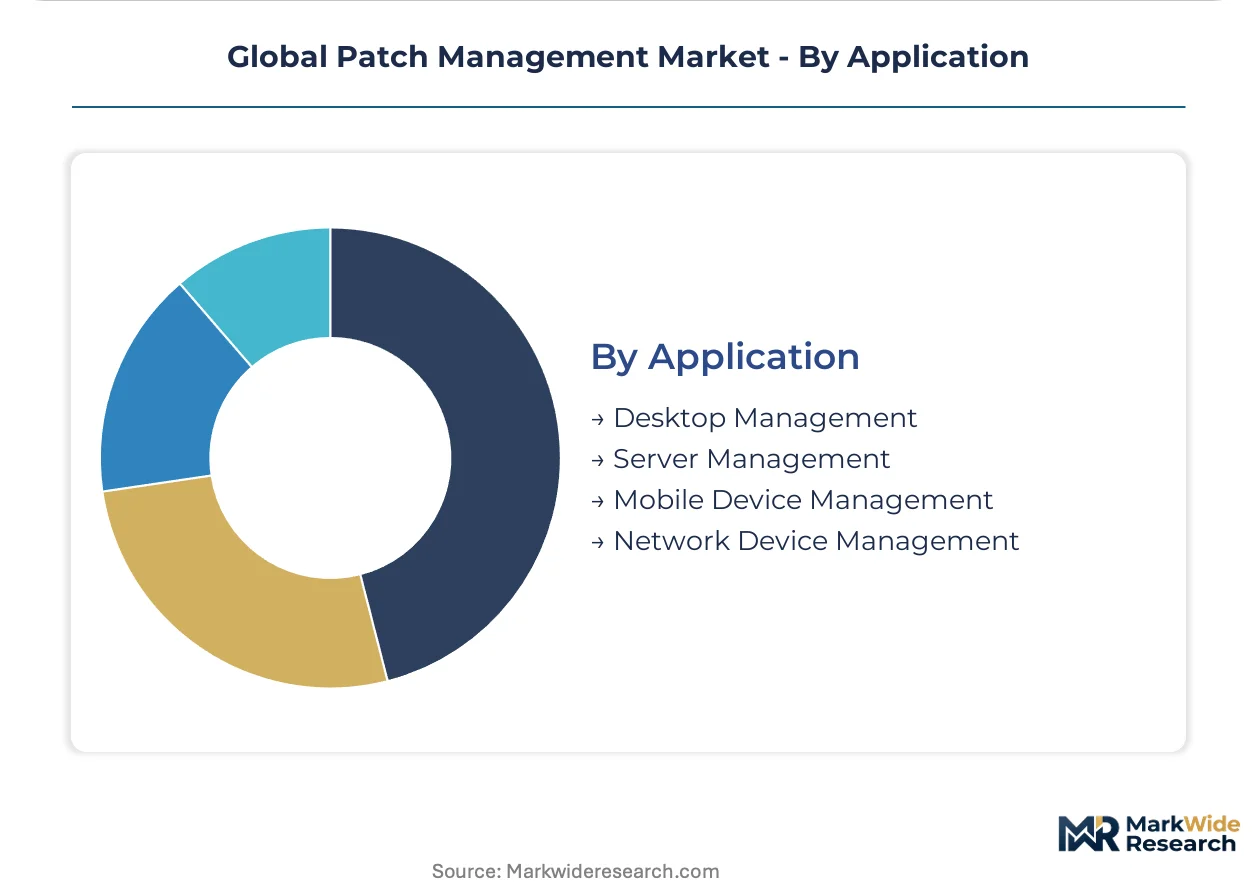
Application:
Device category dictates patch velocity requirements and change control rigor.
- Desktop Management:Windows and macOS endpoint fleets retain the largest addressable volume, though growth moderates as cloud workloads expand. United States enterprises dominate spending on automated deployment tools.
- Server Management:Linux and Windows Server environments demand zero-downtime patching through live kernel update capabilities. Financial institutions in Japan prioritize these features for trading system continuity.
- Mobile Device Management:iOS and Android patch orchestration gains share as regulated industries formalize BYOD policies. German healthcare providers adopt agentless architectures fastest to avoid medical device certification conflicts.
- Network Device Management:Firmware updates for firewalls, switches, and access points require out-of-band recovery mechanisms.
Desktop Management retains volume leadership; Mobile Device Management gains share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial services clusters in New York, Frankfurt, and Tokyo drive concentrated procurement of automated patch orchestration platforms. Regulatory disclosure mandates across multiple jurisdictions compress vendor evaluation cycles and accelerate cloud migration timelines.
United States
SEC cybersecurity disclosure rules mandate four-day incident reporting for public companies, elevating patch velocity to board-level governance. Financial institutions in New York and Chicago dominate enterprise spending on integrated vulnerability-to-remediation platforms. Healthcare providers in Boston accelerate agentless architecture adoption to avoid medical device certification conflicts.
Germany
BSI procurement guidelines prioritize automated response capabilities in federal and critical infrastructure contracts. Manufacturing conglomerates in Bavaria and North Rhine-Westphalia merge IT patch workflows with operational technology maintenance windows. Frankfurt's banking sector consolidates endpoint security spending around BSI-compliant integrated stacks.
Japan
METI cybersecurity framework guidelines promote automated vulnerability response across telecommunications and financial sectors. Tokyo-based enterprises exhibit aggressive pilot-to-production acceleration, compressing vendor proof-of-concept timelines. Osaka manufacturers align patch deployments with operational technology convergence requirements.
India
BIS cybersecurity guidelines under digital infrastructure expansion generate first-time enterprise procurement among domestic conglomerates. Bengaluru and Mumbai technology campuses drive cloud-native patch management adoption. Hyderabad's pharmaceutical clusters invest in compliance management modules for FDA and EMA audit readiness.
France
ANSSI implementation guidance prioritizes automated response capabilities in critical infrastructure procurement specifications. Healthcare providers in Paris and Lyon adopt ANSSI-certified scanners to satisfy NIS2 supply-chain verification mandates. Toulouse aerospace clusters integrate patch verification into DevSecOps pipelines for export compliance.
Global Patch Management Market Competitive Landscape
Global majors compete with regional champions across deployment architecture specialization, creating a tiered competitive structure. Cloud-native platforms with frictionless onboarding capture mid-market expansion, while mainframe-integrated suites retain enterprise incumbency. Three archetypes dominate: hyperscaler-embedded orchestration, standalone vulnerability-to-remediation specialists, and managed security service providers. Consolidation accelerates through strategic partnerships bridging agent-based legacy estates with agentless cloud delivery.
Within the integrated platform tier, Microsoft Corporation and IBM Corporation exemplify divergent anchoring strategies. Microsoft leverages hyperscaler infrastructure to embed patch orchestration within broader endpoint management suites. IBM anchors enterprise trust through mainframe-integrated vulnerability workflows spanning hybrid estates. Qualys occupies a position as a cloud-native specialist extending vulnerability management into native patch remediation without third-party connectors.
| Leading Market Players |
|---|
| Ivanti |
| ManageEngine |
| Microsoft Corporation |
| SolarWinds Corporation |
| ConnectWise |
| IBM Corporation |
| Automox |
| Qualys |
| Symantec |
| Others |
Supply & Pricing Matrix
Cloud-native delivery integration anchors supply positioning and pricing power for patch management vendors, compressing deployment overhead while enabling subscription premiums. Microsoft Azure and AWS hyperscaler ecosystems feed from this integration pattern, embedding orchestration tools within broader endpoint suites that command higher per-seat pricing than standalone modules.
Pricing Analysis
Input-cost pass-through from threat intelligence feed licensing and cloud infrastructure metering shapes SaaS-tiered subscription structures across the market. Pricing stratifies across premium integrated platforms, standard vulnerability-to-remediation bundles, and economy-tier point solutions, with differentiation anchored in certification level (BSI, ANSSI, METI compliance) and automation depth. Cost compression in the economy tier intensifies as open-source scanning engines commoditize baseline vulnerability detection. Mid-size enterprises in Japan exhibit highest price sensitivity due to certified specialist scarcity, while Frankfurt banking institutions show lowest sensitivity given regulatory penalty exposure.
Supply Chain Analysis
Threat intelligence feed supply rests on Israeli, United States, and Estonian cybersecurity research clusters specializing in exploit database curation and zero-day tracking. Cloud compute infrastructure draws from hyperscaler regions in Virginia, Frankfurt, and Tokyo, while endpoint agent development hinges on kernel-level engineering talent concentrated in Germany and Japan. Single-source vulnerability in threat intelligence aggregation creates exposure if geopolitical restrictions interrupt cross-border data sharing. Distribution runs through direct enterprise sales teams for large accounts and hyperscaler marketplaces for mid-market procurement, with managed service providers handling secondary market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Patch management has matured into a late-cycle quality market where procurement concentrates on integrated platforms satisfying NIS2, SEC, and METI automation mandates. Financial services institutions in New York and Frankfurt now demand premium specifications including four-day remediation SLAs and board-level risk dashboards.
For Market Incumbents: To counter agentless cloud-native entrants compressing proof-of-concept timelines, incumbents must anchor mainframe-integrated vulnerability workflows and deepen certification investments across BSI and ANSSI frameworks. Channel control through hyperscaler marketplace listings provides defensive leverage against direct-to-enterprise disintermediation. For New Entrants and Emerging Players: Begin with mid-size manufacturing conglomerates in India and Bavaria where operational technology convergence creates first-time unified patch procurement demand. Target cloud-native managed service delivery to bypass certified specialist scarcity in secondary markets, leveraging frictionless onboarding against legacy professional services incumbents. For Investors and Strategic Acquirers: Roll-up economics work for regional managed security service providers because cyber insurance underwriting is inserting patch velocity clauses that convert compliance verification into recurring revenue streams. Watch carrier policy renewal language as the inflection signal indicating vendor consolidation acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedding patch orchestration within Microsoft Azure and AWS endpoint suites captures enterprise procurement consolidation. |
| Certification Investment | BSI and ANSSI compliance positioning unlocks German and French critical infrastructure contract eligibility. |
| Managed Service Expansion | SLA-backed patch operations overcome certified specialist scarcity in Japan and India secondary markets. |
| Operational Technology Convergence | Unified IT-ICS patch workflows address manufacturing demand in Bavaria and Osaka industrial clusters. |
| Strategic Partnership | Hyperscaler marketplace listings compress enterprise sales cycles and expand mid-market addressability. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs, IT procurement officers, platform engineers, and managed security service directors alongside secondary validation. SEC cybersecurity disclosure filings, BSI procurement guidelines, METI framework documentation, and hyperscaler capex disclosures anchored data triangulation. Bottom-up endpoint deployment estimates and top-down enterprise security spending analysis converged on segment-level sizing.
Segment-weighting across deployment architecture, solution capability, and end-user industry dimensions drove forecast construction over the projection horizon. Cloud-based, managed services, on-premises, and hybrid deployment models combined with vulnerability assessment, automated patch deployment, compliance management, and reporting modules formed the analytical framework. CAGRs derived from regression against regulatory mandate implementation timelines and cyber insurance penetration curves, with inputs from endpoint fleet expansion rates and operational technology convergence adoption patterns.
Several conditions sit outside the modeled scope, including sovereign data localization mandates beyond current NIS2 territorial requirements and quantum-resistant cryptography standards still under ISO development. Forecasts reflect assumptions around SEC disclosure rule enforcement consistency and carrier underwriting standardization. Material deviation in named triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
SSL VPN Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Cloud Security Market
Cybersecurity
Ddos Protection and Mitigation Security Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
Network Security Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Cyber Security As a Service Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Global Mobile Data Protection Market