
 Poland Cybersecurity Market | 2026-2036
Poland Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Poland Cybersecurity Market Analytics
Zero-trust architecture certification is reorganizing procurement priorities across Polish enterprise buyers. Asseco Poland leverages its domestic banking relationships to dominate financial sector deployments. Comarch anchors public-sector contracts through specialized compliance offerings. TestArmy Group differentiates via penetration testing expertise tailored to mid-market manufacturers.
Poland cybersecurity encompasses hardware, software, and service solutions engineered to protect digital infrastructure against unauthorized access, data exfiltration, and operational disruption, with next-generation firewalls processing throughput exceeding 100 Gbps in enterprise-grade deployments. Its primary purpose is ensuring business continuity and regulatory compliance for organizations managing sensitive information assets. Network Security occupies the largest revenue pool as legacy perimeter defenses undergo wholesale replacement. Cloud Security represents the fastest-expanding deployment category as Polish enterprises migrate workloads from on-premises data centers. Managed Security Services captures concentrated margin pools by bundling 24/7 threat monitoring with incident response capabilities.
Poland's cybersecurity sector operates under EU NIS2 Directive obligations transposed through national legislation, with the country's digital affairs ministry enforcing sector-specific incident reporting timelines. The national telecom regulator, UKE, mandates critical infrastructure operators to maintain certified security management systems under Polish telecommunications law. Stakeholders must weigh the capital requirements of AI-based threat detection platforms against the operational risk of retaining signature-dependent defenses.
Market Dynamics
The EU NIS2 Directive's transposition into Polish national law is compressing procurement cycles as critical infrastructure operators race to meet incident reporting timelines and certified security management obligations before enforcement deadlines.
Growth Catalysts
- EU NIS2 Directive:Mandatory incident reporting and operational resilience requirements are compelling Polish energy, transport, and healthcare operators to upgrade monitoring infrastructure and retain managed security services.
- Financial sector digitization:Polish banks and insurers are deploying next-generation firewalls and AI-based threat detection to protect real-time payment systems and customer data repositories.
- Warsaw-Krakow enterprise clustering:Concentrated demand from headquarters operations and shared service centers is driving localized investment in cloud security architecture and zero-trust network access.
Market Restraints
- Certified security professional scarcity:Polish labor markets face acute shortages of CISSP- and CEH-certified practitioners, inflating salary costs for SOC staffing and incident response teams.
- Legacy infrastructure debt:Manufacturing and public sector organizations maintain decades-old operational technology systems that resist modern endpoint detection and response integration without wholesale replacement.
- Input cost concentration:Enterprise-grade firewall and SIEM hardware depends on concentrated semiconductor supply from East Asian foundries, exposing Polish buyers to extended lead times and tariff volatility.
Strategic Opportunities
- Polish SME underpenetration:Mid-sized manufacturers and logistics operators outside Warsaw and Krakow remain reliant on basic antivirus, creating whitespace for managed detection and response offerings.
- Operational technology convergence:Integration of IT and OT security fabrics is opening deployment opportunities for specialized vendors serving Polish critical infrastructure operators.
- EU Cybersecurity Act certification:Common Criteria and EUCC certification schemes are creating preference premiums for Polish vendors achieving recognized assurance levels in public procurement.
Industry Challenges
- Zero-trust architecture migration complexity:Polish enterprises struggle to decommission perimeter-based VPNs and rearchitect identity-centric access without disrupting legacy application workflows.
- Incident response capability gaps:Organizations lack tabletop exercise discipline and forensic readiness, leaving them exposed to ransomware dwell time and regulatory penalty escalation.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Poland Cybersecurity Market |
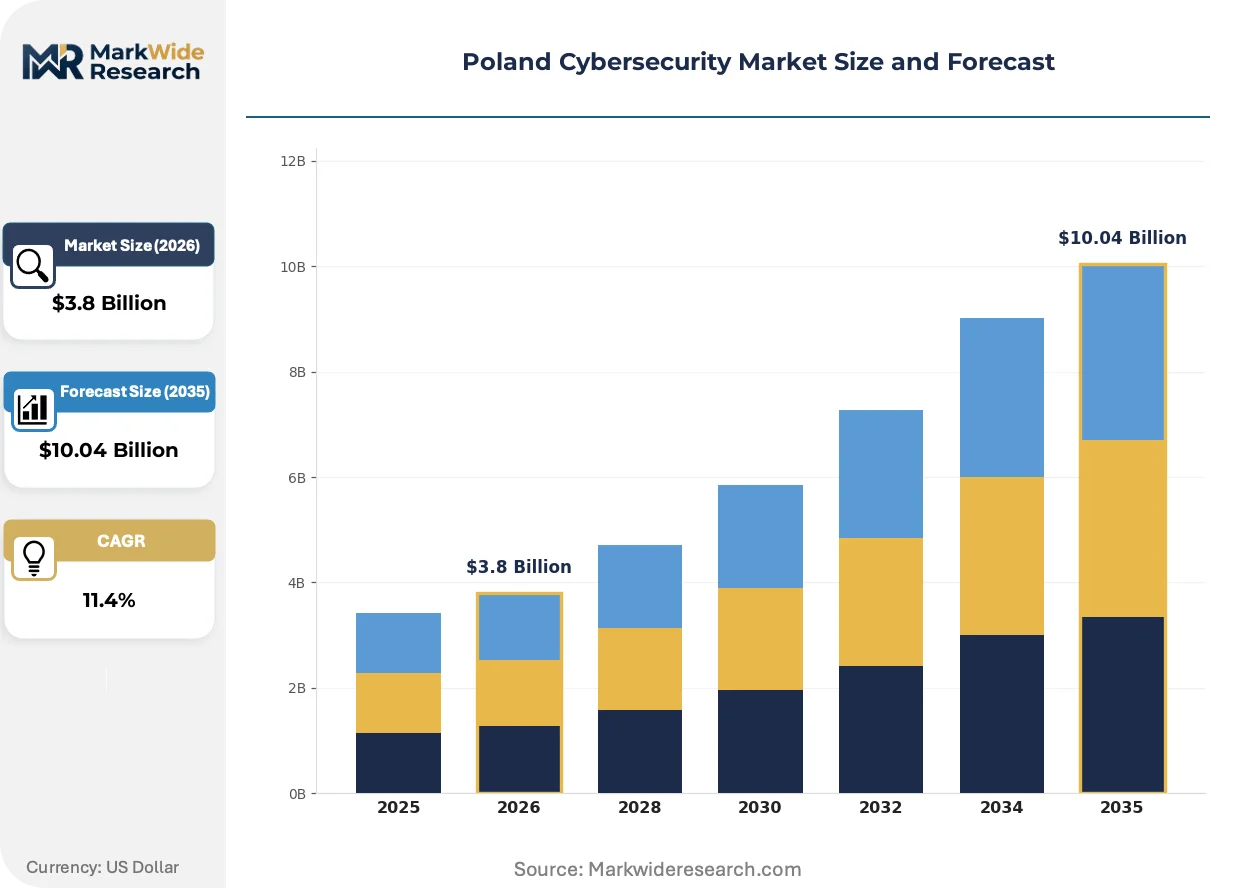
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $10.04 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Network Security, Endpoint Security, Application Security, Cloud Security Deployment Model: On-premises, Cloud-based, Hybrid, Managed Security Services End User: Government, BFSI, Healthcare, Retail Technology: AI-based Security, Blockchain Security, IoT Security, Encryption |
| Companies Covered | Asseco Poland, Comarch, TestArmy Group, RED TEAM, TraceRoute42, Framework Security, Cyberlands, Exatel, Enigma Systemy Ochrony Informacji, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Poland Cybersecurity Market Evolving Landscape
Artificial intelligence is restructuring threat detection economics across Polish security operations, compressing analyst workload while expanding adversarial automation capabilities that demand continuous defensive adaptation.
Extended detection and response platforms aggregate endpoint, network, and cloud telemetry into unified analytics engines that correlate indicators of compromise across attack chains. Polish financial institutions and energy operators are adopting these systems fastest, replacing siloed point solutions with consolidated visibility fabrics. Signature-dependent antivirus is supplanting behavioral heuristics in mid-market procurement, though enterprise buyers retain hybrid architectures.
The EU NIS2 Directive mandates sector-specific security requirements and harmonized incident reporting thresholds across member states. Polish digital affairs ministry enforcement is accelerating compliance investments in security information and event management infrastructure. Critical infrastructure operators in energy and transport verticals face the steepest adaptation curves, with many outsourcing 24/7 monitoring to specialized managed security providers.
Subscription-based consumption models are displacing perpetual license procurement for security software and hardware across Polish enterprise buyers. Chief information security officers prefer operational expenditure structures that bundle threat intelligence updates and vendor-managed patching. This preference shift concentrates most visibly in Warsaw financial services clusters, where multi-year managed detection and response contracts now dominate new security spending.
Poland Cybersecurity Market Segmentation
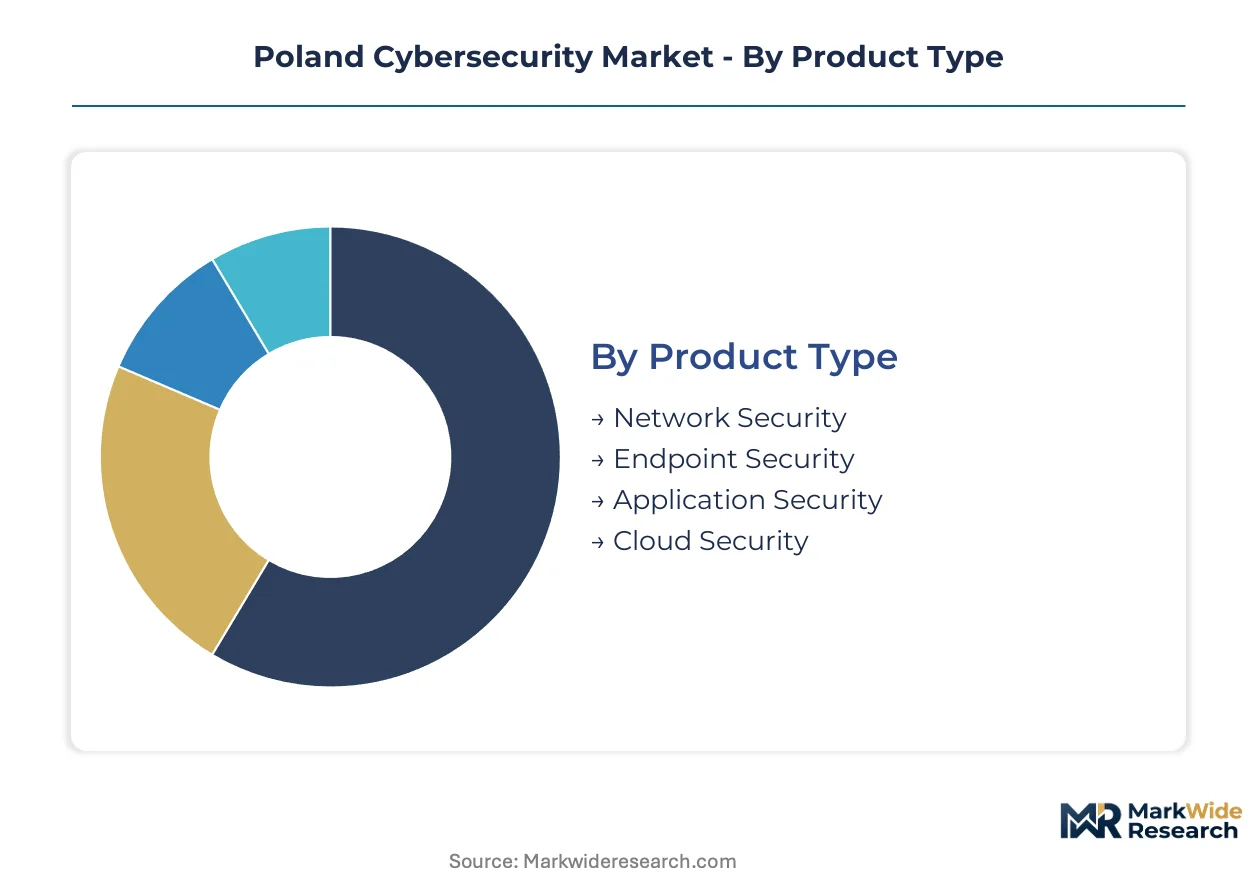
Polish enterprise procurement patterns reveal distinct technology preferences across organizational maturity levels. Security buyers in Warsaw and Krakow clusters prioritize different capability bundles than mid-market manufacturers in secondary cities.
Product Type:
Margin pools concentrate in solutions protecting hybrid infrastructure as Polish enterprises straddle on-premises legacy and cloud-native workloads.
- Network Security:Next-generation firewalls and intrusion prevention systems process throughput exceeding 100 Gbps in enterprise-grade deployments. Polish financial institutions in Warsaw drive replacement cycles as legacy perimeter defenses reach end-of-life.
- Cloud Security:Cloud access security brokers and workload protection platforms secure multi-tenant environments. Krakow shared service centers and SaaS providers are expanding fastest as workload migration accelerates.
- Endpoint Security:Endpoint detection and response agents deploy across laptop, server, and mobile device fleets. Manufacturing and logistics operators outside major metros represent underpenetrated demand.
- Application Security:Static and dynamic testing tools integrate into software development pipelines. Polish fintech developers and e-commerce platforms prioritize DevSecOps tooling.
Network Security holds installed capacity. Cloud Security is rotating up the share rankings.
Deployment Model:
Customer type determines deployment economics — regulated sectors favor capital-intensive control while resource-constrained buyers prefer subscription flexibility.
- Managed Security Services:Twenty-four-hour threat monitoring and incident response bundles delivered via security operations centers. Polish energy and transport operators under NIS2 obligations outsource monitoring to address certified professional scarcity.
- Cloud-based:SaaS-delivered security controls with automatic vendor-managed patching. Mid-market retailers and healthcare clinics adopt fastest to minimize internal IT overhead.
- On-premises:Hardware appliances and perpetual software licenses maintained within customer data centers. Government agencies and defense contractors mandate air-gapped architectures.
- Hybrid:Orchestrated security policies spanning private data centers and public cloud infrastructure. Large Polish banks pursue phased cloud migration while retaining sensitive workload control.
On-premises retains regulatory-mandated share. Managed Security Services is climbing the fastest.
End User:
Compliance exposure and asset sensitivity create divergent spending intensity across verticals.
- BFSI:Real-time payment system protection and customer data vault security dominate procurement. Polish banks deploy AI-based threat detection to defend against authorized push payment fraud.
- Government:Classified network segmentation and citizen identity protection drive classified procurement channels. National critical infrastructure operators face strict NIS2-derived security management obligations.
- Healthcare:Patient record encryption and medical device network isolation address GDPR and NIS2 convergence. Hospital networks in major Polish cities upgrade legacy Windows systems.
- Retail:Point-of-sale terminal hardening and e-commerce platform defense against card-not-present fraud. Omnichannel merchants prioritize PCI-DSS compliant payment processing.
BFSI commands premium pricing. Healthcare is gaining share fastest amid digitization pressure.
Technology:
Capability maturity separates proven defensive layers from emerging investment categories.
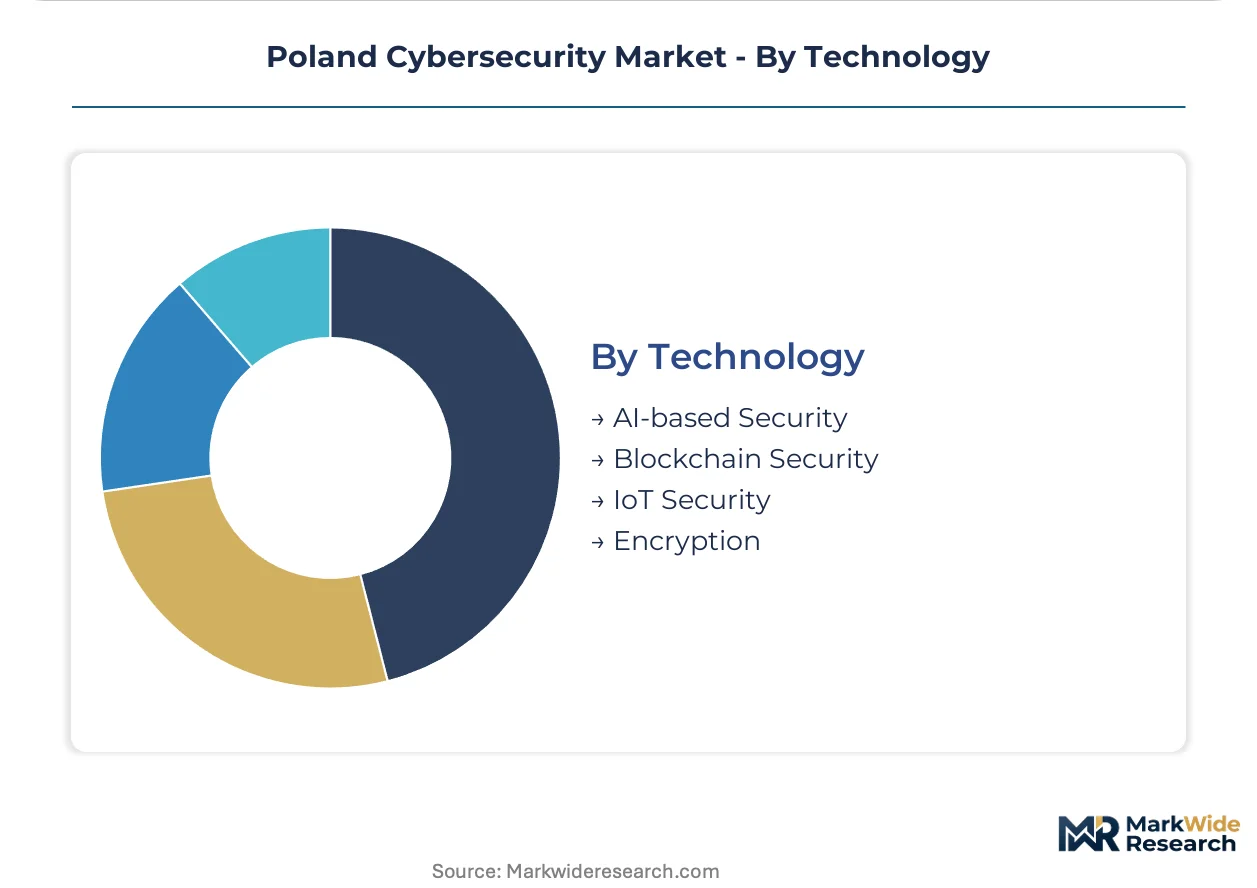
- Encryption:Data-at-rest and data-in-transit cryptographic controls using AES-256 and TLS protocols. Universal baseline across all regulated Polish sectors.
- AI-based Security:Machine learning models trained on behavioral baselines to detect anomalous access patterns. Polish financial institutions pilot adversarial-resistant detection against AI-enabled attacks.
- IoT Security:Device identity management and network microsegmentation for connected operational technology. Manufacturing and energy operators address converged IT-OT attack surfaces.
- Blockchain Security:Distributed ledger integrity verification and smart contract auditing. Limited current deployment beyond cryptocurrency exchange and supply chain traceability pilots.
Encryption maintains foundational ubiquity. AI-based Security is rotating up the share rankings.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Poland's cybersecurity sector operates as a net importer of advanced threat detection hardware, with domestic vendors concentrating on managed services and compliance consulting. Warsaw and Krakow enterprise clusters absorb the majority of security spending, while secondary cities present underpenetrated demand pools for mid-market solutions.
Masovian Voivodeship
Warsaw headquarters operations and financial services clusters drive concentrated demand for next-generation firewalls and AI-based threat detection platforms. The Polish digital affairs ministry enforces NIS2-derived incident reporting timelines for critical infrastructure operators based in the capital. Sectors such as banking and energy maintain security operations centers across Warsaw's central business district.
Lesser Poland Voivodeship
Krakow's shared service centers and SaaS providers accelerate cloud security procurement as workload migration intensifies. UKE, the national telecom regulator, mandates certified security management systems for operators maintaining infrastructure across southern Poland. The city's technology parks host specialized penetration testing firms serving mid-market manufacturers.
Silesian Voivodeship
Heavy industry and manufacturing networks in Katowice require operational technology security integration as IT-OT convergence exposes legacy systems. Polish telecommunications law imposes security obligations on industrial network operators throughout the region. Mining and steel producers deploy endpoint detection and response across aging control system architectures.
Greater Poland Voivodeship
Poznan logistics operators and e-commerce platforms invest in payment security and customer data protection amid PCI-DSS compliance pressure. GDPR enforcement by the national data protection authority shapes procurement priorities for retailers handling cross-border transactions. Regional distribution centers implement cloud access security brokers for multi-tenant warehouse management systems.
Pomeranian Voivodeship
Gdansk port infrastructure and maritime logistics operators face NIS2 obligations for transport sector cybersecurity resilience. The digital affairs ministry coordinates sector-specific adaptation timelines for critical port systems and customs processing networks. Shipyard and container terminal operators upgrade network segmentation to address converged IT-OT attack surfaces.
Poland Cybersecurity Market Competitive Landscape
Listed leaders compete with private specialists across compliance depth and managed service bundling, producing a tiered structure where scale-driven platforms coexist with niche consultancies. Asseco Poland leverages its Warsaw Stock Exchange listing to anchor financial sector relationships, while Comarch occupies public-sector procurement channels through specialized certification offerings. Three strategic archetypes dominate: domestic platform vendors with banking heritage, compliance-focused systems integrators, and penetration testing boutiques serving mid-market verticals. Competitive moves concentrate on zero-trust architecture certification attainment and managed detection and response capacity expansion.
Within the domestic platform tier, Asseco Poland and Comarch exemplify divergent positioning strategies rooted in sector specialization. Asseco Poland represents the banking-anchored archetype, while Comarch occupies the public-sector compliance vector. TestArmy Group sits within the specialist tier, anchoring penetration testing capabilities for manufacturing clients outside major metropolitan clusters. These three firms illustrate how Polish cybersecurity competition segments across institutional relationships rather than pure technology differentiation.
| Leading Market Players |
|---|
| Asseco Poland |
| Comarch |
| TestArmy Group |
| RED TEAM |
| TraceRoute42 |
| Framework Security |
| Cyberlands |
| Exatel |
| Enigma Systemy Ochrony Informacji |
| Others |
Value Network & Pricing Analysis
Semiconductor foundry scale economies in East Asia concentrate firewall and SIEM hardware production, compressing Polish buyer margins while elevating procurement leverage for Warsaw financial institutions placing large-volume orders. This concentration shapes both supply availability and price floors across enterprise security deployments.
Pricing Analysis
Industrial OEM buyers anchor subscription-based pricing structures as Polish energy and transport operators under NIS2 obligations favor operational expenditure models bundling threat intelligence updates. Three-tier pricing stratifies across premium AI-based detection, standard SIEM platforms, and economy endpoint agents. Pricing pressure stems from certified security professional scarcity inflating managed service delivery costs. Mid-market manufacturers outside Warsaw and Krakow clusters exhibit highest price sensitivity, while regulated financial institutions absorb premium tiers with minimal negotiation.
Supply Chain Analysis
Container availability fluctuations across Asia-Europe trade lanes expose Polish buyers to extended lead times for enterprise-grade firewall appliances and GPU-accelerated threat detection hardware. Semiconductor supply concentrates in Taiwan, South Korea, and China, with advanced networking processors and encryption accelerators drawing from concentrated foundry capacity. Single-source vulnerability in East Asian chip fabrication creates systemic exposure to tariff volatility and export restriction risk. Distribution runs through Warsaw-based systems integrators and Krakow cloud service providers serving regional enterprise clusters.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is consolidating among Warsaw financial institutions and Krakow shared service centers, compressing vendor margins while elevating procurement sophistication across Polish enterprise security markets.
For Market Incumbents: Secure zero-trust architecture certification attainment ahead of EU Cybersecurity Act enforcement deadlines, locking in public-sector procurement preferences. Anchor managed detection and response capacity expansion in Masovian and Lesser Poland Voivodeships to defend against emerging cloud-native competitors. Vertical integration into AI-based threat detection training data pipelines addresses analyst scarcity while hardening margin position. For New Entrants and Emerging Players: Mid-market manufacturing security gaps in Silesian and Greater Poland Voivodeships present immediate white-space opportunity, as legacy antivirus reliance creates conversion potential for managed endpoint detection offerings. Polish SME underpenetration outside Warsaw-Krakow clusters offers lowest competitive density for subscription-based security services. Channel partnerships with Poznan logistics operators and Gdansk port authorities accelerate sector-specific credibility without direct incumbent confrontation. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed security service providers bundling 24/7 SOC operations with incident response retainers, offering superior cash flow predictability versus hardware-dependent vendors. Acquisition targets should demonstrate EUCC certification progress and established relationships with Polish critical infrastructure operators. Monitor NIS2 enforcement action intensity as inflection signal for compliance-driven procurement acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Certification | EU Cybersecurity Act compliance unlocks public-sector procurement channels and preference premiums. |
| Managed Detection and Response Expansion | Address certified professional scarcity while capturing recurring revenue from NIS2-obligated operators. |
| AI-Based Threat Detection Platform Launch | Behavioral analytics reduce analyst workload for Polish financial institutions defending real-time payments. |
| Operational Technology Security Integration | IT-OT convergence in Silesian manufacturing creates specialized deployment opportunities with limited competition. |
| Geographic Expansion to Secondary Cities | Poznan and Gdansk logistics clusters offer underpenetrated demand for mid-market cloud security solutions. |
Research Methodology
Two parallel data streams informed the analysis: structured primary interviews with Polish CISOs, SOC directors, and digital affairs ministry officials, and secondary validation against UKE regulatory filings, EU NIS2 transposition documents, and hyperscaler security capex disclosures. Bottom-up triangulation across Warsaw financial services procurement patterns and Krakow SaaS provider deployment data anchored volume estimates. Top-down cross-checks against EU cybersecurity spending benchmarks ensured segmentation coherence.
Across the projection horizon, the analytical framework modeled deployment model transitions, vertical compliance exposure, and technology capability maturity. Segmentation dimensions included product type, deployment architecture, end-user vertical, and geographic enterprise clustering. CAGRs derived from fitted growth curves incorporating NIS2 enforcement timelines and cloud migration velocity. Polish banking digitization rates and critical infrastructure operator outsourcing propensity served as key forecast inputs.
Material uncertainties — regulatory enforcement timing, semiconductor supply disruption, and certified professional availability — sit outside the modeled envelope. Forecasts reflect documented assumptions regarding EU directive transposition consistency and enterprise cloud adoption continuity. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud Application Security Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
New Zealand Cybersecurity Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
Brazil Cybersecurity Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
Cyber Security Market
Cybersecurity
Dark Web Intelligence Market