
 United States Virtualization Security Market | 2026-2036
United States Virtualization Security Market Size, Share, and Industry Trends Forecast 2026-2036
United States Virtualization Security Market Analytics
Software-defined silicon is broadening hardware-rooted trust boundaries for virtualized workloads. VMware Inc. leverages its ESXi hypervisor dominance to embed security controls at the kernel layer. Palo Alto Networks, Inc. competes through Prisma Cloud's agentless scanning for container and VM vulnerabilities across multi-cloud estates. Fortinet, Inc. anchors its position with FortiGate-VM virtual appliances that integrate networking and security policy enforcement.
United States Virtualization Security encompasses technologies that protect hypervisors, virtual machines, containers, and software-defined networks from unauthorized access, lateral movement, and data exfiltration through micro-segmentation, encryption, and continuous compliance monitoring. The primary commercial purpose is to maintain workload isolation and integrity as enterprises consolidate servers and migrate applications to cloud infrastructure. Hybrid Cloud deployments generate the largest revenue pool among deployment models, reflecting federal and financial sector requirements for split workloads between sovereign and commercial infrastructure. Network Security within the security type dimension shows the steepest growth trajectory, driven by east-west traffic inspection demands in microservices architectures. Managed Services capture disproportionate margin share as staffing shortages push healthcare providers and government agencies toward outsourced security operations centers.
FedRAMP authorization requirements from GSA shape product roadmaps for vendors serving federal buyers, mandating continuous monitoring and encrypted data-at-rest for cloud security offerings. NIST SP 800-207 zero-trust architecture guidance drives commercial sector procurement patterns, particularly among defense contractors and critical infrastructure operators. HIPAA security rule enforcement by HHS OCR elevates endpoint protection spending among healthcare providers running virtualized electronic health record systems. Stakeholders must weigh the trade-off between cloud-native security stacks and independent software vendor solutions as AWS, Azure, and Google deepen their native control portfolios.
Market Dynamics
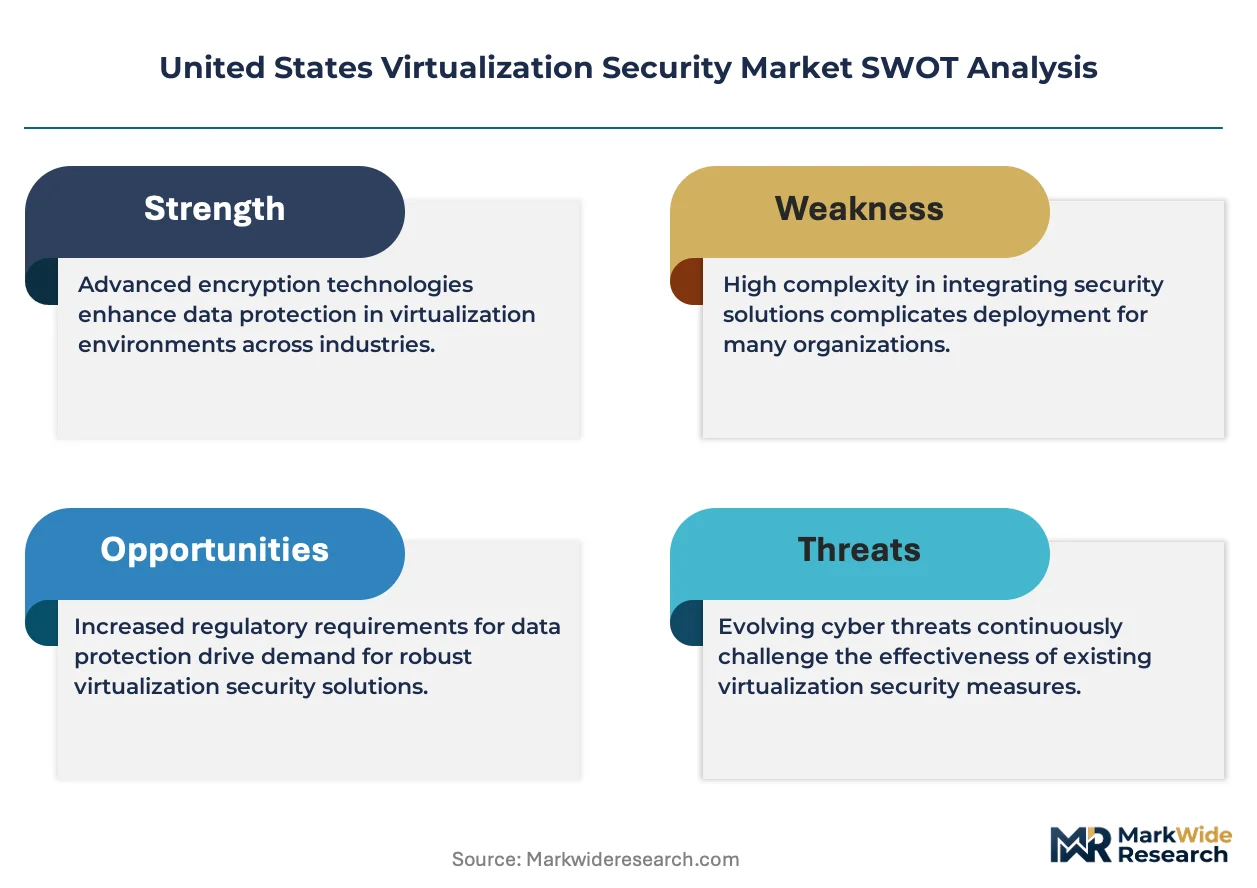
Federal zero-trust mandates are compressing procurement cycles for hypervisor-hardening solutions as agencies race to meet OMB M-22-09 deadlines for cloud workload protection.
Growth Catalysts
- NIST SP 800-207:Federal civilian and defense agencies must implement zero-trust architectures by fiscal year deadlines, forcing immediate investment in micro-segmentation and continuous verification tools for virtualized environments.
- Electronic health record virtualization:HIPAA Security Rule enforcement by HHS OCR drives hospital systems to encrypt patient data across VMware and Hyper-V deployments, creating sustained demand for workload isolation.
- East-west traffic inspection:Containerized microservices architectures in financial services generate explosive demand for software-defined network security that monitors lateral movement between pods.
Market Restraints
- Specialized cybersecurity labor scarcity:Certified cloud security architects command premium salaries that strain state government and mid-market enterprise budgets, slowing deployment velocity.
- Hyperscaler native stack substitution:AWS GuardDuty, Azure Defender, and Google Cloud Security Command Center absorb budget that might otherwise flow to independent software vendors.
- FedRAMP authorization friction:The 12-18 month timeline for JAB or agency ATO approval blocks smaller vendors from federal market access and concentrates supply among incumbent providers.
Strategic Opportunities
- Critical infrastructure operator gap:Water utilities and regional power authorities lag federal agencies in zero-trust implementation, presenting first-mover advantage for vendors with industrial control system expertise.
- Confidential computing convergence:AMD SEV-SNP and Intel TDX integration with Kubernetes is electrifying hardware-rooted attestation for sensitive government workloads.
- Managed detection and response channel:Healthcare providers facing staffing shortages increasingly outsource security operations center functions to specialized service providers with healthcare compliance expertise.
Industry Challenges
- Legacy hypervisor integration complexity:Organizations running mixed VMware vSphere, Microsoft Hyper-V, and KVM environments struggle to enforce consistent policy across disparate virtualization layers.
- Continuous monitoring certification burden:FedRAMP Rev. 5 requirements for monthly vulnerability scanning and annual penetration testing impose operational overhead that smaller contractors struggle to sustain.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | United States Virtualization Security Market |
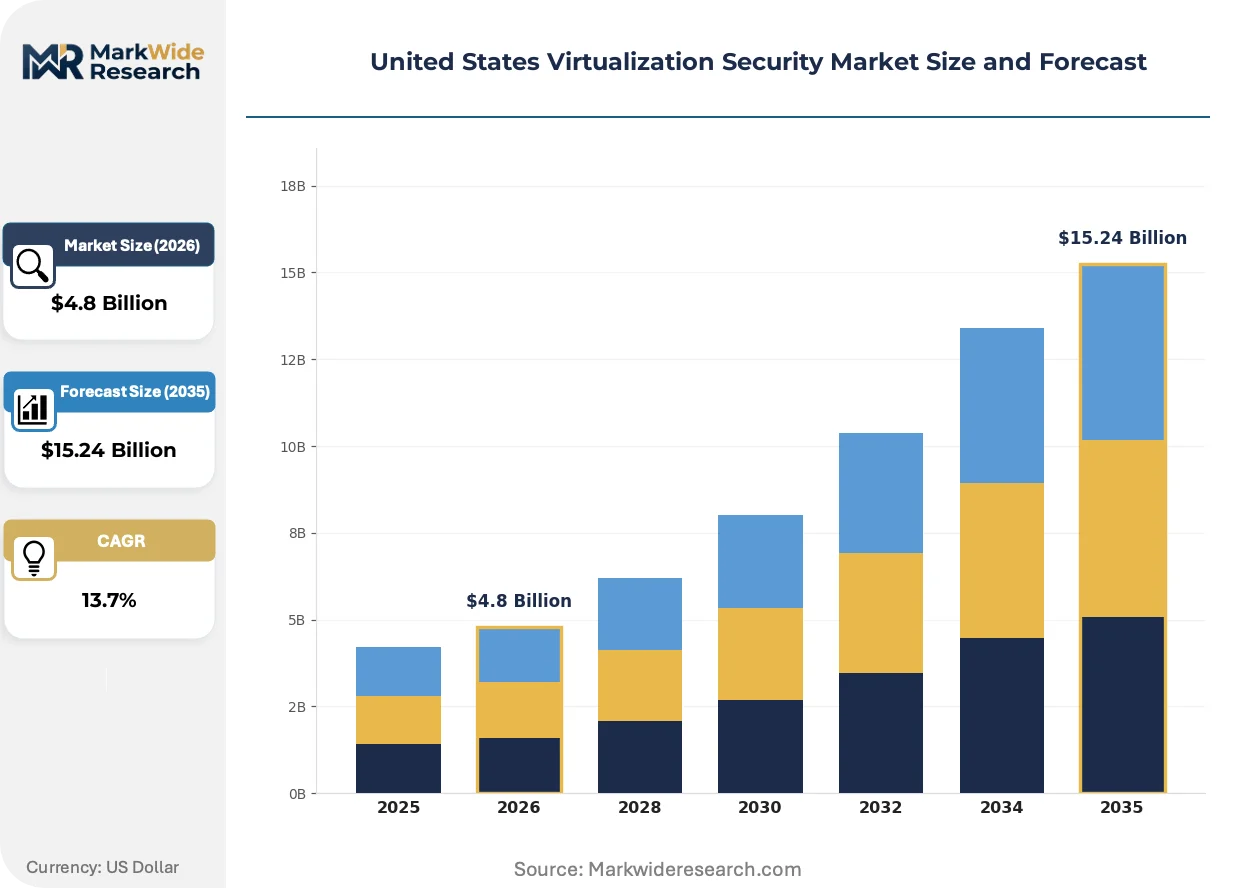
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $15.24 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, On-Premises Security Type: Endpoint Protection, Network Security, Application Security, Data Security End User: Healthcare Providers, Financial Institutions, Educational Organizations, Government Agencies Service Type: Managed Services, Professional Services, Consulting Services, Integration Services |
| Companies Covered | VMware Inc., Trend Micro Incorporated, Cisco Systems, Inc., Microsoft Corporation, Juniper Networks, Inc., Fortinet, Inc., Sophos Ltd., Palo Alto Networks, Inc., Check Point Software Technologies Ltd., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
United States Virtualization Security Market Evolving Landscape
Workload protection is migrating from perimeter defenses toward kernel-embedded controls as hardware-assisted attestation matures. Three developments are compressing competitive positioning.
Confidential computing is electrifying trust boundaries for sensitive federal and financial workloads. AMD Secure Encrypted Virtualization-Secure Nested Paging and Intel Trust Domain Extensions enable memory encryption that isolates virtual machines from hypervisor compromise. Defense contractors handling CUI are adopting these technologies fastest, with DISA publishing implementation guides. This hardware-rooted security is compressing the addressable market for traditional agent-based monitoring tools.
FedRAMP authorization automation is reshaping vendor economics. The GSA's FedRAMP 20x initiative aims to cut authorization timelines through standardized control inheritance and automated evidence collection. Cloud service providers achieving this streamlined path gain disproportionate access to civilian agency contracts. The policy shift most benefits vendors with existing agency sponsorships and mature continuous monitoring pipelines.
Agentless vulnerability scanning is displacing endpoint-heavy approaches in containerized environments. Security teams at SaaS providers and fintechs favor sidecar-based inspection that avoids kernel module installation. This preference favors vendors with native cloud integrations over those requiring privileged access. The behavioral shift is most visible in Northern Virginia's defense contractor corridor, where CISOs prioritize deployment velocity over deep host instrumentation.
United States Virtualization Security Market Segmentation
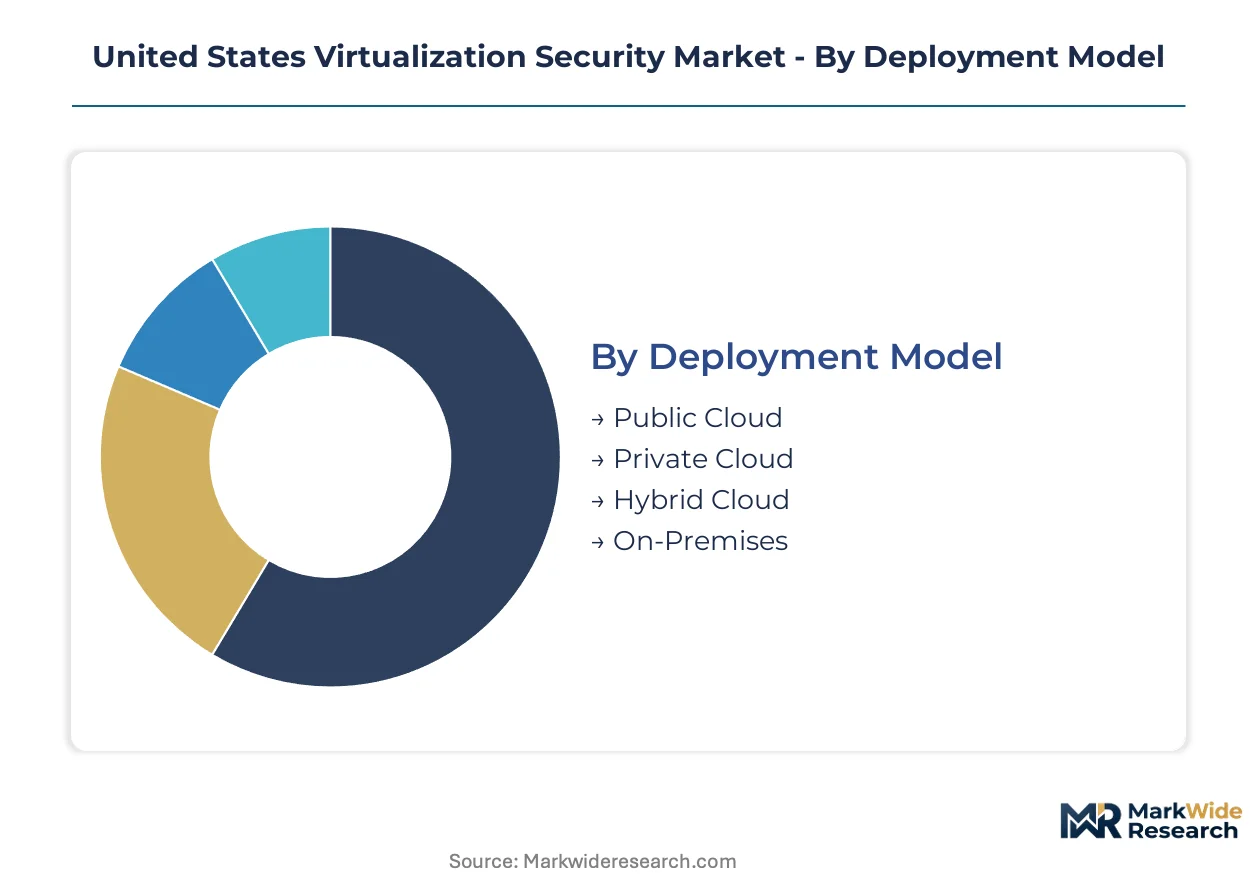
Virtualization security procurement patterns diverge sharply across deployment architectures and compliance mandates. Federal buyers prioritize authorization-ready solutions while healthcare providers optimize for HIPAA-aligned workload isolation. Understanding these segment boundaries reveals where vendor specialization commands premium pricing versus where commoditization pressures dominate.
Deployment Model:
Volume concentrates in split-environment configurations where sovereign data requirements collide with cloud agility demands. Premium pricing attaches to architectures satisfying FedRAMP authorization without sacrificing operational flexibility.
- Hybrid Cloud:Workloads straddle classified government enclaves and commercial hyperscaler infrastructure. Northern Virginia's data center corridor hosts the densest concentration of these deployments as defense contractors process CUI alongside scalable analytics. Federal zero-trust mandates compress procurement timelines for vendors with existing agency sponsorships.
- Public Cloud:Native security stacks from AWS, Azure, and Google absorb budget that independent software vendors once captured. Financial services firms running containerized microservices favor agentless scanning tools that avoid kernel module installation. DISA's cloud security requirements guide shapes implementation patterns.
- Private Cloud:Air-gapped environments serving intelligence community workloads demand hardware-rooted attestation. AMD SEV-SNP and Intel TDX integration commands substantial investment from defense contractors.
- On-Premises:Legacy VMware vSphere and Microsoft Hyper-V estates persist in state government and critical infrastructure operators with limited cloud migration budgets.
Mature deployment sits with On-Premises virtualization in state and local government. Newer deployment is concentrated in Hybrid Cloud architectures among federal civilian agencies.
Security Type:
Application layer protection commands the steepest growth trajectory as microservices architectures multiply attack surfaces. Network security retains the largest revenue pool due to east-west traffic inspection requirements in containerized environments.
- Network Security:Software-defined micro-segmentation monitors lateral movement between pods in Kubernetes clusters. Financial services CISOs in Northern Virginia prioritize deployment velocity over deep host instrumentation for these controls. Palo Alto Networks and Fortinet compete aggressively for this segment through virtual appliance integration.
- Endpoint Protection:Kernel-embedded controls displace perimeter defenses as hardware-assisted attestation matures. Healthcare providers encrypt patient data across VMware and Hyper-V deployments to satisfy HHS OCR enforcement. Agentless approaches gain preference where privileged access creates compliance friction.
- Application Security:Sidecar-based inspection in service meshes addresses vulnerability scanning without container modification. SaaS providers favor this lightweight approach for continuous compliance monitoring.
- Data Security:Encryption-at-rest and confidential computing integration protect sensitive government workloads from hypervisor compromise.
Established procurement patterns dominate Endpoint Protection in healthcare. Application Security represents the fastest-climbing investment category among fintech and SaaS providers.
End User:
Government agencies generate the most concentrated demand for FedRAMP-authorized solutions, while healthcare providers face acute staffing shortages that push spending toward managed service models.
- Government Agencies:OMB M-22-09 deadlines compress procurement cycles for zero-trust architectures. Civilian and defense buyers mandate continuous monitoring and encrypted data-at-rest for cloud workload protection. GSA's FedRAMP 20x initiative reshapes vendor economics through streamlined authorization paths.
- Healthcare Providers:HIPAA Security Rule enforcement drives hospital systems toward outsourced security operations centers. Electronic health record virtualization creates sustained demand for workload isolation across mixed VMware and Hyper-V environments.
- Financial Institutions:Containerized microservices architectures generate explosive demand for east-west traffic inspection. Regional banks lag larger institutions in zero-trust implementation maturity.
- Educational Organizations:Research universities with federal grant obligations adopt NIST SP 800-207 guidance for protecting sensitive research data.
Standardized procurement dominates Government Agencies. Educational Organizations show the most variable deployment maturity across institutional types.
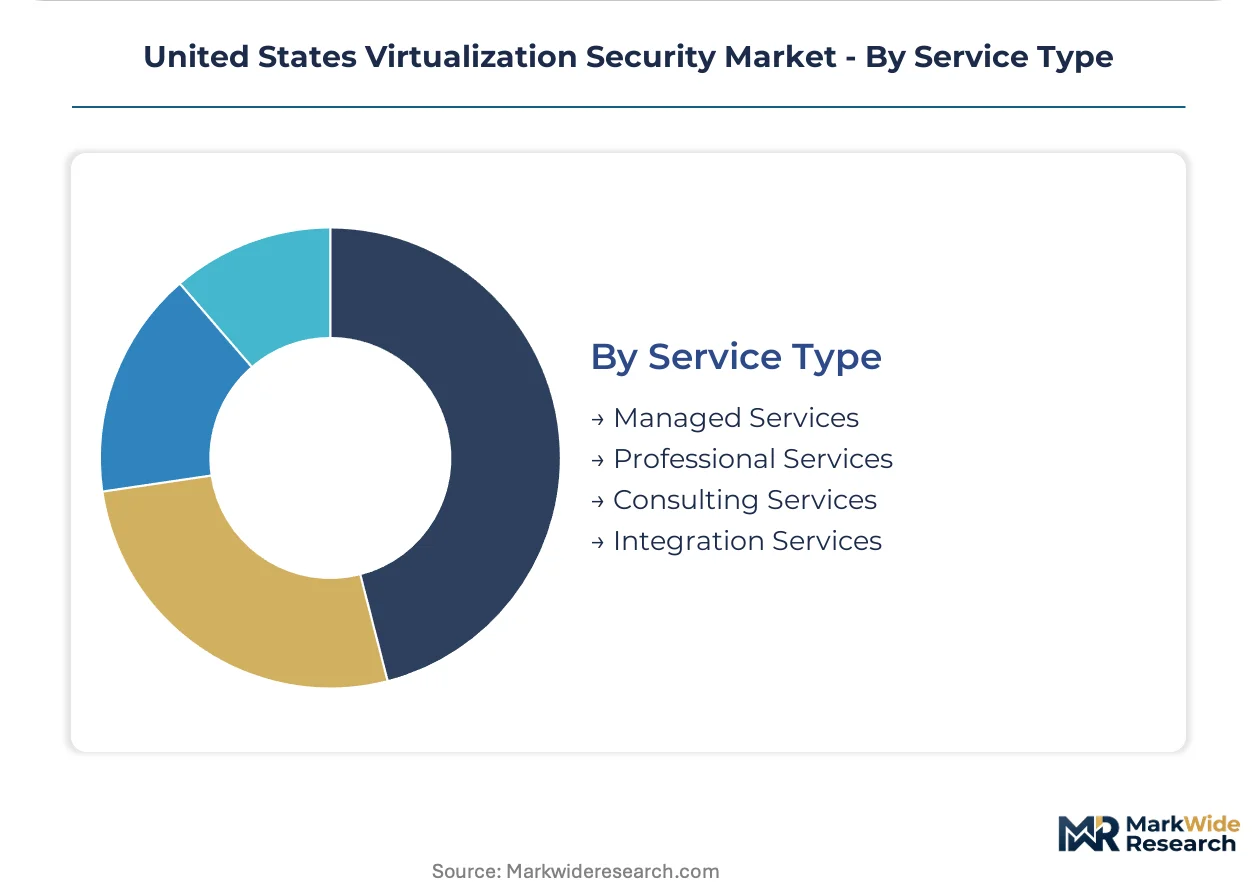
Service Type:
Margin concentration favors ongoing operational relationships over one-time implementation engagements. Healthcare and government buyers facing certified cloud security architect shortages increasingly outsource security operations center functions.
- Managed Services:Specialized providers with healthcare compliance expertise capture disproportionate margin share. Continuous monitoring, threat detection, and incident response are delivered as subscription offerings. State government budgets strain under premium salaries for in-house security architects.
- Professional Services:Implementation and configuration support for zero-trust architectures commands premium pricing during federal fiscal year procurement surges. FedRAMP authorization preparation represents a specialized sub-segment.
- Consulting Services:Risk assessment and compliance gap analysis guide architecture decisions before vendor selection. Defense contractors handling CUI seek confidential computing implementation guidance.
- Integration Services:Legacy hypervisor consolidation across mixed VMware, Hyper-V, and KVM environments creates project-based demand for policy unification.
Recurring revenue concentration sits with Managed Services. Integration Services show the most project-to-project revenue volatility.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Northern Virginia's data center corridor concentrates federal cloud procurement through tax-advantaged enterprise zones. State-level incentives in Texas and California anchor secondary clusters serving defense contractors and healthcare systems.
Northern Virginia
Defense contractors process controlled unclassified information alongside scalable analytics workloads. NIST SP 800-207 zero-trust mandates compress procurement cycles for vendors with existing agency sponsorships. Loudoun County hosts the densest concentration of hyperscaler facilities serving civilian and classified government workloads.
Texas
Financial institutions deploy containerized microservices architectures requiring east-west traffic inspection. State procurement frameworks prioritize FedRAMP-authorized solutions for hybrid cloud deployments. Dallas-Fort Worth anchors banking sector virtualization security spending with specialized managed service providers.
California
SaaS providers favor agentless vulnerability scanning to avoid kernel module installation friction. HIPAA Security Rule enforcement drives hospital systems toward outsourced security operations centers. San Francisco Bay Area fintechs lead adoption of confidential computing for sensitive payment processing workloads.
Greater Boston
Research universities with federal grant obligations implement NIST SP 800-207 guidance for protecting sensitive research data. Massachusetts state contracts mandate continuous monitoring for virtualized electronic health record systems. Cambridge-based defense technology firms integrate hardware-rooted attestation for CUI environments.
Pacific Northwest
Cloud-native enterprises balance AWS native security stacks against independent software vendor solutions. Washington state government agencies face staffing shortages pushing spending toward managed detection and response channels. Seattle's enterprise software corridor generates demand for Kubernetes-integrated workload protection.
United States Virtualization Security Market Competitive Landscape
Branded specialists and contract manufacturers split share differently across segments, with established platform vendors commanding federal procurement while niche players capture healthcare compliance verticals. The vendor landscape consolidates around three strategic archetypes: hypervisor-embedded security providers, multi-cloud workload protection platforms, and managed security service operators. M&A activity concentrates on zero-trust architecture capabilities and confidential computing integration. Strategic partnerships with hyperscalers determine access to public cloud deployment pipelines.
Within the platform-embedded tier, VMware Inc. and Microsoft Corporation occupy positions reflecting their underlying virtualization infrastructure dominance. Palo Alto Networks, Inc. sits within the multi-cloud workload protection segment alongside Fortinet, Inc., with both representing approaches that integrate networking policy enforcement across hybrid estates. These three exemplify how vendor positioning flows from foundational infrastructure control rather than standalone security feature sets.
| Leading Market Players |
|---|
| VMware Inc. |
| Trend Micro Incorporated |
| Cisco Systems, Inc. |
| Microsoft Corporation |
| Juniper Networks, Inc. |
| Fortinet, Inc. |
| Sophos Ltd. |
| Palo Alto Networks, Inc. |
| Check Point Software Technologies Ltd. |
| Others |
Value Network & Pricing Analysis
Federal civilian and defense agencies concentrating procurement through FedRAMP-authorized channels sustain premium pricing for vendors with existing agency sponsorships, compressing budget elasticity for independent software vendors lacking streamlined authorization paths. Subscription-based SaaS tiers dominate commercial transactions while project-based professional services capture surge pricing during federal fiscal year procurement windows.
Pricing Analysis
Short lead-time premiums attach to vendors with pre-positioned agency authorizations as OMB M-22-09 deadlines compress procurement cycles. Three-tier pricing structure across FedRAMP-authorized premium, standard commercial, and economy self-service levels differentiates market access. Pricing pressure stems from hyperscaler native security stacks absorbing budget that independent software vendors once captured. State government buyers exhibit acute price sensitivity due to certified cloud security architect salary premiums, while defense contractors demonstrate reduced elasticity for hardware-rooted attestation solutions.
Supply Chain Analysis
Dual-sourcing requirements from DISA and civilian agencies mandate multi-vendor qualification for hypervisor-embedded security components, preventing single-supplier concentration. Software development concentrates in the United States, India, and Israel, with hardware-rooted trust anchors sourcing from Taiwan and South Korea semiconductor foundries. Raw material dependencies include silicon wafers, specialized encryption processors, and trusted platform modules. Single-source vulnerability in confidential computing hardware exposes supply chains to geopolitical disruption. Distribution runs through authorized federal resellers and hyperscaler marketplaces serving Northern Virginia's data center corridor.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Certified cloud security architect scarcity constrains deployment velocity across federal and healthcare segments, propping pricing power for vendors with pre-qualified implementation partnerships. Capacity bottlenecks in FedRAMP authorization pipelines sustain margin premiums for incumbents with streamlined JAB paths.
For Market Incumbents: Deploy continuous monitoring pipeline automation to compress operational overhead from FedRAMP Rev. 5 monthly vulnerability scanning and annual penetration testing requirements. Fortify position against hyperscaler native stack substitution by deepening hardware-rooted attestation integration with AMD SEV-SNP and Intel TDX technologies. Channel control through authorized federal resellers limits emerging competitor access to defense contractor procurement channels. For New Entrants and Emerging Players: Critical infrastructure operators lag federal agencies in zero-trust implementation maturity, presenting accessible entry points for vendors with industrial control system expertise. Water utilities and regional power authorities represent the most penetrable segment due to limited cloud migration budgets and compliance staffing shortages. Go-to-market execution through managed detection and response channel partnerships bypasses direct certification barriers while capturing recurring revenue streams. For Investors and Strategic Acquirers: The window for entry favors platforms with confidential computing integration and existing healthcare compliance expertise. Long-term viability hinges on sustained differentiation against deepening hyperscaler native security portfolios. Acquisition targets should demonstrate FedRAMP agency sponsorship momentum or specialized industrial control system security capabilities. Deviation in GSA's FedRAMP 20x initiative implementation timeline would shift authorization economics materially.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Streamlining | GSA's 20x initiative compresses vendor access timelines for civilian agency contracts. |
| Confidential Computing Integration | AMD SEV-SNP and Intel TDX embedding differentiates hardware-rooted trust offerings. |
| Managed Detection and Response Expansion | Healthcare provider staffing shortages drive outsourced security operations center demand. |
| Critical Infrastructure Vertical Penetration | Water utilities and power authorities present underdeveloped zero-trust implementation opportunities. |
| Hyperscaler Marketplace Presence | AWS, Azure, and Google Cloud marketplaces determine public cloud deployment pipeline access. |
Research Methodology
Multi-period observation of federal procurement patterns, FedRAMP authorization timelines, and hyperscaler security stack evolution anchored the trend analysis, supplemented by interviews with CISOs at defense contractors, healthcare system IT directors, federal agency procurement officers, and cloud security architects at managed service providers. Secondary validation drew from DISA cloud security requirements guides, GSA FedRAMP authorization databases, HHS OCR enforcement actions, NIST SP 800-207 implementation documentation, and SEC filings of publicly traded cybersecurity vendors. Bottom-up deployment model sizing triangulated against top-down federal IT spending allocations.
Segment-weighting across deployment architecture, security type, end-user vertical, and service model dimensions structured the analytical framework across the projection horizon. CAGRs were derived from deployment velocity assumptions tied to OMB M-22-09 deadline compliance, confidential computing hardware availability, and certified security architect labor market constraints. Industry-specific forecast inputs included federal fiscal year procurement surge patterns, HIPAA Security Rule enforcement intensity, and hyperscaler native security portfolio expansion trajectories.
Revisions become necessary when FedRAMP authorization timeline compression stalls, confidential computing hardware supply disruptions materialize, or hyperscaler native security stacks achieve functional parity with independent vendor offerings. Deviation in certified cloud security architect labor market tightness would shift deployment velocity assumptions materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Romania Cybersecurity Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
North America IoT Security Market
Cybersecurity
Education Data Security Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Data-Centric Security Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Switzerland Cybersecurity Market
Cybersecurity
South Africa Cybersecurity Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market