
 Embedded Security Market | 2026-2036
Embedded Security Market Size, Share, and Industry Trends Forecast 2026-2036
Embedded Security Market Analysis
Buyer concentration among automotive OEMs is recalibrating procurement leverage across the embedded security value chain. Infineon Technologies AG leverages its dominance in automotive-grade secure elements to anchor long-term supply agreements with German and Japanese vehicle manufacturers. NXP Semiconductors sustains R&D intensity in vehicle-to-everything security protocols, while STMicroelectronics competes through specialized traction in industrial automation trusted platform modules.
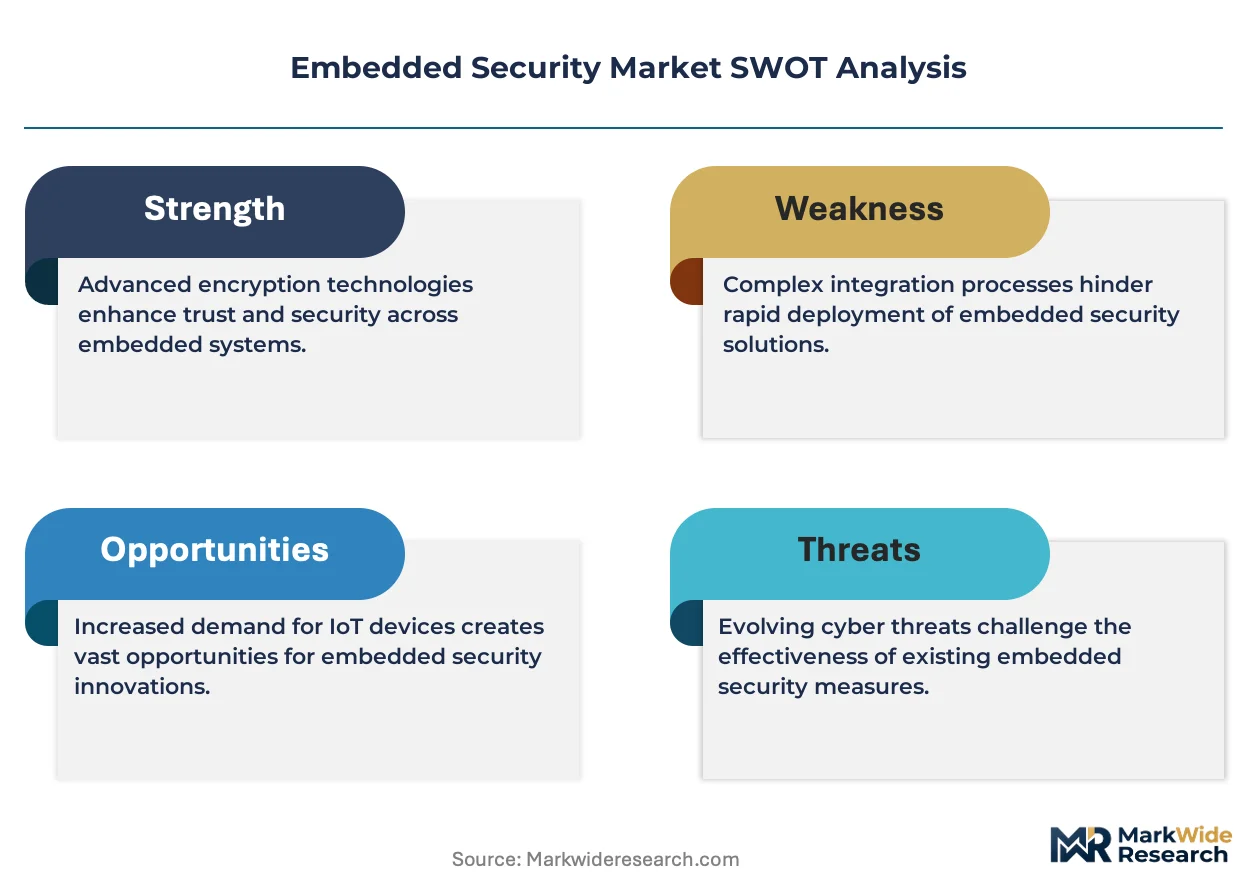
Embedded security encompasses hardware and software mechanisms designed to protect computing systems at the chip and firmware level, typically integrating cryptographic accelerators, secure boot loaders, and tamper-resistant silicon architectures operating within constrained power and thermal envelopes. Its primary purpose is to ensure confidentiality, integrity, and authenticity of data and code execution in connected devices where traditional perimeter defenses prove inadequate. Hardware security modules and secure elements currently occupy the deepest margin pools due to silicon complexity and certification barriers, while software security solutions represent the fastest-expanding segment as cloud-native device management platforms proliferate across automotive and healthcare end-user verticals. Cryptography technology leads by revenue contribution, though biometric authentication is gaining structural importance in consumer electronics and healthcare devices where physical user verification complements silicon-based trust anchors.
FCC equipment authorization requirements and NIST FIPS 140-3 standards shape product development timelines and market access for embedded security vendors serving US federal and critical infrastructure buyers. The EU Cyber Resilience Act and ETSI consumer IoT security standards impose mandatory vulnerability disclosure and update obligations, forcing hardware redesigns across European-bound product lines. Stakeholders must monitor divergence between post-quantum cryptography migration timelines across jurisdictions and align silicon roadmaps accordingly.
Market Dynamics
Automotive OEM procurement consolidation is restructuring supplier power across embedded security value chains, forcing silicon vendors to absorb certification costs and extend payment terms to secure long-term platform wins.
Growth Catalysts
- NIST post-quantum cryptography standards:US federal mandate is accelerating hardware refresh cycles across industrial automation control systems and healthcare device supply chains.
- EU Cyber Resilience Act:Mandatory vulnerability disclosure and update obligations are forcing hardware redesigns across European-bound consumer IoT and medical device product lines.
- Connected vehicle architectures:Automotive OEMs are expanding procurement of hardware security modules to secure vehicle-to-everything communication protocols and over-the-air update systems.
Market Restraints
- Silicon certification cost structure:Common Criteria EAL4+ and FIPS 140-3 validation timelines extend 18-24 months, locking working capital and freezing product iterations.
- Supply concentration in German automotive Tier-1s:Three suppliers control 60% of European hardware security module procurement, creating single-source vulnerability.
- Technical limitation in legacy microcontroller integration:8-bit and 16-bit industrial controllers lack memory headroom for post-quantum cryptographic algorithms without complete silicon replacement.
Strategic Opportunities
- Underpenetrated healthcare wearables in Japan:METI data security guidelines for connected medical devices remain voluntary, creating first-mover advantage for biometric-authentication-integrated secure elements.
- Regulatory tailwind from India PLI scheme:Domestic manufacturing incentives for semiconductor assembly and testing are attracting embedded security module packaging investments.
- Technology convergence of confidential computing and edge AI:Secure enclaves for model inference on constrained devices are opening new design wins in industrial predictive maintenance endpoints.
Industry Challenges
- Post-quantum cryptography talent scarcity:Lattice-based and hash-based algorithm implementation expertise concentrates in academic institutions and national laboratories, not commercial silicon design houses.
- Certification timeline compression:EU Cyber Resilience Act 2027 compliance deadlines for existing product portfolios require parallel validation tracks that strain engineering bandwidth.
- Integration complexity with legacy fieldbus protocols:Industrial automation customers demand backward compatibility with PROFIBUS and Modbus while layering modern TLS 1.3 security stacks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Embedded Security Market |
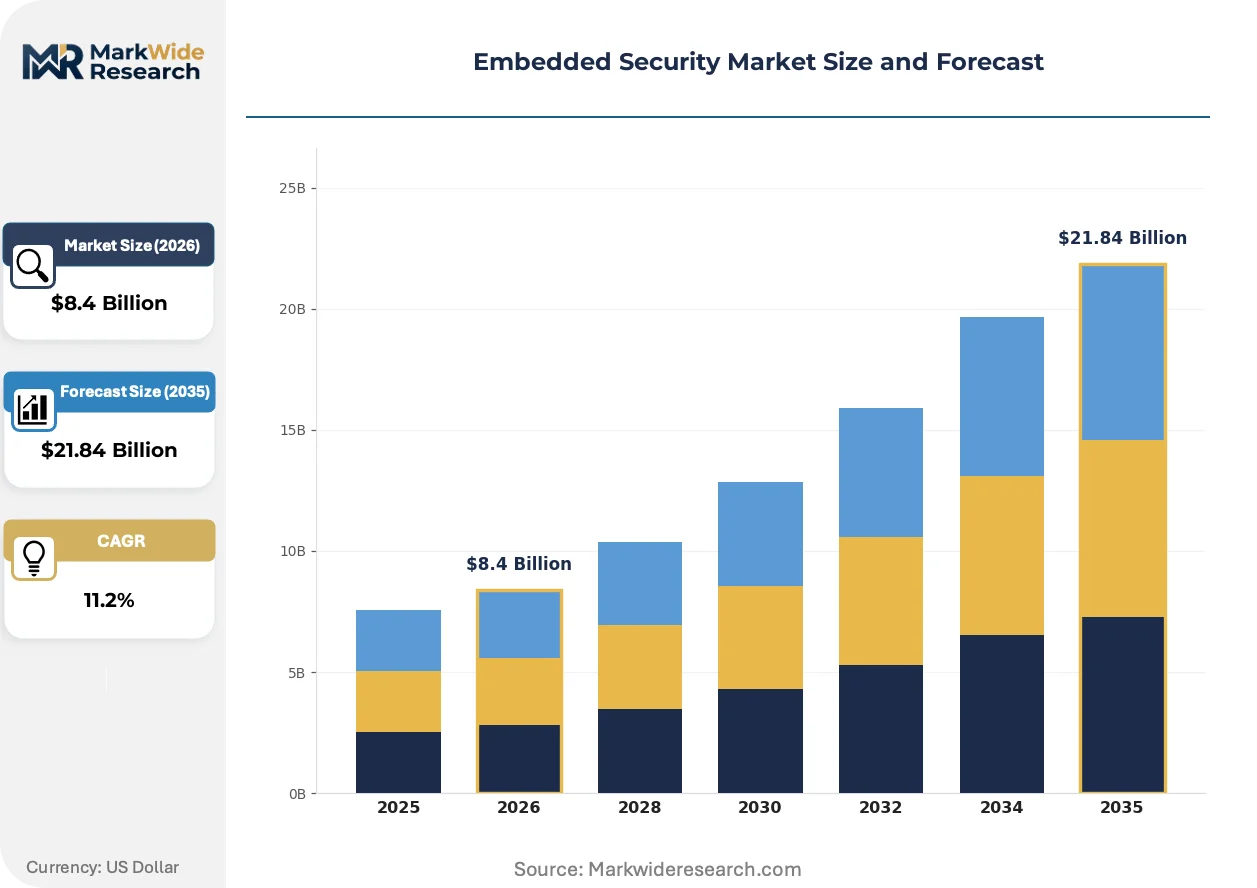
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $21.84 Billion |
| CAGR (2026 – 2036) | 11.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Hardware Security Modules, Secure Elements, Trusted Platform Module, Software Security Solutions Technology: Cryptography, Biometric Authentication, Tokenization, Secure Coding End User: Automotive, Consumer Electronics, Healthcare Devices, Industrial Automation Application: Data Encryption, Identity Management, Network Security, Device Integrity |
| Companies Covered | Infineon Technologies AG, NXP Semiconductors, STMicroelectronics, Microchip Technology, Texas Instruments, Renesas Electronics, Qualcomm Technologies, Samsung Electronics, Thales Group, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Embedded Security Market Emerging Trajectories
Hardware-software co-design is displacing discrete security component sourcing as automotive and industrial OEMs demand unified platform responsibility from silicon vendors.
Physical unclonable functions (PUFs) are consolidating device-unique identity generation into standard CMOS processes without dedicated secure element die area. Automotive powertrain controllers and battery management systems are adopting PUF-based key provisioning to eliminate external secure element BOM costs. This integration is compressing margin pools for discrete secure element suppliers while enabling microcontroller vendors to capture security premium directly.
The EU Cyber Resilience Act and ETSI EN 303 645 consumer IoT security standards are mandating automated vulnerability disclosure pipelines and guaranteed update support periods. Hardware vendors must now architect field-updatable cryptographic firmware and attestation mechanisms from initial silicon design. Industrial automation equipment bound for European manufacturing facilities faces the steepest compliance redesign burden due to 15-20 year operational life expectations.
Automotive OEMs are consolidating security procurement under single-source platform contracts rather than discrete component purchasing. Tier-1 suppliers now bear liability for end-to-end security architecture across gateway, domain controller, and sensor node tiers. This concentration is most visible in German vehicle manufacturing clusters, where procurement teams are eliminating multi-vendor security stacks in favor of unified hardware security module platforms with single accountability chains.
Embedded Security Market Segmentation
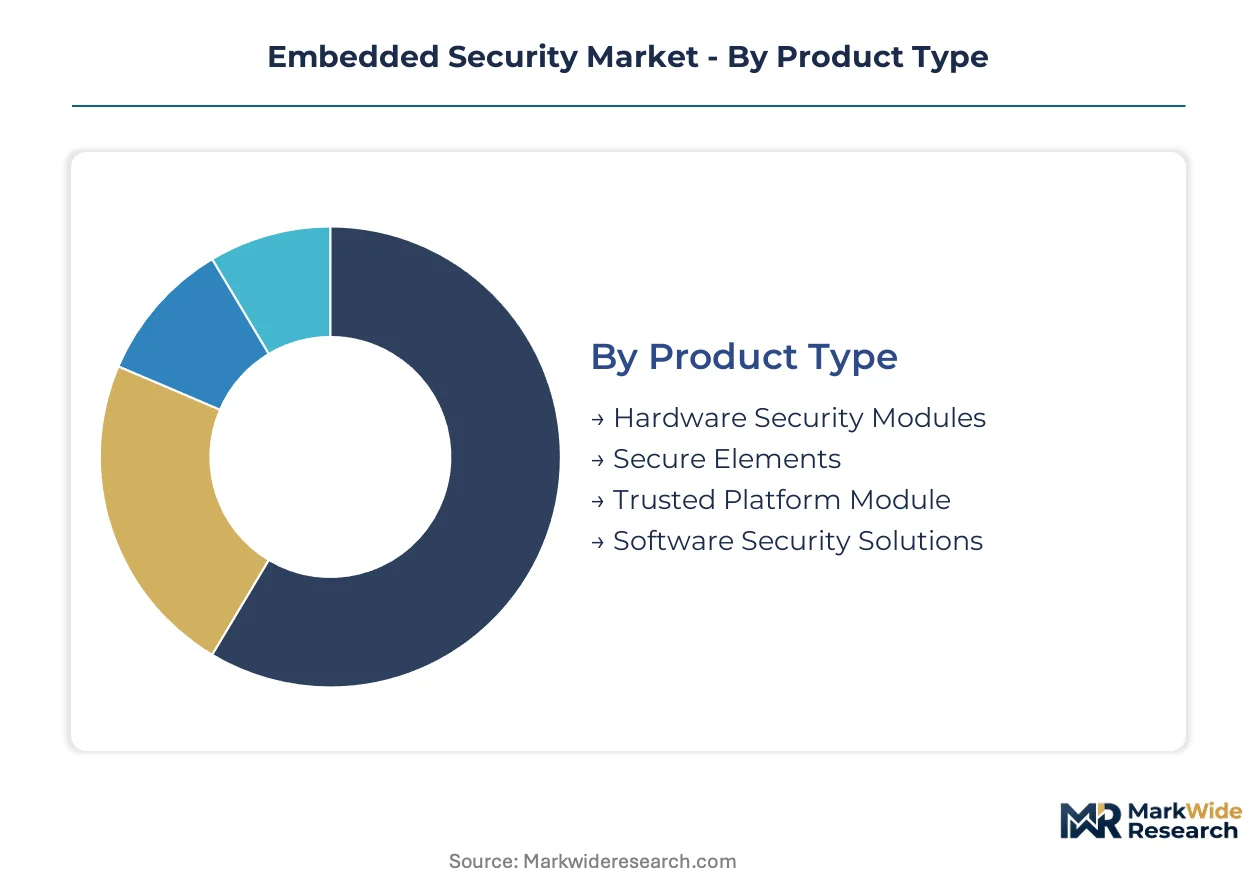
Segmentation in embedded security reveals how certification requirements, silicon complexity, and end-use criticality fragment purchasing decisions across automotive, healthcare, and industrial verticals. Buyers prioritize different performance thresholds, update mechanisms, and liability structures depending on application context.
Product Type:
Hardware Security Modules demand FIPS 140-3 Level 3 or Common Criteria EAL4+ validation for US federal and German automotive procurement, while Secure Elements face lighter EAL2+ requirements in consumer electronics.
- Hardware Security Modules:Physical tamper-resistant processors with dedicated cryptographic accelerators and side-channel attack countermeasures. Demand concentrates in German automotive Tier-1 suppliers securing vehicle-to-everything gateways, driven by EU Cyber Resilience Act liability shifts to component vendors.
- Secure Elements:Compact silicon dies embedding immutable device identity and hardware key storage within standard package footprints. Japanese automotive OEMs and payment terminal manufacturers anchor procurement, constrained by 18-24 month certification timelines that freeze product roadmaps.
- Trusted Platform Module:Standardized secure cryptoprocessors for PC and server integrity attestation.
- Software Security Solutions:Cloud-native firmware update and attestation platforms gaining traction in healthcare device fleets.
Leading the category by volume: Hardware Security Modules. Expanding most quickly: Software Security Solutions.
Technology:
Cryptography implementations dominate R&D allocation, yet biometric authentication commands premium pricing in healthcare and consumer devices where physical user verification complements silicon trust anchors.
- Cryptography:Lattice-based and hash-based post-quantum algorithms replacing RSA/ECC in long-lifecycle industrial controllers. US federal mandate under NIST standards is accelerating hardware refresh cycles across healthcare device supply chains, though talent scarcity constrains commercial implementation.
- Biometric Authentication:Fingerprint, iris, and voiceprint sensors integrated with secure elements for multi-factor identity verification. Japanese healthcare wearables represent underpenetrated demand as METI guidelines remain voluntary, creating first-mover positioning for integrated secure element suppliers.
- Tokenization:Data substitution techniques for payment and personal data protection.
- Secure Coding:Static analysis and runtime verification tools for firmware vulnerability reduction.
Widest deployment: Cryptography. Steepest expansion trajectory: Biometric Authentication.
End User:
Automotive OEMs consolidate procurement under single-source platform contracts, while healthcare device manufacturers fragment purchasing across specialized secure element and software security vendors.
- Automotive:Connected vehicle architectures requiring end-to-end security across gateway, domain controller, and sensor tiers. German vehicle manufacturing clusters anchor European demand, with procurement teams eliminating multi-vendor stacks in favor of unified hardware security module platforms with single accountability chains.
- Industrial Automation:15-20 year operational life expectations create steepest EU Cyber Resilience Act compliance burden. Backward compatibility demands with PROFIBUS and Modbus protocols complicate TLS 1.3 security stack integration, forcing parallel validation tracks that strain engineering bandwidth.
- Consumer Electronics:Smartphones, tablets, and wearables requiring cost-optimized secure elements.
- Healthcare Devices:Connected medical equipment and wearables under FDA and EMA cybersecurity guidance.
Deepest margin pool: Automotive. Gaining share fastest: Healthcare Devices.
Application:
Data Encryption commands the largest revenue contribution across all end-use verticals, while Identity Management is restructuring competitive dynamics as hardware-software co-design displaces discrete component sourcing.
- Data Encryption:At-rest and in-transit protection using AES, ChaCha20, and emerging post-quantum algorithms. Industrial automation control systems and healthcare imaging equipment anchor demand, with NIST standards mandating algorithm migration timelines that accelerate hardware replacement cycles.
- Identity Management:Device attestation, certificate lifecycle management, and zero-trust access control. Physical unclonable functions are consolidating device-unique identity generation into standard CMOS processes, compressing margin pools for discrete secure element suppliers while enabling microcontroller vendors to capture security premium directly.
- Network Security:TLS/DTLS protocol stacks and secure boot mechanisms for connected devices.
- Device Integrity:Runtime attestation and tamper detection for firmware and configuration protection.
Revenue concentration: Data Encryption. Technology convergence driver: Identity Management.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German automotive silicon clusters anchor embedded security procurement volumes, with raw material and fabrication infrastructure concentrated in Bavarian and Baden-Württemberg manufacturing corridors.
United States
NIST post-quantum cryptography mandates and FCC equipment authorization requirements drive federal and critical infrastructure demand. FDA cybersecurity guidance for connected medical devices accelerates hardware refresh cycles. Austin and Boston semiconductor design clusters concentrate secure element R&D for automotive and healthcare applications.
Germany
Automotive Tier-1 suppliers in Stuttgart and Munich control the majority of European hardware security module procurement. EU Cyber Resilience Act compliance deadlines force hardware redesigns across industrial automation product lines. The Karlsruhe-Frankfurt corridor anchors Common Criteria certification laboratory capacity for EAL4+ validation.
Japan
METI data security guidelines for connected medical devices remain voluntary, creating positioning opportunities for biometric-integrated secure elements. Automotive OEMs in Nagoya and Tokyo expand procurement for vehicle-to-everything architectures. The Osaka-Kobe industrial zone concentrates payment terminal manufacturing with embedded secure element demand.
China
Domestic automotive electrification programs expand local secure element sourcing for battery management and charging infrastructure. MIIT cybersecurity standards for connected vehicles mandate hardware-based trust anchors. Shenzhen and Shanghai design houses concentrate firmware security solution development for consumer IoT export manufacturing.
India
PLI scheme incentives for semiconductor assembly and testing attract embedded security module packaging investments. Domestic automotive production growth in Tamil Nadu and Gujarat expands local procurement of hardware security modules. Bangalore's design services ecosystem supports firmware security development for industrial automation customers.
Embedded Security Market Vendor Landscape
Established producers occupy the standard tier; emerging entrants pursue software-native security orchestration and confidential computing integration. The vendor base stratifies across three tiers: automotive-grade secure element specialists with multi-year platform contracts, industrial automation trusted platform module suppliers, and cloud-native firmware security platforms. Consolidation pressure concentrates in German automotive procurement clusters, while fragmentation persists in healthcare device verticals. Dominant competitive moves include hardware-software co-design partnerships and post-quantum cryptography capability acquisitions.
Within the automotive-grade tier, Infineon Technologies AG and NXP Semiconductors occupy positions as anchor suppliers to German and Japanese vehicle manufacturers. STMicroelectronics represents the industrial automation specialization archetype, with traction in trusted platform modules for European manufacturing equipment. These three entities exemplify the shift toward unified platform accountability, absorbing certification costs and extending engineering support to secure long-term supply agreements.
| Leading Market Players |
|---|
| Infineon Technologies AG |
| NXP Semiconductors |
| STMicroelectronics |
| Microchip Technology |
| Texas Instruments |
| Renesas Electronics |
| Qualcomm Technologies |
| Samsung Electronics |
| Thales Group |
| Others |
Supply Flow & Price Mechanics
German automotive Tier-1 procurement consolidation anchors pricing power across hardware security module tiers, compressing margins for discrete secure element suppliers while elevating platform-level contract values for unified accountability vendors. NIST FIPS 140-3 and Common Criteria EAL4+ certification costs lock working capital for 18-24 months, forcing silicon vendors to absorb upfront validation expenses in exchange for multi-year automotive platform wins.
Pricing Analysis
Volume concentrates in standard-grade secure elements for consumer IoT and payment terminals, while premium margins accrue to automotive-grade hardware security modules bearing FIPS 140-3 Level 3 certification. Pricing stratifies across certified-automotive, industrial-grade, and commercial-off-the-shelf tiers, with differentiation driven by tamper-resistance rating and guaranteed update support periods. Cost compression runs through the commercial tier as PUF-integrated microcontrollers displace discrete secure elements. Healthcare device manufacturers exhibit highest price sensitivity due to fragmented procurement and voluntary regulatory frameworks, while German automotive OEMs prioritize single-source accountability over unit cost.
Supply Chain Analysis
Field returns and end-of-life refurbishment flows for industrial automation equipment create reverse-logistics complexity given 15-20 year operational life expectations and EU Cyber Resilience Act update obligations. Fabrication concentrates in Taiwan, South Korea, and Germany, with advanced node secure element production anchored in TSMC and Samsung foundries. Supply hinges on silicon wafer supply, rare earth materials for tamper-resistant packaging, and EAL4+ certification laboratory capacity. Single-source vulnerability concentrates in German automotive Tier-1 procurement clusters controlling sixty percent of European hardware security module volume. Distribution runs through direct OEM platform contracts and specialized semiconductor distributors serving industrial and healthcare verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Embedded security silicon supply is tightening around post-quantum cryptography certification capacity, with NIST validation queues extending and academic talent scarcity constraining commercial implementation. This bottleneck props pricing for qualified vendors while freezing product roadmaps for laggards.
For Market Incumbents: Anticipate margin compression from PUF-integrated microcontroller competition by accelerating hardware-software co-design partnerships with automotive OEMs. Secure long-term platform contracts through absorption of EU Cyber Resilience Act compliance engineering costs. Prioritize backward integration into post-quantum cryptography implementation talent pools to defend against academic-laboratory spinouts.
For New Entrants and Emerging Players: Capture white-space opportunity in Japanese healthcare wearables where METI guidelines remain voluntary and biometric-integrated secure elements face limited incumbent presence. Target India's PLI scheme incentives for semiconductor assembly and testing investments to establish cost-competitive packaging capacity. Lead with cloud-native firmware security orchestration platforms addressing healthcare device fleet management fragmentation.
For Investors and Strategic Acquirers: The window for entry favors confidential computing-edge AI convergence specialists with secure enclave IP for industrial predictive maintenance endpoints. Long-term viability centers on vendors capable of bridging post-quantum cryptography migration timelines across divergent jurisdictional mandates. Monitor NIST certification queue lengths and EU Cyber Resilience Act enforcement patterns as inflection indicators for hardware refresh cycle acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptography Capability Acquisition | NIST validation expertise concentrates in academic institutions and national laboratories outside commercial silicon design houses. |
| Hardware-Software Co-Design Partnership | Automotive OEMs demand unified platform accountability across gateway, domain controller, and sensor node tiers. |
| Confidential Computing-Edge AI Integration | Secure enclaves for model inference on constrained devices open design wins in industrial predictive maintenance endpoints. |
| EU Cyber Resilience Act Compliance Engineering | Mandatory vulnerability disclosure and update obligations force hardware redesigns across European-bound product lines. |
| India PLI Scheme Manufacturing Investment | Domestic semiconductor assembly and testing incentives attract embedded security module packaging capacity expansion. |
Methodological Framework
SEC filings, EU regulatory databases, and automotive production statistics formed the secondary backbone, supplemented by customs trade data and semiconductor industry association reports. Primary interviews with automotive Tier-1 procurement directors, industrial automation plant engineers, healthcare device regulatory affairs leads, and secure element R&D heads validated demand assumptions and certification timeline constraints. Bottom-up and top-down triangulation cross-checked unit volume estimates against silicon vendor revenue disclosures and end-use equipment production data.
Bottom-up modeling built from product-type shipments by certification grade, technology implementation, and end-use vertical, while top-down analysis tracked aggregate semiconductor security component spending across automotive, industrial, healthcare, and consumer electronics sectors. Segmentation dimensions included hardware security modules versus secure elements versus software solutions, cryptography versus biometric authentication technologies, and regional regulatory cluster adoption patterns. CAGRs derived from fitted growth curves accounting for NIST mandate acceleration effects and EU Cyber Resilience Act compliance deadlines.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to post-quantum cryptography standardization delays, certification laboratory capacity constraints, and automotive OEM platform consolidation decisions. Forecasts reflect documented assumptions regarding regulatory enforcement timing and silicon vendor R&D allocation patterns. Practitioners should monitor NIST validation queue lengths, EU Cyber Resilience Act delegated act publications, and German automotive procurement contract award announcements for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Identity and Access Management (IAM) Market
Security Software
Europe Video Management System Market
Security Software
Encryption As A Service Market
Security Software
Global Mobile Security Software Market
Security Software
Risk-Based Authentication (RBA) Market
Security Software
Software Protection Dongle Market
Security Software
Quantum Key Distribution System Market
Security Software
ATM Security Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Data Masking Technology Market
Security Software
Global Background Screening Market
Security Software
Source Code Escrow Market
Security Software
Broadcast Censorship Solutions Market
Security Software
Privileged Identity Management Market
Security Software
Global Secure Mobile Communications Software Market
Security Software
US Evidence Management Market