
 Global Cyber Threat Intelligence Market | 2026-2036
Global Cyber Threat Intelligence Market Size, Share, and Industry Trends Forecast 2026-2036
Global Cyber Threat Intelligence Market Foresight
The United States is tilting toward cloud-native threat intelligence architectures as federal agencies modernize cyber defenses. Palo Alto Networks leverages integrated network and cloud intelligence to anchor enterprise security stacks. CrowdStrike sustains endpoint detection leadership through its graph-based threat correlation engine. IBM Corporation competes across managed security services with its X-Force threat research division.
Cyber threat intelligence encompasses the collection, processing, and analysis of adversary indicators, tactics, and infrastructure to produce actionable defensive guidance. Platforms ingest structured and unstructured data from open-source feeds, dark web monitoring, and proprietary sensor networks, then apply machine learning and human analyst validation to generate threat actor profiles and predictive risk assessments. Cloud intelligence and threat analytics segments are expanding fastest as organizations migrate workloads to distributed environments and seek behavioral anomaly detection beyond signature-based methods. Network intelligence retains the largest installed base but faces margin compression from commoditized signature feeds, while endpoint intelligence occupies the highest-value integration tier through real-time telemetry fusion with extended detection and response platforms.
The National Institute of Standards and Technology Cybersecurity Framework and SEC cyber disclosure rules in the United States, alongside the EU NIS2 Directive and GDPR breach notification mandates in Europe, are compelling regulated entities to procure certified threat intelligence services with audit-ready documentation trails. ISO 27001 and IEC 62443 standards further shape product certification requirements for industrial control system deployments. Stakeholders must weigh build-versus-buy decisions for in-house threat hunting capabilities against managed detection and response partnerships as adversary tradecraft accelerates.
Market Dynamics
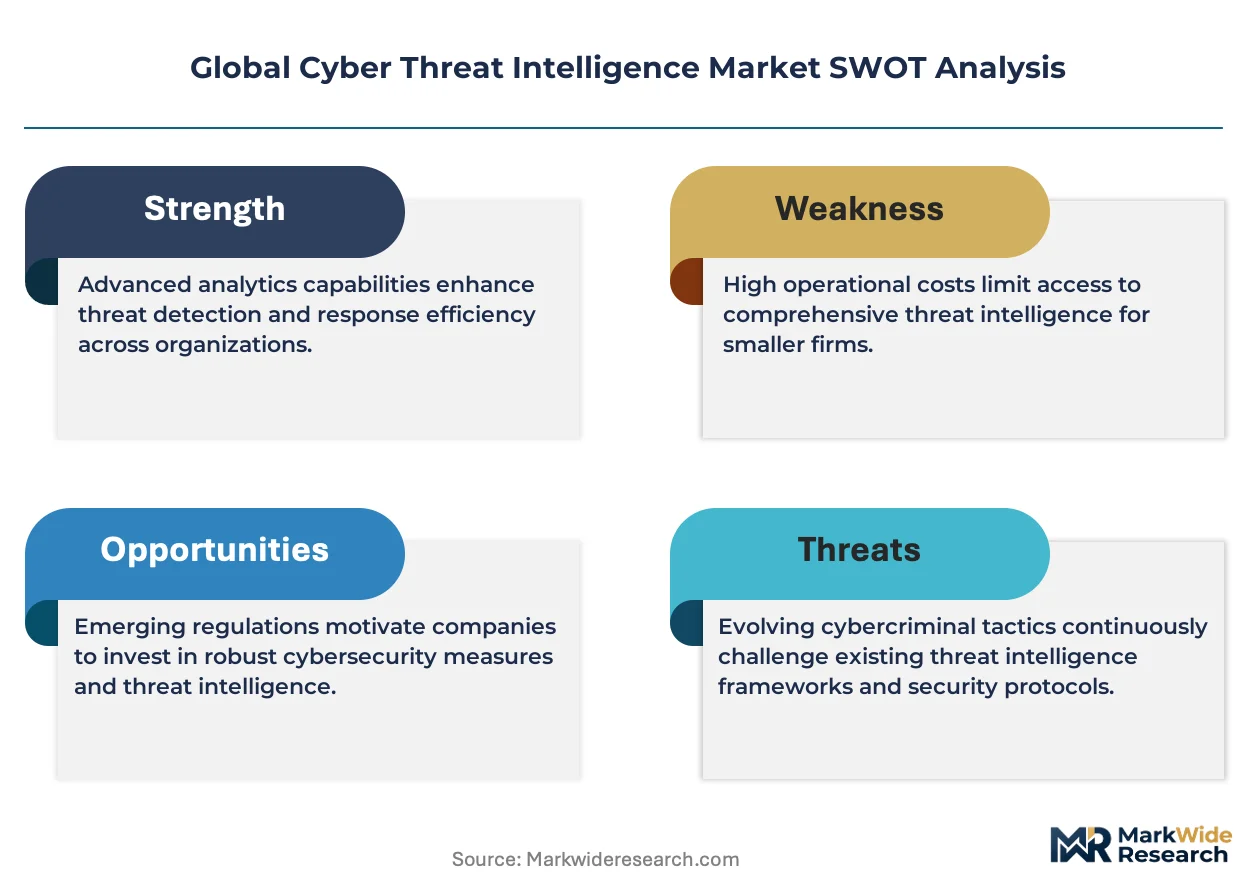
The migration of enterprise workloads to multi-cloud environments is fragmenting attack surfaces and forcing security teams to abandon perimeter-centric defense models. This architectural shift is compressing the window between threat detection and response, elevating real-time intelligence fusion into a core operational requirement.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators across energy, transport, and healthcare must deploy certified threat detection systems with mandatory incident reporting timelines, creating procurement urgency.
- Financial services ransomware exposure:Banks and payment processors are expanding threat intelligence budgets to counter affiliate-based ransomware operations targeting SWIFT infrastructure and treasury systems.
- Behavioral analytics platforms:Machine learning models trained on adversary tradecraft patterns are displacing signature-dependent tools in enterprise security stacks.
Market Restraints
- Skilled analyst scarcity:The shortage of professionals trained in MITRE ATT&CK framework mapping and indicator validation limits platform utilization rates.
- Feed commoditization:Open-source indicator feeds from abuse.ch and MISP instances reduce willingness to pay premium prices for basic signature data.
- Cross-border data friction:GDPR data localization requirements complicate threat intelligence sharing between EU-based SOCs and US-headquartered security vendors.
Strategic Opportunities
- Operational technology convergence:Industrial control system operators in manufacturing and energy seek intelligence platforms that bridge IT and OT visibility gaps.
- Japan's cybersecurity framework:METI guidelines for critical infrastructure protection are mandating threat intelligence integration in utility and railway operators.
- API-native distribution:Security orchestration platforms are consuming threat intelligence through structured APIs rather than portal-based access, enabling embedded workflow integration.
Industry Challenges
- Alert fatigue management:SOC teams struggle to prioritize actionable intelligence from high-volume indicator feeds without automated scoring and contextual enrichment.
- Attribution confidence:Threat actor naming conventions vary across vendors, complicating cross-platform correlation and strategic response coordination.
- Legacy SIEM integration:On-premises security information and event management systems lack native support for STIX/TAXII protocols, requiring costly middleware development.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Cyber Threat Intelligence Market |
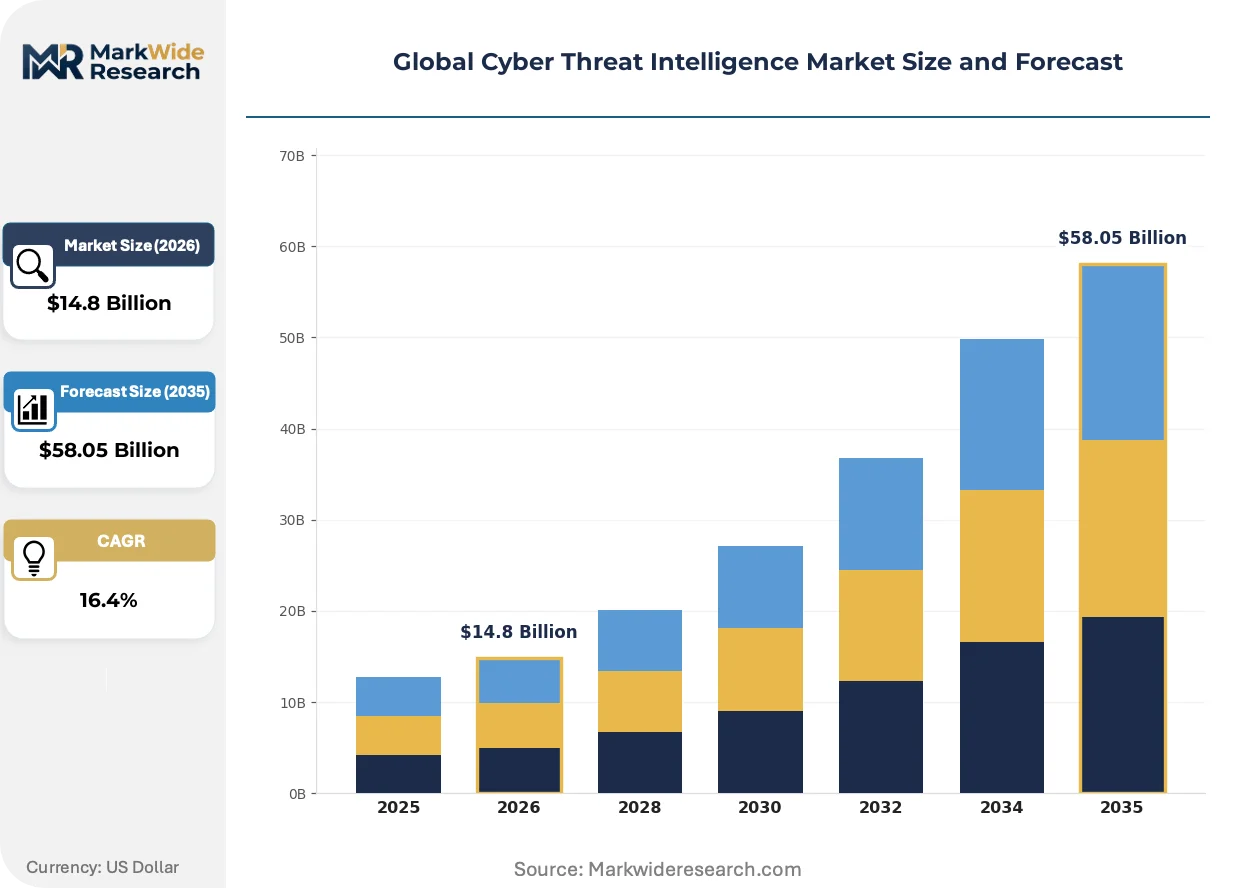
| Market Size in 2026 | $14.8 Billion |
| Market Size in 2035 | $58.05 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Network Intelligence, Endpoint Intelligence, Cloud Intelligence, Threat Analytics, Vulnerability Intelligence Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Security Service Use Case: Fraud Detection, Risk Management, Incident Response, Threat Hunting, Compliance Monitoring Customer Type: Financial Institutions, Telecommunication Providers, Government Agencies, IT Service Providers, Energy Sector |
| Companies Covered | IBM Corporation, Palo Alto Networks, Cisco Systems, CrowdStrike, Microsoft Corporation, Recorded Future, Google (Mandiant), Check Point Software Technology, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Cyber Threat Intelligence Market Shifts & Advancements
Adversary tradecraft automation is compressing the mean-time-to-exploit for newly disclosed vulnerabilities, forcing defensive technology to accelerate detection loop closure. Intelligence platforms are embedding directly into cloud-native security stacks to eliminate latency between signal generation and enforcement action.
Extended detection and response architectures are collapsing the functional separation between endpoint telemetry, network metadata, and cloud audit logs. Financial institutions and defense contractors are deploying these converged platforms to unify threat hunting across hybrid infrastructure. The structural consequence is collapsing standalone threat intelligence portal vendors into acquisition targets for broader security platform providers.
The EU AI Act's risk classification framework for biometric and critical infrastructure applications is mandating algorithmic transparency in automated threat detection systems. Security vendors must document training data provenance and decision logic for high-risk deployments. European critical infrastructure operators are responding by demanding audit-ready intelligence platforms with explainable scoring methodologies.
Security procurement is consolidating around integrated platform contracts rather than point-solution subscriptions. Large enterprises are displacing standalone threat feed vendors with bundled offerings from endpoint and cloud security providers. This concentration is most visible in the United States, where federal procurement vehicles favor FedRAMP-authorized platforms with native intelligence integration over specialized boutique services.
Global Cyber Threat Intelligence Market Segmentation
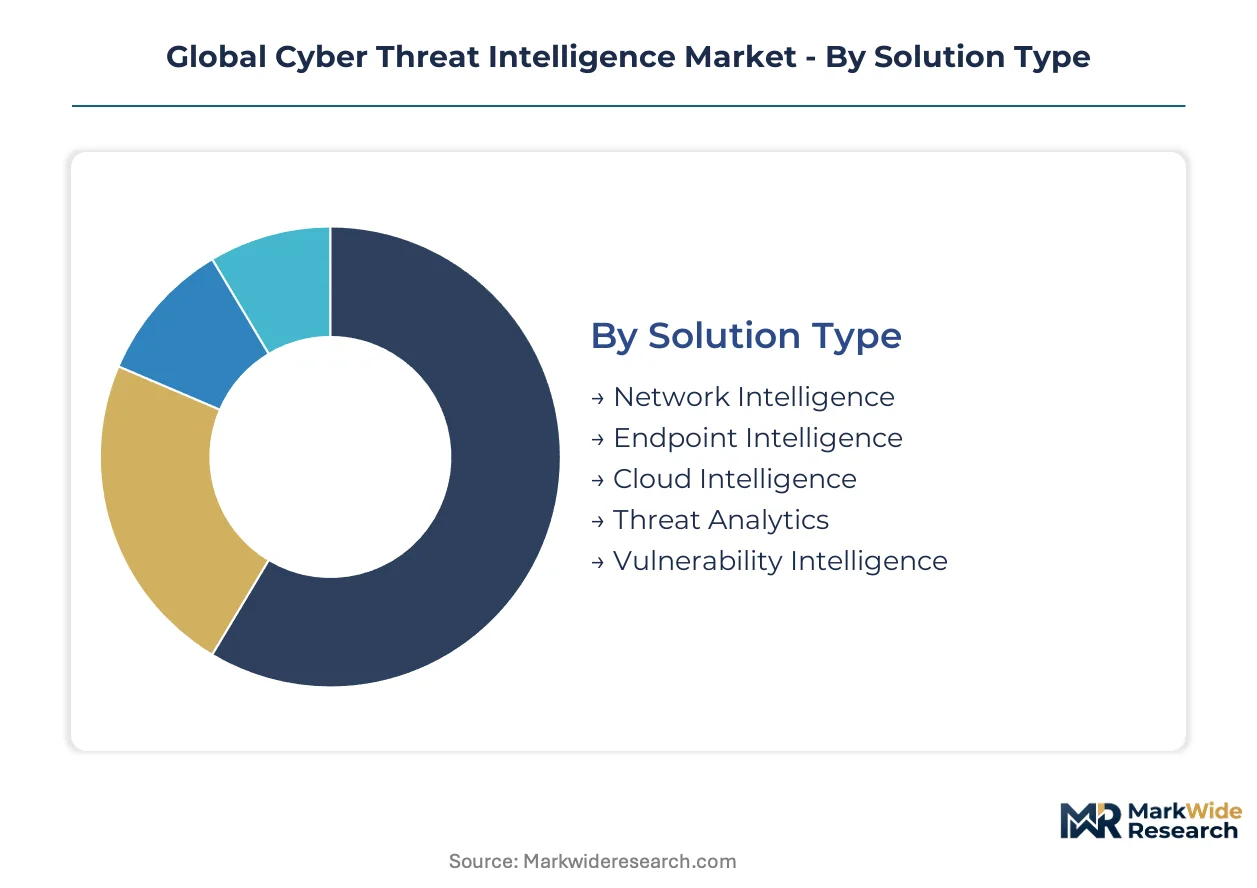
Segmentation in cyber threat intelligence reveals how defensive requirements fragment across infrastructure layers and operational contexts. Procurement patterns diverge sharply between organizations seeking integrated platforms versus specialized point solutions for targeted threat surfaces.
Solution Type:
After-sales service intensity varies dramatically across solution types, with cloud-native platforms demanding continuous model retraining and threat feed curation while network appliances require less frequent signature updates.
- Cloud Intelligence:Platforms ingest telemetry from multi-cloud control planes and container orchestration layers to identify lateral movement across distributed workloads. Financial institutions in the United States are prioritizing these deployments as they migrate treasury systems to AWS and Azure environments, driven by SEC cyber disclosure rules mandating rapid incident documentation.
- Threat Analytics:Machine learning pipelines process behavioral telemetry to surface anomalous patterns without signature dependencies. Energy sector operators across Germany and France are adopting these systems to satisfy EU NIS2 Directive requirements for predictive threat detection in critical infrastructure.
- Network Intelligence:Deep packet inspection and netflow analysis platforms monitor perimeter and east-west traffic for indicator matching. Telecom providers maintain the largest installed base of these systems.
- Endpoint Intelligence:Agents deployed on workstations and servers collect process telemetry for threat actor attribution. IT service providers bundle these capabilities into managed detection and response offerings.
- Vulnerability Intelligence:Correlates exploit availability with asset exposure to prioritize patching sequences. Government agencies leverage these feeds for attack surface management.
Network intelligence holds the largest share; momentum sits with cloud intelligence.
Deployment Model:
Cost tier stratification separates enterprise buyers with capital budget flexibility from mid-market organizations seeking operational expenditure predictability through subscription models.
- Cloud-Based:SaaS delivery eliminates infrastructure ownership while enabling elastic scaling during incident response surges. United States defense contractors are accelerating FedRAMP-authorized cloud deployments as CMMC requirements mature, constrained by data residency specifications for controlled unclassified information.
- Managed Security Service:Third-party analysts operate threat intelligence platforms on client behalf, delivering curated alerts and response playbooks. Healthcare systems in the United Kingdom are expanding these contracts to address NHS cybersecurity standards without internal SOC buildout.
- On-Premises:Air-gapped deployments satisfy classified environment requirements and strict data localization mandates. Intelligence agencies and defense ministries maintain this architecture exclusively.
- Hybrid:Combines on-premises sensors with cloud analytics for sensitive data processing. Japanese manufacturing conglomerates favor this model under METI guidelines.
On-premises deployments retain dominance in classified environments; hybrid architectures are climbing the fastest among regulated commercial sectors.
Use Case:
Application maturity separates established compliance-driven deployments from emerging proactive hunting programs that demand higher analyst sophistication.
- Incident Response:Intelligence platforms accelerate containment by pre-positioning indicators and response playbooks. United States financial institutions facing ransomware campaigns prioritize these capabilities to meet SEC four-day disclosure windows.
- Threat Hunting:Proactive adversary pursuit across enterprise environments requires hypothesis-driven intelligence consumption. Energy sector SOCs in Norway and the Netherlands are building these programs to satisfy NIS2 proactive security mandates.
- Fraud Detection:Correlates threat intelligence with transaction patterns to identify compromised credentials. Payment processors deploy these integrations.
- Risk Management:Quantifies exposure through threat actor targeting assessments and vulnerability prioritization. Insurance underwriters leverage these outputs for cyber policy pricing.
- Compliance Monitoring:Automates evidence collection for regulatory audit trails. European critical infrastructure operators deploy these under GDPR and NIS2 documentation requirements.
Compliance monitoring holds the largest share; threat hunting represents the steepest expansion trajectory.
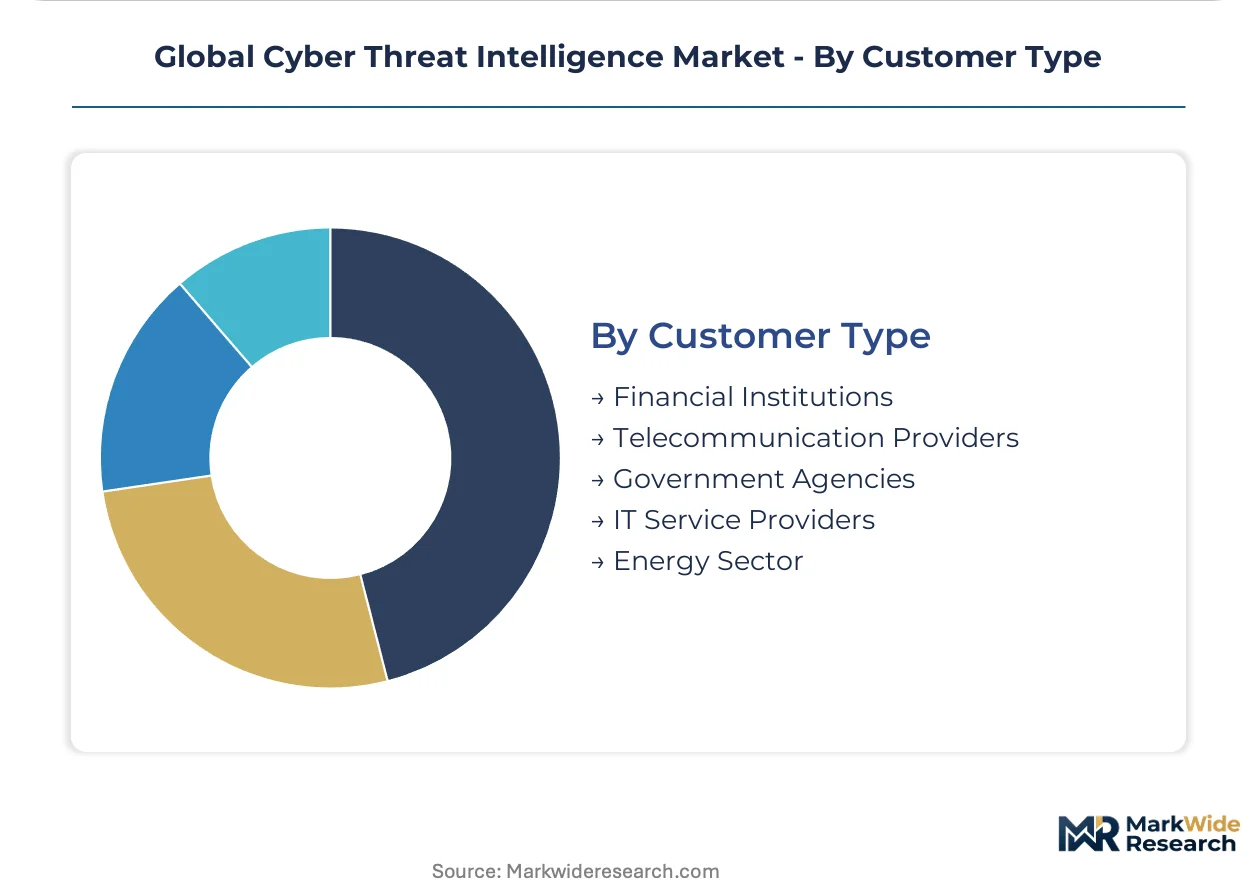
Customer Type:
Customer sophistication and procurement scale create distinct service tier expectations, with government buyers demanding FedRAMP certification and financial institutions requiring sub-second latency guarantees.
- Financial Institutions:Banks, insurers, and payment processors face concentrated targeting by state-sponsored and criminal actors seeking monetary gain. Institutions across Singapore and Switzerland are expanding intelligence budgets following SWIFT infrastructure attacks, constrained by cross-border data sharing restrictions.
- Government Agencies:National security and civilian departments require classified threat feeds and domestic infrastructure deployment. United States federal civilian agencies are consolidating procurement through CDM program vehicles.
- Telecommunication Providers:Network operators defend subscriber data and critical communication infrastructure. Operators in South Korea and Australia are integrating intelligence under national cybersecurity framework obligations.
- IT Service Providers:MSSPs and systems integrators embed intelligence into multi-tenant security offerings. These vendors drive API-native consumption models.
- Energy Sector:Generation, transmission, and distribution operators protect industrial control systems from targeted disruption. European utilities are accelerating procurement ahead of NIS2 enforcement deadlines.
Financial institutions command the largest procurement volumes; government agencies are gaining share fastest through classified program expansion.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The SEC anchors the dominant geography through cyber disclosure rules that compress incident reporting windows to four days. Federal procurement vehicles and CMMC maturation accelerate platform consolidation among defense contractors. Cloud migration across financial services and critical infrastructure operators concentrates demand in jurisdictions with mature certification frameworks.
United States
Defense contractors and federal civilian agencies drive procurement through FedRAMP-authorized platforms. The Cybersecurity and Infrastructure Security Agency coordinates threat feed distribution under the Continuous Diagnostics and Mitigation program. Northern Virginia's intelligence corridor hosts concentrated SOC buildouts serving government and cleared contractor networks.
Germany
Energy sector operators and automotive manufacturers prioritize predictive detection for industrial control system protection. The EU NIS2 Directive mandates certified threat detection with strict incident reporting timelines for critical infrastructure. Munich and Frankfurt clusters concentrate MSSP delivery centers serving DAX-listed industrial conglomerates.
United Kingdom
Healthcare systems expand managed security service contracts to address NHS cybersecurity standards without internal analyst buildout. The National Cyber Security Centre publishes threat advisories that shape procurement specifications for regulated entities. London's financial district drives premium-tier platform adoption among global banks and payment processors.
Japan
Manufacturing conglomerates favor hybrid deployment models under METI guidelines for critical infrastructure protection. The country's cybersecurity framework mandates threat intelligence integration for utility and railway operators. The Nagoya-Tokyo industrial corridor concentrates OT-security convergence projects bridging IT and operational technology visibility.
Singapore
Financial institutions expand intelligence budgets following regional SWIFT infrastructure targeting by affiliate ransomware operations. The Monetary Authority of Singapore enforces technology risk management guidelines that mandate threat detection capabilities. The city-state's data center cluster serves as Asia-Pacific hub for cloud-native security platform delivery.
Global Cyber Threat Intelligence Market Competitive Landscape
Integrated platform providers and specialized intelligence vendors split the market between bundled security stacks and point-solution depth. Consolidation pressure favors vendors with native cloud, endpoint, and network telemetry fusion. Three archetypes dominate: endpoint-native platforms extending into intelligence, cloud security vendors embedding threat feeds, and standalone research-driven intelligence specialists. Competitive moves center on API-native distribution partnerships and FedRAMP authorization acquisition for federal market access.
Among endpoint-native platform providers, CrowdStrike occupies a position exemplifying graph-based correlation architectures. Palo Alto Networks anchors the integrated network-cloud intelligence tier through consolidated security stack positioning. IBM Corporation sits within the managed security services archetype, leveraging threat research divisions to differentiate outsourced SOC delivery. These three represent distinct strategic postures rather than exhaustive market coverage.
| Leading Market Players |
|---|
| IBM Corporation |
| Palo Alto Networks |
| Cisco Systems |
| CrowdStrike |
| Microsoft Corporation |
| Recorded Future |
| Google (Mandiant) |
| Check Point Software Technology |
| Fortinet |
| Others |
Supply & Pricing Matrix
Specialized threat data curators in Israel and the United Kingdom anchor upstream value capture, concentrating margin pools with vendors who maintain proprietary sensor networks and dark web access infrastructure rather than commodity feed aggregators.
Pricing Analysis
North American enterprises pay 40-60% premiums over Asia-Pacific buyers for equivalent threat intelligence packages due to FedRAMP certification requirements and domestic data residency mandates. Pricing stratifies across premium, standard, and economy tiers based on STIX/TAXII protocol support, MITRE ATT&CK mapping depth, and analyst hotline availability. Cost compression in the standard tier is intensifying because open-source MISP feeds erode differentiation. Financial institutions exhibit the lowest price sensitivity due to SEC disclosure deadlines, while mid-market healthcare systems prioritize economy tiers with stripped-down API access.
Supply Chain Analysis
Extended payment terms from 30 to 90 days are becoming standard for threat intelligence vendors serving Fortune 500 accounts, with supply-chain finance facilities bridging working capital gaps. Platform development draws from engineering talent pools in the United States, Israel, and Estonia, while data enrichment relies on human analyst networks in India and Poland. Single-source vulnerability stems from concentration of dark web monitoring infrastructure with three specialized access providers. Distribution runs through direct enterprise sales teams and MSSP channel partnerships, with API-native consumption displacing portal-based licensing.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The cyber threat intelligence market is approaching a platform-economics inflection as extended detection and response architectures collapse point-solution margins and API-native distribution rewires buyer-supplier relationships.
For Market Incumbents: Insulate core revenue by embedding threat intelligence deeper into endpoint and cloud security stacks through native graph correlation engines, while acquiring boutique dark web monitoring specialists to preempt niche entrants from capturing OT-security budgets under NIS2 mandates. For New Entrants and Emerging Players: Build out API-first threat scoring services targeting mid-market MSSPs lacking in-house analyst capacity, with Japan's railway and utility operators representing the most penetrable geography due to METI guideline enforcement creating procurement urgency without established vendor relationships. For Investors and Strategic Acquirers: Capital is best deployed toward standalone intelligence specialists with proven STIX/TAXII interoperability and established analyst teams, as platform consolidation accelerates acquirer interest in differentiated data sources. The signal to watch is federal CDM program contract awards, which indicate which vendors have cleared procurement barriers for downstream platform bundling.| Strategic Initiative | Industry Significance |
|---|---|
| API-Native Platform Integration | Enables embedded threat scoring within SOAR workflows without portal friction. |
| FedRAMP Authorization Acquisition | Unlocks federal procurement vehicles and defense contractor supply chain eligibility. |
| OT-Security Capability Buildout | Captures NIS2-mandated spending from European energy and manufacturing operators. |
| Acquisition of Dark Web Specialist | Secures proprietary access infrastructure that open-source feeds cannot replicate. |
| MITRE ATT&CK Mapping Investment | Differentiates offerings through standardized adversary tradecraft correlation. |
Research Methodology
A standing panel of CISOs, SOC directors, threat intelligence analysts, and MSSP operations leads provided ongoing calibration across the study period, combining structured interviews with secondary validation from SEC cyber disclosure filings, EU NIS2 implementation guidance, CDM program procurement records, and vendor FedRAMP authorization packages. Bottom-up deployment estimates triangulated against top-down addressable market calculations.
Scenario-bracketing framed projections across the analysis window, modeling adoption trajectories by solution type, deployment model, customer vertical, and geographic regulatory cluster. CAGRs derived from weighted average of historical deployment velocity and policy-mandated procurement deadlines. Forecast inputs included CMMC maturity timelines, EU AI Act enforcement phases, and cloud migration patterns among defense contractors.
Practitioners should monitor regulatory enforcement intensity and adversary tradecraft automation rates for early signals of demand inflection. Forecasts reflect assumptions about policy implementation cadence and technology integration feasibility. Macroeconomic contraction affecting security budgets, regulatory delay, or breakthrough in autonomous threat detection would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud DLP Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Global Container and Kubernetes Security Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
Cyber Warfare Market
Cybersecurity
Cyber Deception Market
Cybersecurity
United States Cybersecurity Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Cyber Security in Energy Market
Cybersecurity
Qatar Cybersecurity Market
Cybersecurity
Cyber Security Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
DNS Security Market