
 Global API Security Market | 2026-2036
Global API Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global API Security Market Foresight
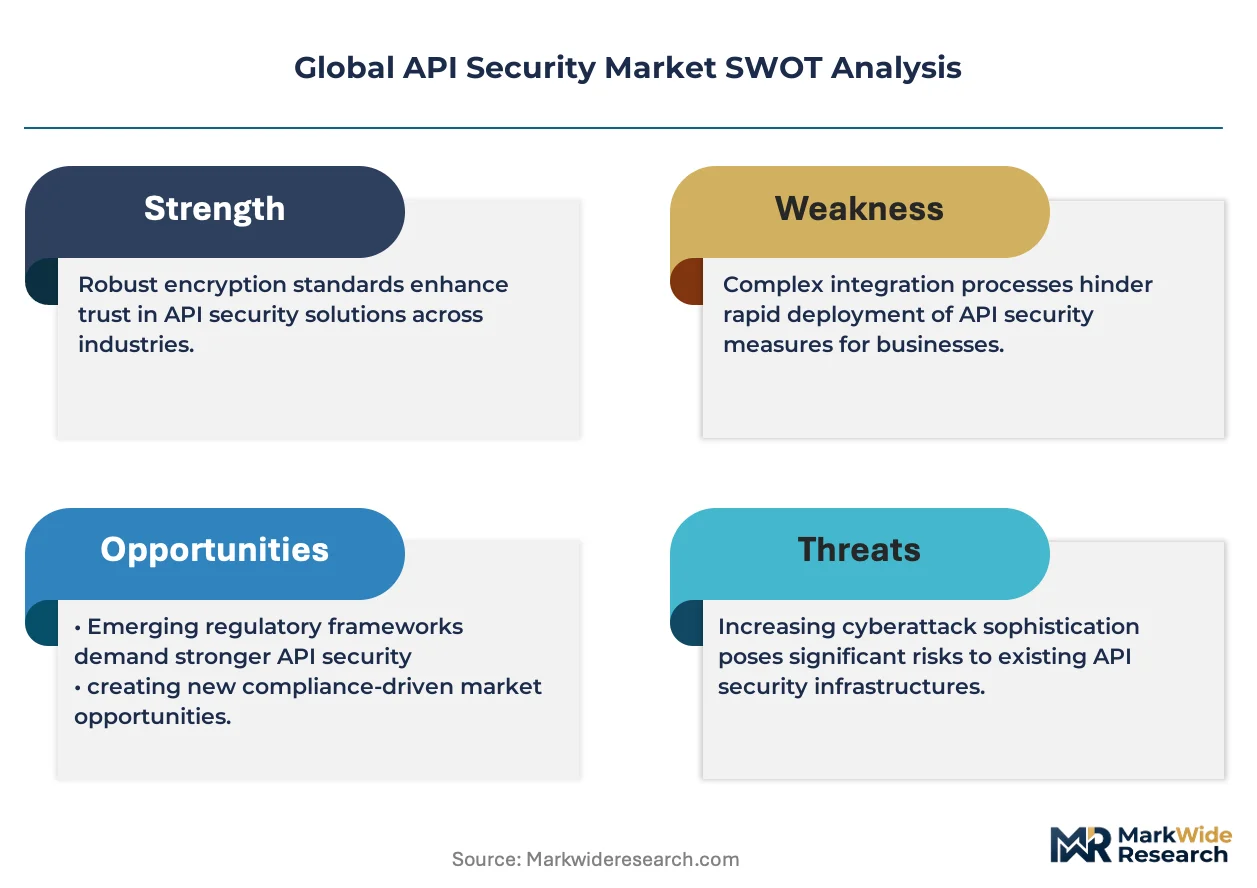
Enterprise buyers in financial services is rotating toward cloud-native API security stacks, displacing legacy on-premises deployments. Salt Security specializes in runtime behavioral analysis for API discovery, while Palo Alto Networks extends its platform through integrated gateway and WAAP capabilities. Google LLC leverages its cloud infrastructure dominance to bundle API security with existing enterprise contracts.
API security encompasses the technologies, policies, and practices that protect application programming interfaces from unauthorized access, data exfiltration, and service disruption through authentication enforcement, traffic inspection, and schema validation at network perimeters. The primary purpose is ensuring data integrity and service continuity across distributed software architectures that expose business logic to external developers and partner ecosystems. Threat detection solutions capture expanding margin pools as organizations prioritize real-time anomaly identification over static access controls. Cloud-based deployment models lead volume adoption among technology providers and e-commerce platforms seeking elastic scalability without infrastructure ownership.
The EU AI Act and GDPR impose mandatory risk assessments and documentation requirements on automated API decision systems processing personal data, while the SEC's cybersecurity disclosure rules in the United States mandate incident reporting that elevates API breach visibility to board-level accountability. ISO 27001 and NIST frameworks provide baseline control catalogs that procurement teams use to evaluate vendor compliance during enterprise selection processes. Stakeholders must monitor how quantum-resistant TLS implementations and post-quantum cryptographic standards reshape certificate lifecycle management before protocol mandates harden.
Market Dynamics
Cloud-native microservices adoption is fragmenting enterprise security perimeters, forcing organizations to abandon perimeter-based defenses in favor of runtime API behavioral monitoring that tracks data flows across distributed service meshes.
Growth Catalysts
- Open Banking Mandates:PSD2 in the European Union and similar frameworks in Australia and Brazil compel financial institutions to expose payment APIs, creating mandatory procurement of authentication and traffic inspection tools.
- Zero Trust Architecture:Enterprise security teams are implementing continuous verification models that treat every API endpoint as untrusted, expanding addressable demand for dynamic access control solutions.
- Serverless Computing:Function-as-a-service deployments from Amazon Web Services, Microsoft Azure, and Google Cloud Platform generate ephemeral API endpoints that static security policies cannot protect.
Market Restraints
- Skills Concentration:Deep expertise in OAuth 2.0, OpenID Connect, and JSON Web Token security resides primarily in Silicon Valley and Tel Aviv talent pools, constraining deployment velocity elsewhere.
- Certificate Authority Fragility:Compromise of any major root CA in the WebPKI ecosystem triggers cascading revocation events that disrupt API authentication chains across dependent services.
- Quantum Vulnerability:Current TLS 1.3 handshakes rely on RSA and elliptic-curve cryptography that quantum algorithms threaten, forcing premature infrastructure replacement before NIST post-quantum standards mature.
Strategic Opportunities
- Latin American Fintech:Brazil's PIX instant payment system and Mexico's CoDi platform expose banking APIs to millions of new users without corresponding security infrastructure depth.
- Healthcare Data Exchange:The United States 21st Century Cures Act mandates API interoperability for electronic health records, creating compliance-driven procurement in hospital systems and health information exchanges.
- AI Model Serving:Machine learning inference endpoints require specialized protection against model extraction and prompt injection attacks that traditional web application firewalls cannot detect.
Industry Challenges
- Shadow API Discovery:Development teams deploy endpoints through infrastructure-as-code pipelines without security review, leaving organizations unable to inventory their full attack surface.
- Schema Drift Management:Continuous integration practices push API changes weekly, forcing security tools to adapt validation rules faster than manual policy updates permit.
- Cross-Border Data Governance:Divergent requirements between China's Personal Information Protection Law, the EU GDPR, and US state privacy laws complicate unified API access logging and retention policies.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global API Security Market |
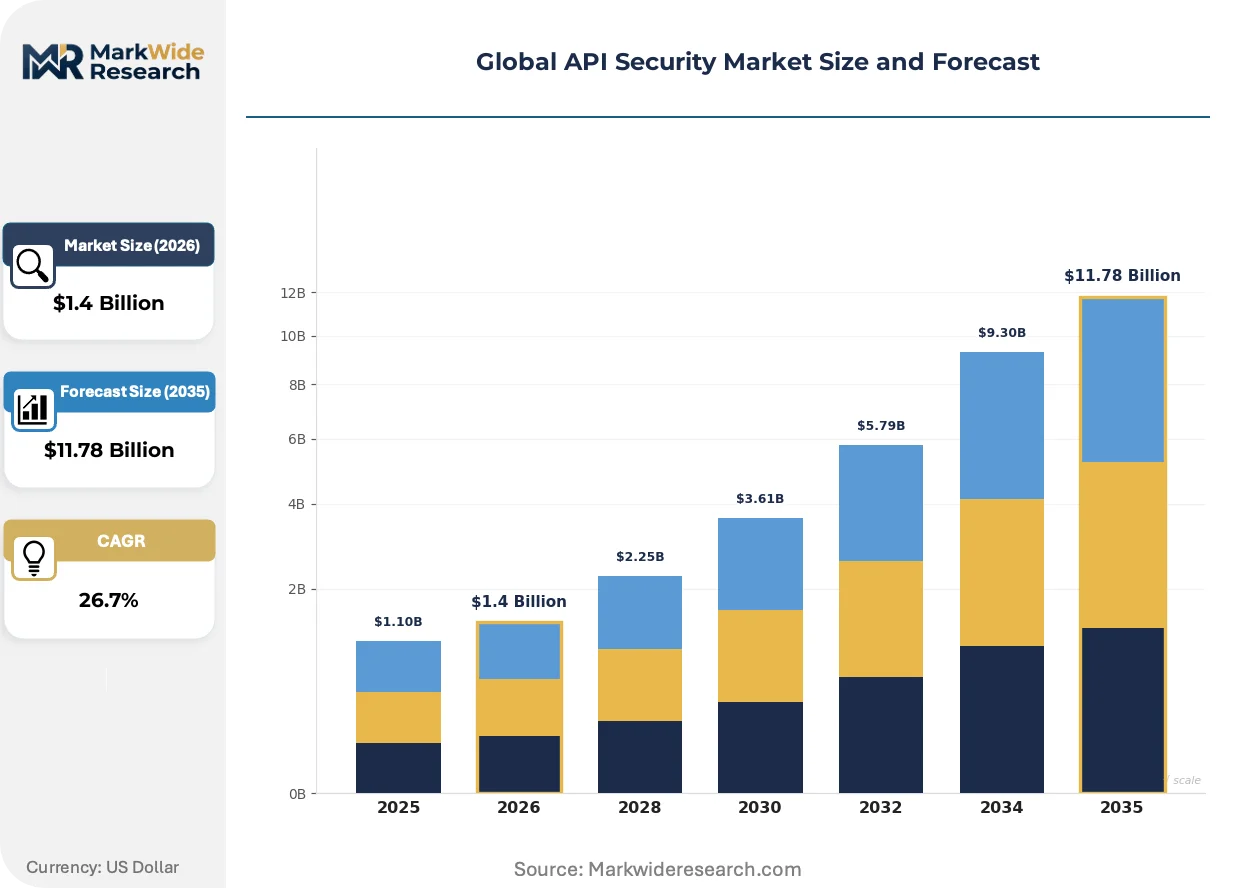
| Market Size in 2026 | $1.4 Billion |
| Market Size in 2035 | $11.78 Billion |
| CAGR (2026 – 2036) | 26.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Identity Management, Threat Detection, Encryption, Access Control, Bot Mitigation, Analytics Deployment Model: Cloud-Based, On-Premises, Hybrid, Managed Services End User Industry: BFSI, Telecommunications, Government Agencies, E-Commerce, Technology Providers, Education Security Protocol: OAuth, OpenID Connect, SAML, JWT, API Gateway Security, TLS/SSL |
| Companies Covered | Google LLC, Microsoft Corporation, Akamai Technologies, Amazon Web Services, Cisco Systems, IBM Corporation, Oracle Corporation, Salt Security, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global API Security Market Shifts & Advancements
Runtime behavioral analysis is displacing static signature detection as the primary API threat identification method, with machine learning models trained on normal traffic patterns now flagging anomalies that rule-based systems miss entirely.
GraphQL query depth limiting and cost analysis is bifurcating API gateway procurement, with e-commerce platforms and content management systems adopting specialized engines that prevent resource exhaustion attacks through nested query structures. Retail technology teams at Shopify and similar platforms deploy these controls to protect against denial-of-wallet incidents where complex queries trigger cascading database load. The technology is compressing margins for generic gateway vendors unable to parse query semantics.
The EU AI Act's risk classification system for automated decision-making APIs imposes documentation and human oversight obligations on financial services and recruitment technology providers operating in European markets. Organizations deploying credit scoring or candidate screening algorithms must maintain technical files and establish governance structures that slow deployment cycles. German and French regulators are already requesting pre-market conformity assessments for high-risk API implementations.
Security procurement among Fortune 500 enterprises now favors consolidated platforms over point solutions, with CISOs reducing vendor counts to simplify incident response and reduce integration debt. Managed detection and response contracts for API traffic are displacing standalone tool licenses in North American financial services and technology verticals. This consolidation is most visible in the United States, where cybersecurity insurance carriers incentivize unified telemetry stacks that streamline claims documentation.
Global API Security Market Segmentation
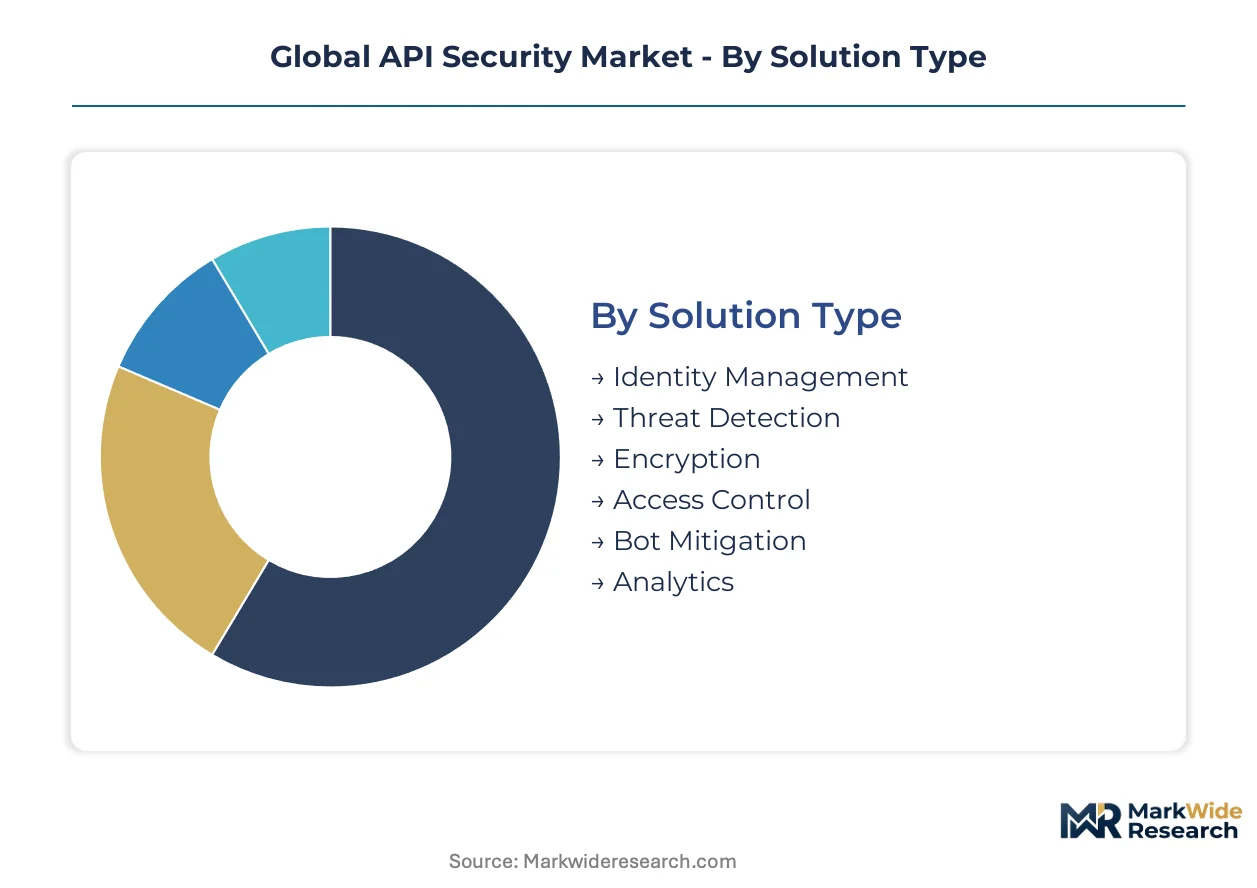
API security procurement patterns diverge sharply across solution architectures, with cloud-native stacks displacing legacy perimeter tools in financial services while regulated industries retain hybrid deployments for audit compliance. Understanding these segment boundaries enables vendors to align R&D investment with substitution pressures and margin concentration.
Solution Type:
Substitution pressure concentrates in static protection layers as behavioral analytics and machine learning detection engines displace signature-based tools.
- Identity Management:Federated authentication systems with OAuth 2.0 and OpenID Connect integration govern user credential lifecycle across distributed service meshes. BFSI institutions in the United States and European Union mandate these controls for open banking compliance, driving procurement volume despite implementation complexity.
- Threat Detection:Runtime behavioral analysis platforms monitor API traffic patterns to identify anomalies that static rules miss entirely. Technology providers and e-commerce platforms deploy these solutions to protect against credential stuffing and data exfiltration attacks.
- Encryption:Field-level and transport-layer cryptographic protection for data at rest and in motion.
- Access Control:Policy enforcement engines governing endpoint authorization and rate limiting.
- Bot Mitigation:Specialized defenses against automated credential abuse and scraping operations.
- Analytics:Post-hoc traffic analysis and compliance reporting dashboards.
Threat Detection anchors the volume base while Identity Management gains share at the steepest rate.
Deployment Model:
Cost tier stratification separates elastic consumption models from capital-intensive infrastructure ownership, with mid-market buyers gravitating toward managed service bundles.
- Cloud-Based:Multi-tenant SaaS platforms delivering API gateway and WAAP functionality without infrastructure ownership. Technology providers in the United States and e-commerce platforms favor this model for elastic scaling during traffic spikes.
- On-Premises:Dedicated hardware and software installations within enterprise data centers for air-gapped environments. Government agencies in Germany and France require these deployments for classified system protection.
- Hybrid:Split architectures placing sensitive authentication on-premises while offloading traffic inspection to cloud nodes.
- Managed Services:Outsourced security operations centers monitoring API traffic and incident response.
Cloud-Based deployments capture the largest revenue pool while Managed Services expand most quickly among resource-constrained mid-market buyers.
End User Industry:
Application intensity varies by digital maturity, with sectors exposing customer-facing APIs exhibiting procurement urgency absent in legacy-protected verticals.
- BFSI:Banking, financial services, and insurance institutions protecting payment initiation and account information APIs under PSD2 and open banking mandates. European institutions face EU AI Act documentation requirements for automated credit decisioning endpoints.
- E-Commerce:Retail platforms defending checkout flows and inventory APIs against bot-driven fraud and inventory hoarding.
- Telecommunications:Network operators securing subscriber data APIs and IoT device management interfaces.
- Government Agencies:Public sector entities implementing zero-trust architectures for citizen service portals.
- Technology Providers:SaaS vendors protecting multi-tenant platform APIs and developer ecosystems.
- Education:Universities securing learning management system integrations and research data exchanges.
BFSI anchors the volume base while E-Commerce climbs the fastest as platform transaction volumes accelerate.
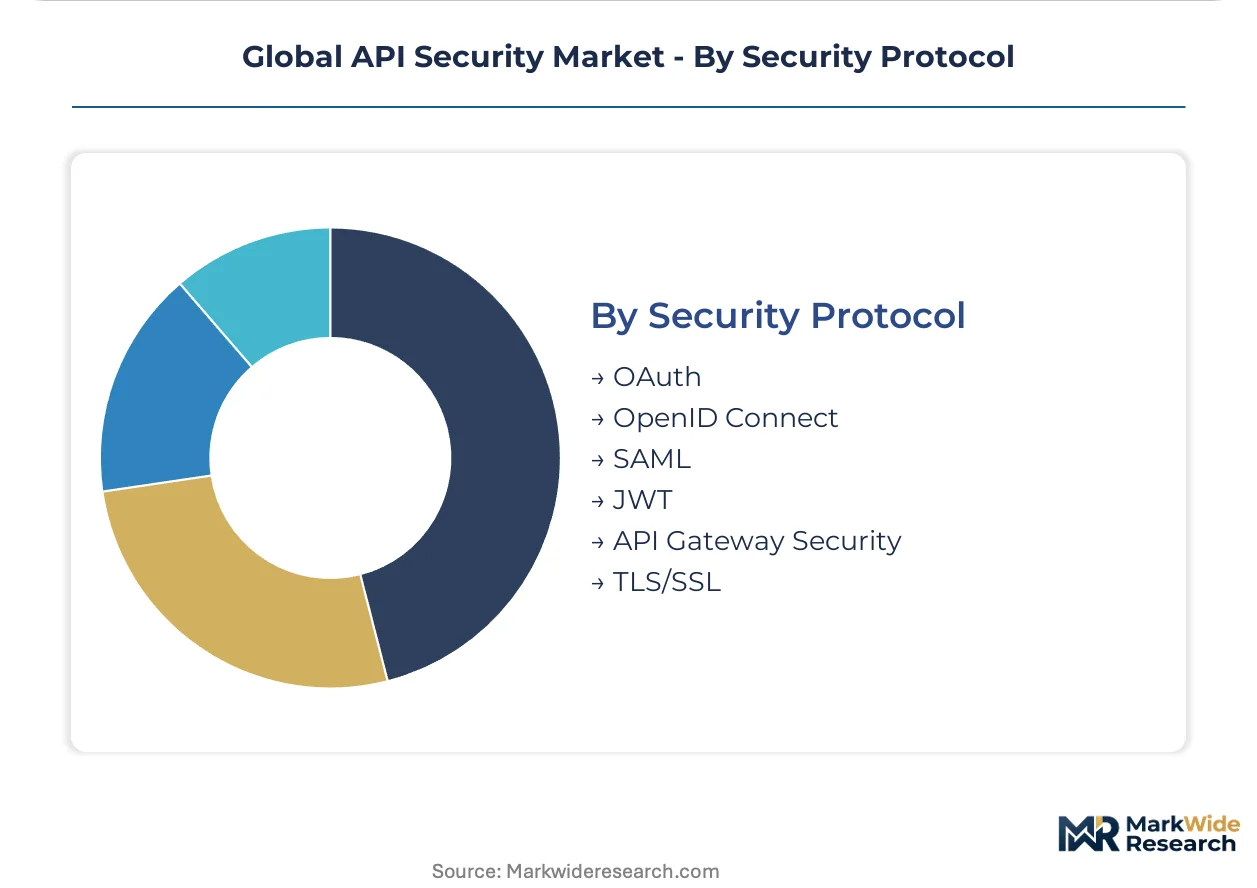
Security Protocol:
Maturity differentiation separates established standards with broad interoperability from emerging specifications requiring specialized implementation expertise.
- OAuth:Delegated authorization framework enabling third-party application access without credential exposure. Open banking implementations in the United Kingdom and Australia rely on OAuth 2.0 for secure payment initiation.
- API Gateway Security:Consolidated policy enforcement points handling authentication, rate limiting, and request validation. Cloud providers bundle these capabilities with infrastructure contracts, compressing standalone vendor margins.
- OpenID Connect:Identity layer atop OAuth 2.0 providing standardized authentication claims.
- SAML:XML-based enterprise single sign-on protocol prevalent in legacy identity federation.
- JWT:Compact token format for stateless authentication claims transmission.
- TLS/SSL:Transport layer encryption protocols protecting data in motion.
OAuth anchors the volume base while API Gateway Security gains share at the steepest rate through cloud provider bundling.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli API security specialists export behavioral analytics platforms to financial institutions in the United Kingdom and Germany, while United States cloud providers bundle gateway security with infrastructure contracts across European enterprise buyers.
United States
Cloud-native fintech adoption drives gateway security procurement among neobanks and payment processors. The SEC's cybersecurity disclosure rules mandate incident reporting that elevates API breach visibility to board-level accountability. Silicon Valley talent pools concentrate OAuth 2.0 and OpenID Connect expertise, constraining deployment velocity elsewhere.
Germany
Automotive manufacturers secure connected vehicle APIs and industrial IoT interfaces under stringent data protection requirements. The EU AI Act imposes mandatory risk assessments on automated decision systems processing personal data. Berlin and Munich host specialized security operations centers monitoring API traffic for DAX-listed enterprises.
United Kingdom
Open banking implementations under PSD2 compel financial institutions to expose payment APIs, creating mandatory procurement of authentication tools. The Financial Conduct Authority enforces operational resilience requirements for critical digital infrastructure. London's fintech cluster drives demand for runtime behavioral analysis platforms protecting retail banking interfaces.
Brazil
The PIX instant payment system exposes banking APIs to millions of new users without corresponding security infrastructure depth. Brazil's central bank mandates strong customer authentication for payment initiation services. São Paulo-based fintechs accelerate procurement of bot mitigation and fraud detection capabilities.
Japan
Financial institutions modernize legacy core systems through API-first architectures, expanding addressable demand for schema validation and traffic inspection. METI guidelines promote zero-trust security models for critical infrastructure operators. Tokyo's banking district concentrates procurement of managed detection and response contracts for API traffic monitoring.
Global API Security Market Competitive Landscape
Player mix skews toward cloud infrastructure incumbents with bundled security offerings, creating tiered competition between hyperscale platforms and specialized behavioral analytics vendors. Market structure concentrates revenue among five dominant providers with integrated gateway-WAAP capabilities. Strategic archetypes include cloud-native specialists, legacy network security extenders, and API-dedicated pure-plays. Competitive moves center on M&A for runtime behavioral technology and strategic partnerships embedding security into developer workflows.
Within the cloud infrastructure tier, Google LLC and Amazon Web Services represent the bundling archetype, anchoring API security within broader enterprise cloud contracts. Microsoft Corporation occupies a similar position through Azure-native gateway deployments. Salt Security exemplifies the pure-play specialist model, focusing exclusively on runtime API discovery and anomaly detection without underlying infrastructure ownership. Palo Alto Networks sits within the network security extender category, integrating API protection into broader platform consolidation strategies.
| Leading Market Players |
|---|
| Google LLC |
| Microsoft Corporation |
| Akamai Technologies |
| Amazon Web Services |
| Cisco Systems |
| IBM Corporation |
| Oracle Corporation |
| Salt Security |
| Palo Alto Networks |
| Others |
Supply & Pricing Matrix
Sixty-to-ninety-day implementation cycles for cloud-native API security platforms compress vendor pricing power while amplifying procurement leverage for enterprise buyers negotiating multi-year enterprise license agreements. This lead-time compression concentrates margin pressure on pure-play specialists without bundled infrastructure offerings, while hyperscale cloud providers absorb pricing discounts through cross-subsidization from compute and storage contracts.
Pricing Analysis
Current-generation runtime behavioral analytics commands substantial premiums over prior-generation signature-based detection tools, while next-generation quantum-resistant cryptographic implementations remain pre-commercial with undefined pricing architectures. Three-tier pricing structure across premium, standard, and economy levels segments by deployment complexity and managed service inclusion, with ISO 27001 certification tiers and dedicated security operations center support driving differentiation. Cost compression in the standard tier intensifies because hyperscaler bundling forces standalone vendors toward feature convergence. Mid-market financial services buyers exhibit highest price sensitivity due to constrained security budgets, while Fortune 500 technology providers demonstrate lowest sensitivity given breach-liability exposure.
Supply Chain Analysis
Inbound logistics costs for hardware security modules and specialized cryptographic processors face intermittent pressure from transpacific container availability constraints affecting semiconductor packaging facilities. Software supply chains draw from development talent pools concentrated in the United States, Israel, and India, with cryptographic libraries and open-source authentication frameworks resting on contributions from European academic institutions. Single-source vulnerability concentrates in root certificate authority infrastructure, where compromise of any major WebPKI trust anchor triggers cascading authentication failures. Distribution runs through direct enterprise sales organizations and cloud marketplace integrations, with hyperscaler co-sell partnerships displacing traditional channel relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Global API Security Market sits at an inflection where EU AI Act documentation mandates and post-quantum cryptographic transition timelines are compressing vendor consolidation windows. This regulatory-technological convergence favors platform breadth over point-solution depth.
For Market Incumbents: Fortify platform positions through runtime behavioral analytics acquisitions that close capability gaps against Salt Security specialists, while embedding API discovery into existing zero-trust architecture deployments to reduce customer churn. Defensive moves must address hyperscaler bundling threats by emphasizing multi-cloud portability and air-gapped deployment options for regulated European financial institutions. For New Entrants and Emerging Players: Anchor in Latin American fintech infrastructure gaps, where Brazil's PIX ecosystem and Mexico's CoDi platform expose banking APIs to millions of users without mature security tooling penetration. White-space targets include healthcare data exchange APIs under the United States 21st Century Cures Act and AI model serving endpoints vulnerable to extraction attacks. Go-to-market execution should prioritize developer workflow integration through infrastructure-as-code plugins rather than standalone console deployments. For Investors and Strategic Acquirers: Long-term, this sits as a consolidation play because runtime behavioral analytics capabilities are concentrating in a narrow talent base while procurement patterns favor unified telemetry stacks. Acquisition targets should display machine learning model differentiation for anomaly detection and established managed detection and response contract revenue. The signal to watch is cybersecurity insurance carrier endorsement of specific platform architectures, which would accelerate enterprise procurement standardization.| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Runtime behavioral analytics capabilities from Israeli specialists address capability gaps in broader platform portfolios. |
| Platform Integration | Embedding API discovery into existing zero-trust deployments reduces integration friction for CISO consolidation strategies. |
| Strategic Partnership | Co-development with hyperscaler marketplaces streamlines procurement for mid-market buyers seeking bundled contracts. |
| Geographic Expansion | Brazil and Mexico fintech corridors offer first-mover positioning before regulatory mandates harden security requirements. |
| Product Launch | Quantum-resistant TLS implementations targeting NIST post-quantum standards capture early compliance-driven procurement. |
Research Methodology
Operator-level perspectives from CISOs, cloud platform engineers, identity architects, and cybersecurity insurance underwriters anchored the qualitative base for this analysis. Primary fieldwork across financial services, technology providers, and healthcare systems combined with secondary validation from SEC cybersecurity disclosure filings, EU AI Act implementation guidance, NIST framework documentation, and hyperscaler infrastructure capex disclosures. Bottom-up deployment model sizing and top-down regulatory mandate impact assessment triangulated market boundaries.
Sensitivity analysis across deployment model elasticity, open banking mandate implementation timelines, and post-quantum cryptographic standard adoption rates shaped the analytical framework. Segmentation dimensions modeled include solution architecture type, deployment model, end-user industry vertical, and regional regulatory cluster complexity. CAGRs derived from elasticity-adjusted adoption curves and compliance-driven procurement inflection points, with inputs from cloud-native microservices penetration rates and zero-trust architecture implementation surveys across enterprise technology estates.
Decision-makers should treat outputs as directional under assumptions of sustained open banking regulatory momentum and stable hyperscaler bundling economics; material deviation in either factor would warrant model refresh. Forecasts reflect documented base-case assumptions regarding EU AI Act enforcement intensity and NIST post-quantum standard finalization schedules. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Wireless Network Security Market
Cybersecurity
Micro Segmentation Technology Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Romania Cybersecurity Market
Cybersecurity
Data Center Security Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
SSL VPN Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Global Ransomware Protection Market