
 Cloud Security Software Market | 2026-2036
Cloud Security Software Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Security Software Market Intelligence
The EU AI Act is recalibrating how European enterprises evaluate cloud security procurement, forcing explicit risk classification for AI systems hosted in shared infrastructure. Microsoft Corporation leverages its compliance tooling investments to anchor multi-cloud governance contracts across regulated industries. Palo Alto Networks competes through specialized cloud-native firewall architectures that integrate with Kubernetes orchestration layers. Fortinet controls mid-market expansion through consolidated secure access service edge bundles priced below modular alternatives.
Cloud security software encompasses tools that enforce confidentiality, integrity, and availability across distributed computing resources through encryption, identity verification, and continuous monitoring protocols; these systems operate at network, application, and data layers to prevent unauthorized access, detect anomalous behavior, and maintain audit trails for regulatory evidence. Identity Management solutions dominate enterprise budgets as workforce mobility and contractor access multiply credential attack surfaces. Threat Detection offerings represent the fastest-expanding solution category as behavioral analytics and automated response replace signature-based scanning. Hybrid Cloud deployment configurations concentrate margin pools where vendors must synchronize on-premises controls with native public cloud security APIs.
The U.S. Securities and Exchange Commission mandates incident disclosure timelines that compress cloud security response windows for publicly traded firms, while the EU NIS2 Directive imposes supply-chain liability extending to managed security service providers. ISO 27017 and ISO 27018 frameworks establish baseline controls for cloud service customer data, shaping procurement qualification requirements across healthcare and government verticals. Stakeholders must monitor whether sovereign cloud mandates fragment security architectures or create consolidation opportunities for vendors with multi-jurisdiction compliance certifications.
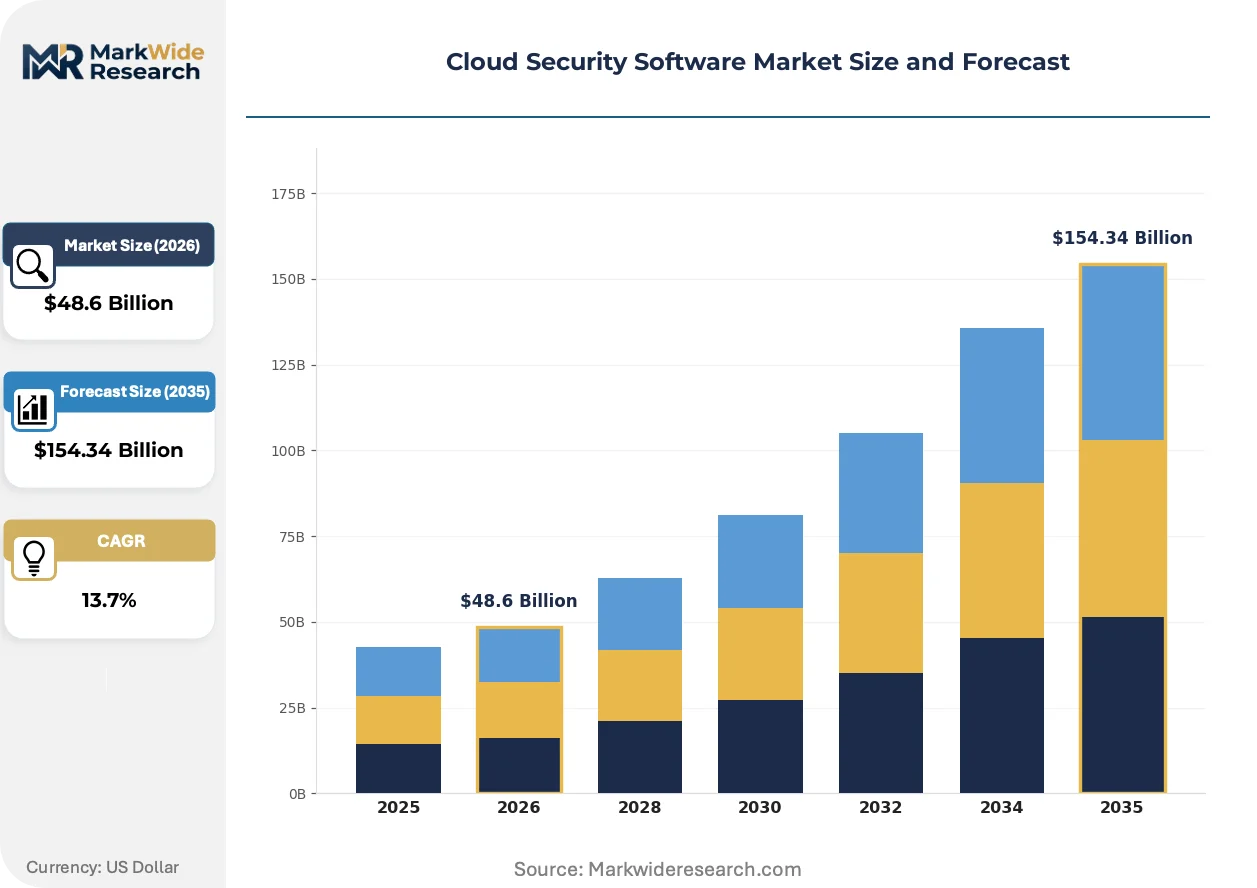
Market Dynamics
The EU AI Act and NIS2 Directive are compressing procurement cycles for cloud security software as European enterprises reclassify risk tiers for AI-hosted workloads and extend liability to managed service providers across supply chains.
Growth Catalysts
- Financial services cloud workload protection:Banks and insurers are deploying cloud-native security platforms to secure containerized trading applications and real-time payment processing environments.
- ISO 27017/27018 procurement mandates:Healthcare and government buyers now require these frameworks as baseline qualification criteria, filtering vendor pools and accelerating replacement cycles.
- Sovereign cloud frameworks:Germany, Japan, and the United States are building national cloud infrastructures that demand localized encryption and residency controls, creating dedicated procurement channels.
Market Restraints
- Multi-cloud API synchronization costs:Vendors must maintain parallel engineering tracks for AWS, Azure, and Google Cloud security APIs, fragmenting R&D budgets and extending breakeven timelines.
- Kubernetes expertise scarcity:Cloud-native firewall and workload protection deployment requires specialized DevSecOps talent concentrated in Silicon Valley and Berlin metro areas.
- SEC incident disclosure windows:The U.S. Securities and Exchange Commission mandates compressed reporting timelines that strain automated response system reliability and inflate compliance insurance premiums.
Strategic Opportunities
- Mid-market SASE consolidation:Secure access service edge bundles priced below modular alternatives are capturing manufacturing and professional services firms previously served by point solutions.
- Behavioral analytics threat detection:Automated response systems replacing signature-based scanning are opening whitespace in retail and logistics verticals with high seasonal workforce volatility.
- EU supply-chain liability extension:NIS2 Directive mandates are forcing managed security service providers to upgrade liability coverage, creating vendor switching windows for certified alternatives.
Industry Challenges
- Hybrid cloud control synchronization:Enterprises struggle to maintain policy consistency between on-premises security appliances and native public cloud controls, generating configuration drift and audit failures.
- Cross-border data residency certification:Vendors must maintain parallel compliance certifications for German, Japanese, and U.S. sovereign cloud requirements, multiplying certification costs and renewal complexity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Security Software Market |
| Market Size in 2026 | $48.6 Billion |
| Market Size in 2035 | $154.34 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Solution: Threat Detection, Data Loss Prevention, Identity Management, Compliance Management End User: Small Enterprises, Large Corporations, Government Agencies, Educational Institutions Service Type: Consulting Services, Managed Services, Integration Services, Support Services |
| Companies Covered | Microsoft Corporation, Amazon Web Services, Broadcom, Palo Alto Networks, Check Point Software Technologies, Fortinet, Cisco Systems, Trend Micro, SentinelOne, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Security Software Market Strategic Shifts & Innovations
Behavioral analytics and automated response protocols are displacing signature-based scanning as the dominant threat detection architecture, while procurement patterns shift toward consolidated platform contracts that bundle identity, network, and workload protection.
Cloud-native firewall architectures are integrating with Kubernetes orchestration layers to enforce microsegmentation policies at the container level. Financial services and healthcare enterprises are adopting these configurations fastest, driven by containerized application deployment. This convergence is compressing the addressable market for standalone network security appliances and redirecting enterprise budgets toward unified cloud security platforms.
The EU AI Act is mandating explicit risk classification for AI systems hosted in shared cloud infrastructure, forcing European enterprises to document training data provenance and model governance. This obligation is reshaping vendor evaluation criteria and disqualifying providers lacking automated compliance documentation tools. German automotive and French pharmaceutical manufacturers are responding by demanding contractual liability caps tied to AI system risk tiers.
Enterprise buyers are consolidating vendor relationships around multi-cloud governance platforms that span identity management, workload protection, and threat detection. Modular point solutions are losing procurement cycles to bundled offerings with unified policy engines. This concentration is most visible among U.S. healthcare systems and German industrial conglomerates seeking to reduce security operations center staffing overhead.
Cloud Security Software Market Segmentation
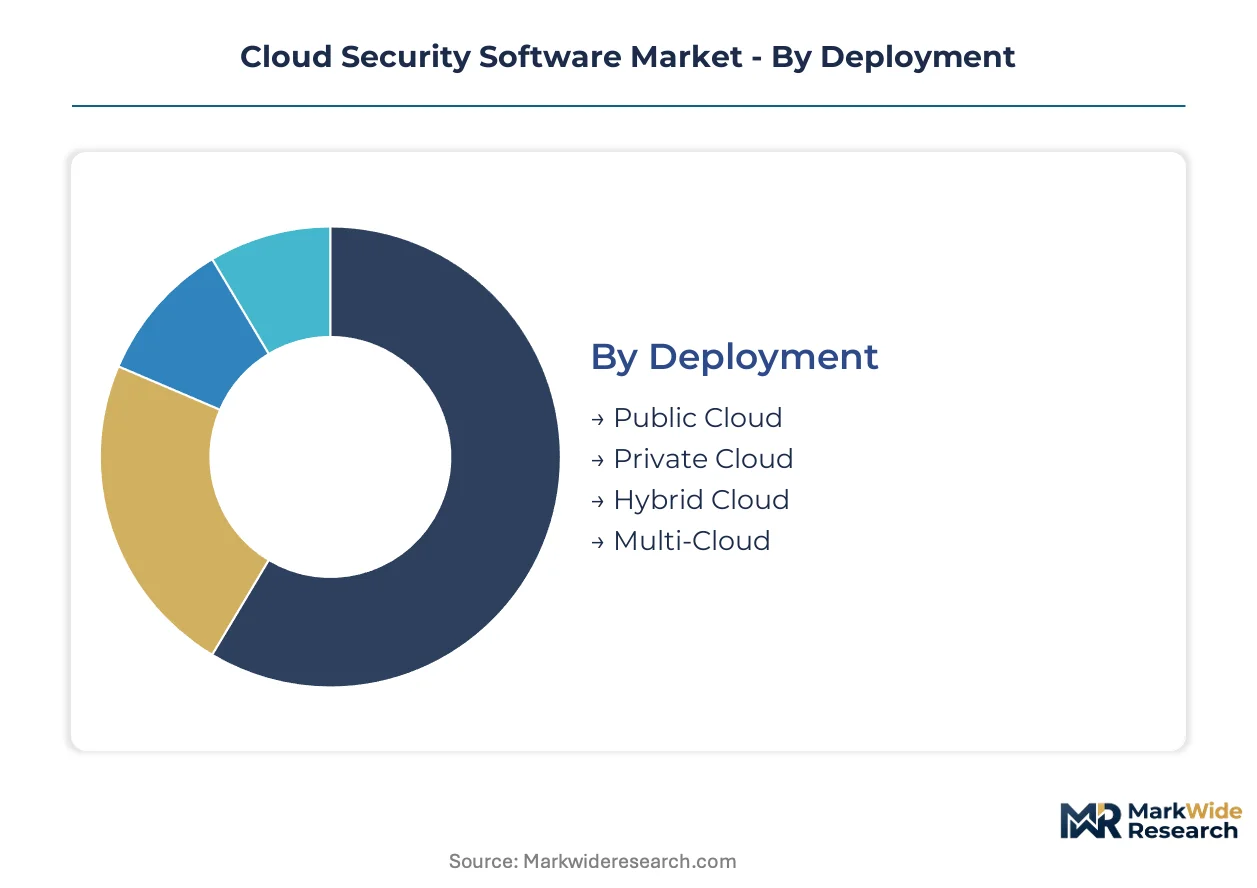
Cloud security software procurement patterns diverge sharply between enterprises seeking turnkey managed services and those building internal SecOps capabilities. Deployment architecture and end-user scale dictate solution complexity, pricing tiers, and vendor selection criteria across the market.
Deployment:
Volume concentrates in public cloud configurations, while premium margins attach to hybrid and sovereign cloud deployments requiring specialized compliance tooling.
- Public Cloud:Shared infrastructure models dominate enterprise adoption due to elastic scaling and native API integration with AWS, Azure, and Google Cloud security frameworks. Financial services firms in the United States and Germany are expanding workload protection here for containerized trading applications, though shared tenancy creates persistent audit complexity for PCI-DSS and GDPR evidence trails.
- Hybrid Cloud:Synchronization between on-premises security appliances and native public cloud controls commands the steepest pricing premiums, with vendors bundling unified policy engines to reduce configuration drift. German automotive manufacturers and U.S. healthcare systems are consolidating procurement around these configurations to satisfy ISO 27017 mandates while retaining legacy mainframe connectivity.
- Private Cloud:Dedicated single-tenant environments serve defense contractors and intelligence agencies requiring air-gapped encryption key management.
- Multi-Cloud:Parallel AWS, Azure, and Google Cloud deployments fragment engineering budgets but reduce vendor lock-in risk for Japanese electronics conglomerates.
Today's leader: Hybrid Cloud. Tomorrow's challenger: Multi-Cloud.
Solution:
Enterprise budget allocation follows credential attack surface expansion, with workforce mobility and contractor access multiplying priority tiers.
- Identity Management:Credential lifecycle platforms now incorporate behavioral biometrics and just-in-time privileged access for DevSecOps pipelines. U.S. healthcare systems and German industrial conglomerates are consolidating vendor relationships here to reduce security operations center staffing overhead, driven by SEC incident disclosure windows that compress response timelines.
- Threat Detection:Behavioral analytics and automated response protocols are displacing signature-based scanning architectures fastest in retail and logistics verticals with high seasonal workforce volatility. Japanese automotive supply chains are adopting these systems to detect anomalous API access patterns across distributed manufacturing networks.
- Data Loss Prevention:Content inspection engines enforce residency controls for EU AI Act training data provenance requirements.
- Compliance Management:Automated documentation tools for NIS2 Directive and ISO 27018 evidence trails are filtering vendor qualification pools.
Identity Management captures current spend dominance. Threat Detection shows the steepest expansion trajectory.
End User:
Procurement sophistication scales with regulatory exposure, separating compliance-driven mandates from cost-optimized point solutions.
- Large Corporations:Bundled platform contracts spanning identity, network, and workload protection are displacing modular alternatives at German pharmaceutical and French luxury goods conglomerates. These buyers demand contractual liability caps tied to AI system risk tiers under EU AI Act documentation requirements.
- Government Agencies:Sovereign cloud mandates in the United States, Germany, and Japan are creating dedicated procurement channels with localized encryption and residency controls. Federal buyers require FedRAMP or equivalent national certification frameworks that extend sales cycles but lock out uncertified competitors.
- Small Enterprises:Consolidated secure access service edge bundles priced below modular alternatives are capturing manufacturing and professional services firms.
- Educational Institutions:Research universities with classified grant portfolios are adopting hybrid cloud configurations for controlled unclassified information handling.
Large Corporations anchor vendor revenue today. Government Agencies are restructuring procurement fastest.
Service Type:
Margin pools concentrate where liability transfer meets specialized talent scarcity, particularly in Kubernetes-native deployment expertise.
- Managed Services:NIS2 Directive supply-chain liability extensions are forcing provider upgrades to professional indemnity coverage, creating vendor switching windows for certified alternatives. German automotive and Japanese electronics manufacturers are outsourcing 24/7 security operations center functions to MSPs with multi-jurisdiction compliance certifications.
- Integration Services:DevSecOps pipeline construction for cloud-native firewall and Kubernetes orchestration layer synchronization commands premium day rates concentrated in Silicon Valley and Berlin metro areas. U.S. fintech startups and German insurtech ventures are competing for this limited talent pool.
- Consulting Services:Risk classification frameworks for AI-hosted workloads under EU AI Act are driving assessment engagements.
- Support Services:Tiered response commitments differentiate vendor retention contracts.
Managed Services dominate recurring revenue. Integration Services face the tightest supply constraint.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cloud security software originated in U.S. technology corridors during the early 2000s public cloud transition, then diffused through European financial centers and Asian manufacturing hubs as regulatory frameworks matured.
United States
SEC incident disclosure mandates compress response windows for publicly traded firms deploying cloud workload protection. FedRAMP certification requirements lock federal procurement channels to pre-approved vendors. Silicon Valley and Seattle metro areas concentrate Kubernetes-native security engineering talent.
Germany
Automotive manufacturers and industrial conglomerates drive sovereign cloud adoption with localized encryption demands. The EU NIS2 Directive extends supply-chain liability to managed security service providers. Bavaria and Baden-Württemberg host dense clusters of ISO 27017-certified system integrators.
Japan
Electronics conglomerates pursue multi-cloud configurations to reduce vendor lock-in across distributed manufacturing networks. METI guidelines shape national cloud infrastructure standards. Tokyo and Osaka metropolitan areas anchor security operations center outsourcing demand.
United Kingdom
Financial services firms in the City of London expand cloud-native firewall procurement for containerized trading applications. GDPR enforcement continues reshaping cross-border data residency strategies. Manchester and Edinburgh emerge as secondary compliance consulting hubs.
India
IT services exporters and fintech startups accelerate DevSecOps pipeline construction for cloud-native deployment. RBI cybersecurity guidelines tighten payment infrastructure protection requirements. Bangalore and Hyderabad concentrate certified integration specialists serving European and North American clients.
Cloud Security Software Market Key Industry Players
Capital-heavy platform providers compete with asset-light specialized vendors across the cloud security software landscape. The market structure concentrates around bundled multi-cloud governance suites and modular point solutions serving distinct buyer sophistication tiers. Three archetypes dominate: hyperscale cloud operators with native security stacks, independent cybersecurity vendors with Kubernetes-native architectures, and consolidated networking incumbents pivoting toward secure access service edge bundles. Dominant competitive moves include vertical capability integration into adjacent identity and workload protection segments and geographic certification expansion for sovereign cloud compliance.
Within the hyperscale operator tier, Microsoft Corporation and Amazon Web Services occupy foundational positions anchoring enterprise procurement decisions through native API integration and compliance tooling investments. Among independent cybersecurity specialists, Palo Alto Networks and Fortinet exemplify divergent strategic postures—one pursuing cloud-native firewall architectures synchronized with container orchestration layers, the other capturing mid-market expansion through consolidated SASE bundles priced below modular alternatives. Check Point Software Technologies represents the established networking incumbent archetype adapting legacy firewall portfolios toward distributed cloud deployment models.
| Leading Market Players |
|---|
| Microsoft Corporation |
| Amazon Web Services |
| Broadcom |
| Palo Alto Networks |
| Check Point Software Technologies |
| Fortinet |
| Cisco Systems |
| Trend Micro |
| SentinelOne |
| Others |
Cost & Logistics Intelligence
Horizontal integration across managed security service providers anchors supply positioning and pricing power for cloud security software vendors. NIS2 Directive liability extensions force European enterprises to consolidate procurement around certified providers with multi-jurisdiction compliance coverage, compressing vendor pools and supporting premium pricing for qualified alternatives.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels dominates cloud security software procurement, with premium tiers capturing ISO 27017/27018-certified configurations and dedicated sovereign cloud deployments. Price differentiation rests on certification grade and geographic delivery cost, with German and Japanese residency controls commanding substantial premiums over standard multi-tenant offerings. Cost compression in the standard tier is intensifying because hyperscale operators bundle native security APIs at marginal cost. Small enterprises and mid-market manufacturing firms exhibit the highest price sensitivity, while financial services and government agencies accept premium pricing for liability transfer and audit readiness.
Supply Chain Analysis
Dual-sourcing requirements from large European and Japanese enterprises mandate multi-supplier qualification for critical security functions, fragmenting vendor concentration. Engineering talent concentrates in the United States, Germany, and India, with Kubernetes-native expertise anchored in Silicon Valley and Berlin metro areas. Raw material dependencies include specialized semiconductor hardware for encryption accelerators, proprietary threat intelligence feeds, and certified data center real estate. Single-source vulnerability in DevSecOps talent pipelines creates supply risk during expansion cycles. Distribution runs through direct enterprise sales teams for large accounts and hyperscaler marketplaces for mid-market adoption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The cloud security software market functions as a stable compounder, with regulatory compliance mandates across the EU, United States, and Japan creating durable replacement cycles and vendor stickiness.
For Market Incumbents: Deepen vertical integration into threat intelligence data pipelines and sovereign cloud infrastructure to defend against hyperscale operator bundling. Invest in FedRAMP and German BSI certification expansion to lock federal procurement channels. Prioritize automated compliance documentation tooling for EU AI Act risk classification requirements. For New Entrants and Emerging Players: Enter via mid-market SASE consolidation in manufacturing and professional services verticals, where bundled pricing below modular alternatives opens whitespace. Target Japanese electronics supply chains with multi-cloud governance platforms that reduce vendor lock-in. Pursue channel partnerships with established system integrators in Bangalore and Hyderabad to bypass direct sales buildout costs. For Investors and Strategic Acquirers: Roll-up economics work for Kubernetes-native security specialists because talent scarcity and certification complexity create natural barriers to organic entry. The five-to-ten year viability window favors platforms with existing hyperscaler marketplace presence and multi-jurisdiction compliance coverage. Monitor NIS2 Directive enforcement actions as the signal to watch for vendor switching velocity inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies identity, workload, and threat detection layers for German automotive manufacturers. |
| Sovereign Cloud Certification | Unlocks dedicated procurement channels under German BSI and Japanese METI frameworks. |
| Strategic Partnership | Accelerates Kubernetes-native firewall deployment through hyperscaler marketplace listings. |
| Acquisition of Specialist Firm | Captures scarce DevSecOps talent concentrated in Silicon Valley and Berlin metro areas. |
| Geographic Expansion | Addresses EU AI Act compliance documentation demand from French pharmaceutical manufacturers. |
Research Approach
Bottom-up enterprise deployment modeling reconciled against top-down vendor revenue tracking forms the analytical core of this study. Primary interviews with CISOs, cloud architects, IT procurement officers, and managed security service provider executives were cross-validated against secondary sources including SEC filings, hyperscaler capex disclosures, FedRAMP authorization databases, and EU regulatory implementation guidance. Triangulation between demand-side budget allocation surveys and supply-side product roadmap disclosures ensured segmentation integrity.
Input-output matrices mapped deployment architecture, solution category, and end-user scale against regulatory framework adoption curves across the analysis window. Modeled dimensions included hybrid versus multi-cloud configuration, identity management versus threat detection spend allocation, and sovereign cloud mandate compliance status. CAGRs were derived from fitted growth curves adjusted for ISO 27017 procurement mandate acceleration and SEC incident disclosure timeline compression.
Inputs from regulatory filings and vendor product announcements were available through the study window; gaps in private company financial disclosures introduce uncertainty bands around mid-market SASE bundle penetration estimates. Forecasts reflect documented assumptions about NIS2 Directive enforcement intensity and Kubernetes talent pipeline expansion. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Contactless Smart Card Market
Security Software
Global Cloud IAM Market
Security Software
Doorbell Camera Market
Security Software
North America Video Management System Market
Security Software
Cyber Attack Simulation Software Market
Security Software
Europe Enterprise Firewall Market
Security Software
Embedded Security Market
Security Software
Asia-Pacific Encryption Software Market
Security Software
Global Background Check Software Market
Security Software
Parental Monitoring Software Market
Security Software
Europe Anti-Money Laundering Software Market
Security Software
Web Content Filtering Market
Security Software
Enterprise Rights Management Solution Market
Security Software
GDPR Software and Tools Market
Security Software
Global Advanced Authentication Market
Security Software
Global Software-Defined Security Market