
 Japan Cybersecurity Market | 2026-2036
Japan Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Japan Cybersecurity Market Outlook
Mid-market manufacturers is rotating toward managed detection and response services as Japan's factory digitization deepens. Trend Micro anchors its position through endpoint specialization across industrial control environments. NEC Corporation leverages domestic channel control to dominate government and critical infrastructure bids. SoftBank Technology competes on cloud-native security stacks for enterprise hybrid deployments.
Japan cybersecurity encompasses hardware, software, and services engineered to protect digital assets against unauthorized access, disruption, or data exfiltration through cryptographic protocols, behavioral analytics, and network segmentation operating at throughput rates exceeding 100 Gbps in next-generation firewalls. Network Security captures the largest installed base due to legacy perimeter investments, while Cloud Security registers the fastest expansion as Japanese enterprises migrate SAP and Oracle workloads to domestic and hyperscale platforms. Endpoint Security maintains mature margins in regulated verticals where antivirus and EDR agents face mandatory deployment under supply-chain security frameworks.
METI's Cybersecurity Management Guidelines, alongside JIS Q 27001 alignment and PMDA data integrity requirements for medical device software, compel systematic risk assessment and third-party audit cycles across covered entities. The country's national cybersecurity regulator enforces incident reporting timelines that shorten product update cycles and elevate managed services attachment rates. Stakeholders must monitor evolving critical infrastructure designations and corresponding compliance scope expansions that reshape addressable market boundaries.
Market Dynamics
Zero-trust architecture mandates from METI are compressing legacy perimeter security procurement cycles as Japanese financial institutions and manufacturers simultaneously restructure network access protocols.
Growth Catalysts
- Factory digitization:Manufacturing IoT deployments across Osaka's industrial corridor are expanding attack surfaces that require continuous monitoring and automated response capabilities.
- METI Cybersecurity Management Guidelines:Revised compliance frameworks mandate systematic risk assessment cycles that elevate managed security services attachment rates among covered entities.
- Cloud migration:Enterprise SAP and Oracle workload shifts to domestic and hyperscale platforms are accelerating demand for cloud-native security stacks and hybrid environment protection.
Market Restraints
- Specialized talent scarcity:Domestic shortage of industrial control system security engineers constrains deployment velocity for manufacturing sector projects.
- Legacy infrastructure lock-in:Extensive installed base of legacy network security equipment in Tokyo's enterprise corridor delays full-stack modernization timelines.
- Compliance cost burden:JIS Q 27001 alignment and PMDA data integrity requirements impose recurring audit expenses that compress mid-market vendor margins.
Strategic Opportunities
- Managed detection and response:Mid-market manufacturers rotating from product-centric to service-centric security procurement create white space for subscription revenue models.
- Medical device cybersecurity:PMDA software integrity requirements for connected healthcare equipment open specialized verticals with premium pricing tolerance.
- Critical infrastructure expansion:Evolving government designations of critical systems extend compliance scope to previously uncovered industrial operators.
Industry Challenges
- Integration complexity:Operational technology environments in manufacturing facilities resist seamless integration with IT security tools without production downtime.
- Certification timeline compression:Shortened incident reporting deadlines under national cybersecurity regulator enforcement strain product update cycles and quality assurance protocols.
- Supply chain security verification:Mandatory deployment of antivirus and EDR agents under supply-chain frameworks requires vendor coordination across multi-tier supplier networks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Japan Cybersecurity Market |
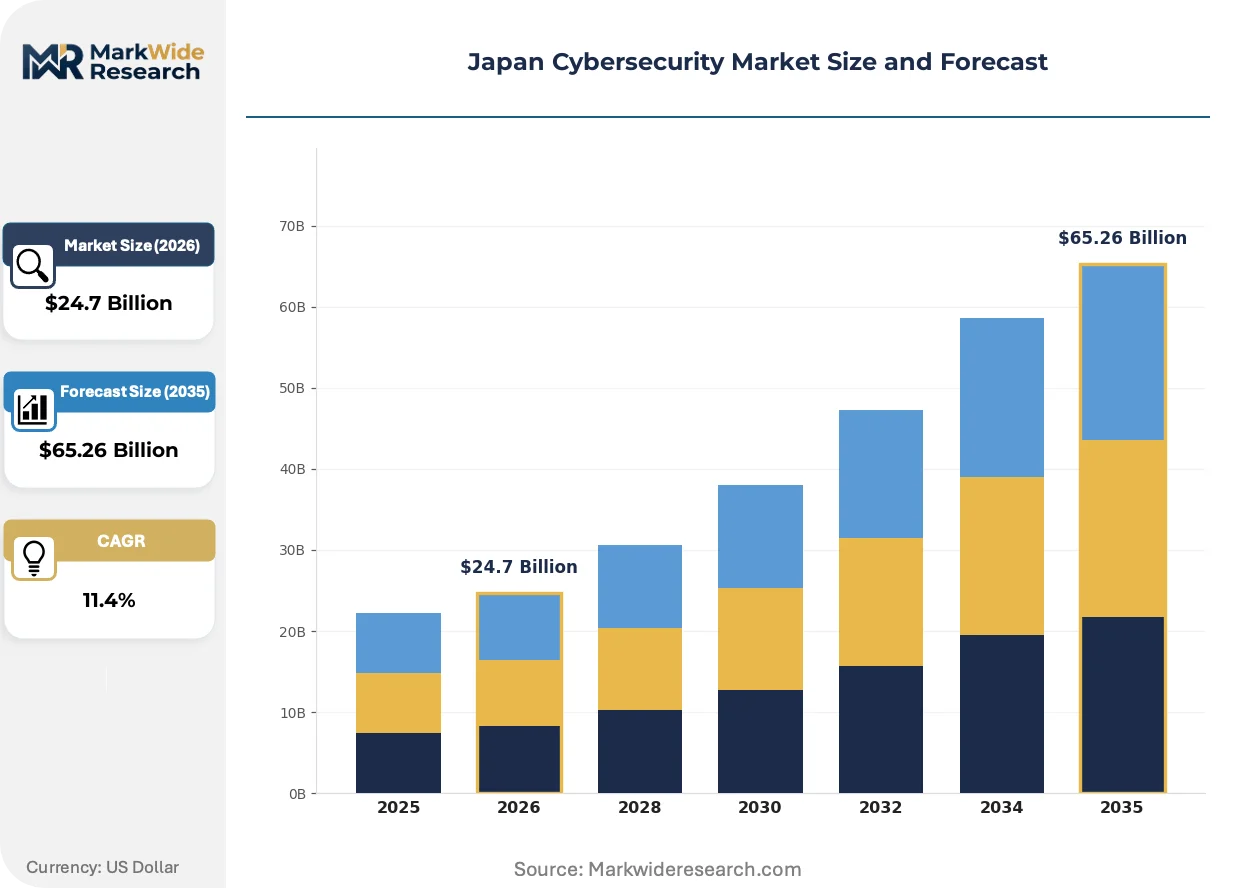
| Market Size in 2026 | $24.7 Billion |
| Market Size in 2035 | $65.26 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Intrusion Detection System, Antivirus, Encryption Application: Network Security, Cloud Security, Endpoint Security, Application Security End User: Government, BFSI, Healthcare, Retail Deployment: On-premises, Cloud-based, Hybrid, Managed Services |
| Companies Covered | NTT Security, SoftBank Technology, Trend Micro, Check Point Software Technologies, Cisco Systems, NEC Corporation, Hitachi Systems, Secure Brain Corporation, Fujitsu, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Japan Cybersecurity Market Strategic Shifts
Behavioral analytics engines are replacing signature-based detection as the primary threat identification mechanism across Japanese enterprise security stacks.
Extended detection and response platforms consolidate endpoint, network, and cloud telemetry into unified analysis layers that reduce mean-time-to-detection metrics. Financial institutions in Tokyo's enterprise corridor are adopting these platforms at accelerated procurement cycles. This consolidation is displacing standalone point-product deployments that previously dominated security architecture budgets.
METI's revised Cybersecurity Management Guidelines now explicitly address supply-chain risk assessment obligations for covered entities. Industrial manufacturers must document third-party security postures across their supplier networks. Osaka's manufacturing cybersecurity clusters are responding by embedding security requirements into procurement contracts and vendor qualification processes.
Japanese enterprises are unbundling after-sales service from perpetual license agreements in favor of subscription-based managed security outcomes. Mid-market manufacturers are driving this shift as they seek predictable operational expenditures over capital-intensive security infrastructure ownership. This behavioral change is most visible among factory digitization projects where internal security operations center staffing remains economically unviable.
Japan Cybersecurity Market Segmentation
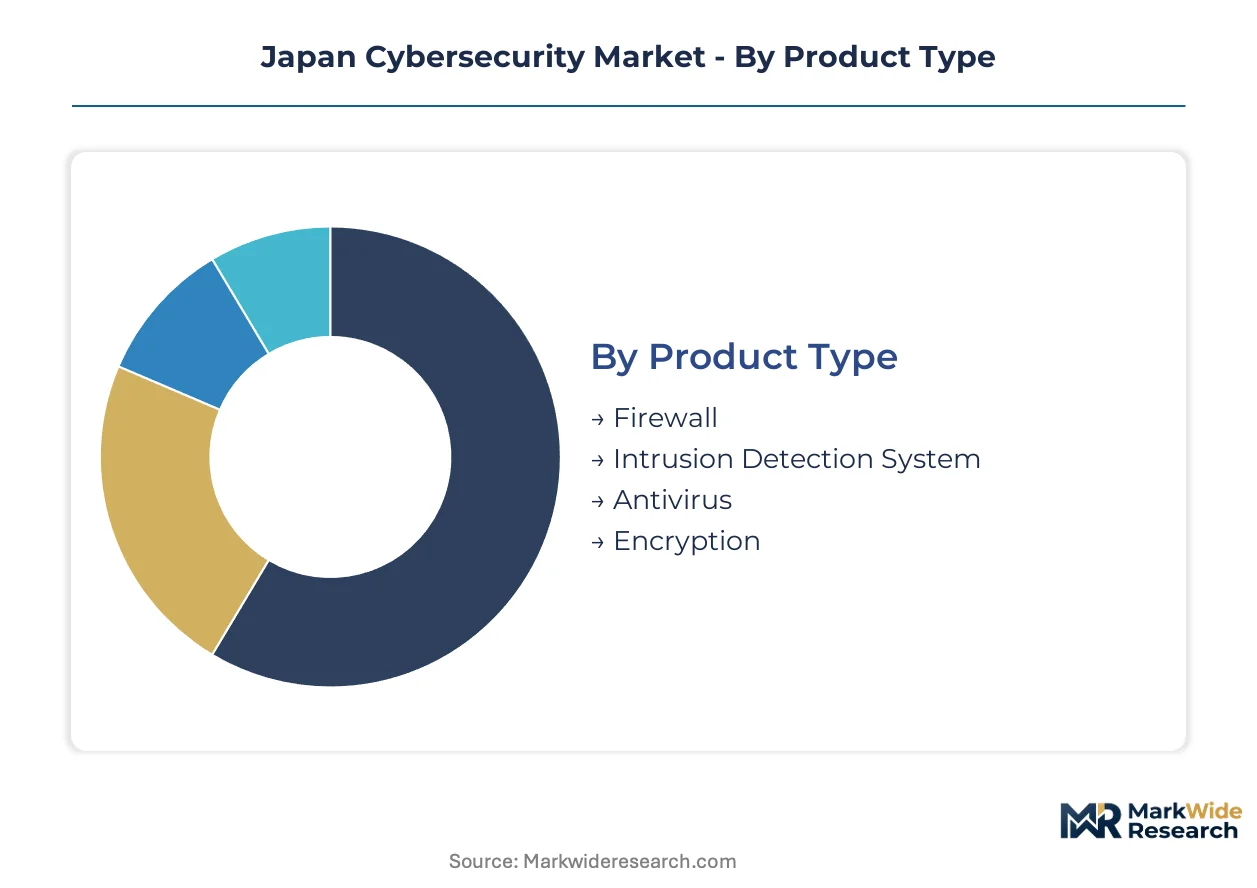
Segmentation reveals how METI compliance mandates and factory digitization reshape procurement patterns across Japan's cybersecurity landscape. Distinct buyer behaviors emerge between legacy-heavy network security buyers and cloud-native adopters in financial services.
Product Type:
Firewall and antivirus segments face acute substitution pressure from behavioral analytics platforms that displace signature-based detection across Tokyo's enterprise corridor.
- Firewall:Next-generation appliances process throughput exceeding 100 Gbps using deep packet inspection and application-aware filtering. Osaka's manufacturing cybersecurity clusters deploy these at network perimeters to segment operational technology environments from corporate IT systems under METI's zero-trust mandates.
- Intrusion Detection System:Network-based and host-based sensors monitor traffic anomalies through machine learning classifiers trained on Japanese-language threat intelligence. Financial institutions in Tokyo accelerate IDS refresh cycles as legacy perimeter architectures collapse under revised Cybersecurity Management Guidelines.
- Antivirus:Signature-matching engines now embed within broader endpoint detection platforms rather than operating as standalone agents.
- Encryption:Hardware security modules and data-at-rest protocols address PMDA data integrity requirements for medical device software and JIS Q 27001 alignment.
Firewall anchors the volume base while intrusion detection systems gain share at the steepest rate as behavioral analytics displace rule-based monitoring.
Application:
Cost tier differentiation separates premium cloud-native stacks from commoditized endpoint agents across Japan's buyer landscape.
- Network Security:Legacy perimeter investments dominate installed base with next-generation firewalls and secure web gateways. Tokyo's enterprise corridor sustains refresh demand despite zero-trust migration, as hybrid architectures retain hardware-dependent inspection points for regulated traffic flows.
- Cloud Security:Native workload protection and CASB platforms secure SAP and Oracle migrations to domestic hyperscale environments. Mid-market manufacturers adopt these fastest as factory digitization eliminates capital-intensive security infrastructure ownership.
- Endpoint Security:Mature margins persist in regulated verticals where EDR agents face mandatory deployment under supply-chain security frameworks.
- Application Security:Code scanning and runtime protection address software integrity in connected medical devices and industrial control systems.
Network security captures the largest revenue pool while cloud security climbs the fastest as enterprise workload migration accelerates.
End User:
Customer type determines procurement sophistication, with government buyers enforcing strict domestic channel requirements that elevate NEC Corporation's position.
- Government:Critical infrastructure designations and national cybersecurity regulator enforcement compel systematic risk assessment cycles. METI's Cybersecurity Management Guidelines mandate third-party audit requirements that elevate managed services attachment rates across central and prefectural agencies.
- BFSI:Zero-trust architecture mandates compress legacy procurement cycles as financial institutions restructure network access protocols. Tokyo's banking concentration drives consolidated platform purchases displacing point-product deployments.
- Healthcare:PMDA software integrity requirements for connected medical devices open specialized verticals with premium pricing tolerance.
- Retail:Point-of-sale protection and e-commerce fraud prevention address supply-chain security verification across multi-tier supplier networks.
Government anchors the volume base while healthcare gains share at the steepest rate as medical device connectivity expands attack surfaces.
Deployment:
Supply concentration in managed services channels reshapes how Japanese enterprises consume security capabilities versus in-house operations.
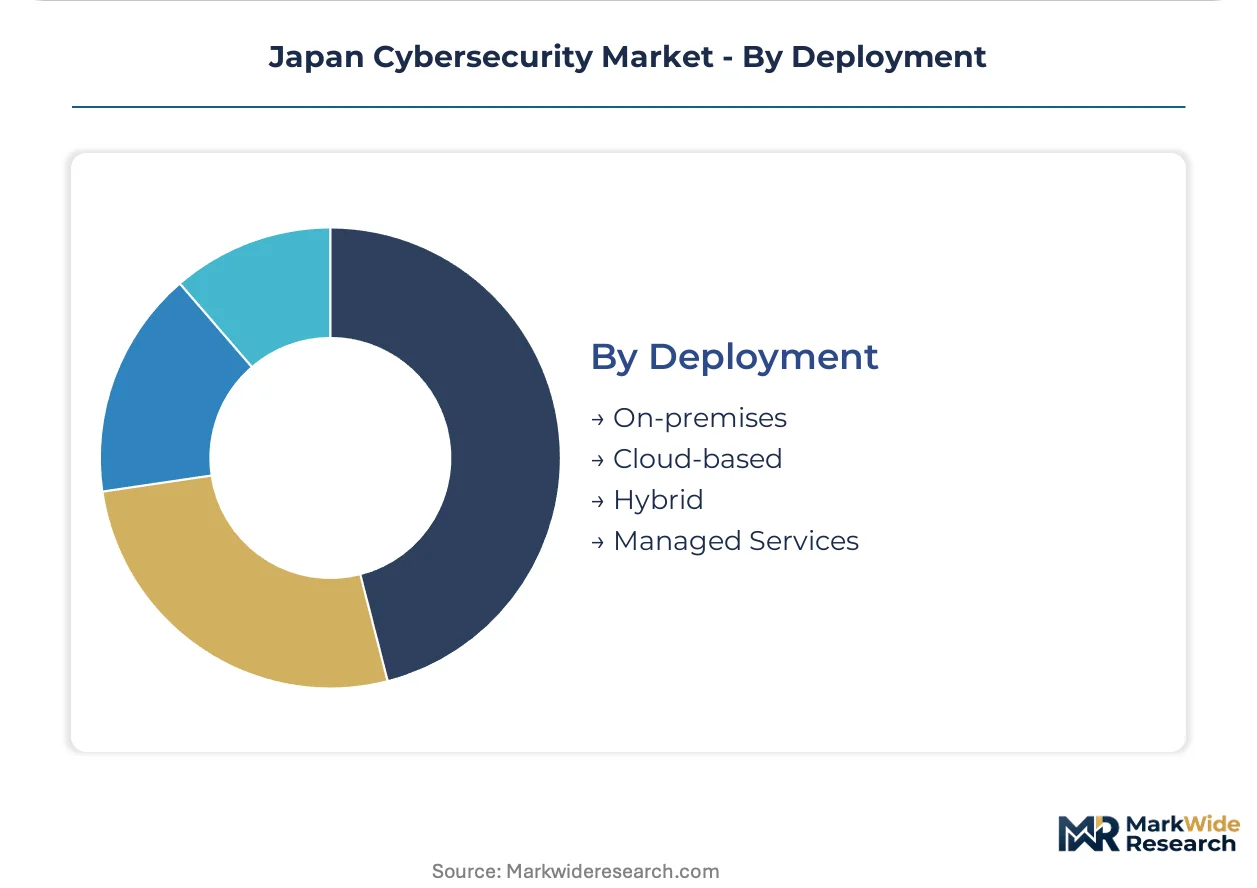
- On-premises:Hardware appliances and perpetual software licenses persist in regulated environments requiring air-gapped operational technology networks. Osaka's manufacturing clusters retain these for industrial control system segmentation where cloud connectivity remains prohibited.
- Cloud-based:SaaS-delivered security controls scale elastically with enterprise cloud migration patterns. SoftBank Technology competes aggressively in this segment for hybrid deployment scenarios.
- Hybrid:Split architectures combine on-premises inspection with cloud-native analytics for transitional zero-trust implementations.
- Managed Services:Subscription-based outcomes replace capital-intensive ownership as mid-market manufacturers seek predictable operational expenditures.
On-premises deployment anchors the volume base while managed services gains share at the steepest rate as internal security operations center staffing proves economically unviable for factory digitization projects.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Japan's cybersecurity market concentrates along the Tokaido Shinkansen corridor, where fiber-optic trunk lines and data center clusters connect Tokyo, Nagoya, and Osaka into a contiguous digital infrastructure zone.
Kanto/Tokyo
Financial institutions and government agencies drive zero-trust architecture procurement in the capital region. METI's Cybersecurity Management Guidelines mandate systematic risk assessment cycles that elevate managed security services attachment rates. Tokyo's enterprise corridor sustains refresh demand for next-generation firewalls and intrusion detection systems as hybrid architectures retain hardware-dependent inspection points.
Kansai/Osaka
Manufacturing IoT deployments across Osaka's industrial corridor expand attack surfaces requiring continuous monitoring. Factory digitization projects eliminate capital-intensive security infrastructure ownership, rotating mid-market manufacturers toward subscription-based managed detection and response. Industrial control system segmentation persists in air-gapped operational technology networks where cloud connectivity remains prohibited.
Chubu/Nagoya
Automotive and precision equipment manufacturers anchor demand for operational technology security in Japan's central industrial belt. PMDA data integrity requirements for connected medical devices open specialized verticals with premium pricing tolerance. Nagoya's manufacturing base embeds security requirements into procurement contracts and vendor qualification processes.
Kyushu
Semiconductor fabrication facilities and renewable energy infrastructure drive critical infrastructure protection spending in Japan's southwestern manufacturing hub. National cybersecurity regulator enforcement compels shortened incident reporting timelines that strain product update cycles. Fukuoka's emerging tech corridor attracts cloud-native security stack deployments for enterprise hybrid implementations.
Tohoku
Post-disaster reconstruction investments and smart grid modernization create cybersecurity demand in Japan's northeastern region. Supply-chain security frameworks mandate antivirus and EDR agent deployment across multi-tier supplier networks. Sendai's medical device manufacturing cluster addresses PMDA software integrity requirements through specialized encryption and hardware security module adoption.
Japan Cybersecurity Market Competitive Environment
Concentration sits with domestic system integrators and global platform vendors competing across distinct capability layers. The vendor base separates into three strategic archetypes: telecommunications-affiliated security providers leveraging infrastructure control, specialized endpoint protection vendors with industrial control expertise, and multinational platform companies competing on cloud-native stacks. Competitive moves center on managed services portfolio expansion and zero-trust architecture certification acceleration.
Among telecommunications-affiliated providers, NTT Security and SoftBank Technology anchor the domestic infrastructure layer. Trend Micro exemplifies the specialized endpoint protection archetype with industrial control environment focus. NEC Corporation occupies a position within the government and critical infrastructure bid ecosystem through domestic channel control. These three patterns represent how vendor positioning aligns with buyer procurement sophistication across regulated verticals.
| Leading Market Players |
|---|
| NTT Security |
| SoftBank Technology |
| Trend Micro |
| Check Point Software Technologies |
| Cisco Systems |
| NEC Corporation |
| Hitachi Systems |
| Secure Brain Corporation |
| Fujitsu |
| Others |
Value Chain & Pricing Dynamics
Subscription-based capacity reservation contracts dominate Japanese cybersecurity procurement, locking in multi-year service access for financial institutions while insulating managed security providers from spot-market volatility. METI compliance mandates enforce systematic audit cycles that elevate attachment rates for bundled service tiers.
Pricing Analysis
Volume-discount tiering structures separate enterprise-grade zero-trust deployments from mid-market managed detection packages. Pricing stratifies across premium certification tiers, JIS Q 27001 alignment levels, and bundled after-sales support depth. Cost compression in standard-tier endpoint security is intensifying because antivirus commoditization displaces standalone agent margins. Mid-market manufacturers exhibit highest price sensitivity, while government buyers tolerate premium pricing for domestic channel compliance.
Supply Chain Analysis
Inventory lead times for hardware security modules and next-generation firewall appliances stretch due to semiconductor fabrication bottlenecks in Taiwan and South Korea. Component sourcing draws from specialized foundries in Japan, Malaysia, and Germany for cryptographic processors and deep packet inspection chipsets. Single-source vulnerability concentrates in Taiwan-based semiconductor supply for 100 Gbps+ throughput appliances. Distribution runs through domestic system integrators and telecommunications-affiliated channels rather than direct vendor relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation opportunity emerges as factory digitization fragments buyer needs across operational technology segmentation, cloud-native migration timelines, and compliance maturity tiers. Niche specialization rewards vendors addressing specific integration complexity pain points.
For Market Incumbents: Compound defensive positioning through accelerated zero-trust architecture certification and captive supply of industrial control system security engineering talent. Threat substitution from cloud-native security stacks demands backward integration into managed services delivery. Channel control in government procurement remains the priority lever against multinational platform encroachment.
For New Entrants and Emerging Players: Differentiate on medical device cybersecurity specialization targeting PMDA software integrity requirements. White space concentrates in mid-market manufacturing clusters rotating from capital-intensive ownership to subscription outcomes. Go-to-market through Osaka industrial corridor partnerships bypasses Tokyo's incumbent-dominated enterprise corridor.
For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed detection and response providers serving factory digitization projects. Long-term viability across the analysis window favors vendors with operational technology integration capabilities and METI guideline certification velocity. Acquisition targets should demonstrate domestic channel relationships and critical infrastructure designation coverage. Signal to monitor: evolving government critical infrastructure scope expansions that extend compliance mandates to previously uncovered industrial operators.
| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Certification | Accelerates procurement eligibility under METI's revised Cybersecurity Management Guidelines for financial institutions. |
| Managed Detection and Response Portfolio Expansion | Captures mid-market manufacturer demand for predictable operational expenditures over capital ownership. |
| Industrial Control System Security Talent Acquisition | Addresses domestic scarcity constraining deployment velocity for Osaka manufacturing corridor projects. |
| Medical Device Cybersecurity Specialization | Opens PMDA-regulated verticals with premium pricing tolerance for connected healthcare equipment. |
| Domestic Channel Partnership Deepening | Secures government and critical infrastructure bid access against multinational platform competition. |
Study Parameters
Two parallel data streams informed the analysis: structured interviews with CISOs at financial institutions and manufacturing enterprises, and secondary validation through METI regulatory filings, JIS Q 27001 certification databases, and hyperscaler security stack disclosures. Primary fieldwork engaged cybersecurity procurement officers, industrial control system engineers, and managed services delivery leads. Secondary sources included PMDA medical device software guidance documents, national cybersecurity regulator enforcement records, and customs data on hardware security module imports. Bottom-up segment sizing triangulated against top-down macroeconomic anchors.
Across the projection horizon, the analytical framework modeled deployment mode transitions, organization size tiers, vertical regulatory intensity, and regional adoption clusters spanning Tokyo, Osaka, Nagoya, and Fukuoka corridors. CAGRs derived from segment-level growth rate reconciliation against aggregate market boundary conditions. Forecast inputs incorporated cloud migration velocity for SAP and Oracle workloads, factory digitization investment cycles, and compliance scope expansion trajectories under evolving critical infrastructure designations.
Material uncertainties — regulatory timeline shifts, semiconductor supply disruptions, and industrial control system integration failure rates — sit outside the modeled envelope. Forecasts reflect documented assumptions about METI guideline enforcement consistency and mid-market manufacturer subscription conversion rates. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market
Cybersecurity
Cyber Warfare Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Threat Hunting Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Cryptojacking Solution Market
Cybersecurity
Global API Security Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Global Healthcare IoT Security Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Ddos Protection and Mitigation Security Market
Cybersecurity
Europe Web Application Firewall Market