
 SD-WAN Security Market | 2026-2036
SD-WAN Security Market Size, Share, and Industry Trends Forecast 2026-2036
SD-WAN Security Market Analytics
Subscription-based security-as-a-service bundling is rebalancing how SD-WAN vendors monetize customer relationships. Cisco leverages its installed base of routing equipment to anchor security upsells across enterprise accounts. Fortinet sustains competitive pressure through integrated firewall-SD-WAN appliances that reduce vendor sprawl. Palo Alto Networks differentiates via cloud-delivered branch security that collapses multiple point products into unified policy management.
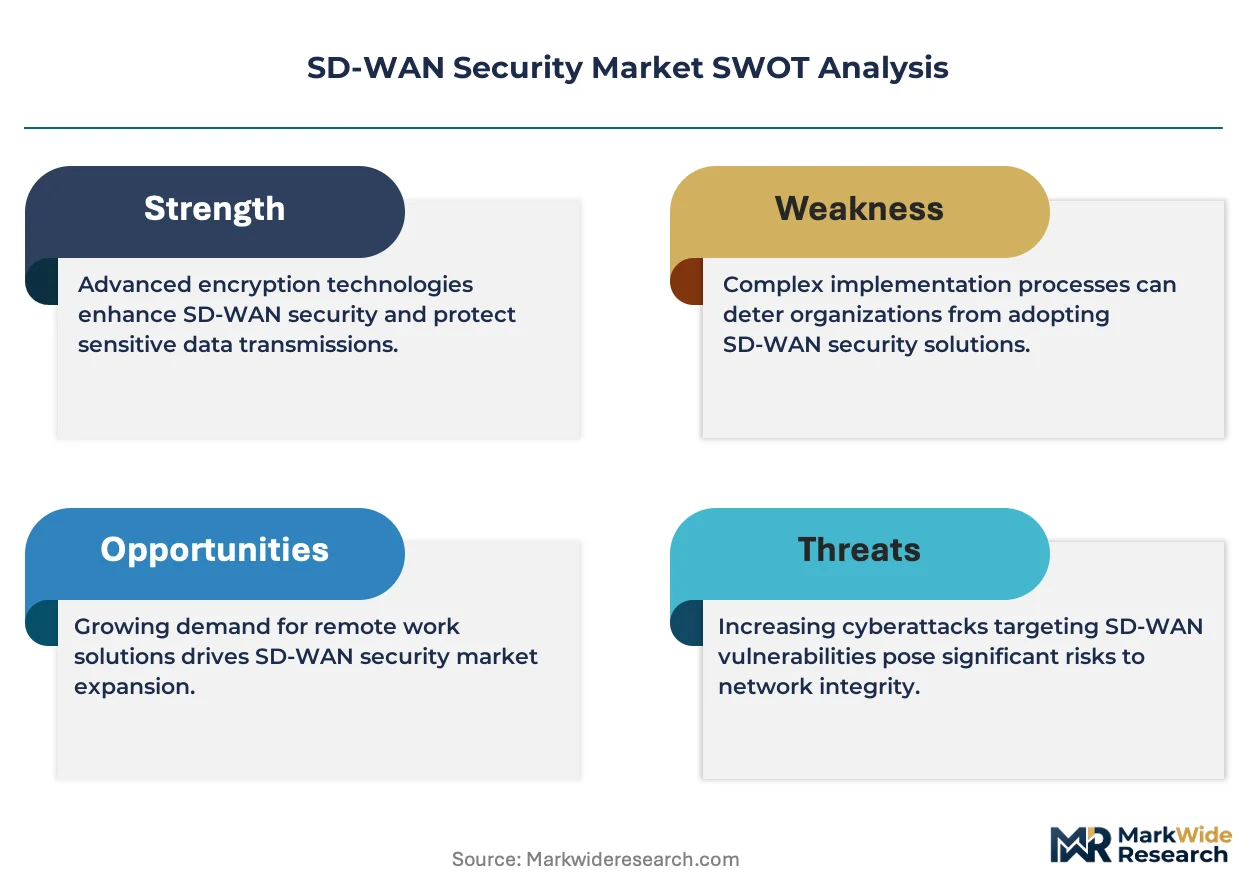
SD-WAN Security encompasses software-defined wide area networking architectures with embedded threat protection, encompassing encryption protocols, zero-trust access verification, and real-time traffic inspection across distributed enterprise locations. The technology serves commercial and industrial purposes by enabling secure direct-to-cloud connectivity without backhauling traffic through centralized data centers. Managed Services captures recurring revenue from enterprises lacking internal security operations capacity, while Hybrid Cloud deployment models attract organizations navigating phased cloud migration. Threat Intelligence represents the fastest-growing technology segment as behavioral analytics displace signature-based detection in branch security stacks.
FCC guidelines on communications infrastructure security intersect with NIST zero-trust mandates to reshape federal procurement specifications for SD-WAN deployments. ISO 27001 and IEC 62443 standards further constrain product design for multinational manufacturers operating critical infrastructure networks. Stakeholders must monitor evolving certification requirements as sovereign data-residency rules fragment what constitutes acceptable cross-border traffic inspection architecture.
Market Dynamics
Zero-trust architecture mandates are compressing procurement cycles as federal and enterprise buyers replace legacy perimeter-based security with identity-verified network access. This structural shift forces SD-WAN vendors to embed continuous authentication and microsegmentation into core platform offerings.
Growth Catalysts
- NIST SP 800-207:Federal agencies in the United States must implement zero-trust principles by fiscal deadlines, accelerating replacement of hub-and-spoke WAN architectures with direct-to-cloud SD-WAN deployments.
- Branch digitization in financial services:Retail banking networks require encrypted transaction processing at thousands of distributed locations, pulling secure SD-WAN into core infrastructure budgets.
- Behavioral analytics engines:Threat intelligence platforms using machine learning for anomaly detection are displacing signature-based branch firewalls in enterprise security stacks.
Market Restraints
- Semiconductor supply concentration:Custom ASIC production for high-throughput SD-WAN appliances depends on Taiwan-based foundry capacity, creating procurement risk for specialized encryption hardware.
- Fragmented sovereign data rules:Cross-border traffic inspection architectures face compliance friction as Germany, France, and Japan impose divergent data-residency requirements on cloud-delivered security services.
- Skills scarcity in SASE integration:Enterprise IT teams lack personnel trained in converging SD-WAN with cloud-native security service edge frameworks, delaying deployment timelines.
Strategic Opportunities
- Managed security service provider channel:Mid-market enterprises without internal security operations centers present recurring revenue potential for channel partners bundling SD-WAN with 24/7 threat monitoring.
- Industrial IoT edge protection:Manufacturing facilities deploying IEC 62443-compliant network segmentation require hardened SD-WAN gateways for operational technology isolation.
- Post-quantum cryptography preparation:NIST's post-quantum encryption standards create upgrade cycles for federal contractors refreshing branch security infrastructure ahead of compliance deadlines.
Industry Challenges
- Multi-vendor orchestration complexity:Enterprises operating hybrid cloud environments struggle to unify policy management across disparate SD-WAN, firewall, and identity platforms.
- Certification timeline compression:ISO 27001 and SOC 2 audit requirements for managed SD-WAN services extend sales cycles as providers document control frameworks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | SD-WAN Security Market |
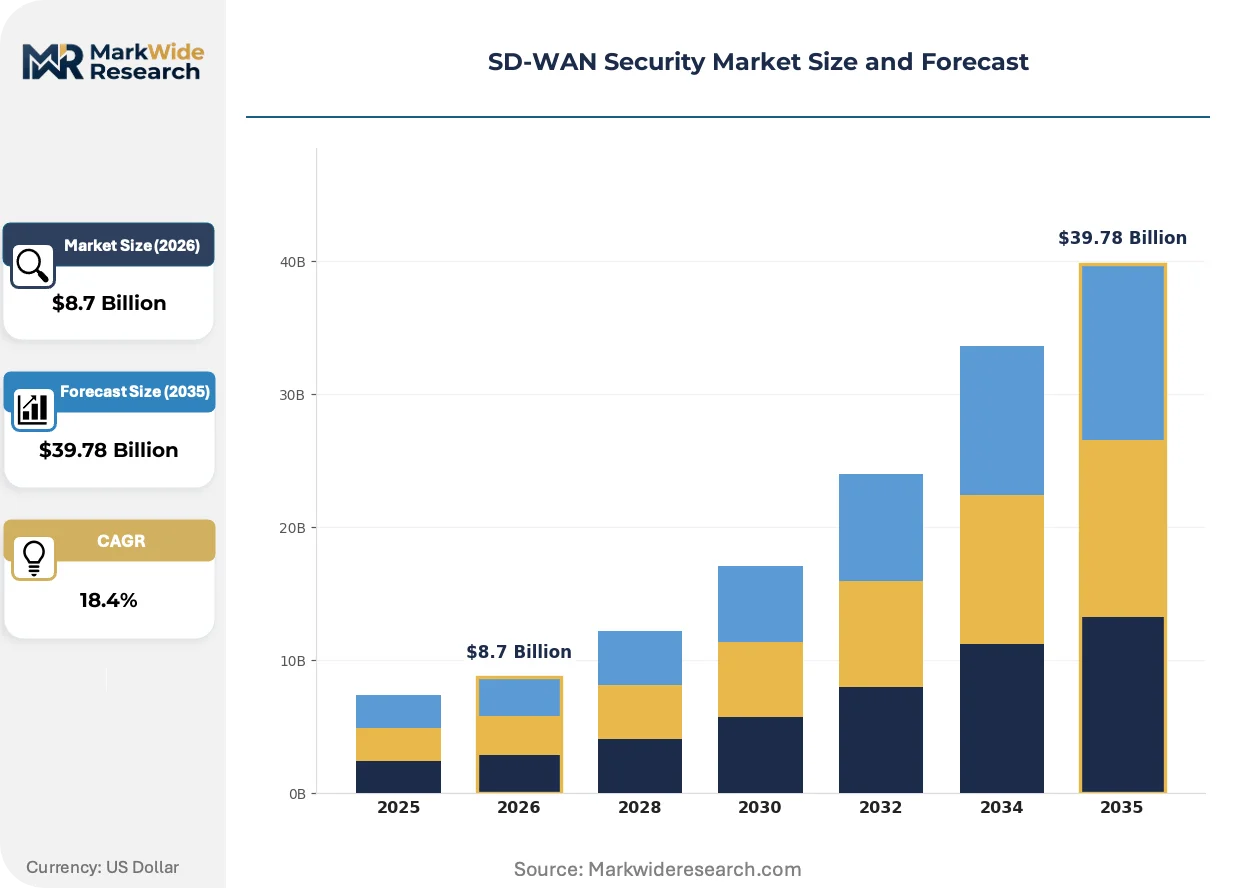
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $39.78 Billion |
| CAGR (2026 – 2036) | 18.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Services, Security-as-a-Service, Professional Services, Consulting Services Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, On-Premises End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Agencies Technology: Firewall, Intrusion Prevention System, Threat Intelligence, Secure Web Gateway |
| Companies Covered | Cisco, Fortinet, VMware, Palo Alto Networks, Hewlett Packard Enterprise, Juniper Networks, Versa Networks, Zscaler, Check Point Software, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
SD-WAN Security Market Evolving Landscape
Artificial intelligence is embedding autonomous threat response into distributed network edges, compressing the window between detection and remediation. This evolution demands new architectural choices around where inference workloads execute.
Secure access service edge frameworks are expanding into mid-market branch deployments by collapsing SD-WAN, firewall-as-a-service, and zero-trust network access into single-vendor cloud stacks. Regional banks and healthcare clinic networks adopt these converged platforms to eliminate point-product procurement. The consolidation is expanding into adjacent security categories as vendors bundle cloud access security broker and data loss prevention functions.
FCC guidelines on communications infrastructure security intersect with NIST zero-trust mandates to reshape federal procurement specifications for SD-WAN deployments. Equipment vendors must now document supply chain provenance and firmware integrity attestation to qualify for government contracts. Defense contractors and critical infrastructure operators face the steepest compliance burden as these requirements layer onto existing DFARS cybersecurity clauses.
Subscription-based consumption models are displacing perpetual licensing in enterprise SD-WAN procurement, with buyers preferring operational expenditure treatment and bundled support. Managed service providers capture margin by aggregating multi-tenant platform licenses across customer bases. This shift is most visible in United States healthcare and financial services verticals where capital expenditure constraints favor predictable monthly security spending.
SD-WAN Security Market Segmentation
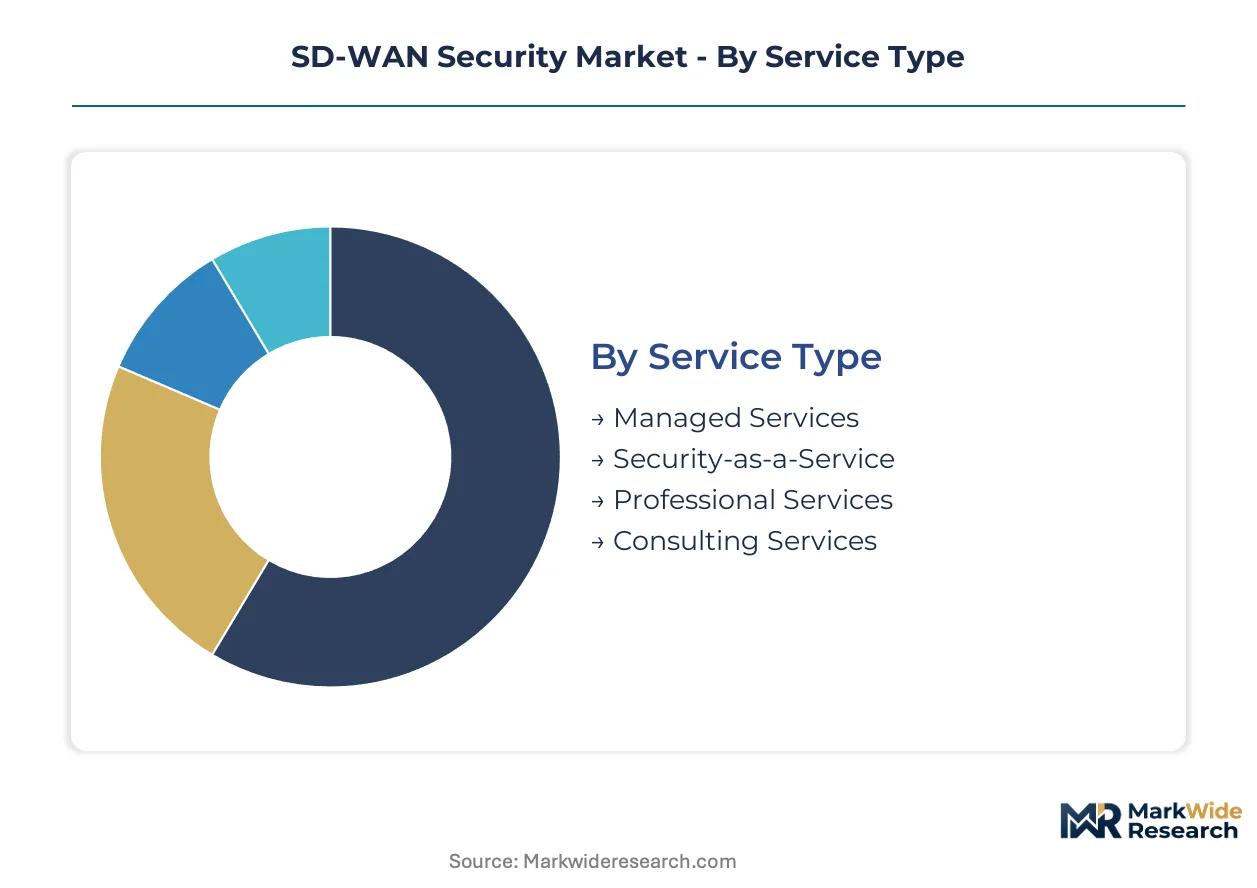
SD-WAN Security procurement patterns diverge sharply across service delivery models, infrastructure ownership structures, and organizational scale. Segment boundaries determine vendor selection criteria, pricing mechanisms, and deployment complexity for distributed network architectures.
Service Type:
Capital intensity concentrates in managed service relationships requiring dedicated security operations infrastructure and multi-tenant platform investments.
- Managed Services:Providers deploy and operate SD-WAN security stacks through 24/7 security operations centers, absorbing capital expenditure for hardware and specialized personnel. Financial services institutions in the United States and Germany favor this model to satisfy regulatory audit requirements without building internal SOCs.
- Security-as-a-Service:Cloud-native delivery eliminates premise-based appliance procurement through subscription consumption. Mid-market enterprises across Japan prioritize this segment to compress deployment timelines and shift spending to operational budgets.
- Professional Services:Implementation and integration support for complex multi-vendor environments.
- Consulting Services:Advisory engagements for zero-trust architecture design and compliance roadmap development.
Most installed capacity flows through Managed Services. Expansion is steepest in Security-as-a-Service.
Deployment Model:
Control requirements and data sovereignty obligations segment buyers across infrastructure ownership spectra.
- Hybrid Cloud:Organizations maintain selective on-premises gateways for latency-sensitive traffic while routing cloud-bound sessions through cloud-native security stacks. Manufacturing networks in Germany adopt this architecture to satisfy IEC 62443 segmentation mandates while enabling direct SaaS connectivity.
- Public Cloud:Fully cloud-delivered SD-WAN security eliminates premise hardware through edge-PoP architectures. United States healthcare clinic networks deploy this model to satisfy HIPAA technical safeguards without capital-intensive branch infrastructure.
- Private Cloud:Single-tenant deployments for organizations with strict data residency requirements.
- On-Premises:Self-managed appliance stacks for air-gapped or classified network environments.
Hybrid Cloud carries the heaviest integration burden. Public Cloud is gaining share fastest among new deployments.
End User:
Organizational scale dictates procurement authority, compliance exposure, and internal technical capacity.
- Large Enterprises:Multi-thousand-branch networks with dedicated procurement teams and complex multi-vendor orchestration requirements. These organizations in the United States negotiate enterprise licensing agreements and demand API-driven policy automation across heterogeneous security stacks.
- Government Agencies:Federal buyers subject to NIST SP 800-207 zero-trust mandates and FCC supply chain integrity guidelines. United States defense contractors face layered DFARS cybersecurity clauses atop baseline requirements.
- Medium Enterprises:Organizations with 100-999 employees seeking converged platforms to reduce vendor sprawl.
- Small Enterprises:Limited IT staff driving preference for fully managed service bundles with minimal configuration overhead.
Large Enterprises command the deepest customization. Government Agencies are expanding most quickly following federal compliance deadlines.
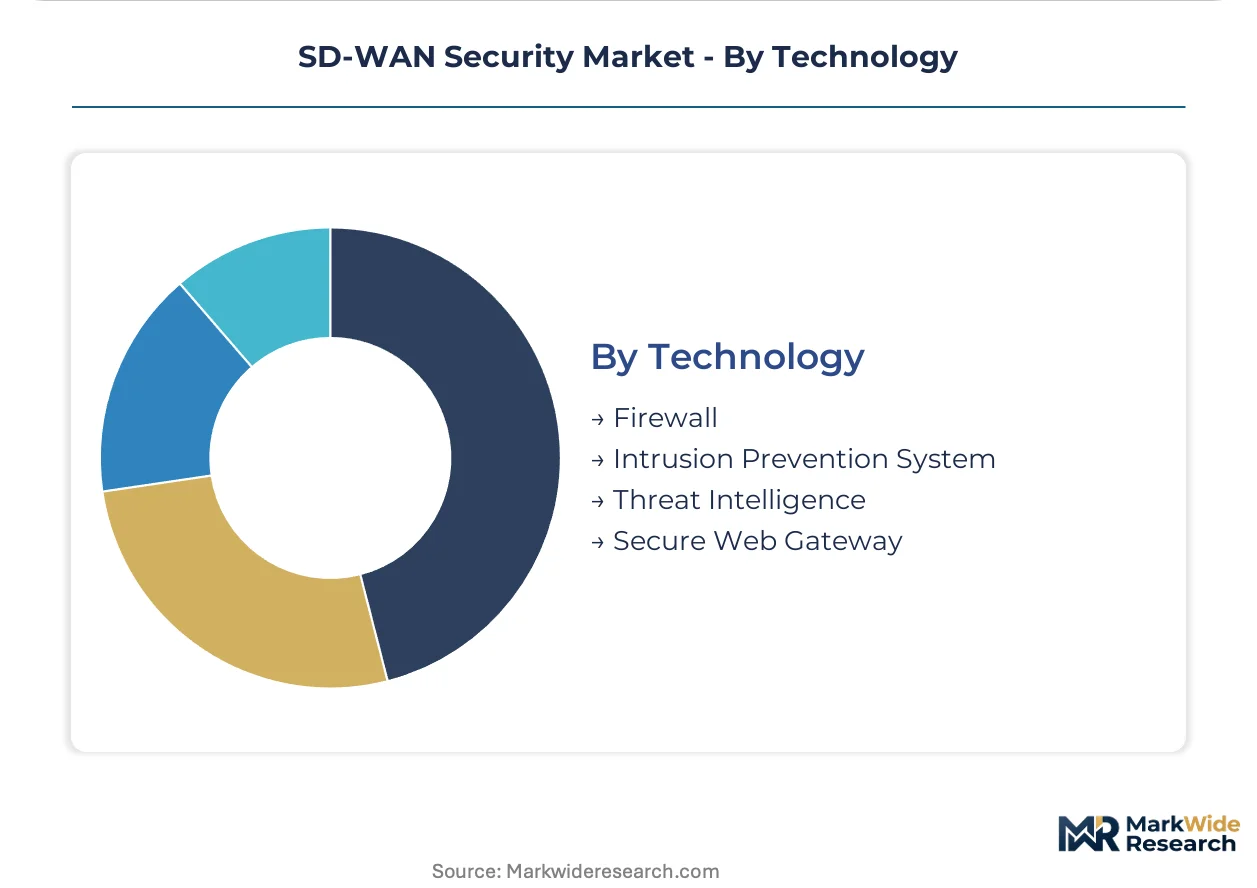
Technology:
Functional specialization within security stacks determines architectural integration complexity and threat coverage breadth.
- Threat Intelligence:Machine learning behavioral analytics platforms displacing signature-based detection in branch security architectures. Financial services networks across Japan and Germany deploy these engines to identify anomalous transaction patterns at distributed locations.
- Firewall:Stateful and next-generation inspection capabilities embedded within SD-WAN edge appliances. Integrated firewall-SD-WAN convergence reduces hardware footprint for branch deployments.
- Intrusion Prevention System:Deep packet inspection for exploit and malware detection at network boundaries.
- Secure Web Gateway:Cloud-delivered URL filtering and content inspection for direct-to-internet traffic.
Firewall dominates current deployment share. Threat Intelligence exhibits the steepest expansion trajectory as behavioral analytics mature.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cost-of-compliance arbitrage is redirecting SD-WAN security procurement toward jurisdictions with harmonized federal standards. Enterprises migrate branch security budgets away from fragmented regulatory environments toward markets offering unified certification pathways.
United States
NIST SP 800-207 zero-trust mandates and FCC supply chain integrity guidelines compress federal procurement cycles. Defense contractors face layered DFARS cybersecurity clauses atop baseline requirements. Financial services institutions in New York and Chicago accelerate branch digitization projects to satisfy encrypted transaction processing standards.
Germany
Industrial manufacturers prioritize IEC 62443-compliant network segmentation for operational technology isolation. The country's national cybersecurity regulator enforces strict data-residency requirements on cloud-delivered security services. Automotive suppliers in Bavaria deploy hybrid cloud SD-WAN architectures to satisfy latency-sensitive production line connectivity.
Japan
METI guidelines on critical infrastructure protection reshape procurement specifications for financial services networks. Behavioral analytics engines displace signature-based detection in Tokyo-based banking security stacks. Manufacturing clusters in Osaka and Nagoya require hardened SD-WAN gateways for factory floor network isolation.
United Kingdom
NCSC zero-trust architecture guidance influences enterprise security transformation roadmaps. The country's national data protection regulator constrains cross-border traffic inspection architectures for cloud-delivered services. London-based financial services firms negotiate enterprise licensing agreements for API-driven policy automation.
France
ANSSI cybersecurity certification mandates reshape procurement criteria for critical infrastructure operators. The country's national data protection regulator imposes divergent data-residency requirements on managed security service providers. Healthcare clinic networks in Paris adopt public cloud SD-WAN to satisfy technical safeguard obligations without capital-intensive branch infrastructure.
SD-WAN Security Market Competitive Landscape
Branded specialists and contract manufacturers split share differently across segments, with integrated platform vendors capturing premium positioning while point-product specialists defend niche applications. The vendor base organizes around three archetypes: routing equipment incumbents leveraging installed base relationships, converged security fabric providers, and cloud-native pure-plays. Consolidation pressure intensifies as enterprises demand unified policy management across heterogeneous stacks. Strategic moves concentrate on portfolio diversification through adjacent security category bundling and geographic expansion via managed service provider channel partnerships.
Within the converged security tier, Cisco, Fortinet, and Palo Alto Networks exemplify distinct platform strategies. Cisco anchors enterprise relationships through routing equipment upsell pathways. Fortinet occupies a position emphasizing integrated appliance convergence to reduce hardware footprint. Palo Alto Networks represents cloud-delivered branch security consolidation, collapsing multiple point products into unified policy frameworks.
| Leading Market Players |
|---|
| Cisco |
| Fortinet |
| VMware |
| Palo Alto Networks |
| Hewlett Packard Enterprise |
| Juniper Networks |
| Versa Networks |
| Zscaler |
| Check Point Software |
| Others |
Value Network & Pricing Analysis
Captive ASIC fabrication partnerships in Taiwan anchor both supply security and pricing power for high-throughput SD-WAN appliance vendors. This vertical integration choice insulates specialized encryption hardware producers from spot-market semiconductor volatility while enabling premium positioning against commodity white-box competitors.
Pricing Analysis
Direct-to-enterprise subscription margins compress distributor markup layers as vendors like Cisco and Fortinet bypass traditional channel intermediaries for large accounts. Three-tier pricing structure across premium threat-intelligence bundles, standard firewall-integrated appliances, and economy-focused managed service tiers segments buyer willingness-to-pay. Pricing pressure stems from cloud-native pure-plays undercutting appliance-heavy incumbents on total cost of ownership calculations. Mid-market enterprises exhibit highest price sensitivity, while federal contractors absorbing NIST compliance costs show lowest elasticity.
Supply Chain Analysis
Reverse-logistics flows for firmware-upgraded appliances create secondary market refurbishment channels extending hardware lifecycles. Taiwan, South Korea, and the United States concentrate custom encryption chip fabrication capacity. Supply chains draw from silicon wafer inputs, specialized network processor cores, and hardened enclosure manufacturing. Single-source vulnerability around Taiwan-based foundry capacity represents structural supply risk. Distribution runs through authorized reseller networks and managed service provider aggregators serving multi-tenant deployments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
SD-WAN Security functions as a stable compounder where regulatory compliance mandates generate predictable replacement cycles across federal and financial services verticals.
For Market Incumbents: Deploy certification investment levers to deepen DFARS and ISO 27001 audit documentation capabilities before federal procurement deadlines tighten. Consolidate adjacent security categories through cloud access security broker bundling to counter cloud-native pure-play substitution. Fortify channel control over managed service provider relationships as mid-market enterprises outsource security operations capacity. For New Entrants and Emerging Players: Begin with Security-as-a-Service delivery models targeting Japan's mid-market enterprises seeking operational expenditure flexibility without capital-intensive branch infrastructure. White-space concentrates in industrial IoT edge protection for IEC 62443-compliant manufacturing networks. Go-to-market leverage rests on 24/7 security operations center partnerships eliminating buyer SOC buildout requirements. For Investors and Strategic Acquirers: Roll-up economics work for regional managed security service providers because fragmented SOC capacity across European markets enables platform consolidation at 4-5x revenue multiples. Five-to-ten year viability hinges on post-quantum cryptography upgrade cycles accelerating federal contractor refresh spending. Monitor NIST post-quantum encryption standard finalization timelines as inflection signal for infrastructure replacement demand.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Certification | NIST SP 800-207 compliance unlocks federal procurement pipelines worth billions in contracted volume. |
| Managed Security Service Provider Channel Expansion | Mid-market enterprise outsourcing trends concentrate recurring revenue in aggregator hands across Germany and Japan. |
| Post-Quantum Cryptography Readiness | Federal contractor infrastructure refresh cycles accelerate as NIST finalizes encryption standards. |
| Industrial IoT Edge Gateway Hardening | IEC 62443-compliant manufacturing networks require operational technology isolation driving specialized appliance demand. |
| Cloud-Native Security Service Edge Convergence | SASE framework adoption collapses point-product procurement into unified vendor relationships. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary conversations with CISOs, federal procurement officers, managed service provider operations directors, and network security architects with secondary validation against NIST publication archives, FCC rulemaking dockets, SEC 10-K infrastructure spending disclosures, and hyperscaler edge-PoP deployment announcements. Bottom-up branch deployment counts triangulated against top-down vendor revenue segmentation.
Historical reference periods anchored volume and value trajectories across the projection horizon, with segmentation modeling spanning service delivery mode, deployment architecture, organizational scale, and technology functional specialization. CAGRs derived from fitted growth curves incorporating threat intelligence platform adoption rates, zero-trust mandate compliance deadlines, and cloud-native security service edge penetration patterns.
Several conditions sit outside the modeled scope, including sovereign data-residency rule fragmentation effects and Taiwan semiconductor supply disruption scenarios. Practitioners should monitor NIST post-quantum cryptography standard publication and federal fiscal appropriation cycles for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Global Healthcare IoT Security Market
Cybersecurity
Kuwait Cybersecurity Market
Cybersecurity
IoT Security Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Europe Mobile Security Market