
 Secaas Market | 2026-2036
Secaas Market Size, Share, and Industry Trends Forecast 2026-2036
Secaas Market Outlook
The EU AI Act is hardening data governance mandates across European enterprises, forcing cloud security architectures toward sovereign deployment models. IBM Corporation leverages its hybrid cloud security stack to anchor compliance-heavy workloads in regulated industries. Palo Alto Networks competes through Prisma Cloud's unified posture management, while Zscaler differentiates via zero-trust network access that eliminates traditional perimeter appliances.
Security as a Service delivers cloud-native cybersecurity capabilities through subscription-based models, encompassing threat detection, identity management, and continuous compliance monitoring across distributed IT estates. The technology operates through API-integrated agents and cloud-hosted control planes that scale elastically with workload expansion. Hybrid Cloud deployment dominates enterprise procurement as organizations straddle on-premises legacy systems with multi-cloud strategies. Network Security use cases command premium positioning as ransomware frequency escalates operational risk for critical infrastructure operators. SME end-user segments represent the fastest-growing adoption pool as managed security services collapse barriers to enterprise-grade protection.
FDA cybersecurity guidance for medical devices, SEC disclosure rules for material cyber incidents, and GDPR cross-border data transfer mechanisms collectively reshape Secaas product roadmaps and geographic service delivery architectures. The EU Cyber Resilience Act introduces mandatory security-by-design requirements for connected products, expanding addressable market scope for embedded security services. Stakeholders must monitor evolving national data localization statutes that fragment cloud architecture standardization and complicate single-platform global rollout strategies.
Market Dynamics
The EU AI Act and GDPR enforcement are compressing cloud security procurement cycles as financial services firms and industrial operators race to deploy sovereign-compliant architectures before audit deadlines.
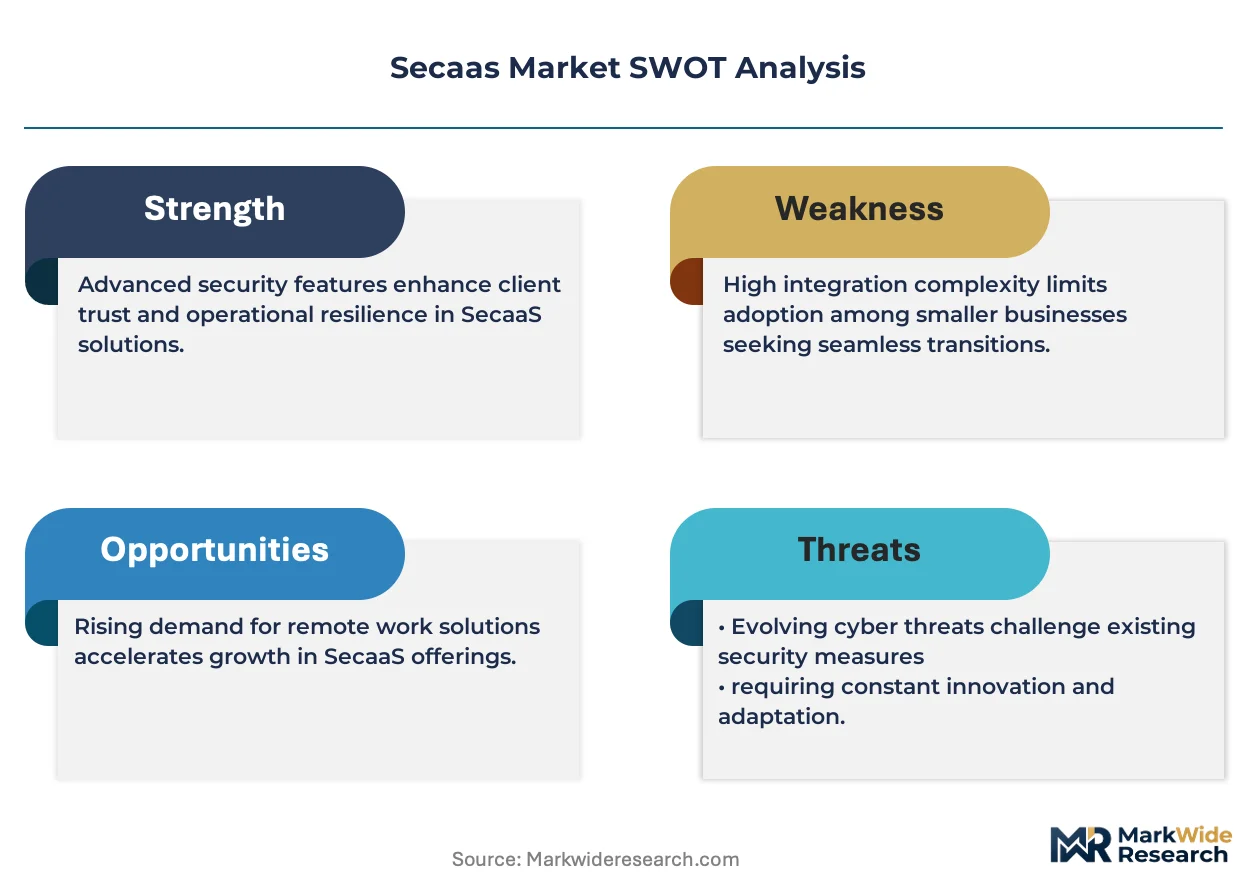
Growth Catalysts
- EU Cyber Resilience Act:Mandatory security-by-design requirements for connected products expand addressable market scope for embedded security services across European manufacturing clusters.
- Ransomware frequency:Critical infrastructure operators in energy and healthcare are accelerating network security spending to meet operational resilience mandates.
- SME managed services:Subscription-based security service models collapse capital barriers, unlocking enterprise-grade protection for mid-market firms previously priced out of comprehensive coverage.
Market Restraints
- Data localization statutes:Fragmented national requirements across EU member states complicate single-platform global rollout strategies and inflate compliance engineering costs.
- Hybrid cloud complexity:Organizations straddling on-premises legacy systems with multi-cloud estates face integration friction that delays Secaas deployment timelines.
- Skilled security operations talent:Shortage of certified cloud security architects and SOC analysts constrains vendor scaling velocity and service quality consistency.
Strategic Opportunities
- Industrial IoT security:Germany's manufacturing digitization creates concentrated demand for operational technology security overlays in automotive and machinery clusters.
- AI-powered threat detection:Machine learning anomaly detection converging with automated response orchestration opens premium pricing tiers for real-time security operations.
- SEC disclosure rules:Material cyber incident reporting mandates drive board-level security investment urgency across US-listed enterprises, expanding managed detection and response adoption.
Industry Challenges
- Legacy system integration:Mainframe and proprietary industrial control systems resist API-native security agent deployment, requiring costly custom engineering.
- Cross-border data transfer certification:GDPR adequacy decisions and standard contractual clause negotiations extend sales cycles for multinational deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Secaas Market |
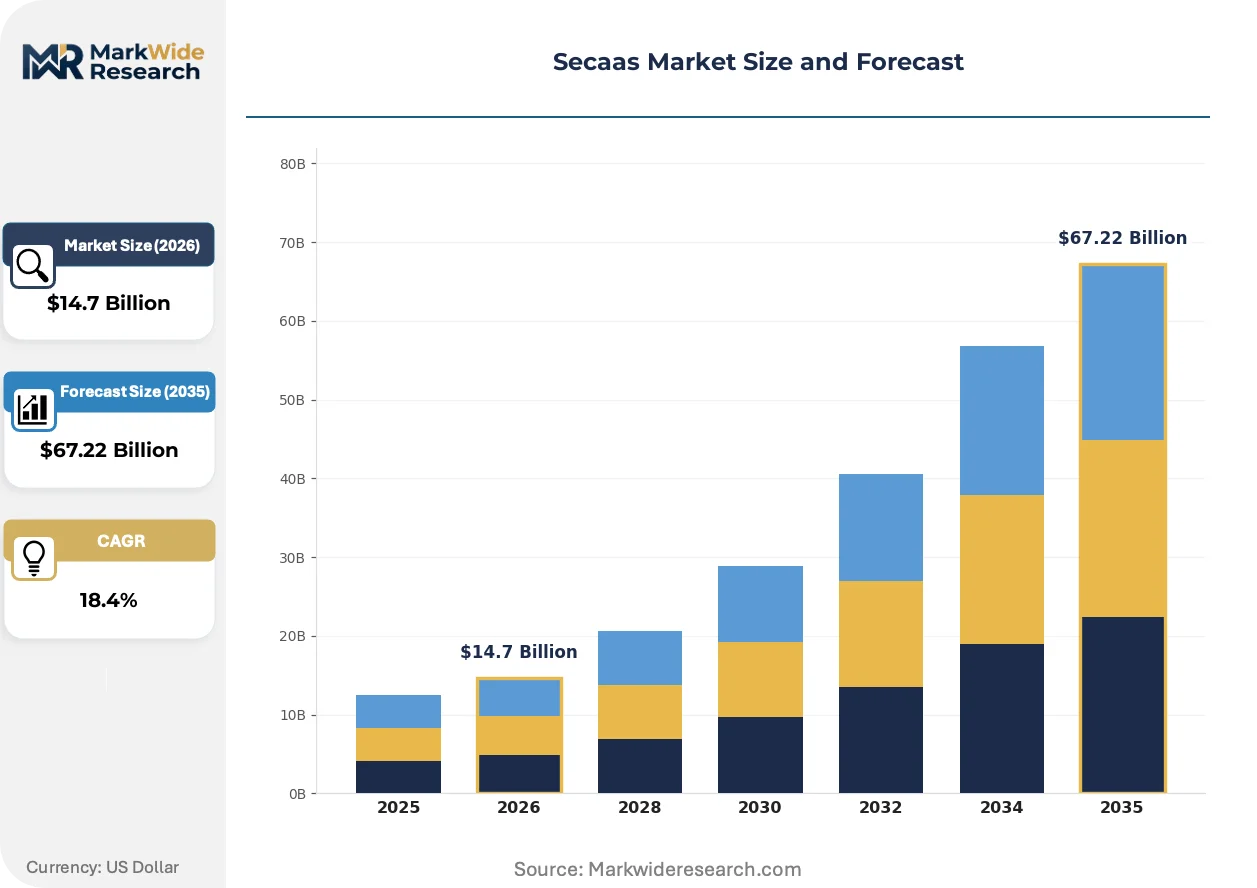
| Market Size in 2026 | $14.7 Billion |
| Market Size in 2035 | $67.22 Billion |
| CAGR (2026 – 2036) | 18.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Community Cloud Service Type: Infrastructure as a Service, Platform as a Service, Software as a Service, Function as a Service Use Case: Data Backup, Disaster Recovery, Network Security, Application Security End User: SMEs, Enterprises, Government, Educational Institutions |
| Companies Covered | IBM Corporation, Cisco Systems, Amazon Web Services, Google Cloud, Microsoft, Zscaler, Palo Alto Networks, Trend Micro, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Secaas Market Strategic Shifts
Zero-trust architectures are displacing perimeter-based security models as distributed workforces and cloud-native applications dissolve traditional network boundaries. Three developments are compressing competitive positioning.
Extended detection and response platforms aggregate telemetry across endpoints, networks, and cloud workloads into unified threat hunting interfaces. Mid-market enterprises are adopting these consolidated stacks fastest, abandoning point-product sprawl. The technology is converging with security orchestration and automated response, collapsing mean-time-to-remediation from hours to minutes.
The EU AI Act's risk-based classification system for automated decision-making systems imposes documentation and human oversight mandates on high-risk deployments. Financial services algorithms and healthcare diagnostic tools face the strictest compliance burdens. German and French regulators are issuing sector-specific guidance first, forcing vendors to localize product roadmaps.
Consumption-based security licensing is replacing perpetual seat models as buyers demand elasticity matching cloud workload volatility. Managed security service providers are capturing this shift through usage-metered contracts that align costs with actual protected assets. This pattern is most visible among US and UK technology sector buyers with highly variable development environments.
Secaas Market Segmentation
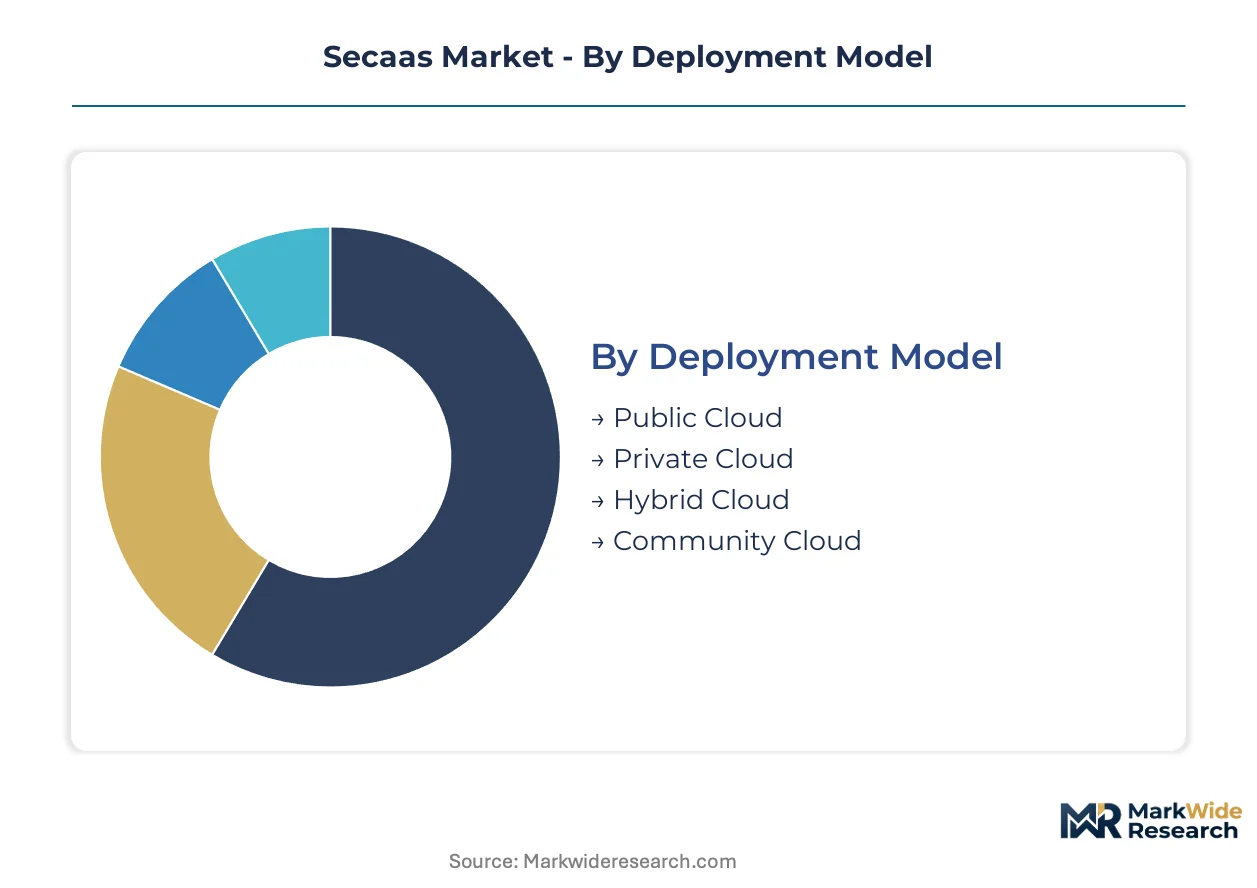
Security-as-a-Service procurement decisions hinge on deployment sovereignty requirements, workload elasticity needs, and compliance architecture constraints. Buyers evaluate segments through the lens of data residency mandates, integration complexity with legacy estates, and the operational maturity of internal security operations centers.
Deployment Model:
Data sovereignty regulations and workload sensitivity drive deployment architecture selection across regulated industries.
- Hybrid Cloud:Organizations straddle on-premises legacy systems with multi-cloud strategies, requiring unified policy enforcement across fragmented estates. Financial services firms in Germany and France prioritize this model to maintain audit-ready data lineage while tapping elastic cloud compute for non-sensitive workloads.
- Private Cloud:Dedicated infrastructure delivers tenant-isolated security controls for classified government systems and critical infrastructure operators. Demand concentrates among defense contractors and national healthcare systems facing mandatory air-gapping requirements under GDPR and national security frameworks.
- Public Cloud:Shared infrastructure models offer rapid provisioning for development environments and non-regulated workloads.
- Community Cloud:Sector-specific deployments serve collaborative ecosystems with mutualized compliance costs.
Volume sits with Hybrid Cloud; growth tilts toward Private Cloud as sovereign computing mandates expand.
Service Type:
Buyer sophistication and internal development velocity determine service abstraction layer preferences.
- Software as a Service:Pre-built security applications deliver immediate threat detection and compliance reporting without engineering overhead. Mid-market enterprises across US technology corridors and UK financial services adopt these solutions fastest to collapse time-to-protection from quarters to weeks.
- Infrastructure as a Service:Compute and storage resources with embedded security controls support custom security stack development. Large enterprises with mature DevSecOps pipelines in Germany's automotive clusters leverage this layer for tailored threat hunting platforms.
- Platform as a Service:Managed runtime environments accelerate secure application deployment.
- Function as a Service:Event-driven security automation scales response actions without persistent infrastructure.
Revenue concentrates in Software as a Service; Platform as a Service climbs the fastest as containerization standardizes.
Use Case:
Operational risk exposure and regulatory pressure intensity shape security investment prioritization.
- Network Security:Perimeter dissolution and ransomware escalation demand continuous traffic inspection and microsegmentation. Critical infrastructure operators in energy and healthcare sectors across France, Germany, and the US deploy these capabilities to satisfy operational resilience mandates and SEC disclosure readiness.
- Application Security:Shift-left testing and runtime protection secure cloud-native development pipelines. Technology sector buyers in Silicon Valley and London's fintech corridors prioritize this use case to prevent credential stuffing and API abuse in customer-facing platforms.
- Data Backup:Immutable storage and geographic redundancy protect against encryption attacks.
- Disaster Recovery:Orchestrated failover maintains business continuity during regional outages.
Spending concentrates in Network Security; Application Security gains share fastest as software supply chain attacks proliferate.
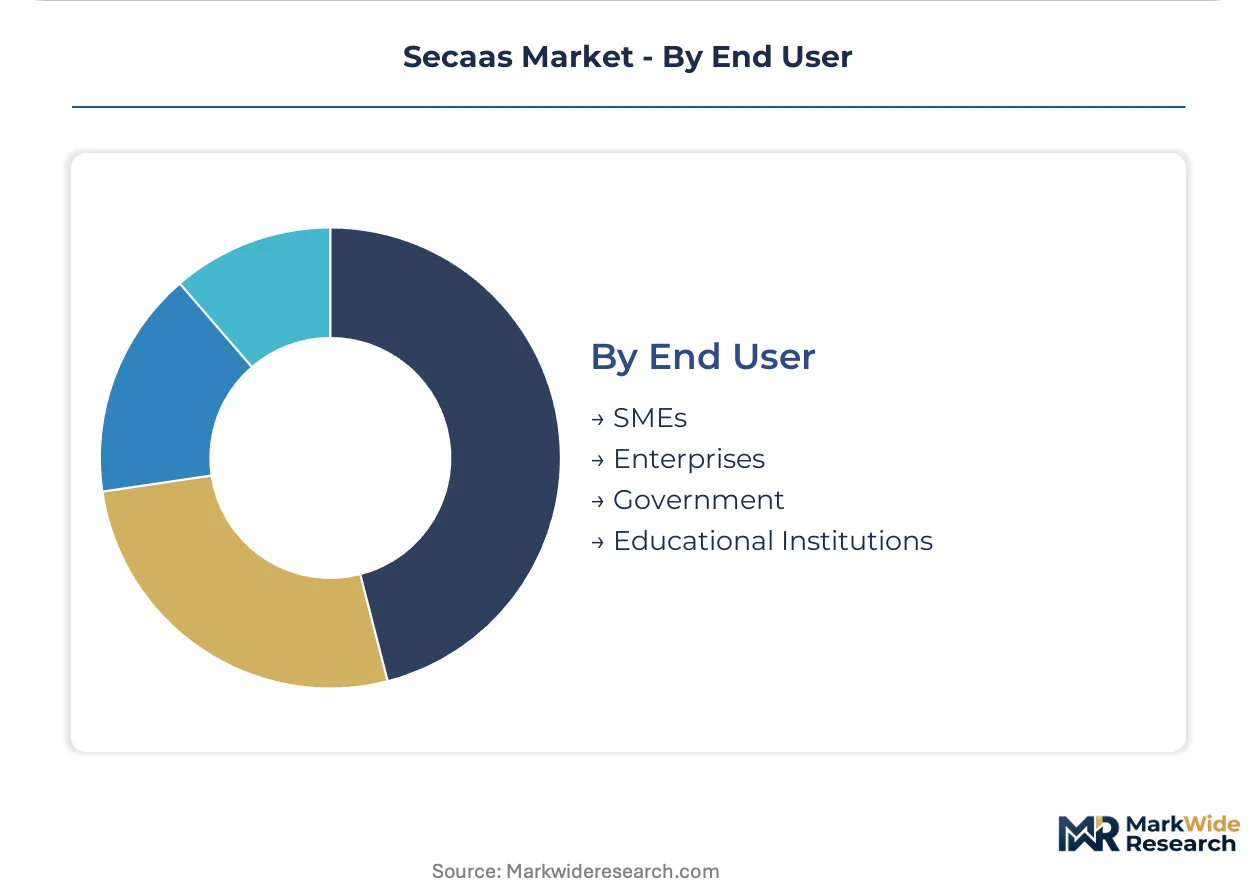
End User:
Security maturity, budget elasticity, and regulatory exposure differentiate buyer segment requirements.
- SMEs:Subscription-based managed security services collapse capital barriers and talent acquisition constraints. Mid-market manufacturers in Italy's industrial districts and professional services firms across Spain adopt these offerings to access enterprise-grade SOC capabilities without internal hiring.
- Enterprises:Custom architectures integrate with existing identity providers and governance frameworks. Multinational corporations headquartered in Switzerland and the Netherlands deploy these solutions to harmonize security posture across acquired subsidiaries and joint venture structures.
- Government:Classified procurement channels and certification requirements shape vendor selection.
- Educational Institutions:Research data protection and student privacy compliance drive adoption.
Contract value sits with Enterprises; SME adoption expands most quickly as managed service penetration deepens.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Frankfurt's financial district anchors European Secaas procurement intensity as compliance deadlines compress deployment timelines across continental banking centers.
United States
SEC disclosure rules and FDA cybersecurity guidance for medical devices drive board-level urgency across healthcare and publicly traded enterprises. New York and San Francisco technology corridors concentrate managed detection and response adoption as ransomware insurance requirements harden. Silicon Valley cloud-native firms prioritize consumption-based licensing models that align security spending with development velocity.
Germany
Industrial IoT security demand concentrates in Bavaria and Baden-Württemberg as automotive and machinery clusters digitize operational technology. The EU Cyber Resilience Act and GDPR enforcement mandate security-by-design integration for connected manufacturing equipment. Munich and Stuttgart engineering hubs anchor sovereign cloud deployments that satisfy federal data residency requirements.
United Kingdom
London's fintech corridor accelerates application security spending to prevent credential stuffing attacks in customer-facing platforms. The Financial Conduct Authority's operational resilience framework imposes strict recovery time objectives on critical financial infrastructure. Edinburgh and Manchester professional services clusters adopt subscription-based managed security to access enterprise-grade SOC capabilities without internal hiring.
France
CNIL guidance on automated decision-making systems shapes AI security product roadmaps for financial services algorithms and healthcare diagnostic tools. Paris anchors compliance-heavy workload migration as EU AI Act risk classifications impose documentation mandates. Lyon and Toulouse aerospace clusters demand embedded security services for connected product lines under emerging Cyber Resilience Act requirements.
India
Bengaluru and Hyderabad technology hubs drive SME adoption of cloud-native security services as mid-market firms bypass capital-intensive infrastructure builds. RBI cybersecurity guidelines for financial institutions compress procurement cycles for zero-trust network architectures. Mumbai's banking sector concentrates demand for hybrid cloud security that harmonizes legacy mainframe integration with multi-cloud elasticity.
Secaas Market Competitive Environment
Premium-margin players sit above commodity-margin players across compliance architecture depth and sovereign deployment capabilities. The vendor base stratifies into three tiers: hyperscale cloud providers with integrated security stacks, specialized zero-trust networking firms, and managed security service providers collapsing talent barriers for mid-market buyers. Consolidation pressure intensifies as cross-border data transfer certification requirements favor vendors with localized infrastructure footprints. Dominant competitive moves include strategic partnerships with regional system integrators and portfolio diversification into operational technology security overlays.
Within the established technology conglomerate tier, IBM Corporation and Cisco Systems anchor hybrid cloud security positioning through compliance-heavy workload capture. Palo Alto Networks exemplifies the unified platform archetype, while Zscaler occupies the zero-trust specialization vector. Microsoft and Amazon Web Services leverage cloud infrastructure dominance to bundle security services at scale. Google Cloud represents the data-native security tier with embedded AI threat detection capabilities.
| Leading Market Players |
|---|
| IBM Corporation |
| Cisco Systems |
| Amazon Web Services |
| Google Cloud |
| Microsoft |
| Zscaler |
| Palo Alto Networks |
| Trend Micro |
| Fortinet |
| Others |
Value Chain & Pricing Dynamics
Certified cloud security architects concentrated in Bengaluru and Hyderabad create labor-cost differentials that widen pricing-tier spreads between premium managed detection services and economy-tier endpoint protection packages. EU GDPR compliance engineering and US SEC disclosure readiness requirements add fixed-cost layers that vendors recover through outcome-based contract premiums.
Pricing Analysis
Consumption-based pricing tied to protected asset throughput anchors Secaas contract structures, replacing perpetual seat licenses as buyers demand elasticity matching cloud workload volatility. Three-tier pricing structure across premium, standard, and economy levels separates sovereign-compliant hybrid deployments from basic SaaS endpoint protection. Cost compression in the mid-market tier is intensifying because managed security service providers compete aggressively for SME accounts with standardized SOC offerings. Technology sector buyers in Silicon Valley and London's fintech corridors demonstrate lowest price sensitivity, prioritizing real-time threat detection latency over per-seat economics.
Supply Chain Analysis
EU Cyber Resilience Act domestic-content mandates for connected product security are reshaping sourcing patterns for embedded security modules and operational technology overlays. Engineering talent concentrates in India, Germany, and the United States, while cloud infrastructure provisioning draws from hyperscaler data center networks across Ireland, Frankfurt, and Singapore. Supply chain risk centers on single-source vulnerability for specialized threat intelligence feeds and zero-day research capabilities. Distribution runs through regional system integrators and managed security service providers that bundle vendor platforms with local compliance expertise.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Secaas procurement is transitioning from perimeter appliance refresh cycles to zero-trust cloud-native architectures, with API-integrated agents displacing hardware-dependent network security stacks.
For Market Incumbents: Acquire specialized operational technology security firms to capture industrial IoT demand in Germany's automotive clusters. Consolidate threat intelligence data streams to defend against pure-play AI-native entrants. Invest in sovereign cloud certification for EU member state data residency mandates. For New Entrants and Emerging Players: Cloud-native channel partnerships with hyperscaler marketplaces offer the lowest-friction route to mid-market enterprise accounts. Target Italy's industrial districts and Spain's professional services clusters with subscription-based SOC-as-a-service offerings. Differentiate through automated response orchestration that collapses mean-time-to-remediation. For Investors and Strategic Acquirers: Re-rating potential sits with vertical-focused managed security providers given EU AI Act documentation mandates for high-risk algorithmic systems. Long-term viability favors vendors with localized infrastructure footprints that simplify cross-border data transfer certification. Monitor SEC enforcement patterns around material cyber incident disclosures as an inflection indicator for board-level security investment urgency.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies telemetry across endpoints, networks, and cloud workloads into single threat hunting interfaces. |
| Strategic Partnership | Aligns vendor roadmaps with regional system integrators possessing sovereign cloud deployment expertise. |
| Acquisition of Specialist Firm | Adds operational technology security capabilities for industrial IoT deployments in manufacturing clusters. |
| Geographic Expansion | Establishes localized data centers to satisfy GDPR and EU AI Act residency requirements. |
| Product Launch | Introduces consumption-metered contracts matching security spending to actual protected asset volatility. |
Study Parameters
SEC filings, hyperscaler capex disclosures, and EU regulatory guidance documents formed the secondary backbone of this analysis. Primary interviews with CISOs, cloud architects, and managed security service executives validated demand patterns and procurement timelines. Bottom-up sizing of subscription contract values triangulated against top-down market aggregation from vendor revenue disclosures.
Historical trendline analysis of SaaS security spending patterns informed projection frameworks across deployment models, organization size tiers, and vertical industry clusters. Segmentation dimensions modeled include hybrid cloud versus sovereign private deployments, SME versus enterprise buyer archetypes, and network security versus application security use cases. CAGRs were derived through regression analysis of adoption velocity curves and compliance deadline impacts.
Inputs from regulatory filings and vendor financial disclosures were available through the study window; gaps in private company contract values introduce uncertainty bands around SME segment estimates. Forecasts reflect assumptions about enforcement intensity of EU AI Act risk classifications and SEC cyber disclosure rules. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
VPN Software Market
Security Software
Door Phone Market
Security Software
US and Latin America Identity and Access Management (IAM) Market
Security Software
Bot Mitigation Market
Security Software
Global Mobile Identification Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Confidential Computing Market
Security Software
Information Rights Management Market
Security Software
Enterprise Rights Management Solution Market
Security Software
Global Anti-Spam Software Market
Security Software
Consumer Endpoint Security Market
Security Software
Social Media Security Market
Security Software
Global Automatic Number Plate Recognition (ANPR) System Market
Security Software
Patch and Remediation Software Market
Security Software
Global Electronic Passports Market
Security Software
Asia-Pacific Extended Detection and Response Market