
 Managed Security Services Market | 2026-2036
Managed Security Services Market Size, Share, and Industry Trends Forecast 2026-2036
Managed Security Services Market Intelligence
Subscription-based financing for security operations centers is narrowing the capital barrier that once favored only the largest integrators. IBM leverages its hybrid cloud platform to anchor multi-tenant managed detection and response services across enterprise clients. LevelBlue sustains competitive positioning through specialized threat intelligence feeds tailored to sector-specific attack patterns. Secureworks differentiates via proprietary software-defined security orchestration that reduces analyst touchpoints per incident.
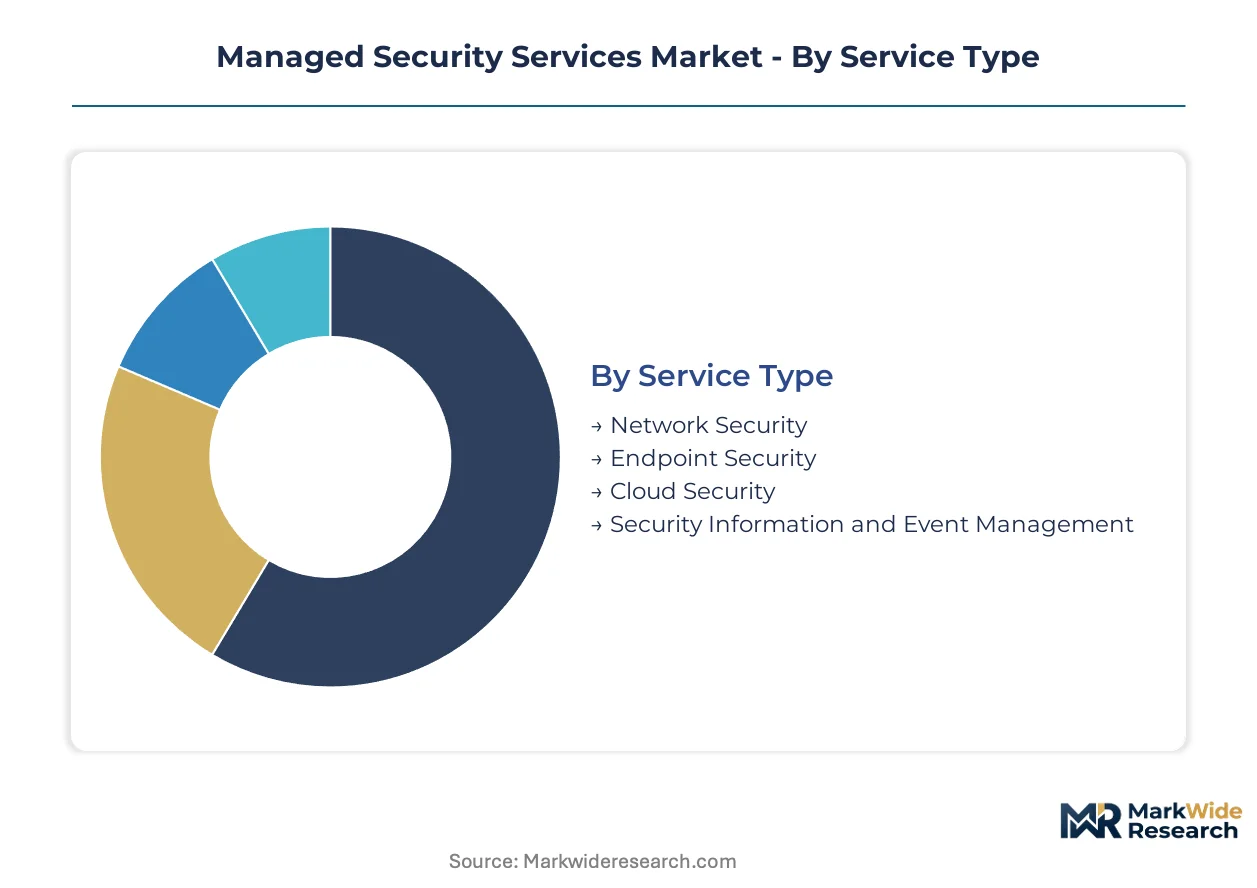
Managed security services encompass the continuous outsourcing of threat monitoring, incident response, vulnerability management, and security infrastructure administration to specialized third-party providers, typically delivered through 24/7 security operations centers with defined mean-time-to-detect and mean-time-to-respond service level agreements. Cloud Security commands the fastest expansion within service type segmentation as distributed workforces and multi-cloud architectures multiply attack surfaces beyond traditional perimeter defenses. Endpoint Security retains the largest revenue share due to persistent device proliferation and the complexity of securing unmanaged bring-your-own-device environments. Artificial Intelligence within the technology segment is concentrating vendor R&D investment toward autonomous threat-hunting capabilities that reduce dependency on scarce analyst labor.
The SEC's cybersecurity disclosure rules now mandate timely incident reporting and governance accountability for publicly traded entities, directly elevating demand for documented security operations center capabilities. The EU NIS2 Directive extends compliance obligations to a broader set of essential and important entities across member states, tightening procurement specifications for managed security providers. HIPAA security rule enforcement by the Office for Civil Rights continues to drive healthcare sector outsourcing as organizations seek demonstrable control documentation for protected health information environments. Stakeholders must evaluate provider resilience against concentration risk in threat intelligence sourcing and the scalability of human analyst augmentation as artificial intelligence capabilities mature.
Market Dynamics
Artificial intelligence is collapsing the traditional analyst-to-alert ratio that once governed security operations center economics, compressing detection timelines while simultaneously creating new attack surfaces through adversarial machine learning exploitation.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:US publicly traded entities must now document governance accountability and incident response capabilities, elevating procurement specifications for managed detection and response services.
- Healthcare PHI Outsourcing:HIPAA Security Rule enforcement by the Office for Civil Rights drives hospitals and payers toward documented control frameworks for protected health information environments.
- Multi-Cloud Attack Surface Expansion:Distributed workforces and hybrid infrastructure deployments multiply perimeter complexity beyond traditional network boundaries, forcing enterprises toward centralized monitoring architectures.
Market Restraints
- Analyst Labor Scarcity:The cybersecurity skills gap constrains provider scaling, with qualified security operations center personnel commanding premium compensation that compresses service margins.
- Threat Intelligence Concentration:Dependency on a limited set of commercial intelligence feeds creates systemic vulnerability if sourcing channels degrade or pricing escalates.
- Legacy Infrastructure Integration Friction:Heterogeneous on-premises security stacks resist seamless orchestration with cloud-native managed services, extending deployment timelines.
Strategic Opportunities
- EU NIS2 Directive Expansion:The mandate extends compliance obligations to important entities across member states, tightening procurement specifications and enlarging the addressable provider base.
- Artificial Intelligence Convergence:Autonomous threat-hunting capabilities reduce dependency on scarce analyst labor while enabling predictive incident anticipation rather than reactive response.
- Subscription Financing Penetration:Operational expenditure models narrow capital barriers for mid-market enterprises previously excluded from enterprise-grade security operations center capabilities.
Industry Challenges
- Mean-Time-to-Respond Compression:Escalating ransomware velocity demands sub-hour containment protocols that strain human-machine workflow design and service level agreement feasibility.
- Adversarial AI Countermeasures:Attackers increasingly deploy machine learning to evade detection signatures, forcing continuous algorithmic retraining and false-positive management.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Managed Security Services Market |
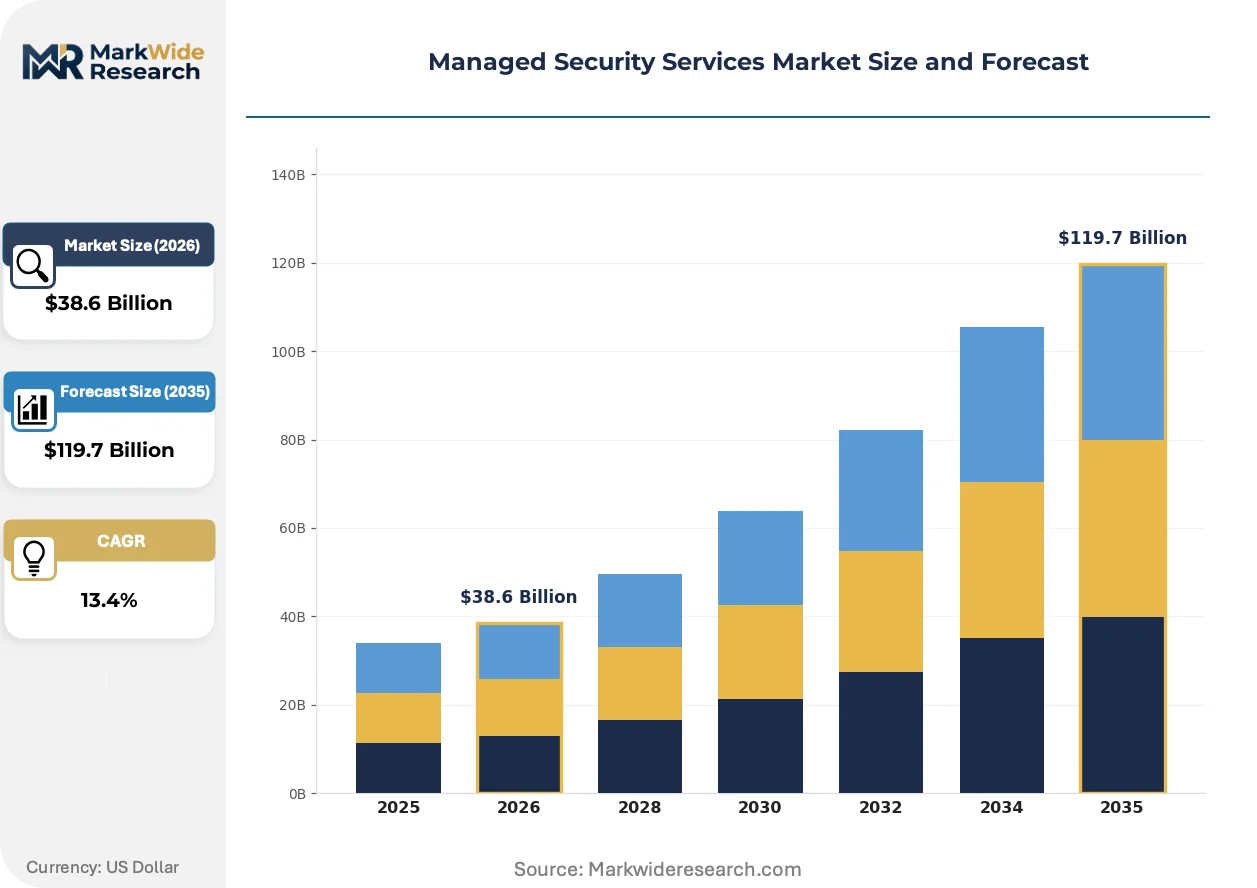
| Market Size in 2026 | $38.6 Billion |
| Market Size in 2035 | $119.7 Billion |
| CAGR (2026 – 2036) | 13.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Network Security, Endpoint Security, Cloud Security, Security Information and Event Management Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed End User: Government, Banking, Healthcare, Retail Technology: Artificial Intelligence, Machine Learning, Blockchain, Encryption |
| Companies Covered | IBM, LevelBlue, AT&T, Secureworks, NTT, Accenture, Verizon, Palo Alto Networks, Check Point Software Technologies, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Managed Security Services Market Strategic Shifts & Innovations
Security service delivery is undergoing fundamental restructuring as automation, regulatory mandates, and buyer sophistication converge to redefine value capture mechanisms and competitive differentiation.
Extended detection and response platforms are collapsing the distinction between endpoint telemetry and network-layer visibility, enabling unified threat hunting across cloud workloads and on-premises infrastructure. Financial services firms are adopting these architectures fastest, drawn by consolidated vendor relationships and reduced alert fatigue. The structural consequence is compression of standalone endpoint security providers into broader platform ecosystems.
The EU NIS2 Directive is mandating stricter incident reporting timelines and supply chain security obligations across critical infrastructure operators in member states. Industrial consequence includes mandatory procurement of documented security operations center capabilities with auditable mean-time-to-detect metrics. Energy and transport verticals within Europe are responding fastest, embedding compliance specifications directly into managed service contracts.
Enterprise buyers are consolidating vendor relationships around integrated platform providers rather than best-of-breed point solutions. The mid-market segment is displacing multi-vendor security stacks with single-provider accountability models. This concentration is most visible in the United States, where ransomware frequency has elevated executive-level risk tolerance for vendor lock-in in exchange for measurable response guarantees.
Managed Security Services Market Segmentation
Segmentation in managed security services reflects divergent buyer capabilities, infrastructure maturity, and regulatory exposure. Procurement patterns split sharply between organizations seeking full operational transfer versus those retaining internal control over sensitive assets.
Service Type:
Use-case spectrum spans legacy perimeter defense through cloud-native workload protection, with buyer sophistication determining service bundling preferences.
- Network Security:Continuous monitoring of traffic flows, firewall management, and intrusion detection systems deployed across enterprise WAN and LAN architectures. Financial services firms in the United States concentrate procurement here as ransomware campaigns targeting payment systems intensify.
- Endpoint Security:Device-level threat detection, patch management, and behavioral analytics covering managed and unmanaged endpoints. Healthcare systems facing HIPAA enforcement prioritize this segment for demonstrable control documentation across bring-your-own-device environments.
- Cloud Security:Workload protection, configuration management, and identity controls across multi-tenant and private cloud deployments.
- Security Information and Event Management:Log aggregation, correlation engines, and compliance reporting dashboards for audit-ready security telemetry.
Established volume favors Endpoint Security; emerging adoption favors Cloud Security.
Deployment Model:
Cost tier segmentation separates capital-intensive infrastructure ownership from operational expenditure flexibility, with hybrid architectures capturing mid-market migration paths.
- On-Premises:Dedicated security infrastructure housed within client-controlled data centers with direct hardware ownership. Defense and intelligence agencies mandate this model for classified environment handling.
- Cloud-Based:Fully hosted security operations center capabilities delivered through provider-managed SaaS platforms. Retail chains with distributed footprints adopt this fastest for rapid deployment without regional data center investment.
- Hybrid:Split architecture preserving sensitive on-premises controls while outsourcing commodity monitoring functions.
- Managed:Complete operational transfer of security function to third-party staff with defined service level agreements.
Cloud-Based deployment is climbing the fastest among mid-market entrants; On-Premises retains preference in regulated government verticals.
End User:
Customer type segmentation aligns procurement sophistication with sector-specific threat exposure and compliance burden intensity.
- Government:Federal, state, and municipal entities requiring FedRAMP-authorized or equivalent certified security operations. Procurement concentrates through classified and unclassified contract vehicles with emphasis on domestic personnel requirements.
- Banking:Commercial banks, investment firms, and payment processors subject to SEC disclosure rules and FFIEC examination standards. This vertical demands sub-hour mean-time-to-respond guarantees and documented board-level governance accountability.
- Healthcare:Hospital systems, insurers, and pharmaceutical manufacturers managing protected health information under HIPAA Security Rule enforcement.
- Retail:E-commerce platforms and brick-and-mortar chains protecting payment card data and customer PII against point-of-sale intrusion.
Banking sector procurement exhibits the steepest expansion trajectory; Healthcare outsourcing is accelerating fastest among previously insourced operations.
Technology:
Maturity segmentation separates proven cryptographic foundations from emerging autonomous capabilities with unproven operational integration.
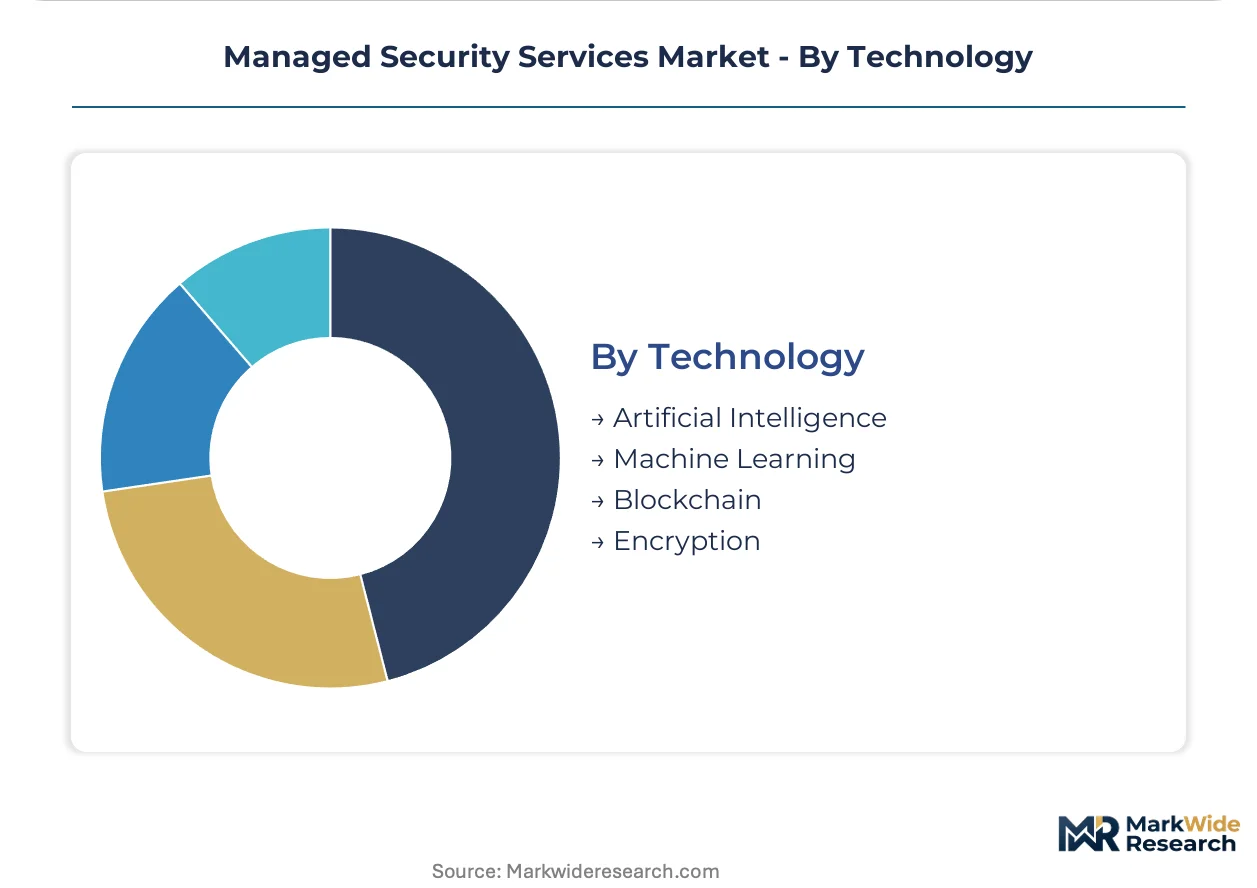
- Artificial Intelligence:Autonomous threat-hunting algorithms, predictive incident anticipation, and natural language processing for alert triage. Vendor R&D investment concentrates here to compress analyst-to-alert ratios and offset labor scarcity.
- Machine Learning:Supervised and unsupervised models for baseline behavior establishment and anomaly detection across endpoint and network telemetry.
- Blockchain:Distributed ledger applications for immutable audit trails and identity verification in supply chain security contexts.
- Encryption:Data-at-rest and data-in-transit protection through AES, RSA, and emerging post-quantum cryptographic standards.
Encryption represents established infrastructure spend; Artificial Intelligence commands the fastest-growing investment intensity among technology segments.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial services and critical infrastructure operators concentrate procurement in jurisdictions with mature regulatory frameworks and elevated ransomware exposure. Buyer sophistication splits between compliance-driven European mandates and threat-velocity-driven North American deployment.
United States
Banking and payment processors drive demand as SEC disclosure rules mandate documented governance accountability and sub-hour incident response capabilities. HIPAA enforcement by the Office for Civil Rights compels hospital systems toward outsourced security operations centers with auditable control frameworks. The Northeast corridor from New York to Boston hosts the densest concentration of managed detection and response procurement as financial institutions consolidate vendor relationships.
Germany
Industrial manufacturers and automotive suppliers are expanding security operations center outsourcing under EU NIS2 Directive supply chain security obligations. The KBA and sector regulators are tightening procurement specifications for critical infrastructure operators. The Rhine-Ruhr and Stuttgart industrial clusters are embedding managed security contracts with mandatory mean-time-to-detect metrics into supplier agreements.
United Kingdom
Investment firms and insurance underwriters are elevating procurement standards following the Financial Conduct Authority's operational resilience requirements. The UK National Cyber Security Centre guidance is shaping vendor selection criteria for financial services. London's City and Canary Wharf districts are driving fastest adoption of cloud-native managed detection platforms among hedge funds and private equity groups.
Japan
Tokyo-based financial institutions and semiconductor manufacturers are consolidating security vendor relationships amid METI cybersecurity framework updates. The 2024 amendments to the Act on Protection of Specially Designated Secrets are expanding cleared personnel requirements for government contractors. The Kanto region around Tokyo anchors procurement concentration as manufacturing supply chains digitize operational technology monitoring.
Singapore
Wealth management firms and maritime logistics operators are adopting managed security services under Monetary Authority of Singapore technology risk management guidelines. The Cybersecurity Agency of Singapore's licensing framework for critical information infrastructure is tightening provider qualification standards. The Marina Bay financial district and Jurong Port cluster are driving regional hub demand for multi-tenant security operations centers serving Southeast Asian operations.
Managed Security Services Market Key Industry Players
Channel-controlling players compete with product-specialist players across a market consolidating around integrated platform providers. The vendor base stratifies between global systems integrators with hybrid cloud anchoring capabilities and specialized threat intelligence boutiques with sector-specific feeds. Two archetypes dominate: scale-driven multi-service platforms and AI-automation specialists compressing analyst-to-alert ratios. Competitive moves concentrate on strategic partnerships for threat intelligence sourcing and portfolio diversification into cloud-native workload protection.
Among technology-anchored providers, IBM, Secureworks, and Palo Alto Networks exemplify contrasting strategic positions. IBM represents the scale-driven platform archetype leveraging hybrid cloud infrastructure for multi-tenant service delivery. Secureworks occupies the automation-specialist tier with software-defined orchestration capabilities. Palo Alto Networks anchors the network-security-origin expansion into managed services. These three demonstrate how vendor provenance shapes competitive positioning without determining market outcomes.
| Leading Market Players |
|---|
| IBM |
| LevelBlue |
| AT&T |
| Secureworks |
| NTT |
| Accenture |
| Verizon |
| Palo Alto Networks |
| Check Point Software Technologies |
| Others |
Cost & Logistics Intelligence
Transatlantic fiber-optic cable routes carrying threat intelligence feeds between Virginia Beach and Marseille shape cost structures for managed security services, concentrating pricing power among providers with dedicated low-latency infrastructure while forcing tiered service differentiation based on telemetry delivery speed.
Pricing Analysis
Cost-plus contracts indexed to analyst labor rate escalators dominate enterprise procurement, with IBM and Accenture anchoring premium tiers through FedRAMP-authorized delivery capabilities. Three-tier pricing structure across premium, standard, and economy levels separates SOC-as-a-service bundles with sub-hour SLAs from commodity log management. Cost compression in mid-market tiers is intensifying because NTT and LevelBlue are automating tier-1 alert triage. Healthcare systems exhibit highest price sensitivity due to constrained capital budgets, while banking verticals prioritize response guarantees over unit cost.
Supply Chain Analysis
Contract manufacturing concentration among specialized security operations center builders in India, Poland, and the Philippines holds capacity for 24/7 staffing augmentation. Provider infrastructure draws from commercial threat intelligence aggregators in Israel and Estonia, proprietary SIEM platforms developed in the United States, and cloud compute from hyperscaler regions. Single-source vulnerability in commercial intelligence feed licensing creates systemic exposure if sourcing channels degrade. Distribution runs through direct enterprise sales teams and managed service provider channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Managed security services represent a service-attach opportunity where recurring threat-hunting subscriptions and incident response retainers are expanding faster than hardware-centric detection appliance sales.
For Market Incumbents: Entrench multi-tenant platform dominance by deepening vertical integration into proprietary threat intelligence collection, insulating against feed pricing volatility. Accenture and IBM should expand analyst training academies in Poland and India to offset labor scarcity constraining competitor scaling. NIS2 Directive procurement specifications favor incumbents with documented mean-time-to-detect metrics. For New Entrants and Emerging Players: Build out specialized AI-automation capabilities targeting mid-market healthcare systems previously excluded from enterprise-grade SOC services. Singapore and Japan offer the most penetrable regulatory environments for new provider qualification. Channel partnerships with regional value-added resellers accelerate credentialing without direct enterprise sales investment. For Investors and Strategic Acquirers: Boutique threat intelligence firms with sector-specific feed development anchor acquisition value in a consolidating vendor landscape. Long-term viability hinges on autonomous detection capabilities reducing analyst dependency. Watch NIS2 enforcement variance across EU member states as inflection indicator for compliance-driven procurement velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Threat Intelligence Feed Acquisition | Proprietary telemetry sourcing reduces dependency on commercial aggregators and insulates margin structure. |
| AI-Automation Platform Integration | Autonomous alert triage compresses analyst-to-alert ratios and addresses labor scarcity constraining scaling. |
| FedRAMP Authorization Investment | US government procurement eligibility opens classified contract vehicles with multi-year revenue visibility. |
| Healthcare Vertical Specialization | HIPAA-compliant control documentation commands premium pricing from hospital systems facing OCR enforcement. |
| EU NIS2 Compliance Certification | Mandatory procurement specifications for critical infrastructure operators enlarge addressable contract base. |
Research Approach
Initial hypotheses were tested against primary input from CISOs at financial services firms, healthcare system IT directors, managed security provider delivery heads, and channel partner technical specialists and refined through secondary validation against SEC cybersecurity disclosure filings, EU NIS2 implementation guidance documents, HIPAA enforcement action records, and hyperscaler security service revenue disclosures. Bottom-up service line build-ups and top-down market sizing triangulated volume estimates.
Demand-supply balance framing anchored the forecast framework, modeling adoption curves across service type, deployment model, end-user vertical, and technology segment dimensions over the projection horizon. CAGRs derived from logistic penetration curves fitted to historical outsourcing velocity and regulatory mandate implementation timelines. Inputs included analyst labor compensation trajectories and threat intelligence feed pricing trends.
Stress conditions across ransomware campaign frequency, EU member state enforcement variance, and AI-automation deployment speed were modeled; outcomes outside those bands fall beyond the analytical envelope. Cross-checking against disclosed security operations center contract values in SEC filings is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Extended Detection and Response Market
Security Software
Cybersecurity Software Market
Security Software
Network Camera Market
Security Software
BYOD Security Market
Security Software
VPN Software Market
Security Software
Phone Antivirus Software Market
Security Software
Digital Risk Protection Platform Market
Security Software
Smart Video Doorbell Market
Security Software
Network Security Appliance Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Public Key Infrastructure (PKI) Market
Security Software
Data Loss Prevention Market
Security Software
Asia Pacific Anti Money Laundering Solutions Market
Security Software
Global Data Protection As a Service (Dpaas) Market
Security Software
Europe IP Video Intercom Device and Equipment Market
Security Software
Cloud Encryption Software Market