
 Global Secure Access Service Edge Market | 2026-2036
Global Secure Access Service Edge Market Size, Share, and Industry Trends Forecast 2026-2036
Global Secure Access Service Edge Market Foresight
Cloud infrastructure buildout in North American hyperscale regions is hardening the supply base for SASE delivery. Palo Alto Networks leverages its Prisma platform to anchor enterprise deployments across distributed workforces. Zscaler sustains cloud-native differentiation through a globally distributed proxy architecture. Fortinet competes by integrating SD-WAN with security functions at the network edge.
Secure Access Service Edge converges wide-area networking and network security services into a unified cloud-delivered architecture, typically enforcing policies through distributed points of presence within 30 milliseconds of end users. Its primary purpose is to replace legacy perimeter-based security with identity-driven, context-aware access control for distributed resources. Cloud-native deployment dominates solution delivery, while Zero Trust Network Access captures the fastest expansion as organizations retire VPN infrastructure. Firewall as a Service occupies mature margin pools in regulated verticals requiring certified traffic inspection.
FCC guidelines on communications infrastructure resilience, EU GDPR cross-border data transfer rules, and Japan's METI cybersecurity frameworks collectively shape product certification and procurement standards for SASE vendors. NIST zero-trust architecture guidance in the United States further hardens baseline requirements for federal and defense-adjacent contracts. Stakeholders must monitor convergence between sovereign cloud mandates and vendor interoperability certifications as procurement criteria evolve.
Market Dynamics
Zero-trust architecture mandates are compressing procurement cycles for converged networking-security stacks, forcing enterprises to retire perimeter-based VPN infrastructure faster than vendor roadmaps anticipated.
Growth Catalysts
- EU AI Act compliance deadlines:European financial services firms must implement continuous identity verification by 2025, accelerating zero-trust network access deployments.
- Hybrid workforce persistence:Distributed engineering teams in Germany and Japan require sub-30ms policy enforcement at global points of presence.
- FCC resilience guidelines:US telecommunications carriers now mandate redundant cloud-delivered security for critical infrastructure protection.
Market Restraints
- Certified hardware shortage:FIPS 140-2 validated edge appliances face 14-week lead times from Taiwanese foundries, constraining regulated vertical rollouts.
- Cross-border data friction:GDPR Article 44 transfer mechanisms create architectural complexity for US-headquartered vendors serving European enterprises.
- Skills concentration:Zero-trust architecture expertise clusters in Silicon Valley and Tel Aviv, inflating implementation costs elsewhere.
Strategic Opportunities
- India's digital public infrastructure:The country's PLI scheme for data centers creates localized SASE delivery requirements for multinational IT services firms.
- Operational technology convergence:Manufacturing plants in Japan combine SD-WAN with industrial firewall services to secure Industry 4.0 deployments.
- Sovereign cloud mandates:Germany's Gaia-X framework opens procurement channels for EU-hosted security service edges.
Industry Challenges
- Multi-cloud policy orchestration:Enterprises struggle to maintain consistent access controls across AWS, Azure, and GCP native networking stacks.
- Legacy MPLS contract lock-in:Three-year carrier agreements delay cloud-native migration for mid-market financial institutions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Secure Access Service Edge Market |
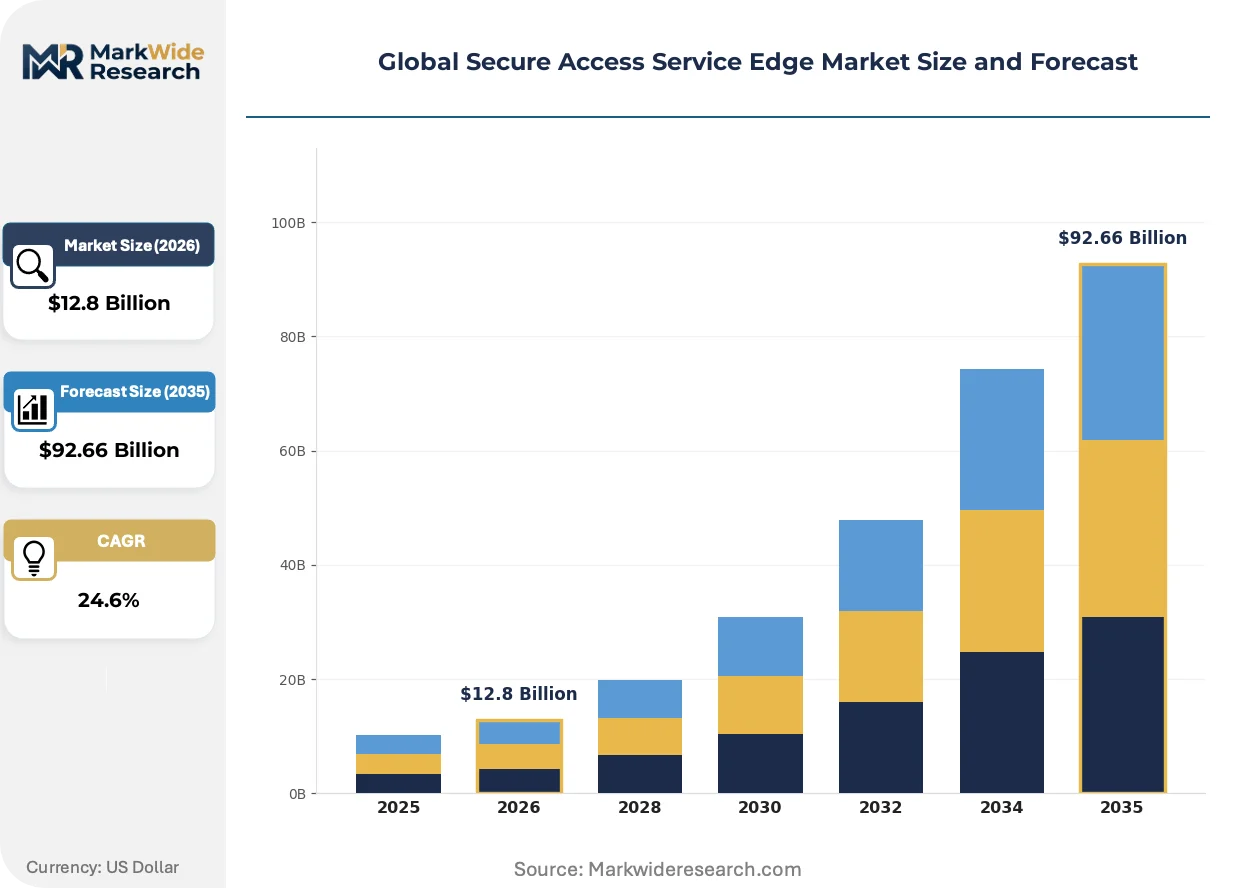
| Market Size in 2026 | $12.8 Billion |
| Market Size in 2035 | $92.66 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Mode: Cloud-native, On-premises, Hybrid, Multi-cloud Solution Offering: Security Gateway, Zero Trust Network Access, Firewall as a Service, Cloud Access Security Broker, Secure Web Gateway Use Case: Remote Workforce Enablement, Branch Connectivity, Cloud Migration, Internet of Things Protection, Application Segmentation End User: BFSI, Telecommunications, Manufacturing, Government, Education |
| Companies Covered | Palo Alto Networks, Zscaler, Cisco Systems, Fortinet, Cloudflare, Cato Networks, Broadcom, Akamai Technologies, Check Point Software Technologies, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Secure Access Service Edge Market Shifts & Advancements
Artificial intelligence inference at the network edge is compressing threat detection latency, reshaping how security policies adapt to behavioral anomalies in real time.
Single-vendor SASE platforms are consolidating SD-WAN, secure web gateway, cloud access security broker, and zero-trust network access into unified policy engines. Fortune 500 enterprises in the United States are adopting these stacks to reduce vendor management overhead. The consolidation is compressing procurement from four separate RFP cycles to single-source negotiations.
Japan's METI cybersecurity framework now mandates continuous device posture assessment for critical infrastructure operators. Industrial conglomerates must demonstrate real-time compliance to maintain operational licenses. Heavy manufacturing and energy utilities are responding by embedding SASE agents directly into operational technology gateways.
Enterprise sourcing patterns favor consumption-based pricing over perpetual licensing for network security functions. Mid-market buyers in Germany now procure firewall-as-a-service through managed service providers rather than direct vendor relationships. This shift is most visible among automotive suppliers consolidating multi-site security under regional IT outsourcers.
Global Secure Access Service Edge Market Segmentation
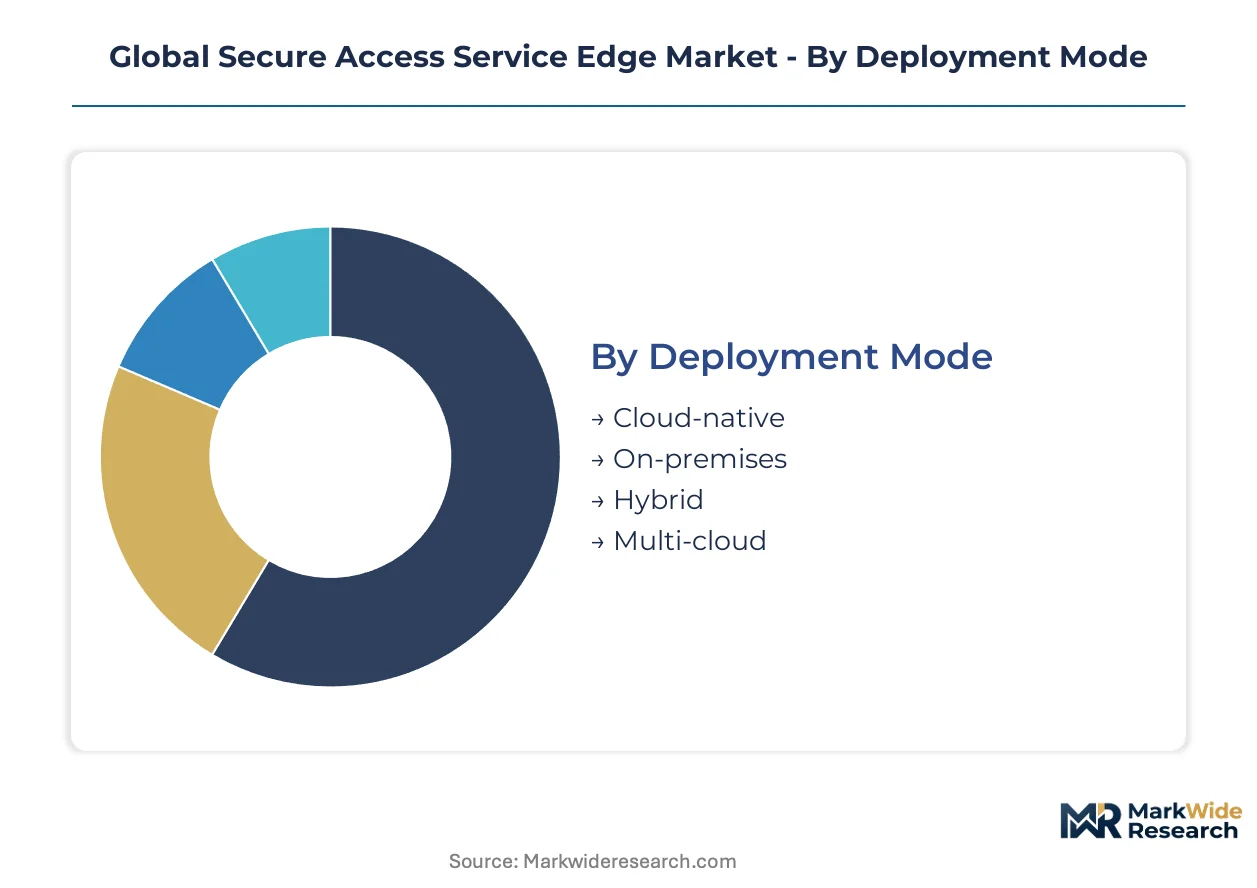
SASE architectures fragment across deployment topologies, security functions, and organizational maturity levels. Procurement patterns diverge sharply between cloud-native adopters and regulated verticals requiring certified on-premises inspection. Understanding these fault lines exposes where vendor roadmaps align with buyer constraints.
Deployment Mode:
Cost tier separates buyers in this category, with capital intensity and compliance burden driving opposite ends of the spectrum.
- Cloud-native:Fully distributed policy enforcement through vendor-managed points of presence eliminates data center footprint. Financial services firms in the United States and Germany dominate consumption as they retire MPLS contracts for consumption-based alternatives.
- Hybrid:Split traffic inspection between cloud proxies and on-premises appliances satisfies data residency requirements. Japanese manufacturers and European utilities favor this mode to satisfy METI and GDPR localization mandates without full cloud migration.
- On-premises:Certified hardware appliances process sensitive traffic within sovereign boundaries. Government and defense contractors in Germany require FIPS 140-2 validated edge devices for classified network segments.
- Multi-cloud:Consistent policy orchestration across AWS, Azure, and GCP native networking stacks. Large enterprises with distributed cloud estates use this mode to avoid vendor lock-in, though operational complexity remains acute.
Cloud-native leads volumes today; multi-cloud is gaining share fastest.
Solution Offering:
Application maturity and margin concentration divide this category, with established functions competing against high-growth replacements for legacy VPN.
- Zero Trust Network Access:Identity-driven session authentication replaces perimeter-based VPN tunnels with continuous verification. EU AI Act compliance deadlines are compressing procurement cycles for European financial institutions replacing remote access infrastructure.
- Firewall as a Service:Cloud-delivered traffic inspection with certified logging for regulated industries. US telecommunications carriers and German automotive suppliers procure through managed service providers to satisfy FCC resilience guidelines and TISAX certification requirements.
- Security Gateway:Unified policy enforcement point consolidating multiple security functions. Mid-market buyers favor bundled capabilities to reduce vendor management overhead.
- Cloud Access Security Broker:Visibility and control layer for sanctioned and unsanctioned cloud applications. Shadow IT discovery drives adoption among professional services firms with distributed workforces.
- Secure Web Gateway:URL filtering and malware inspection for internet-bound traffic. Mature functionality with compressed margins, often bundled into broader SASE suites rather than procured standalone.
Firewall as a Service leads volumes today; Zero Trust Network Access is expanding most quickly.
Use Case:
Organizational transformation stage determines buyer priorities, with post-pandemic workforce patterns competing against industrial digitization initiatives.
- Remote Workforce Enablement:Sub-30ms policy enforcement for distributed knowledge workers accessing cloud applications. German engineering firms and US technology companies dominate this segment as hybrid work persists.
- Branch Connectivity:SD-WAN integration with security functions to replace expensive MPLS backhaul. Retail and hospitality chains in Japan consolidate hundreds of locations under unified management planes.
- Cloud Migration:Secure transit between on-premises data centers and public cloud workloads. Financial institutions use this case to decommission legacy perimeter defenses during application modernization.
- Internet of Things Protection:Microsegmentation for unmanaged device fleets in operational technology environments. Japanese manufacturing plants embed SASE agents into Industry 4.0 gateways under METI cybersecurity mandates.
- Application Segmentation:Fine-grained access controls between microservices and legacy monoliths. DevOps teams in Silicon Valley and Tel Aviv clusters drive adoption for zero-trust service mesh integration.
Remote Workforce Enablement leads volumes today; Internet of Things Protection shows the steepest expansion trajectory.
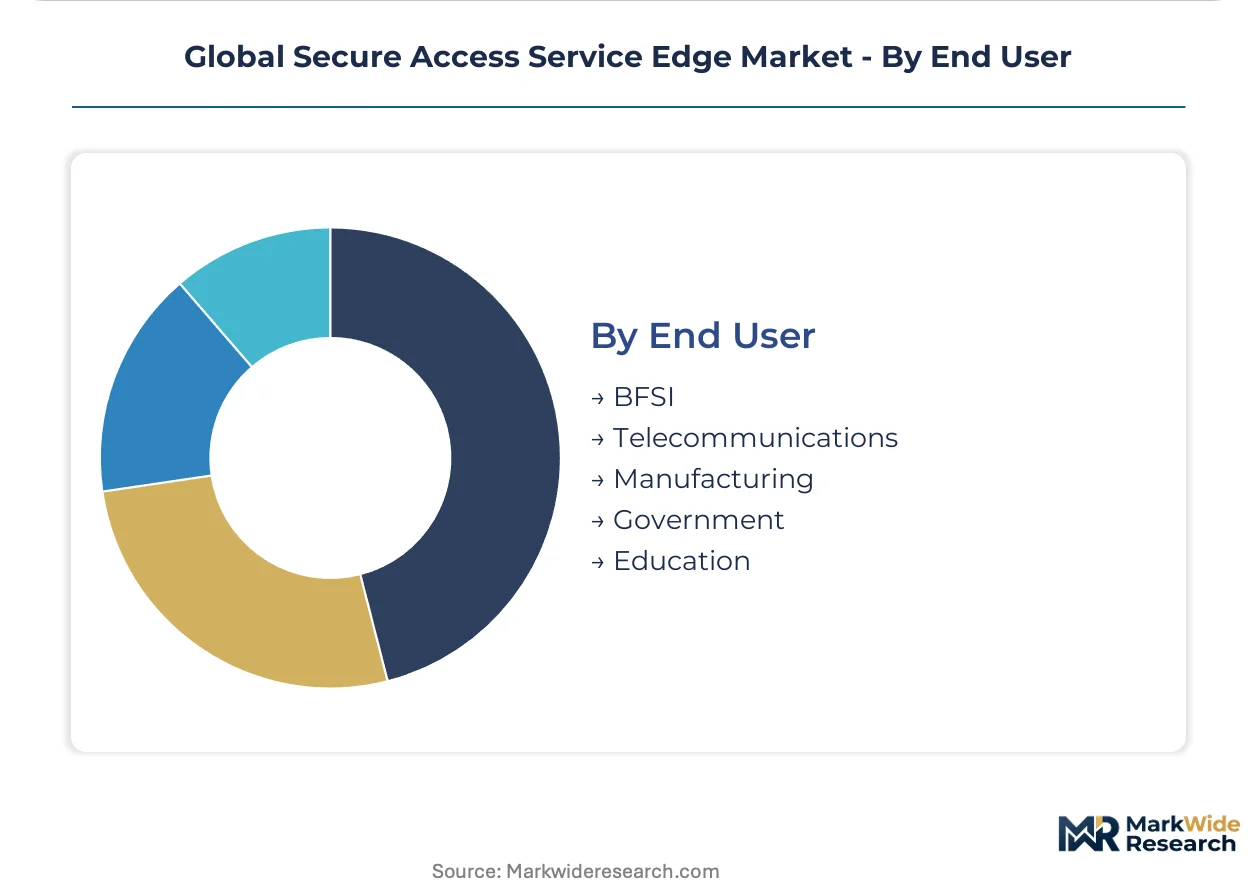
End User:
Regulatory intensity and procurement sophistication separate buyers, with certified verticals demanding validated architectures.
- BFSI:Continuous identity verification and transaction logging to satisfy EU AI Act, GDPR, and SEC cybersecurity disclosure rules. European and US institutions represent the most demanding certification requirements.
- Telecommunications:Critical infrastructure protection under FCC resilience guidelines and national security frameworks. US carriers mandate redundant cloud-delivered security with 99.999% availability commitments.
- Manufacturing:Convergence of IT and OT networks under Industry 4.0 initiatives. Japanese industrial conglomerates combine SD-WAN with industrial firewall services for real-time compliance demonstration.
- Government:Sovereign cloud mandates and classified data handling requirements. German federal procurement channels favor EU-hosted security service edges under Gaia-X framework alignment.
- Education:Cost-constrained protection for distributed campuses and research networks. US public universities procure through consortium arrangements to achieve scale pricing.
BFSI leads volumes today; Manufacturing is climbing the fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory arbitrage is accelerating vendor investment decisions, as compliance cost differentials between jurisdictions reshape where SASE infrastructure gets deployed. Enterprises migrate procurement toward markets with harmonized certification standards, compressing deployment timelines for cross-border implementations.
United States
NIST zero-trust architecture guidance hardens federal procurement requirements, mandating continuous identity verification for defense-adjacent contracts. FCC resilience guidelines compel telecommunications carriers to adopt redundant cloud-delivered security with 99.999% availability commitments. Silicon Valley engineering clusters concentrate zero-trust architecture expertise, inflating implementation costs for enterprises sourcing outside California and Tel Aviv.
Germany
Gaia-X framework procurement channels favor EU-hosted security service edges, creating localized delivery requirements for sovereign cloud mandates. GDPR Article 44 cross-border data transfer mechanisms generate architectural complexity for non-EU vendors serving German automotive and financial institutions. Bavarian industrial conglomerates combine SD-WAN with industrial firewall services to satisfy TISAX certification requirements under Industry 4.0 initiatives.
Japan
METI cybersecurity frameworks mandate continuous device posture assessment for critical infrastructure operators, requiring real-time compliance demonstration to maintain operational licenses. Manufacturing plants in the Chubu region embed SASE agents directly into operational technology gateways, securing Industry 4.0 deployments. Heavy manufacturing and energy utilities anchor demand for hybrid deployment modes that split traffic inspection between cloud proxies and on-premises appliances.
India
PLI scheme incentives for data center infrastructure create localized SASE delivery requirements for multinational IT services firms operating across the subcontinent. Karnataka and Telangana technology corridors concentrate cloud-native adoption among engineering teams serving global clients. Domestic financial institutions accelerate zero-trust network access deployments to satisfy RBI cybersecurity guidelines for digital payment infrastructure.
United Kingdom
Financial Conduct Authority operational resilience rules compress procurement cycles for converged networking-security stacks among London-headquartered institutions. NCSC zero-trust guidance shapes baseline requirements for government and critical national infrastructure contracts. Southeast England technology clusters drive adoption of single-vendor SASE platforms to reduce vendor management overhead across distributed cloud estates.
Global Secure Access Service Edge Market Competitive Landscape
United States vendors anchor the premium tier through integrated platform architectures; Israeli and European specialists hold differentiated positions in threat intelligence and data sovereignty compliance. Market structure exhibits moderate consolidation, with scale players capturing Fortune 500 procurement while regional providers serve compliance-constrained verticals. Three archetypes dominate: cloud-native pure-plays with globally distributed proxy infrastructure, networking incumbents converging SD-WAN with security functions, and managed service providers packaging consumption-based pricing for mid-market buyers. Competitive intensity centers on M&A activity to acquire zero-trust architecture talent, and strategic partnerships with hyperscale cloud providers to embed security into native networking stacks.
Within the cloud-native tier, Zscaler and Cloudflare exemplify globally distributed delivery models that eliminate data center footprint for distributed workforces. Palo Alto Networks occupies a position bridging networking heritage with converged security platform consolidation. Among networking-heritage competitors, Fortinet represents the integration archetype combining SD-WAN with edge security functions. These three anchors illustrate how vendor roadmaps diverge between proxy-native architectures and appliance-integrated stacks, with procurement patterns increasingly favoring single-source negotiations over multi-vendor RFP cycles.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Zscaler |
| Cisco Systems |
| Fortinet |
| Cloudflare |
| Cato Networks |
| Broadcom |
| Akamai Technologies |
| Check Point Software Technologies |
| Others |
Supply & Pricing Matrix
EU sovereign cloud mandates under the Gaia-X framework gate qualified supply for premium-tier SASE deployments, restricting certified vendor participation to providers with EU-hosted infrastructure and FIPS 140-2 validated edge appliances. German automotive suppliers and financial institutions now pay material premiums for compliant service edges, while non-certified vendors face exclusion from federal procurement channels.
Pricing Analysis
Distributor margins for managed service providers compress direct-to-enterprise pricing by 15-25 points, driving mid-market buyers toward consumption-based firewall-as-a-service procurement. Three-tier pricing structure across premium, standard, and economy levels separates Gaia-X certified deployments from uncertified cloud-native alternatives, with certification grade and volume scale as primary differentiation drivers. Pricing pressure stems from hyperscaler-native security bundles eroding standalone vendor value propositions. Mid-market manufacturing segments exhibit highest price sensitivity; defense-adjacent federal contracts show lowest.
Supply Chain Analysis
India's PLI scheme for data center infrastructure reshapes sourcing patterns, mandating local content thresholds for multinational IT services firms operating across the subcontinent. Hardware supply concentrates in Taiwan, South Korea, and the United States, with FIPS 140-2 validated edge appliances drawing from specialized semiconductor foundries and cryptographic module fabricators. Single-source vulnerability runs through Taiwanese foundry capacity for certified silicon. Distribution runs through hyperscale cloud marketplaces and regional managed service providers rather than direct vendor relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market reads as a late-cycle quality story. Enterprise procurement is compressing toward single-vendor SASE platforms with integrated zero-trust network access, displacing multi-RFP legacy stacks.
For Market Incumbents: Extend platform consolidation roadmaps to capture retiring VPN infrastructure replacement cycles before hyperscaler-native bundles capture mid-market share. Acquire zero-trust architecture talent clusters in Tel Aviv and Silicon Valley to defend implementation margins against service provider commoditization. Fortify Gaia-X certification investments to maintain access to German federal and automotive procurement channels. For New Entrants and Emerging Players: Cloud-native channel partnerships with hyperscale marketplaces offer the lowest-friction route to mid-market manufacturing accounts in Japan's Chubu industrial corridor and India's Karnataka technology belt. Target Internet of Things Protection use cases in operational technology environments, where METI compliance mandates create urgency but incumbent platforms lack embedded gateway integration. Lead with consumption-based pricing and rapid deployment guarantees to differentiate from legacy appliance vendors. For Investors and Strategic Acquirers: Roll-up economics work for regional managed service providers with sovereign cloud certifications because procurement centralization under FCC resilience guidelines and EU AI Act deadlines is compressing vendor counts. Five-to-ten year viability favors providers with hybrid deployment capabilities spanning cloud-native and certified on-premises inspection. Watch hyperscaler security bundle attach rates as the inflection signal for standalone vendor margin compression.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Platform Integration | Consolidates SD-WAN, SWG, CASB, and ZTNA into unified policy engines for Fortune 500 procurement compression. |
| Gaia-X Certification Investment | Opens German federal and automotive procurement channels under sovereign cloud mandates and TISAX requirements. |
| Hyperscale Marketplace Partnership | Embeds SASE offerings into AWS, Azure, and GCP native networking stacks for mid-market consumption-based adoption. |
| OT Gateway Embedding | Positions SASE agents directly into industrial control systems for METI-compliant Japanese manufacturing deployments. |
| Zero-Trust Talent Acquisition | Secures scarce architecture expertise in Tel Aviv and Silicon Valley to defend implementation margins. |
Research Methodology
Multiple input streams — primary interviews with CISOs and IT procurement officers, hyperscaler capex disclosures, and regulatory filing analysis — were reconciled to construct bottom-up and top-down market estimates. Stakeholder conversations spanned zero-trust architects at financial services firms, channel partners distributing firewall-as-a-service, and compliance officers navigating EU AI Act implementation. Secondary validation drew from FCC resilience guideline filings, METI cybersecurity framework documentation, Gaia-X procurement channel records, and SEC 10-K security revenue disclosures.
Data-stream reconciliation anchored volume projections to deployment mode adoption curves and solution offering replacement rates across the analysis window. Segmentation dimensions modeled include deployment topology, security function maturity, organizational size tier, and regional regulatory cluster. CAGRs were derived from S-curve penetration modeling against MPLS contract expiration cycles and VPN infrastructure retirement timelines. Forecast inputs incorporated EU AI Act compliance deadline clustering and FCC critical infrastructure protection mandates.
The model assumes a particular technology adoption path; alternative pathways for AI-driven edge inference would alter the outlook if threat detection latency compression accelerates beyond current vendor roadmaps. Forecasts reflect documented assumptions regarding hybrid workforce persistence and sovereign cloud procurement centralization. Regulatory fragmentation, certified hardware supply constraints, and hyperscaler bundle attach rates constitute specific revision risks. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
North America Secure Access Service Edge Market
Security Software
Global Security Operation Center As a Service Market
Security Software
Global Mobile Security Software Market
Security Software
Patch and Remediation Software Market
Security Software
IAM Security Services Market
Security Software
Asia Pacific Anti Money Laundering Solutions Market
Security Software
Stalkerware Market
Security Software
Key Management Service Market
Security Software
Security Software Market
Security Software
Encryption Software Market
Security Software
Global Enterprise Data Loss Prevention Software Market
Security Software
Application Control Market
Security Software
Europe Encryption Software Market
Security Software
Enterprise Rights Management Solution Market
Security Software
Doorbell Camera Market
Security Software
Asia-Pacific Smart Doorbell Market