
 Business Email Compromise (BEC) Market | 2026-2036
Business Email Compromise (BEC) Market Size, Share, and Industry Trends Forecast 2026-2036
Business Email Compromise (BEC) Market Outlook
Enterprise-grade email authentication with DMARC enforcement and behavioral anomaly detection is reorganizing how organizations evaluate BEC defense procurement. Proofpoint leverages cloud-native architecture to anchor its position among large corporations requiring real-time threat intelligence. Mimecast sustains competitive pressure through integrated archiving and impersonation protection, while Check Point Software Technologies extends its firewall-centric customer base into email security with unified threat management.
Business Email Compromise denotes a targeted cyberattack where adversaries compromise or spoof corporate email accounts to execute fraudulent wire transfers or extract sensitive data, typically exploiting identity deception rather than malware payloads. The attack vector relies on social engineering precision, domain similarity tactics, and compromised credentials to bypass traditional perimeter defenses. Cloud-based delivery models are capturing expanding share as small and medium enterprises abandon on-premises maintenance burdens. Large corporations drive premium spending on managed services combining incident response with continuous employee assessment, while software solutions segment attracts consolidation plays from platform vendors seeking bundled security stacks.
The Federal Trade Commission scrutinizes BEC victim reimbursement practices under consumer protection statutes, while NIST and the Cybersecurity and Infrastructure Security Agency mandate phishing-resistant authentication for federal contractors. European operators face parallel pressure from GDPR breach notification timelines and the Digital Operational Resilience Act's incident reporting thresholds. Stakeholders must weigh whether to build in-house security operations center capacity or outsource to managed detection and response providers as attack sophistication outpaces internal training cycles.
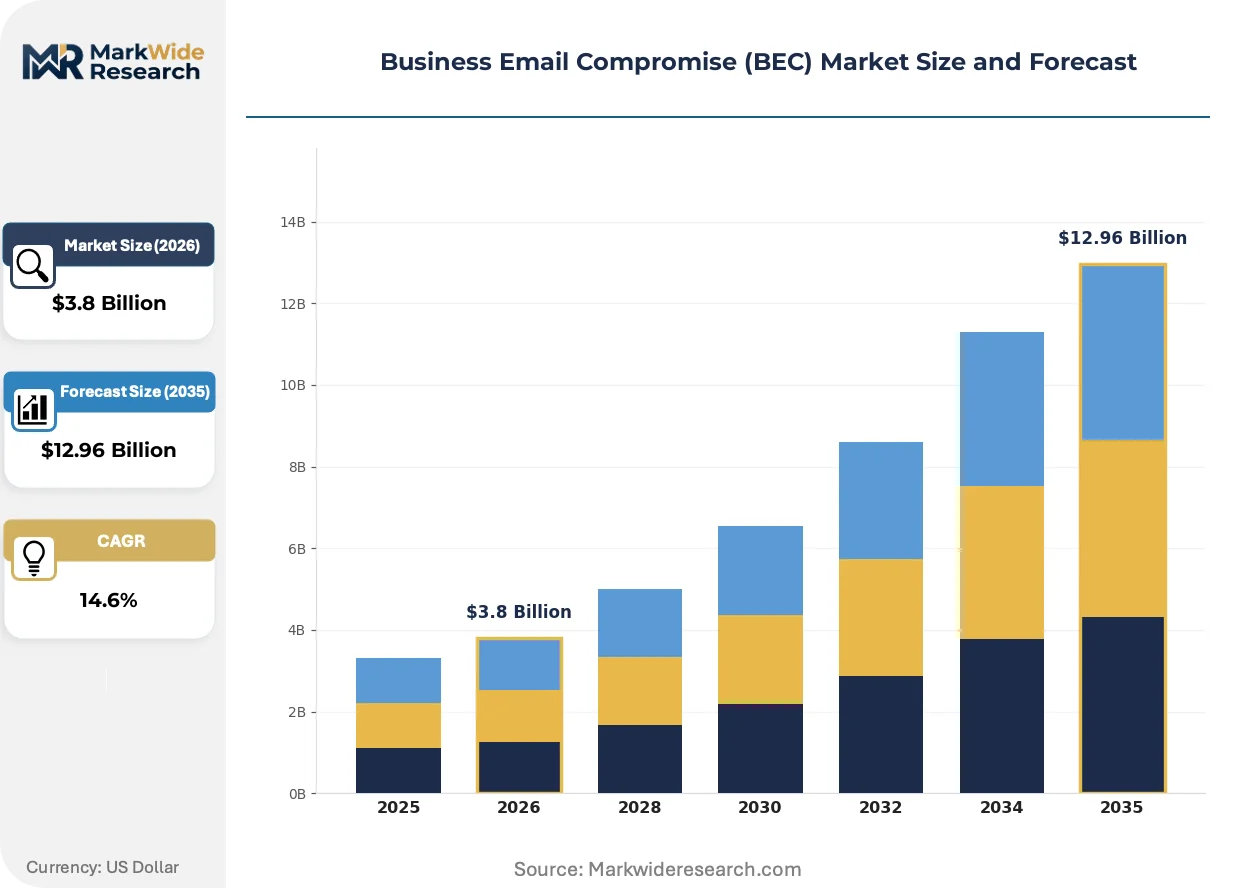
Market Dynamics
AI-powered behavioral anomaly detection is fragmenting traditional perimeter-based email security architectures, forcing organizations to rebuild authentication stacks around identity-centric rather than network-centric trust models. This structural shift concentrates procurement decisions on vendors capable of real-time sender verification and continuous credential monitoring.
Growth Catalysts
- SEC Disclosure Mandates:Public companies face accelerated reporting timelines for material cybersecurity incidents, driving board-level investment in BEC prevention infrastructure.
- Cloud Migration:Enterprise shift to Microsoft 365 and Google Workspace creates native integration opportunities for API-based email security overlays.
- Wire Transfer Automation:Treasury departments at multinational manufacturers deploy dual-authorization workflows that require embedded email authentication.
Market Restraints
- Skilled Analyst Shortage:Security operations centers struggle to hire personnel capable of tuning machine learning models for false-positive reduction.
- Legacy Email Gateway Lock-in:Enterprises with multi-year contracts face switching costs that delay migration to cloud-native alternatives.
- Cross-Border Data Friction:GDPR data localization requirements complicate centralized threat intelligence sharing across European operations.
Strategic Opportunities
- Mid-Market Managed Services:Organizations with 500-5,000 employees lack internal security operations capacity, creating demand for outsourced BEC monitoring.
- API-First Architecture:Native integration with collaboration platforms enables pre-inbox filtering without MX record changes.
- NIST Framework Alignment:Federal contractor compliance requirements open procurement pathways for vendors with FedRAMP authorization.
Industry Challenges
- Deepfake Voice Synthesis:Adversaries combine compromised email credentials with synthetic audio to bypass verbal verification protocols.
- Vendor Consolidation Complexity:Organizations struggle to integrate point solutions into coherent security orchestration workflows.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Business Email Compromise (BEC) Market |
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $12.96 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Phishing, Spoofing, Malware, Ransomware Delivery Model: Cloud-based, On-premises, Hybrid, Managed Service End User: Small Enterprises, Medium Enterprises, Large Corporations, Government Agencies Service Type: Incident Response, Training, Assessment, Software Solutions |
| Companies Covered | Proofpoint, Mimecast, Check Point Software Technologies, Broadcom, Fortra, Trend Micro, GreatHorn, Tessian, Acronis International GmbH, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Business Email Compromise (BEC) Market Strategic Shifts
Generative AI is arming attackers with linguistically sophisticated phishing content while simultaneously enabling defenders to deploy predictive detection models. This dual-use tension accelerates investment in continuous authentication mechanisms that transcend static rule-based filtering.
Natural language processing engines trained on executive communication patterns are fragmenting conventional signature-based detection methods. Financial services firms deploy these tools to baseline sender behavior and flag anomalous request phrasing. The technology compresses mean-time-to-detection for impersonation attempts from hours to minutes.
The NIST Cybersecurity Framework revision mandates phishing-resistant authentication for federal contractors handling controlled unclassified information. Defense industrial base suppliers must deploy FIDO2 hardware keys or equivalent protections. This regulatory pressure cascades through supply chains, compelling prime contractors to impose identical requirements on subcontractors.
Buyers increasingly unbundle email security from broader cybersecurity suites, selecting best-of-breed BEC specialists over bundled offerings. Fortune 500 procurement teams run parallel evaluations of point solutions and platform extensions. This pattern concentrates most visibly in United States healthcare systems navigating HIPAA security rule enforcement.
Business Email Compromise (BEC) Market Segmentation
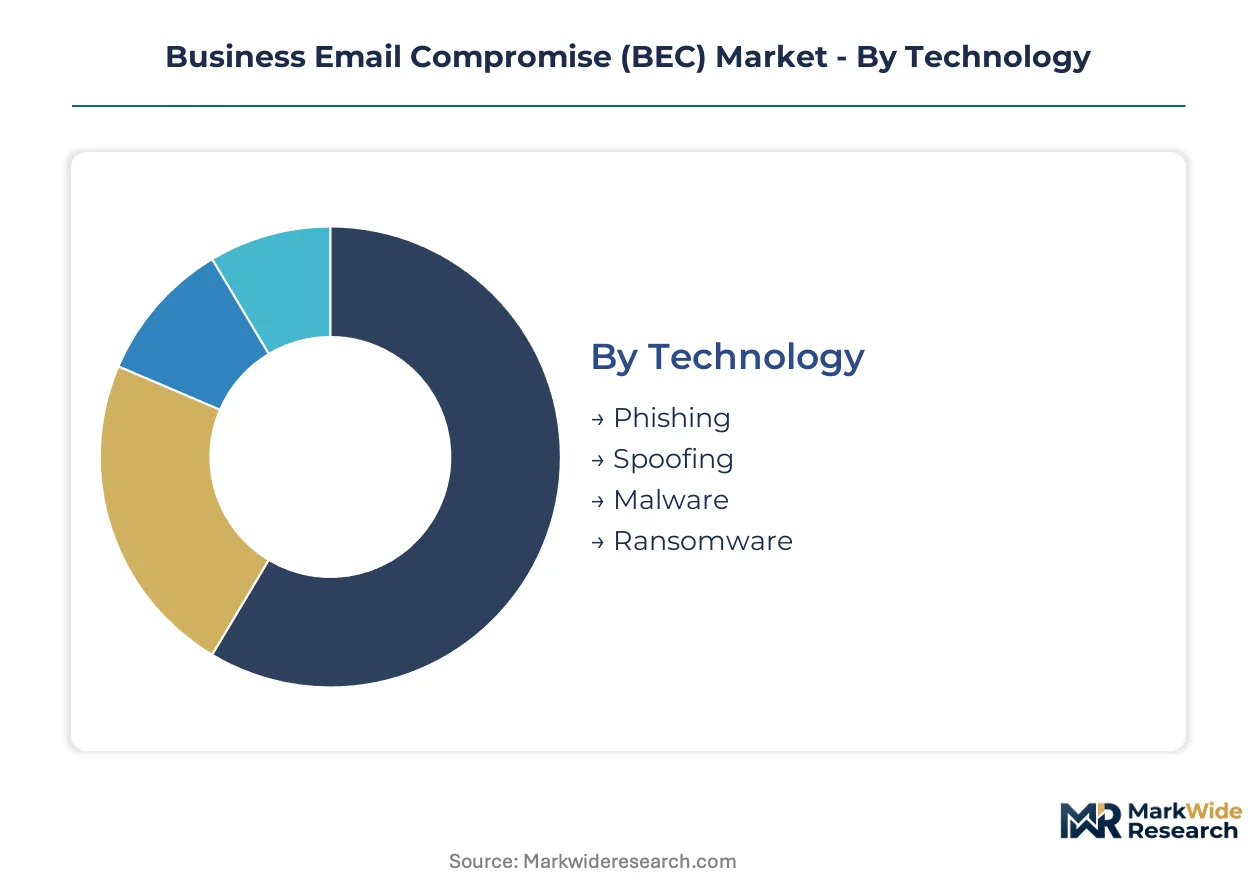
Segmentation in the BEC market reveals how procurement patterns diverge across technical architectures, deployment preferences, and organizational scale. Buyers with distinct risk profiles and compliance obligations select fundamentally different solution bundles, creating parallel demand channels that vendors must address separately.
Technology:
Channel mix varies sharply by attack vector sophistication, with advanced persistent threat methods flowing through managed security service providers while commodity attack defenses concentrate in direct software sales.
- Phishing:Social engineering campaigns leverage credential harvesting through deceptive links and fraudulent login portals. Financial services firms in the United States drive premium spending on real-time link analysis and sandbox detonation capabilities as wire fraud losses mount.
- Spoofing:Domain impersonation and display name manipulation exploit trust in established business relationships. DMARC enforcement adoption concentrates among Fortune 500 procurement teams seeking sender authentication at scale.
- Malware:Malicious attachments and weaponized documents bypass perimeter filters through encryption and polymorphic payloads. Detection relies on behavioral analysis engines integrated with endpoint protection platforms.
- Ransomware:Encryption-based extortion often follows initial email compromise, with affiliates purchasing network access from BEC operators. Incident response retainers dominate this channel.
Phishing dominates installed base. Spoofing is where expansion concentrates.
Delivery Model:
Cost tier segmentation separates capital-constrained buyers seeking operational expenditure predictability from organizations prioritizing data sovereignty and customization control.
- Cloud-based:API-native deployments integrate directly with Microsoft 365 and Google Workspace without MX record modifications. Small and medium enterprises abandon on-premises maintenance burdens fastest here.
- On-premises:Hardware appliances and virtualized gateways retain appeal in regulated industries with strict data residency mandates. Large manufacturers with legacy network architectures sustain this segment.
- Hybrid:Split configurations route sensitive communications through local inspection while leveraging cloud intelligence for bulk traffic. Government agencies with classified and unclassified email streams favor this architecture.
- Managed Service:Outsourced security operations centers monitor, investigate, and remediate threats under service level agreements. Mid-market organizations with 500-5,000 employees lack internal analyst capacity.
Cloud-based deployments dominate installed base. Managed Service is climbing the fastest.
End User:
Customer type determines whether procurement flows through value-added resellers, direct enterprise sales teams, or federal contracting vehicles.
- Small Enterprises:Organizations below 100 employees rely on bundled security suites from productivity platform vendors. Price sensitivity pushes adoption toward cloud-native solutions with minimal implementation overhead.
- Medium Enterprises:IT security teams with limited headcount seek automated remediation and managed detection overlays. This segment represents the fastest-growing trajectory for outsourced BEC monitoring services.
- Large Corporations:Dedicated security operations centers demand real-time threat intelligence feeds and custom rule development. Procurement runs through direct vendor relationships with dedicated customer success functions.
- Government Agencies:Federal, state, and municipal entities require FedRAMP authorization and compliance with NIST Cybersecurity Framework mandates. Specialized resellers with security clearance capabilities control this channel.
Large Corporations dominate installed base. Government Agencies is where expansion concentrates.
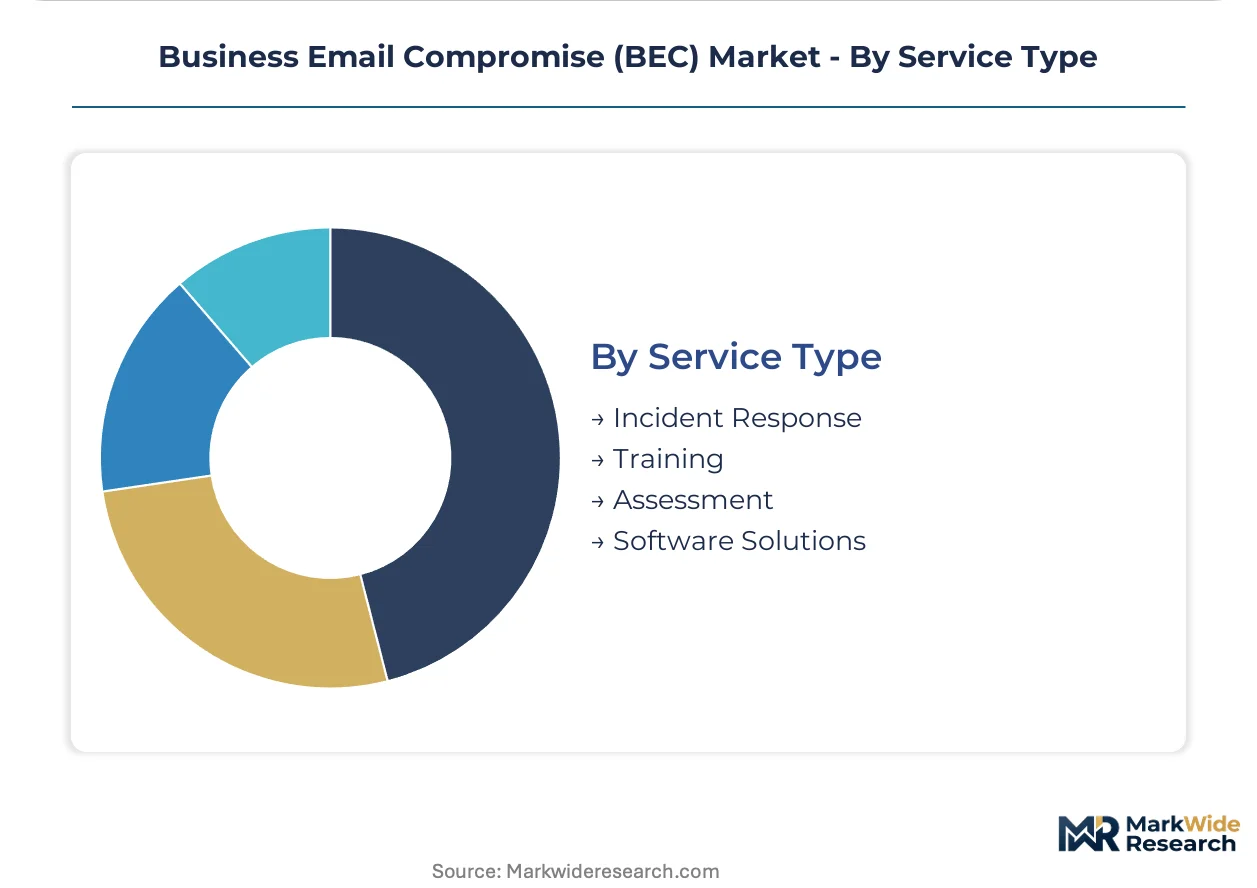
Service Type:
Application-based segmentation separates reactive incident containment from proactive risk reduction, with procurement cycles and stakeholder buyers differing fundamentally across these modes.
- Incident Response:Retained forensic teams investigate confirmed compromises, contain lateral movement, and restore operational integrity. Breach notification statutes in the United States and European Union accelerate demand.
- Training:Simulated phishing exercises and security awareness curricula reduce susceptibility to social engineering. Human resources and compliance departments jointly procure these programs.
- Assessment:Domain security audits, DMARC readiness evaluations, and executive impersonation risk scans identify vulnerabilities before exploitation. Consulting firms and specialized boutiques compete here.
- Software Solutions:Perpetual licenses and subscription access to email security platforms with embedded AI detection engines. Chief information security officers evaluate these against broader cybersecurity suite bundles.
Software Solutions dominate installed base. Incident Response is gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand elasticity varies sharply across geographies. United States buyers prioritize premium managed services with minimal price sensitivity, while small enterprises in emerging markets favor low-touch cloud deployments with predictable operational expenditure.
United States
Fortune 500 procurement of integrated BEC prevention suites accelerates as SEC disclosure mandates tighten board-level accountability. The FTC scrutinizes victim reimbursement practices under consumer protection statutes. Silicon Valley and New York financial centers concentrate deployment of AI-powered behavioral anomaly detection systems.
Germany
Manufacturing conglomerates and automotive suppliers drive demand for email authentication stacks aligned with NIS2 Directive requirements. The Federal Office for Information Security mandates phishing-resistant authentication for critical infrastructure operators. Industrial clusters in Baden-Württemberg and Bavaria anchor managed security service provider expansion.
United Kingdom
Financial services firms in the City of London expand procurement of real-time sender verification tools as wire fraud losses mount. The National Cyber Security Centre enforces DMARC compliance across government supply chains. Thames Valley technology corridor hosts concentrated deployment of API-native email security overlays.
Japan
Keiretsu trading houses and electronics manufacturers prioritize embedded email authentication for automated treasury workflows. METI guidelines on supply chain cybersecurity cascade authentication requirements through subcontractor networks. Tokyo-Osaka industrial corridor concentrates hybrid deployment architectures serving classified and unclassified communications.
Australia
Mid-market organizations with limited security operations capacity drive fastest-growing demand for outsourced BEC monitoring. The Australian Cyber Security Centre mandates incident reporting thresholds aligned with critical infrastructure protection legislation. Sydney and Melbourne financial districts anchor cloud-native solution adoption among regional banking headquarters.
Business Email Compromise (BEC) Market Competitive Environment
Technology leadership and cost leadership are held by different player archetypes across the BEC defense ecosystem. The vendor base organizes around three strategic tiers: cloud-native specialists with API-first architectures, platform extenders leveraging existing cybersecurity customer relationships, and managed security service providers bundling monitoring with incident response. Consolidation pressure intensifies as platform vendors acquire point solutions to complete bundled security stacks, while pure-play specialists defend position through FedRAMP authorization and vertical-specific compliance expertise.
Among the cloud-native specialists, Proofpoint and Mimecast occupy positions exemplifying the API-first architecture archetype, while Check Point Software Technologies represents the platform extension model leveraging firewall-centric customer bases. These three companies anchor the competitive structure, with each archetype competing for distinct procurement decision-makers: chief information security officers evaluating best-of-breed solutions versus those prioritizing unified threat management consolidation.
| Leading Market Players |
|---|
| Proofpoint |
| Mimecast |
| Check Point Software Technologies |
| Broadcom |
| Fortra |
| Trend Micro |
| GreatHorn |
| Tessian |
| Acronis International GmbH |
| Others |
Value Chain & Pricing Dynamics
Ninety-day implementation cycles for cloud-native email security deployments compress procurement timelines while amplifying vendor pricing power among FedRAMP-authorized providers. This lead-time compression concentrates contract value in recurring subscription streams rather than perpetual licenses, reshaping how Proofpoint and Mimecast structure customer lifetime value calculations against on-premises appliance competitors.
Pricing Analysis
Managed detection and response service tiers now drive lifetime value in the BEC defense market, with incident response retainers and continuous employee assessment bundles commanding premium positioning. Three-tier pricing structure across premium, standard, and economy levels separates Fortune 500 enterprises seeking dedicated security operations center support from mid-market buyers prioritizing automated remediation. Cost compression in the small enterprise tier intensifies as Microsoft and Google bundle basic email protection with productivity platform subscriptions. Government agencies exhibit least price sensitivity due to NIST Cybersecurity Framework compliance mandates, while sub-100-employee organizations face acute budget constraints.
Supply Chain Analysis
Just-in-time threat intelligence distribution dominates vendor operations, with API-native platforms pushing signature updates in sub-minute intervals rather than batching daily releases. The technology stack draws from United States cloud infrastructure providers, Israeli behavioral analytics research centers, and Indian security operations center talent pools. Single-source vulnerability concentrates in specialized natural language processing engine licensing from a narrow cohort of AI research labs. Distribution runs through value-added resellers with security clearance capabilities for government verticals, direct enterprise sales teams for Fortune 500 accounts, and hyperscaler marketplaces for small and medium enterprise self-service procurement.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation opportunity persists as mid-market organizations abandon bundled security suites for best-of-breed BEC specialists, creating niche openings for API-first vendors with vertical-specific compliance expertise.
For Market Incumbents: Shield market position by acquiring managed detection and response boutiques with FedRAMP authorization to close coverage gaps in government supply chains. Deepen API integration investments with Microsoft 365 and Google Workspace to raise switching costs against platform extenders like Check Point. Prioritize vertical integration into natural language processing engine development to reduce dependency on third-party AI licensing. For New Entrants and Emerging Players: FedRAMP authorization fast-track opens procurement pathways among defense industrial base suppliers facing NIST Cybersecurity Framework revision deadlines. Target mid-market managed services for organizations with 500-5,000 employees lacking internal security operations capacity, where outsourced BEC monitoring demand climbs fastest. Lead with API-first architecture enabling pre-inbox filtering without MX record changes to reduce implementation friction against legacy gateway incumbents. For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-compliance play because SEC disclosure mandates and European Digital Operational Resilience Act thresholds permanently elevate email security governance to board-level accountability. Acquisition candidates with phishing-resistant authentication alignment and incident response retainer revenue streams offer defensive positioning. Monitor NIST Cybersecurity Framework revision implementation velocity across federal contractor supply chains as inflection indicator for premium vendor pricing power.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Pursuit | Opens federal contractor procurement pathways under NIST Cybersecurity Framework mandates. |
| API-Native Platform Integration | Enables pre-inbox filtering without MX record changes for Microsoft 365 and Google Workspace. |
| Managed Detection and Response Expansion | Captures mid-market organizations with 500-5,000 employees lacking internal analyst capacity. |
| Natural Language Processing Engine Development | Reduces dependency on third-party AI licensing for behavioral anomaly detection capabilities. |
| Incident Response Retainer Packaging | Bundles forensic investigation and breach notification compliance under service level agreements. |
Study Parameters
Desk research of vendor pricing disclosures, federal procurement databases, and cloud security alliance certification registries preceded structured interviews with chief information security officers, managed security service provider operations directors, federal contracting officers, and email security platform product managers. Primary intelligence combined with secondary validation against SEC filing references to cybersecurity infrastructure spending, hyperscaler marketplace transaction data, and NIST framework implementation guidance. Bottom-up deployment estimates triangulated against top-down market sizing from technology vendor revenue disclosures.
Variance decomposition across the analysis window isolates growth contributions from cloud migration velocity, regulatory compliance deadlines, and managed service penetration rates. Segmentation dimensions modeled include delivery model architecture, organization size tier, vertical industry, attack vector sophistication, and geographic regulatory cluster. CAGRs derive from logistic diffusion curves fitted to adoption saturation levels by customer segment, with inputs from treasury automation deployment timelines and security operations center analyst hiring trajectories.
Underlying assumptions cover sustained SEC enforcement of cybersecurity disclosure rules and stable hyperscaler platform market share, with deviation risk concentrated in generative AI attack sophistication outrunning defensive model retraining cycles. Forecasts reflect these conditions without explicit probability weighting. Revision becomes warranted when phishing-resistant authentication mandate implementation crosses federal contractor supply chain penetration thresholds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Europe Anti-Money Laundering Software Market
Security Software
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Network Video Recorder (NVR) Market
Security Software
Spam Blocking Software Market
Security Software
Identity Verification Software Market
Security Software
Network Camera Market
Security Software
Facial Recognition Market
Security Software
Digital Credential Management Software Market
Security Software
Cybersecurity Software Market
Security Software
North America Secure Access Service Edge Market
Security Software
Identity-As-A-Service (Idaas) Market
Security Software
Secaas Market
Security Software
Global Security Assertion Markup Language (SAML) Authentication Market
Security Software
Remote Access Management Market
Security Software
Anti-Fraud Management System Market