
 Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market | 2026-2036
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market Size, Share, and Industry Trends Forecast 2026-2036
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market Analysis
Healthcare network security spending is consolidating as hospital systems merge and centralize IT governance. Cisco Systems, Inc. dominates enterprise firewall-integrated IPS deployments across North American hospital networks. Palo Alto Networks, Inc. specializes in cloud-native threat detection for multi-site healthcare systems. Check Point Software Technologies Ltd. extends its position through managed security services tailored to mid-size clinic chains.
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) refers to network security technologies that monitor traffic flows for malicious signatures or behavioral anomalies, typically operating at line speeds exceeding 10 Gbps with deep packet inspection latency under 100 microseconds. These systems serve the primary commercial purpose of blocking or alerting on unauthorized access attempts before data exfiltration or service disruption occurs. Signature-based detection still occupies the largest installed base due to its deterministic false-positive rates, though anomaly-based methods are capturing the fastest expansion as machine learning training pipelines mature for encrypted traffic analysis. Hybrid deployment architectures concentrate margin pools where vendors bundle on-premises appliances with cloud-based telemetry correlation.
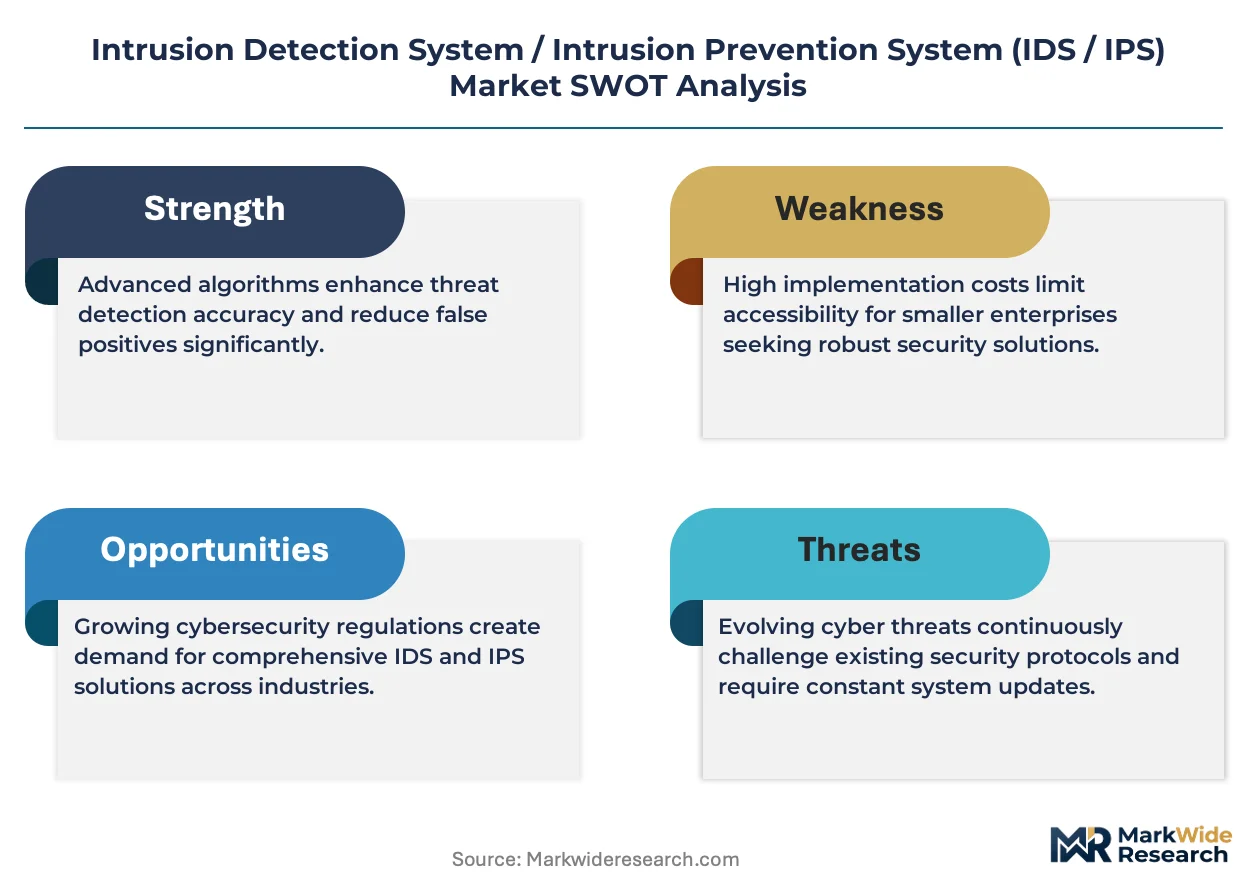
The National Institute of Standards and Technology (NIST) Cybersecurity Framework and the EU Network and Information Security Directive (NIS2) are tightening mandatory incident detection capabilities for critical infrastructure operators across both jurisdictions. HIPAA security rule enforcement in the United States is pushing healthcare providers toward continuous monitoring rather than periodic audit approaches. Stakeholders must weigh the operational overhead of hybrid cloud IPS architectures against the detection coverage gaps that pure cloud or pure on-premises deployments leave in multi-vendor environments.
Market Dynamics
The convergence of NIST Cybersecurity Framework mandates with EU NIS2 directives is compressing deployment timelines for continuous monitoring infrastructure across financial services and healthcare verticals. This regulatory synchronization is forcing vendors to rearchitect product roadmaps around hybrid cloud telemetry correlation rather than on-premises appliance dominance.
Growth Catalysts
- NIS2 Directive:The EU Network and Information Security Directive mandates incident detection capabilities for critical infrastructure operators across energy, transport, and digital services, expanding addressable market scope for managed security providers.
- Real-time payment infrastructure:Financial services institutions are deploying inline IPS at transaction speeds exceeding 10 Gbps to prevent fraud before settlement finality, creating deterministic demand for sub-100-microsecond latency solutions.
- Machine learning pipelines:Anomaly-based detection methods are capturing expansion as encrypted traffic analysis training datasets mature, displacing signature-dependent architectures in multi-site healthcare systems.
Market Restraints
- Silicon supply concentration:Deep packet inspection ASIC fabrication depends on TSMC advanced nodes, creating vulnerability to Taiwan Strait geopolitical friction and foundry allocation constraints.
- False positive management costs:Anomaly-based systems generate alert volumes requiring security operations center analyst scaling, compressing net operating margins for mid-size clinic chains with limited SOC staffing.
- Legacy IPv4 infrastructure:Brownfield industrial control systems in German manufacturing retain decades-old protocol stacks incompatible with modern DPI engines without expensive gateway retrofits.
Strategic Opportunities
- India's critical infrastructure:The country's national cybersecurity regulator is finalizing continuous monitoring mandates for power grid and telecom operators, opening greenfield deployment opportunities ahead of formal compliance deadlines.
- 5G network slicing:Telecom operators are converging IPS functions with subscriber-edge security for enterprise private networks, enabling per-slice threat containment as a differentiated service tier.
- Post-quantum cryptography:NIST's algorithm standardization timeline is creating upgrade cycles for certificate inspection engines, positioning vendors with hardware-accelerated TLS decryption for multi-year replacement waves.
Industry Challenges
- Encrypted traffic blind spots:TLS 1.3 pervasive encryption is collapsing visibility for signature-based engines, forcing costly inline decryption architectures that introduce latency unacceptable to high-frequency trading platforms.
- Multi-vendor integration complexity:Hybrid cloud IPS deployments require API normalization across AWS, Azure, and on-premises firewall ecosystems, extending professional services engagements and delaying revenue recognition.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market |
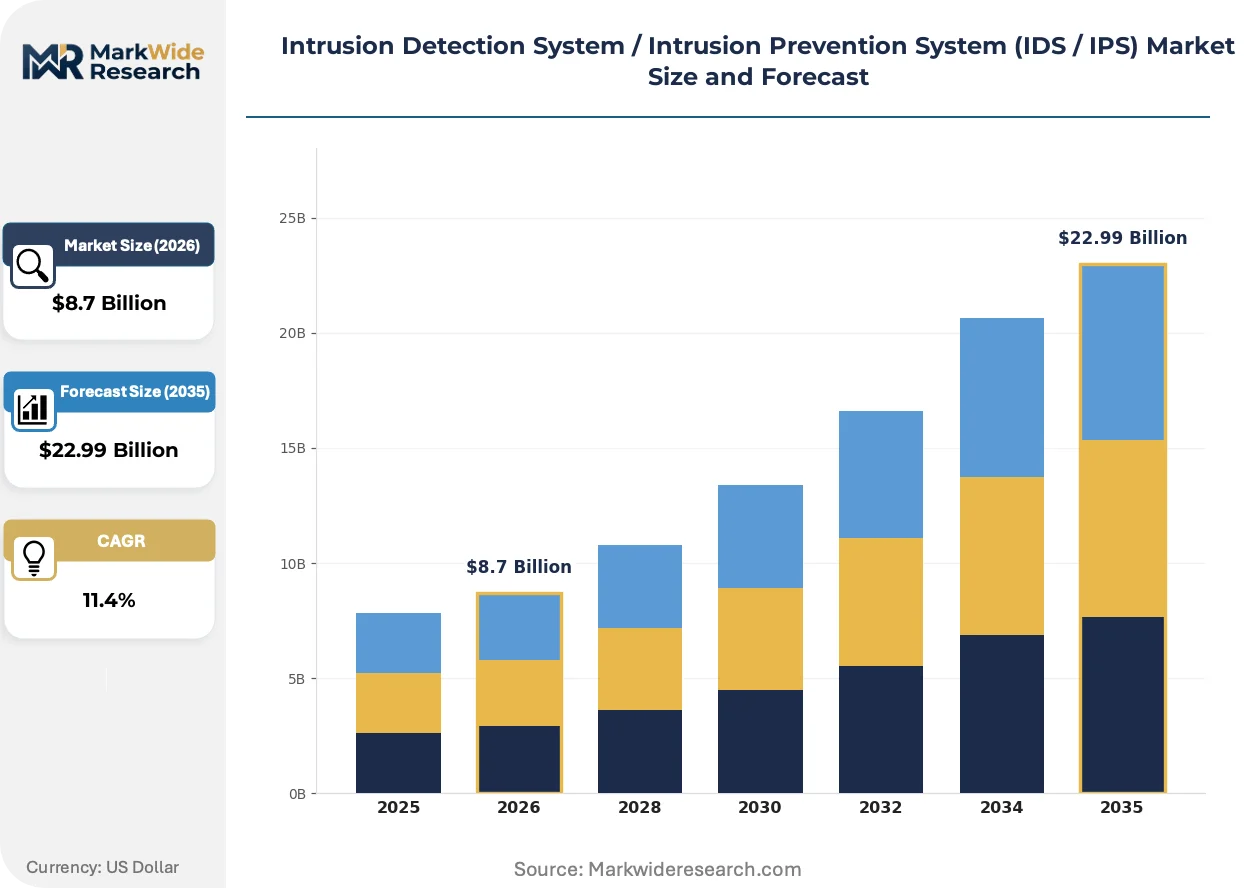
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $22.99 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Signature-Based, Anomaly-Based, Hybrid, Application-Based Deployment: On-Premises, Cloud-Based, Hybrid Cloud, Managed Services End User: Healthcare, Financial Services, Retail, Government Solution: Integrated Solutions, Standalone Solutions, Open-Source Solutions, Proprietary Solutions |
| Companies Covered | Check Point Software Technologies Ltd., International Business Machines Corporation, Cisco Systems, Inc., Trend Micro Incorporated, Huawei Technologies Co., Ltd., Fortinet, Inc., Juniper Networks, Inc., McAfee, LLC, Palo Alto Networks, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market Emerging Trajectories
Machine learning inference at the network edge is absorbing capital allocation previously directed toward centralized security information and event management platforms. This architectural pivot is compressing detection-to-response intervals while fragmenting vendor competitive positioning around telemetry correlation capabilities.
Extended Berkeley Packet Filter is absorbing kernel-level packet processing functions previously executed by proprietary ASIC architectures. Cloud-native security vendors are adopting eBPF for Linux-based workload protection, enabling inspection without hypervisor agent deployment. This shift is absorbing margin from hardware-centric incumbents while accelerating feature velocity for software-defined competitors.
REACH chemical substance restrictions are forcing hardware manufacturers to reformulate printed circuit board flame retardants and capacitor electrolytes. European OEMs are accelerating supplier audits to preempt compliance gaps ahead of 2025 substance evaluation deadlines. German industrial control system vendors are absorbing these certification costs into premium product tiers, widening price spreads against Asian competitors.
Hospital system consolidation is compressing procurement cycles from fragmented department-level purchasing to centralized enterprise security architecture decisions. Multi-site health networks are unbundling managed detection and response services from appliance sales, displacing traditional channel partner margin structures. This concentration is most visible across United States hospital systems executing IT governance centralization post-merger integration.
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market Segmentation
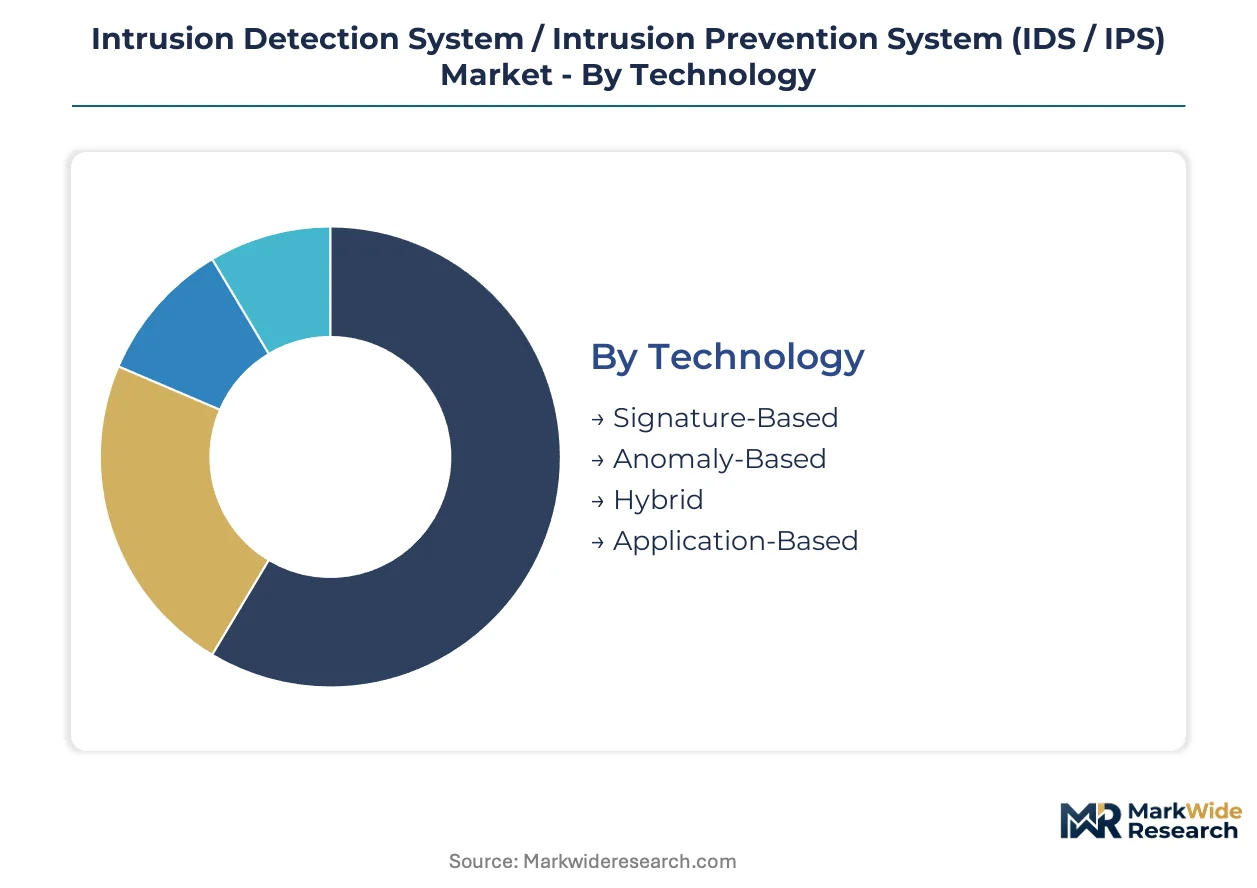
IDS/IPS procurement patterns diverge sharply across technology maturity curves and infrastructure ownership models. Capital allocation priorities shift between deterministic signature engines and probabilistic anomaly systems depending on organizational risk tolerance and security operations maturity.
Technology:
Capital intensity peaks where hardware acceleration meets machine learning inference at line speed.
- Signature-Based:Deterministic pattern matching against known threat databases executes on dedicated ASICs with sub-100-microsecond latency. Financial services institutions in the United States deploy these engines for real-time payment infrastructure protection where false positive rates must stay below 0.001%.
- Anomaly-Based:Behavioral baselines trained on encrypted traffic metadata require GPU clusters for model inference, driving higher upfront infrastructure spend. Multi-site healthcare systems in Germany favor this approach for detecting zero-day exploits in consolidated hospital networks where signature databases lag behind attack evolution.
- Hybrid:Correlates signature alerts with behavioral deviations to reduce analyst workload.
- Application-Based:Protocol-aware inspection targets web application firewalls and API gateways.
Signature-Based systems absorb the bulk of installed capacity; Anomaly-Based is expanding most quickly.
Deployment:
Operational overhead varies dramatically between appliance ownership and telemetry correlation responsibilities.
- On-Premises:Dedicated hardware appliances with deep packet inspection ASICs demand capital expenditure for chassis, power, and cooling infrastructure. German industrial control system operators under EU NIS2 directives retain this model for air-gapped manufacturing environments where cloud connectivity violates operational technology security protocols.
- Cloud-Based:Agentless traffic mirroring and virtual appliance deployment shifts spending to operational expenditure with per-gigabyte inspection pricing. Mid-size clinic chains in the United States adopt this model post-merger to avoid security operations center staffing expansion.
- Hybrid Cloud:Correlates on-premises appliance telemetry with cloud-native threat intelligence feeds.
- Managed Services:Outsources alert triage and incident response to specialized security providers.
On-Premises retains the largest revenue base; Cloud-Based deployment climbs the fastest as healthcare consolidation accelerates.
End User:
Regulatory enforcement intensity determines procurement urgency and solution sophistication tiers.
- Healthcare:HIPAA Security Rule enforcement and hospital system mergers drive continuous monitoring mandates. United States health networks prioritize inline IPS with sub-50-microsecond latency for patient monitoring device protection where service disruption risks clinical outcomes.
- Financial Services:Real-time gross settlement systems and instant payment rails demand deterministic fraud prevention. Institutions across Germany and the United States deploy hybrid architectures combining on-premises appliances for transaction processing with cloud correlation for threat intelligence.
- Retail:PCI-DSS compliance and point-of-sale malware protection shape deployment patterns.
- Government:NIST Cybersecurity Framework mandates and classified network segmentation requirements dominate procurement.
Healthcare captures the steepest spending trajectory; Financial Services maintains the deepest installed base.
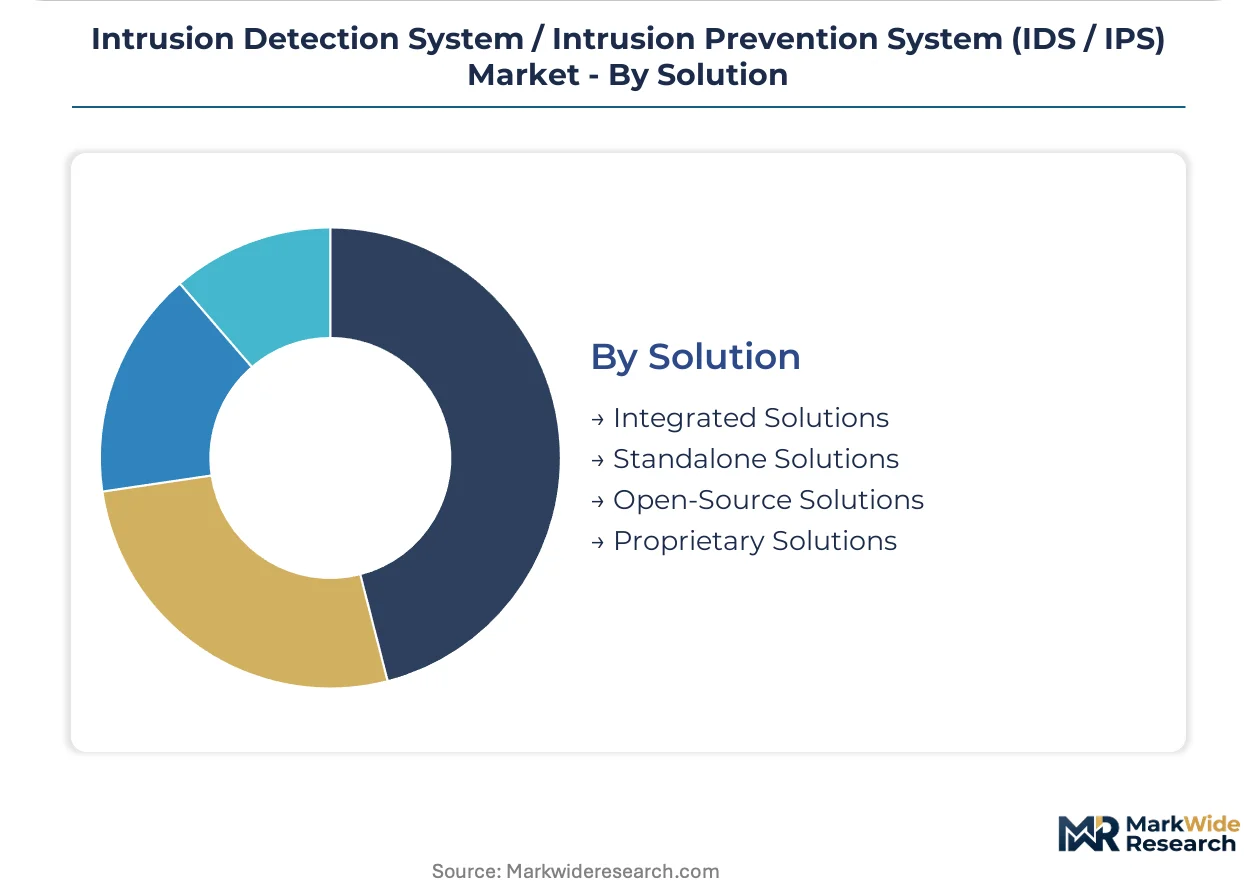
Solution:
Intellectual property control and integration depth separate pricing tiers across ownership models.
- Integrated Solutions:Bundled firewall-IPS platforms with unified policy management reduce multi-vendor integration complexity. North American hospital networks favor this architecture for simplified procurement and single-vendor support accountability.
- Standalone Solutions:Best-of-breed detection engines with open API ecosystems enable custom security stack assembly. German manufacturing operators select these for industrial control system environments requiring protocol-specific parsers unavailable in integrated platforms.
- Open-Source Solutions:Community-maintained detection rules with commercial support subscriptions.
- Proprietary Solutions:Vendor-locked threat intelligence and closed signature databases.
Integrated Solutions dominate enterprise procurement; Standalone Solutions gain share fastest among specialized industrial deployments.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Special economic zones in India and tax-incentive corridors in Germany are concentrating IDS/IPS procurement decisions. Regulatory deadlines in both jurisdictions compress vendor selection timelines. Enterprise buyers in these zones prioritize hybrid cloud architectures with local data residency guarantees.
United States
NIST Cybersecurity Framework mandates drive continuous monitoring procurement across financial services and healthcare verticals. HIPAA enforcement actions against hospital networks accelerate inline IPS deployment for patient monitoring protection. The Dallas-Fort Worth metroplex hosts concentrated data center construction where edge-native threat detection absorbs capital allocation.
Germany
EU NIS2 transposition deadlines force industrial control system operators toward air-gapped appliance architectures. REACH chemical restrictions elevate hardware certification costs for printed circuit board manufacturers. Bavarian automotive suppliers embed IPS functions directly into manufacturing execution systems to satisfy supply chain security audits.
India
The national cybersecurity regulator's draft continuous monitoring mandates for power grid operators open greenfield deployment opportunities. RBI guidelines for payment system operators specify sub-millisecond fraud detection latency requirements. Telangana's Hyderabad Cyberabad district anchors managed security service provider expansion serving Asia-Pacific enterprise clients.
Japan
METI critical infrastructure protection guidelines mandate encrypted traffic inspection capabilities for financial institutions. Post-quantum cryptography migration timelines accelerate hardware replacement cycles for TLS decryption engines. Tokyo's Otemachi financial district concentrates procurement decisions for real-time gross settlement system protection.
United Kingdom
NCSC Cyber Assessment Framework enforcement drives public sector procurement toward certified IPS products. NHS Digital consolidation of hospital network security governance compresses vendor selection to enterprise-scale integrated platforms. London's Canary Wharf fintech cluster demands cloud-native threat detection for instant payment rail protection.
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market Vendor Landscape
Top-tier vendors anchor enterprise firewall-integrated portfolios, while specialized threat intelligence providers occupy adjacent niches. The vendor base stratifies across three functional tiers: hardware-centric incumbents with ASIC fabrication relationships, cloud-native software vendors with eBPF-based inspection, and managed security service providers outsourcing SOC operations. Strategic consolidation centers on telemetry correlation platform acquisition and vertical-specific compliance certification attainment.
Within the integrated platform tier, Cisco Systems, Inc. and Palo Alto Networks, Inc. exemplify divergent architectural philosophies—one rooted in appliance dominance, the other in cloud-native elasticity. Check Point Software Technologies Ltd. occupies a position bridging on-premises heritage with managed service delivery for mid-market clinic chains. These three entities collectively represent the competitive tension between hardware acceleration and software-defined inspection that defines current procurement debates.
| Leading Market Players |
|---|
| Check Point Software Technologies Ltd. |
| International Business Machines Corporation |
| Cisco Systems, Inc. |
| Trend Micro Incorporated |
| Huawei Technologies Co., Ltd. |
| Fortinet, Inc. |
| Juniper Networks, Inc. |
| McAfee, LLC |
| Palo Alto Networks, Inc. |
| Others |
Supply Flow & Price Mechanics
Financial services institutions deploying sub-100-microsecond inline IPS for real-time payment infrastructure command premium pricing tiers that compress margins for mid-size healthcare buyers lacking equivalent procurement leverage. This buyer-archete concentration forces vendors to stratify offerings across performance-certified appliance tiers while absorbing REACH compliance costs into German industrial deliveries.
Pricing Analysis
Short lead-time premiums of 15-25% apply to deep packet inspection ASICs sourced from TSMC advanced nodes facing foundry allocation constraints. The dominant pricing structure runs through three-tier hardware licensing with recurring threat intelligence subscriptions, where NIST Cybersecurity Framework certification grade separates premium chassis from standard appliances. Price differentiation hinges on encrypted traffic inspection throughput and EU NIS2 compliance attestation, with cloud-native virtual appliances eroding on-premises hardware margins. Mid-size clinic chains exhibit highest price sensitivity due to SOC staffing limitations, while German automotive suppliers accept premium tiers for manufacturing execution system integration.
Supply Chain Analysis
Freight cost volatility for specialized cooling infrastructure and chassis assemblies elevates landed costs for air-gapped industrial deployments. Geographic supply concentration centers on Taiwan for DPI ASIC fabrication, China for printed circuit board assembly, and Germany for precision mechanical enclosures. Raw material dependencies encompass advanced silicon wafers, halogen-free flame retardants, and tantalum capacitors. Single-source vulnerability to Taiwan Strait geopolitical friction dominates risk exposure. Distribution runs through authorized security integrators serving hospital networks and direct OEM relationships for industrial control system vendors.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a cost-of-compliance story where EU NIS2 and NIST Cybersecurity Framework mandates erect barrier-to-entry moats favoring certified incumbents with established regulatory relationships.
For Market Incumbents: Deepen telemetry correlation platform investments to defend against eBPF-based cloud-native entrants displacing proprietary ASIC architectures. Prioritize backward integration into threat intelligence data lakes and expand India-based managed security service delivery to capture greenfield critical infrastructure mandates before compliance deadlines compress procurement windows. For New Entrants and Emerging Players: NIS2 in Germany opens a window for air-gapped appliance specialists serving brownfield manufacturing environments where legacy protocol compatibility demands custom parsers unavailable from integrated platform vendors. Target Bavarian automotive supplier clusters with embedded IPS modules for manufacturing execution systems, leveraging post-merger hospital procurement centralization in the United States to displace channel-dependent incumbents with direct cloud-native sales. For Investors and Strategic Acquirers: The window for entry favors cloud-native security vendors with proven eBPF inspection stacks and established healthcare vertical certifications. Acquisition targets should demonstrate machine learning inference pipelines trained on encrypted traffic metadata with deployment traction across multi-site health networks. Monitor NIST post-quantum cryptography standardization announcements as hardware replacement cycle inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifying on-premises appliance telemetry with cloud-native threat intelligence feeds satisfies hybrid cloud procurement mandates from merging hospital systems. |
| Acquisition of Specialist Firm | Absorbing industrial control system protocol parsers addresses air-gapped manufacturing requirements under EU NIS2 directives. |
| Geographic Expansion | Establishing managed security service presence in Telangana's Hyderabad Cyberabad district captures Asia-Pacific enterprise demand. |
| Product Launch | Introducing hardware-accelerated TLS decryption engines positions vendors for NIST post-quantum cryptography upgrade cycles. |
| Strategic Partnership | Aligning with telecom operators on 5G network slicing security enables per-slice threat containment as differentiated enterprise service tier. |
Methodological Framework
Independent corroboration across primary interviews with CISOs at multi-site health networks, security architects at financial services institutions, and procurement leads at German industrial control system operators underwrites the qualitative findings. Secondary validation drew from NIST cybersecurity framework documentation, EU NIS2 transposition filings, SEC 10-K disclosures from network security vendors, and hospital system merger integration reports. Bottom-up deployment sizing across signature-based, anomaly-based, and hybrid technology tiers triangulates against top-down addressable market estimates from regulatory mandate scope.
Rate-of-change decomposition across the projection horizon isolates technology transition effects from pure demand expansion, modeling segmentation dimensions spanning deployment architecture, detection methodology, end-user vertical, and solution integration depth. CAGRs derive from installed base replacement cycles, greenfield compliance-driven procurement, and encrypted traffic inspection capability upgrades. Forecast inputs incorporate machine learning training pipeline maturation timelines and TSMC foundry capacity allocation patterns for advanced node ASIC production.
The model assumes a particular technology adoption path; alternative pathways for eBPF-based kernel-level inspection displacing proprietary hardware architectures would alter the outlook. Forecasts reflect assumptions regarding regulatory enforcement intensity, supply chain continuity, and buyer consolidation trajectories. Stakeholders should weight assumptions against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Network Encryption Market
Security Software
Global Error Monitoring Software Market
Security Software
Antivirus Software Package Market
Security Software
Europe Video Management System Market
Security Software
Global Privileged Access Management (PAM) Solutions Market
Security Software
Global Security Software in Telecom Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Software Protection Dongle Market
Security Software
US Evidence Management Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Banking Encryption Software Market
Security Software
Certification Authority Market
Security Software
Video Intercom Devices and Equipment Market
Security Software
Europe Smart Doorbell Market
Security Software
Decentralized Identity Software Market
Security Software
United States Consumer Identity and Access Management Market