
 Smart Security in Healthcare Market | 2026-2036
Smart Security in Healthcare Market Size, Share, and Industry Trends Forecast 2026-2036
Smart Security in Healthcare Market Insights
Hospital procurement teams are unwinding legacy reliance on standalone physical security vendors in favor of converged cyber-physical platforms. Cisco Systems dominates enterprise networking infrastructure for healthcare campuses, extending its footprint into integrated threat detection. Palo Alto Networks specializes in zero-trust architectures that segment clinical networks from administrative systems. Fortinet anchors mid-market hospital chains with consolidated firewall and IoT security appliances.
Smart security in healthcare encompasses biometric authentication, RFID tracking, networked surveillance, and cloud-native threat intelligence orchestrated through unified command platforms. These systems typically operate at sub-100-millisecond latency for real-time access decisions while maintaining AES-256 encryption for patient data streams, serving the dual purpose of protecting physical premises and ensuring continuity of clinical operations. Cloud-based solutions represent the fastest-expanding technology segment as hospitals migrate security operations centers off-site to reduce capital expenditure and tap elastic compute for AI-driven anomaly detection. Access control systems remain the largest product category by installed base, though intrusion detection platforms command premium pricing in research laboratories and pharmaceutical storage facilities where regulatory audit trails are mandatory.
HIPAA security rules enforced by the Office for Civil Rights mandate risk assessments that directly elevate spending on audit-ready access logging and encryption. The FDA's post-market cybersecurity guidance requires medical device manufacturers to disclose vulnerabilities, which cascades into hospital procurement clauses demanding vendor security certifications. Stakeholders must weigh the trade-off between cloud agility and on-premises data sovereignty as state-level patient privacy laws diverge from federal frameworks.
Market Dynamics
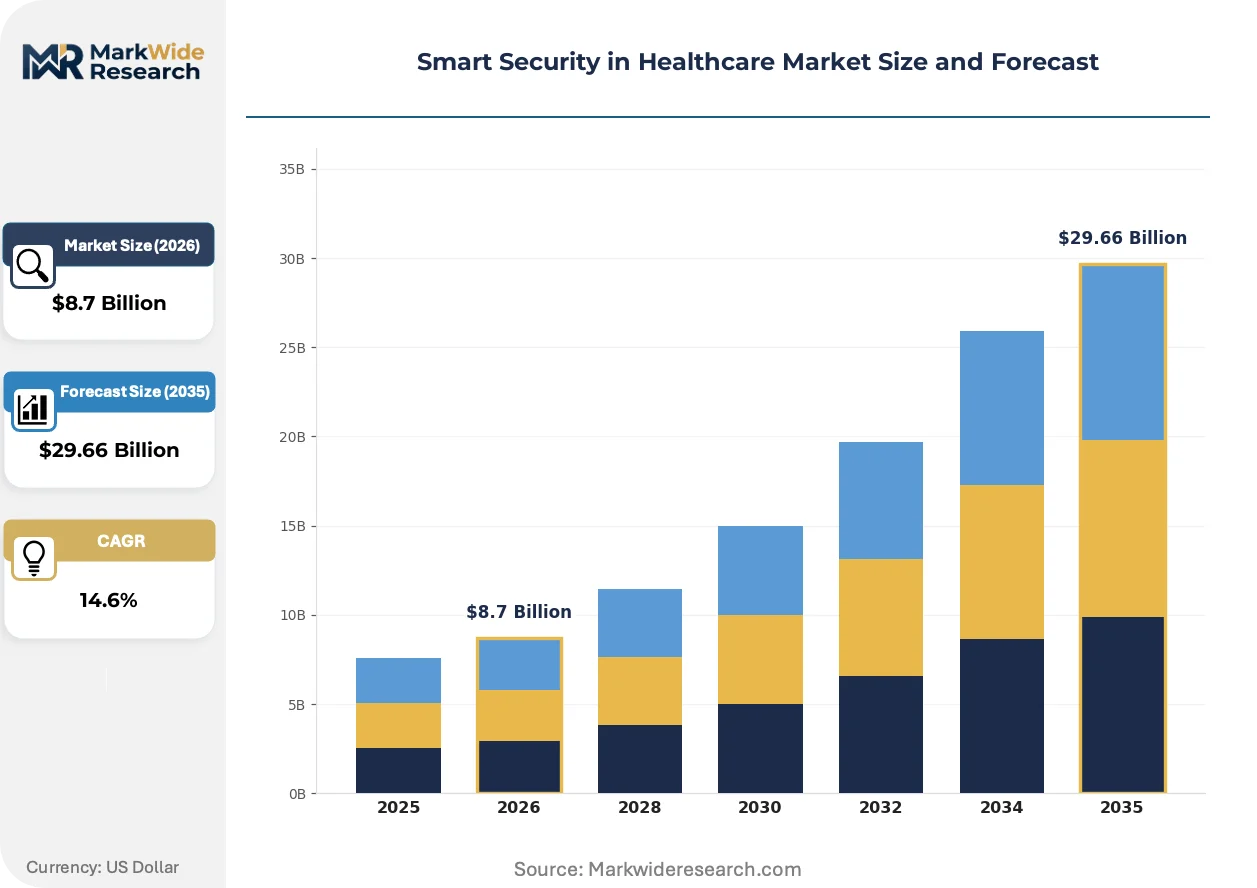
Hospital security procurement is converging cyber-physical systems under unified command platforms, driven by HIPAA audit mandates and FDA medical device cybersecurity guidance that now flow through to vendor contracts and insurance premiums.
Growth Catalysts
- HIPAA Security Rule enforcement:The Office for Civil Rights mandates risk assessments that compel hospitals to deploy audit-ready access logging and encryption, directly expanding security budgets for compliance infrastructure.
- Biometric authentication maturation:Fingerprint and iris recognition systems now operate at sub-100-millisecond latency, enabling real-time clinical access decisions without disrupting emergency workflows.
- Cloud-native SOC migration:Hospital networks are offloading security operations centers to managed services, reducing capital expenditure while accessing elastic compute for AI-driven threat detection.
Market Restraints
- Silicon supply concentration:Specialized security chipsets for biometric sensors and encryption modules depend on concentrated East Asian foundry capacity, exposing procurement timelines to geopolitical disruption.
- Interoperability friction:Legacy physical access control systems from disparate vendors resist API integration with modern cyber-physical platforms, forcing expensive rip-and-replace cycles.
- Skill scarcity in clinical cybersecurity:The shortage of professionals credentialed in both HIPAA compliance and industrial control system security constrains deployment velocity for integrated architectures.
Strategic Opportunities
- Rural hospital security gaps:Community health systems and critical access hospitals remain underpenetrated by converged platforms, presenting white space for consolidated appliance vendors with simplified deployment models.
- Pharmaceutical cold chain tracking:RFID and environmental sensor convergence for temperature-controlled medication storage opens adjacent revenue streams beyond traditional premises security.
- State-level privacy law divergence:California's CMIA and emerging patient data sovereignty statutes create demand for regionally configurable encryption and data residency controls that federal frameworks do not address.
Industry Challenges
- Medical device patching complexity:FDA post-market cybersecurity guidance requires vulnerability disclosure, yet embedded devices in active clinical use cannot tolerate downtime for security updates without jeopardizing patient care.
- Cross-functional coordination:Security deployments must align with Joint Commission accreditation cycles, IT capital planning horizons, and facilities maintenance windows, compressing implementation timelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Smart Security in Healthcare Market |
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $29.66 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Access Control Systems, Surveillance Cameras, Intrusion Detection, Alarm Systems Technology: Biometric Sensors, RFID, IoT Devices, Cloud-Based Solutions End User: Hospitals, Clinics, Laboratories, Long-Term Care Facilities Installation: On-Premises, Remote Monitoring, Hybrid Solutions, Integrated Systems |
| Companies Covered | Cisco Systems, IBM Corporation, Check Point Software Technologies, Palo Alto Networks, FireEye, General Electric Company, Honeywell International, McAfee, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Smart Security in Healthcare Market Trends and Innovations
Healthcare security architecture is pivoting from perimeter defense to zero-trust segmentation, with artificial intelligence now embedded at the edge of clinical networks for real-time anomaly detection without cloud latency.
Edge-deployed machine learning inference engines for behavioral biometrics and network traffic analysis are fragmenting the traditional centralized SOC model. Community hospitals and outpatient surgical centers are adopting these appliances fastest, drawn by subscription pricing that converts capital expenditure to operational budgets. Vendor consolidation pressure is intensifying as point-solution providers lose procurement battles to platforms offering unified physical-cyber dashboards.
FDA's 2023 post-market cybersecurity guidance for medical devices mandates coordinated vulnerability disclosure between manufacturers and hospital operators. Device makers must now document security update capabilities in 510(k) submissions, which cascades into procurement contract language requiring vendor security certifications. Research hospitals and academic medical centers with extensive device fleets face the steepest compliance burden, driving demand for automated asset inventory and risk scoring platforms.
Hospital buying committees are consolidating vendor relationships to reduce integration complexity and liability exposure. Integrated delivery networks now issue single-source contracts for physical access, network security, and IoT device monitoring, displacing the fragmented procurement patterns of the 2010s. This concentration is most pronounced in the United States, where health system mergers have created super-regional entities with centralized capital allocation authority.
Smart Security in Healthcare Market Segmentation
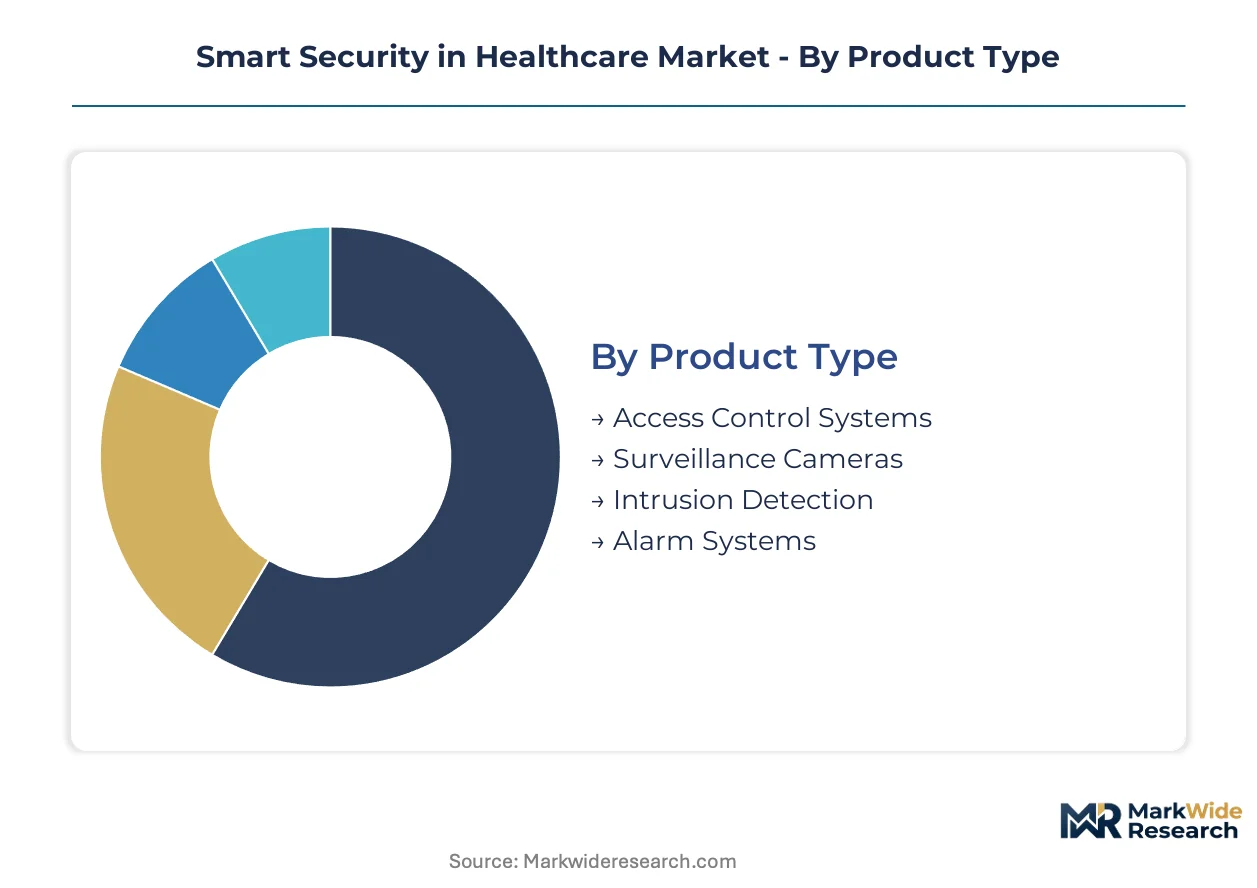
Segmentation in healthcare security reveals distinct procurement patterns across product categories, technology platforms, and deployment models. Hospital systems prioritize integrated architectures that unify physical access with network threat detection under single vendor relationships.
Product Type:
Access control systems concentrate procurement among domestic hospital networks seeking HIPAA-compliant audit trails. Surveillance camera deployments split between on-campus physical security and cloud-native remote monitoring for multi-site health systems.
- Access Control Systems:Biometric readers and card-based entry points enforce role-based permissions across clinical and administrative zones. Major hospital systems in the United States standardize on platforms with sub-100-millisecond authentication latency to prevent workflow disruption in emergency departments.
- Surveillance Cameras:IP camera networks with edge analytics detect unauthorized access in pharmaceutical storage and pediatric units. Cloud-connected models gain traction among outpatient surgical centers seeking reduced on-site infrastructure.
- Intrusion Detection:Perimeter sensors and motion analytics protect research laboratories with temperature-controlled assets.
- Alarm Systems:Integrated duress buttons and mass notification platforms serve psychiatric facilities and emergency departments.
Access Control Systems commands the established base. The steepest expansion runs through Surveillance Cameras.
Technology:
Technology selection tracks the tension between on-premises data sovereignty and cloud agility. Biometric sensors and RFID dominate patient-facing applications, while IoT and cloud platforms expand fastest in mid-market hospital chains.
- Biometric Sensors:Fingerprint and iris recognition modules operate at clinical-grade accuracy thresholds required for FDA-regulated device environments. Academic medical centers deploy these for secure access to operating suites and research specimen repositories.
- Cloud-Based Solutions:Elastic compute for AI-driven anomaly detection converts capital expenditure to subscription budgets. Community hospitals adopt these fastest to bypass dedicated security operations center staffing.
- RFID:Asset tags and personnel badges enable real-time location tracking for high-value medical equipment.
- IoT Devices:Networked environmental sensors monitor pharmaceutical cold chain integrity in hospital pharmacies.
Biometric Sensors anchors current procurement volumes. Cloud-Based Solutions expands most quickly as managed security services penetrate smaller health systems.
End User:
End user segmentation reflects divergent compliance burdens and threat surfaces. Hospitals face the most complex cyber-physical integration requirements, while long-term care facilities lag in security modernization.
- Hospitals:Integrated delivery networks demand unified command platforms spanning physical access, network segmentation, and medical device monitoring. These installations must align with Joint Commission accreditation cycles and facilities maintenance windows.
- Long-Term Care Facilities:Nursing homes and assisted living centers present underpenetrated demand for simplified appliance-based security. Medicaid reimbursement pressures constrain capital budgets, favoring subscription-priced solutions.
- Clinics:Outpatient facilities prioritize compact access control with cloud dashboard management.
- Laboratories:Research and diagnostic labs require audit-ready access logging for regulatory inspection.
Hospitals commands the established base. The steepest expansion runs through Long-Term Care Facilities.
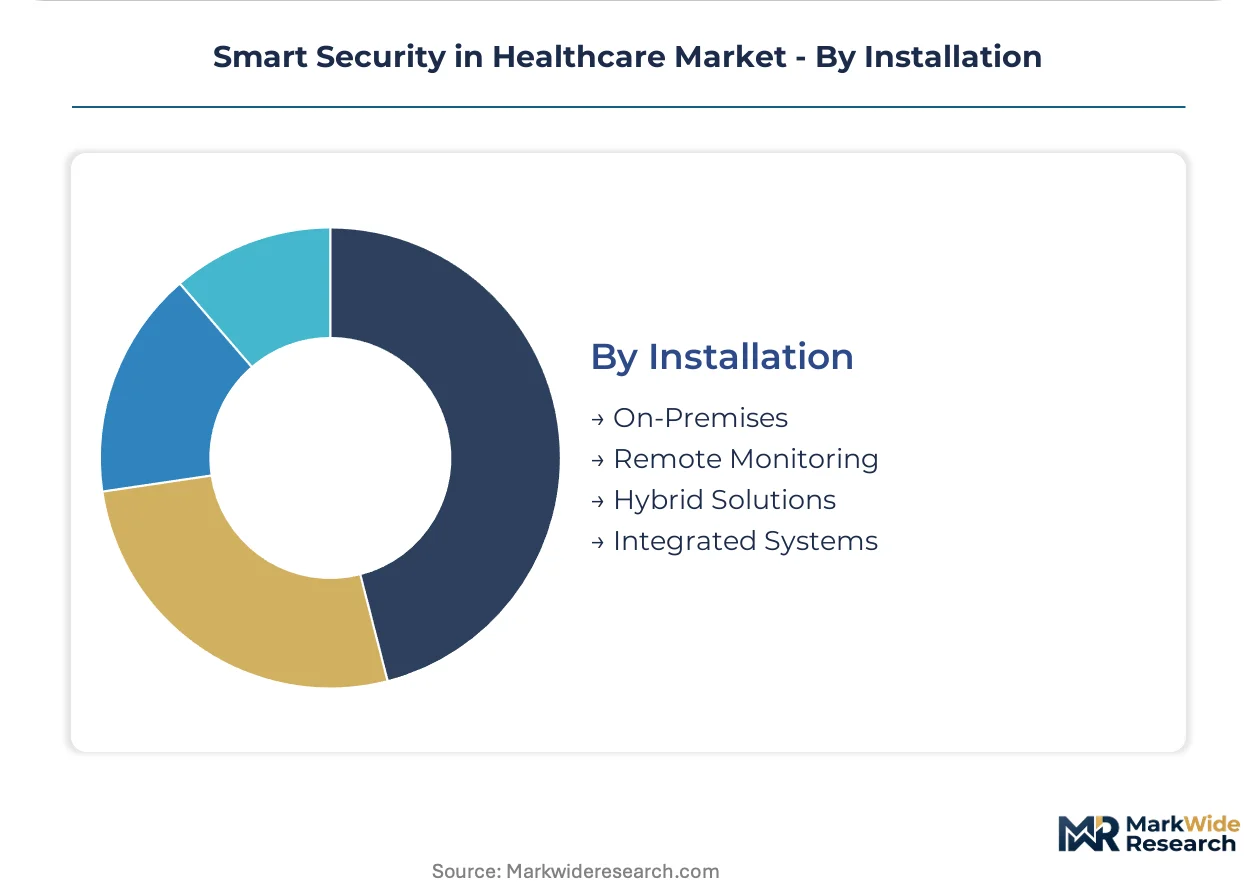
Installation:
Installation mode selection hinges on data residency requirements and internal IT capability. Hybrid architectures predominate as hospitals retain sensitive patient data on-premises while offloading analytics to cloud infrastructure.
- Hybrid Solutions:Split architectures keep authentication logs and encryption keys local while leveraging cloud compute for threat correlation. State-level patient privacy laws in California and emerging jurisdictions drive this configuration.
- Integrated Systems:Single-vendor cyber-physical platforms reduce liability exposure and procurement complexity. Super-regional health systems in the United States consolidate contracts around these offerings.
- On-Premises:Fully localized deployments persist in Veterans Affairs facilities and defense-affiliated medical centers.
- Remote Monitoring:Outsourced security operations center services appeal to critical access hospitals with limited cybersecurity staffing.
Integrated Systems commands the established base. The steepest expansion runs through Hybrid Solutions.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli cybersecurity firms export threat-intelligence platforms to hospital networks across Germany, the United Kingdom, and the United States, establishing a dominant trade corridor in clinical network defense.
United States
Hospital procurement teams at HCA Healthcare and Kaiser Permanente deploy converged cyber-physical platforms under single-vendor contracts. HIPAA enforcement by the Office for Civil Rights mandates audit-ready access logging, accelerating consolidation around integrated delivery networks. The Boston-Cambridge cluster anchors medical device cybersecurity R&D, with Massachusetts General Brigham requiring vendor security certifications in all procurement clauses.
Germany
University hospitals in Baden-Württemberg and Bavaria adopt zero-trust architectures for clinical network segmentation. The EU Medical Device Regulation (MDR) imposes post-market surveillance obligations that cascade into hospital procurement specifications. The Rhine-Main region around Frankfurt concentrates health IT security consulting, with Fraunhofer institutes testing biometric authentication latency for emergency department workflows.
United Kingdom
NHS England's cybersecurity improvement program drives procurement of cloud-native security operations centers across integrated care systems. GDPR compliance intersects with NHS Digital's data security standards, requiring regionally configurable encryption. The London-Oxford-Cambridge golden triangle houses medical AI security startups, with Guy's and St Thomas' NHS Foundation Trust piloting edge-deployed anomaly detection.
Japan
Metropolitan hospital networks in Tokyo and Osaka migrate physical access control to biometric platforms with JIS-compliant encryption modules. METI's cybersecurity guidelines for critical infrastructure extend to university hospitals, mandating network segmentation for medical devices. The Kansai region's medical device manufacturers coordinate vulnerability disclosure with hospital operators under PMDA-aligned protocols.
Australia
State health departments in New South Wales and Victoria consolidate security procurement for multi-site hospital networks. The Therapeutic Goods Administration (TGA) medical device cybersecurity guidance requires hospitals to document security update capabilities. Melbourne's biomedical precinct clusters health IT security vendors serving the Asia-Pacific export market.
Smart Security in Healthcare Market Competitive Landscape
Player mix skews toward diversified technology conglomerates with healthcare vertical specialization, creating a tiered structure where enterprise networking vendors hold procurement leverage over point-solution providers. Network infrastructure specialists occupy the premium tier, while cybersecurity pure-plays compete on zero-trust segmentation capabilities. Consolidation pressure intensifies as integrated delivery networks issue single-source contracts spanning physical access, network security, and IoT monitoring. Dominant competitive moves include portfolio diversification into converged cyber-physical platforms and strategic partnerships with medical device manufacturers to embed security at the design stage.
Within the enterprise networking tier, Cisco Systems and Palo Alto Networks exemplify platform consolidation strategies, with the former anchoring campus infrastructure deployments and the latter representing zero-trust architecture specialization. Fortinet occupies a position among consolidated appliance vendors serving mid-market hospital chains with simplified deployment models. These three companies collectively represent the competitive archetypes now displacing fragmented point-solution procurement patterns.
| Leading Market Players |
|---|
| Cisco Systems |
| IBM Corporation |
| Check Point Software Technologies |
| Palo Alto Networks |
| FireEye |
| General Electric Company |
| Honeywell International |
| McAfee |
| Fortinet |
| Others |
Pricing and Supply Chain Analysis
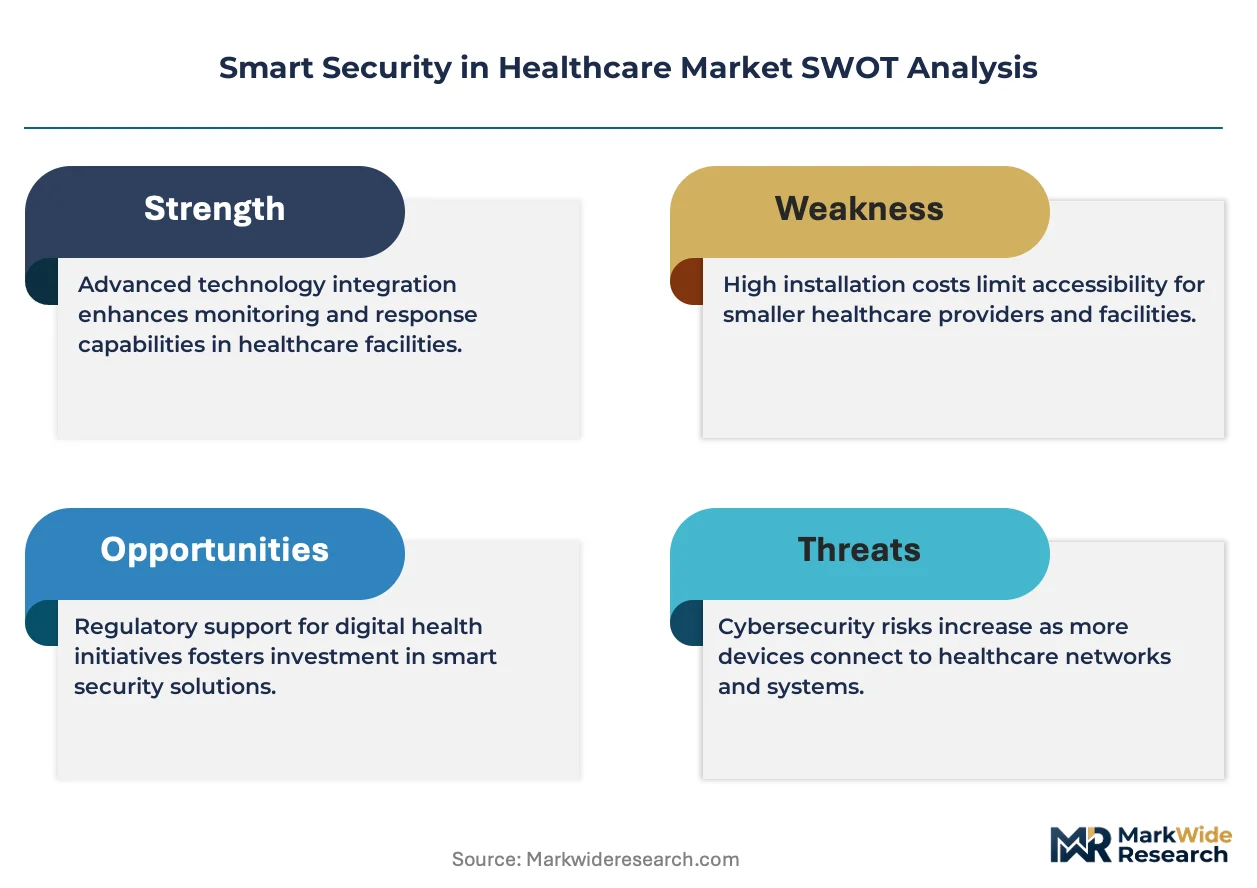
FDA cybersecurity guidance for medical devices gates both vendor qualification and price differentiation simultaneously, as hospitals now demand security certifications that segment procurement tiers while concentrating purchasing power among certified suppliers.
Pricing Analysis
Prior-generation on-premises access control systems trade at 40-60% discounts to cloud-native platforms with AI-driven analytics, while next-generation edge-deployed biometric appliances command premiums for sub-100-millisecond latency performance. Subscription SaaS pricing dominates mid-market hospital chains seeking operational budget conversion, with HIPAA audit-ready encryption tiers separating premium from standard offerings. Cost compression in legacy hardware is intensifying because cloud migration accelerates depreciation cycles. Community hospitals exhibit highest price sensitivity due to Medicaid reimbursement constraints, while academic medical centers prioritize certification grade over unit cost.
Supply Chain Analysis
Taiwan and South Korea anchor specialized security chipset fabrication for biometric sensors and encryption modules, while Japan supplies JIS-compliant hardware for metropolitan hospital networks in East Asia. Foundry capacity for AES-256 encryption processors draws from concentrated East Asian manufacturing clusters, with raw silicon and rare earth magnet inputs feeding sensor assembly. Single-source vulnerability in advanced node semiconductor production exposes procurement timelines to geopolitical disruption. Distribution runs through authorized healthcare technology distributors with FDA compliance documentation capabilities, bypassing general IT channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Smart security in healthcare sits in early-cycle expansion as HIPAA enforcement and FDA medical device cybersecurity guidance create mandatory upgrade tailwinds across hospital networks previously reliant on fragmented point solutions.
For Market Incumbents: Compound platform consolidation momentum by acquiring biometric sensor specialists with FDA 510(k) pathways already cleared, while deepening backward integration into encryption module production to defend margins against foundry cost volatility. Prioritize zero-trust architecture R&D investments as emerging cloud-native entrants threaten appliance-based revenue streams. For New Entrants and Emerging Players: Differentiate on pharmaceutical cold chain convergence, combining RFID asset tracking with environmental monitoring for temperature-controlled medication storage—a white space where legacy physical security vendors lack domain expertise. Target rural critical access hospitals with subscription-priced managed security services, bypassing capital-intensive SOC buildouts that constrain community health system adoption. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting downward across cloud-native security operations center services as elastic compute converts fixed infrastructure to variable cost structures. Long-term viability favors platforms with unified cyber-physical dashboards over point-solution vendors facing procurement exclusion. Watch hospital system merger velocity as the signal indicating centralized capital allocation authority shifts that accelerate single-source contract concentration.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Certification | Palo Alto Networks' segmentation capabilities address FDA medical device network isolation mandates. |
| Biometric Sensor Acquisition | Cisco Systems' fingerprint and iris recognition modules achieve sub-100-millisecond clinical access latency. |
| Cloud-Native SOC Partnership | Fortinet's managed services convert hospital capital expenditure to subscription budgets for mid-market chains. |
| Medical Device Security Integration | GE Healthcare embeds vulnerability disclosure protocols into 510(k) submissions per FDA guidance. |
| State Privacy Law Compliance Module | Honeywell's regionally configurable encryption addresses California CMIA divergences from federal HIPAA frameworks. |
Research Methodology
Cross-validation between hospital procurement database analysis and FDA cybersecurity guidance documentation anchors the qualitative findings in this study. Primary interviews with hospital purchasing committee chairs, biomedical engineers, GPO contracts managers, and clinical cybersecurity officers combined with secondary validation from CMS Medicare reimbursement data, hospital capital expenditure filings, and medical device 510(k) submission records. Bottom-up vendor revenue triangulation against top-down health system security budget allocations ensures segmentation integrity.
Sensitivity analysis across deployment model, organization size, and regional regulatory cluster dimensions informs the analytical framework over the projection horizon. CAGRs derive from modeled adoption curves for cloud-native versus on-premises architectures, with inputs including hospital merger velocity, HIPAA audit enforcement intensity, and medical device fleet cybersecurity maturity scores. Segmentation by product type, technology platform, end user, and installation mode captures procurement pattern variation.
The analysis sits within stated boundaries; outcomes outside sustained HIPAA enforcement and FDA guidance implementation would require recalibration. Forecasts reflect assumptions regarding cloud migration pace and biometric sensor cost curves, with revision triggers including geopolitical semiconductor supply disruption or state-level patient privacy law fragmentation. Recalibration cycles align with material shifts in hospital system consolidation patterns and medical device cybersecurity incident frequency.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Global Intrusion Detection System Market
Security and Surveillance
Europe Security Screening Market
Security and Surveillance
Global Security As a Service Market
Security and Surveillance
Europe Security Testing Market
Security and Surveillance
Europe Security Services Market
Security and Surveillance
Residential Security Market
Security and Surveillance
Seaport Security Management Market
Security and Surveillance
Explosive Trace Detection Market
Security and Surveillance
Explosive Vapour Detector Market
Security and Surveillance
Night Vision Binoculars Market
Security and Surveillance
Radar Security Market
Security and Surveillance
Air Cargo Security and Screening Systems Market
Security and Surveillance
Air Cargo Screening Systems Market
Security and Surveillance
Europe Baggage and Parcel Screening Market
Security and Surveillance
Signal Jamming Systems Market
Security and Surveillance
Electronic Alarms Market