
 Global Security As a Service Market | 2026-2036
Global Security As a Service Market Size, Share, and Industry Trends Forecast 2026-2036
Global Security As a Service Market Foresight
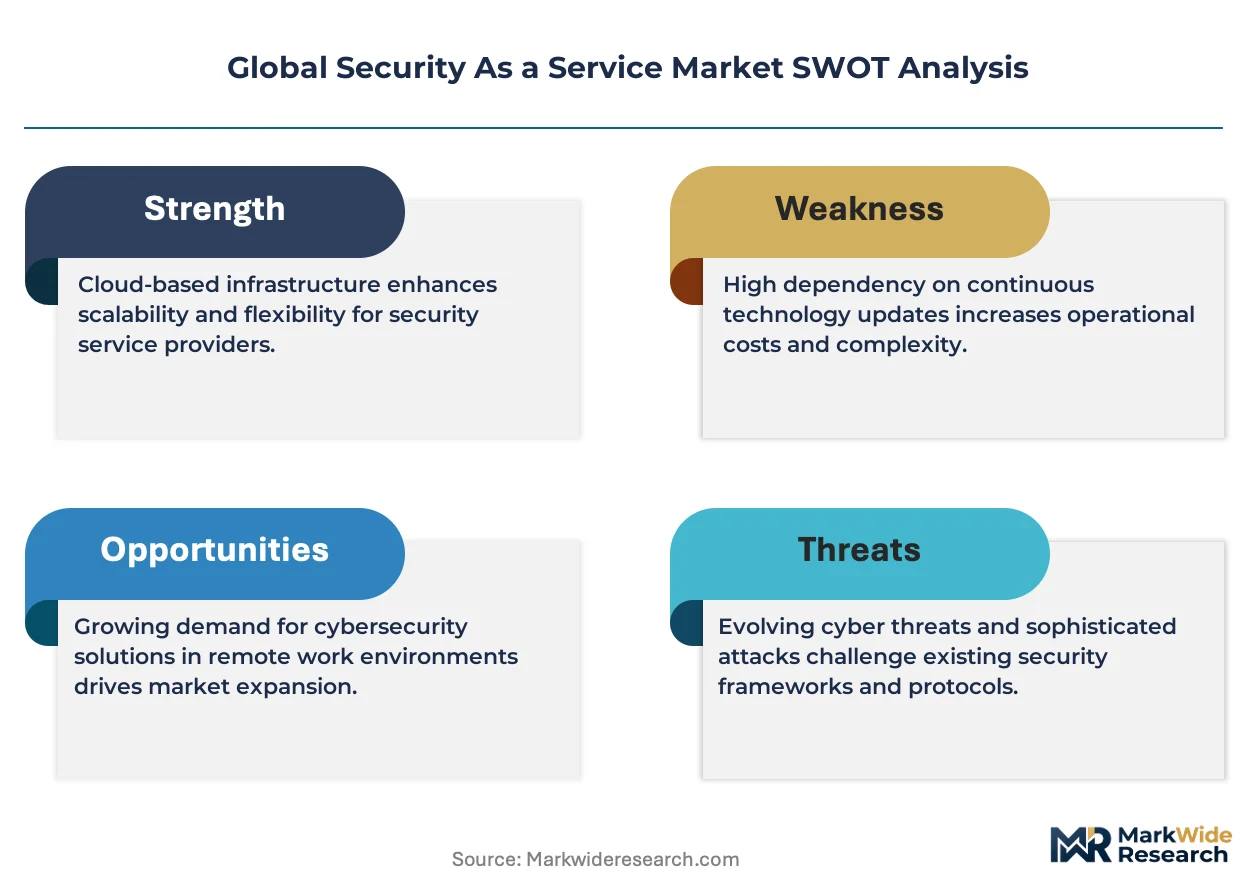
Mid-market enterprises are redrawing demand patterns for cloud-delivered security platforms, displacing legacy on-premise spending by large financial institutions. IBM leverages its managed detection portfolio to anchor enterprise accounts across North America and Europe. Microsoft competes through native integration of identity management with Azure cloud infrastructure. Zscaler specializes in zero-trust network access, dominating remote workforce security deployments.
Security as a Service encompasses cloud-hosted cybersecurity functions delivered through subscription models, typically integrating threat intelligence feeds, automated incident response orchestration, and continuous vulnerability scanning across distributed endpoints. The architecture eliminates capital expenditure on hardware appliances while enabling real-time policy updates against evolving attack vectors. Cloud-based deployment leads solution uptake among organizations lacking internal security operations centers, while managed detection services capture expanding margin pools as labor shortages persist. Identity management retains structural importance due to credential-based attack frequency, though incident response is accelerating fastest as breach costs escalate.
FDA oversight of medical device cybersecurity, EU NIS2 Directive requirements for critical infrastructure operators, and Japan's METI guidelines for supply chain data protection collectively elevate compliance-driven procurement across the analysis window. These frameworks mandate documented incident response capabilities and third-party risk assessments, directly expanding addressable demand for subscription security services. Stakeholders must monitor divergence between regional certification standards when architecting multi-tenant platform roadmaps.
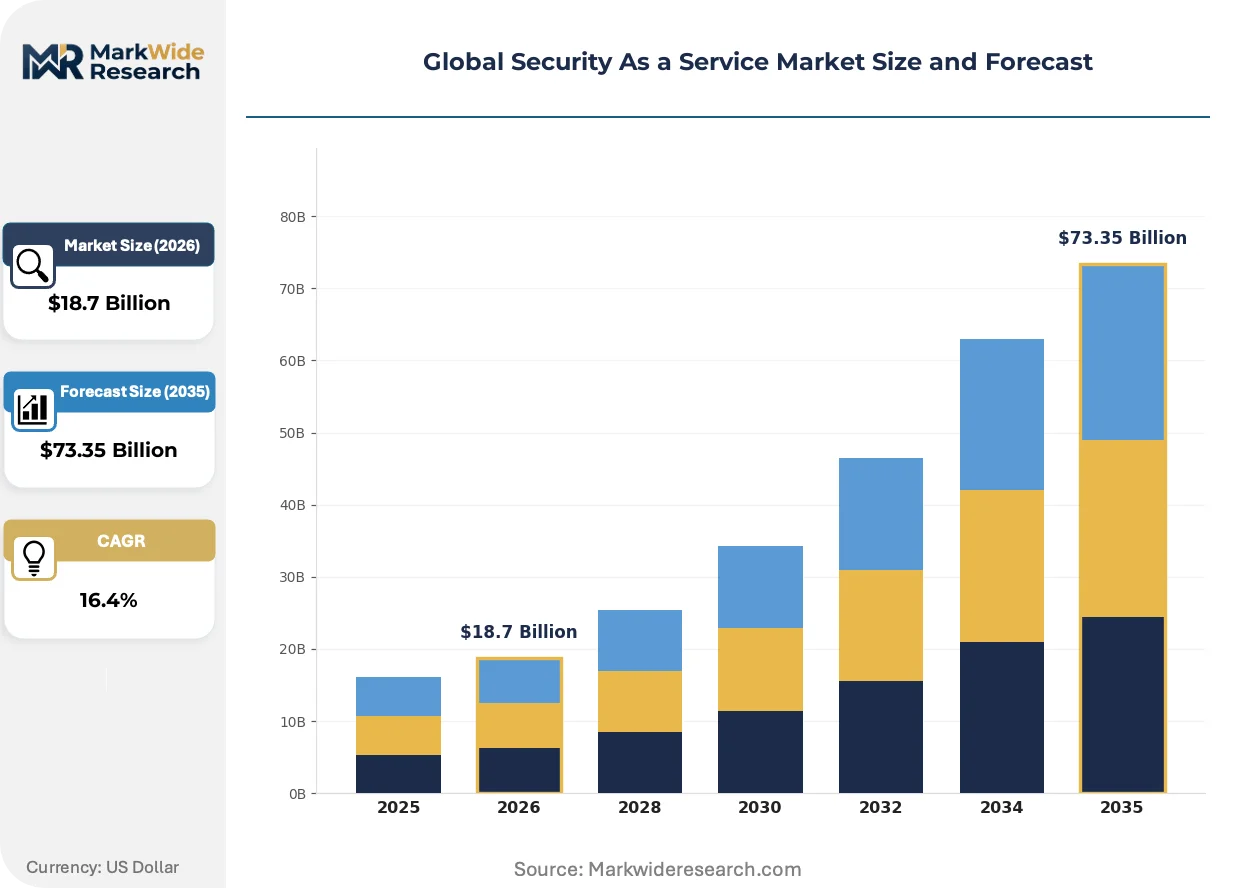
Market Dynamics
Cloud-delivered security architectures are compressing traditional hardware procurement cycles as mid-market enterprises bypass capital-intensive appliance deployments. The EU AI Act and NIS2 Directive are forcing documented incident response capabilities into standard procurement requirements.
Growth Catalysts
- EU NIS2 Directive:Mandates continuous vulnerability scanning and third-party risk assessments for critical infrastructure operators across member states, expanding subscription security demand.
- Remote workforce permanence:Distributed endpoint architectures require zero-trust network access deployments that legacy perimeter defenses cannot satisfy.
- Japan:METI supply chain data protection guidelines are elevating managed detection services procurement among manufacturing exporters.
Market Restraints
- Skilled analyst scarcity:Labor shortages in security operations centers inflate managed detection service delivery costs beyond mid-market budget thresholds.
- Multi-cloud fragmentation:Inconsistent API architectures across hyperscaler platforms complicate unified policy orchestration and increase integration overhead.
- Legacy appliance stranded costs:Sunk investments in on-premise hardware delay cloud migration timelines for established financial institutions.
Strategic Opportunities
- India:Underpenetrated mid-market manufacturing and IT services sectors lack internal security operations centers, creating greenfield demand for cloud-hosted platforms.
- Medical device cybersecurity:FDA oversight requirements for connected healthcare equipment are opening specialized compliance-driven service tiers.
- AI-augmented threat hunting:Convergence of machine learning with automated incident response orchestration enables predictive rather than reactive security postures.
Industry Challenges
- SOC analyst talent pipeline:Certification requirements for threat intelligence interpretation outpace vocational training program output in Germany, Japan, and the United States.
- Legacy identity system integration:Directory service migration complexity extends deployment timelines and elevates professional services dependency for enterprise accounts.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Security As a Service Market |
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $73.35 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Cloud-Based, Hybrid, On-Premise, Virtual Private Network Solution Type: Identity Management, Threat Intelligence, Data Loss Prevention, Incident Response End User: Government Agencies, Telecommunication Providers, Educational Institutions, Financial Services Service Model: Managed Detection, Vulnerability Management, Risk Assessment, Compliance Management |
| Companies Covered | IBM, Microsoft, Cisco Systems, Trend Micro, Zscaler, Fortinet, McAfee, Sophos, Barracuda Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Security As a Service Market Shifts & Advancements
Security delivery models are pivoting from perimeter defense to identity-centric architectures as credential-based attacks dominate breach vectors. Platform consolidation and native cloud integration are compressing vendor diversity in enterprise procurement.
Zero-trust network access is supplanting traditional VPN appliances for distributed workforce connectivity. Mid-market enterprises are adopting cloud-native remote access solutions within twelve-to-eighteen-month procurement cycles. This shift is compressing hardware firewall refresh timelines and redirecting capital toward subscription identity verification services.
The EU AI Act's risk-classification framework for automated decision-making systems is mandating algorithmic transparency documentation. Security vendors must now embed explainable AI modules into threat detection pipelines to serve regulated European clients. Financial services and healthcare verticals are prioritizing vendors with pre-certified compliance architectures.
Consumption-based licensing is displacing seat-count pricing for identity management platforms. Enterprise buyers in Germany and the United States are negotiating usage-tiered contracts that scale with active authentication events rather than named users. This model reduces overprovisioning waste but requires real-time metering infrastructure that smaller vendors struggle to operationalize.
Global Security As a Service Market Segmentation
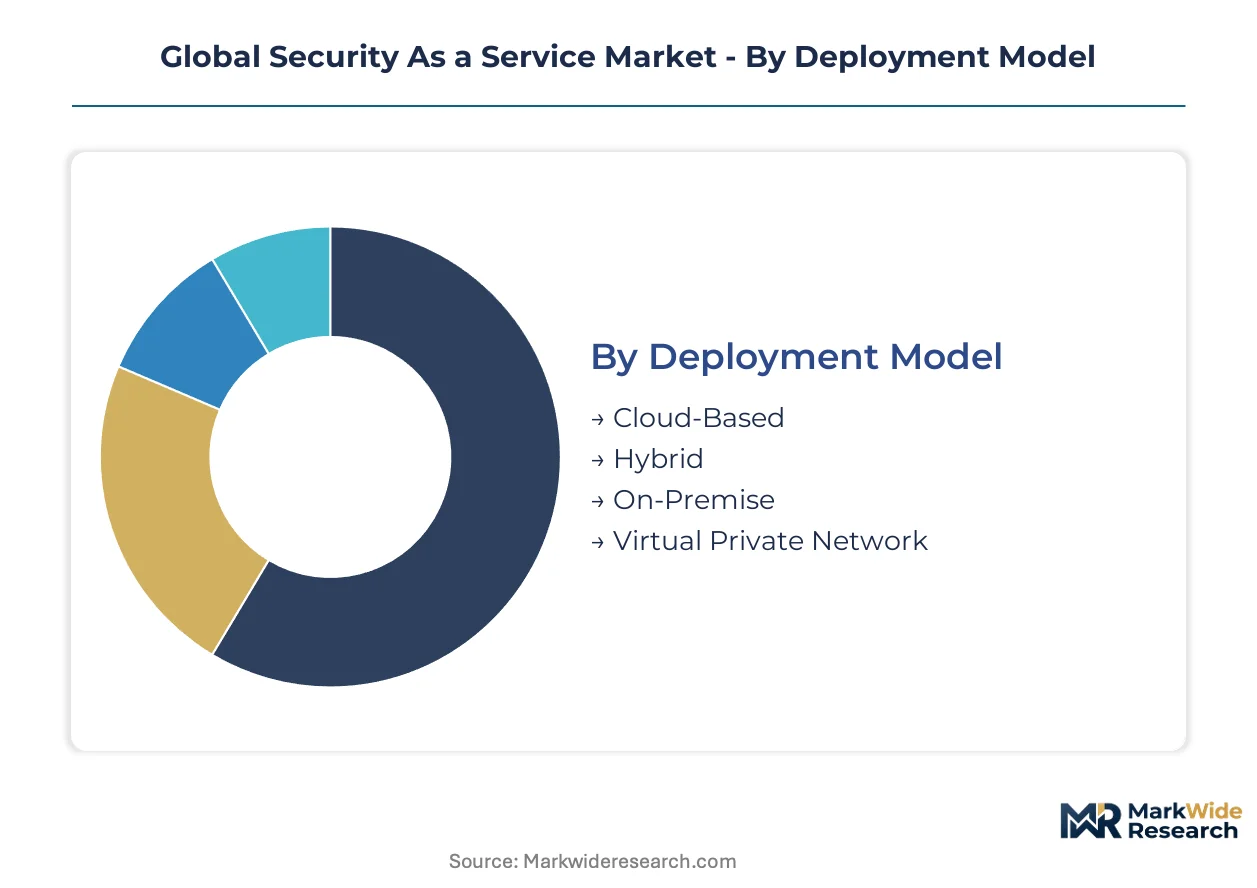
Security as a Service architectures fragment across deployment topologies, solution functions, and procurement models. Each segmentation axis reveals distinct margin concentration patterns and competitive positioning strategies for vendors architecting multi-tenant platforms.
Deployment Model:
Margin pools concentrate in subscription cloud platforms that eliminate capital expenditure friction for mid-market buyers.
- Cloud-Based:Fully hosted security stacks delivered through browser-accessible dashboards eliminate hardware procurement cycles. Demand concentrates among German and Japanese manufacturing exporters seeking rapid deployment without internal security operations centers. EU NIS2 Directive vulnerability scanning mandates are accelerating procurement.
- Hybrid:Split architectures retain sensitive data processing on-premise while offloading threat intelligence feeds to cloud infrastructure. Financial services institutions in the United States favor this model for regulatory compartmentalization. Legacy appliance stranded costs extend deployment timelines.
- On-Premise:Appliance-based deployments persist in classified government environments with air-gapped network requirements.
- Virtual Private Network:Encrypted tunnel architectures for remote workforce connectivity face displacement from zero-trust alternatives.
Cloud-Based holds installed capacity. Hybrid is rotating up the share rankings.
Solution Type:
Application intensity varies dramatically across credential protection, threat visibility, and breach response functions.
- Identity Management:Multi-factor authentication and privileged access management platforms form the defensive perimeter against credential-based attacks. Financial services and healthcare verticals in Germany and the United States prioritize consumption-based licensing tied to active authentication events. Japan's METI supply chain guidelines elevate procurement.
- Incident Response:Automated orchestration platforms with forensic containment capabilities address escalating breach cost exposure. Demand is climbing fastest among United States healthcare providers facing FDA medical device cybersecurity oversight. SOC analyst scarcity inflates service delivery costs.
- Threat Intelligence:Curated indicator feeds and adversary tracking services inform proactive defense postures.
- Data Loss Prevention:Content inspection and egress monitoring tools protect regulated data categories.
Identity Management anchors current procurement volume. Incident Response is expanding most quickly as breach notification mandates tighten.
End User:
Customer type determines contract structure, with regulated industries accepting premium pricing for compliance documentation.
- Financial Services:Banks and insurers demand pre-certified architectures aligned with SEC disclosure requirements and EU AI Act algorithmic transparency mandates. Germany and United States institutions negotiate usage-tiered contracts reducing overprovisioning waste. Legacy identity system integration complexity extends deployment timelines.
- Government Agencies:Federal and state entities require FedRAMP or equivalent sovereign cloud certifications. United States procurement concentrates on documented incident response capabilities for critical infrastructure protection.
- Telecommunication Providers:Network operators face NIS2 Directive obligations across EU member states.
- Educational Institutions:Universities and school districts represent price-sensitive volume with limited security operations staffing.
Financial Services commands pricing premiums. Government Agencies are climbing the fastest as critical infrastructure designations expand.
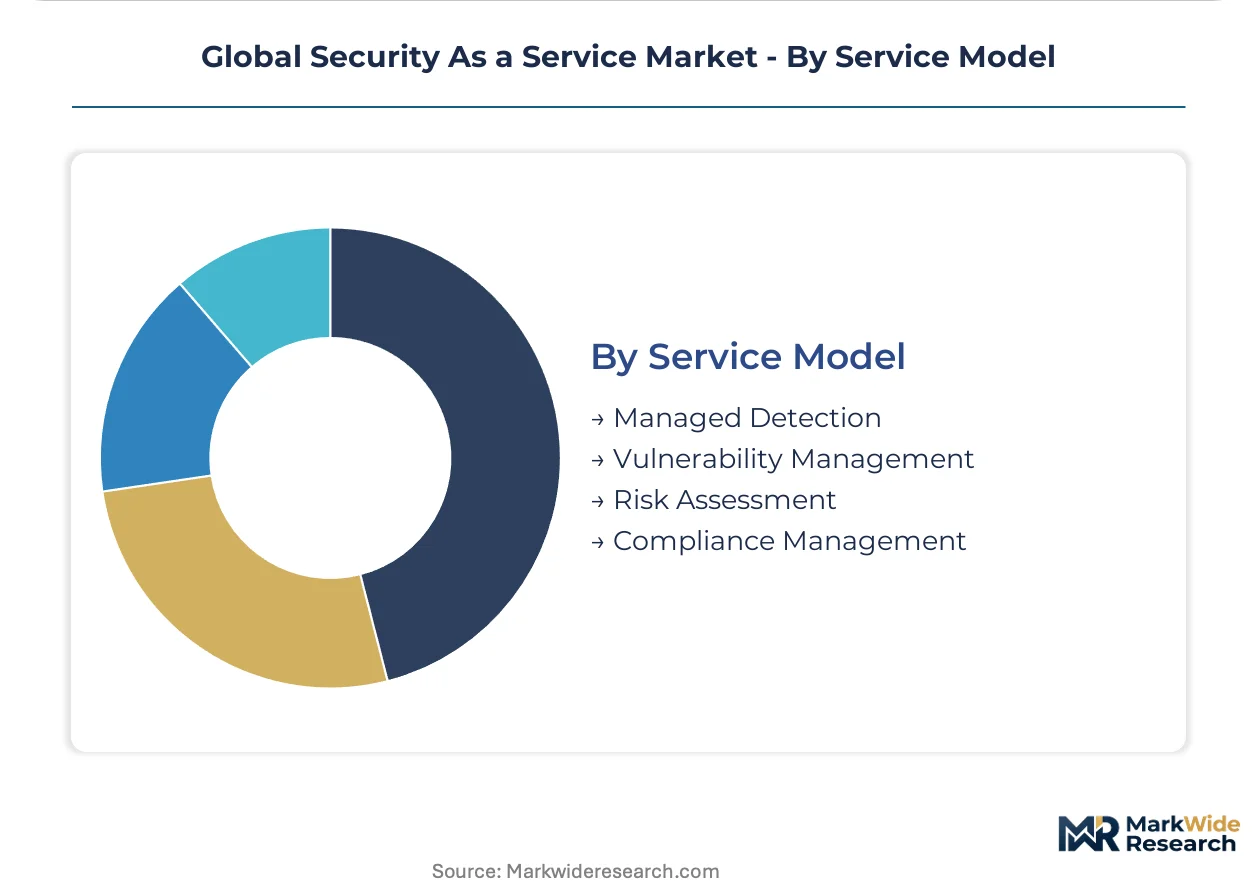
Service Model:
Delivery economics separate technology-enabled automation from labor-dependent professional services.
- Managed Detection:24/7 security operations center monitoring with analyst-driven threat validation captures expanding margin pools. Labor shortages in Germany, Japan, and the United States constrain service scalability. Mid-market enterprises bypass internal SOC buildouts entirely.
- Vulnerability Management:Continuous scanning and patch prioritization workflows address EU NIS2 Directive technical requirements. Cloud-native deployment eliminates hardware sensor deployment friction.
- Risk Assessment:Third-party vendor security scoring and attack surface mapping services support procurement due diligence.
- Compliance Management:Documentation automation for regulatory audit trails reduces professional services dependency.
Managed Detection holds the steepest expansion trajectory. Vulnerability Management is rotating up the share rankings as continuous scanning mandates proliferate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Transatlantic data cable capacity underwrites United States dominance in cloud-delivered security infrastructure, while EU regulatory harmonization accelerates procurement velocity across member states. Japan's undersea cable landing stations anchor Asia-Pacific demand concentration for managed detection services.
United States
Financial services institutions in New York and Chicago drive consumption-based identity management contracts tied to SEC disclosure mandates. FDA medical device cybersecurity oversight expands addressable demand among Boston and Minneapolis healthcare technology clusters. Silicon Valley hyperscaler integration partnerships compress deployment timelines for mid-market SaaS vendors.
Germany
Automotive manufacturers in Stuttgart and Munich elevate managed detection procurement under EU NIS2 Directive vulnerability scanning mandates. Frankfurt's financial clearing infrastructure demands pre-certified algorithmic transparency architectures per EU AI Act requirements. Industrial machinery exporters in North Rhine-Westphalia bypass internal SOC buildouts entirely.
Japan
Tokyo-based electronics manufacturers accelerate zero-trust adoption under METI supply chain data protection guidelines. Osaka pharmaceutical clusters face breach notification mandates that inflate incident response service premiums. Nagoya automotive suppliers concentrate procurement among cloud-native platforms eliminating hardware refresh cycles.
United Kingdom
London financial institutions negotiate usage-tiered identity contracts reducing overprovisioning waste against FCA operational resilience requirements. Manchester and Birmingham healthcare trusts document incident response capabilities for NHS Digital compliance. Edinburgh fintech clusters favor hybrid architectures retaining sensitive processing on-premise.
India
Bangalore IT services exporters and Mumbai financial institutions represent greenfield demand lacking internal security operations centers. CERT-In breach reporting mandates elevate subscription security procurement among Hyderabad pharmaceutical manufacturers. Delhi-NCR government digitization programs expand sovereign cloud certification requirements.
Global Security As a Service Market Competitive Landscape
Concentration sits with diversified technology conglomerates anchoring enterprise accounts through native cloud integration. The vendor base spans three tiers: hyperscale platforms bundling security with infrastructure, pure-play specialists commanding zero-trust premiums, and regional managed service providers capturing mid-market price sensitivity. Strategic moves center on portfolio consolidation through acquisition and consumption-based licensing model transitions.
Within the platform integration tier, Microsoft and IBM exemplify archetypes leveraging existing cloud infrastructure relationships to displace standalone vendors. Zscaler occupies a specialist position in zero-trust network access, representing the pure-play vector where architectural focus commands deployment velocity advantages. These three anchors illustrate competitive positioning across integration depth versus functional specialization trade-offs.
| Leading Market Players |
|---|
| IBM |
| Microsoft |
| Cisco Systems |
| Trend Micro |
| Zscaler |
| Fortinet |
| McAfee |
| Sophos |
| Barracuda Networks |
| Others |
Supply & Pricing Matrix
FedRAMP and EU sovereign cloud certifications gate vendor qualification and tier price differentiation simultaneously, compressing mid-market access to premium service tiers while elevating procurement thresholds for government and critical infrastructure accounts.
Pricing Analysis
Volume-discount tiering structures dominate enterprise procurement, with consumption-based licensing scaling from per-authentication-event metering at the low end to unlimited SOC analyst hours at premium tiers. Price differentiation rests on certification depth—FedRAMP High versus Moderate baselines—and geographic redundancy guarantees for data residency compliance. Cost compression in standard tiers intensifies as hyperscalers bundle security with infrastructure commitments. Mid-market manufacturing exporters in Germany and Japan exhibit highest price sensitivity, while United States financial institutions accept premium positioning for documented incident response capabilities.
Supply Chain Analysis
United States hyperscalers anchor cloud infrastructure provisioning, while Israel and Estonia concentrate threat intelligence feed curation and adversary research specialization. Taiwan feeds semiconductor components for security appliance manufacturing, though cloud-native deployment is displacing hardware dependencies. Single-source vulnerability in specialized analyst labor pools—particularly forensic investigators certified in EU NIS2 documentation standards—elevates service delivery risk. Distribution runs through direct enterprise sales for large accounts and managed service provider intermediaries for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
EU NIS2 Directive enforcement creates a high-growth disruption as continuous vulnerability scanning mandates force procurement decisions across critical infrastructure operators previously reliant on periodic assessments.
For Market Incumbents: Fortify managed detection service scalability through automation investments that offset SOC analyst labor shortages constraining delivery capacity. Acquire specialized threat intelligence boutiques in Estonia or Israel to deepen adversary tracking capabilities. Certification pre-positioning for EU AI Act algorithmic transparency requirements will defend margin position against compliance-driven RFP disqualification.
For New Entrants and Emerging Players: Lead with AI-augmented incident response orchestration targeting United States healthcare providers facing FDA medical device cybersecurity oversight, a segment where incumbent platforms carry legacy integration debt. White-space concentration in India's underpenetrated mid-market manufacturing sector offers greenfield deployment velocity absent entrenched vendor relationships. Channel partnership with domestic IT services exporters accelerates trust establishment.
For Investors and Strategic Acquirers: EU AI Act implementation reshapes the acquisition landscape toward vendors with pre-certified explainable AI modules embedded in threat detection pipelines. Long-term viability favors platforms demonstrating consumption-based licensing operationalization and multi-tenant architecture scalability. Watch NIS2 Directive enforcement variance across member states as the signal indicating regional demand inflection timing.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration Partnership | Native Azure or AWS embedding compresses standalone vendor displacement cycles for enterprise accounts. |
| Acquisition of Specialist Firm | Threat intelligence boutiques in Israel or Estonia deepen adversary tracking capabilities against nation-state actors. |
| Geographic Expansion | India mid-market manufacturing penetration captures greenfield demand lacking internal security operations centers. |
| Product Launch | AI-augmented incident response modules address FDA medical device cybersecurity documentation requirements. |
| Strategic Partnership | Managed service provider alliances extend mid-market reach without direct sales force buildout. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted across primary fieldwork, including CISOs at financial services and healthcare institutions, security operations center directors, managed detection service procurement leads, and cloud infrastructure architects. Secondary validation drew from SEC 10-K cybersecurity risk disclosures, EU NIS2 implementation guidance documents, FDA medical device cybersecurity premarket submissions, and hyperscaler security service revenue segment reporting. Bottom-up deployment sizing across named countries and top-down market triangulation against infrastructure spending patterns anchored value estimates.
Across the analysis window, the forecasting framework modeled deployment model transitions, solution type intensity shifts, end-user vertical concentration, and service model margin evolution. CAGRs derived from segment-level growth rate distributions weighted by installed base momentum and regulatory mandate enforcement calendars. Inputs included SOC analyst labor supply projections, cloud migration velocity indices, and breach cost escalation trajectories.
The analysis sits within stated boundaries; outcomes outside sustained regulatory enforcement intensity or accelerated hyperscaler bundling would require recalibration. Forecasts reflect documented assumptions regarding EU member state implementation variance and mid-market budget accessibility thresholds. Recalibration cycles align with material shifts in NIS2 audit frequency mandates and AI Act risk classification finalization.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Lawful Interception Market
Security and Surveillance
Multi-Layer Security Market
Security and Surveillance
Proactive Security Market
Security and Surveillance
Global Law Enforcement Software Market
Security and Surveillance
Global Security and Vulnerability Management Market
Security and Surveillance
North America Security Testing Market
Security and Surveillance
Specialized Threat Analysis and Protection Market
Security and Surveillance
Commercial Security Market
Security and Surveillance
Private Military Security Services Market
Security and Surveillance
Full Body Scanner Market
Security and Surveillance
Global Container Security Market
Security and Surveillance
Global Intrusion Detection System Market
Security and Surveillance
Global School and Campus Security Market
Security and Surveillance
Europe Security Testing Market
Security and Surveillance
Europe Baggage and Parcel Screening Market
Security and Surveillance
Airport Baggage Screening Systems Market