
 Europe Security Testing Market | 2026-2036
Europe Security Testing Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Security Testing Market Foresight
Healthcare is realigning toward cloud-based security testing as European hospitals digitize patient records and connected medical devices. IBM leverages its consulting footprint to anchor large-scale penetration testing contracts across German healthcare networks. Accenture competes through outcome-based managed security services that bundle dynamic analysis with compliance reporting. Veracode specializes in static analysis tooling for software supply chains serving pharmaceutical and medical device developers.
Europe Security Testing encompasses systematic evaluation of software, networks, and systems to identify vulnerabilities through automated scanning, manual exploitation techniques, and code review against frameworks such as OWASP and CVSS scoring. Its primary purpose is to reduce breach probability and demonstrate regulatory conformity before production deployment. Penetration testing commands the largest share of service type revenue because CISOs require adversarial simulation to satisfy cyber insurance underwriters and NIS2 audit criteria. Cloud-based deployment is expanding fastest as mid-market firms abandon capital-intensive on-premises toolchains for subscription vulnerability management platforms. Hybrid architectures retain relevance among defense contractors and critical infrastructure operators in France and Italy that segment classified workloads from public cloud scan data.
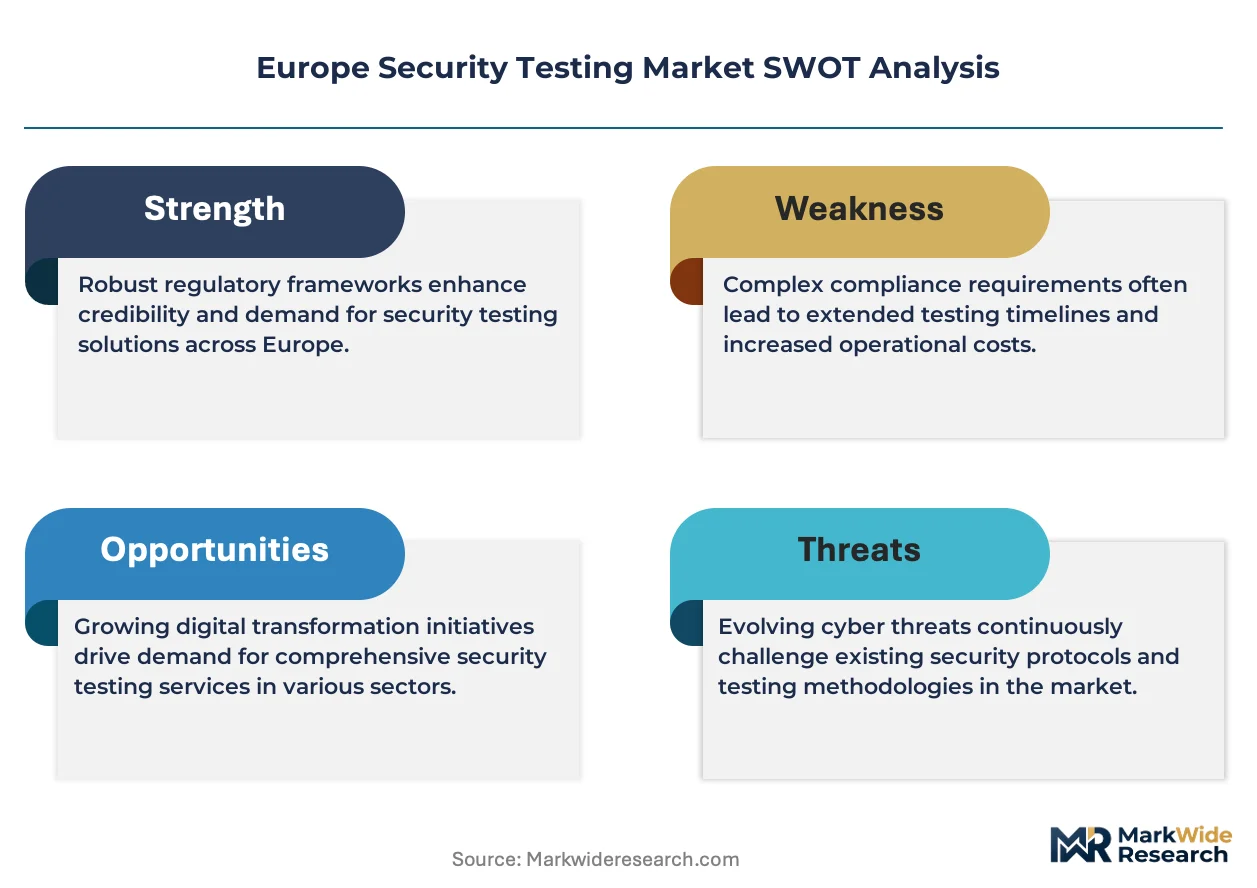
The EU AI Act, NIS2 Directive, and GDPR enforcement by national data protection authorities are tightening mandatory security assessment schedules for high-risk digital service providers. ETSI cyber standards and CE marking for connected devices further embed testing into product lifecycle gates before market access. Stakeholders must track how ENISA threat intelligence feeds reshape testing scope requirements and whether national transposition of NIS2 accelerates mandatory third-party certification timelines.
Market Dynamics
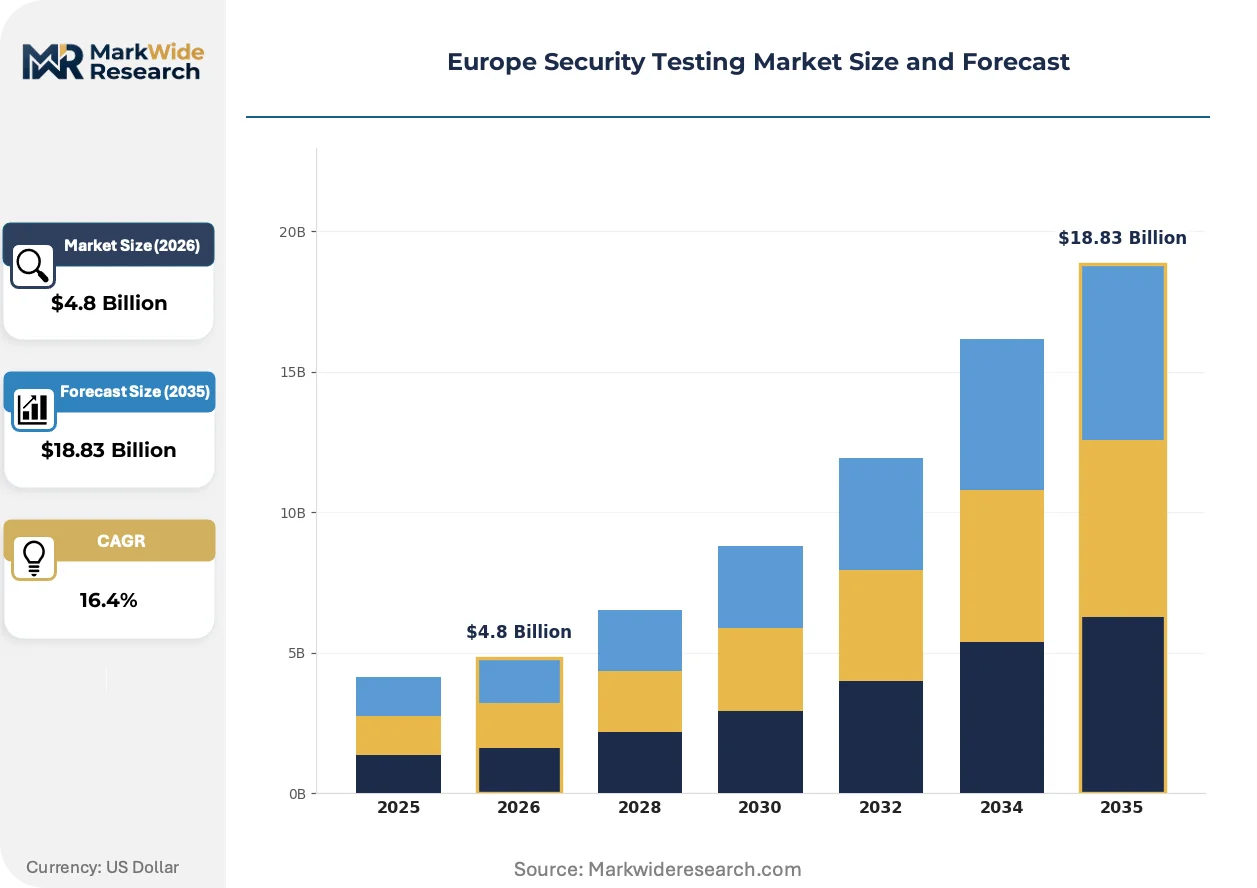
NIS2 transposition deadlines across EU member states are compressing procurement cycles for mandatory third-party security assessments, forcing mid-market enterprises to abandon discretionary vulnerability programs in favor of certified audit-ready testing frameworks.
Growth Catalysts
- GDPR Article 32 mandates:Data controllers in France and Germany must demonstrate technical safeguards through documented penetration testing, creating recurring revenue streams for qualified assessors.
- Healthcare digitization:Connected medical devices in Dutch and Swedish hospitals require CE-marked cybersecurity validation before market authorization, expanding device-focused testing volumes.
- Cloud migration velocity:German automotive suppliers are abandoning on-premises security stacks for continuous vulnerability management platforms that integrate with DevSecOps pipelines.
Market Restraints
- Qualified assessor scarcity:ENISA certification requirements for NIS2-critical entity testing have created bottlenecks in Spain and Italy, extending project lead times.
- Input cost volatility:Specialized hardware for hardware security module testing faces semiconductor supply constraints, inflating equipment depreciation schedules for penetration testing labs.
- Technical limitation:Static analysis tools generate false positive rates exceeding 40% in legacy COBOL systems common at Italian financial institutions, degrading remediation efficiency.
Strategic Opportunities
- Underpenetrated vertical:Agricultural technology deployers in Poland and Romania lack embedded security testing protocols for IoT sensor networks, representing uncaptured service demand.
- Regulatory tailwind:The EU AI Act's high-risk system classification will mandate security assessments for algorithmic decision systems in French public sector procurement from 2026.
- Technology convergence:Runtime application self-protection integration with continuous integration pipelines enables real-time vulnerability remediation for Danish software vendors.
Industry Challenges
- Certification timeline compression:Common Criteria evaluations for government-facing solutions now require 18-month cycles, misaligning with agile development sprints at UK defense contractors.
- Skill fragmentation:Offensive security expertise concentrates in London and Berlin, leaving satellite markets in Portugal and Greece dependent on remote delivery models with higher attrition rates.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Security Testing Market |
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $18.83 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Static Analysis, Dynamic Analysis, Penetration Testing, Security Auditing Deployment Mode: On-premises, Cloud-based, Hybrid, Managed Services End User: Government, BFSI, Healthcare, Retail Industry Vertical: IT, Telecommunications, Manufacturing, Education |
| Companies Covered | Hewlett Packard Enterprise Development LP, IBM, Veracode, McAfee, Cisco Systems, Accenture, Intertek, NTT DATA, Core Security Technologies, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Security Testing Market Shifts & Advancements
Attack surface management platforms are absorbing discrete vulnerability scanning functions, compressing vendor landscapes while elevating expectations for continuous exposure validation across European enterprise security programs.
Extended detection and response tooling is consolidating security testing telemetry from previously siloed dynamic application security testing, interactive application security testing, and penetration testing workflows into unified risk scoring engines. German manufacturing CISOs are prioritizing these consolidated platforms to satisfy NIS2 supply chain security documentation requirements. The structural consequence is margin compression for point-solution vendors as procurement committees favor bundled security operations center augmentation contracts.
The EU AI Act's security requirements for high-risk AI systems are mandating adversarial robustness testing and model extraction attack validation before CE marking authorization. Industrial consequence includes new testing protocols for machine learning pipelines deployed in healthcare diagnostics and credit scoring applications. French AI deployers are responding by embedding security testing gates within MLOps workflows, creating demand for specialized AI red team capabilities distinct from traditional application testing.
Buyer procurement patterns are rotating toward continuous security validation subscriptions that displace annual penetration testing engagements. Mid-market firms in the Netherlands and Belgium are replacing point-in-time compliance audits with attack surface monitoring contracts priced per asset under management. This shift is most visible in financial services, where cyber insurance underwriters now accept continuous vulnerability exposure metrics in lieu of static annual test reports for premium calculations.
Europe Security Testing Market Segmentation
Security testing procurement patterns diverge sharply across deployment architectures, regulatory exposure levels, and asset criticality. Buyers in Frankfurt, London, and Paris prioritize certified assessor credentials over unit economics, fragmenting vendor selection criteria across the four core segmentation dimensions.
Service Type:
Technical sophistication separates buyers selecting automated scanning from those demanding adversarial simulation with documented exploit chains.
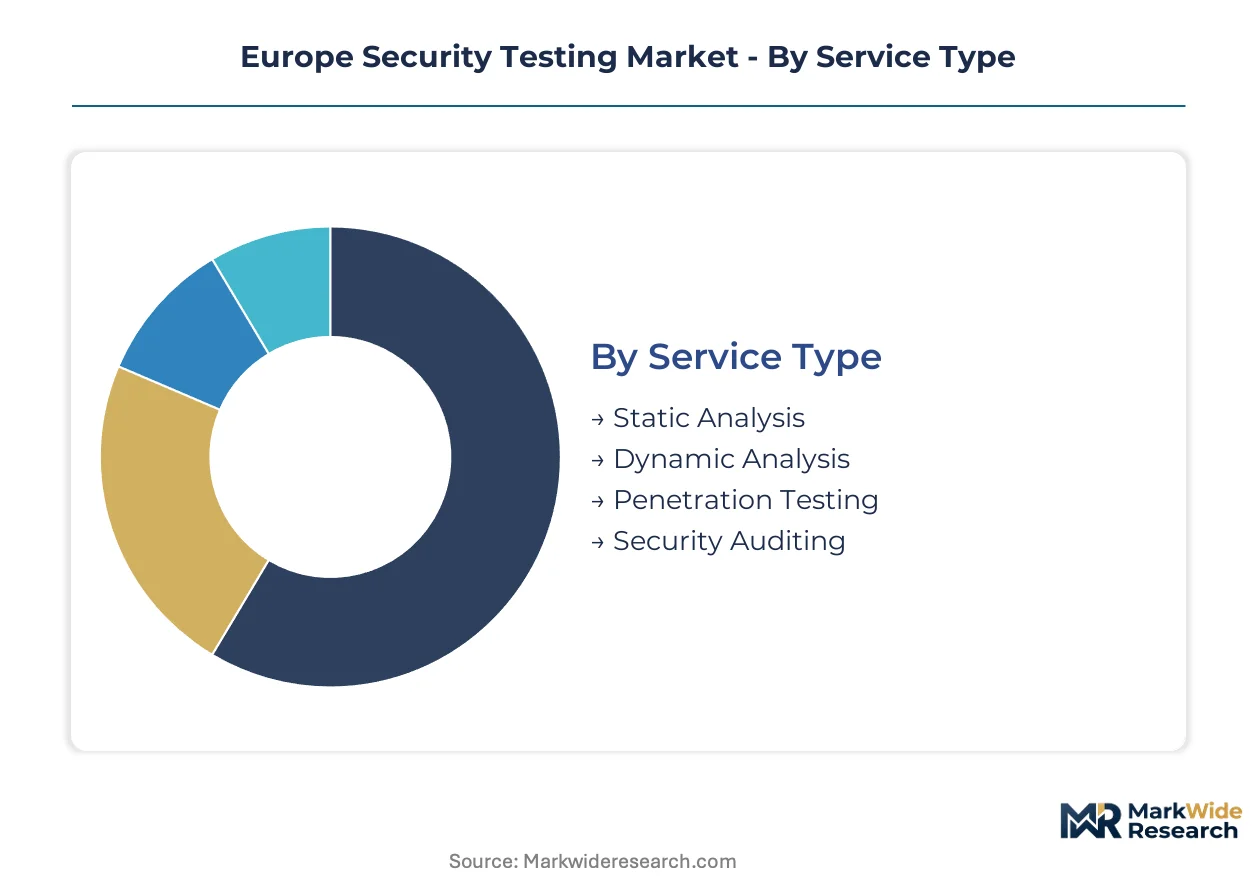
- Penetration Testing:Adversarial simulation exercises where certified ethical hackers attempt controlled breaches against production systems. Frankfurt-based BFSI institutions commission quarterly red team engagements to satisfy NIS2 audit criteria and cyber insurance underwriters.
- Static Analysis:Automated source code examination without execution, identifying vulnerabilities through pattern matching and data flow analysis. Pharmaceutical developers in Basel and Cambridge embed SAST gates within CI/CD pipelines to satisfy MDR software validation requirements.
- Dynamic Analysis:Runtime vulnerability detection through simulated attack traffic against executing applications.
- Security Auditing:Compliance-focused documentation review against GDPR Article 32 and ISO 27001 control frameworks.
Volume sits with Penetration Testing; growth tilts toward Static Analysis.
Deployment Mode:
Capital intensity and data sovereignty requirements partition buyers between subscription platforms and captive infrastructure investments.
- Cloud-based:SaaS-delivered vulnerability management with continuous scanning and API-native DevSecOps integration. Dutch mid-market firms and Belgian fintechs are displacing annual penetration testing contracts with per-asset subscription pricing.
- Hybrid:Segmented architectures isolating classified scan data on-premises while leveraging cloud analytics for non-sensitive workloads. French defense contractors and Italian critical infrastructure operators retain this model to satisfy national security compartmentalization rules.
- On-premises:Self-hosted scanning appliances requiring dedicated hardware maintenance and license management.
- Managed Services:Outcome-based contracts bundling testing execution with remediation workflow management.
Revenue concentrates in Cloud-based deployments; expansion is steepest in Hybrid configurations.
End User:
Regulatory enforcement intensity and breach liability exposure determine testing frequency and certification requirements.
- BFSI:Banking, insurance, and capital markets institutions subject to ECB guidance on ICT risk and DORA operational resilience mandates. London and Frankfurt institutions maintain continuous testing programs with dedicated internal red teams.
- Healthcare:Hospitals, medical device manufacturers, and health data processors facing GDPR health data provisions and MDR cybersecurity annex requirements. Dutch university hospitals and Swedish regional health authorities are prioritizing connected device testing.
- Government:Central and regional public sector bodies with classified system accreditation requirements.
- Retail:E-commerce platforms and payment processors managing PCI-DSS compliance cycles.
BFSI commands the largest absolute spend; Healthcare is climbing the fastest.
Industry Vertical:
Digital asset density and supply chain interconnection complexity shape testing scope and third-party certification demands.
- IT:Software vendors and cloud service providers integrating security testing throughout product lifecycles. Danish SaaS developers and Irish data center operators are embedding continuous validation within customer-facing SLAs.
- Manufacturing:Industrial automation and automotive suppliers addressing IEC 62443 standards for operational technology security. German automotive Tier-1s are extending testing requirements down semiconductor supplier tiers.
- Telecommunications:Network operators subject to NIS2 designation as critical entities with mandatory incident reporting.
- Education:Universities and research institutions managing open research data repositories and student information systems.
IT verticals absorb the highest testing intensity; Manufacturing is gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Frankfurt's Mainhattan financial district anchors continental demand for certified penetration testing services, with London's Canary Wharf and Paris's La Défense forming complementary clusters where NIS2 compliance deadlines concentrate procurement budgets.
Germany
Frankfurt-based BFSI institutions commission quarterly red team engagements to satisfy ECB guidance on ICT risk and cyber insurance mandates. The NIS2 Directive's transposition into national law compresses procurement cycles for mandatory third-party assessments. Bavarian automotive suppliers extend testing requirements down semiconductor supplier tiers, embedding IEC 62443 validation into procurement contracts.
United Kingdom
London institutions maintain continuous testing programs with dedicated internal red teams to address DORA operational resilience requirements. The Financial Conduct Authority's cyber resilience rules mandate documented penetration testing for authorized firms. Edinburgh and Manchester host growing specialist consultancies serving mid-market fintechs displaced from annual compliance audits.
France
Parisian defense contractors retain hybrid architectures to satisfy national security compartmentalization rules for classified workloads. ANSSI certification requirements for critical entity testing create assessor bottlenecks in regional markets. Lyon and Toulouse clusters see expanding demand for medical device cybersecurity validation under MDR annex requirements.
Netherlands
Dutch mid-market firms and Belgian fintechs displace annual penetration testing contracts with per-asset subscription pricing for cloud-based platforms. The Dutch Authority for Digital Infrastructure enforces NIS2 designation timelines for telecom operators. Amsterdam's health data processors prioritize connected device testing for CE-marked cybersecurity validation.
Italy
Milanese financial institutions face degraded remediation efficiency from static analysis false positives in legacy COBOL systems. The national cybersecurity agency's ENISA certification requirements extend project lead times for critical infrastructure operators. Turin and Rome defense contractors segment classified workloads from public cloud scan data under national security protocols.
Europe Security Testing Market Competitive Landscape
Top-tier vendors anchor enterprise penetration testing and managed security services, while mid-tier specialists compete on vertical-specific compliance automation. The vendor base stratifies across three strategic archetypes: consulting-led integrators bundling advisory with testing execution, pure-play software vendors delivering static and dynamic analysis tooling, and certification-focused assessors targeting regulated BFSI and healthcare endpoints. Consolidation pressure favors bundled security operations center augmentation contracts over point-solution procurement. Geographic expansion into underpenetrated CEE markets and technology convergence around attack surface management platforms represent dominant competitive vectors.
Within the consulting-led tier, Accenture and IBM occupy positions exemplifying outcome-based managed security services that bundle dynamic analysis with compliance reporting. Veracode anchors the pure-play software archetype, representing static analysis specialization for software supply chains. These three entities collectively illustrate how vendor selection criteria in Frankfurt, London, and Paris prioritize certified assessor credentials over unit economics, fragmenting competitive positioning across service type and deployment architecture dimensions.
| Leading Market Players |
|---|
| Hewlett Packard Enterprise Development LP |
| IBM |
| Veracode |
| McAfee |
| Cisco Systems |
| Accenture |
| Intertek |
| NTT DATA |
| Core Security Technologies |
| Others |
Supply & Pricing Matrix
Frankfurt-based BFSI institutions anchor pricing power through bundled managed security services that absorb point-solution vendors into subscription frameworks, compressing margins for standalone penetration testing providers.
Pricing Analysis
Short lead-time premiums of 30-50% apply to ENISA-certified assessor engagements as NIS2 transposition deadlines compress procurement cycles across German and French critical infrastructure operators. Three-tier pricing structure across premium certified assessor engagements, standard automated scanning subscriptions, and economy self-service SaaS tiers dominates procurement patterns. Cost compression in the standard tier is intensifying because mid-market firms are displacing annual penetration testing contracts with per-asset continuous monitoring platforms. Healthcare and government verticals demonstrate least price sensitivity due to mandatory certification requirements, while Dutch and Belgian mid-market firms exhibit highest elasticity.
Supply Chain Analysis
Direct-to-enterprise channels handle hyperscale buyer demand from London and Frankfurt financial institutions, while value-added resellers serve fragmented mid-market demand across Southern Europe. Specialized hardware for hardware security module testing concentrates supply in Germany, the United Kingdom, and the Netherlands, drawing from semiconductor fabrication facilities in Taiwan and South Korea. Supply chain risk centers on single-source vulnerability for ENISA-certified ethical hacker talent pools concentrated in Berlin and London. Distribution runs through consulting-led integrators bundling advisory with testing execution, compressing standalone software vendor margins.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
ENISA certification bottlenecks for NIS2-critical entity testing prop pricing premiums for qualified assessors, creating a supply-constrained market structure favoring incumbent consolidation.
For Market Incumbents: Deepen vertical integration into MLOps security testing capabilities to capture EU AI Act-mandated adversarial robustness validation demand before specialized AI red team competitors scale. Acquire ENISA-certified assessor capacity in Spain and Italy to alleviate geographic skill fragmentation threatening remote delivery attrition. Channel control through exclusive partnerships with German automotive Tier-1s anchors IEC 62443 supply chain security documentation workflows. For New Entrants and Emerging Players: Capture agricultural technology deployers in Poland and Romania through embedded IoT sensor network security protocols, an underpenetrated vertical lacking standardized testing frameworks. Target Polish agritech cooperatives with outcome-based managed services priced per hectare under monitoring rather than capital-intensive tool licensing. Partner with regional system integrators possessing existing relationships with agricultural equipment distributors to bypass direct enterprise sales cycle barriers. For Investors and Strategic Acquirers: The window for entry favors pure-play AI security testing specialists with adversarial robustness capabilities distinct from traditional application testing toolchains. Long-term viability hinges on regulatory tailwinds from EU AI Act high-risk system classifications mandating security assessments for algorithmic decision systems. Watch ENISA threat intelligence feed scope expansions as the inflection signal for accelerated mandatory third-party certification timeline compression.| Strategic Initiative | Industry Significance |
|---|---|
| ENISA Certification Acquisition | Expands qualified assessor capacity to serve NIS2-mandated critical infrastructure testing in Spain and Italy. |
| AI Red Team Capability Buildout | Positions vendors for EU AI Act adversarial robustness testing requirements in French healthcare diagnostics deployments. |
| Attack Surface Management Platform Integration | Consolidates discrete vulnerability scanning functions to satisfy German manufacturing CISO demand for unified risk scoring. |
| CE Marking Cybersecurity Partnership | Enables medical device manufacturers to satisfy MDR annex requirements for connected device validation in Dutch hospitals. |
| Continuous Monitoring Subscription Pivot | Displaces annual penetration testing contracts with per-asset pricing accepted by cyber insurance underwriters in Belgium. |
Research Methodology
Independent corroboration across primary interviews with CISOs at Frankfurt BFSI institutions, ENISA certification body representatives, and healthcare procurement officers at Dutch university hospitals underwrites the qualitative findings. Secondary validation draws from ECB guidance documents on ICT risk, NIS2 Directive transposition notices, and MDR cybersecurity annex technical specifications. Bottom-up triangulation of service provider revenue disclosures with top-down regulatory mandate scope assessments calibrates market sizing.
Rate-of-change decomposition separates volume growth from pricing dynamics across the projection horizon. Segmentation dimensions modeled include service type, deployment architecture, end-user vertical, and geographic regulatory cluster. CAGRs derive from regression analysis of historical procurement cycle compression against mandatory assessment timeline acceleration. Industry-specific forecast inputs incorporate ENISA threat intelligence feed expansion trajectories and cyber insurance underwriting acceptance of continuous vulnerability metrics.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to NIS2 national transposition variance and semiconductor supply constraints for hardware security module testing equipment. Forecasts reflect assumptions regarding ENISA certification pipeline expansion and EU AI Act implementation sequencing without presuming specific regulatory calendar adherence. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Intrusion Alarm System Market
Security and Surveillance
Global Threat Intelligence Management Market
Security and Surveillance
X-Ray Security Screening System Market
Security and Surveillance
Europe Security Assurance Market
Security and Surveillance
5G-Enhanced Surveillance Market
Security and Surveillance
Russian Intelligent Eavesdropping Detection System Market
Security and Surveillance
Anti-Piracy Protection Market
Security and Surveillance
Global Manned Security Service Market
Security and Surveillance
Narcotics Scanner Market
Security and Surveillance
Integrated Security Solutions Market
Security and Surveillance
Mass Transit Security Market
Security and Surveillance
India CCTV Market
Security and Surveillance
Security Operations Center Market
Security and Surveillance
Lawful Interception Market
Security and Surveillance
Global Cargo Inspection Market
Security and Surveillance
Home Security Sensors Market