
 Global Intrusion Detection System Market | 2026-2036
Global Intrusion Detection System Market Size, Share, and Industry Trends Forecast 2026-2036
Global Intrusion Detection System Market Foresight
Critical infrastructure operators is repositioning procurement priorities toward hybrid detection architectures that span both network and host layers. Cisco Systems, Inc. leverages its installed base of enterprise routers to embed anomaly-based sensors directly at traffic ingress points. Honeywell International Inc. anchors its industrial cybersecurity suite with signature-based protocols tailored for operational technology environments. Palo Alto Networks competes through cloud-native intrusion detection deployments that extend visibility across multi-tenant data center fabrics.
An intrusion detection system monitors network traffic and system activities for malicious patterns or policy violations, typically operating through signature databases, behavioral baselines, or stateful protocol inspection engines with detection thresholds measured in milliseconds. These systems serve primarily to alert security operations centers before lateral movement or data exfiltration occurs. Network-Based deployment retains the largest installed base due to its non-intrusive tap architecture, though Hybrid configurations are capturing the fastest growth as organizations consolidate point solutions. Anomaly-Based technology leads R&D investment flows because machine learning training pipelines demand continuous refinement against adversarial evasion tactics, while Signature-Based detection remains margin-diluted from commoditized open-source rule sets.
The U.S. Cybersecurity and Infrastructure Security Agency mandates intrusion detection coverage for federal agencies under Binding Operational Directive 22-01, while the EU NIS2 Directive imposes baseline monitoring requirements across energy, transport, and digital infrastructure sectors. Japan's METI has issued operational technology security guidelines that explicitly reference host-based detection for manufacturing control systems. Stakeholders must weigh whether to build in-house security operations centers or outsource monitoring to managed detection and response providers as alert volumes from encrypted traffic inspection overwhelm internal analyst capacity.
Market Dynamics
Hybrid detection architectures are compressing procurement cycles as security teams consolidate network and host-layer monitoring into unified platforms, forcing vendors to restructure licensing models around integrated sensor deployment rather than point-product sales.
Growth Catalysts
- EU NIS2 Directive:Mandatory baseline monitoring requirements across energy, transport, and digital infrastructure sectors are accelerating replacement of legacy passive scanning tools with real-time detection systems in Germany, France, and the Netherlands.
- Machine learning training pipelines:Continuous refinement against adversarial evasion tactics is attracting venture funding into anomaly-based detection engines, particularly for encrypted traffic inspection where signature methods fail.
- Financial services:Real-time threat monitoring deployments are expanding fastest among payment processors and digital banking platforms in Japan and the United States as transaction volumes shift to instant settlement rails.
Market Restraints
- Semiconductor supply concentration:Specialized packet-processing ASICs for high-throughput network sensors rely heavily on Taiwan-based foundry capacity, creating lead time vulnerability for hardware-dependent deployments.
- Commoditized signature rule sets:Open-source detection libraries maintained by the Emerging Threats community and Suricata project are eroding margins for vendors relying on proprietary signature subscriptions as primary revenue.
- Encrypted traffic blind spots:TLS 1.3 with perfect forward secrecy prevents deep packet inspection at network edges without certificate pinning or inline termination, degrading detection fidelity for signature-based systems.
Strategic Opportunities
- India's critical infrastructure:The country's national power grid and urban metro systems remain underpenetrated for operational technology intrusion detection, with CEA guidelines still in draft consultation for substation monitoring mandates.
- Extended detection and response convergence:Managed security service providers are bundling intrusion detection with automated response playbooks, creating attach-rate opportunities for vendors with SOAR-integrated sensor fabrics.
- Japan METI guidelines:Explicit host-based detection requirements for manufacturing control systems are opening procurement windows in automotive and electronics supply chains across Aichi and Kanagawa prefectures.
Industry Challenges
- Security operations analyst scarcity:Alert volumes from encrypted traffic inspection and cloud-native sensor proliferation are overwhelming internal SOC capacity, forcing choices between false-positive tolerance and detection latency.
- Legacy SCADA integration:Operational technology environments running decades-old control protocols require protocol-specific parsers and air-gapped deployment architectures that complicate vendor certification timelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Intrusion Detection System Market |
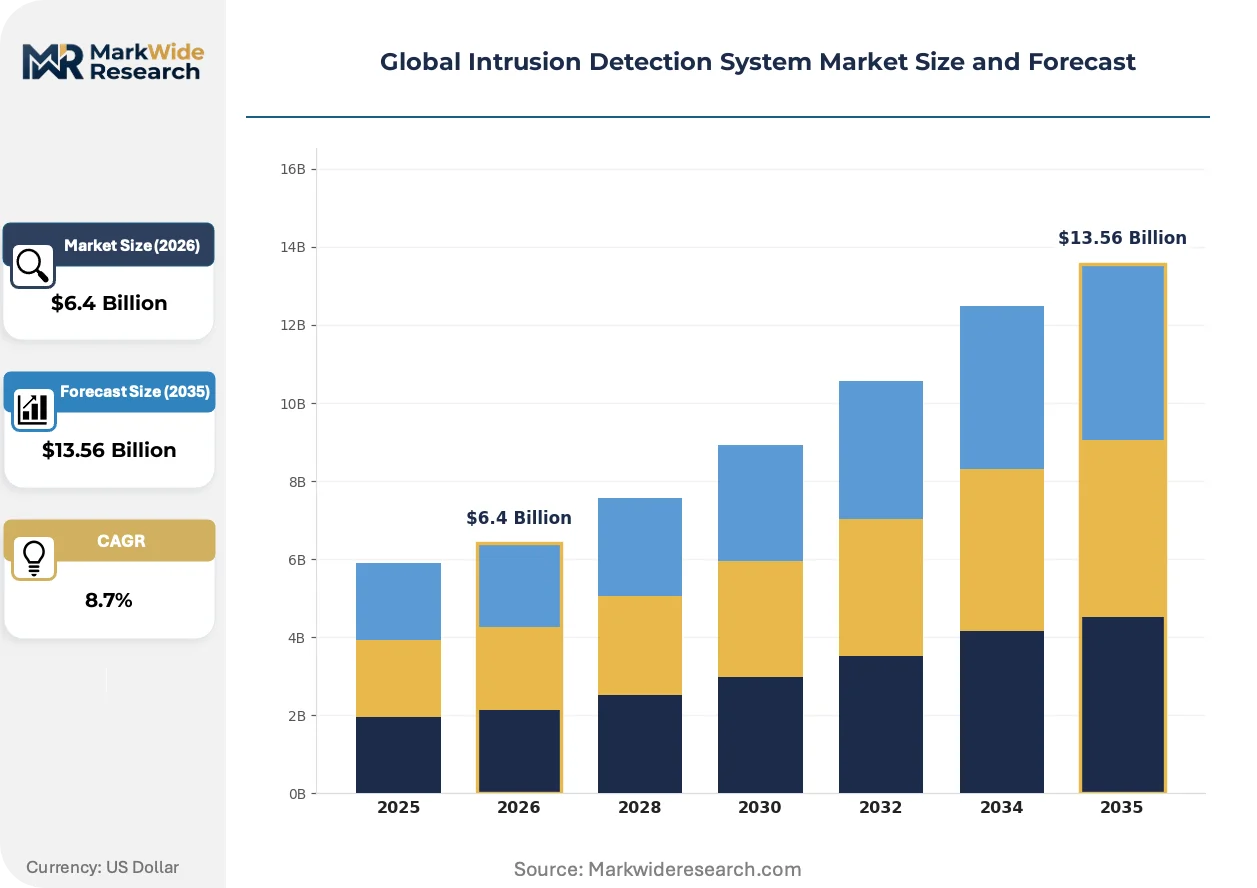
| Market Size in 2026 | $6.4 Billion |
| Market Size in 2035 | $13.56 Billion |
| CAGR (2026 – 2036) | 8.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Network-Based, Host-Based, Hybrid, Wireless Technology: Signature-Based, Anomaly-Based, Stateful Protocol Analysis, Hybrid Detection Application: Government Agencies, BFSI, Telecom, Manufacturing End User: Enterprises, Data Centers, Cloud Service Providers, Educational Institutions |
| Companies Covered | Schneider Electric, Cisco Systems, Inc., Honeywell International Inc., Palo Alto Networks, Fortinet, Inc., FLIR Systems, Senstar Corporation, Check Point Software Technologies Ltd., Johnson Controls, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Intrusion Detection System Market Shifts & Advancements
Detection technology is migrating from perimeter appliances toward distributed sensor fabrics embedded in cloud workloads and container orchestration layers, compressing the traditional network security stack into software-defined enforcement points.
Extended Berkeley Packet Filter is expanding into kernel-space traffic analysis for cloud-native intrusion detection, enabling inspection at line rate without hypervisor bypass. Major hyperscale operators and financial services firms are adopting eBPF-based sensors for containerized workloads. This architecture is expanding into multi-tenant data center fabrics where traditional tap-and-span deployments prove cost-prohibitive.
The EU AI Act's risk classification framework for biometric and behavioral analysis systems is forcing detection vendors to document training data provenance and adversarial testing protocols for machine learning models deployed in critical infrastructure. Industrial consequence includes mandatory conformity assessments before market placement. Energy sector operators in Germany and utilities in Spain are front-loading procurement to secure pre-certification deployment windows.
Consolidated platform procurement is displacing best-of-breed point solutions as CISOs prioritize vendor reduction over specialized feature depth. Managed detection and response providers are capturing mid-market accounts previously served by in-house SIEM deployments. This pattern is most visible in the United States federal contractor base, where CISA's Binding Operational Directive 22-01 compliance deadlines are compressing evaluation cycles.
Global Intrusion Detection System Market Segmentation
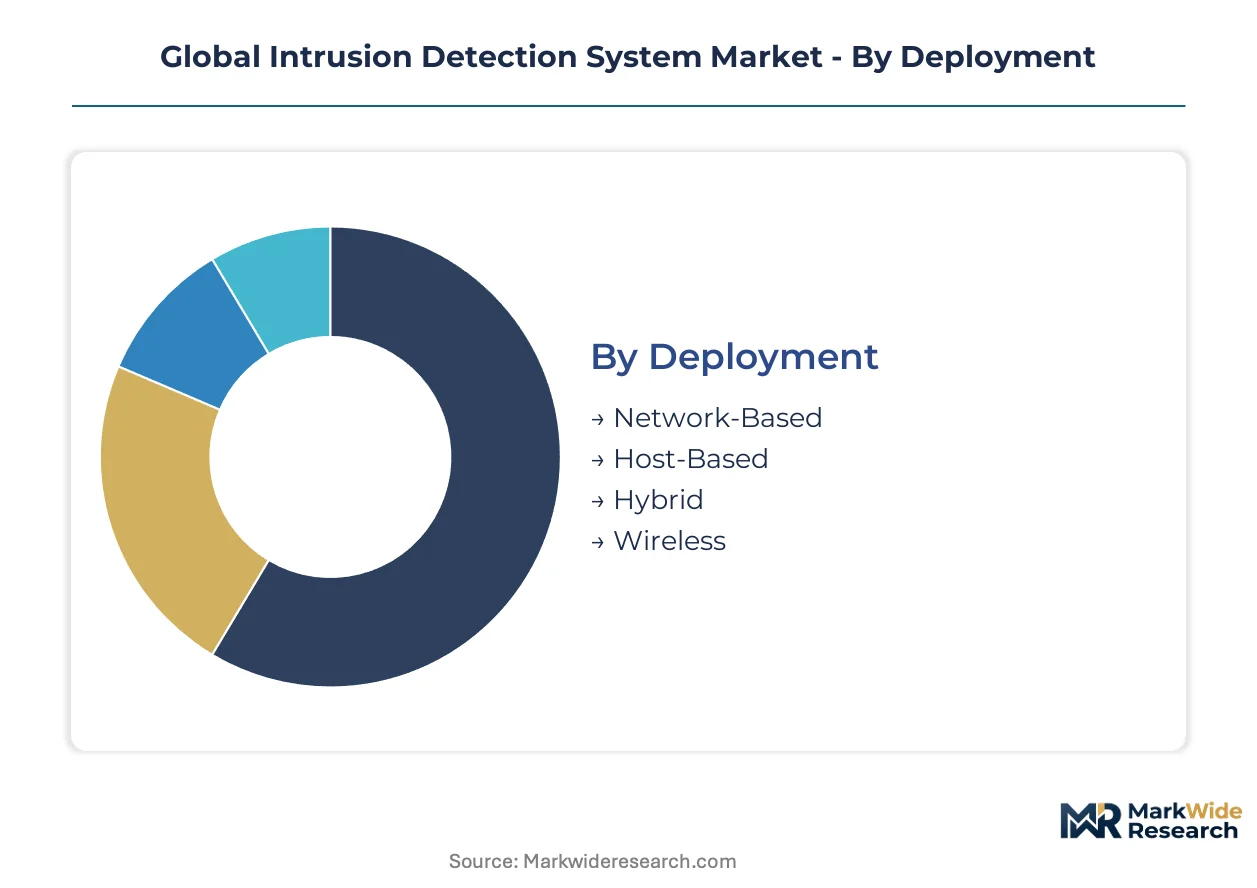
Intrusion detection architectures diverge sharply across deployment topologies, analytical engines, and operational contexts. Procurement patterns cluster where regulatory mandates intersect with specific threat models, creating four distinct segmentation axes that govern vendor positioning and pricing power.
Deployment:
Deployment topology determines sensor placement relative to protected assets and governs integration complexity with existing network fabrics.
- Network-Based:Sensors operate at traffic aggregation points using passive tap or SPAN port architectures without endpoint agent installation. Demand concentrates in United States federal agencies complying with CISA Binding Operational Directive 22-01, where non-intrusive inspection preserves legacy system stability during mandated coverage expansion.
- Hybrid:Correlates network traffic telemetry with host-level process and file system events through unified management planes. Financial services institutions in Japan and Germany are consolidating procurement around hybrid architectures as encrypted traffic volumes degrade pure network visibility.
- Host-Based:Endpoint agents monitor system calls, registry modifications, and memory-resident threats on individual assets. Manufacturing control systems in Aichi Prefecture deploy host-based sensors per METI operational technology security guidelines.
- Wireless:Specialized sensors detect rogue access points, evil twin attacks, and protocol-specific exploits in 802.11 and Bluetooth environments. Campus networks and distributed logistics facilities deploy wireless detection for device proliferation coverage.
Network-Based leads on installed base scale; Hybrid leads on procurement momentum.
Technology:
Detection methodology separates vendors by computational intensity, false-positive tolerance, and adversarial robustness.
- Anomaly-Based:Machine learning models establish behavioral baselines for users, devices, and network flows, flagging deviations without prior threat signatures. European critical infrastructure operators front-load investment ahead of EU AI Act conformity assessments for biometric and behavioral analysis systems.
- Signature-Based:Pattern-matching engines compare traffic against curated threat intelligence databases with deterministic detection outcomes. Open-source rule sets from the Suricata project compress margins for proprietary subscription vendors.
- Stateful Protocol Analysis:Tracks connection state machines against RFC specifications to detect protocol violations and tunneling attempts. Industrial control system deployments rely on protocol-specific parsers for Modbus and DNP3 traffic.
- Hybrid Detection:Orchestrates signature, anomaly, and stateful methods with confidence scoring to reduce analyst alert fatigue. Managed detection and response providers bundle hybrid engines for mid-market accounts lacking internal SOC capacity.
Signature-Based retains the largest revenue base; Anomaly-Based commands the steepest R&D investment trajectory.
Application:
Sector-specific threat models and compliance architectures shape solution configuration and deployment density.
- BFSI:Real-time transaction monitoring and SWIFT network protection drive sub-millisecond detection latency requirements. Payment processors in the United States and Japan deploy specialized sensors for instant settlement rail security.
- Government Agencies:Classified network segmentation and supply chain integrity mandates govern procurement specifications. Federal contractors face compressed evaluation cycles under CISA compliance deadlines.
- Telecom:5G core network function virtualization expands attack surfaces requiring container-native detection sensors. European operators integrate monitoring with NIS2 Directive incident reporting workflows.
- Manufacturing:Air-gapped operational technology environments demand specialized deployment architectures for legacy SCADA protocol visibility. German automotive supply chains anchor industrial cybersecurity procurement volumes.
BFSI leads on per-entity deployment spend; Government Agencies lead on mandate-driven replacement velocity.
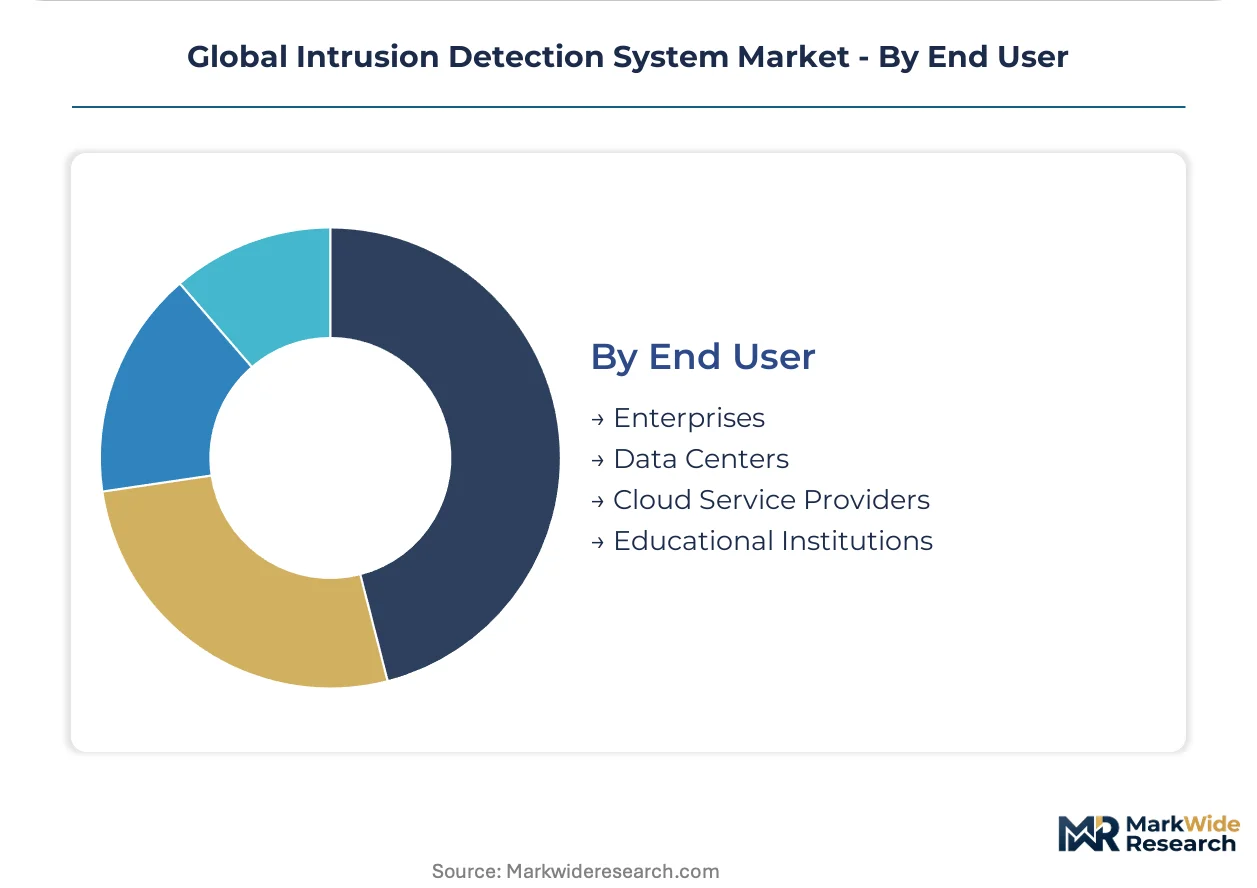
End User:
Organizational scale and infrastructure ownership models determine sensor management responsibility and operational cost structures.
- Enterprises:Diverse IT-OT convergence creates demand for unified detection platforms spanning campus, branch, and manufacturing facilities. CISOs prioritize vendor consolidation over point-solution depth.
- Cloud Service Providers:Multi-tenant data center fabrics require eBPF-based kernel-space sensors for cost-effective traffic inspection at hyperscale. Extended Berkeley Packet Filter architectures displace traditional tap-and-span deployments.
- Data Centers:Colocation and wholesale facilities offer intrusion detection as a value-added service to tenant customers. East-West traffic visibility between customer environments drives microsegmentation sensor deployment.
- Educational Institutions:Research network membership and open campus policies create distinctive threat models combining state-sponsored targeting with student device proliferation. Federated identity integration complicates behavioral baseline establishment.
Enterprises lead on aggregate procurement volume; Cloud Service Providers lead on technology adoption velocity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory divergence between jurisdictions with mature cybersecurity frameworks and those still drafting baseline mandates is redirecting procurement investment toward markets with codified compliance deadlines. The cost-of-compliance gap favors early-mover countries where CISOs can justify unified platform spending against specific penalty schedules.
United States
Federal agencies face compressed deployment timelines under CISA Binding Operational Directive 22-01, which mandates intrusion detection coverage for all internet-accessible assets. The Department of Defense and civilian agencies anchor procurement volumes in the Washington-Arlington-Alexandria corridor, where contractors cluster to support compliance implementation.
Germany
Energy sector operators front-load investment ahead of EU NIS2 Directive enforcement deadlines for critical infrastructure monitoring. The Rhine-Ruhr industrial belt drives hybrid detection adoption as manufacturing conglomerates consolidate network and host-layer visibility across converged IT-OT environments.
Japan
METI operational technology security guidelines explicitly mandate host-based detection for manufacturing control systems, opening procurement windows in automotive supply chains. Aichi Prefecture's automotive cluster and Kanagawa Prefecture's electronics manufacturers anchor industrial cybersecurity deployment volumes.
India
The Central Electricity Authority's draft guidelines for substation monitoring create anticipatory procurement activity in the national power grid. Metro rail systems in Delhi, Mumbai, and Bengaluru represent underpenetrated verticals where operational technology intrusion detection remains nascent.
United Kingdom
NCSC guidance on network monitoring for critical national infrastructure aligns procurement specifications with NIS2-equivalent baseline requirements. London's financial services concentration drives real-time threat monitoring investment among payment processors and clearing institutions.
Global Intrusion Detection System Market Competitive Landscape
Branded specialists and contract manufacturers split share differently across segments, with consolidated platform vendors capturing enterprise accounts while point-solution providers defend niche industrial verticals. The vendor base organizes around three strategic archetypes: network infrastructure incumbents leveraging installed router bases, industrial automation specialists with operational technology protocol expertise, and cloud-native security platforms targeting multi-tenant data center fabrics. Competitive intensity centers on M&A activity consolidating adjacent detection capabilities and strategic partnerships embedding sensors within managed security service provider stacks.
Among industrial automation specialists, Schneider Electric and Honeywell International Inc. exemplify the operational technology-centric archetype with embedded cybersecurity suites. Cisco Systems, Inc. anchors the network infrastructure tier, representing vendors that distribute detection capabilities through existing enterprise routing footprints rather than standalone appliance sales.
| Leading Market Players |
|---|
| Schneider Electric |
| Cisco Systems, Inc. |
| Honeywell International Inc. |
| Palo Alto Networks |
| Fortinet, Inc. |
| FLIR Systems |
| Senstar Corporation |
| Check Point Software Technologies Ltd. |
| Johnson Controls |
| Others |
Supply & Pricing Matrix
Federal contractor consolidation around CISA-compliant unified platforms is forcing sensor vendors to absorb certification costs while maintaining hardware margins, compressing net pricing power across the mid-market tier.
Pricing Analysis
Distributor margins for network-based appliances run 15-22 percent before value-added installation services, while direct-to-OEM arrangements for embedded router sensors command steeper volume discounts. Three-tier pricing structure across premium, standard, and economy levels separates AI-powered anomaly engines from signature-based subscriptions and open-source rule set deployments. Pricing pressure stems from Suricata-project commoditization eroding proprietary subscription renewals. Cloud-native buyers exhibit lowest price sensitivity; educational institutions and municipal utilities show highest.
Supply Chain Analysis
Regional distribution centers in Singapore, Rotterdam, and Los Angeles anchor hub-and-spoke fulfillment for hardware-dependent network sensors. Specialized packet-processing ASICs draw from Taiwan-based foundry capacity, FPGA logic from Xilinx supply chains, and precision timing components from Japanese manufacturers. Single-source vulnerability concentrates in advanced semiconductor nodes. Distribution runs through authorized value-added resellers serving federal compliance verticals alongside direct hyperscale contracts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The intrusion detection market compounds steadily as regulatory mandates harden baseline monitoring requirements across critical infrastructure sectors worldwide.
For Market Incumbents: Lock in router-embedded sensor positions through Cisco's installed base leverage while consolidating anomaly-detection capabilities via targeted acquisition of eBPF-native startups. The threat of cloud-native platforms displacing hardware-dependent revenue demands backward integration into kernel-space inspection technology. Certification investment for EU AI Act conformity assessments anchors pricing power in European energy verticals. For New Entrants and Emerging Players: Managed security service providers represent the most penetrable channel for hybrid detection platforms lacking direct enterprise sales infrastructure. India's draft CEA substation guidelines and Japan's METI manufacturing mandates open white-space procurement windows before incumbent saturation. A SOAR-integrated sensor fabric bundled through MSSP attach rates bypasses direct SOC capacity constraints. For Investors and Strategic Acquirers: Asymmetric upside sits with industrial automation specialists possessing operational technology protocol parsers for legacy SCADA environments. The five-to-ten year viability window favors vendors with air-gapped deployment architectures and Modbus/DNP3 expertise. Watch NIS2 Directive enforcement velocity in Germany as the inflection signal for European replacement cycle timing.| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of eBPF-Native Specialist | Kernel-space inspection capability anchors cloud-native detection differentiation against tap-and-span incumbents. |
| EU AI Act Conformity Pre-Certification | Front-loaded procurement from German energy operators secures deployment windows ahead of mandatory assessments. |
| MSSP Strategic Partnership | SOAR-integrated sensor fabrics capture mid-market accounts overwhelmed by encrypted traffic alert volumes. |
| Industrial Protocol Parser Development | Modbus and DNP3 expertise opens operational technology procurement in manufacturing and utility verticals. |
| Router-Embedded Sensor Expansion | Cisco's enterprise routing footprint enables non-intrusive detection deployment without standalone appliance sales cycles. |
Research Methodology
Direct dialogue with CISOs at financial services institutions, security operations center directors, federal procurement officers, managed detection and response providers, and industrial control system engineers grounded qualitative assessment. Secondary validation drew from CISA Binding Operational Directive filings, EU NIS2 implementation guidance, METI operational technology security guidelines, SEC 10-K cybersecurity risk disclosures, and hyperscaler infrastructure capex reports. Bottom-up sensor deployment estimates triangulated against top-down critical infrastructure protection spending allocations.
Bottom-up modeling aggregated deployment density by sector, organization size, and compliance mandate intensity across the projection horizon. Segmentation dimensions included deployment topology, detection methodology, application vertical, and end-user infrastructure ownership model. CAGRs derived from regression against historical replacement cycles and regulatory deadline acceleration patterns. Forecast inputs incorporated Taiwan semiconductor foundry capacity utilization and encrypted traffic volume growth trajectories.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to adversarial evasion tactic evolution and EU AI Act enforcement consistency. Outputs reflect documented assumptions around regulatory timeline adherence and supply chain lead time stability. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Europe Rockfall Radar Market
Security and Surveillance
Air Cargo Screening Systems Market
Security and Surveillance
Asia-Pacific Security Screening Market
Security and Surveillance
Global Alarm Monitoring Market
Security and Surveillance
Residential Security Market
Security and Surveillance
Global School and Campus Security Market
Security and Surveillance
Global Security As a Service Market
Security and Surveillance
Narcotics Scanner Market
Security and Surveillance
Home Security Sensors Market
Security and Surveillance
Explosive Detection Technology Market
Security and Surveillance
Russian Intelligent Eavesdropping Detection System Market
Security and Surveillance
Global Cargo Inspection Market
Security and Surveillance
Explosive Detection Kit Market
Security and Surveillance
Consumer Security Market
Security and Surveillance
Urban Security Screening Market
Security and Surveillance
Security Holograms Market