
 Security Testing Market | 2026-2036
Security Testing Market Size, Share, and Industry Trends Forecast 2026-2036
Security Testing Market Intelligence
The shift from in-house security teams to hybrid sourcing models is rebalancing how enterprises procure adversarial testing and continuous validation. Rapid7 leverages its managed detection platform to sustain recurring revenue from mid-market clients seeking outsourced validation. Coalfire anchors its position in FedRAMP and cloud compliance testing, competing directly with specialized boutiques for federal contractor wallets. Bishop Fox differentiates through its attack-surface management tools, while NetSPI specializes in cloud-native penetration testing for Fortune 500 technology stacks.
Security testing encompasses systematic evaluation of information systems, networks, and applications to identify exploitable weaknesses before malicious actors can leverage them, typically employing automated vulnerability scanners, manual penetration techniques, and adversarial simulation protocols against defined threat models. Its primary commercial purpose is to reduce residual cyber risk and demonstrate due diligence to regulators, insurers, and board-level stakeholders. Penetration testing services command premium pricing due to scarcity of certified practitioners and high liability exposure, while cloud-based deployment is displacing on-premises toolkits as multi-cloud architectures complicate attack-surface visibility. Application security testing sits at the fastest-expanding margin pool, driven by DevSecOps pipeline integration and software supply-chain mandates.
FDA cybersecurity guidance for connected medical devices, SEC disclosure rules for material cyber incidents, and EU NIS2 requirements for critical entity testing are reshaping procurement specifications and vendor qualification criteria across healthcare, finance, and energy verticals. These frameworks elevate demand for compliance-integrated testing that produces auditable evidence rather than standalone vulnerability reports. Stakeholders must monitor how emerging AI-generated attack techniques alter the skills premium for human-led adversarial testing versus automated platform scalability.
Market Dynamics
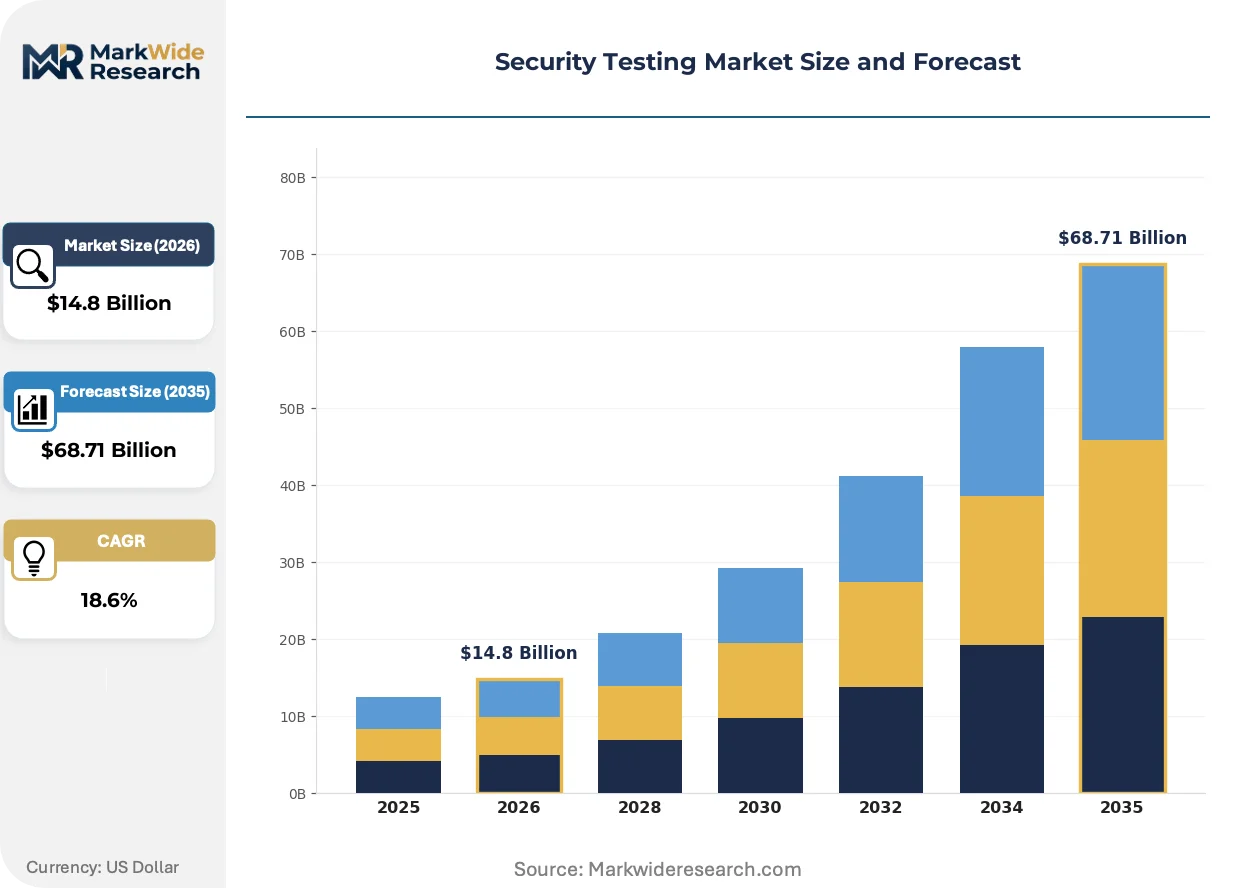
Hybrid sourcing models are rebalancing how enterprises procure adversarial testing, with continuous validation platforms absorbing budgets previously allocated to annual penetration testing cycles. This structural shift concentrates procurement power among vendors who can embed testing into DevSecOps pipelines.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators in energy, transport, and digital services must conduct more frequent third-party assessments, creating recurring demand for compliance-integrated testing.
- DevSecOps pipeline integration:Software supply-chain mandates from federal procurement standards are forcing application security testing into CI/CD workflows at build time.
- Cloud-native architectures:Multi-cloud deployments complicate attack-surface visibility, driving demand for specialized cloud penetration testing across distributed technology stacks.
Market Restraints
- Certified practitioner scarcity:Penetration testing services face supply constraints from limited pools of credentialed ethical hackers, compressing service delivery capacity.
- High liability exposure:Professional indemnity costs for red-team operations limit boutique firm expansion and deter market entry.
- Automated scanner commoditization:Low-cost vulnerability scanning tools threaten pricing power for baseline assessment services.
Strategic Opportunities
- Connected medical devices:FDA cybersecurity guidance creates compliance-driven testing demand across healthcare technology manufacturers.
- Attack-surface management convergence:Continuous external reconnaissance platforms are absorbing budgets from point-in-time penetration testing.
- FedRAMP authorization pathways:Cloud compliance testing for federal contractors represents underpenetrated wallet share within defense-adjacent technology providers.
Industry Challenges
- Adversarial AI skill gaps:Human-led red teams must develop capabilities to detect and counter machine-generated attack techniques.
- Legacy system integration:Operational technology environments in critical infrastructure resist automated testing deployment due to uptime requirements.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Testing Market |
| Market Size in 2026 | $14.8 Billion |
| Market Size in 2035 | $68.71 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Vulnerability Assessment, Penetration Testing, Security Audits, Compliance Testing Deployment: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Healthcare, Finance, Government, Retail Technology: Network Security, Application Security, Endpoint Security, Cloud Security |
| Companies Covered | SpecterOps, IOActive, DeepStrike, BreachLock, Rapid7, Coalfire, NetSPI, Cigniti Technologies, Bishop Fox, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Testing Market Strategic Shifts & Innovations
Artificial intelligence is absorbing testing workflows across the security validation stack, compressing timelines for vulnerability discovery while elevating the premium on human expertise for complex exploitation chains.
Automated adversarial simulation platforms are absorbing routine red-team functions through continuous breach-and-attack simulation. Financial services firms deploy these tools weekly rather than quarterly. The technology is absorbing budget share from traditional consulting engagements.
SEC disclosure rules for material cyber incidents are reshaping procurement specifications across publicly traded entities. Boards now demand auditable evidence of security testing rather than standalone vulnerability reports. Healthcare and energy verticals are responding by embedding compliance documentation into testing deliverables.
Continuous validation contracts are displacing annual penetration testing purchases among mid-market enterprises. Managed detection providers bundle testing services into recurring subscriptions. This pattern is most visible in United States technology and financial services segments.
Security Testing Market Segmentation
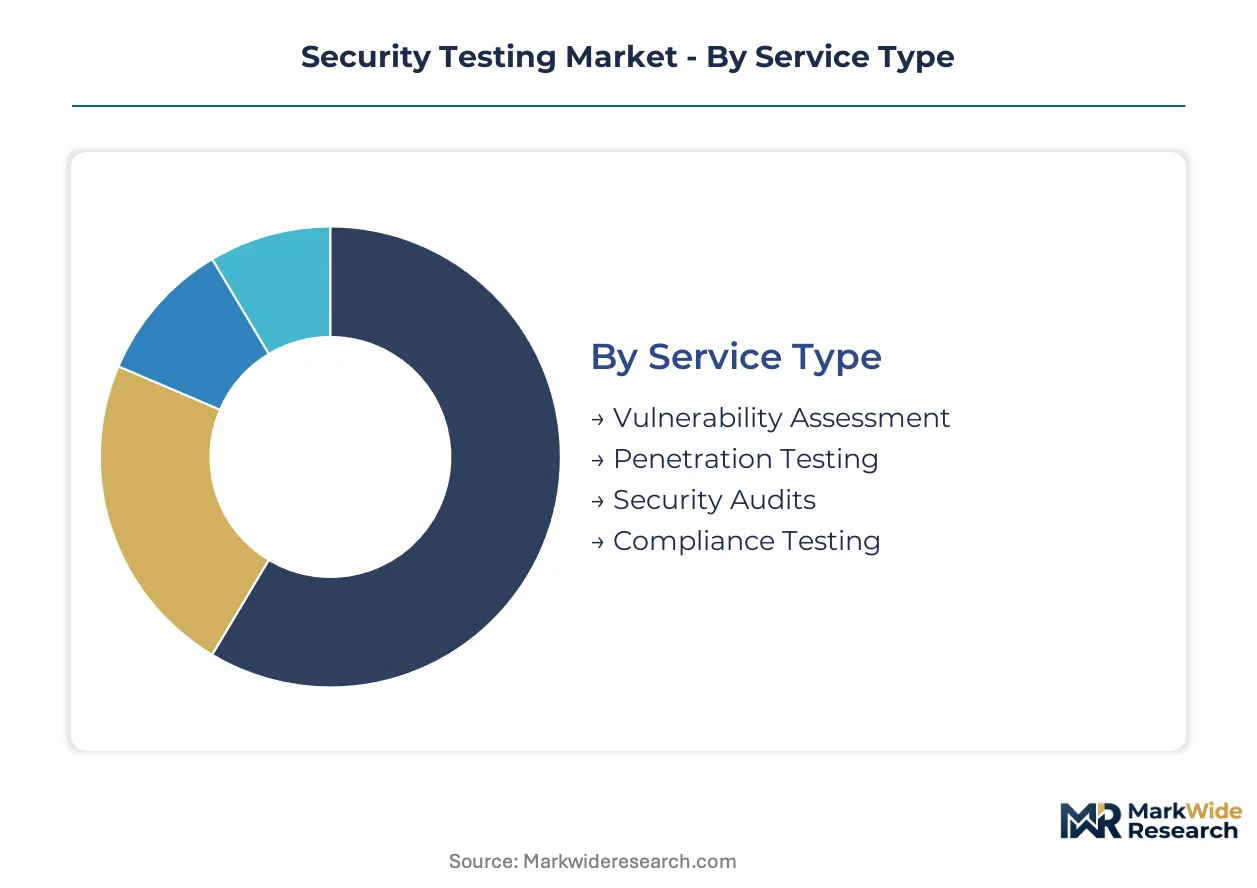
Security testing procurement patterns diverge sharply across service delivery models, infrastructure footprints, and regulatory exposure profiles. Understanding these fault lines reveals where vendor margins concentrate and which segments absorb technology displacement.
Service Type:
Supply concentration tilts toward high-touch engagements where certified practitioner scarcity creates pricing power and client lock-in.
- Penetration Testing:Manual adversarial simulation by credentialed ethical hackers against defined threat models. Demand concentrates among United States federal contractors facing FedRAMP authorization deadlines, with procurement pipelines prioritizing red-team operations over automated alternatives. Certified practitioner scarcity sustains premium pricing tiers.
- Vulnerability Assessment:Automated scanning protocols identifying known weaknesses across network perimeters and application layers. United States mid-market enterprises deploy these weekly through managed detection platforms, compressing timelines that previously required quarterly consulting engagements.
- Security Audits:Systematic evaluation of control frameworks against ISO 27001 or SOC 2 standards.
- Compliance Testing:Evidence generation for FDA cybersecurity guidance, SEC disclosure rules, and EU NIS2 Directive mandates.
Today's leader: Penetration Testing. Tomorrow's challenger: Compliance Testing.
Deployment:
Cost tier stratification separates capital-intensive on-premises toolkits from recurring-revenue cloud subscriptions.
- Cloud-Based:SaaS delivery of vulnerability scanning and attack-surface management platforms. United States technology firms with multi-cloud architectures drive procurement, seeking distributed visibility across AWS, Azure, and Google Cloud environments without hardware procurement cycles.
- Managed Service:Outsourced continuous validation bundled with threat detection and incident response. United States financial services firms favor this model for adversarial simulation, replacing annual penetration testing with weekly automated breach simulations.
- On-Premises:Licensed software deployed within client data centers for air-gapped environments.
- Hybrid:Orchestrated combination of cloud-delivered scanning with on-premises sensors for legacy system coverage.
Cloud-Based deployments are climbing the fastest. Hybrid architectures are gaining share fastest among critical infrastructure operators.
End User:
Application context determines testing frequency, with regulated verticals mandating quarterly third-party assessments.
- Finance:Banks, insurers, and payment processors facing SEC disclosure rules and breach notification laws. United States institutions expand security testing budgets fastest, embedding validation into DevSecOps pipelines for trading platforms and mobile banking applications.
- Government:Federal agencies and defense contractors maintaining the largest procurement pipelines for adversarial simulation services.
- Healthcare:Connected medical device manufacturers responding to FDA cybersecurity guidance with pre-market testing requirements.
- Retail:E-commerce platforms and point-of-sale system operators prioritizing payment card industry compliance.
Finance commands the steepest expansion trajectory. Healthcare represents the most underpenetrated wallet share for compliance-integrated testing.
Technology:
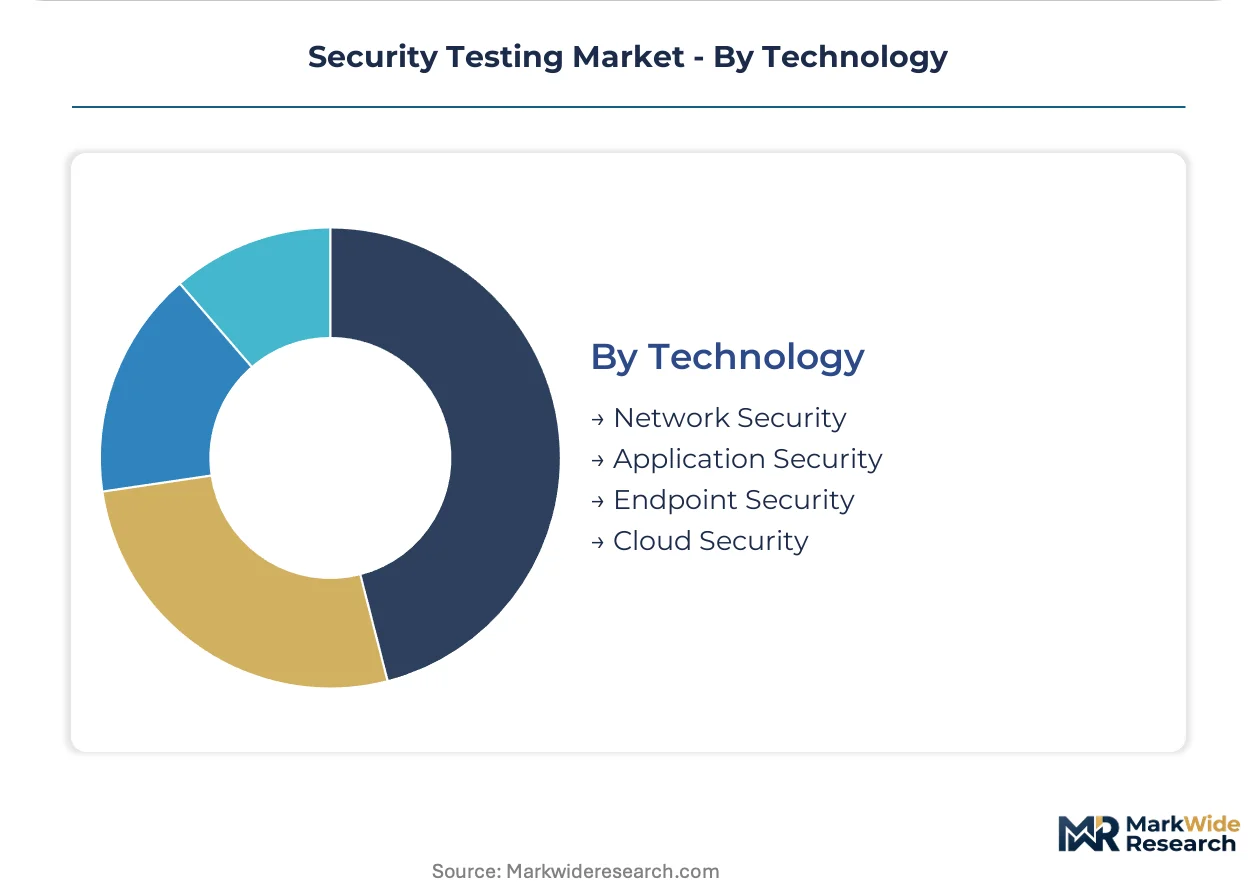
Maturity gradients separate established network security testing from emerging cloud-native validation protocols.
- Application Security:Static and dynamic analysis integrated into CI/CD workflows at build time. DevSecOps pipeline mandates from federal procurement standards concentrate demand among United States software vendors, with testing shifting left to prevent vulnerabilities from reaching production.
- Cloud Security:Specialized penetration testing for containerized workloads, serverless functions, and identity misconfigurations. Fortune 500 technology stacks in the United States drive procurement as multi-cloud deployments complicate attack-surface visibility.
- Network Security:Perimeter and segmentation testing for on-premises and hybrid infrastructure.
- Endpoint Security:Device-level validation against ransomware and lateral movement techniques.
Application Security dominates current procurement volume. Cloud Security shows the steepest expansion trajectory as distributed architectures proliferate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal procurement pipelines anchor global demand for adversarial simulation and red-team services. Defense contractors and civilian agencies sustain the largest concentrated budgets for continuous validation platforms. Geographic procurement patterns diverge sharply based on regulatory exposure and critical infrastructure density.
United States
Federal agencies and defense contractors drive concentrated procurement for FedRAMP authorization and red-team operations. SEC disclosure rules for material cyber incidents reshape board-level testing specifications across publicly traded entities. The Washington DC-Baltimore corridor hosts the densest cluster of specialized boutiques serving classified program requirements.
Germany
Automotive OEMs and industrial automation firms expand security testing budgets for connected vehicle platforms and operational technology environments. The EU NIS2 Directive compels critical infrastructure operators in energy and transport to conduct quarterly third-party assessments. Munich and Stuttgart industrial clusters concentrate demand for compliance-integrated testing with auditable evidence deliverables.
United Kingdom
Financial services institutions in the City of London embed continuous validation into DevSecOps pipelines for trading platforms. The UK National Cyber Security Centre mandates standardized adversarial testing for critical national infrastructure operators. London's technology corridor attracts specialized cloud penetration testing providers serving Fortune 500 European headquarters.
Japan
Manufacturing conglomerates and semiconductor fabricators prioritize supply-chain security testing for vendor risk management programs. METI guidelines for critical infrastructure protection elevate demand for operational technology assessment capabilities. The Tokyo-Osaka industrial corridor concentrates procurement for hybrid cloud and on-premises security validation services.
Singapore
Regional headquarters for multinational banks and commodity trading firms drive demand for compliance-integrated testing across ASEAN operations. The Monetary Authority of Singapore's technology risk management guidelines mandate regular third-party security assessments for financial institutions. The city-state's data center cluster attracts specialized cloud security testing providers serving Asia-Pacific multi-cloud deployments.
Security Testing Market Key Industry Players
Established producers occupy the standard tier; emerging entrants pursue cloud-native automation and AI-augmented adversarial techniques. The vendor base stratifies across three maturity tiers: global platforms with managed service bundles, specialized boutiques with certified practitioner depth, and automation-first challengers with SaaS delivery models. Dominant competitive moves include strategic partnerships for DevSecOps pipeline integration and geographic expansion through compliance certification reciprocity.
Within the specialized boutique tier, SpecterOps and IOActive exemplify practitioner-scarce, high-touch service delivery models. Rapid7 and Coalfire occupy positions across the platform-managed service boundary, representing hybrid sourcing archetypes that bundle continuous validation with detection capabilities. NetSPI anchors the cloud-native specialization vector, reflecting Fortune 500 technology stack penetration strategies.
| Leading Market Players |
|---|
| SpecterOps |
| IOActive |
| DeepStrike |
| BreachLock |
| Rapid7 |
| Coalfire |
| NetSPI |
| Cigniti Technologies |
| Bishop Fox |
| Others |
Cost & Logistics Intelligence
FedRAMP authorization requirements in the United States gate both qualified practitioner supply and premium-tier pricing access for security testing services. Compliance-integrated testing that produces auditable evidence commands pricing multiples over standalone vulnerability assessments, while certified ethical hacker scarcity constrains service delivery capacity.
Pricing Analysis
Certified practitioner compensation pass-through dominates service pricing structures, with credentialed ethical hacker scarcity compressing margins for boutique penetration testing firms. Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized red-team operations from automated vulnerability scanning and baseline compliance audits. Price differentiation hinges on certification depth and liability coverage limits. Cost compression in automated scanning tiers is intensifying because low-cost tool proliferation erodes baseline assessment pricing power. Mid-market enterprises exhibit highest price sensitivity, while United States federal contractors demonstrate lowest sensitivity due to mandate-driven procurement.
Supply Chain Analysis
Domestic-content mandates for classified program access reshape sourcing patterns for security testing talent and tooling. Practitioner supply concentrates in the United States, United Kingdom, and Germany where certification ecosystems and clearance pathways develop credentialed ethical hackers. Service delivery draws from cloud infrastructure provisioning, specialized exploitation frameworks, and continuous validation platform licensing. Single-source vulnerability in practitioner pipeline depth threatens capacity scaling. Distribution runs through direct enterprise sales for high-touch engagements and managed service provider channels for mid-market subscription bundles.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market represents a late-cycle quality story as SEC disclosure rules and EU NIS2 mandates shift procurement specifications toward premium compliance-integrated testing with auditable evidence deliverables.
For Market Incumbents: Lock in practitioner talent through specialized training pipelines and clearance sponsorship programs to defend against boutique firm poaching. Deepen vertical integration into cloud-native validation tooling to capture recurring revenue from DevSecOps pipeline embedding. FedRAMP authorization reciprocity expansion represents the priority certification investment for federal contractor wallet retention.
For New Entrants and Emerging Players: EU NIS2 Directive in Europe opens a window for compliance-integrated testing specialization targeting critical infrastructure operators in energy and transport verticals. Healthcare connected medical device manufacturers present the most penetrable segment given FDA cybersecurity guidance recency and incumbent coverage gaps. Cloud-native penetration testing for multi-cloud architectures offers the strongest go-to-market angle against legacy platform incumbents.
For Investors and Strategic Acquirers: Roll-up economics work for specialized boutiques with certified practitioner depth because scarcity-driven pricing power sustains margin profiles through consolidation. Target acquisition archetypes include cloud-native penetration testing specialists and attack-surface management platform developers. Watch for AI-generated attack technique proliferation as the inflection signal indicating human-led adversarial testing premium compression versus automated platform scalability.
| Strategic Initiative | Industry Significance |
|---|---|
| DevSecOps Pipeline Integration | Embedding security testing into CI/CD workflows captures recurring revenue from software vendors facing federal procurement mandates. |
| FedRAMP Authorization Expansion | Compliance certification reciprocity unlocks federal contractor procurement pipelines concentrated in the Washington DC-Baltimore corridor. |
| Attack-Surface Management Platform Launch | Continuous external reconnaissance capabilities absorb budgets from point-in-time penetration testing among United States technology firms. |
| Healthcare Compliance Specialization | FDA cybersecurity guidance alignment creates differentiated positioning for connected medical device manufacturer testing demand. |
| Practitioner Certification Pipeline Investment | Ethical hacker scarcity mitigation secures service delivery capacity for premium-tier red-team operations against boutique competitors. |
Research Approach
Multiple input streams — primary interviews with CISOs and security procurement officers, regulatory filing analysis, and vendor contract disclosure review — were reconciled to construct market estimates. Conversations with DevSecOps platform engineers, federal contracting officers, healthcare technology compliance leads, and managed detection service heads informed demand-side validation. Secondary sources included SEC 10-K cybersecurity disclosures, FedRAMP authorization databases, EU NIS2 implementation guidance, and FDA cybersecurity guidance documents. Bottom-up service provider revenue aggregation and top-down enterprise security spending allocation were cross-referenced for triangulation.
Historical spending patterns were cross-referenced against expert panel input regarding procurement specification shifts. The analytical framework modeled segmentation across service type, deployment model, end-user vertical, and technology layer throughout the forecast period. CAGRs were derived from regression analysis against regulatory mandate implementation timelines and cloud adoption curves. Forecast inputs incorporated FedRAMP authorization pipeline depth, certified practitioner graduation rates, and DevSecOps tooling penetration metrics.
Revisions become necessary when regulatory implementation delays, practitioner supply expansion through certification program scaling, or AI-driven testing automation breakthroughs materialize outside modeled assumptions. Forecasts reflect documented assumptions regarding compliance mandate enforcement intensity and enterprise cloud migration velocity. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Data Protection As a Service (Dpaas) Market
Security Software
Asia-Pacific Smart Doorbell Market
Security Software
Data Loss Prevention Market
Security Software
Data Privacy Software Market
Security Software
Identity Verification Software Market
Security Software
SSL Inspection Solution Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Social Media Security Market
Security Software
Messaging Security Market
Security Software
Mass Notification System Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
Global Background Check Software Market
Security Software
Network Video Recorder (NVR) Market
Security Software
Global Data Classification Market
Security Software
North America Secure Access Service Edge Market
Security Software
Global Data Masking Market