
 Social Media Security Market | 2026-2036
Social Media Security Market Size, Share, and Industry Trends Forecast 2026-2036
Social Media Security Market Intelligence
ISO 27001 certification is rotating as the baseline qualification for vendor selection in enterprise procurement cycles. Palo Alto Networks leverages its integrated platform architecture to anchor large-scale deployments across cloud-native environments. Trend Micro sustains competitive relevance through deep specialization in threat intelligence feeds tailored to social media vectors. Sophos Group differentiates via channel-controlled distribution that reaches mid-market clients without direct sales overhead.
Social media security encompasses technical systems designed to monitor, detect, and neutralize threats across public social platforms including unauthorized account access, brand impersonation, data exfiltration, and coordinated misinformation campaigns. These systems deploy machine-learning classifiers, natural language processing engines, and real-time API monitoring to enforce policy across fragmented channel ecosystems. Threat Intelligence solutions within the Solution Type segment command premium pricing due to the specialized data engineering required for signal validation across noisy social feeds. Cloud-Based deployment modes now lead volume uptake as enterprises abandon on-premises infrastructure for elastic, API-native architectures that match platform scale.
The EU AI Act and GDPR impose algorithmic transparency and data processing constraints on automated content moderation tools sold into Europe. The SEC's cybersecurity disclosure rules and HIPAA's breach notification standards extend compliance obligations to social channels for regulated US industries. Stakeholders must monitor how platform API policy changes by Meta, X, and ByteDance reshape data access economics for third-party security vendors.
Market Dynamics
API policy volatility at major platforms is compressing vendor margins and forcing architectural pivots toward synthetic data pipelines and federated learning models that reduce dependency on direct platform access.
Growth Catalysts
- GDPR and EU AI Act mandates:European enterprises must deploy algorithmic transparency tools for automated content moderation, accelerating procurement of explainable AI security stacks.
- Financial services digitization:Banks and insurers now monitor social channels for brand impersonation and fraudulent account schemes, expanding addressable spend.
- Real-time threat detection:Natural language processing engines processing multilingual social feeds at sub-second latency enable preemptive neutralization of coordinated misinformation campaigns.
Market Restraints
- Platform API access restrictions:Meta, X, and ByteDance impose tiered pricing and rate limits that inflate data acquisition costs for third-party security vendors.
- Cloud infrastructure concentration:Overreliance on AWS, Azure, and GCP for elastic compute creates single-point-of-failure exposure during regional outages.
- Signal-to-noise degradation:Encrypted messaging migrations and ephemeral content formats degrade monitoring efficacy for legacy detection systems.
Strategic Opportunities
- Mid-market channel expansion:Managed security service providers now bundle social media monitoring into broader cyber offerings, opening SMB segments previously unreachable through direct enterprise sales.
- Deepfake detection convergence:Integration of synthetic media forensics with social monitoring platforms addresses emerging video-based impersonation vectors.
- India's Digital Personal Data Protection Act:Compliance mandates for social platforms operating in India create localized deployment requirements that favor regional system integrators.
Industry Challenges
- ISO 27001 certification timelines:Vendor qualification cycles now stretch 9-14 months as enterprises demand evidence of continuous control monitoring.
- Multilingual NLP engineering scarcity:Talent capable of training classifiers for low-resource languages commands premium compensation, constraining product roadmap velocity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Social Media Security Market |
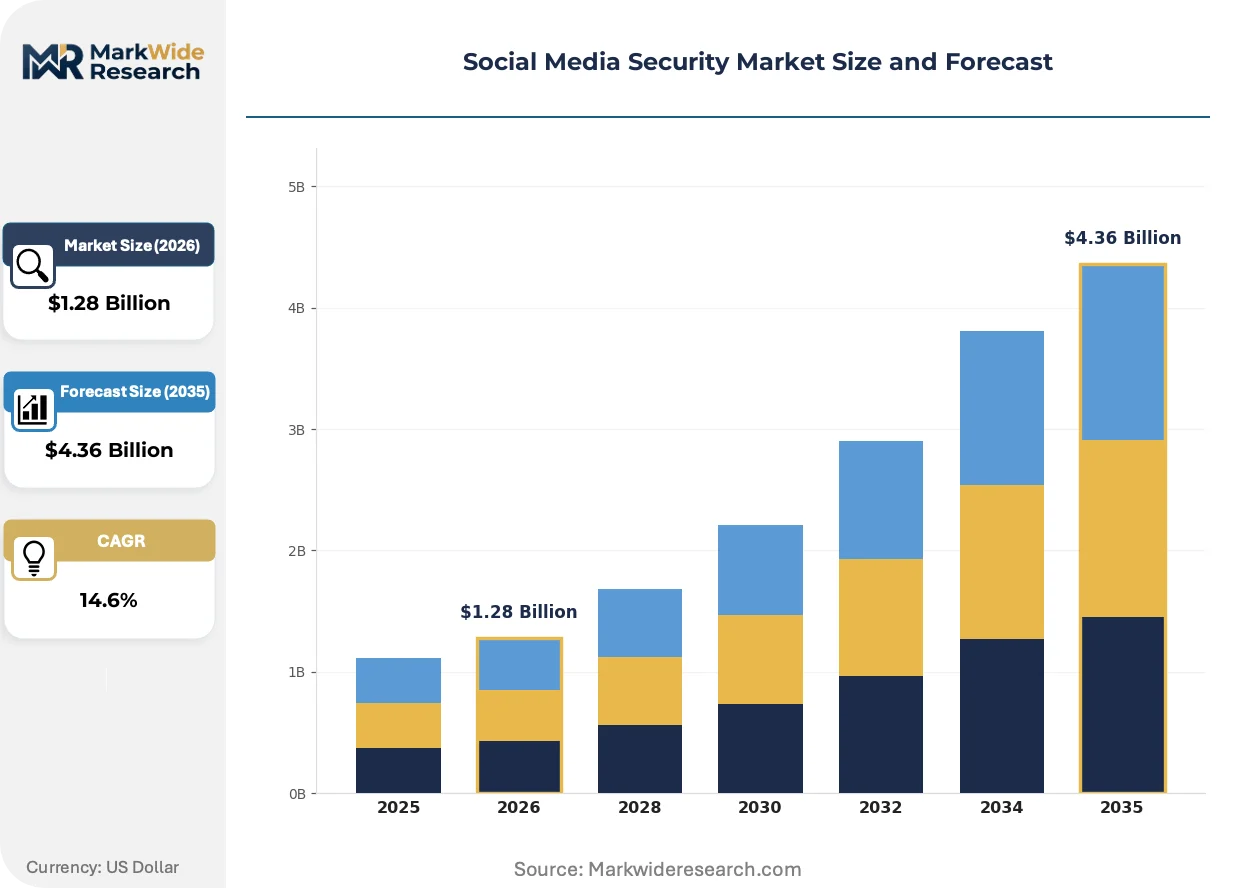
| Market Size in 2026 | $1.28 Billion |
| Market Size in 2035 | $4.36 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Threat Intelligence, Access Management, Data Loss Prevention, Identity Verification, Account Protection, Content Filtering Deployment Mode: Cloud-Based, On-Premises, Hybrid, Hosted, Dedicated, Multi-Tenant Use Case: Brand Monitoring, Fraud Detection, Privacy Management, Incident Response, Compliance Enforcement, User Behavior Analysis Client Type: Enterprises, Media Agencies, Government Agencies, E-Commerce Platforms, Educational Institutions, Nonprofit Organizations |
| Companies Covered | Palo Alto Networks, Trend Micro, Proofpoint, Check Point Software Technologies, McAfee, SolarWinds, Digital Shadows, Sophos Group, KnowBe4, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Social Media Security Market Strategic Shifts & Innovations
Edge-deployed inference architectures are displacing centralized cloud processing for latency-sensitive detection tasks. Platform-native security tooling is fragmenting procurement patterns. Synthetic training data generation is reducing dependency on historical breach datasets.
On-device machine learning for social media threat detection is miniaturizing. Financial services deploy these models directly on employee smartphones and tablets to intercept phishing links before cloud sync. This compression eliminates round-trip latency to centralized security operations centers while satisfying data residency constraints.
The EU AI Act's risk-based classification system imposes documentation burdens on high-risk automated moderation tools. Vendors must maintain technical files and conformity assessments for systems deployed in European Union member states. Enterprise buyers now require contractual indemnification for algorithmic bias liabilities, shifting compliance costs upstream.
Subscription fatigue among CISOs is compressing vendor consolidation timelines. Fortune 500 security teams now demand unified platforms covering endpoint, cloud, and social channels rather than point solutions. This preference shift most visibly affects procurement patterns in United States federal agencies and healthcare systems subject to HIPAA breach notification standards.
Social Media Security Market Segmentation
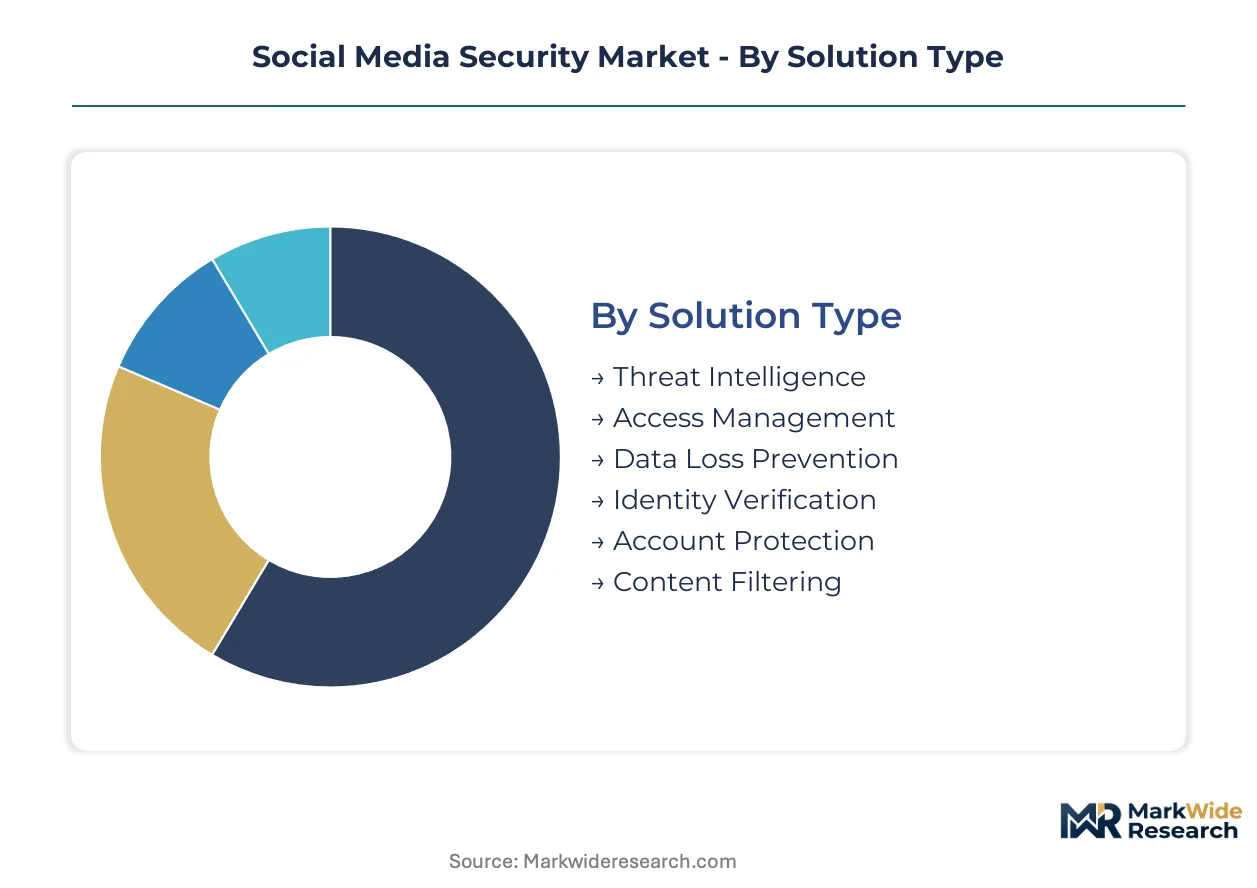
Social media security procurement patterns diverge sharply across solution architectures and client risk profiles. Deployment constraints imposed by GDPR and the EU AI Act reshape how vendors configure product tiers for regulated versus unregulated buyers.
Solution Type:
GDPR's algorithmic transparency mandates and HIPAA's breach notification standards create divergent certification requirements across solution categories.
- Threat Intelligence:Machine-learning classifiers process multilingual social feeds to validate threat signals against noisy data streams. Financial services firms in the United States now deploy these systems for real-time detection of coordinated misinformation campaigns targeting brand integrity.
- Access Management:OAuth token monitoring and privileged credential vaulting prevent unauthorized account takeover across fragmented platform ecosystems. European enterprises subject to EU AI Act documentation burdens favor vendors offering explainable AI audit trails for automated access decisions.
- Data Loss Prevention:API-native scanning engines intercept sensitive data exfiltration via direct messages and ephemeral content formats.
- Identity Verification:Biometric liveness detection and document authentication reduce synthetic identity fraud in social platform onboarding flows.
- Account Protection:Behavioral biometrics and device fingerprinting detect anomalous login patterns indicative of credential stuffing attacks.
- Content Filtering:Natural language processing engines enforce policy across user-generated content at sub-second latency for high-volume publishers.
Threat Intelligence handles the majority of throughput; Access Management is gaining share fastest among regulated industries.
Deployment Mode:
Cost tier differentiation separates elastic API-native architectures from fixed-capacity infrastructure commitments.
- Cloud-Based:Elastic compute architectures match platform API scale without capital-intensive infrastructure provisioning. Fortune 500 companies in the United States now abandon on-premises stacks for consumption-based pricing that aligns with seasonal campaign volumes.
- On-Premises:Air-gapped deployments satisfy data residency constraints for classified government workloads and healthcare systems processing PHI under HIPAA. German federal agencies mandate sovereign infrastructure for social media monitoring of domestic threat actors.
- Hybrid:Split processing routes sensitive analytics to private infrastructure while leveraging public cloud for bulk storage.
- Hosted:Single-tenant managed services reduce operational overhead for mid-market clients lacking dedicated security operations centers.
- Dedicated:Isolated hardware instances address latency requirements for sub-100ms threat response in high-frequency trading environments.
- Multi-Tenant:Shared infrastructure economics enable price-competitive entry points for educational institutions and nonprofit organizations.
Cloud-Based deployments capture the dominant share of new procurement; Hybrid architectures show the steepest expansion trajectory among organizations navigating cross-border data transfer restrictions.
Use Case:
Application maturity varies by vertical risk exposure and regulatory enforcement intensity.
- Brand Monitoring:Natural language processing engines track impersonation accounts and trademark infringement across multilingual social feeds. Media agencies in France deploy these tools to detect coordinated inauthentic behavior targeting luxury brand reputation.
- Fraud Detection:Transaction pattern analysis and synthetic identity scoring intercept payment fraud originating from compromised social accounts. E-commerce platforms operating in India face escalating refund scam volumes that demand real-time behavioral anomaly detection.
- Privacy Management:Automated data subject request fulfillment and consent orchestration reduce GDPR compliance operational burden.
- Incident Response:Triage automation and forensic evidence preservation accelerate breach containment timelines for regulated industries.
- Compliance Enforcement:Policy engines map social content against SEC disclosure rules and FINRA advertising guidelines for financial services.
- User Behavior Analysis:Insider threat detection models identify data exfiltration precursors in employee social media activity.
Brand Monitoring processes the highest query volumes; Fraud Detection is expanding most quickly as payment integration deepens across social commerce platforms.
Client Type:
Customer procurement sophistication dictates solution packaging and sales channel economics.
- Enterprises:Unified platform demands spanning endpoint, cloud, and social channels compress vendor consolidation timelines. United States federal agencies now require ISO 27001 certification as baseline qualification for procurement cycles stretching 9-14 months.
- Government Agencies:Classified threat intelligence feeds and sovereign infrastructure mandates dominate procurement criteria for national security applications. India's Digital Personal Data Protection Act creates localized deployment requirements favoring regional system integrators.
- Media Agencies:Campaign-conditional pricing and creative workflow integration prioritize ease of deployment over deep customization.
- E-Commerce Platforms:Transaction volume-based pricing aligns security spend with monetization events rather than user counts.
- Educational Institutions:Budget constraints and limited security staffing drive preference for managed detection and response bundles.
- Nonprofit Organizations:Grant-funded procurement cycles favor open-source integrations and volunteer-accessible administration interfaces.
Enterprises dominate absolute spend; Government Agencies are climbing the fastest on share as classified social media monitoring programs expand.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Government cybersecurity disclosure mandates and platform liability statutes are accelerating procurement across national markets. Sovereign data residency requirements reshape deployment architectures for multinational vendors. Compliance fragmentation creates localized competitive advantages for domestic system integrators.
United States
SEC cybersecurity disclosure rules and HIPAA breach notification standards compel Fortune 500 firms to expand social channel monitoring budgets. Federal agencies now mandate ISO 27001 certification for procurement cycles stretching 9-14 months. The Washington DC-Arlington corridor hosts classified threat intelligence programs serving national security applications.
Germany
Bundesamt für Sicherheit in der Informationstechnik (BSI) guidelines enforce sovereign infrastructure mandates for domestic threat actor monitoring. The EU AI Act's risk-based classification system imposes documentation burdens on automated moderation tools deployed across German enterprises. Munich and Frankfurt clusters concentrate financial services security procurement for banking and insurance sectors.
United Kingdom
Financial Conduct Authority (FCA) operational resilience requirements extend to social media channels for payment institutions and investment platforms. The Online Safety Bill creates platform accountability frameworks that downstream security vendors must integrate. London's Square Mile anchors demand from hedge funds and asset managers monitoring brand impersonation vectors.
India
The Digital Personal Data Protection Act mandates localized deployment requirements for social platforms processing citizen data. Reserve Bank of India (RBI) cybersecurity frameworks now explicitly cover social channel fraud detection for payment systems. Bengaluru and Hyderabad clusters host regional system integrators capturing compliance-driven procurement from e-commerce and fintech operators.
France
Commission Nationale de l'Informatique et des Libertés (CNIL) enforcement actions elevate algorithmic transparency requirements for automated content moderation. ANSM pharmaceutical advertising guidelines extend to social influencer monitoring for healthcare compliance. Paris anchors luxury brand security spending as media agencies deploy multilingual NLP engines for trademark infringement detection.
Social Media Security Market Key Industry Players
Listed leaders compete with private specialists across platform integration depth and threat intelligence specialization. The vendor base concentrates around three strategic tiers: integrated cybersecurity platforms spanning endpoint, cloud, and social channels; pure-play social media security specialists with deep API-native architectures; and managed security service providers bundling monitoring into broader cyber offerings. Dominant competitive moves include strategic partnerships with major social platforms and portfolio diversification into adjacent fraud detection capabilities.
Within the integrated platform tier, Palo Alto Networks and Check Point Software Technologies exemplify scale-driven consolidation strategies. Trend Micro and Sophos Group occupy positions emphasizing threat intelligence specialization and channel-controlled distribution respectively. These archetypes reflect the market's bifurcation between unified platform demands from enterprise buyers and modular point-solution preferences among mid-market clients lacking dedicated security operations centers.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Trend Micro |
| Proofpoint |
| Check Point Software Technologies |
| McAfee |
| SolarWinds |
| Digital Shadows |
| Sophos Group |
| KnowBe4 |
| Others |
Cost & Logistics Intelligence
Capacity reservation contracts with tiered API access commitments lock in both platform data streams and predictable unit economics for social media security vendors. European enterprises subject to GDPR algorithmic transparency mandates now demand multi-year pricing visibility that bundles explainable AI audit trails with base platform fees.
Pricing Analysis
Certification level creates the primary spread between vendor tiers, with ISO 27001-certified platforms commanding premium positioning over uncertified alternatives. Subscription-based SaaS pricing dominates, stratifying across premium threat intelligence bundles, standard access management modules, and economy-tier content filtering tiers. Cost compression in the economy tier is intensifying because platform API rate limits inflate data acquisition overhead. Mid-market clients lacking dedicated security operations centers exhibit highest price sensitivity, while Fortune 500 federal contractors accept premium positioning for sovereign infrastructure guarantees.
Supply Chain Analysis
Just-in-time talent acquisition for multilingual NLP engineering creates supply bottlenecks that strategic stockpiling of pre-trained model architectures can partially offset. Core technology development concentrates in the United States, Israel, and the United Kingdom, with India emerging as a hub for annotation labor and regional system integration. The vendor ecosystem draws from cloud infrastructure providers, threat intelligence data brokers, and academic research partnerships. Single-source vulnerability to AWS, Azure, and GCP regional outages represents the dominant structural risk. Distribution runs through direct enterprise sales, managed security service providers, and channel-controlled partner networks.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics now hinge on API interoperability as Meta, X, and ByteDance fragment data access economics, forcing architectural pivots toward synthetic data pipelines and federated learning models.
For Market Incumbents: Consolidate through backward integration into proprietary threat intelligence collection networks that reduce dependency on platform API access. Acquire specialist firms with deep multilingual NLP engineering capabilities to defend against talent scarcity constraints. Anchor large-scale deployments through unified platform architectures spanning endpoint, cloud, and social channels. For New Entrants and Emerging Players: Differentiate on edge-deployed inference architectures that eliminate round-trip latency to centralized security operations centers. Target India's compliance-driven procurement under the Digital Personal Data Protection Act, where localized deployment requirements favor regional system integrators. Pursue managed security service provider partnerships as the primary go-to-market angle for mid-market channel expansion. For Investors and Strategic Acquirers: Capital is best deployed toward pure-play social media security specialists with API-native architectures and deep platform integration moats. Long-term viability across a five-to-ten year window rests on vendors' ability to navigate algorithmic transparency mandates without sacrificing detection latency. Watch for platform API policy changes as the critical inflection signal that reshapes data access economics.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration Partnership | Deep API-native architectures reduce dependency on volatile third-party data access economics. |
| Acquisition of Specialist Firm | Multilingual NLP engineering capabilities address talent scarcity constraining product roadmap velocity. |
| Geographic Expansion | Localized deployment in India captures compliance-driven procurement under the Digital Personal Data Protection Act. |
| Product Launch | Edge-deployed inference miniaturizes threat detection for financial services mobile deployments. |
| Strategic Partnership | Managed security service provider bundling opens SMB segments previously unreachable through direct sales. |
Research Approach
A spread of perspectives from chief information security officers, platform engineering leads, threat intelligence analysts, and regulatory compliance officers converged on the working assumptions driving this analysis. Primary fieldwork combined structured interviews with secondary validation against SEC cybersecurity disclosure filings, EU AI Act implementation guidance, and hyperscaler API policy documentation. Bottom-up deployment estimates and top-down market sizing triangulated on convergent figures across the analysis window.
Segmentation dimensions modeled include solution type, deployment mode, use case, client type, and regional regulatory cluster. CAGRs were derived from trend extrapolation anchored in documented procurement cycles and platform adoption patterns. Forecast inputs incorporated API policy volatility scenarios and compliance mandate enforcement timelines.
Material uncertainties — platform API access restrictions, encrypted messaging migrations, and sovereign data residency requirement shifts — sit outside the modeled envelope. Forecasts reflect assumptions about regulatory enforcement intensity and threat actor tactic evolution. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Security Operation Center As a Service Market
Security Software
IAM Security Services Market
Security Software
Content Protection and Watermarking Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Asia Pacific Anti Money Laundering Solutions Market
Security Software
Global IMSI Catcher Market
Security Software
Ultra-Secure Smartphone Market
Security Software
Passport Reader Market
Security Software
Employee Computer Monitoring Software Market
Security Software
Global Electronic Passports Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Italy Endpoint Detection and Response Market
Security Software
Cloud Security Software Market
Security Software
Europe User Provisioning Market
Security Software
Sound Masking Systems Market
Security Software
Privileged Identity Management Market