
 Cyber Security Market | 2026-2036
Cyber Security Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Security Market Intelligence
Mid-market enterprises are rotating toward managed security services as their primary procurement archetype, displacing large financial institutions that historically anchored sector spending. Palo Alto Networks leverages extensive cloud-native platform integration to capture this shift. CrowdStrike sustains endpoint detection leadership through AI-driven threat intelligence pipelines. Check Point Software Technologies anchors network security dominance with deep firewall specialization across hybrid deployments.
Cyber security encompasses technologies, processes, and controls designed to protect systems, networks, and data from digital attacks, with core functional parameters spanning encryption strength, detection latency, and incident response time measured in milliseconds. Its primary commercial purpose is risk mitigation for organizations handling sensitive information or critical infrastructure operations. Managed security services and cloud deployment configurations represent the fastest-expanding margin pools as organizations outsource complexity. On-premises firewall and antivirus segments remain mature revenue bases with slower expansion curves but stable renewal economics.
The EU AI Act and NIS2 Directive reshape European procurement standards by mandating incident reporting timelines and supply-chain security attestations. In the United States, NIST zero-trust architecture requirements and SEC cyber disclosure rules compel publicly traded entities to accelerate security modernization. Stakeholders must monitor regulatory divergence between jurisdictions to align product certification roadmaps with divergent compliance timelines.
Market Dynamics
Mid-market enterprises are rotating toward managed security services as their primary procurement archetype, displacing large financial institutions that historically anchored sector spending. This shift compresses sales cycles and elevates platform consolidation over point-solution procurement.
Growth Catalysts
- Zero-trust mandates:NIST architecture requirements and SEC cyber disclosure rules compel publicly traded entities to accelerate security modernization across federal and corporate networks.
- Cloud migration velocity:Distributed workforces and SaaS proliferation expand attack surfaces, forcing organizations to adopt cloud-native security platforms with integrated threat intelligence.
- EU regulatory tightening:The AI Act and NIS2 Directive mandate incident reporting timelines and supply-chain security attestations, creating compliance-driven procurement urgency.
Market Restraints
- Skilled labor scarcity:Shortages of certified security architects and incident responders constrain service delivery capacity across managed security providers.
- Vendor consolidation risk:Platform concentration among dominant cloud security providers creates single-point-of-failure exposure for enterprise customers.
- Legacy infrastructure drag:On-premises firewall and antivirus investments with stable renewal economics slow full-stack modernization timelines.
Strategic Opportunities
- Operational technology security:Manufacturing and energy infrastructure operators seek specialized ICS/SCADA protection as industrial digitization accelerates.
- AI-powered threat detection:Machine learning-driven behavioral analytics converge with automated response orchestration to reduce mean time to containment.
- SMB channel expansion:Managed service providers and value-added resellers unlock underpenetrated small and medium business segments with bundled security offerings.
Industry Challenges
- Certification fragmentation:Divergent national security standards and industry-specific frameworks complicate product certification roadmaps for multi-jurisdiction vendors.
- Integration complexity:Security operations centers struggle to normalize telemetry across disparate toolsets, degrading correlation accuracy and alert fidelity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Security Market |
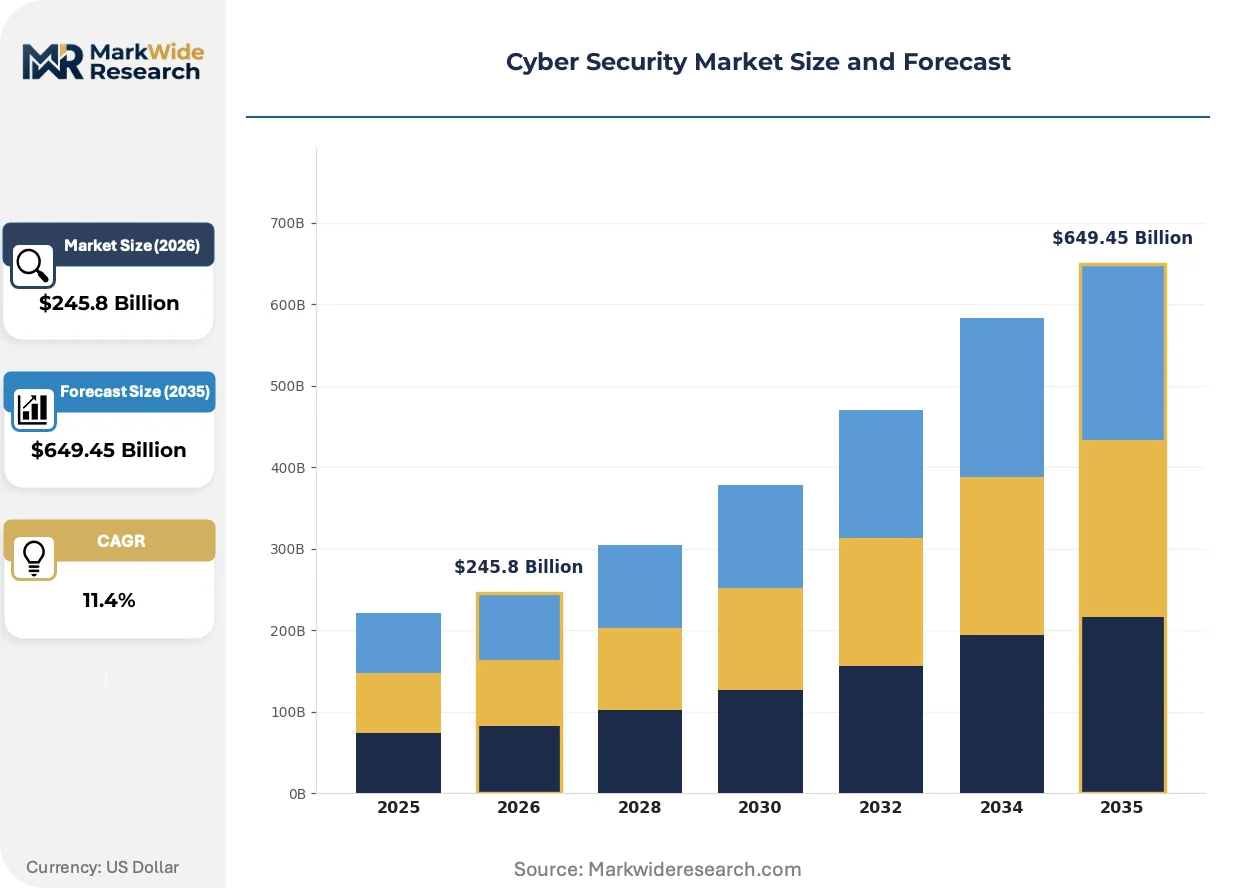
| Market Size in 2026 | $245.8 Billion |
| Market Size in 2035 | $649.45 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Antivirus, Intrusion Detection, Encryption Service Type: Consulting, Managed Security, Incident Response, Identity Management End User: Government, Financial Institutions, Healthcare, Educational Institutions Deployment: On-Premises, Cloud, Hybrid, Mobile |
| Companies Covered | Cloudflare, Cisco Systems, Palo Alto Networks, Microsoft Security, Check Point Software Technologies, CrowdStrike, Zscaler, IBM Security, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Security Market Strategic Shifts & Innovations
Security delivery models are converging around platform consolidation and intelligence-driven automation. Vendors race to embed predictive capabilities while buyers demand measurable risk reduction.
Extended detection and response platforms are displacing siloed endpoint, network, and identity tools through unified telemetry pipelines and automated remediation workflows. Mid-market enterprises adopt these consolidated stacks fastest, trading best-of-breed flexibility for operational simplicity. The displacement compresses point-solution vendor margins while elevating platform-native integration as a primary selection criterion.
Europe's NIS2 Directive mandates 24-hour incident reporting and supply-chain security attestations for critical infrastructure operators. Member states must transpose these requirements into national law by October 2024, forcing security vendors to retool certification processes. Financial services and energy verticals face the steepest compliance burdens, accelerating procurement of pre-certified managed services.
Buyers now demand consumption-based pricing tied to measurable security outcomes rather than perpetual licenses. Managed security service providers respond with tiered offerings aligning fees to detected threat volumes and response times. This shift is most visible in United States federal contracting, where outcome-based service level agreements increasingly displace traditional technology acquisition models.
Cyber Security Market Segmentation
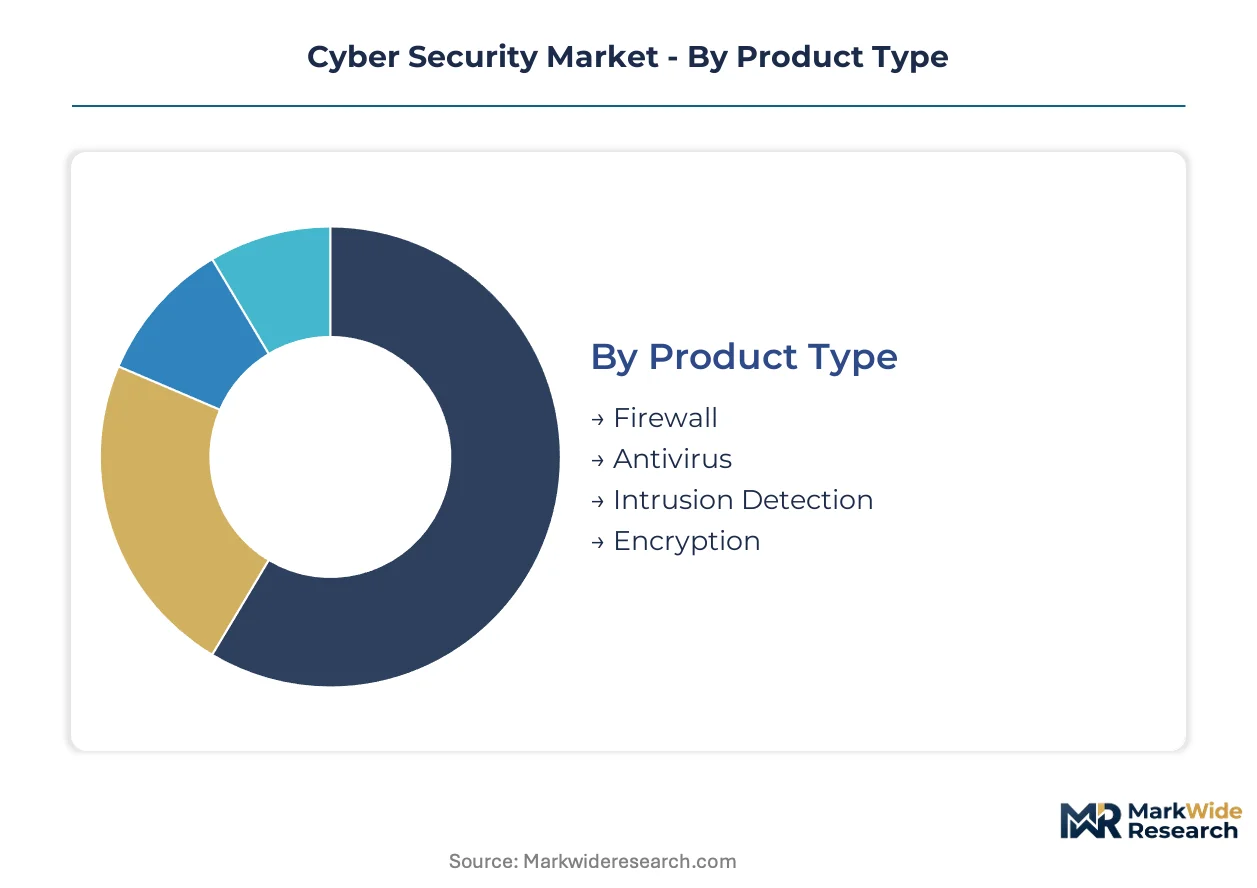
Cyber security procurement splits across four fundamental dimensions that determine vendor engagement models and margin structures. Product and service configurations dictate whether buyers favor perpetual licenses or consumption-based contracts. Deployment architecture and end-user verticals shape integration complexity and compliance requirements.
Product Type:
Channel mix varies sharply by product category, with firewalls and antivirus flowing through established reseller networks while encryption and intrusion detection increasingly route through direct enterprise sales and managed service providers.
- Firewall:Deep packet inspection engines and next-generation application awareness form the technical core. United States federal agencies drive replacement cycles as NIST zero-trust mandates obsolete perimeter-centric architectures. Palo Alto Networks and Check Point Software Technologies anchor this segment with hybrid cloud integration capabilities.
- Antivirus:Signature-based detection converges with behavioral heuristics and machine learning classifiers. Small and medium businesses sustain volume through bundled endpoint protection suites, though margin compression accelerates as Microsoft Defender displaces standalone solutions.
- Intrusion Detection:Network traffic analysis and anomaly correlation engines detect lateral movement patterns. Critical infrastructure operators in energy and manufacturing verticals generate specialized demand for industrial protocol-aware variants.
- Encryption:Data-at-rest and data-in-transit protection spans symmetric, asymmetric, and quantum-resistant algorithm implementations. Financial institutions facing SEC disclosure rules prioritize database and communications encryption with auditable key management.
Firewall dominates installed base. Encryption is where expansion concentrates.
Service Type:
Cost tier stratification separates high-touch consulting engagements from standardized managed service subscriptions, with incident response commanding premium pricing during active breach scenarios.
- Consulting:Risk assessment, architecture design, and compliance readiness engagements deliver project-based revenue. Large enterprises undergoing zero-trust transformations sustain demand for vendor-agnostic advisory services.
- Managed Security:24/7 security operations center monitoring, threat hunting, and vulnerability management delivered as subscription services. Mid-market enterprises represent the fastest-expanding customer archetype as internal staffing constraints force outsourcing decisions.
- Incident Response:Retainer and emergency breach containment services with forensic investigation capabilities. Ransomware frequency elevates procurement urgency, though episodic demand creates revenue volatility.
- Identity Management:Privileged access management, single sign-on orchestration, and zero-trust identity verification. SaaS proliferation and distributed workforces expand attack surfaces requiring continuous authentication enforcement.
Consulting anchors professional services revenue. Managed Security climbs the fastest as recurring models displace project work.
End User:
Application context determines threat model sophistication, with financial services and government verticals demanding certified solutions while healthcare and education prioritize cost-effective bundled protection.
- Government:Federal, state, and municipal agencies with classified and unclassified network segmentation requirements. United States procurement velocity accelerates under executive orders mandating zero-trust architecture adoption.
- Financial Institutions:Banks, insurers, and payment processors subject to SEC disclosure rules and PCI-DSS compliance frameworks. Real-time transaction monitoring and fraud detection integrate with core security stacks.
- Healthcare:Hospital systems, clinics, and medical device manufacturers balancing HIPAA compliance with clinical workflow continuity. Medical IoT expansion creates specialized endpoint protection requirements.
- Educational Institutions:K-12 districts and universities with constrained IT budgets and open network access policies. Ransomware targeting student data drives insurance-mandated security upgrades.
Financial Institutions command highest per-seat spending. Healthcare is gaining share fastest as medical digitization accelerates.
Deployment:
Maturity curves diverge across deployment modes, with on-premises infrastructure representing stable renewal economics while cloud-native architectures capture new security budget allocation.
- On-Premises:Hardware appliances and perpetual software licenses operating within customer data centers. Legacy firewall and antivirus investments sustain maintenance revenue though new purchase velocity decelerates.
- Cloud:SaaS-delivered security controls, cloud access security brokers, and workload protection platforms. Multi-cloud environments drive demand for unified policy orchestration across AWS, Azure, and Google Cloud.
- Hybrid:Integrated on-premises and cloud-native controls with consistent policy enforcement. Enterprise architects favor this architecture during multi-year modernization transitions.
- Mobile:Endpoint protection for smartphones, tablets, and field-deployed devices beyond traditional corporate perimeters. Bring-your-own-device policies and 5G connectivity expand attack surfaces requiring containerized security.
On-Premises dominates installed base. Cloud is where expansion concentrates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli cyber security exports flow into United States federal procurement channels and European critical infrastructure operators. German industrial automation vendors source threat detection systems from Israeli specialists. Japanese financial institutions import cloud-native security platforms from United States providers.
United States
Federal zero-trust mandates and SEC cyber disclosure rules drive procurement velocity across defense contractors and publicly traded entities. NIST architecture requirements compel security modernization across civilian agencies and military networks. The Washington DC-Baltimore corridor concentrates security operations centers serving federal clients.
Germany
Industrial digitization and automotive supply-chain security create specialized demand for operational technology protection. The EU NIS2 Directive mandates incident reporting timelines that German regulators enforce through BSI certification requirements. Munich and Stuttgart host clusters of industrial cyber security specialists serving manufacturing verticals.
United Kingdom
Financial services compliance and critical national infrastructure protection anchor procurement budgets. The National Cyber Security Centre sets assurance frameworks that vendors must satisfy for government contracts. London's financial district drives demand for real-time transaction monitoring and fraud detection integration.
Japan
Manufacturing supply-chain resilience and Olympic infrastructure legacy investments sustain enterprise security spending. METI guidelines on supply-chain cyber risk management compel tier-1 suppliers to upgrade protection standards. Tokyo and Osaka metropolitan areas concentrate security operations for multinational corporations.
Israel
Military technology spinoffs and venture capital depth generate specialized threat intelligence capabilities. The Israel National Cyber Directorate coordinates export licensing for dual-use security technologies. Tel Aviv's cyber security cluster supplies advanced persistent threat detection to NATO allies and Gulf states.
Cyber Security Market Key Industry Players
Listed leaders compete with private specialists across platform consolidation and managed service delivery. The vendor base organizes into three tiers: cloud-native platform providers, network security incumbents with hybrid capabilities, and endpoint detection specialists. Strategic moves center on portfolio diversification through acquisition and geographic expansion into regulated European markets.
Within the cloud-native platform tier, Cloudflare and Zscaler exemplify architecture approaches that displace hardware-centric deployments. Palo Alto Networks anchors the integrated platform archetype with extensive hybrid cloud integration capabilities. Check Point Software Technologies occupies a position in network security specialization with deep firewall expertise across enterprise deployments.
| Leading Market Players |
|---|
| Cloudflare |
| Cisco Systems |
| Palo Alto Networks |
| Microsoft Security |
| Check Point Software Technologies |
| CrowdStrike |
| Zscaler |
| IBM Security |
| Fortinet |
| Others |
Cost & Logistics Intelligence
Cloud-native security platform substitution for hardware appliances simultaneously shifts supply geography toward software development hubs and compresses pricing economics through SaaS delivery models. This displacement concentrates procurement leverage with hyperscale cloud providers while fragmenting vendor margins across consumption-based tiers.
Pricing Analysis
Next-generation AI-powered detection commands premium positioning over signature-based antivirus and first-generation firewalls now relegated to economy tiers. Three-tier pricing structure across premium, standard, and economy levels separates managed detection and response bundles from standalone endpoint agents and legacy perimeter tools. Price differentiation hinges on SOC automation depth and FedRAMP authorization status. Cost compression in the antivirus tier is intensifying because Microsoft Defender bundling eliminates standalone purchase justification. Small and medium businesses exhibit highest price sensitivity, while United States federal agencies accept premium positioning for zero-trust certified architectures.
Supply Chain Analysis
Trans-Pacific container availability constraints elevate inbound logistics costs for Israeli threat intelligence hardware and Taiwanese semiconductor components feeding security appliance manufacturing. Software development concentrates in Israel, United States, and India, while cloud infrastructure provisioning draws from hyperscaler data center networks across Virginia, Frankfurt, and Singapore. Raw material dependencies span advanced processors, specialized encryption accelerators, and rare earth elements for hardware security modules. Single-source vulnerability permeates the foundry layer where advanced node production rests on Taiwan Semiconductor Manufacturing capacity. Distribution runs through direct enterprise sales teams for large accounts and managed service provider channels for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cyber security platform economics now reward ecosystem orchestration over point-solution depth, as interoperability requirements under NIST zero-trust architecture force vendor consolidation decisions.
For Market Incumbents: Secure managed security service provider channel relationships before cloud-native competitors capture mid-market subscription flows. Invest in FedRAMP and StateRAMP certification pipelines to maintain federal procurement eligibility against emerging compliance barriers. Prioritize API-first architecture development that embeds threat intelligence into customer security operations center workflows, reducing switching costs that protect installed base revenue. For New Entrants and Emerging Players: Differentiate on operational technology security specialization targeting manufacturing and energy infrastructure operators underserved by IT-centric incumbents. Penetrate the German industrial automation supply chain through BSI certification and Munich-based channel partnerships. Pursue managed service provider white-label arrangements that accelerate customer acquisition without direct enterprise sales infrastructure. For Investors and Strategic Acquirers: The EU NIS2 Directive reshapes the acquisition landscape by elevating incident response capability valuations and compliance automation premiums. Five-to-ten-year viability favors platforms with unified telemetry architectures over point-solution vendors facing margin compression. Target acquisition archetypes include industrial protocol-aware detection specialists and identity verification automation providers. Monitor United States federal zero-trust implementation velocity as the primary demand inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and identity telemetry into consolidated security operations center workflows reducing tool sprawl. |
| Acquisition of Specialist Firm | Absorbs industrial control system expertise or quantum-resistant cryptography capabilities accelerating vertical penetration. |
| Geographic Expansion | Establishes European Union presence ahead of NIS2 Directive enforcement capturing compliance-driven procurement urgency. |
| Strategic Partnership | Aligns with hyperscaler marketplaces embedding security controls into cloud infrastructure provisioning workflows. |
| Product Launch | Introduces consumption-based managed detection pricing aligning vendor compensation with measurable threat containment outcomes. |
Research Approach
Two parallel data streams informed the analysis: structured primary interviews with chief information security officers, managed security service provider executives, federal procurement officers, and channel partner principals; and secondary validation against SEC 10-K cybersecurity risk disclosures, FedRAMP authorization databases, NIST publication repositories, and European Union official journal regulatory texts. Bottom-up triangulation across vendor revenue segmentation and top-down demand modeling from enterprise IT budget surveys converged on market sizing estimates.
Across the analysis window, forecasts reflect product type, service type, deployment architecture, and end-user vertical segmentation with regional adoption pattern differentiation. CAGRs derive from regression analysis against historical procurement velocity indexed to regulatory milestone timing and cloud migration penetration curves. Model inputs incorporate federal zero-trust mandate implementation schedules and EU NIS2 Directive transposition progress by member state.
Material uncertainties — geopolitical technology export restrictions, hyperscaler platform consolidation decisions, and quantum computing timeline acceleration — sit outside the modeled envelope. Forecasts reflect assumptions regarding sustained regulatory compliance investment and managed service outsourcing momentum. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Application Security Market
Cybersecurity
SSL VPN Market
Cybersecurity
China Ransomware Protection Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
North America Extended Detection and Response Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Cloud-Based IDS IPS Market