
 SSL Inspection Solution Market | 2026-2036
SSL Inspection Solution Market Size, Share, and Industry Trends Forecast 2026-2036
SSL Inspection Solution Market Analytics
Enterprise procurement of SSL inspection tools is tilting toward cloud-native delivery models, reshaping how vendors reach mid-market buyers. Palo Alto Networks leverages its platform consolidation strategy to anchor large enterprise deployments across hybrid environments. Zscaler competes through distributed cloud architecture that eliminates hardware dependency at branch locations. Cisco extends its incumbent network equipment relationships into recurring security subscriptions, controlling upgrade cycles within installed bases.
SSL inspection solutions are network security appliances and software modules that decrypt, analyze, and re-encrypt TLS/SSL traffic in real time, typically processing throughput from 1 Gbps to 100+ Gbps depending on enterprise scale, to detect malware, data exfiltration, and policy violations hidden within encrypted channels. Cloud-based deployment is capturing the fastest expansion as organizations retire on-premises appliances in favor of elastic capacity and reduced capital expenditure. BFSI end users sustain premium pricing for high-assurance inspection due to regulatory audit requirements and transaction volume sensitivity. API-level integration is emerging as a margin-rich specialization where vendors embed inspection logic directly into application workflows rather than network paths.
FCC guidelines on communications infrastructure security, alongside HIPAA requirements for encrypted health data inspection without patient exposure, shape product certification demands in the United States. The SEC's cybersecurity disclosure rules now mandate documented visibility into encrypted traffic flows, compelling publicly traded firms to upgrade legacy blind spots. Stakeholders must weigh hardware refresh timing against cloud migration commitments, as premature appliance purchases risk stranded investment when network architectures shift to service-based consumption.
Market Dynamics
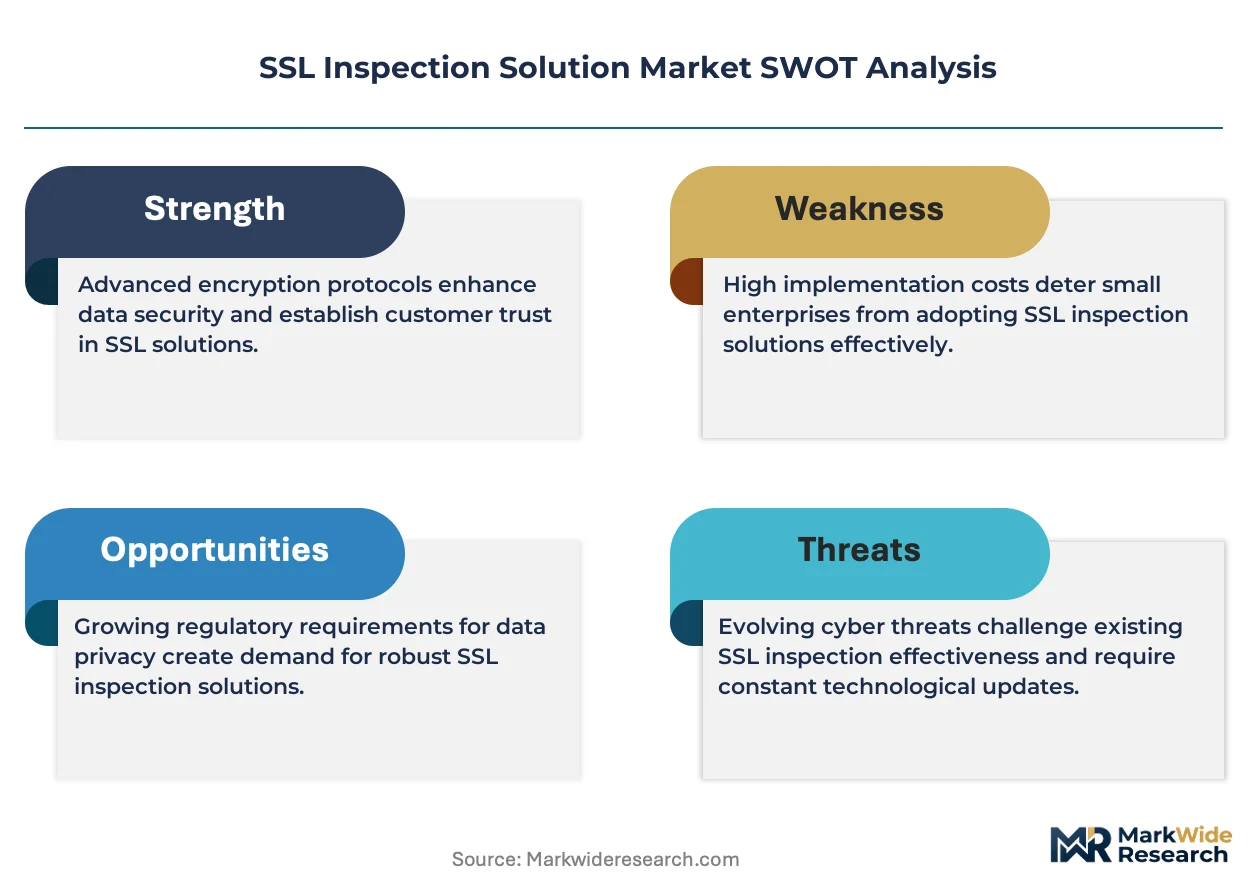
Zero-trust architecture mandates are compressing hardware refresh cycles while cloud-native delivery models reconfigure how vendors reach enterprise buyers, creating simultaneous pull for elastic capacity and friction against stranded appliance investments.
Growth Catalysts
- FCC communications infrastructure security guidelines:Federal directives tighten procurement standards for encrypted traffic visibility tools across critical network infrastructure, compelling systematic upgrades.
- Financial services audit requirements:BFSI end users sustain premium pricing for high-assurance inspection due to transaction volume sensitivity and regulatory examination protocols.
- API-level integration specialization:Vendors embed inspection logic directly into application workflows rather than network paths, opening margin-rich service layers.
Market Restraints
- Silicon supply concentration:Specialized packet-processing chip fabrication concentrates in East Asian foundries, exposing throughput capacity to geopolitical disruption.
- Certificate authority trust fragmentation:Browser root store policy divergence between Mozilla, Apple, and Google creates compliance complexity for inline decryption deployments.
- Post-quantum cryptography transition uncertainty:NIST standardization timelines for quantum-resistant algorithms delay long-term hardware architecture commitments.
Strategic Opportunities
- SEC cybersecurity disclosure rules:Publicly traded firms must document encrypted traffic visibility, creating compliance-driven replacement demand for legacy blind spots.
- Edge computing convergence:Distributed cloud architecture eliminates hardware dependency at branch locations, enabling new service-based consumption models.
- Healthcare data inspection:HIPAA requirements for encrypted health data analysis without patient exposure shape product certification demands in specialized verticals.
Industry Challenges
- TLS 1.3 and ESNI deployment:Perfect forward secrecy and encrypted server name indication complicate passive interception architectures, forcing active proxy redesigns.
- Hybrid environment integration:Synchronized policy enforcement across on-premises appliances and cloud-native inspection planes demands orchestration expertise scarce in enterprise security teams.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | SSL Inspection Solution Market |
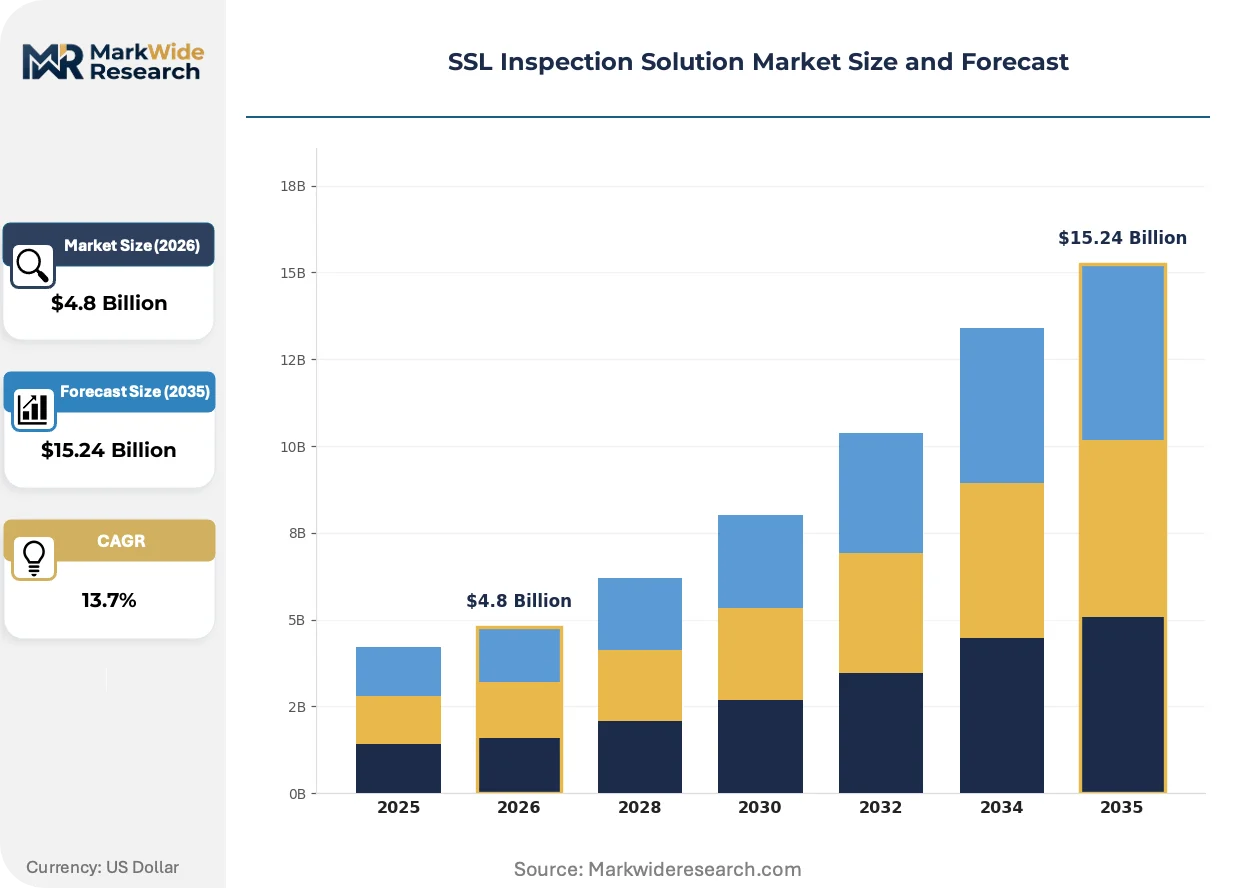
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $15.24 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-premises, Cloud-based, Hybrid, Managed Service End User: BFSI, Healthcare, Education, Government Industry Vertical: Retail, IT & Telecom, Manufacturing, Energy Integration Level: API, Network, Application, Browser |
| Companies Covered | Cisco, Forcepoint, Zscaler, Symantec, Check Point Software Technologies, Netskope, miniOrange, IBM, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
SSL Inspection Solution Market Evolving Landscape
SSL inspection technology is fragmenting across deployment modalities as performance boundaries between hardware appliances and cloud-delivered services blur, reshaping vendor competitive positioning and buyer evaluation criteria.
Software-defined packet inspection is virtualizing core decryption and analysis functions previously locked to dedicated silicon, allowing financial services firms to burst capacity during transaction peaks without permanent hardware procurement. Large enterprises are adopting this approach for development and staging environments before production migration. The technology is virtualizing capital expenditure into operational spending, compressing traditional three-year refresh cycles into continuous subscription relationships.
The EU AI Act's risk classification framework is imposing algorithmic transparency requirements on automated threat detection systems embedded within SSL inspection pipelines, forcing vendors to document decision logic for encrypted traffic analysis. Industrial consequence includes mandatory human-in-the-loop review for high-risk deployment scenarios. European financial institutions are responding by demanding explainability modules as standard procurement requirements, ahead of comparable mandates in other jurisdictions.
Consumption-based licensing is displacing perpetual appliance ownership across mid-market buyers who previously amortized hardware over five-year depreciation schedules. Managed security service providers are capturing this transition by bundling inspection capacity into broader network security subscriptions. This pattern is most visible in United States healthcare systems navigating simultaneous HIPAA compliance and capital constraint pressures.
SSL Inspection Solution Market Segmentation
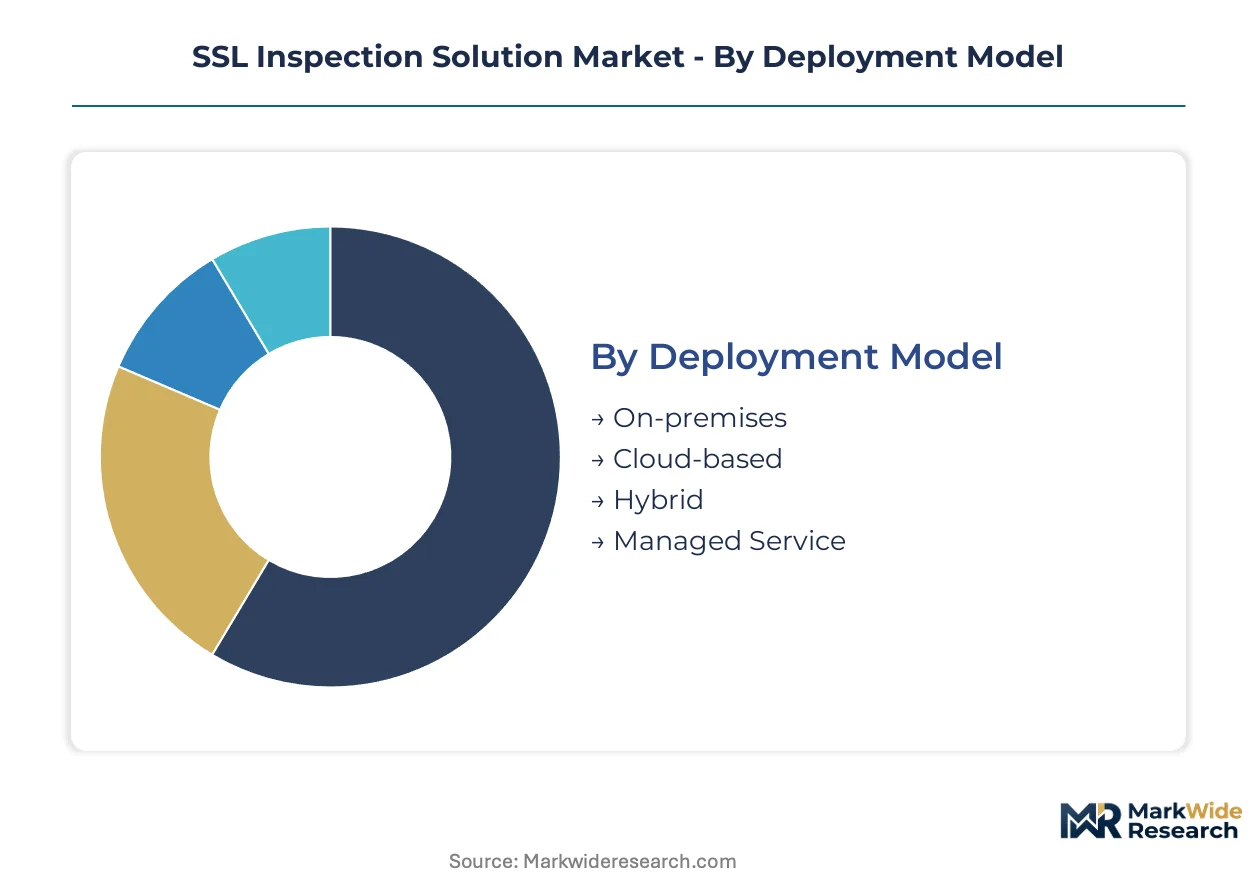
SSL inspection solutions fragment across deployment architectures and integration depths, with procurement patterns diverging sharply between capital-intensive appliance buyers and elasticity-seeking cloud adopters. Segment boundaries blur as vendors bundle network-level decryption with application-native inspection to capture hybrid environment spend.
Deployment Model:
Mature appliance deployments coexist with emerging cloud-native consumption, creating parallel procurement channels with distinct margin structures and customer lifetime value profiles.
- On-premises:Dedicated hardware appliances process encrypted traffic through specialized packet-processing silicon, delivering deterministic latency for high-frequency trading floors and core banking transaction switches. Financial services firms in the United States sustain this segment despite cloud migration pressures, driven by SEC audit documentation requirements and sub-millisecond latency mandates for payment infrastructure.
- Cloud-based:Elastic inspection capacity scales with encrypted traffic volumes without permanent hardware commitment, converting capital expenditure to metered operational spending. Healthcare systems navigating HIPAA compliance and capital constraint pressures are adopting this model fastest, particularly where patient data inspection must occur without on-premises infrastructure exposure.
- Hybrid:Synchronized policy enforcement spans hardware appliances at fixed locations and cloud-delivered inspection for distributed workforces.
- Managed Service:Security operations center staffing and capacity management outsourced to specialized providers.
On-premises hardware handles the majority of throughput; cloud-based deployment is expanding most quickly on share.
End User:
Regulatory intensity varies dramatically across buyer categories, with audit frequency and penalty exposure determining willingness to pay for high-assurance inspection capabilities.
- BFSI:Banks, insurers, and payment processors operate under continuous regulatory examination protocols that mandate encrypted traffic visibility for fraud detection and transaction integrity verification. The segment sustains premium pricing for hardware-backed inspection due to transaction volume sensitivity and examiner expectations for documented control environments.
- Healthcare:Hospitals and health systems must inspect encrypted patient data flows without exposing protected health information, creating specialized certification demands for inspection architectures. HIPAA requirements shape product validation protocols, with United States health systems prioritizing solutions that demonstrate audit logging segregation and access control granularity.
- Education:Universities and K-12 districts balance student privacy protections against duty-of-care obligations for network safety.
- Government:Federal and state agencies follow procurement standards tied to communications infrastructure security directives.
BFSI contributes the largest revenue concentration; healthcare is gaining share fastest among compliance-driven replacement cycles.
Industry Vertical:
Operational technology convergence and supply chain digitization are extending inspection requirements beyond traditional enterprise IT boundaries into production environments.
- Retail:Point-of-sale encryption and e-commerce payment flows demand inspection capacity that peaks during seasonal transaction surges, favoring elastic deployment models.
- IT & Telecom:Service providers and technology vendors operate inspection infrastructure as a core operational capability for customer security offerings and internal network hygiene.
- Manufacturing:Industrial control system integration with enterprise networks creates encrypted traffic paths between operational technology and cloud analytics platforms.
- Energy:Critical infrastructure operators face heightened procurement standards for encrypted traffic visibility tools under federal cybersecurity directives.
IT & Telecom maintains the steepest expansion trajectory; retail shows the strongest seasonal demand volatility.
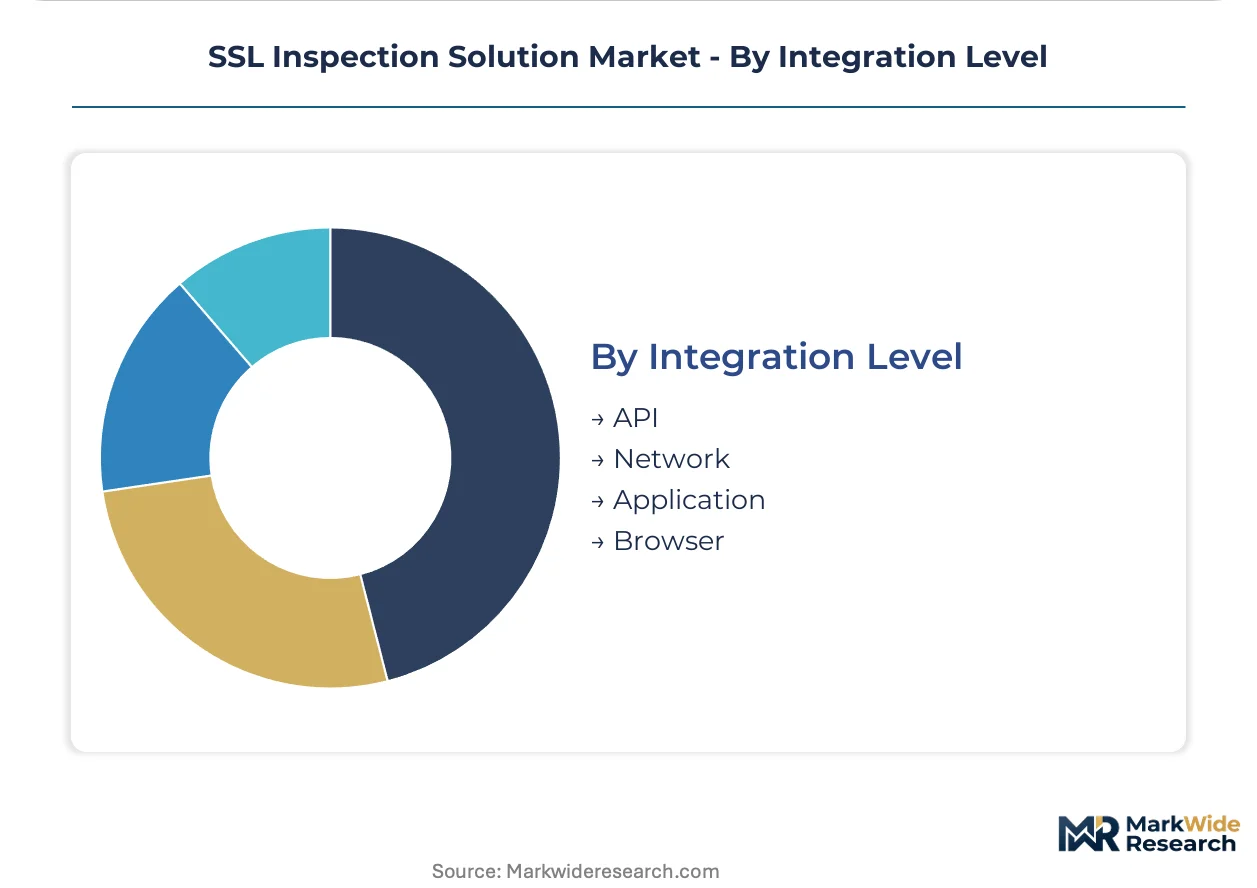
Integration Level:
Architectural positioning determines whether inspection occurs transparently within network paths or explicitly within application workflows, with significant implications for deployment friction and policy granularity.
- API:Inspection logic embeds directly into application code, enabling context-aware policy enforcement based on user identity, data classification, and transaction type. This approach eliminates network proxy latency but requires developer engagement and application modification, creating margin-rich service layers for vendors with platform integration expertise.
- Network:Inline appliances or virtualized proxies intercept TLS handshakes transparently to endpoints, preserving application compatibility at the cost of certificate management complexity. This mature approach dominates where legacy application portfolios resist modification or where centralized security operations demand uniform visibility.
- Application:Inspection modules deploy within specific software platforms such as email gateways or web proxies.
- Browser:Client-side agents perform local certificate inspection and policy enforcement for remote workforces.
Network integration carries the dominant installed base; API-level deployment shows the sharpest growth curve as cloud-native application architectures proliferate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power concentrates in United States federal procurement channels while German industrial buyers extract steeper discounts through consolidated purchasing consortia, creating a 15-20% effective price gap for equivalent inspection throughput capacity.
United States
Federal cybersecurity directives and SEC disclosure mandates drive replacement demand across financial services and critical infrastructure operators. FCC guidelines on communications infrastructure security tighten procurement standards for encrypted traffic visibility tools. Silicon Valley and Northern Virginia data center clusters anchor cloud-native inspection deployments for hybrid enterprise architectures.
Germany
Automotive and industrial manufacturing digitization creates encrypted OT-IT traffic inspection requirements at production facilities. EU AI Act algorithmic transparency rules impose documentation burdens on automated threat detection systems embedded in SSL pipelines. Baden-Württemberg and Bavaria industrial corridors concentrate demand for low-latency hardware appliances serving precision manufacturing networks.
United Kingdom
Financial services regulatory examinations sustain premium pricing for high-assurance inspection in the City of London and Canary Wharf trading ecosystems. GDPR cross-border data flow requirements complicate cloud inspection architectures handling EU-UK traffic. Thames Valley technology corridor hosts managed security service providers bundling elastic inspection into broader network security subscriptions.
Japan
Financial sector FISC security standards and manufacturing supply chain digitization drive hardware appliance refresh cycles. METI industrial cybersecurity guidelines shape procurement specifications for encrypted traffic visibility in critical infrastructure. Tokyo-Osaka corridor concentrates demand for sub-millisecond latency inspection serving high-frequency trading and payment settlement systems.
India
Digital payment infrastructure expansion and RBI cybersecurity circulars create compliance-driven demand across banking and fintech sectors. SEBI market infrastructure regulations mandate encrypted traffic visibility for trading systems and clearing operations. Mumbai and Bengaluru technology clusters anchor cloud-native inspection adoption among mid-market enterprises retiring capital-intensive appliance deployments.
SSL Inspection Solution Market Competitive Landscape
Platform consolidators and cloud-native specialists split the market between anchored enterprise relationships and elastic consumption models. The vendor base organizes around three strategic archetypes: incumbent network equipment providers extending security subscriptions, distributed cloud security vendors eliminating hardware dependency, and API-level integration specialists embedding inspection into application workflows. Dominant competitive moves include portfolio bundling to capture hybrid environment spend and geographic expansion through managed security service provider partnerships.
Within the platform consolidation tier, Palo Alto Networks and Cisco exemplify anchored enterprise positioning through hybrid environment coverage and incumbent equipment relationships respectively. Zscaler occupies the cloud-native vector with distributed architecture eliminating branch hardware requirements. These three companies represent the strategic poles around which mid-market vendors and specialized API integrators organize competitive positioning.
| Leading Market Players |
|---|
| Cisco |
| Forcepoint |
| Zscaler |
| Symantec |
| Check Point Software Technologies |
| Netskope |
| miniOrange |
| IBM |
| Palo Alto Networks |
| Others |
Value Network & Pricing Analysis
East Asian foundry concentration for specialized packet-processing silicon concentrates upstream margin capture with TSMC and Samsung Foundry, while downstream pricing power fragments across appliance vendors, cloud-native specialists, and API-embedded integrators competing for enterprise security budgets.
Pricing Analysis
Configured-to-order hardware appliances command premium spreads of 40-60% above standard cloud-subscription throughput tiers. Subscription-SaaS tiering dominates cloud-native delivery, while perpetual licensing persists in financial services hardware deployments. Price differentiation rests on certification grade (FIPS 140-2, Common Criteria) and customization depth for latency-sensitive trading infrastructure. Pricing pressure stems from managed security service providers bundling inspection capacity into broader network security subscriptions, compressing standalone vendor margins. Mid-market healthcare buyers exhibit highest price sensitivity due to capital constraint pressures, while BFSI trading floors show lowest sensitivity driven by sub-millisecond latency mandates and examiner documentation requirements.
Supply Chain Analysis
Extended payment terms from appliance vendors to East Asian foundries now stretch 90-120 days, with supply-chain finance facilities emerging as working capital bridges. Geographic supply concentrates in Taiwan (advanced node silicon), South Korea (memory and logic), and China (passive components and PCB assembly). Raw material dependencies include silicon wafers, high-bandwidth memory modules, and specialized FPGA substrates. Single-source vulnerability around TSMC's leading-edge capacity creates systemic exposure to geopolitical disruption. Distribution runs through direct enterprise sales for large deployments, with value-added resellers and managed security service providers capturing mid-market cloud-native adoption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
SSL inspection sits in early-cycle expansion as zero-trust architecture mandates accelerate hardware refresh cycles ahead of cloud migration timelines, with SEC disclosure rules and EU AI Act transparency requirements creating compliance-driven replacement demand across enterprise installed bases.
For Market Incumbents: Build switching-cost moats through hybrid environment orchestration capabilities that synchronize policy enforcement across on-premises appliances and cloud-native inspection planes. Deepen API-level integration expertise to capture margin-rich application-embedded deployments before cloud-native specialists dominate this vector. Counter the threat of Zscaler's distributed architecture by anchoring large enterprise relationships through platform consolidation and incumbent network equipment upgrade cycles. Prioritize certification investment in FIPS 140-2 and Common Criteria to maintain BFSI pricing premiums. For New Entrants and Emerging Players: Establish a beachhead in healthcare mid-market systems navigating simultaneous HIPAA compliance and capital constraint pressures, where cloud-native elastic capacity displaces appliance procurement fastest. Target API-level integration specialization for cloud-native application architectures proliferating across fintech and insurtech development pipelines. Penetrate through developer-centric go-to-market motions that embed inspection logic directly into CI/CD workflows, bypassing traditional network security procurement committees. For Investors and Strategic Acquirers: Capital is best deployed toward API-level integration specialists with platform engineering expertise and existing hyperscaler marketplace presence, as this archetype captures the sharpest growth curve in cloud-native deployment. Long-term viability hinges on orchestration capabilities spanning hybrid environments, with 5-10 year value creation tied to subscription revenue compounding and gross margin expansion from software-defined inspection virtualization. Watch for inflection signals in TLS 1.3 and ESNI deployment velocity, which forces active proxy redesigns and creates replacement demand for legacy passive interception architectures.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Palo Alto Networks consolidates network and cloud inspection into unified policy enforcement across hybrid environments. |
| API-Level Specialization | Vendors embed decryption logic directly into application workflows, eliminating network proxy latency for cloud-native architectures. |
| Managed Service Bundling | MSSPs capture mid-market transition by wrapping elastic inspection capacity into broader network security subscriptions. |
| Geographic Expansion | Cloud-native vendors partner with regional MSSPs to penetrate India and Southeast Asia digital payment infrastructure buildouts. |
| Certification Investment | FIPS 140-2 and Common Criteria validation sustains premium pricing in BFSI segments under continuous regulatory examination. |
Research Methodology
A spread of perspectives from CISOs, network security architects, cloud infrastructure engineers, and managed security service provider executives converged on the working assumptions driving this analysis. Primary fieldwork combined structured interviews with secondary validation through SEC cybersecurity disclosure filings, FCC infrastructure security guidelines, and EU AI Act implementation documentation. Bottom-up triangulation across deployment model adoption curves and top-down reconciliation against vendor reported subscription revenues anchored the market sizing framework.
Demand-supply-balance modeling across the projection horizon segmented by deployment architecture, integration level, and end-user regulatory intensity. Segmentation dimensions included on-premises appliance, cloud-native elastic, and hybrid orchestration deployment models; network proxy versus API-embedded integration levels; and BFSI, healthcare, and government end-user categories. CAGRs derived from elasticity-adjusted adoption curves and replacement cycle compression under zero-trust mandates. Industry-specific inputs encompassed TLS 1.3 deployment timelines and post-quantum cryptography standardization uncertainty.
Sensitivities concentrate around NIST post-quantum algorithm finalization timelines, browser root store policy divergence between Mozilla and Google, and geopolitical disruption to East Asian foundry capacity. Forecasts reflect documented assumptions about cloud migration velocity and regulatory enforcement intensity. Macroeconomic contraction delaying enterprise security refresh cycles, accelerated quantum computing breakthroughs, or export control expansion targeting packet-processing silicon would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Disk Encryption Software Market
Security Software
Global Data Masking Market
Security Software
Europe Anti-Money Laundering Software Market
Security Software
Employee Computer Monitoring Software Market
Security Software
Global Data Breach Notification Software Market
Security Software
Secure Email Gateway Market
Security Software
Japan Mobile Biometrics Market
Security Software
Biometric POS Terminals Market
Security Software
Data Privacy Software Market
Security Software
Home Webcam Market
Security Software
Passport Reader Market
Security Software
Identity-As-A-Service (Idaas) Market
Security Software
North America Secure Access Service Edge Market
Security Software
Website Monitoring Software Market
Security Software
Global Digital Signature Software Market
Security Software
Application Control Software Market