
 North America Secure Access Service Edge Market | 2026-2036
North America Secure Access Service Edge Market Size, Share, and Industry Trends Forecast 2026-2036
North America Secure Access Service Edge Market Analytics
FCC cybersecurity guidance for critical infrastructure operators is hardening the cost-of-entry calculus for SASE vendors seeking federal contracts. Palo Alto Networks leverages extensive channel partnerships to sustain enterprise dominance across the United States and Canada. Zscaler anchors cloud-native security positioning with a fully distributed architecture that eliminates on-premises hardware dependencies. Cisco Systems competes through deep integration between its networking heritage and security stack, targeting hybrid workforce deployments.
Secure Access Service Edge converges software-defined wide area networking with cloud-delivered security functions including secure web gateway, cloud access security broker, zero-trust network access, and firewall-as-a-service into a single policy framework managed through unified orchestration planes. Cloud-based deployment models are capturing the fastest expansion as enterprises abandon MPLS backhaul in favor of direct-to-cloud connectivity, while hybrid architectures retain substantial share among regulated industries requiring data residency controls. Managed services command premium pricing by offloading policy tuning and threat response to specialized operators, whereas professional services around migration and integration represent high-margin, project-based revenue pools.
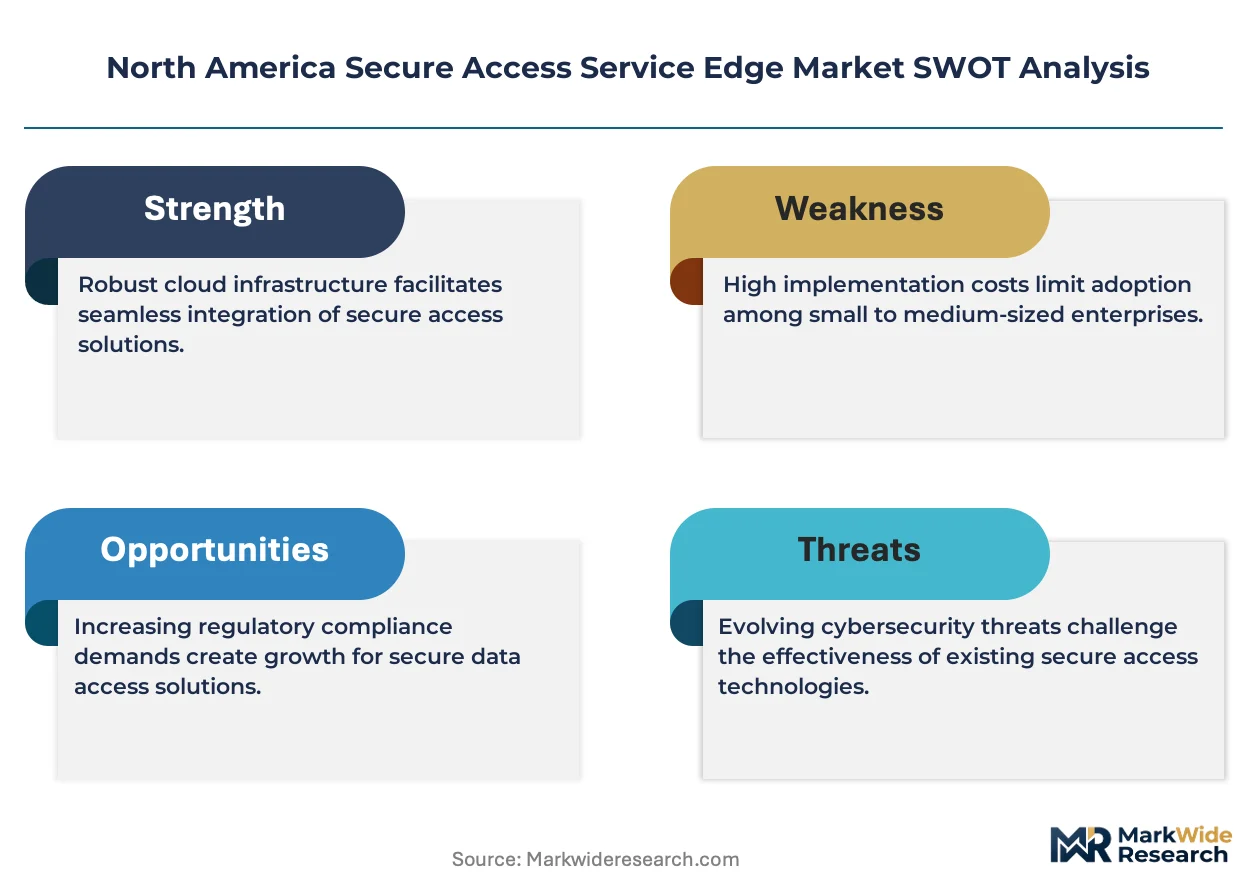
NIST zero-trust architecture standards and HIPAA security rule enforcement shape product requirements across healthcare and government verticals, with FedRAMP authorization functioning as a gatekeeper for federal procurement eligibility. The Securities and Exchange Commission's cyber disclosure rules for publicly traded companies amplify board-level urgency for converged network security investments. Stakeholders must monitor evolving state-level privacy legislation in California, Texas, and New York, as fragmented compliance obligations will favor vendors offering granular data residency and policy segmentation capabilities.
Market Dynamics
Federal zero-trust mandates are compressing procurement cycles across the United States and Canada, forcing enterprises to consolidate legacy WAN and security stacks into unified cloud-native architectures rather than maintain fragmented point solutions.
Growth Catalysts
- FedRAMP Authorization:Federal agencies now require FedRAMP-authorized SASE platforms for cloud procurement eligibility, creating a certified vendor pool that accelerates enterprise adoption through pre-validated security postures.
- SEC Cyber Disclosure Rules:Publicly traded companies face board-level accountability for breach reporting, driving converged network security investments that unify visibility across distributed workforces.
- Healthcare Cloud Migration:HIPAA-covered entities are replacing MPLS backhaul with direct-to-cloud connectivity, requiring CASB and SWG functions embedded within SASE fabrics to maintain compliance during patient data access.
Market Restraints
- Certification Timeline Friction:FedRAMP authorization requires 12-18 month validation cycles that lock out emerging vendors and entrench incumbent providers with existing federal credentials.
- Skill Concentration:Zero-trust architecture expertise clusters in coastal technology hubs, leaving mid-market enterprises in the US Midwest and Canadian Prairies dependent on managed service intermediaries.
- Legacy Hardware Stranding:Enterprises with depreciating on-premises firewall and VPN appliances face sunk-cost resistance when evaluating full cloud-native replacement.
Strategic Opportunities
- State-Level Privacy Fragmentation:California's CPRA, Texas HB4, and New York SHIELD Act create compliance complexity that favors vendors offering granular data residency controls and policy segmentation engines.
- Operational Technology Convergence:Manufacturing and energy firms are extending SASE fabrics to secure industrial IoT endpoints, merging IT/OT network policies through unified orchestration planes.
- Managed Service Penetration:Mid-market enterprises in Canada and secondary US markets represent underpenetrated demand for fully managed SASE offerings that offload policy tuning and threat response.
Industry Challenges
- Multi-Cloud Policy Consistency:Enterprises operating across AWS, Azure, and Google Cloud struggle to maintain uniform security postures when native cloud networking tools conflict with third-party SASE policy engines.
- Identity Architecture Integration:SASE deployments require deep integration with existing identity providers and privileged access management systems, creating project delays when legacy IAM infrastructures lack modern API connectivity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | North America Secure Access Service Edge Market |
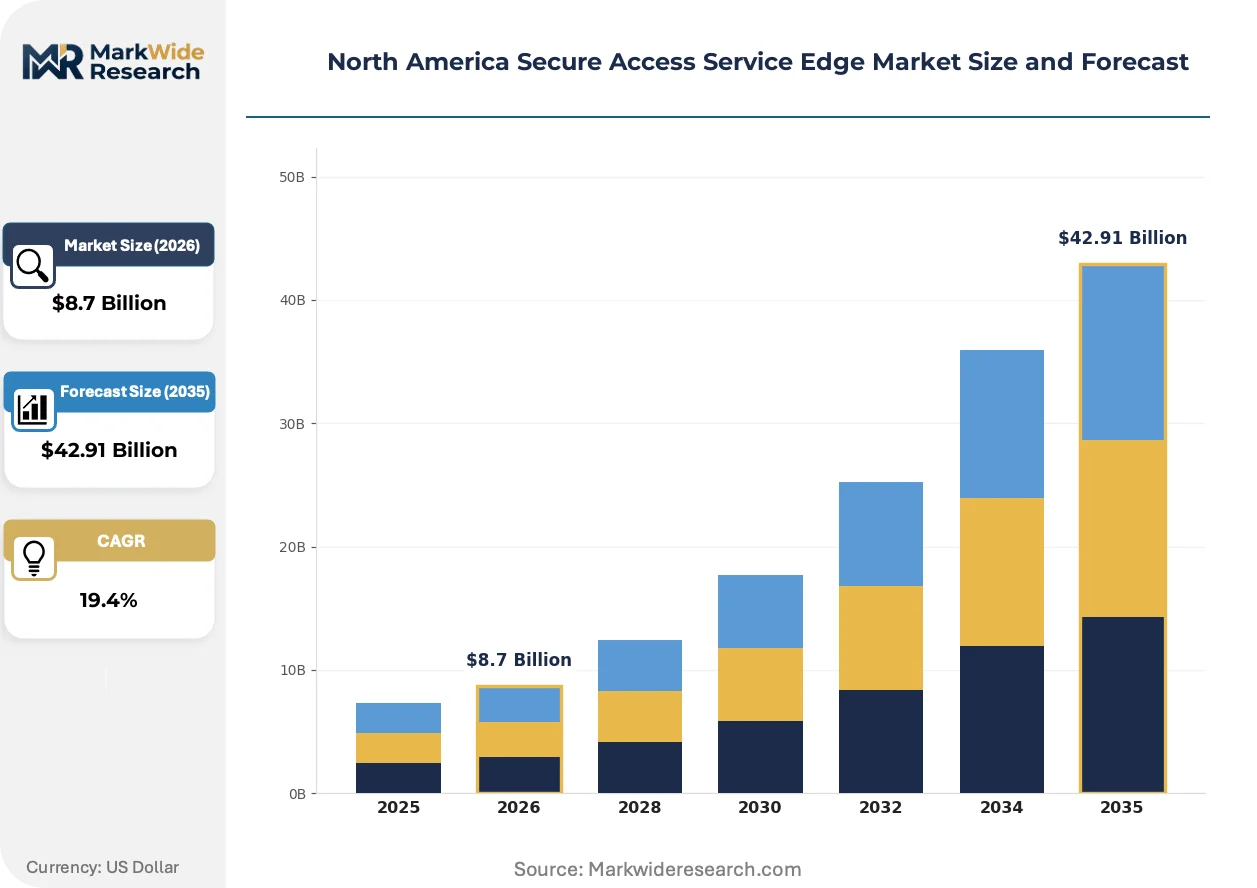
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $42.91 Billion |
| CAGR (2026 – 2036) | 19.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Services, Professional Services, Consulting Services, Maintenance Services Deployment Model: On-Premises, Cloud-Based, Hybrid, Remote Customer Type: Enterprises, SMEs, Government, Educational Institutions End User Industry: Healthcare, Finance, Retail, Manufacturing |
| Companies Covered | Fortinet, Akamai Technologies, Palo Alto Networks, Netskope, Cloudflare, Cisco Systems, Cato Networks, Broadcom, Zscaler, Others |
| Regions Covered | North America: US, Canada, Mexico |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
North America Secure Access Service Edge Market Evolving Landscape
Artificial intelligence is embedding into SASE policy engines, shifting security operations from reactive rule maintenance toward predictive threat containment and autonomous access decisions.
AI-powered security analytics is automating threat detection and response workflows within SASE platforms. Fortune 500 enterprises are deploying these capabilities to reduce mean-time-to-remediation for compromised credentials. The technology is automating policy adjustments that previously required dedicated security engineering teams.
NIST zero-trust architecture standards are hardening procurement specifications across federal and regulated industries. Healthcare providers and financial services firms must now demonstrate continuous verification and least-privilege enforcement to satisfy audit requirements. Organizations are responding by prioritizing vendors with native microsegmentation and device trust scoring.
Enterprise buyers are consolidating vendor relationships and demanding integrated platforms over best-of-breed point solutions. Chief information security officers are replacing standalone CASB, SWG, and ZTNA contracts with unified SASE subscriptions. This consolidation is most visible among US-based multinational corporations standardizing on single-vendor architectures for global branch consistency.
North America Secure Access Service Edge Market Segmentation
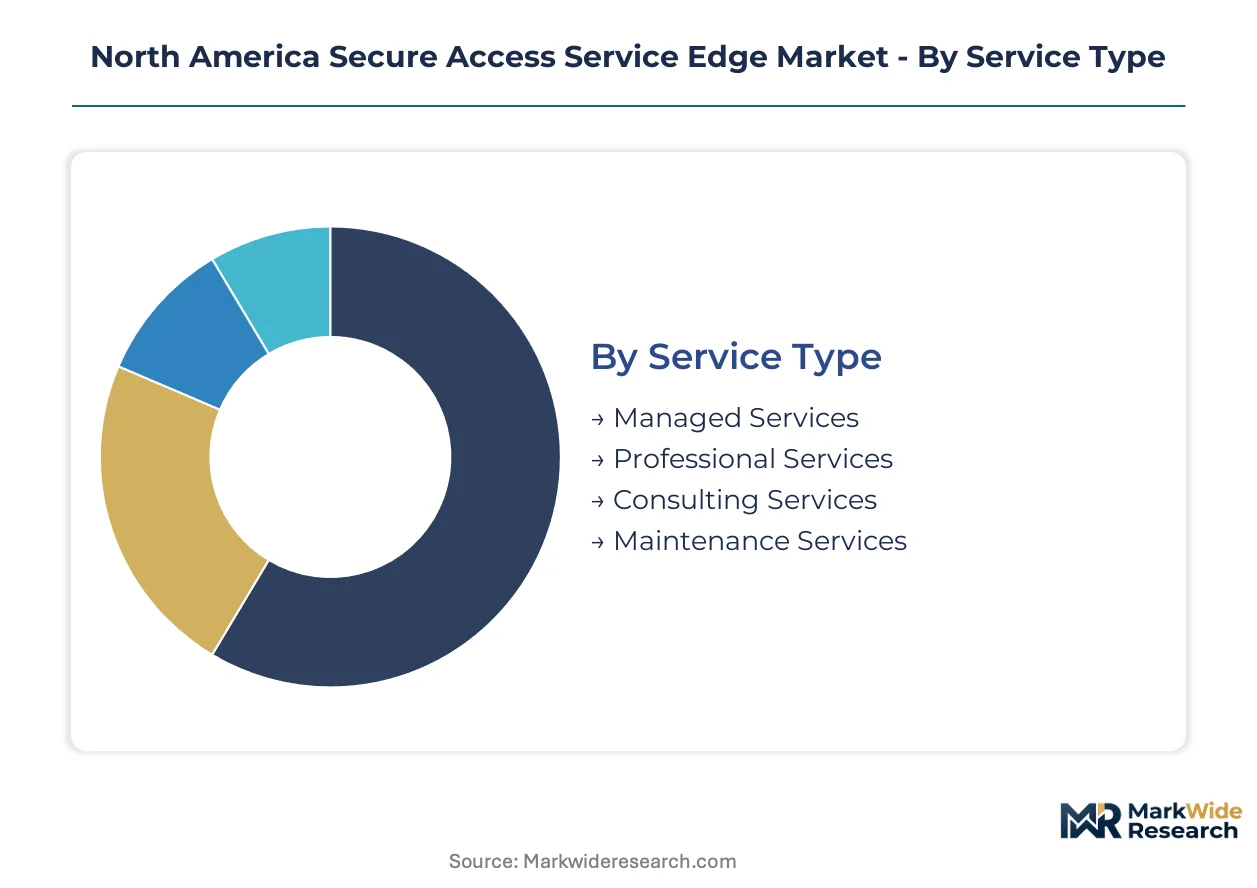
SASE procurement patterns diverge sharply across service delivery modes and infrastructure maturity levels. Deployment architecture choices determine compliance posture and operational cost structure for North American enterprises navigating federal mandates.
Service Type:
Volume concentrates in standardized offerings with recurring revenue streams, while premium tiers capture complex integration scenarios.
- Managed Services:Comprehensive policy orchestration and threat response delivered through specialized operators. Fortune 500 enterprises in the United States offload security operations center functions to managed SASE providers, driven by FedRAMP authorization requirements that internal teams struggle to maintain.
- Professional Services:Project-based migration consulting and legacy WAN transformation engagements. Canadian financial institutions and US healthcare systems purchase these high-margin engagements during MPLS-to-cloud transitions, constrained by compressed procurement cycles from federal zero-trust mandates.
- Consulting Services:Architecture assessment and vendor selection advisory for initial SASE strategy formulation.
- Maintenance Services:Post-deployment support contracts covering policy tuning and platform updates.
Today's leader: Managed Services. Tomorrow's challenger: Professional Services.
Deployment Model:
Cost tier separation reflects data residency requirements versus agility demands across regulated and unregulated verticals.
- Cloud-Based:Fully distributed architecture eliminating on-premises hardware dependencies. US technology firms and retail chains deploy cloud-native SASE for direct-to-cloud connectivity, abandoning MPLS backhaul as SEC disclosure rules intensify board-level urgency for unified visibility.
- Hybrid:Split traffic processing between cloud gateways and retained edge appliances. HIPAA-covered entities and defense contractors in Texas and California maintain this architecture, balancing agility against state-level privacy fragmentation requiring granular data residency controls.
- On-Premises:Dedicated hardware deployments for air-gapped or classified environments.
- Remote:Lightweight agent-based access for distributed workforces without fixed branch infrastructure.
Cloud-Based deployments command premium pricing elasticity; Hybrid architectures retain defensive share in regulated pockets.
Customer Type:
Application intensity varies by procurement sophistication and compliance exposure to federal standards.
- Enterprises:Multinational corporations standardizing global branch consistency through single-vendor architectures. US-based Fortune 500 companies consolidate fragmented CASB, SWG, and ZTNA contracts, responding to NIST zero-trust architecture specifications with native microsegmentation requirements.
- Government:Federal agencies and state entities bound by FedRAMP authorization gatekeeping. Civilian and defense departments procure only through pre-certified vendor pools, with 12-18 month validation cycles locking out emerging providers.
- SMEs:Mid-market enterprises dependent on managed service intermediaries for zero-trust expertise.
- Educational Institutions:Universities and K-12 districts with distributed campus networks and research collaborations.
Enterprise segment anchors current revenue; Government vertical shapes long-term procurement standards.
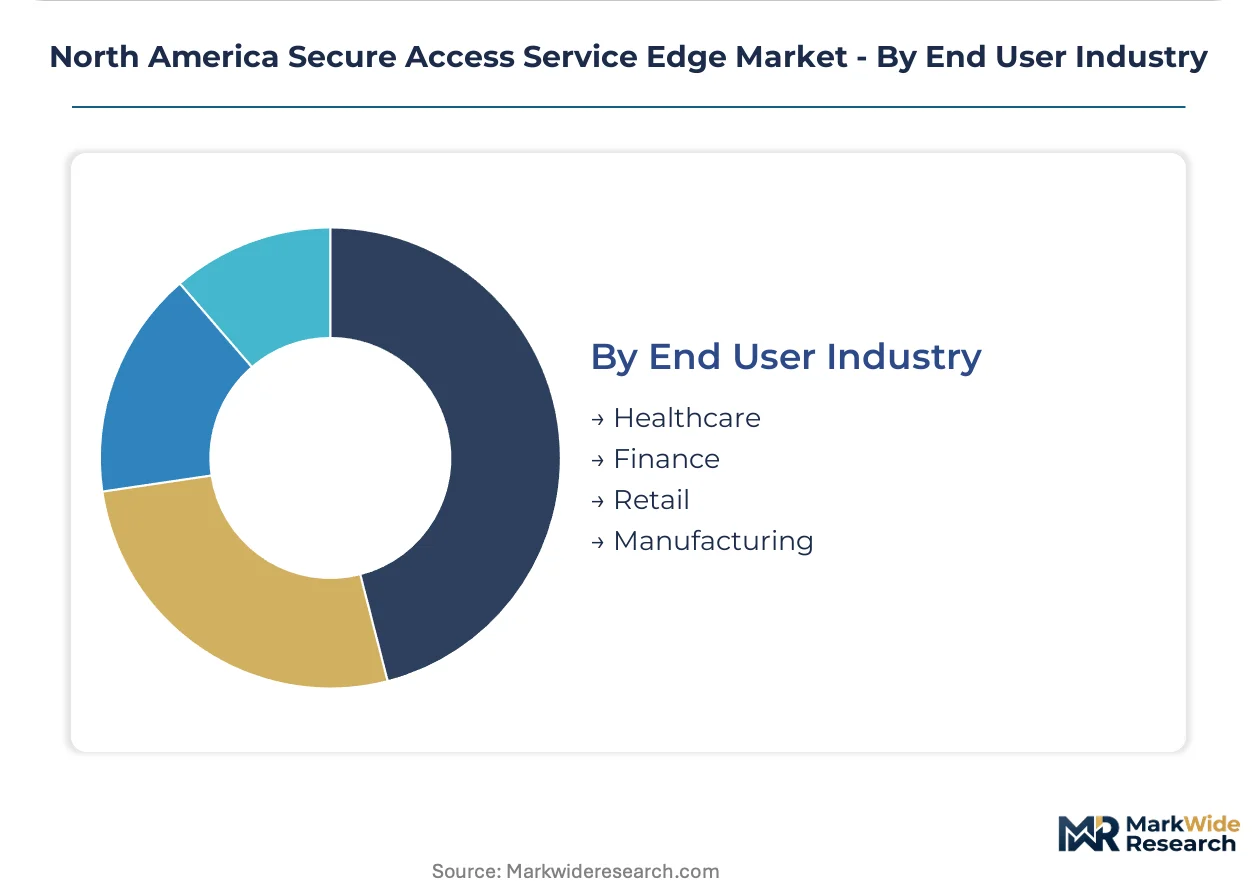
End User Industry:
Margin structure reflects regulatory enforcement intensity and legacy infrastructure replacement cycles.
- Finance:Banks, insurers, and securities firms unifying branch connectivity and cloud security postures. Financial services firms across New York and Toronto accelerate SASE adoption as SEC cyber disclosure rules impose board-level accountability for breach reporting and continuous verification.
- Healthcare:Hospitals, clinics, and payers replacing MPLS backhaul for patient data access. HIPAA-covered entities in the United States embed CASB and SWG functions within SASE fabrics, maintaining compliance during cloud migration while satisfying audit requirements for least-privilege enforcement.
- Retail:Omnichannel merchants securing distributed point-of-sale and e-commerce endpoints.
- Manufacturing:Industrial firms extending SASE fabrics to operational technology environments.
Finance drives near-term contract value; Manufacturing offers steepest expansion trajectory through IT/OT convergence.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Zero-trust architecture expertise clusters in coastal technology hubs across the continent, creating geographic asymmetries in enterprise procurement velocity and managed service dependency.
United States
Federal zero-trust mandates and SEC cyber disclosure rules compress procurement cycles for Fortune 500 enterprises. NIST architecture standards reshape product requirements across civilian and defense agencies. The Washington DC-Boston corridor anchors federal contract activity, while Silicon Valley and Seattle drive cloud-native platform development.
Canada
Mid-market enterprises in Ontario and Quebec rely heavily on managed service intermediaries for zero-trust expertise. Health Canada cybersecurity guidance for critical infrastructure operators hardens procurement criteria for federal contracts. Toronto's financial district concentrates SASE adoption among banks and insurers modernizing legacy WAN infrastructure.
Mexico
Manufacturing firms in Nuevo León and Mexico City Metro extend SASE fabrics to secure industrial IoT endpoints across maquiladora operations. The central bank's operational resilience requirements for financial institutions accelerate converged network security investments. Guadalajara's technology corridor attracts cloud-native security deployments from multinational corporations standardizing regional branch consistency.
California
CPRA privacy mandates and granular data residency requirements favor vendors offering policy segmentation engines for healthcare and technology enterprises. HIPAA-covered entities in Los Angeles and San Francisco embed CASB and SWG functions within SASE fabrics during patient data access migrations. The state's fragmented compliance obligations create premium pricing for granular control capabilities.
Texas
HB4 privacy legislation and defense contractor concentration drive hybrid architecture retention for data residency controls. Energy firms in Houston extend SASE fabrics to operational technology environments, merging IT/OT network policies. Dallas-Fort Worth's telecom corridor anchors enterprise deployments abandoning MPLS backhaul for direct-to-cloud connectivity.
North America Secure Access Service Edge Market Competitive Landscape
Diversified conglomerates compete with focused pure-play specialists across deployment architectures and service delivery modes. The vendor base stratifies into three tiers: cloud-native specialists with fully distributed architectures, networking incumbents leveraging infrastructure heritage, and managed service operators capturing mid-market demand. Strategic moves concentrate on FedRAMP authorization pursuit, channel partnership expansion, and AI-powered security analytics integration.
Within the cloud-native specialist tier, Zscaler and Netskope exemplify fully distributed architectures eliminating on-premises hardware dependencies. Palo Alto Networks occupies a position among networking-security converged providers, leveraging extensive channel partnerships across the United States and Canada. These three anchors represent divergent approaches to unified policy orchestration and threat response automation.
| Leading Market Players |
|---|
| Fortinet |
| Akamai Technologies |
| Palo Alto Networks |
| Netskope |
| Cloudflare |
| Cisco Systems |
| Cato Networks |
| Broadcom |
| Zscaler |
| Others |
Value Network & Pricing Analysis
FedRAMP-certified vendor scarcity creates a bifurcation between premium authorized providers and unqualified alternatives, concentrating pricing power among incumbent operators while forcing supply chain dependencies on specialized cloud infrastructure operators and managed security service intermediaries.
Pricing Analysis
Bundled platform subscriptions dominate enterprise procurement, while unbundled point solutions face margin compression. Pricing stratifies across FedRAMP-authorized premium tiers, standard commercial deployments, and economy managed service offerings. Price differentiation rests on compliance certification level and geographic data residency granularity. Cost compression in the mid-market intensifies because managed service intermediaries aggregate demand and standardize policy templates. Government verticals exhibit lowest price sensitivity due to mandate-driven procurement timelines, while Canadian mid-market enterprises demonstrate highest sensitivity to per-seat licensing costs.
Supply Chain Analysis
Single-source vulnerability sits with hyperscale cloud infrastructure providers concentrated in the United States. Core platform components draw from specialized silicon foundries in Taiwan, South Korea, and the United States for AI-accelerated security processing. Supply chain risk centers on FedRAMP authorization bottlenecks that constrain vendor pool expansion and extend procurement cycles. Distribution runs through channel partners and systems integrators rather than direct sales, particularly for mid-market penetration across Canadian provinces and US Midwest states.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Geographic arbitrage opportunities emerge between FedRAMP-authorized US federal contracts commanding premium pricing and Canadian mid-market managed service demand where compliance requirements remain less stringent but expertise scarcity drives margin capture.
For Market Incumbents: Deepen vertical integration into AI-powered threat analytics to differentiate against cloud-native specialists eroding platform stickiness. Fortify channel control across Canadian Prairies and US Midwest markets where managed service intermediaries concentrate buyer relationships. Prioritize certification investment in emerging state privacy frameworks before fragmentation hardens procurement specifications. For New Entrants and Emerging Players: Begin with operational technology security extensions for manufacturing and energy verticals, where IT/OT convergence creates white-space demand outside saturated enterprise WAN replacement cycles. Target Mexico's maquiladora corridors and Texas energy corridor as the most penetrable geographies lacking incumbent saturation. Pursue strategic partnership routes with industrial automation vendors rather than direct enterprise sales. For Investors and Strategic Acquirers: Consolidation pressure builds where FedRAMP authorization timelines strand emerging vendors without federal eligibility. Long-term viability favors platforms with native microsegmentation architectures over hardware-dependent hybrid solutions. Acquisition target archetypes include regional managed security service providers with established Health Canada or state-agency relationships. Watch NIST zero-trust architecture specification updates as inflection indicators for vendor obsolescence risk.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Pursuit | Federal procurement eligibility gates revenue access to civilian and defense agencies under NIST standards. |
| AI Security Analytics Integration | Autonomous threat containment reduces customer security engineering headcount and improves retention metrics. |
| Channel Partnership Expansion | Canadian and US Midwest mid-market penetration depends on managed service intermediary relationships. |
| Operational Technology Convergence | Manufacturing and energy verticals merge IT/OT policies through unified SASE orchestration planes. |
| State Privacy Framework Certification | CPRA, Texas HB4, and New York SHIELD Act compliance creates premium pricing for granular controls. |
Research Methodology
Coverage spans the United States, Canada, and Mexico, with primary inputs from each market combined with secondary validation. Interviews with CISOs, federal procurement officers, managed security service providers, and cloud infrastructure architects informed demand-side dynamics. Secondary sources include SEC cyber disclosure filings, FedRAMP authorization databases, Health Canada cybersecurity guidance, and hyperscaler capex disclosures. Bottom-up deployment modeling and top-down market sizing triangulated volume estimates.
Rate-of-change decomposition across the analysis window separates organic expansion from mandate-driven replacement cycles. Segmentation dimensions modeled include deployment architecture, service delivery mode, customer scale tier, vertical industry, and regional regulatory cluster. CAGRs derived from installed base evolution and annual contract value trajectories. Industry-specific inputs encompass FedRAMP authorization pipeline velocity and state-level privacy legislation enactment schedules.
Caveats apply where NIST specification revisions or state privacy law fragmentation could materially shift the outlook. Forecasts reflect assumptions about federal mandate enforcement consistency and hyperscaler infrastructure availability. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Application Control Market
Security Software
VPN Software Market
Security Software
Software Assurance Market
Security Software
Global Log Management Market
Security Software
Phone Antivirus Software Market
Security Software
Antivirus Software Package Market
Security Software
Public Key Infrastructure (PKI) Market
Security Software
Messaging Security Market
Security Software
Sound Masking Systems Market
Security Software
E Passport Market
Security Software
AD-Blocking Software Market
Security Software
Europe Video Management System Market
Security Software
Digital Risk Protection Software Market
Security Software
Global Error Monitoring Software Market
Security Software
Passwordless Authentication Market
Security Software
Latin America Fraud Detection and Prevention Market