
 Global Runtime Application Self-Protection Market | 2026-2036
Global Runtime Application Self-Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Global Runtime Application Self-Protection Market Foresight
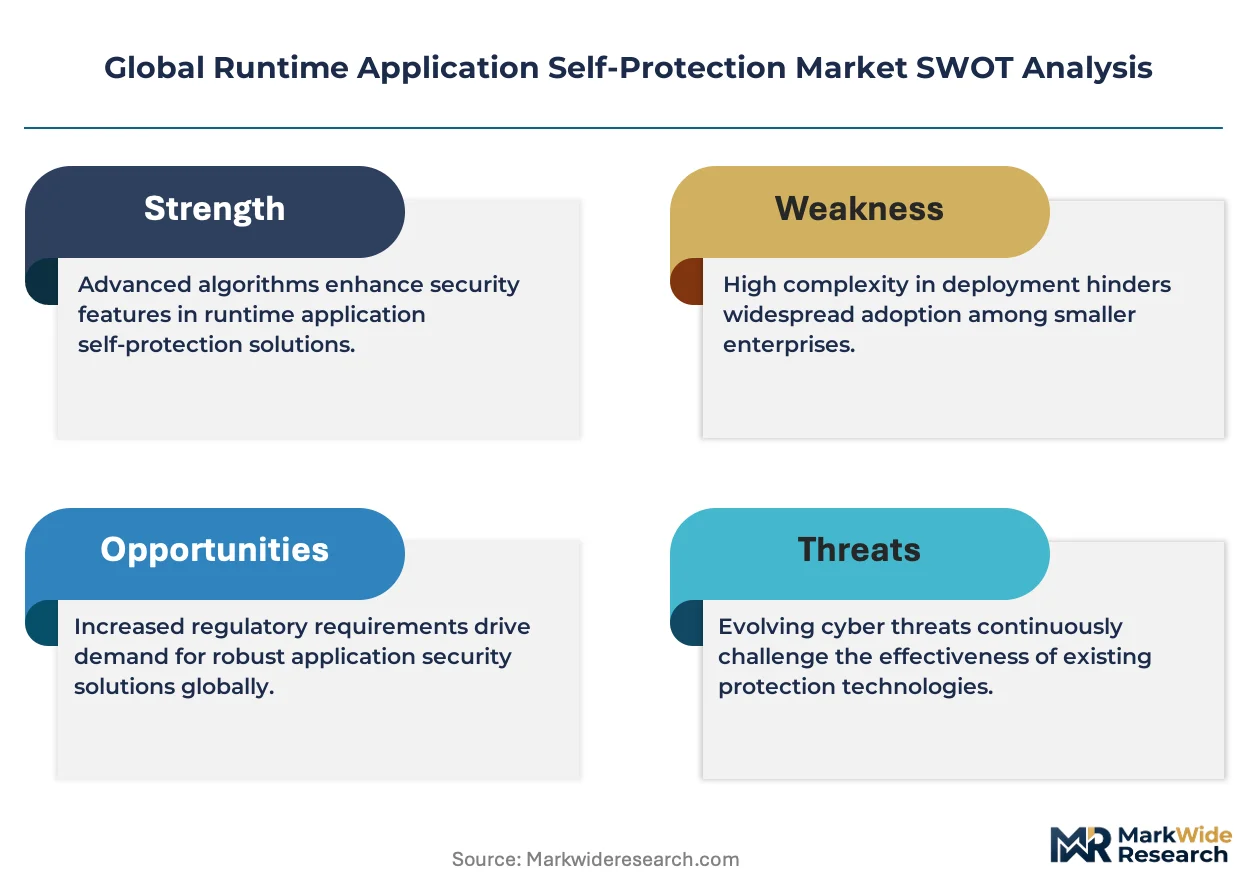
Subscription-based SaaS delivery is narrowing the capital barrier for mid-market buyers seeking enterprise-grade runtime protection. Imperva leverages its cloud-native architecture to compete across hybrid deployment environments. Palo Alto Networks anchors its position through in-house production of embedded security modules that extend across containerized workloads. Dynatrace differentiates by integrating application performance monitoring with real-time threat detection, occupying a converged tooling niche.
Runtime Application Self-Protection refers to security technology embedded within applications to detect and block attacks during execution through instrumentation of application code, memory, and behavior. The technology operates by monitoring application runtime states against defined security policies to prevent code injection, data exfiltration, and unauthorized access in live production environments. Cloud-Based deployment leads solution delivery as financial institutions and technology firms abandon capital-intensive on-premises infrastructure. API Protection represents the fastest-growing use case segment, driven by microservices architectures and open banking mandates across multiple jurisdictions. Threat Detection solutions command the deepest margin pools due to continuous telemetry requirements and recurring analytics consumption.
The EU AI Act and GDPR impose strict algorithmic transparency and data processing accountability requirements that elevate demand for behavior monitoring and access control capabilities. In the United States, the SEC cybersecurity disclosure rules and NIST guidelines shape procurement standards for financial institutions and publicly traded technology firms. India's Digital Personal Data Protection Act and BIS cloud security standards are creating compliance-driven procurement cycles among domestic e-commerce platforms and government agencies. Stakeholders must monitor how fragmented regulatory timelines across the European Union, United States, and India will fragment product certification requirements and channel investment toward multi-jurisdiction compliance engineering.
Market Dynamics
The convergence of cloud-native architectures with zero-trust security mandates is compressing deployment timelines for runtime protection solutions. Financial services and technology firms now embed self-protection modules directly into CI/CD pipelines rather than retrofitting post-deployment.
Growth Catalysts
- EU AI Act compliance deadlines:European enterprises must implement real-time algorithmic monitoring by fixed regulatory timelines, accelerating procurement of behavior-analytics platforms.
- Microservices proliferation:Containerized application architectures expose thousands of API endpoints that traditional perimeter defenses cannot adequately protect.
- Open banking mandates:Jurisdictions including the United Kingdom, Brazil, and Australia require financial institutions to expose customer data through secured APIs.
Market Restraints
- Specialized talent scarcity:Runtime instrumentation requires expertise in both application security and systems programming, with qualified practitioners concentrated in technology hubs.
- Performance overhead concerns:In-memory monitoring and behavioral analysis introduce latency that conflicts with high-frequency trading and real-time transaction processing requirements.
- Fragmented certification requirements:Divergent security standards across FedRAMP, ISO 27001, and BIS cloud guidelines force redundant engineering investments.
Strategic Opportunities
- Indian e-commerce expansion:Domestic platforms and government digital services under the Digital Personal Data Protection Act represent underpenetrated demand for compliance-integrated runtime monitoring.
- Convergence with APM tooling:Unified platforms combining application performance monitoring with threat detection reduce vendor sprawl and operational complexity.
- Edge computing workloads:Distributed IoT and 5G applications outside traditional data center perimeters require embedded protection that cannot rely on network-based controls.
Industry Challenges
- DevSecOps integration friction:Security instrumentation must align with agile release cycles without breaking existing automation workflows or developer productivity metrics.
- False positive management:Behavioral detection models require continuous tuning to prevent alert fatigue that degrades incident response effectiveness.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Runtime Application Self-Protection Market |
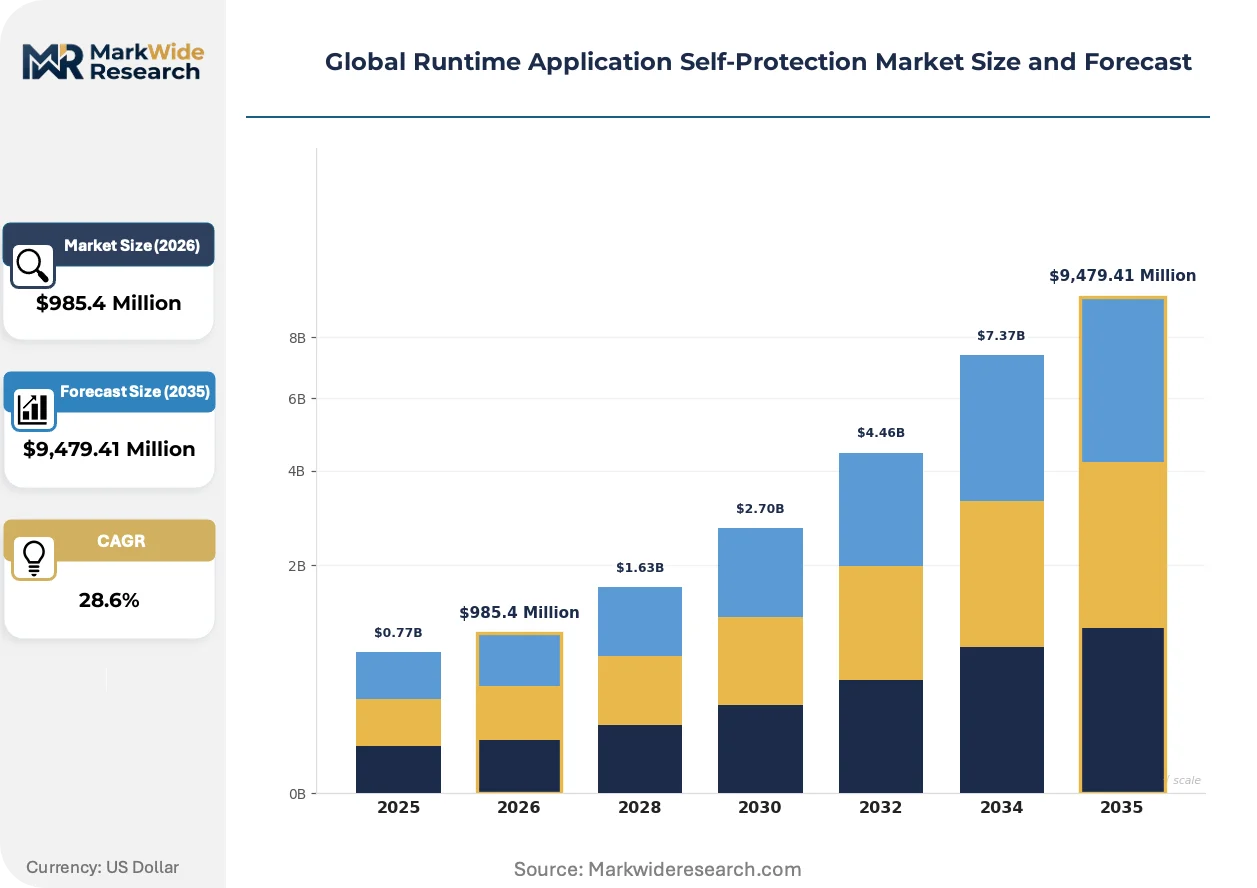
| Market Size in 2026 | $985.4 Million |
| Market Size in 2035 | $9,479.41 Million |
| CAGR (2026 – 2036) | 28.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Containerized, Serverless Solution Type: Threat Detection, Data Leakage Prevention, Behavior Monitoring, Access Control, Code Hardening Use Case: Web Application Security, API Protection, Mobile Application Defense, Microservices Security, Payment Security End User: Financial Institutions, E-commerce Platforms, Telecom Operators, Government Agencies, Technology Firms |
| Companies Covered | Contrast Security, Imperva, Pradeo, Guardsquare, Promon, Palo Alto Networks, Dynatrace, Veracode, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Runtime Application Self-Protection Market Shifts & Advancements
Instrumentation techniques are shifting from external agents toward embedded modules that operate within application memory spaces. This evolution eliminates network dependency and reduces attack surface exposure.
Agentless runtime protection is collapsing the distinction between security and observability tooling. Cloud-native platforms embed protection through language-specific libraries and kernel-level hooks rather than sidecar containers. Technology firms and financial services deploy these modules across serverless functions and Kubernetes clusters. The compression of security into application runtimes eliminates separate infrastructure procurement cycles.
The EU AI Act and GDPR impose algorithmic transparency requirements that elevate demand for explainable threat detection. Automated decision-making in security contexts must now provide audit trails and human-interpretable reasoning. European enterprises and multinational firms with EU operations retrofit existing runtime platforms with logging and attribution capabilities. This regulatory pressure accelerates replacement of black-box detection models with interpretable alternatives.
Consumption-based pricing models are displacing perpetual licenses across mid-market buyer segments. Subscription delivery narrows capital barriers while embedding vendors deeper into operational workflows. Channel partners and managed security providers bundle runtime protection with broader detection and response services. Germany and India exhibit the strongest momentum toward utility-based procurement structures.
Global Runtime Application Self-Protection Market Segmentation
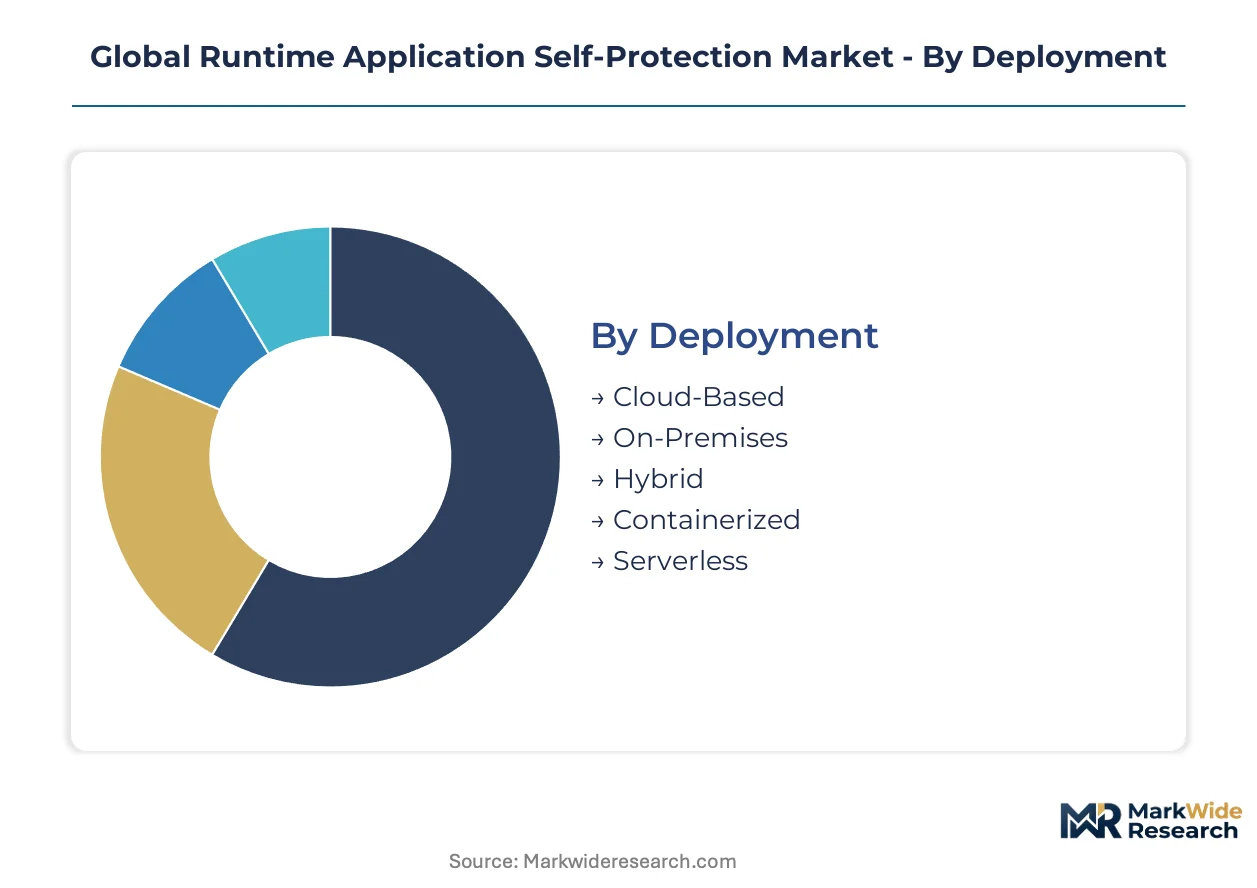
Runtime Application Self-Protection solutions fragment across deployment architectures, functional modules, and vertical risk profiles. Buyers align procurement decisions with cloud migration status, regulatory exposure, and application portfolio composition. Segmentation clarity enables vendors to anchor pricing and packaging against specific operational constraints rather than generic security postures.
Deployment:
The use-case spectrum spans legacy data center retention through fully abstracted serverless functions, with each architecture imposing distinct instrumentation requirements and latency budgets.
- Cloud-Based:Native SaaS delivery eliminates infrastructure ownership while embedding protection through language-specific libraries and kernel-level hooks. Financial institutions in the United States and Germany dominate consumption as FedRAMP and BSI cloud certification timelines compress procurement cycles.
- Containerized:Sidecar-less instrumentation modules deploy directly within Kubernetes clusters and Docker runtimes, monitoring memory spaces without network dependency. Technology firms migrating microservices architectures drive fastest expansion as API endpoint proliferation outstrips perimeter defense scalability.
- Hybrid:Unified policy engines synchronize protection across on-premises legacy systems and public cloud workloads. Enterprises with regulated data residency requirements in India and Germany anchor demand.
- On-Premises:Capital-intensive appliance and agent deployment persists among government agencies with air-gapped security mandates. Procurement concentrates in defense and critical infrastructure sectors.
- Serverless:Function-as-a-service protection through deployment-time instrumentation addresses ephemeral execution environments. Early adoption clusters among technology firms building event-driven architectures.
Established volume favors Cloud-Based; emerging adoption favors Containerized.
Solution Type:
Functional modules align with distinct margin structures based on telemetry intensity and recurring analytics consumption.
- Threat Detection:Continuous behavioral analysis and anomaly scoring against baseline application profiles generates highest recurring revenue per deployment. Financial institutions facing SEC disclosure rules and NIST guidelines mandate real-time incident telemetry, concentrating demand in the United States.
- Behavior Monitoring:EU AI Act algorithmic transparency requirements elevate explainable detection models that provide audit trails and human-interpretable reasoning. European enterprises retrofit platforms with logging capabilities, accelerating replacement of black-box systems.
- Data Leakage Prevention:Runtime data flow inspection blocks unauthorized exfiltration through application-layer channels. E-commerce platforms under India's Digital Personal Data Protection Act drive compliance-integrated procurement.
- Access Control:Context-aware authorization decisions embedded within application execution paths. Zero-trust mandates across government agencies expand addressable market.
- Code Hardening:Deployment-time instrumentation that removes vulnerable code patterns before production exposure. DevSecOps pipeline integration determines competitive positioning.
Recurring revenue intensity favors Threat Detection; regulatory retrofit cycles favor Behavior Monitoring.
Use Case:
Protection requirements diverge sharply across application surface area, transaction value, and attack vector exposure.
- API Protection:Microservices architectures expose thousands of endpoints beyond traditional perimeter reach. Open banking mandates in the United Kingdom, Brazil, and Australia force financial institutions to secure customer data interfaces, generating steepest expansion trajectory across all use cases.
- Payment Security:PCI-DSS compliance and real-time transaction fraud prevention impose sub-millisecond latency tolerances. United States payment processors and Indian e-commerce platforms anchor procurement volume.
- Web Application Security:Established protection against injection attacks and session hijacking dominates current installed base. Legacy three-tier applications sustain replacement demand.
- Microservices Security:Service-to-service communication monitoring within container meshes. Technology firms with cloud-native portfolios drive segment growth.
- Mobile Application Defense:Runtime application protection shielding against tampering and reverse engineering. Financial services mobile banking deployments concentrate demand.
Compliance mandate density favors API Protection; transaction value concentration favors Payment Security.
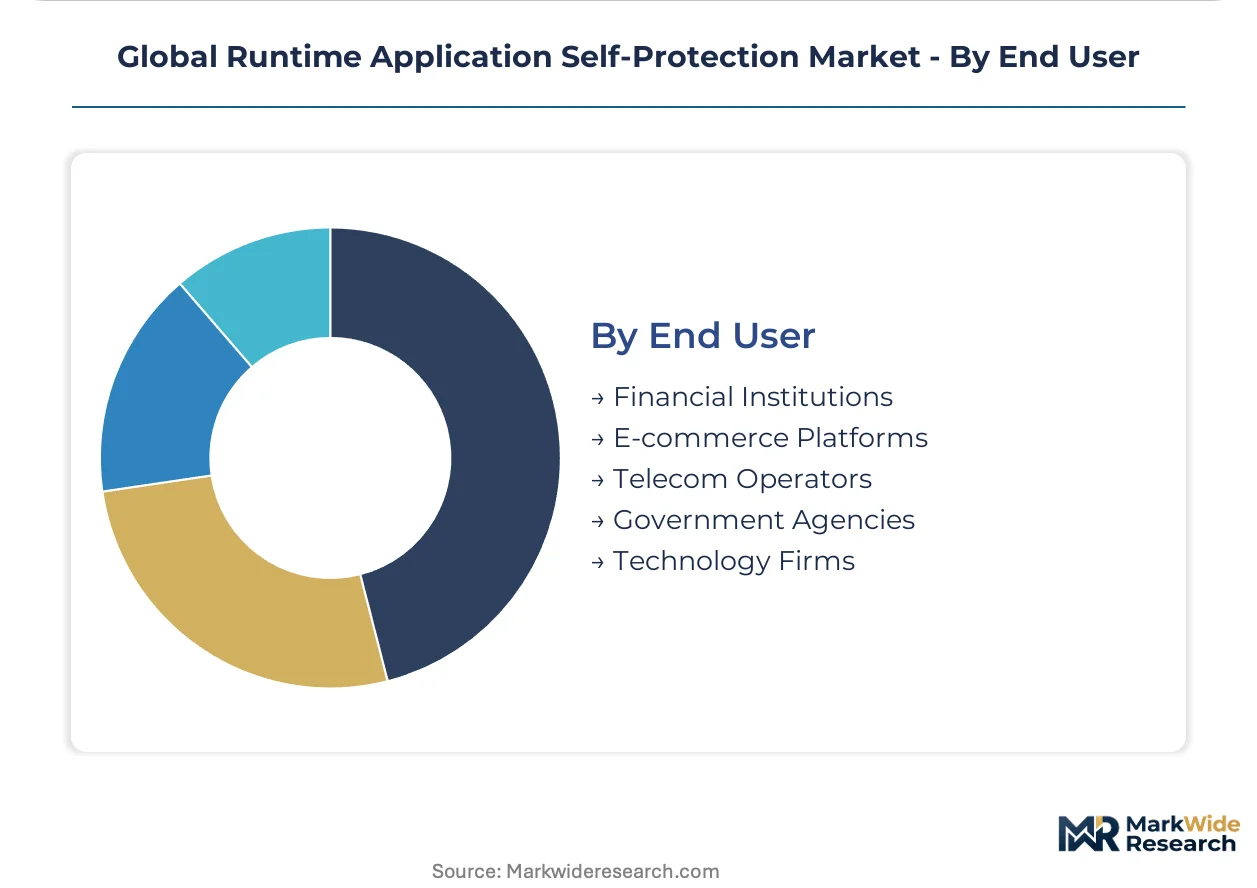
End User:
Vertical risk profiles and regulatory exposure determine procurement urgency and solution sophistication requirements.
- Financial Institutions:SEC cybersecurity disclosure rules, PCI-DSS, and open banking mandates create overlapping compliance burdens. United States banks and German insurers represent deepest account penetration and highest average contract values.
- E-commerce Platforms:India's Digital Personal Data Protection Act and BIS cloud security standards trigger compliance-driven procurement cycles among domestic marketplaces and government digital service providers.
- Technology Firms:DevSecOps-native buyers embed protection into CI/CD pipelines rather than retrofitting post-deployment. Containerized and serverless deployment modes dominate.
- Government Agencies:FedRAMP, BIS, and nation-specific certification requirements fragment vendor qualification. Air-gapped and hybrid deployments persist despite cloud migration trends.
- Telecom Operators:5G network slicing and edge computing workloads require distributed protection beyond traditional data center perimeters. Early-stage segment with infrastructure-specific requirements.
Contract value depth favors Financial Institutions; regulatory velocity favors E-commerce Platforms.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
SEC cybersecurity disclosure rules and NIST guidelines are compressing procurement timelines for financial institutions across multiple jurisdictions. The EU AI Act mandates real-time algorithmic monitoring by fixed deadlines. India's Digital Personal Data Protection Act triggers compliance-driven procurement among domestic platforms.
United States
Financial institutions and payment processors dominate runtime protection procurement under SEC disclosure mandates. FedRAMP certification requirements shape cloud security procurement for government agencies. Silicon Valley technology firms embed protection modules directly into CI/CD pipelines for containerized workloads.
Germany
BSI cloud certification timelines and GDPR enforcement accelerate enterprise adoption of behavior monitoring platforms. Automotive and industrial software manufacturers retrofit legacy systems with embedded protection modules. Munich and Frankfurt financial centers anchor demand for API security solutions under open banking frameworks.
India
BIS cloud security standards and the Digital Personal Data Protection Act create overlapping compliance obligations for e-commerce platforms. Domestic marketplaces in Bangalore and Mumbai integrate runtime monitoring to satisfy data localization requirements. Government digital service providers under the India Stack initiative drive hybrid deployment adoption.
United Kingdom
Open banking mandates and Financial Conduct Authority guidelines force institutions to secure thousands of exposed API endpoints. London fintech clusters deploy serverless protection for event-driven transaction architectures. Cybersecurity vendors target the UK market as a bridgehead for EU regulatory alignment post-Brexit.
Japan
METI cybersecurity guidelines and critical infrastructure protection standards elevate runtime protection for industrial control systems. Tokyo financial institutions integrate behavioral analytics to satisfy cross-border data governance requirements. Osaka-based manufacturing technology firms adopt embedded modules for IoT edge computing workloads.
Global Runtime Application Self-Protection Market Competitive Landscape
Channel-controlling players compete with product-specialist players across deployment modes and vertical segments. The vendor base organizes into three tiers: cloud-native platform providers with bundled security-observability stacks, standalone runtime protection specialists with deep instrumentation expertise, and network security incumbents extending into application-layer controls. Dominant competitive moves include strategic partnerships with DevOps tooling vendors and geographic expansion through managed security service provider channels.
Within the cloud-native platform tier, Dynatrace and Palo Alto Networks exemplify converged security-observability positioning. Imperva occupies a specialist position anchored in hybrid deployment expertise. Contrast Security represents the pure-play runtime instrumentation archetype with deep code-level embedding capabilities. These three companies collectively span the strategic spectrum from bundled platform delivery to targeted protection modules.
| Leading Market Players |
|---|
| Contrast Security |
| Imperva |
| Pradeo |
| Guardsquare |
| Promon |
| Palo Alto Networks |
| Dynatrace |
| Veracode |
| Fortinet |
| Others |
Supply & Pricing Matrix
United States-based cloud infrastructure providers concentrate upstream supply of runtime protection instrumentation modules, anchoring margin pools in threat detection analytics and recurring telemetry consumption rather than perpetual licensing. Pricing power downstream concentrates with vendors bundling security-observability convergence, while standalone instrumentation specialists face compression from consumption-based SaaS alternatives.
Pricing Analysis
Certification level (FedRAMP/BSI/ISO 27001-grade) creates the primary spread between premium and standard tiers, with government-grade compliance adding substantial uplift. Subscription-based SaaS delivery dominates, displacing perpetual licenses as mid-market buyers seek operational expenditure alignment. Price differentiation hinges on telemetry intensity and multi-jurisdiction compliance engineering, with financial institutions showing lowest sensitivity due to regulatory mandate density. Cost compression in the standard tier is intensifying because hyperscaler marketplaces aggregate undifferentiated runtime agents.
Supply Chain Analysis
Export-control regimes around advanced behavioral analytics and kernel-level instrumentation limit technology flows from the United States to certain jurisdictions, fragmenting vendor qualification paths. Supply concentrates in the United States, Germany, and India for cloud-native protection modules, with Israel and the United Kingdom contributing specialist instrumentation expertise. Component dependencies include language-specific runtime libraries, container orchestration hooks, and explainable AI attribution engines. Single-source vulnerability around FedRAMP-authorized cloud regions poses structural risk. Distribution runs through hyperscaler marketplaces and managed security service provider channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Runtime Application Self-Protection represents a service-attach opportunity where threat detection analytics and continuous compliance monitoring expand faster than base platform licensing, embedding vendors deeper into operational workflows.
For Market Incumbents: Insulate recurring revenue streams by deepening vertical integration into explainable AI attribution engines, reducing black-box replacement risk from EU AI Act compliance cycles. Fortify FedRAMP and BSI certification moats against emerging cloud-native entrants lacking government qualification timelines. Channel control through managed security service provider exclusivity agreements anchors enterprise account retention. For New Entrants and Emerging Players: Establish a beachhead in Indian e-commerce platforms facing Digital Personal Data Protection Act compliance deadlines, where domestic runtime protection penetration remains underdeveloped. Target serverless function protection for technology firms building event-driven architectures, a segment underserved by legacy agent-based vendors. Lead with consumption-based pricing and DevOps-native instrumentation to bypass incumbent enterprise sales cycles. For Investors and Strategic Acquirers: Secondary-cycle assets sit with private equity-backed runtime protection specialists possessing deep instrumentation expertise but lacking cloud-native platform scale. Long-term viability over the coming decade hinges on convergence with application performance monitoring and observability tooling. Watch for inflection signals in hyperscaler marketplace attachment rates, which indicate platform distribution leverage.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration with APM Tooling | Dynatrace and Palo Alto Networks anchor converged security-observability positioning against vendor sprawl. |
| FedRAMP Certification Investment | United States government procurement mandates disqualify uncertified vendors from federal cloud security contracts. |
| Strategic Partnership with DevOps Vendors | CI/CD pipeline embedding accelerates procurement cycles among technology firms with cloud-native portfolios. |
| Acquisition of Specialist Instrumentation Firms | Deep code-level embedding capabilities address containerized and serverless protection gaps in incumbent platforms. |
| Geographic Expansion through MSSP Channels | Managed security service providers bundle runtime protection with broader detection and response services in Germany and India. |
Research Methodology
Two parallel data streams informed the analysis: primary interviews with chief information security officers, DevSecOps leads, cloud platform engineers, and managed security service provider executives; and secondary validation through SEC cybersecurity disclosure filings, FedRAMP authorization databases, BSI cloud certification registries, and hyperscaler marketplace telemetry disclosures. Bottom-up deployment counts across cloud-native, containerized, hybrid, on-premises, and serverless architectures were triangulated against top-down vendor revenue segmentation.
Forecast inputs considered deployment model migration velocity, regulatory compliance deadline clustering, and API endpoint proliferation rates across the projection horizon. Segmentation dimensions modeled include deployment architecture, solution type, use case, and end-user vertical, with regional adoption patterns calibrated against jurisdiction-specific certification requirements. CAGRs were derived from weighted scenario analysis across baseline, accelerated cloud migration, and extended compliance timeline cases.
Stress conditions across FedRAMP authorization delays, EU AI Act enforcement variance, and talent scarcity in runtime instrumentation expertise were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions about regulatory timeline adherence and cloud migration continuity. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
E Passport Market
Security Software
Confidential Computing Market
Security Software
Encryption As A Service Market
Security Software
Sound Masking Systems Market
Security Software
Asia-Pacific Fraud Detection & Prevention Market
Security Software
Software Assurance Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Risk-Based Authentication (RBA) Market
Security Software
Next-Generation Intrusion Prevention System (NGIPS) Market
Security Software
Consumer Endpoint Security Market
Security Software
IAM Security Services Market
Security Software
Global Digital Signature Software Market
Security Software
Vsaas Market
Security Software
Global Optical Encryption Market
Security Software
Asia-Pacific Encryption Software Market
Security Software
AI in Security Market