
 Network Security Market | 2026-2036
Network Security Market Size, Share, and Industry Trends Forecast 2026-2036
Network Security Market Intelligence
Platform bundling is pivoting buyer evaluation criteria from point-product efficacy to integrated control-plane coverage. Palo Alto Networks leverages its Prisma and Cortex consolidation to anchor extended detection and response workloads. CrowdStrike differentiates through cloud-native endpoint protection that competes with legacy perimeter stacks. Fortinet sustains hardware-software convergence in distributed enterprise branches.
Network security encompasses the policies, hardware, and software technologies designed to protect network infrastructure from unauthorized access, misuse, or denial of service, operating through packet inspection, behavioral analytics, and encrypted tunneling at throughput rates exceeding 100 Gbps in carrier-grade deployments. Its primary purpose is to preserve data confidentiality, integrity, and availability across enterprise, government, and service-provider environments. Cloud-based deployment models represent the fastest-expanding configuration as organizations migrate security inspection closer to distributed workforces. Firewall solutions retain the largest installed base but face margin compression from open-source alternatives. Government end-user procurement concentrates in sovereign-cloud and classified-network segments with stringent certification requirements.
The U.S. Cybersecurity and Infrastructure Security Agency enforces binding operational directives that shape federal agency procurement timelines and vendor qualification criteria. The EU NIS2 Directive and GDPR collectively mandate incident reporting and data-protection-by-design, forcing multinational enterprises to harmonize control frameworks across jurisdictions. Stakeholders must monitor evolving SEC disclosure rules for material cybersecurity incidents and calibrate product roadmaps against emerging quantum-resistant encryption standards.
Market Dynamics
Zero-trust architecture mandates from federal agencies are compressing procurement cycles and forcing legacy perimeter vendors to reengineer product roadmaps around identity-centric access controls.
Growth Catalysts
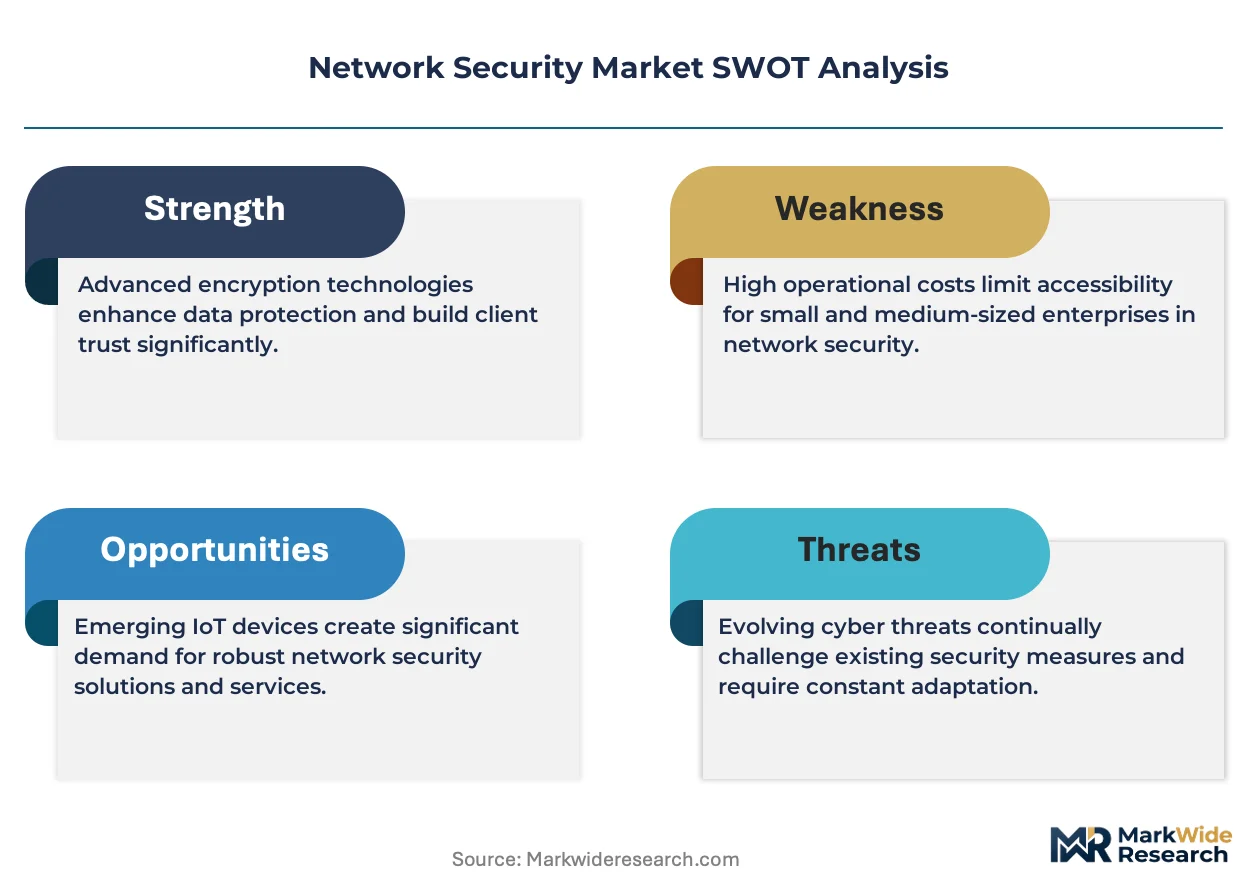
- EU NIS2 Directive:The directive mandates baseline security obligations across critical infrastructure operators in energy, transport, and digital services, expanding addressable market for compliance-grade solutions.
- Cloud-native SASE adoption:Financial services firms deploy Secure Access Service Edge frameworks to consolidate networking and security stacks for distributed workforces.
- Quantum-resistant encryption standards:NIST's post-quantum cryptography guidelines are accelerating refresh cycles in classified-network and sovereign-cloud segments.
Market Restraints
- Semiconductor supply concentration:Advanced packet-processing ASICs depend on fabrication capacity concentrated in Taiwan, creating vulnerability for firewall and DPI appliance manufacturers.
- Skills scarcity in zero-trust implementation:Enterprise IT departments lack personnel certified in identity-aware proxy configuration and microsegmentation deployment.
- Open-source firewall commoditization:pfSense and OPNsense distributions erode pricing power in mid-market branch office deployments.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy sectors require unified IT/OT security platforms as industrial control systems interconnect with corporate networks.
- SEC disclosure rule alignment:Material incident reporting requirements create demand for automated compliance documentation and forensic-ready logging architectures.
- Managed detection and response services:Mid-market enterprises in Germany and France outsource SOC functions to overcome internal capability gaps.
Industry Challenges
- Legacy perimeter integration friction:Hybrid environments force coexistence of hardware firewalls with cloud-native controls, complicating policy orchestration.
- Certification timeline compression:Common Criteria and FIPS 140-3 validation processes extend product launch windows by 12-18 months for federal contractors.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Network Security Market |
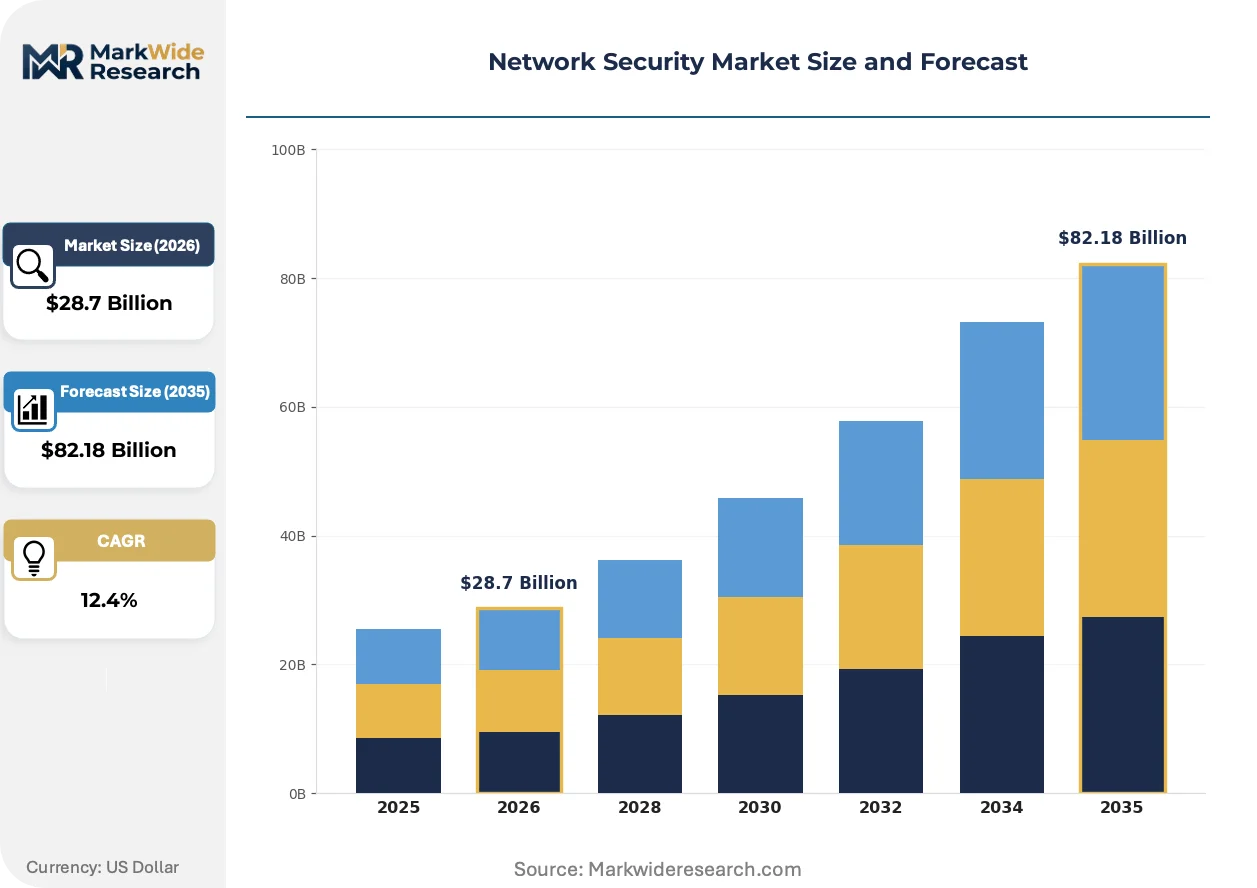
| Market Size in 2026 | $28.7 Billion |
| Market Size in 2035 | $82.18 Billion |
| CAGR (2026 – 2036) | 12.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Firewall, Intrusion Prevention System, Antivirus Software, VPN Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed End User Type: Small Business, Large Enterprise, Government, Military Threat Type: Malware, Phishing, Ransomware, DDoS |
| Companies Covered | Check Point, CrowdStrike, Palo Alto Networks, Trend Micro, Microsoft, Fortinet, Zscaler, Tenable, Cisco, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Network Security Market Strategic Shifts & Innovations
Security function consolidation is collapsing the traditional firewall-SIEM-SOAR stack into unified control planes, with artificial intelligence augmenting detection throughput and reducing mean-time-to-response.
Extended detection and response platforms are modularizing security operations by unifying telemetry from endpoints, networks, and cloud workloads into queryable data lakes. Large enterprises in defense contracting and financial services are replacing point-product deployments with these consolidated architectures. This consolidation is modularizing vendor competitive dynamics, forcing specialization in data-layer analytics or control-plane orchestration rather than monolithic stack ownership.
The EU AI Act imposes risk-tiered obligations on automated decision systems used in security operations, requiring human oversight for high-risk threat-response automation. Security vendors must reengineer autonomous containment features to maintain compliance for European critical infrastructure operators. Financial services and healthcare sectors in France and Germany are prioritizing explainable AI features in procurement evaluations to satisfy regulator scrutiny.
Consumption-based licensing is displacing perpetual appliance purchases as hyperscaler marketplaces become preferred procurement channels. Mid-market buyers in the United States now source network security through AWS Marketplace and Azure Marketplace, compressing traditional reseller margins. Defense contractors and SaaS providers represent the verticals where this channel shift is most pronounced, driven by cloud migration mandates and simplified billing consolidation.
Network Security Market Segmentation
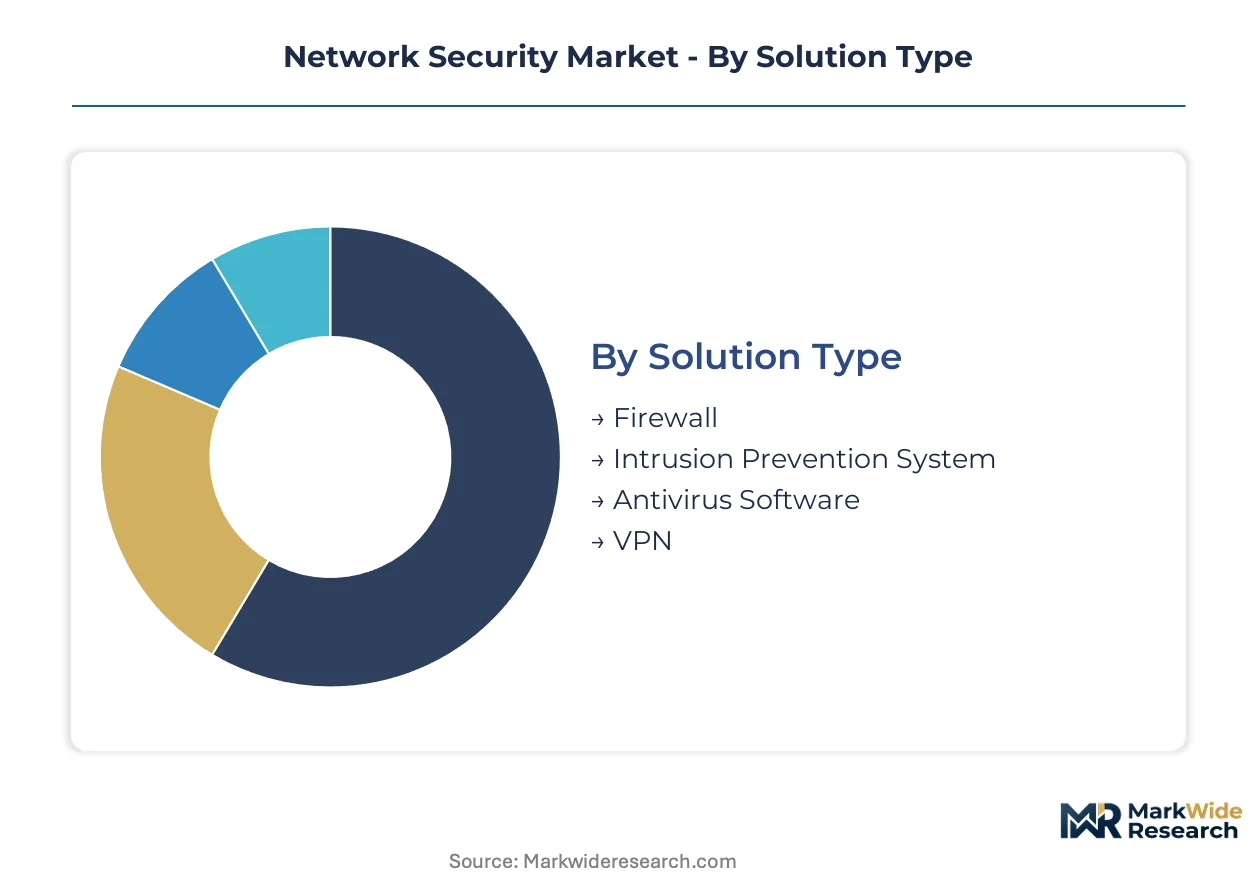
Network security procurement patterns diverge sharply across organizational scale and infrastructure maturity. Solution architecture, deployment topology, and threat exposure profiles collectively determine vendor selection criteria and pricing elasticity.
Solution Type:
Supply concentration in packet-processing silicon shapes competitive dynamics across hardware-dependent categories.
- Firewall:Deep packet inspection appliances process traffic at 100+ Gbps throughput rates using custom ASICs. Defense contractors and federal agencies in the United States drive procurement of FIPS 140-3 certified hardware, constrained by Taiwan fabrication capacity bottlenecks.
- Intrusion Prevention System:Signature and behavioral analysis engines operate inline with sub-millisecond latency requirements. Financial services firms in Germany and France deploy these at network egress points to satisfy EU NIS2 Directive baseline obligations.
- Antivirus Software:Endpoint agents with cloud-managed policy consoles dominate mid-market deployments.
- VPN:Encrypted tunneling solutions face margin pressure from open-source alternatives in branch office configurations.
Firewall solutions absorb the bulk of installed capacity; cloud-native alternatives are expanding most quickly.
Deployment Model:
Cost tier differentiation separates capital-intensive appliance purchases from consumption-based SaaS licensing.
- Cloud-Based:Security service edge architectures consolidate networking and policy enforcement in distributed points of presence. United States defense contractors and SaaS providers source these through AWS Marketplace and Azure Marketplace, compressing traditional reseller margins.
- Hybrid:Split-tunnel configurations route sensitive traffic through on-premises inspection while directing general workloads to cloud gateways. Large enterprises in manufacturing and energy sectors favor this topology to preserve operational technology segmentation.
- On-Premises:Hardware appliances retain dominance in classified-network and sovereign-cloud segments with stringent certification requirements.
- Managed:Outsourced security operations centers address skills scarcity in zero-trust implementation across mid-market enterprises.
On-premises deployments retain the largest revenue base; cloud-based configurations are climbing the fastest.
End User Type:
Customer type determines procurement channel, certification requirements, and pricing negotiation leverage.
- Government:Sovereign-cloud and classified-network segments demand Common Criteria and FIPS 140-3 validation, extending vendor product launch windows. United States federal agency procurement follows binding operational directives from the Cybersecurity and Infrastructure Security Agency.
- Large Enterprise:Platform consolidation strategies favor integrated control planes over point-product efficacy. Extended detection and response workloads unify telemetry from endpoints, networks, and cloud workloads into queryable data lakes.
- Military:Quantum-resistant encryption standards accelerate refresh cycles in classified communications infrastructure.
- Small Business:Open-source firewall distributions erode pricing power in branch office deployments with limited IT staffing.
Large enterprise accounts generate the majority of vendor revenue; government procurement is gaining share fastest.
Threat Type:
Maturity of defensive countermeasures varies with attack vector sophistication and monetization mechanisms.
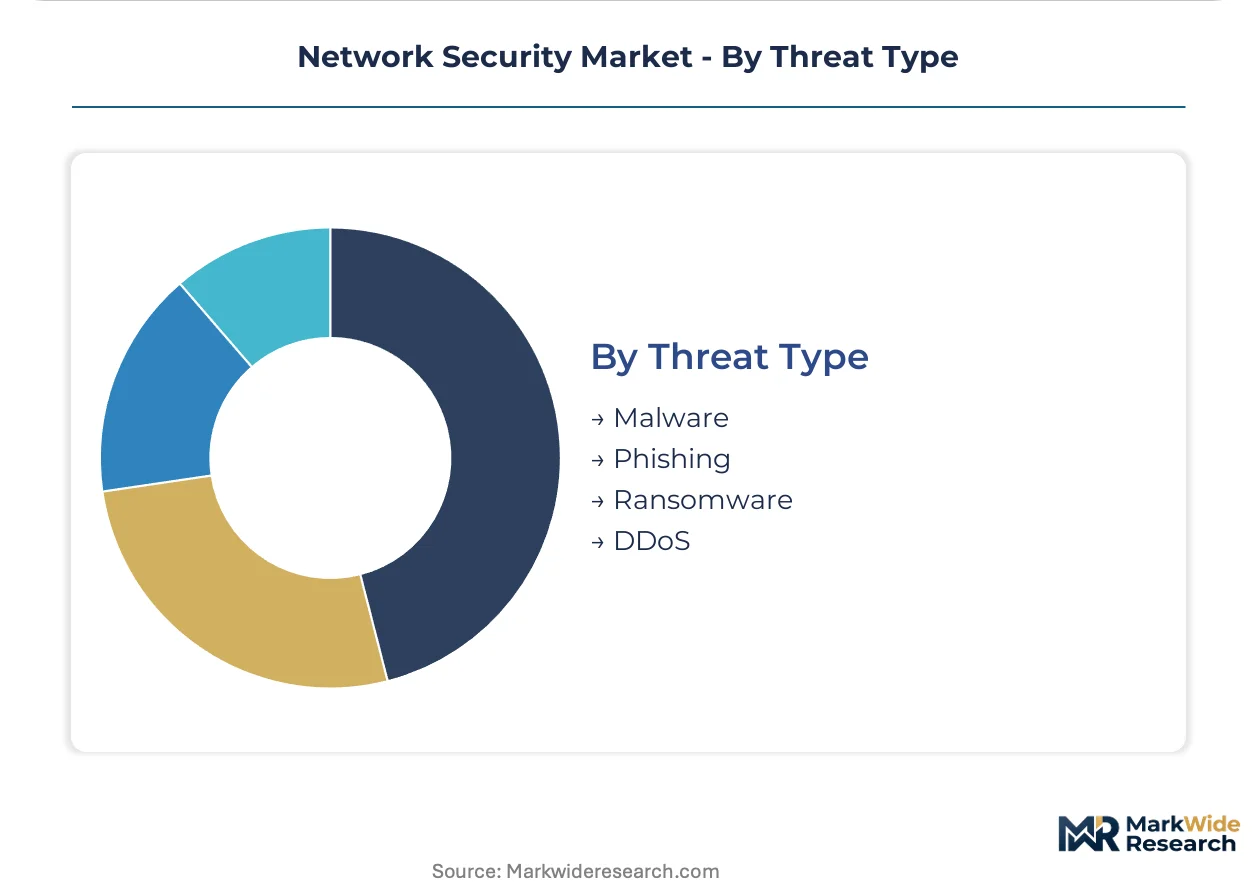
- Ransomware:Encryption-based extortion campaigns target backup infrastructure and operational technology networks. Manufacturing and energy sectors require unified IT/OT security platforms as industrial control systems interconnect with corporate networks.
- Phishing:Credential harvesting through deceptive communications drives demand for identity-aware proxy configuration and microsegmentation deployment.
- Malware:File-based and fileless execution techniques demand behavioral analytics augmentation of signature-based detection.
- DDoS:Volumetric and application-layer floods require carrier-grade scrubbing capacity with geographic distribution.
Ransomware defense absorbs the bulk of security operations investment; phishing prevention capabilities are expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's concentration of venture capital and defense procurement offices anchors North American network security demand. Federal contracting corridors in Northern Virginia and Maryland amplify this concentration through classified infrastructure spending.
United States
Defense contractors in the Washington metropolitan area drive procurement of FIPS 140-3 certified hardware under CISA binding operational directives. The Cybersecurity and Infrastructure Security Agency compresses vendor qualification timelines for federal agencies. Cloud migration mandates push SaaS providers toward AWS Marketplace and Azure Marketplace procurement channels.
Germany
Industrial automation clusters in Bavaria and Baden-Württemberg demand unified IT/OT security platforms for manufacturing floor integration. The EU NIS2 Directive imposes baseline security obligations on critical infrastructure operators. Frankfurt's financial services hub deploys Secure Access Service Edge frameworks for distributed workforce consolidation.
France
Energy sector operators in Île-de-France and Provence-Alpes-Côte d'Azur face tightened incident reporting requirements under EU NIS2. ANSM and CNIL oversight extends to automated threat-response systems under the EU AI Act. Paris-based financial institutions prioritize explainable AI features in security procurement evaluations.
United Kingdom
London's financial services concentration accelerates cloud-native SASE adoption for regulatory compliance documentation. The National Cyber Security Centre shapes vendor qualification criteria for critical national infrastructure operators. Scottish energy utilities integrate OT security platforms as offshore wind infrastructure interconnects with corporate networks.
Japan
Tokyo's financial district and Osaka's manufacturing corridor drive demand for quantum-resistant encryption in classified communications. METI guidelines accelerate refresh cycles in critical infrastructure protection systems. Yokohama's port automation projects require behavioral analytics augmentation for operational technology networks.
Network Security Market Key Industry Players
Diversified conglomerates compete with focused pure-play specialists across converged security stacks. Platform bundling compresses margins for point-product vendors while elevating integrated control-plane providers. Three archetypes dominate: hardware-software convergers, cloud-native consolidators, and identity-centric access specialists. M&A activity targets zero-trust capability gaps, while strategic partnerships address semiconductor supply constraints.
Within the cloud-native consolidator tier, Palo Alto Networks and CrowdStrike exemplify platform bundling strategies that collapse traditional firewall-SIEM-SOAR stacks. Fortinet occupies a position bridging hardware-software convergence with distributed enterprise branch requirements. These three anchors represent divergent responses to federal zero-trust mandates and EU NIS2 compliance pressures.
| Leading Market Players |
|---|
| Check Point |
| CrowdStrike |
| Palo Alto Networks |
| Trend Micro |
| Microsoft |
| Fortinet |
| Zscaler |
| Tenable |
| Cisco |
| Others |
Cost & Logistics Intelligence
Custom ASIC fabrication migration to advanced process nodes simultaneously escalates R&D amortization costs and concentrates packet-processing silicon supply among Taiwan-based foundries. This dual compression reshapes vendor margin structures and procurement risk profiles across firewall and DPI appliance categories.
Pricing Analysis
Short lead-time premiums for FIPS 140-3 certified hardware run 15-25% above standard procurement cycles, while spot inventory of prior-generation appliances trades at distressed clearing levels. Three-tier pricing structure across certified sovereign-cloud, enterprise-grade, and mid-market branch configurations dominates vendor catalogs. Price differentiation rests on Common Criteria certification level and throughput scale. Cost compression in mid-market tiers is intensifying because pfSense and OPNsense distributions erode proprietary appliance value. Small business buyers exhibit highest price sensitivity; defense contractors demonstrate lowest elasticity due to mandate-driven replacement schedules.
Supply Chain Analysis
Reverse-logistics flows for firewall appliance refurbishment remain underdeveloped, creating stranded hardware value and circular economy gaps. Packet-processing ASIC supply concentrates in Taiwan, South Korea, and the United States. Advanced node fabrication draws from EUV lithography equipment, high-purity silicon wafers, and specialty chemical precursors. Single-source vulnerability in Taiwan fabrication capacity represents the dominant structural risk. Distribution runs through hyperscaler marketplaces, direct OEM channels, and traditional value-added resellers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform consolidation is compressing viable vendor count as zero-trust mandates force point-product specialists toward acquisition or exit. EU NIS2 compliance costs and federal certification timelines disproportionately burden undercapitalized players.
For Market Incumbents: Deepen hardware-software convergence in distributed enterprise branches to defend against cloud-native displacement. Fortify Taiwan supply relationships through multi-foundry qualification and strategic inventory positioning. Accelerate Cortex and Prisma-style platform bundling to capture extended detection and response workloads before point-product competitors recover.
For New Entrants and Emerging Players: Begin with managed detection and response services for mid-market German and French enterprises lacking internal SOC capabilities. Operational technology convergence in manufacturing and energy sectors offers the most penetrable white-space. Pursue consumption-based licensing through AWS Marketplace and Azure Marketplace to bypass traditional channel margin compression.
For Investors and Strategic Acquirers: Exit pathways concentrate in platform bundling acquisitions by diversified conglomerates seeking zero-trust capability gaps. Long-term viability favors vendors with sovereign-cloud certification traction and quantum-resistant encryption roadmaps. Watch NIST post-quantum cryptography standard finalization as inflection signal for classified-network refresh cycle acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies firewall-SIEM-SOAR stacks into queryable data lakes for defense contractors. |
| Strategic Partnership | Addresses Taiwan fabrication concentration through multi-foundry ASIC qualification. |
| Acquisition of Specialist Firm | Fills zero-trust identity-aware proxy gaps in consolidated control planes. |
| Geographic Expansion | Captures EU NIS2 compliance demand across German industrial automation clusters. |
| Product Launch | Deploys quantum-resistant encryption modules for classified-network refresh cycles. |
Research Approach
Independent corroboration across CISO interviews, federal procurement officer consultations, and hyperscaler channel manager discussions underwrites the qualitative findings. Primary fieldwork encompassed security architects at financial services firms, OT security leads at energy utilities, and IT procurement officers at defense contractors. Secondary validation drew from CISA binding operational directives, NIST post-quantum cryptography guidelines, EU NIS2 implementation texts, and SEC cybersecurity disclosure rule filings. Bottom-up vendor revenue triangulation against top-down addressable market sizing anchored segmentation outputs.
Rate-of-change decomposition across hardware refresh cycles, cloud migration trajectories, and compliance mandate timelines structured the analytical framework. Segmentation dimensions modeled include solution type, deployment topology, organization scale, threat exposure profile, and regional regulatory cluster. CAGRs derived from fitted adoption curves calibrated against historical procurement velocity and policy implementation schedules. Quantum-resistant encryption standard readiness and SASE architecture penetration served as industry-specific forecast inputs.
Semiconductor supply disruption, EU AI Act enforcement intensity, and federal procurement timeline compression are the dominant revision risks. Forecasts reflect documented assumptions regarding Taiwan fabrication capacity continuity and NIST standard finalization pacing. Practitioners should monitor CISA directive issuance frequency and ANSM/CNIL automated decision system rulings for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
Cognitive Security Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Data Center Security Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Romania Cybersecurity Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Global Container and Kubernetes Security Market