
 Security Product Integration Services Market | 2026-2036
Security Product Integration Services Market Size, Share, and Industry Trends Forecast 2026-2036
Security Product Integration Services Market Analytics
Enterprise buyers are bifurcating from small commercial purchasers as the dominant revenue pool for integration services. Johnson Controls dominates large-scale building automation integrations across North American critical infrastructure. Bosch Security Systems anchors European demand through its deep specialization in multi-vendor surveillance system convergence.
Security product integration services encompass the engineering, configuration, and interoperability enablement of disparate physical and digital security technologies into unified operational platforms, typically requiring API-level protocol translation, edge-to-cloud data pipeline construction, and centralized command interface deployment. Cloud-based delivery models are capturing the fastest expansion as hybrid architectures reduce on-premise capital intensity for mid-market adopters. Installation services retain the largest margin pool due to site-specific engineering complexity and certified technician scarcity.
FDA cybersecurity guidance for connected medical devices, HIPAA administrative safeguards, and EU GDPR data processing requirements collectively reshape procurement specifications for healthcare and financial integrations. NIST SP 800-53 controls and ISO 27001 certification frameworks further gate vendor participation in government and enterprise segments. Stakeholders must monitor evolving zero-trust architecture mandates and their downstream impact on multi-vendor system certification costs.
Market Dynamics
Converged physical-cyber security mandates from financial regulators and critical infrastructure authorities are compressing procurement cycles while elevating certification requirements for system integrators serving enterprise accounts.
Growth Catalysts
- EU AI Act compliance deadlines:Financial institutions in Germany and France are accelerating unified platform deployments to meet algorithmic transparency requirements for automated threat detection systems.
- Industrial facility operators:German manufacturing conglomerates are prioritizing edge-to-cloud security pipelines that unify OT network monitoring with physical access control.
- API-level protocol translation:Multi-vendor surveillance convergence is eliminating vendor lock-in, enabling mid-market buyers to integrate best-of-breed sensors without forklift replacements.
Market Restraints
- Certified technician scarcity:Installation services face margin compression as qualified security engineers with both IT networking and physical system credentials remain concentrated in metropolitan Germany and the Netherlands.
- NIST SP 800-53 control mapping:Government segment participation requires 18-24 month vendor accreditation timelines that freeze out smaller integrators lacking dedicated compliance staff.
- On-premise capital intensity:Hybrid architecture transitions are stranding legacy DVR and NVR investments for commercial buyers unable to absorb simultaneous cloud migration and hardware refresh costs.
Strategic Opportunities
- Healthcare cybersecurity gaps:FDA guidance for connected medical devices creates demand for specialized integrators capable of bridging HIPAA administrative safeguards with ISO 27001 certification frameworks.
- Zero-trust architecture mandates:Federal procurement specifications are opening white space for vendors offering continuous authentication integration across physical and logical access layers.
- Mid-market cloud delivery:Subscription-based managed security service platforms are penetrating underserved commercial segments previously excluded by upfront integration capital requirements.
Industry Challenges
- Multi-vendor certification complexity:System integrators must maintain concurrent manufacturer authorizations across competing surveillance, access control, and intrusion detection brands, fragmenting technical training investments.
- Legacy analog infrastructure:Decades of installed coaxial cable and proprietary control panels in European industrial facilities complicate IP migration paths and extend project timelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Product Integration Services Market |
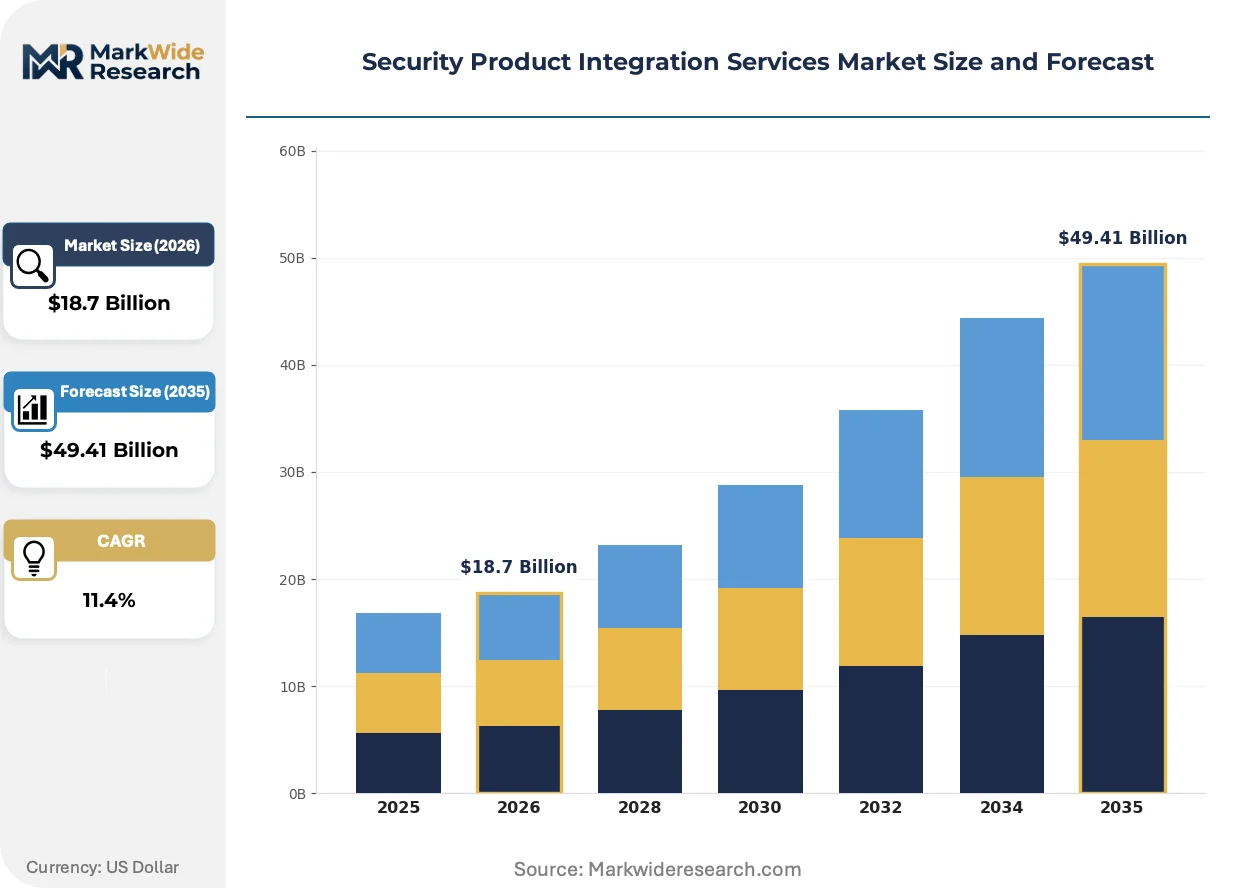
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $49.41 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Consultation, Installation, Customization, Maintenance Delivery Model: On-Premise, Cloud-Based, Managed, Hybrid End User: Retailers, Financial Institutions, Government, Healthcare Providers Technology: Surveillance Systems, Access Control, Intrusion Detection, Alarm Systems |
| Companies Covered | Schneider Electric, Bosch Security Systems, Johnson Controls, Axis Communications AB, ADT Inc., Honeywell International Inc., Cisco Systems, Inc., Convergint, Siemens AG, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Product Integration Services Market Evolving Landscape
Security integration is pivoting from hardware-centric installation toward software-defined orchestration, with edge computing and machine learning inference reshaping how physical security data flows into enterprise IT architectures.
Software-defined perimeter technology is decomposing traditional network security boundaries by embedding micro-segmentation directly into physical access control decisions. Large financial institutions in Frankfurt and London are deploying these architectures at scale. The approach is compressing the distinction between building automation and cybersecurity vendor categories.
GDPR data processing impact assessments now govern biometric surveillance deployments across EU member states, forcing integrators to engineer privacy-by-default architectures with automated data retention enforcement. Healthcare and transportation verticals face the steepest compliance burdens. German facility operators are responding by demanding ISO 27701-certified integration partners.
Enterprise buyers are consolidating vendor relationships around unified platform providers capable of spanning video analytics, identity management, and IoT device security through single-pane command interfaces. Value-added distributors in the Netherlands and Belgium are repositioning as integration orchestrators. This concentration is most visible among Dutch critical infrastructure operators managing port and airport security ecosystems.
Security Product Integration Services Market Segmentation
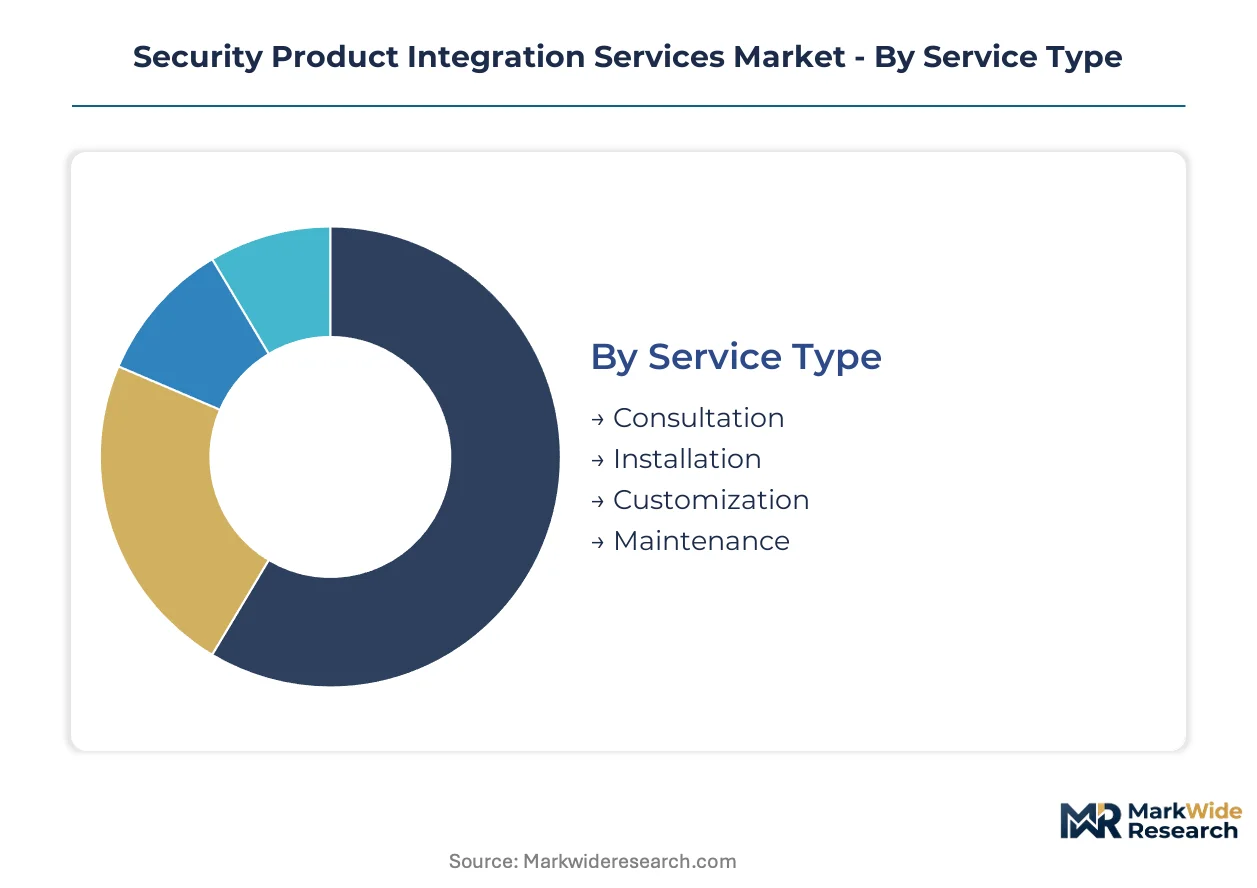
Segmentation in security product integration services determines vendor certification requirements, margin structures, and procurement channel selection. Buyers in regulated verticals demand specialized compliance capabilities that reshape competitive positioning across each category.
Service Type:
EU AI Act algorithmic transparency mandates and NIST SP 800-53 control frameworks create divergent compliance burdens across service tiers, concentrating procurement with certified specialists.
- Consultation:Front-end assessment of security architecture gaps against GDPR data processing requirements and FDA cybersecurity guidance for healthcare deployments. German financial institutions in Frankfurt prioritize consultative engagements that map zero-trust principles to existing physical access infrastructure.
- Installation:Site-specific engineering of edge-to-cloud pipelines and API-level protocol translation requiring dual-credentialed technicians with IT networking and physical system expertise. Dutch critical infrastructure operators at Rotterdam port facilities drive concentrated demand for certified installation teams.
- Customization:Tailored integration of multi-vendor surveillance and access control platforms to specific operational workflows.
- Maintenance:Ongoing system health monitoring, firmware updates, and compliance audit documentation.
Installation handles the majority of throughput; Consultation is gaining share fastest as regulatory complexity elevates upfront architecture planning.
Delivery Model:
Capital intensity thresholds and hybrid architecture maturity determine buyer access to each delivery tier, with subscription models penetrating mid-market segments previously excluded by upfront integration costs.
- On-Premise:Dedicated hardware deployment with localized data retention satisfying GDPR sovereignty requirements for biometric surveillance in French transportation hubs.
- Cloud-Based:Centralized orchestration of distributed security sensors through software-defined perimeter technology, eliminating forklift hardware replacements. London financial institutions deploy these architectures at scale to compress building automation and cybersecurity vendor categories.
- Managed:Outsourced security operations with continuous monitoring and incident response.
- Hybrid:Edge computing inference with cloud analytics aggregation, balancing latency-sensitive physical access decisions against centralized threat intelligence.
Hybrid architectures are expanding most quickly as industrial operators reconcile legacy analog investments with cloud analytics requirements.
End User:
Vertical-specific regulatory frameworks reshape procurement specifications, with HIPAA administrative safeguards and EU AI Act deadlines creating divergent vendor qualification barriers.
- Financial Institutions:Unified platform deployments spanning video analytics, identity management, and IoT device security through single-pane command interfaces. German banks in Frankfurt accelerate procurement to meet algorithmic transparency deadlines for automated threat detection systems.
- Government:NIST SP 800-53 accreditation requirements and 18-24 month vendor certification timelines that freeze out smaller integrators. Federal procurement specifications in Washington D.C. open white space for continuous authentication integration across physical and logical access layers.
- Healthcare Providers:FDA cybersecurity guidance for connected medical devices creates demand for specialized HIPAA-ISO 27001 bridge capabilities.
- Retailers:Loss prevention and customer analytics with GDPR-compliant biometric data handling.
Financial institutions command the largest procurement volumes; Healthcare providers are climbing the fastest as medical device connectivity mandates multiply integration touchpoints.
Technology:
Software-defined orchestration is displacing hardware-centric installation across all technology categories, with machine learning inference reshaping how physical security data flows into enterprise IT architectures.
- Surveillance Systems:Multi-vendor camera convergence with privacy-by-default architectures featuring automated data retention enforcement. GDPR impact assessments now govern biometric deployments across EU member states, forcing ISO 27701-certified integration partnerships.
- Access Control:Software-defined perimeter technology embedding micro-segmentation directly into physical access decisions. Belgian value-added distributors reposition as integration orchestrators for unified identity management platforms.
- Intrusion Detection:Sensor fusion across perimeter, interior, and network-layer threat vectors.
- Alarm Systems:Legacy panel modernization with IP-enabled central station connectivity.
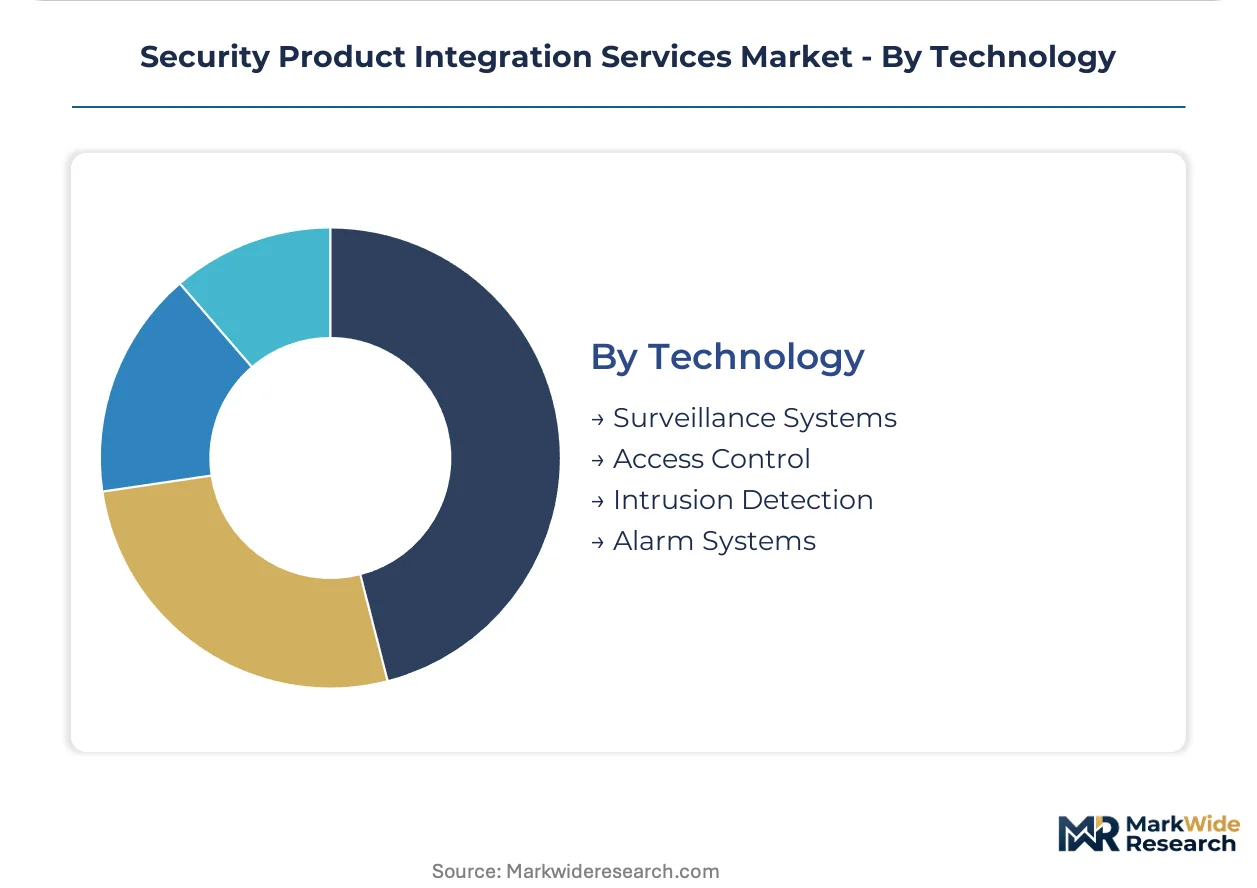
Surveillance systems absorb the greatest integration engineering hours; Access control is expanding most quickly as zero-trust mandates compress physical-cyber security boundaries.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Port of Rotterdam's automated container handling systems anchor Dutch demand for converged physical-cyber security architectures. Frankfurt's banking infrastructure drives German procurement of unified threat detection platforms. London's financial district accelerates cloud-based security orchestration deployments.
United States
Federal procurement specifications for zero-trust architectures and critical infrastructure protection drive enterprise integration demand. NIST SP 800-53 accreditation requirements create 18-24 month vendor certification barriers that favor established integrators. Washington D.C. and New York Metro financial institutions deploy continuous authentication systems across physical and logical access layers.
Germany
Industrial facility operators in the Ruhr Valley prioritize edge-to-cloud security pipelines unifying OT network monitoring with physical access control. EU AI Act algorithmic transparency deadlines accelerate unified platform deployments for automated threat detection. Frankfurt banking clusters demand ISO 27701-certified integration partners for biometric surveillance compliance.
United Kingdom
London financial institutions deploy software-defined perimeter technology at scale to compress building automation and cybersecurity vendor categories. GDPR data processing requirements govern biometric surveillance deployments across transportation hubs. The City of London's critical infrastructure operators consolidate vendor relationships around single-pane command interfaces.
Netherlands
Rotterdam port facilities and Amsterdam Schiphol Airport drive concentrated demand for certified installation teams with dual IT-physical system credentials. Value-added distributors reposition as integration orchestrators for unified identity management platforms. Dutch critical infrastructure operators manage complex multi-vendor surveillance convergence across maritime and aviation security ecosystems.
France
Paris transportation hubs face steep GDPR compliance burdens for biometric surveillance deployments requiring privacy-by-default architectures. CNIL enforcement actions accelerate automated data retention enforcement engineering. French financial institutions in La Défense accelerate procurement to meet EU AI Act deadlines for algorithmic transparency in automated threat detection.
Security Product Integration Services Market Competitive Landscape
Concentration sits with diversified industrial conglomerates possessing dedicated security divisions and certified compliance capabilities. The vendor base spans building automation specialists, multi-vendor surveillance integrators, and IT networking incumbents extending into physical security. Three archetypes dominate: industrial automation conglomerates with captive security divisions; pure-play security integrators with deep manufacturer authorizations; and IT infrastructure vendors leveraging existing enterprise relationships. Competitive moves center on strategic partnerships for multi-vendor certification coverage and geographic expansion through acquisition of regional installation specialists.
Among diversified industrial conglomerates, Schneider Electric, Siemens AG, and Johnson Controls exemplify the archetype of building automation incumbents extending into converged physical-cyber security integration. These entities occupy positions where industrial facility relationships and certified technician networks create defensive moats against pure-play competitors. Bosch Security Systems and Axis Communications AB represent European specialists in multi-vendor surveillance system convergence, anchoring demand through deep manufacturer authorization portfolios. IT infrastructure incumbents including Cisco Systems and Honeywell International sit within a distinct tier, leveraging existing enterprise networking relationships to capture security orchestration opportunities as zero-trust mandates compress traditional vendor boundaries.
| Leading Market Players |
|---|
| Schneider Electric |
| Bosch Security Systems |
| Johnson Controls |
| Axis Communications AB |
| ADT Inc. |
| Honeywell International Inc. |
| Cisco Systems, Inc. |
| Convergint |
| Siemens AG |
| Others |
Value Network & Pricing Analysis
Ninety-day lead times for certified integration engineers in metropolitan Germany compress margin structures while amplifying pricing power for dual-credentialed technician networks. This inventory scarcity interacts with EU AI Act compliance deadlines to create tiered service premiums that separate certified specialists from commodity installation providers.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels separates ISO 27701-certified integrators serving Frankfurt banking clusters from uncertified regional installers. Price differentiation rests on compliance certification grade and geographic technician density, with German industrial operators absorbing premium rates for edge-to-cloud pipeline engineering. Cost compression in mid-market cloud delivery intensifies as subscription models displace project-based contracting. Small commercial purchasers exhibit highest price sensitivity, while critical infrastructure operators prioritize certification over cost.
Supply Chain Analysis
Germany and the Netherlands anchor certified technician training pipelines, while Taiwan and South Korea feed sensor hardware and edge computing components into integration architectures. Raw material dependencies span silicon for video analytics processors, rare earth elements for access control magnets, and specialized cabling for IP migration projects. Single-source vulnerability concentrates in NIST SP 800-53 accreditation consultancies, where qualified compliance staff remain tethered to Washington D.C. and Frankfurt. Distribution runs through value-added distributors repositioning as integration orchestrators in Belgium and the Netherlands.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Security product integration services are crossing into platform economics as software-defined perimeter technology collapses traditional vendor boundaries between building automation and cybersecurity. API-level protocol standardization is creating network effects that reward early unified platform adopters.
For Market Incumbents: Shield certified technician networks in Germany and the Netherlands through captive training academy investments and non-compete enforcement. Acquire regional installation specialists in France and Belgium to preempt pure-play competitors from capturing EU AI Act compliance-driven procurement waves. Consolidate manufacturer authorization portfolios to reduce multi-vendor certification fragmentation costs.
For New Entrants and Emerging Players: Lead with HIPAA-ISO 27001 bridge capabilities targeting healthcare providers facing FDA cybersecurity guidance deadlines. Penetrate mid-market cloud delivery segments through subscription-based managed security platforms previously excluded by capital intensity barriers. Partner with Dutch value-added distributors for channel access to Rotterdam port and Schiphol Airport ecosystems.
For Investors and Strategic Acquirers: Long-term, this sits as a compliance-arbitrage play because regulatory certification moats deepen faster than technical differentiation erodes. Target acquisition profiles should emphasize ISO 27701-certified integrators with established Frankfurt or London financial institution relationships. Monitor CNIL enforcement action velocity as the signal indicating biometric surveillance compliance spending inflection.
| Strategic Initiative | Industry Significance |
|---|---|
| Multi-Vendor Certification Expansion | Reduces training fragmentation costs for integrators serving competing surveillance brands. |
| Edge-to-Cloud Pipeline Development | Enables German industrial operators to unify OT network monitoring with physical access control. |
| ISO 27701 Certification Investment | Opens GDPR-compliant biometric surveillance procurement from Frankfurt banking clusters. |
| Zero-Trust Architecture Integration | Captures federal procurement specifications for continuous authentication across access layers. |
| Healthcare Cybersecurity Specialization | Bridges FDA guidance requirements with HIPAA administrative safeguards for medical device connectivity. |
Research Methodology
A spread of perspectives from security integration engineers, critical infrastructure procurement officers, compliance consultants, and value-added distributor executives converged on the working assumptions. Primary fieldwork combined structured interviews with secondary validation against SEC filings, EU regulatory databases, customs records for security hardware imports, and NIST publication archives. Bottom-up technician capacity modeling and top-down enterprise IT spending analysis were triangulated to derive service demand estimates.
Segmentation dimensions modeled span service type, delivery model, end-user vertical, and technology category across the projection horizon. CAGRs were derived from regression analysis of historical procurement cycle data and regulatory deadline acceleration effects. Forecast inputs incorporated EU AI Act implementation timelines, NIST SP 800-53 accreditation queue lengths, and cloud migration adoption curves among mid-market commercial buyers.
Forecasts assume regulatory continuity in EU AI Act enforcement and NIST cybersecurity framework adoption; material policy shifts would require re-modeling compliance-driven procurement acceleration. Specific risks include tariff exposure on Taiwanese edge computing components, CNIL enforcement variability affecting biometric deployment timelines, and technician training pipeline constraints in German metropolitan markets. Recalibration cycles align with material shifts in regulatory deadline schedules and zero-trust architecture mandate expansions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Vietnam Private Security Market
Security and Surveillance
Consumer Security Market
Security and Surveillance
Global Security As a Service Market
Security and Surveillance
Proactive Security Market
Security and Surveillance
Global Traveler Security Services Market
Security and Surveillance
Speed Limit Radar Signs Market
Security and Surveillance
Smart Home Security Market
Security and Surveillance
Radar Security Market
Security and Surveillance
Shock Sensor Market
Security and Surveillance
Global Security Orchestration Market
Security and Surveillance
Middle East and Africa Baggage and Parcel Screening Market
Security and Surveillance
Security System Integrators Market
Security and Surveillance
Global Law Enforcement Software Market
Security and Surveillance
Anti-Piracy Protection Market
Security and Surveillance
Intelligent Fencing Market
Security and Surveillance
Global X-Ray Security Scanner Market